
✨ panel-live-server


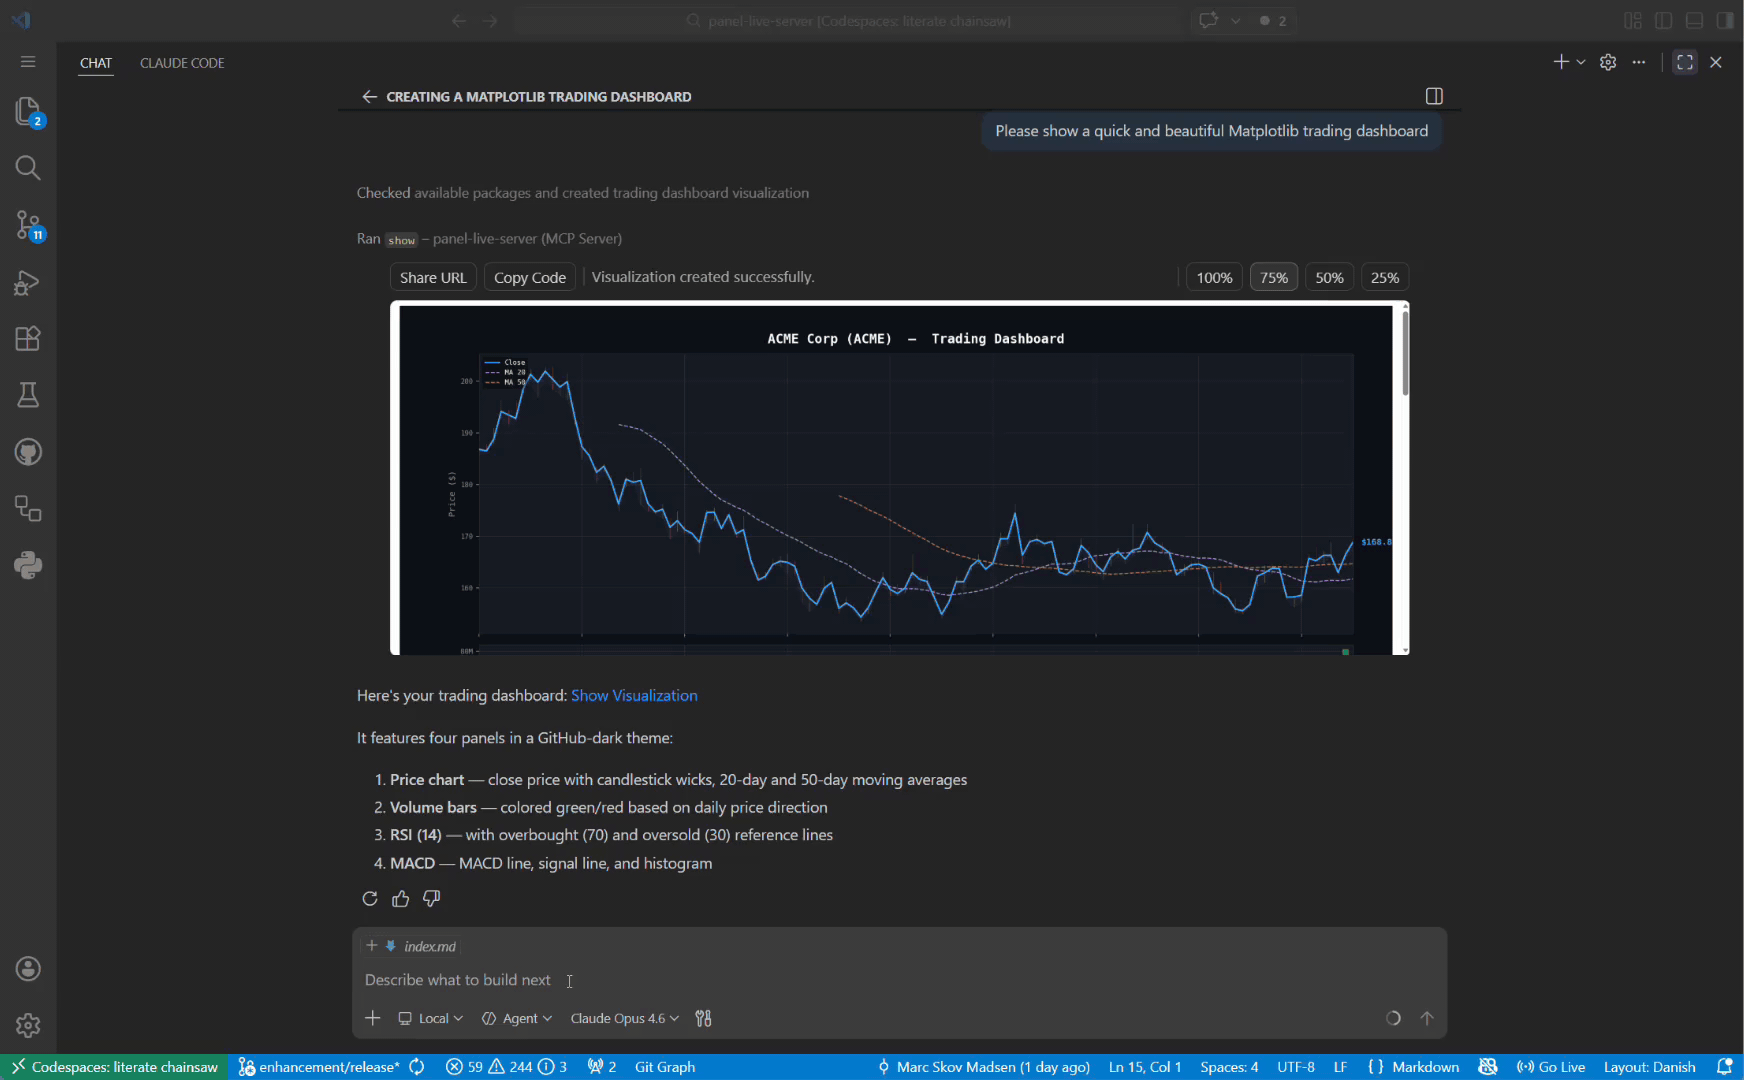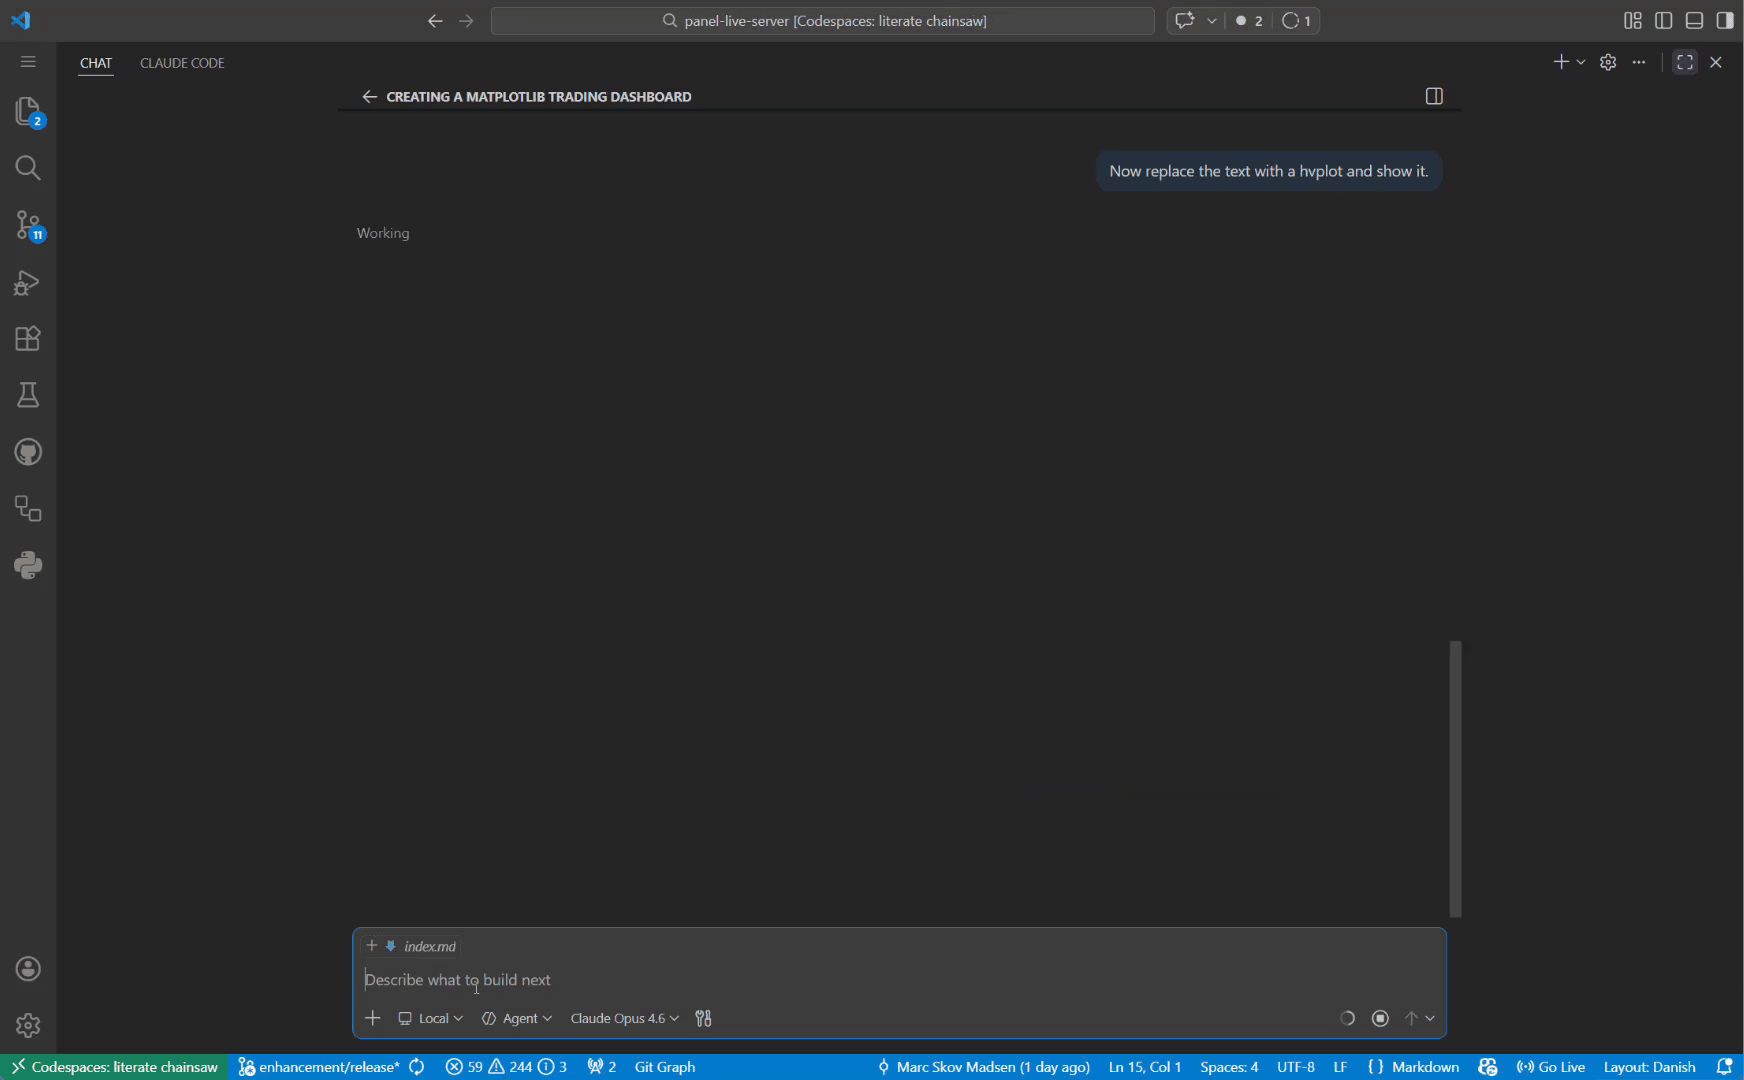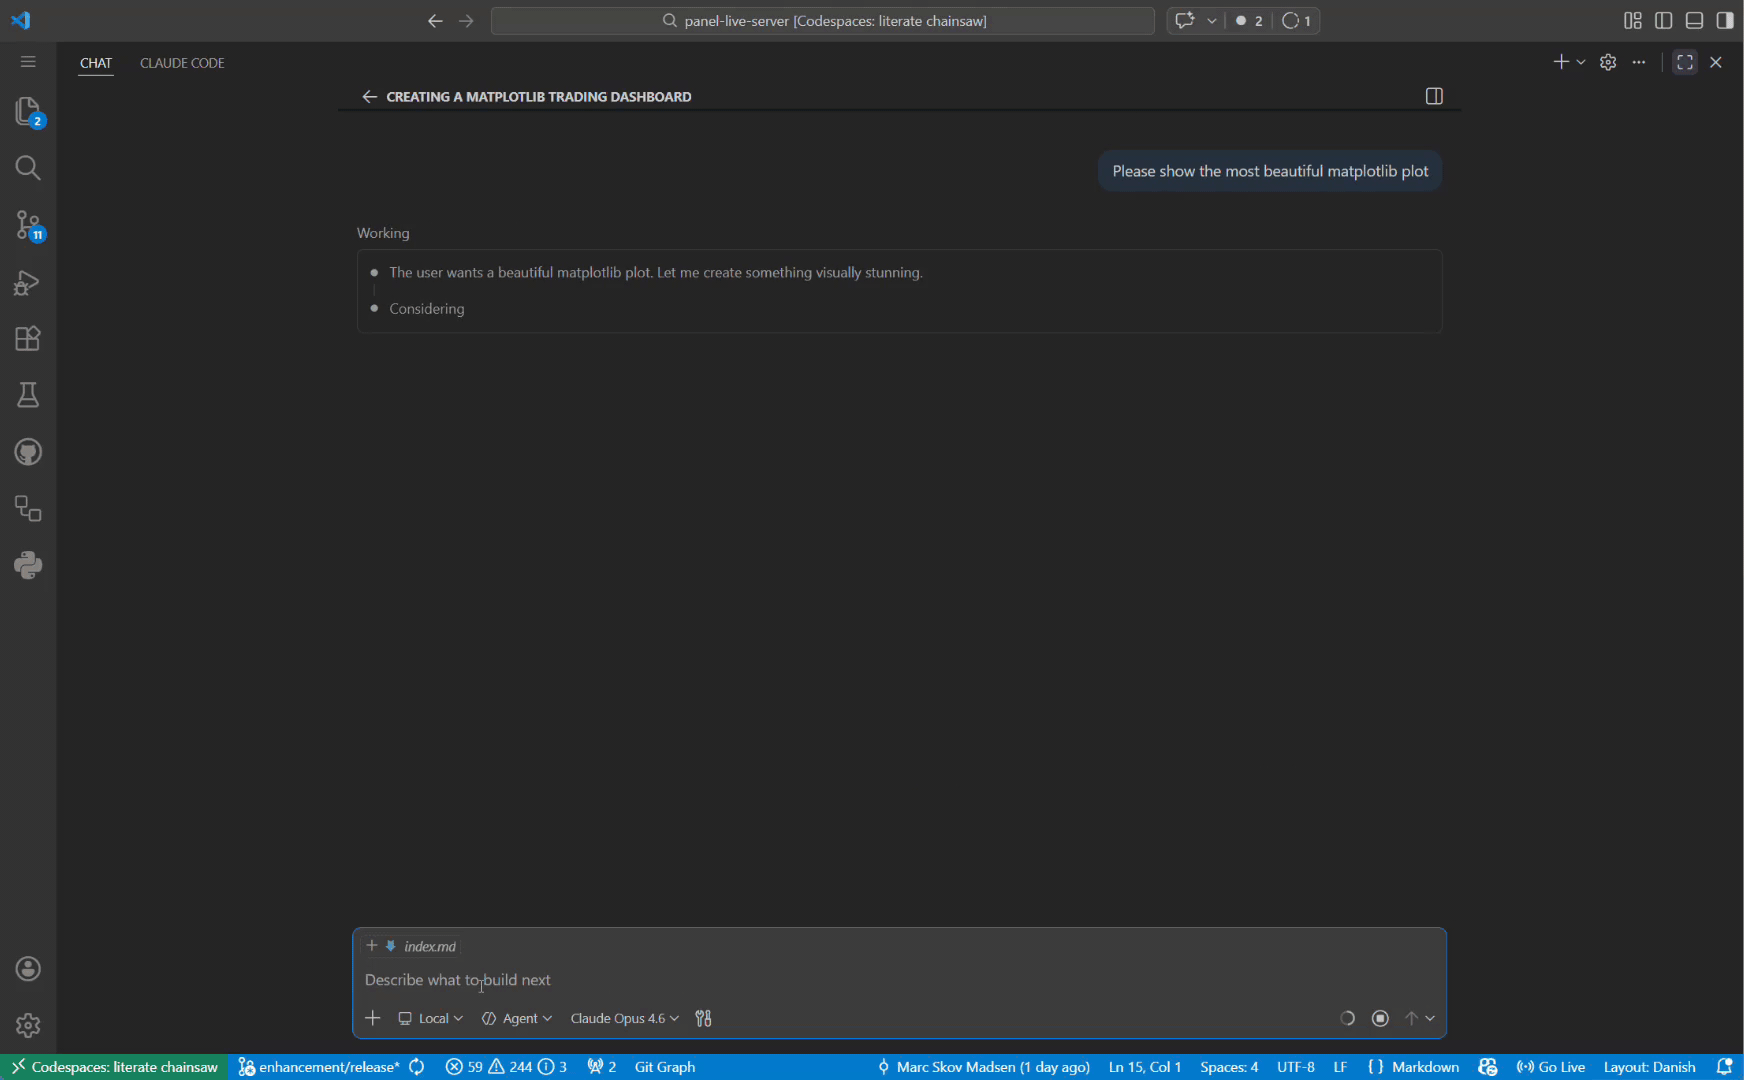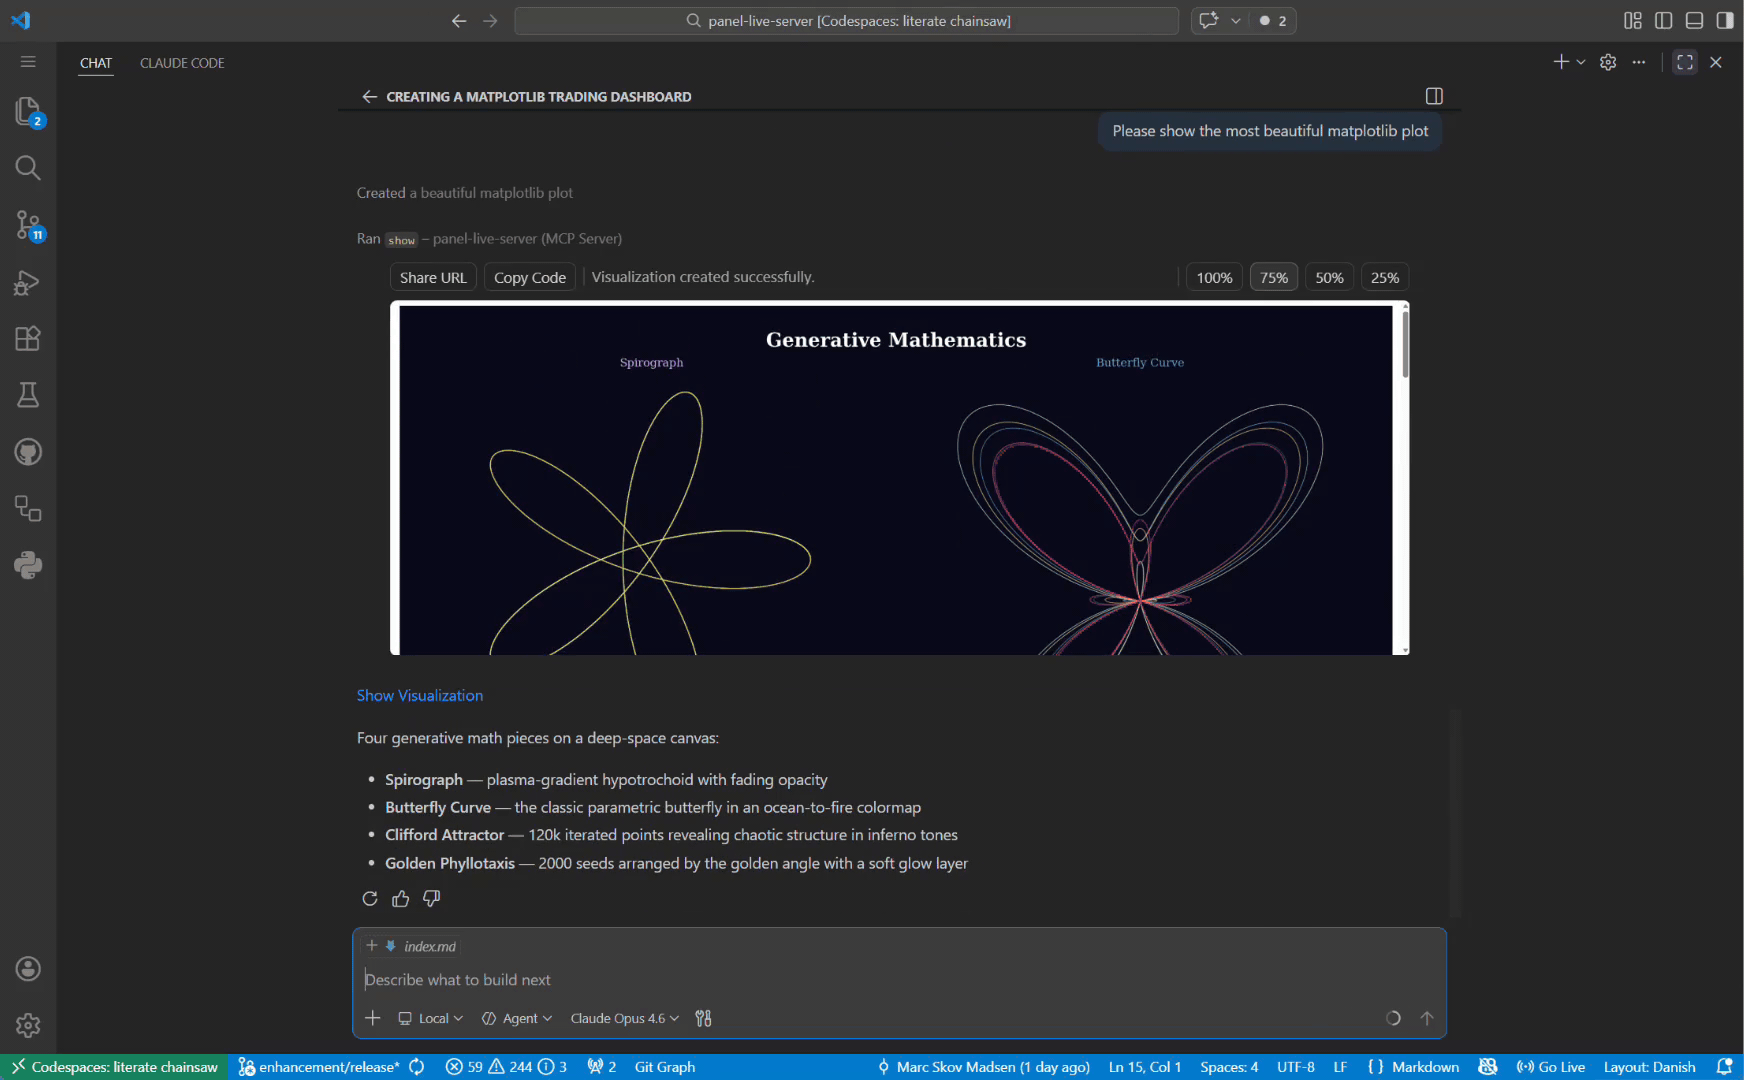
Panel Live Server is a local Panel web server and MCP server that executes Python code snippets and renders the resulting visualizations as live, interactive web pages — enabling humans and AI assistants to display and inspect Python outputs in real time.
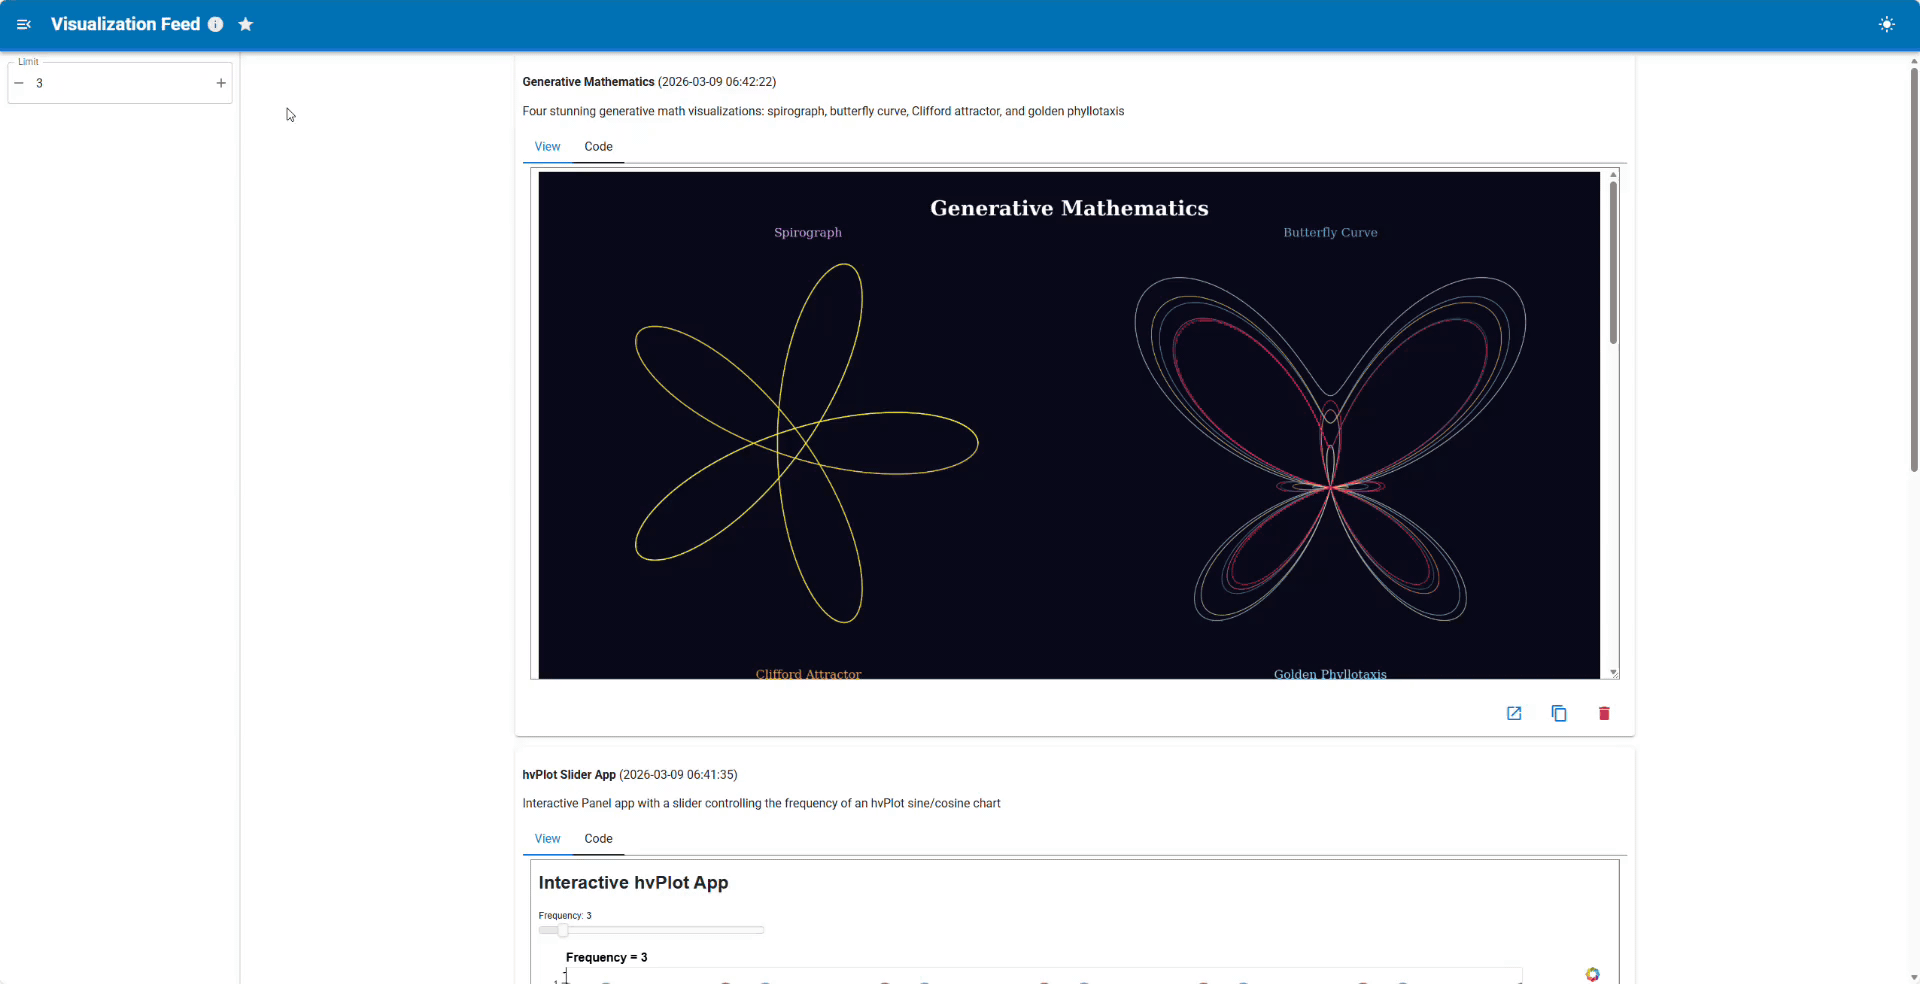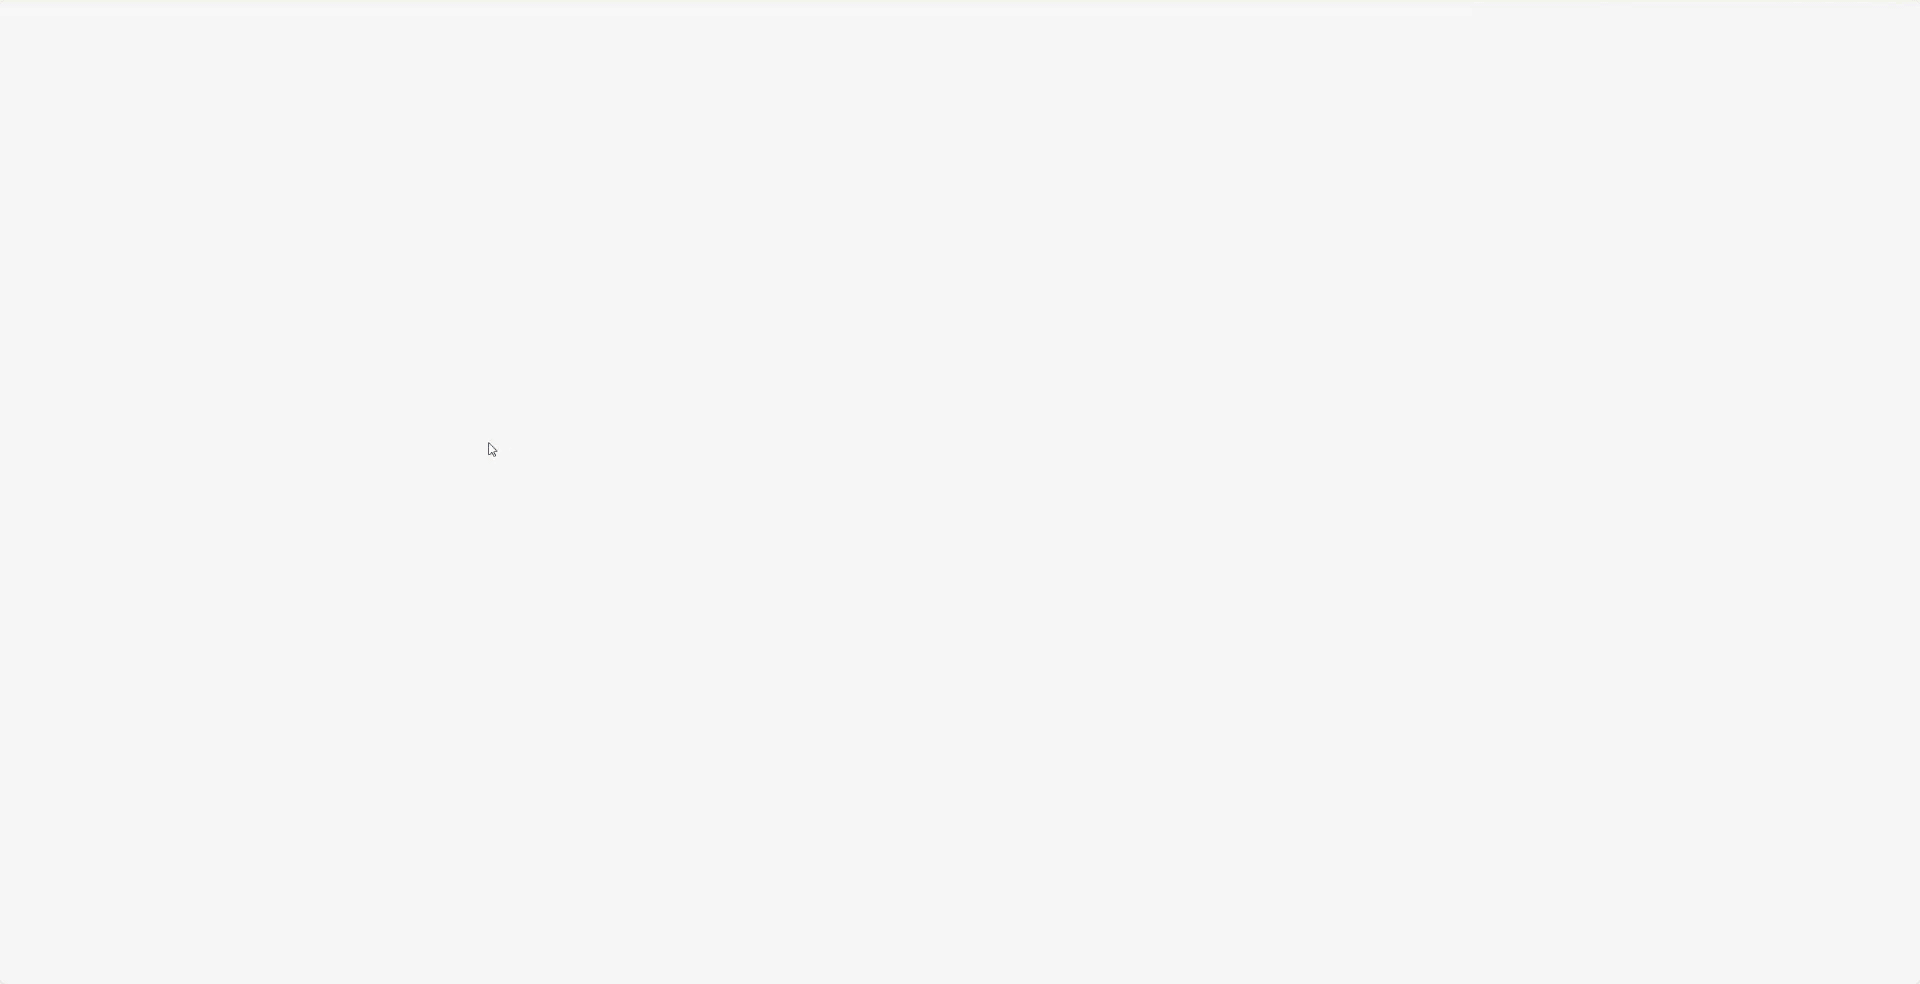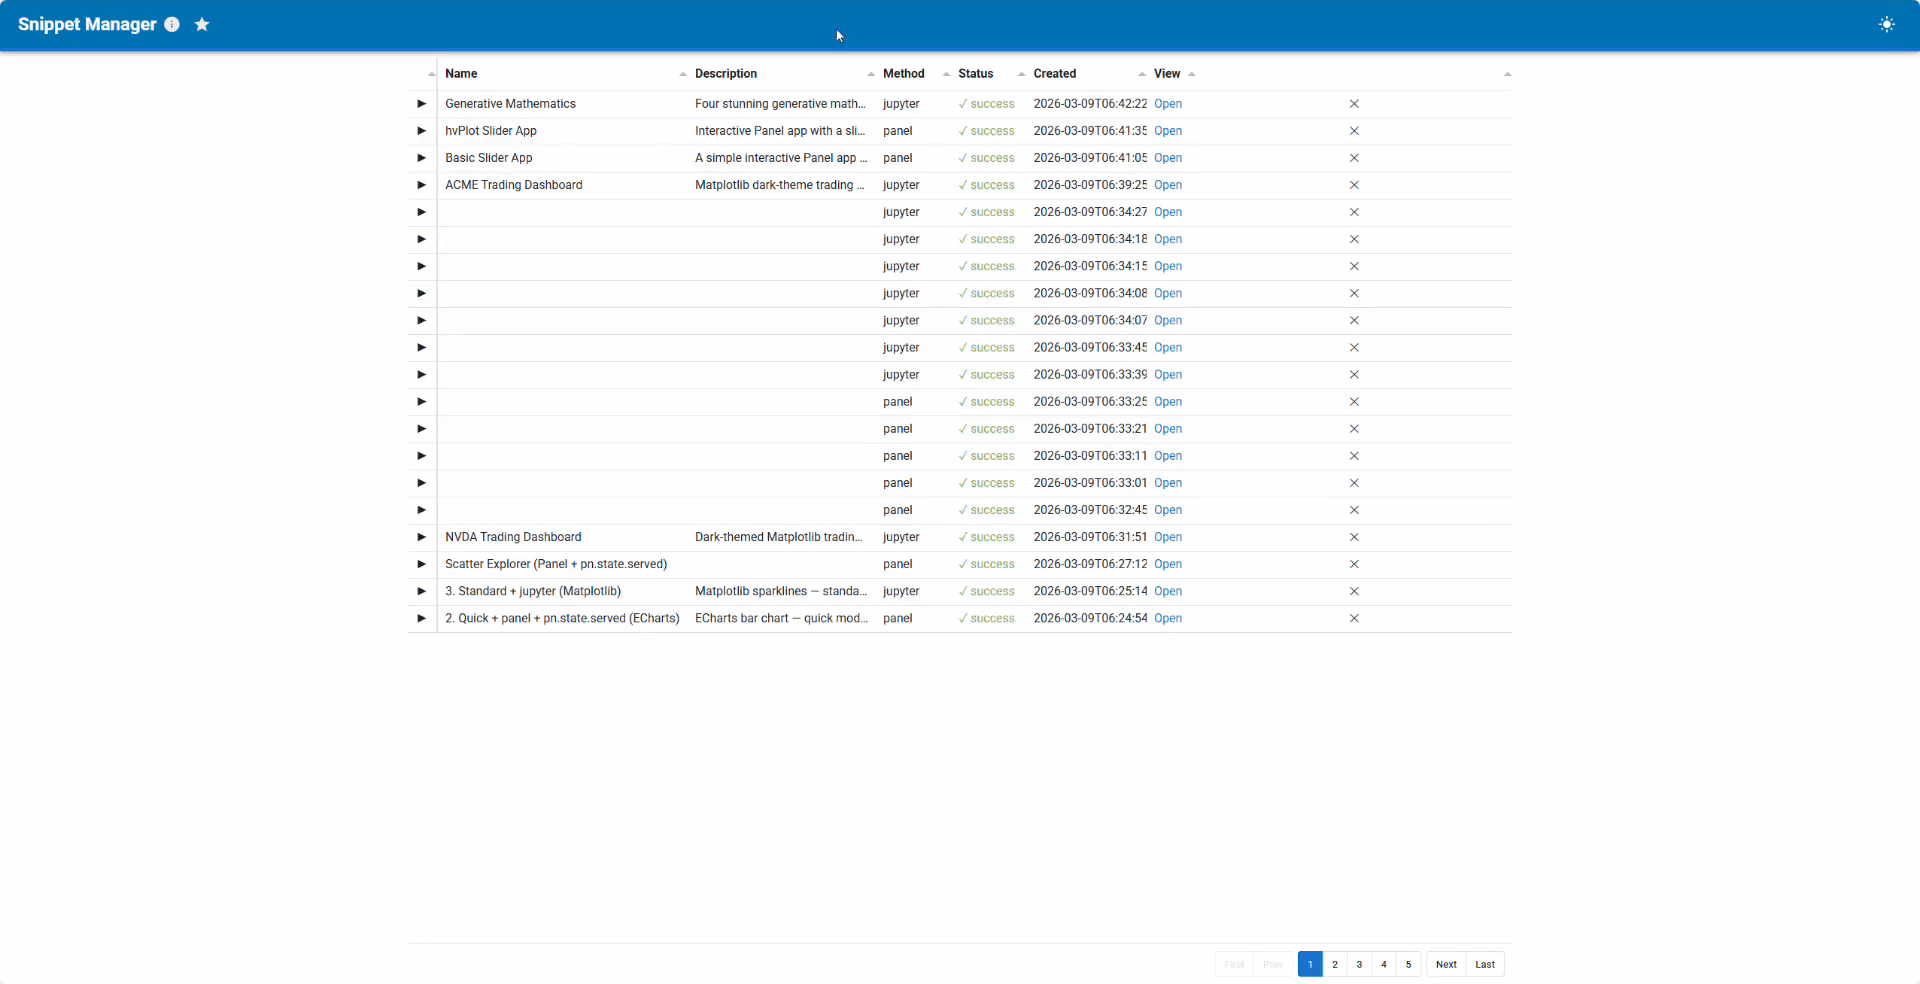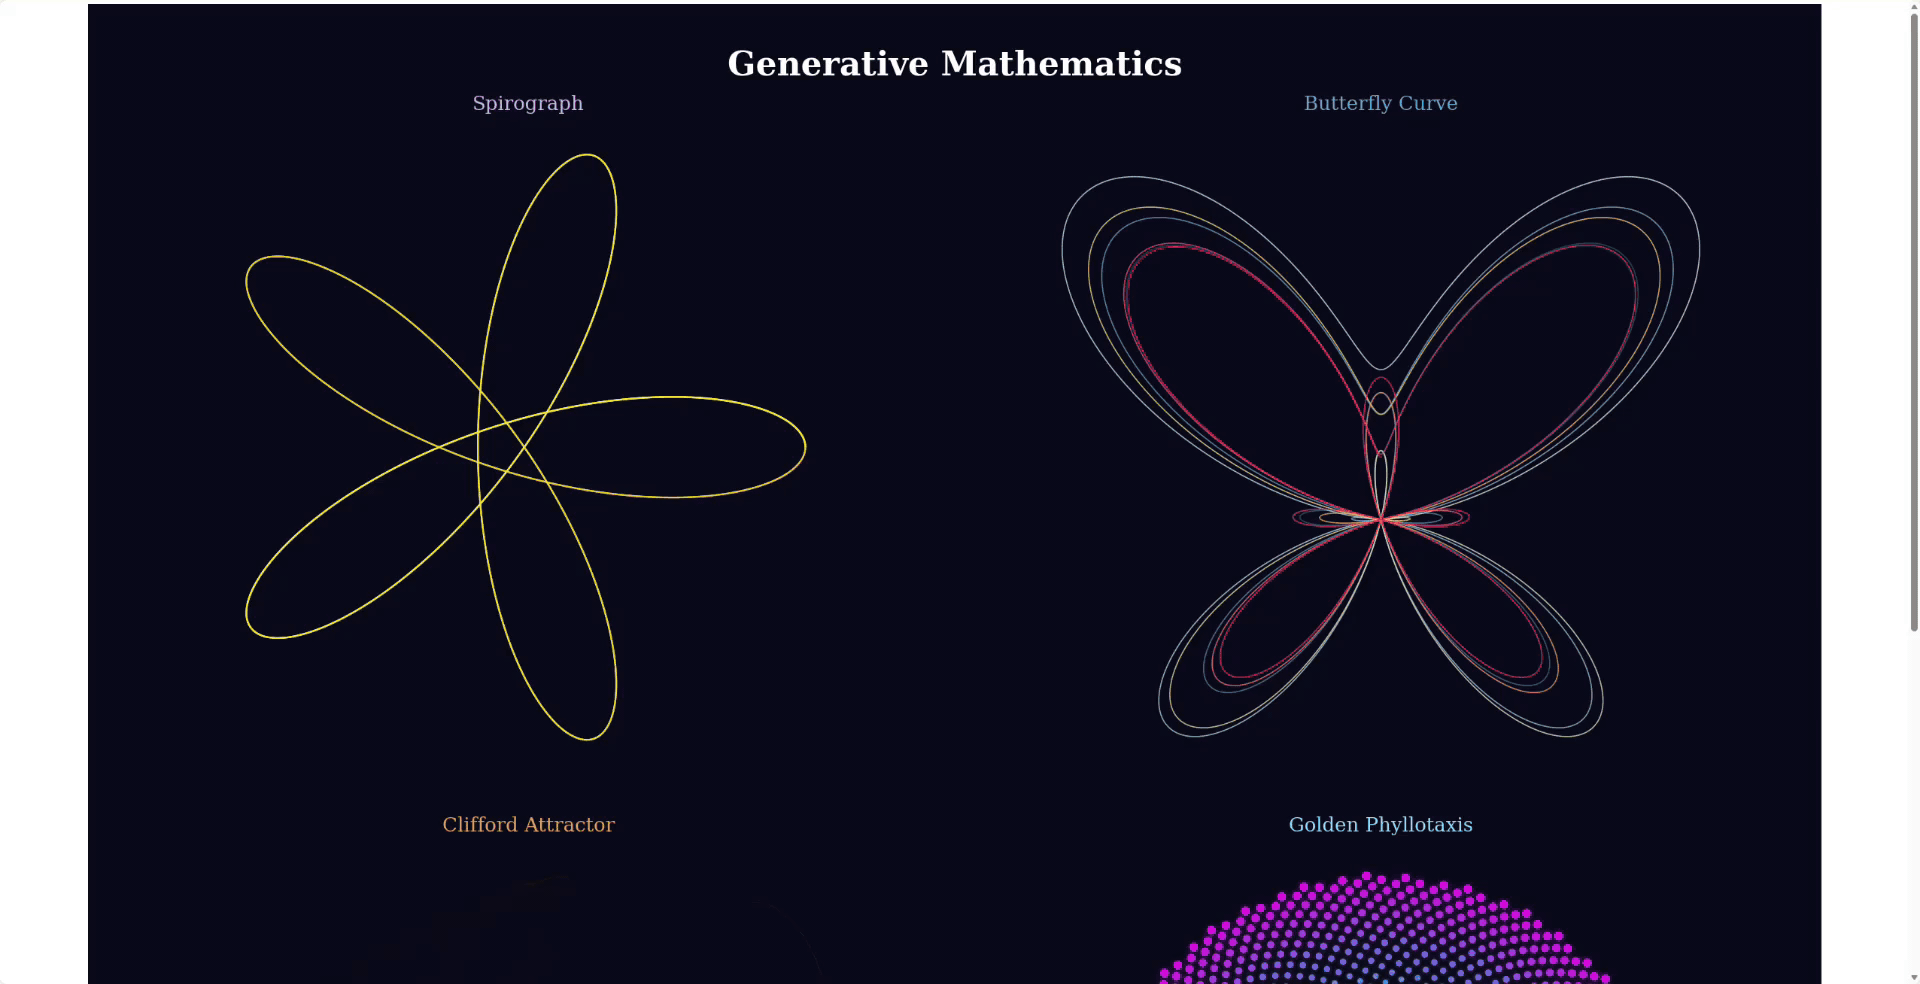
Features
- Two interfaces —
pls serve(standalone browser UI) andpls mcp(MCP server for AI assistants) - Any visualization library — hvplot · plotly · altair · matplotlib · seaborn · holoviews · bokeh · and more
- Validate before render —
showruns syntax, security, package, and extension checks before any rendering happens - Visual validation —
screenshotMCP tool lets the AI inspect the rendered output visually before presenting it, and returns the snippet's stdout plus any browser console errors alongside the image - Read a value, skip the picture —
evaluateMCP tool runs code in the server environment and returns its text output, so the AI can check a fact without launching a browser - Persistent storage — SQLite database with full-text search; every snippet gets its own permanent URL
- Auto-restart — Panel subprocess is health-monitored and automatically restarted on failure
- Works everywhere — local, JupyterHub, GitHub Codespaces; URLs externalized automatically
Installation
Install via uv, pip, or pixi — see the Installation guide for full instructions including how to find your pls path.
uv tool install "panel-live-server[pydata]"
Pin your version — this project is in its early stages. Pin to a specific version to avoid unexpected changes:
uv tool install "panel-live-server[pydata]==0.1.0a1"
Connect to your AI assistant
Use the absolute path printed by which pls above — not just pls.
Full setup instructions for each client: docs → Connect to your MCP client
| Client | Config location |
|---|---|
| VS Code | .vscode/mcp.json |
| Cursor | ~/.cursor/mcp.json |
| Claude Desktop | claude_desktop_config.json |
| Claude Code | claude mcp add panel-live-server -- /path/to/pls mcp |
| claude.ai | HTTP transport + tunnel — see docs |
Usage
$ pls

 Usage: pls [OPTIONS] COMMAND [ARGS]...

 Panel Live Server - Execute and visualize Python code snippets.

╭─ Options ────────────────────────────────────────────────────────────────────────────────────────────╮
│ --version  -V        Show version and exit.                                                          │
│ --help               Show this message and exit.                                                     │
╰──────────────────────────────────────────────────────────────────────────────────────────────────────╯
╭─ Commands ───────────────────────────────────────────────────────────────────────────────────────────╮
│ serve   Start the Panel Live Server directly.                                                        │
│ mcp     Start as an MCP server for AI assistants.                                                    │
│ status  Check whether the Panel server is running.                                                   │
│ list    List resources (packages, etc.).                                                             │
╰──────────────────────────────────────────────────────────────────────────────────────────────────────╯
You can also use panel-live-server but pls is shorter and easier to remember.
Security
Panel Live Server executes arbitrary Python. That is its purpose — show, screenshot,
and evaluate all run code you or an AI assistant supplied, in the Panel server process, with
the full privileges of the user who started it. It can read and write your files and reach the
network exactly as any script you ran yourself could.
The validation show performs — syntax, a blocked-import list, ruff's security rules, package
availability — is a guardrail, not a sandbox. It catches the plausible mistakes an assistant
makes and refuses obviously inappropriate imports. It is not a security boundary and cannot be
relied on as one.
So:
- Run
plsonly in an environment you would be willing to run arbitrary code in. - Don't expose the server's port to an untrusted network. It has no authentication; anyone who
can reach
/api/snippetor/api/evaluatecan execute code in that environment. - Treat a shared or production machine as the wrong place for it.
Development
See the Contributing guide for the full setup (fork, install, connect to MCP client, run tests).
❤️ Contributing
Contributions are welcome! Please follow these steps:
- Fork the repository.
- Create a new branch:
git checkout -b feature/YourFeature. - Make your changes and commit them:
git commit -m 'Add some feature'. - Push to the branch:
git push origin feature/YourFeature. - Open a pull request.
Please ensure your code passes all tests and linting before submitting.
1 maintainer

Metadata
1 maintainer
Release files for panel-live-server 0.5.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| panel_live_server-0.5.0.tar.gz | 19.9 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| panel_live_server-0.5.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 20.0 MB
Release files / panel_live_server-0.5.0.tar.gz
| Download URL | panel_live_server-0.5.0.tar.gz |
|---|---|
| Size | 19.9 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
4a82e32485aa22ac04dbfeca07d54d471a0de5a3a3a241f90d50f15acda833ed
|
|
BLAKE2b-256 checksum How to use checksums |
b9771872345473c91c43e8c7183558ecd1a787d5be3e13ffbbe9b3bdac07b2eb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 19, 2026.
Transparency logRelease files / panel_live_server-0.5.0-py3-none-any.whl
| Download URL | panel_live_server-0.5.0-py3-none-any.whl |
|---|---|
| Size | 113.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
7bf1857f87dcfcd3ef600fbcf59bbc1cbf9094a8dcd3f79fc85584ab77e8e9e7
|
|
BLAKE2b-256 checksum How to use checksums |
b028980b065f2288c0c44d4c4703f5f1eb3a32f1f5ed04c9f91d7a238596f9c0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 19, 2026.
Transparency log













