
PolicyAware AI Gateway & Agent Control Plane
PyPI: policyaware | Downloads: Pepy stats | Python: 3.10+ | License: Apache-2.0 | Docs: GitHub Pages
PolicyAware adds deny-by-default policy, PII redaction, MCP tool governance, model routing, runtime evaluation, local code scanning, and audit traces to LLM, RAG, and AI agent applications in minutes.
PolicyAware is an open-source AI control plane and security gateway for governed LLM applications, RAG pipelines, MCP-style tools, and autonomous AI agents. Distributed as a lightweight Python package (pip install policyaware), it helps teams inspect prompts, request context, tool calls, model routing decisions, outputs, local code, and audit traces before AI workflows move into production.
Unlike basic content filters that only check text strings, PolicyAware provides policy-aware governance across requests, tools, models, evaluations, and local code scans.
Deployment model: PolicyAware is an adoption-ready open-source framework that teams embed and operate inside their own AI applications, platforms, and CI workflows. It keeps the base install lightweight with native rules-based governance, and uses optional integrations such as Presidio, ProtectAI/Transformers, NeMo Guardrails, Guardrails AI, Haystack, and provider adapters when teams need deeper detection or ecosystem-specific behavior.
Documentation site: https://ktirupati.github.io/policyaware/
Capability docs: docs/capabilities.md
Branding: standard PolicyAware icon and positioning
Coding-agent integrations: Codex, Antigravity, Claude Code, Cursor, and Windsurf workflow packs
Use-case guides: AI firewall, MCP tool gateway, policy-as-code, centralized policy distribution, PII redaction, token budgets, and OpenTelemetry audit logging
Ready-to-use YAML policies: docs/capabilities/ready-to-use-yaml.md
Comparison guide: PolicyAware vs guardrails vs AI gateway vs model router
Why PolicyAware: short positioning and trust-first category fit
Alternatives guide: PolicyAware alternatives for guardrails, AI gateways, model routers, and MCP governance
Usage modes: Gateway vs callbacks vs tool governance vs scan
Enterprise readiness: enterprise AI governance checklist
Limitations: current scope and production validation notes
Security model: deny-by-default and layered AI governance
Security boundaries: SDK mode vs sidecar/gateway enforcement
Examples matrix: choose the right runnable example
Compatibility: Python, providers, extras, and integration status
Integrations strategy: official vs compatible integrations
Benchmarks: lightweight governance benchmarks
Production checklist: deployment validation steps for governed AI workflows
Release notes: PolicyAware 0.4.7 highlights
GitHub release draft: copy-paste v0.4.7 release body
Policy packs: healthcare, finance, EU AI Act, and SOC 2 starter policies
HTTP sidecar: use PolicyAware from Node.js, Go, Java, Rust, and other services
Dynamic policy distribution: central HTTP, S3, GCS, and ADLS policy sources with refresh, cache, and emergency revoke patterns
Stateful session governance: detect cumulative leakage and repeated tool activity across a session
Enterprise hardening: SQLite session state, emergency revokes, checksum pinning, and signed audit traces
Policy rollout and trace correlation: shadow policy evaluation, canary enforcement, parent traces, and dashboard
Observability templates: Grafana, Prometheus, and OpenTelemetry examples
Performance and visual simulation: fast-core boundary, semantic telemetry, and simulator reports
Enterprise attestation and test harness: confidential-computing patterns, ecosystem certification, and deterministic policy stress tests
Official GitHub Action: ktirupati/policyaware-action for PolicyAware pull-request scans, annotations, SARIF, and report artifacts
Policy contract checks: prevent YAML/tool drift in CI
MCP filesystem tutorial: secure an MCP filesystem server with PolicyAware
Policy composition: hierarchical global, compliance, tenant, app, and local overrides
Adaptive governance: policy suggestion, synthetic redaction, safe rewrite, plan preflight, and shadow AI scan signals
Enterprise structural layers: jury consensus, retrieval-hook defense, tamper-evident audit chains, and budget circuit breakers
Edge and policy intelligence: air-gapped readiness, cross-framework policy translation, drift canaries, and fairness monitoring
Runnable contract example: examples/policy-contract-checks
Demo outputs: captured terminal output for runnable examples
Changelog: release history
Coding-Agent Integration Packs
PolicyAware includes lightweight workflow packs for coding-agent tools. These packs help agents scan repositories, create policyaware.yaml, add CI scan workflows, explain findings, and recommend the right PolicyAware integration path.
| Tool | Integration Pack |
|---|---|
| Codex | integrations/codex |
| Antigravity | integrations/antigravity |
| Claude Code | integrations/claude |
| Cursor | integrations/cursor |
| Windsurf | integrations/windsurf |
Search-Friendly Use Cases
| Developer Search | Start Here |
|---|---|
| AI firewall for LLM agents | AI Firewall For LLM Agents |
| Intercept MCP tools in Python | MCP Tool Permission Gateway |
| Policy-as-code for LLMs | Policy-As-Code For LLMs |
| Centralized YAML policy distribution with S3, GCS, ADLS, or HTTP | Centralized AI Policy Distribution |
| Redact PII and secrets before a prompt leaves infrastructure | PII Redaction Before LLM Calls |
| Python LLM token budget and rate limiting | LLM Token Budget And Cost Controls |
| OpenTelemetry hooks for blocked AI actions | LLM Audit Logging And OpenTelemetry |
Enterprise Core Capabilities
1. Agent Control Plane And MCP Governance
- Action-level tool governance: Evaluates connector names, action names, arguments, user role, tenant, region, and approval requirements before agent tools execute.
- Deny-by-default tool shielding: Supports MCP-style tool policies that block unauthorized or destructive actions unless explicitly allowed.
2. Multi-Engine Security And Guardrail Orchestration
- Unified governance pipeline: Combines data protection, YAML policy enforcement, risk classification, model routing, guardrail adapters, evaluation, and audit logging in one modular Python framework.
- Optional security integrations: Supports optional integrations such as Microsoft Presidio for stronger PII detection, ProtectAI/Transformers-based classifiers for ML signals, NVIDIA NeMo Guardrails, and Guardrails AI adapters.
3. Cost-Aware Runtime Routing And FinOps Controls
- Policy-based model routing: Routes requests across local and external model providers based on task type, risk level, region, provider availability, cost, quality, and policy constraints.
- Token and budget controls: Supports token, budget, and risk-aware limits to help reduce runaway agent loops and uncontrolled model usage.
4. Observability, Audit, And Local Code Scanning
- Audit-ready traces: Records structured policy decisions, risk tiers, reason codes, model choices, evaluation scores, token estimates, and request/response snapshots.
- Observability exporters: Provides live sidecar
/metrics, Prometheus-style metrics, OpenTelemetry-shaped events, and audit-trace exports for monitoring and compliance workflows. - Performance and policy debugging: Provides lightweight runtime diagnostics, reproducible local benchmarks, semantic governance metrics, and a visual policy simulator for explaining blocked or mutated agent actions.
- Deterministic policy test harness: Runs seeded concurrent policy stress tests, including 10,000-request CI checks, to catch YAML regressions and thread-safety issues before production.
- Structured rejection handshakes: Returns canonical blocked-action payloads with decision, reason codes, matched rules, trace IDs, remediation, and telemetry fields so API wrappers do not swallow governance context.
- Fail-closed security posture: Treats untrusted policy state, validation failures, checksum mismatches, unavailable remote policy sources, and validator errors as blocked or approval-required conditions instead of implicit allow.
- Dynamic policy retry protection: Applies strict fetch timeouts, refresh TTLs, exponential backoff, jitter, last known-good cache, and emergency fallback policies for central HTTP/S3/GCS/ADLS policy sources.
- Offline AI governance linter:
policyaware scanruns locally or in CI before deployment to find PII/PHI/secrets, direct LLM calls, unmapped MCP tools, missing tool governance, weak routing controls, audit gaps, and policy YAML issues. GitHub Actions can block pull requests before unvetted AI tools or prompts reach production. - Adaptive governance helpers: Generate starter policies from scan findings, use synthetic redaction to preserve prompt utility, return auditable safe-rewrite state patches, preflight multi-step agent plans, and detect shadow-AI patterns such as dynamic installs or runtime tool registration.
- Enterprise structural layers: Use jury consensus for high-risk decisions, sanitize retrieved RAG context before prompt assembly, verify tamper-evident audit chains, and pause runaway agent sessions with token, cost, and tool-rate circuit breakers.
- Edge and policy intelligence: Validate air-gapped local deployment, translate one policy across orchestrators, run drift canaries, and monitor fairness distributions for decisioning agents.
- First-class MCP isolation: Intercept MCP JSON-RPC
tools/callrequests, evaluate connector/action policy, redact sensitive arguments, and return structured JSON-RPC errors before MCP servers touch the host. - Framework callbacks: Includes lightweight LangChain and LlamaIndex callback handlers that aggregate streamed tokens and report policy, risk, leakage, eval, and token-accounting results.
- LangGraph node guard: Adds dependency-free node/state and tool-call governance for graph-based AI agents.
- Haystack governance components: Adds optional Haystack-style components for RAG query governance, output evaluation, and agent tool permission checks.
- Microsoft AGT-style evidence export: Converts PolicyAware policy, tool, gateway, and audit decisions into dependency-free evidence JSON for enterprise agent governance workflows.
- Smart integration recommender: Inspects project signals and user hints to recommend FastAPI, LangChain, LangGraph, Haystack, MCP/tool governance, privacy, guardrails, routing, audit, or scan entry points with reasons.
- Policy packs and sidecar mode: Includes compliance-oriented starter policy packs and a lightweight HTTP sidecar so non-Python services can call PolicyAware.
- Policy/code contract checks: Detects drift between tool-governance YAML and Python tool function signatures before production.
Runtime Flow Summary
flowchart LR
    A["AI App / RAG Pipeline / Agent"] --> B["PolicyAware SDK / CLI / Middleware / Callback"]
    B --> C["Data Protection"]
    C --> D["Risk Classification"]
    D --> E["Policy Decision"]
    E -->|deny| F["Stop"]
    E -->|approval| G["Human Approval"]
    E -->|allow| H["Model Routing"]
    E --> J["MCP Tool Governance"]
    H --> I["Model Provider"]
    J --> K["Tool / Connector"]
    I --> L["Runtime Evaluation"]
    K --> L
    L --> M["Audit Trace / Evidence"]
Read more: Architecture
Which Entry Point Should I Use?
| Need | Use |
|---|---|
| Full model request control, routing, eval, and audit | Gateway.chat(...) |
| Existing LangChain or LlamaIndex pipeline telemetry | PolicyAwareCallbackHandler |
| LangGraph node/state governance | PolicyAwareNodeGuard |
| MCP-style connector/action permissions | ToolPolicyEngine |
| Pre-deployment code governance scan | policyaware scan ./app |
| Microsoft AGT-style evidence export | to_agt_tool_evidence(...) |
| Find the best integration for a project | policyaware integrations recommend . |
| Copy a compliance-oriented starter policy | policyaware policy packs copy healthcare-hipaa --out policyaware.yaml |
| Compose global, compliance, app, and local policies | policyaware policy compose policy-stack.yaml |
| GitHub pull-request scan gate | ktirupati/policyaware-action@v1 |
| Use PolicyAware from non-Python services | policyaware up --policy policyaware.yaml --port 8080 |
| Prevent YAML/tool contract drift | policyaware contract check ./src --policy tool-governance.yaml |
| Generate a starter policy from scan signals | policyaware policy suggest . --out policyaware.generated.yaml |
| Preflight a multi-step agent plan | policyaware plan check plan.yaml |
| Preserve prompt utility while replacing sensitive values | policyaware protect synthesize "Email jane@example.com" |
| Run high-risk jury consensus | policyaware consensus check "transfer funds for jane@example.com" --risk high |
| Sanitize retrieved RAG context | policyaware retrieval sanitize retrieved-context.txt --out safe-context.txt |
| Check cost/token circuit breakers | policyaware budget check --cost-usd 10 --max-cost-usd 5 |
| Verify tamper-evident audit chain | policyaware audit verify-chain .policyaware/traces.jsonl |
| Check raw MCP JSON-RPC tool calls | policyaware mcp check examples/policies/tool-governance.yaml mcp-request.json |
| Run a live MCP stdio policy proxy | policyaware mcp proxy policyaware.yaml --connector filesystem --server-command "python filesystem_mcp_server.py" |
| Check air-gapped deployment readiness | policyaware airgap check --policy policyaware.yaml --model local |
| Translate one policy across frameworks | policyaware translate policy policyaware.yaml --frameworks langchain,llamaindex,autogen,raw |
| Run drift canaries | policyaware drift canary canaries.yaml --threshold 0.1 |
| Check fairness distribution | policyaware fairness check decisions.jsonl --attribute group --positive-outcomes approved |
| Simple PII/PHI/secrets string check | DataProtectionEngine.inspect(...) |
| YAML policy unit testing | PolicyEngine.decide(...) |
Read more: Usage Modes
Where PolicyAware Fits
Use Guardrails AI or NeMo Guardrails when your main goal is conversational safety, structured outputs, or model response validation.
Use an AI gateway or model router when your main goal is provider abstraction, API key handling, retries, rate limits, fallback, or cost/latency routing.
Use PolicyAware when AI requests and agent actions need governance: user/tenant/context policy, PII/PHI/secrets handling, MCP/tool permissions, approval decisions, model routing after policy approval, evaluations, and audit evidence.
Short version: use PolicyAware when AI actions need governance, not just generation.
PolicyAware is intentionally focused on AI systems. For ordinary web APIs or microservices that do not use LLMs, RAG, MCP tools, or autonomous agents, standard API security controls are usually a better first layer. For deeper ML-based detection or conversational safety, PolicyAware keeps the base install lightweight and lets teams opt into Presidio, ProtectAI/Transformers, NeMo Guardrails, Guardrails AI, Haystack, and provider extras. Runtime overhead should be benchmarked in your own request path, especially when optional ML or external guardrail engines are enabled.
Scan Report Preview
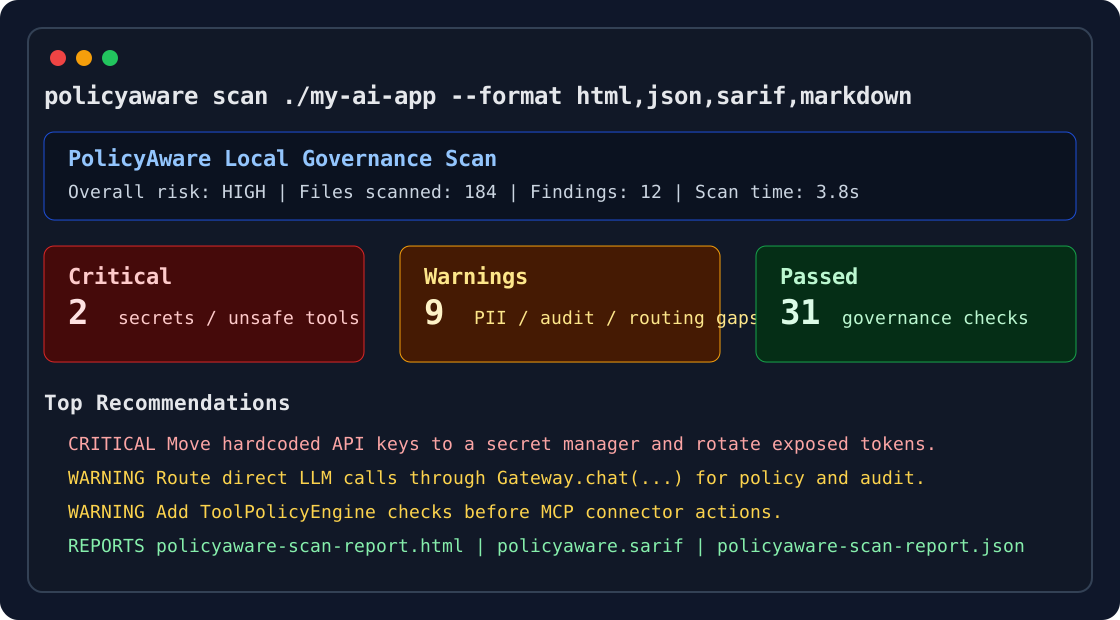
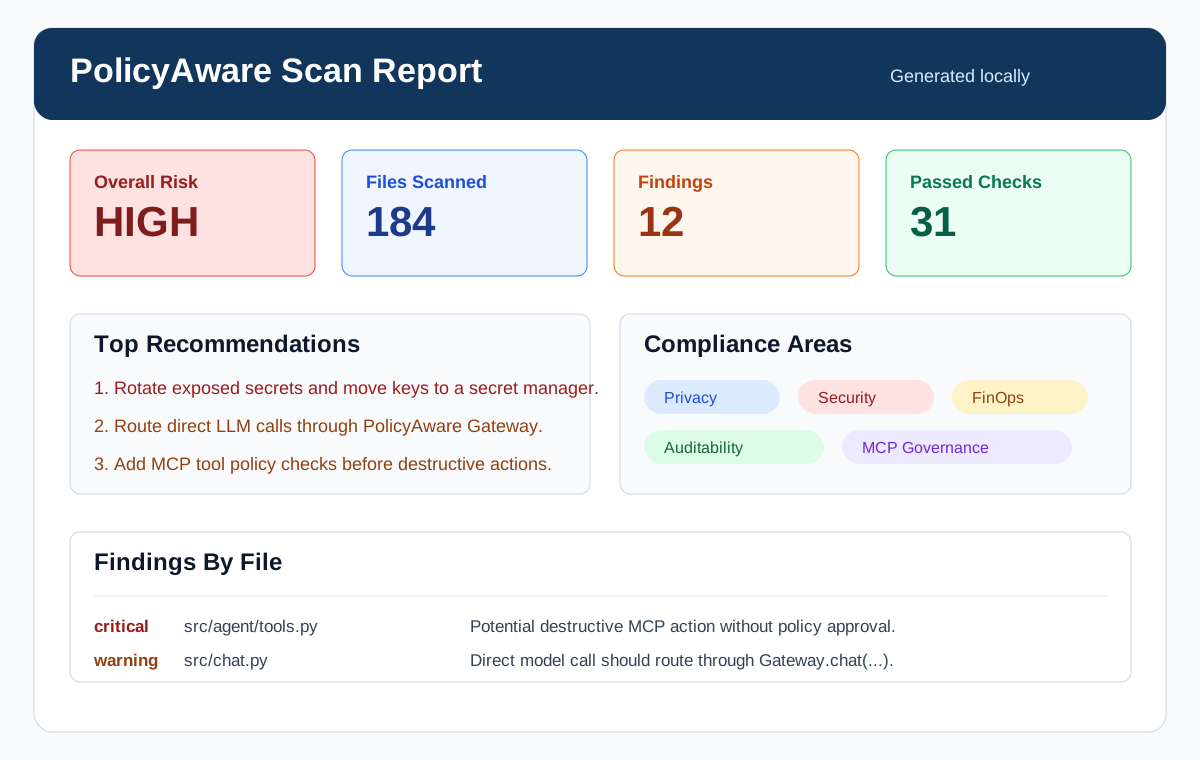
policyaware scan is one of PolicyAware's highest-utility differentiators: it works as an offline AI governance linter for repositories. Most runtime guardrails only discover policy gaps when the application executes. PolicyAware can catch structural AI governance risks during local development or CI/CD.
policyaware scan . --format html,json,sarif,markdown --fail-on high
Author
Created and maintained by Krishna Kishor Tirupati.
Project links:
- PyPI: policyaware
- GitHub: ktirupati/policyaware
- Documentation: PolicyAware AI Gateway Docs
- LinkedIn: Krishna Tirupati
Feedback And Testimonials
Using PolicyAware in a project, prototype, enterprise AI workflow, security review, or governance evaluation?
Please share feedback, use cases, feature requests, and testimonials through the channels below:
- Private structured feedback form: PolicyAware User Feedback And Testimonials
- Public discussions: GitHub Discussions
- Testimonials and user stories: Show and Tell
- Issues and bugs: GitHub Issues
Helpful feedback includes what you built, which PolicyAware feature you used, what risk or governance gap it helped identify, and what should improve next.
Please do not share secrets, private prompts, PHI, PII, customer data, or confidential internal details.
Contributing And Roadmap
PolicyAware welcomes focused contributions from developers, AI platform engineers, security engineers, and governance practitioners.
- Contributing guide: CONTRIBUTING.md
- Roadmap: ROADMAP.md
- Good first issues: GOOD_FIRST_ISSUES.md
- Security policy: SECURITY.md
- Adoption and impact tracking: ADOPTION.md
- Curated testimonials: TESTIMONIALS.md
Quick Start
pip install policyaware
policyaware about
policyaware feedback
policyaware integrations list
policyaware integrations recommend .
policyaware integrations recommend . --use-case rag --framework haystack --needs "citations pii audit"
policyaware integrations recommend . --html integration-report.html
policyaware doctor
policyaware examples list
policyaware examples copy mcp-policy-proxy-demo ./policyaware-mcp-demo
policyaware examples run langgraph-agent-governance
policyaware policy packs list
policyaware policy packs copy healthcare-hipaa --out policyaware.yaml
policyaware policy compose-check examples/policy-composition/policy-stack-safe.yaml
policyaware policy compose examples/policy-composition/policy-stack-safe.yaml --out policyaware.composed.yaml
policyaware policy suggest . --out policyaware.generated.yaml
policyaware plan check agent-plan.yaml --fail-on high
policyaware protect synthesize "Email jane@example.com or call 212-555-7890"
policyaware contract check ./src --policy tool-governance.yaml
policyaware up --policy policyaware.yaml --port 8080
policyaware up --policy-url s3://policy-configs/prod/policyaware.yaml --policy-cache .policyaware/policy-cache.yaml --fallback-policy examples/policies/emergency-fallback-deny.yaml --require-auth
policyaware init
policyaware policy validate policyaware.yaml
policyaware policy doctor policyaware.yaml
policyaware policy summarize policyaware.yaml
policyaware policy lint policyaware.yaml
policyaware policy checklist policyaware.yaml
policyaware policy normalize policyaware.yaml --out policyaware.normalized.yaml
policyaware policy diff old-policy.yaml new-policy.yaml --fail-on-relaxed
policyaware policy migrate policyaware.yaml --to 0.3 --out policyaware.v0.3.yaml
policyaware dev simulate
policyaware risk classify "Email jane@example.com about a patient diagnosis" --domain healthcare
policyaware scan ./mylocalfolder
policyaware scan ./mylocalfolder --json policyaware-scan-report.json --fail-on high
policyaware scan ./mylocalfolder --sarif policyaware.sarif
policyaware scan ./mylocalfolder --markdown policyaware-scan-report.md
policyaware scan ./mylocalfolder --baseline policyaware-baseline.json
policyaware scan ./mylocalfolder --config examples/policyaware-scan.yaml
policyaware scan ./mylocalfolder --ruleset ai-agent-security
policyaware scan ./mylocalfolder --diff --diff-base origin/main
policyaware scan ./mylocalfolder --format html,json,sarif,markdown
policyaware guards list examples/full-stack-guardrails/policy.yaml
For GitHub pull-request checks, use the official action:
- uses: actions/checkout@v4
- uses: ktirupati/policyaware-action@v1
Advanced CI/CD flows can combine the action with policyaware policy validate,
policyaware policy compose-check, policyaware policy compose,
policyaware contract check, and SARIF-producing policyaware scan commands.
Installation Profiles
The default install is intentionally lightweight. It includes the core CLI, local scanner, policy engine, routing abstractions, cost/risk governance primitives, audit/eval contracts, and YAML policy support.
pip install policyaware
Install optional integrations only when you need them:
pip install "policyaware[privacy]"     # Presidio + spaCy privacy detection
pip install "policyaware[guardrails]"  # NeMo Guardrails + Guardrails AI
pip install "policyaware[haystack]"    # Haystack RAG/agent integration environment
pip install "policyaware[providers]"   # Provider extras such as Bedrock boto3
pip install "policyaware[ml]"          # Transformers/Torch classifiers
pip install "policyaware[onnx]"        # ONNX runtime path for supported classifiers
pip install "policyaware[all]"         # All optional integrations
For production containers, install only the extras that service needs. The base package stays lightweight; privacy, ML, provider, and guardrail extras add larger third-party dependency stacks.
Backward-compatible aliases are also available:
pip install "policyaware[presidio]"
pip install "policyaware[nemo]"
pip install "policyaware[guardrails-ai]"
pip install "policyaware[full]"
For local development from this repository:
pip install -e ".[dev]"
policyaware policy test examples/policies/basic.yaml
policyaware policy validate examples/policies/basic.yaml
policyaware risk classify "Summarize this patient diagnosis" --domain healthcare
policyaware tools check examples/policies/tool-governance.yaml --agent code_assistant --connector github --action create_pr
policyaware eval run examples/evals/support_rag.yaml
policyaware scan . --out policyaware-scan-report.html
policyaware scan . --include ".py,.yaml,.json" --exclude "tests,fixtures"
policyaware scan . --write-baseline policyaware-baseline.json
policyaware scan . --config examples/policyaware-scan.yaml --format html,json,sarif,markdown
policyaware policy suggest . --out policyaware.generated.yaml
policyaware plan check agent-plan.yaml --json
policyaware protect inspect "Email jane@example.com" --json
policyaware protect redact "Email jane@example.com" --json
policyaware protect synthesize "Email jane@example.com" --json
For copy-pasteable end-to-end examples, see Working Examples.
Local code scan docs: policyaware scan
Official GitHub integration: ktirupati/policyaware-action
GitHub Action docs: PolicyAware policy CI/CD with GitHub Actions
CLI usability docs: doctor, examples, migration, recommendation reports
Microsoft AGT-style interop example: examples/microsoft-agt-interop
LangGraph governance example: examples/langgraph-agent-governance
Enterprise control-plane demo: examples/enterprise-ai-control-plane
Generate A Starter Policy
Create a NIST-aligned baseline starter policy in the current directory:
policyaware init
policyaware init --profile mcp --out mcp-policy.yaml
policyaware init --profile rag --out rag-policy.yaml
policyaware init --profile pii --out pii-policy.yaml
policyaware init --profile agent --out agent-policy.yaml
policyaware policy validate policyaware.yaml
Use a custom path or overwrite intentionally:
policyaware init --out config/policyaware.yaml
policyaware init --out policyaware.yaml --force
The generated template is deny-by-default and includes baseline rules for PII/PHI/secrets handling, risky MCP/tool command blocking, approval for side-effecting tool actions, token budget caps, and high-iteration agent workflows.
LangChain And LlamaIndex Callbacks
Use callbacks when you already have an LLM framework pipeline and want PolicyAware governance results without changing the model call.
from policyaware.integrations.langchain import PolicyAwareCallbackHandler

policyaware_callback = PolicyAwareCallbackHandler(config="policyaware.yaml")

response = chain.invoke(
    {"question": "Summarize this customer ticket."},
    config={"callbacks": [policyaware_callback]},
)

result = policyaware_callback.last_result
print(result.policy_decision.decision)
print(result.risk.tier)
print(result.output_findings.contains_sensitive)
Streaming-friendly manual example:
from policyaware.integrations.langchain import PolicyAwareCallbackHandler

handler = PolicyAwareCallbackHandler(config="policyaware.yaml")
handler.on_llm_start(prompts=["Email jane@example.com with the ticket summary."])

for token in ["Safe ", "summary ", "without ", "private ", "data."]:
    handler.on_llm_new_token(token)

result = handler.on_llm_end()
print(result.to_dict())
LlamaIndex-style callbacks are also available:
from policyaware.integrations.llamaindex import PolicyAwareCallbackHandler

handler = PolicyAwareCallbackHandler(config="policyaware.yaml")
handler.on_event_start(payload={"query_str": "Answer with citations from policy documents."})
handler.on_llm_new_token("The policy requires citation review [doc-1].")
result = handler.on_event_end(payload={})
More details: LangChain and LlamaIndex callback integrations
Copy-Paste Examples
- Zero-config OpenAI preflight: wrap a raw OpenAI client with local PolicyAware checks before the prompt leaves your app.
- FastAPI LLM policy middleware: protect a FastAPI
/chatendpoint with policy checks before model execution. - LangChain policy guardrails: wrap a chain-style LLM call with deny-by-default policy, PII redaction, and secret blocking.
- MCP tool permission gateway: govern connector-level and action-level tool permissions for agent workflows.
- MCP JSON-RPC policy proxy demo: intercept raw MCP
tools/callrequests before the server executes filesystem, Git, database, or API actions. - Haystack RAG governance: add PolicyAware query, output, and tool governance around Haystack-style RAG and agent workflows.
- PII redaction policy: inspect and redact sensitive text before model execution.
- Regulated RAG assistant: require citations and stricter controls for healthcare-style RAG.
- Provider routing by risk: route public-safe requests to low-cost models and high-risk requests to approved models.
- Audit trace viewer: write audit traces and generate a local HTML trace viewer.
- Approval workflow hooks: send high-risk requests to approval instead of calling a model.
- Local code scan: scan local AI app code and generate an HTML governance report.
- Full-stack guardrails: orchestrate NeMo Guardrails, Guardrails AI, or custom validators as input/output guards.
Zero-config raw OpenAI preflight:
import policyaware
from openai import OpenAI

gateway = policyaware.Gateway.from_policy_file("policy.yaml")
client = OpenAI()
user_context = {"user_role": "billing_admin", "session_id": "99x-delta", "risk": "low"}
safe_prompt, token_meta = gateway.inspect_and_mutate(
    prompt="Email jane@example.com about claim ACME-42.",
    context=user_context,
    app="zero-config",
)
print(token_meta["decision"], token_meta["actions"])
response = client.responses.create(model="gpt-4.1-mini", input=safe_prompt)
print(response.output_text)
inspect_and_mutate(...) fails closed with PermissionError for denied or approval-required requests, returns redacted prompt text when policy applies a redact transform, and emits audit/telemetry metadata through the normal PolicyAware runtime path.
Captured terminal output for the runnable examples is available in docs/demo-outputs.md.
Articles
- PolicyAware vs Guardrails vs AI Gateways vs Model Routers
- Build a Policy-Aware AI Gateway in Python
- Stop Shipping AI Features Without Guardrails
from policyaware import Gateway, GatewayRequest

gateway = Gateway.from_policy_file("examples/policies/basic.yaml")

response = gateway.chat(
    GatewayRequest(
        tenant="acme",
        app="claims-assistant",
        user={"id": "u_123", "role": "claims_adjuster"},
        context={"region": "us", "task_type": "summarization", "risk": "low"},
        messages=[{"role": "user", "content": "Summarize claim ACME-42."}],
    )
)

print(response.content)
print(response.policy.decision)
print(response.policy.reason_codes)
print(response.trace_id)
Architecture
Application / Agent / RAG App
        |
        v
PolicyAware SDK / Middleware
        |
        v
Identity + Context Resolver
        |
        v
Policy Decision Engine -> Data Protection Engine -> Model Router -> Provider/Tool
        |
        v
Runtime Evaluation -> Audit Trace -> Response
Repository Layout
src/policyaware/
  audit.py              Request traces and audit export records
  cli.py                policyaware CLI
  data_protection.py    PII/PHI/secret detection and redaction
  evals.py              Offline and runtime evaluation primitives
  gateway.py            Main SDK facade
  models.py             Core typed contracts
  policy.py             Deny-by-default policy engine
  providers.py          Provider abstraction and local simulated provider
  routing.py            Policy-aware model routing
  integrations/         FastAPI, Flask, LangChain, LlamaIndex shims
examples/
  policies/
  evals/
tests/
Policy Example
id: basic_enterprise_policy
default: deny

rules:
  - name: allow_low_risk_support
    effect: allow
    when:
      user.role_in: ["support_agent", "claims_adjuster"]
      request.risk_in: ["low", "medium"]
      data.contains_secrets: false

  - name: redact_pii_for_non_privileged_users
    effect: transform
    action: redact
    when:
      data.contains_pii: true
      user.role_not_in: ["privacy_admin", "compliance_officer"]

  - name: require_approval_for_high_risk
    effect: require_approval
    when:
      request.risk: "high"
Development Status
This is a production-oriented open-source framework: the core extension points and executable behavior are present, while teams can connect their preferred identity systems, workflow tools, storage backends, dashboards, and enterprise review processes around it.
v0.2 MVP Capabilities
- Deterministic risk classification: low, medium, high, critical.
- Explainable policy decisions with reason codes and remediation.
- Replayable audit trace snapshots.
- Audit bundle generation.
- Tool governance policies for MCP-style connectors and actions.
- Governance-aware eval report schema.
- Provider adapters for OpenAI-compatible APIs, Azure OpenAI, Anthropic, Bedrock, Vertex AI, Ollama, and vLLM.
- Optional ML signal integrations for Presidio PII detection, ProtectAI prompt-injection detection, and custom Transformers domain/risk classifiers.
- Optional NeMo Guardrails and Guardrails AI adapters for full-stack guardrail orchestration.
- Fast local code scanner and HTML recommendation report.
- SQLite audit storage and static trace viewer.
- Prometheus text and OpenTelemetry-shaped JSON exporters.
- File and webhook approval hooks.
- Executable golden dataset policy checks.
Third-Party ML Models
Optional ML integrations may download third-party models at runtime. PolicyAware does not bundle model weights. Review and accept the license or access terms for any model you configure, especially gated Hugging Face models.
Recommended GitHub Topics
For discovery, use repository topics such as llm, ai-gateway, llm-governance, guardrails, rag, mcp, ai-agents, pii-redaction, model-routing, audit, python, and open-source.
License
Apache-2.0
1 maintainer

Release files for policyaware 0.4.7
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| policyaware-0.4.7.tar.gz | 415.6 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| policyaware-0.4.7-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 593.5 kB
Release files / policyaware-0.4.7.tar.gz
| Download URL | policyaware-0.4.7.tar.gz |
|---|---|
| Size | 415.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
2dd13e6b2751001f5ec03a2f269163023436f28167161c7139cd8d22136a4b59
|
|
BLAKE2b-256 checksum How to use checksums |
0d8fb0ab1ce2b297c7d4ec5d37edffc765b8dcd794a96a18ede9216cd411a39f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 22, 2026.
Transparency logRelease files / policyaware-0.4.7-py3-none-any.whl
| Download URL | policyaware-0.4.7-py3-none-any.whl |
|---|---|
| Size | 177.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
1ba0d60cb86bbd9d772d98f5ccd0c6ff55f1129f5e816db9491704c24f5ff34a
|
|
BLAKE2b-256 checksum How to use checksums |
a1d4cae58afb6a6d0c582a2e02e0336cb3943553b2007809f887dae6ffcd857e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 22, 2026.
Transparency log













