
pydeno
The sandbox for AI-written JavaScript: charts, graphs, 3D and rich UI libraries. Secure, fast, easy.
Let a model write code, run it in a real V8 inside an OS-sandboxed worker, and get the result back, with the tools you choose as its only way out. Plain logic? Use Monty. Real JavaScript libraries? Use pydeno.



Quickstart · Code mode for agents · Security · Speed · How it compares · Docs · Security policy
Agents increasingly answer by writing code: a data transform, a chart, a loop that calls your tools in
parallel instead of one JSON call at a time. That code is untrusted by construction. pydeno runs it behind a
boundary that holds even if the code is hostile, and gives it exactly the tools you pass in.
from pydeno import Pydeno

with Pydeno() as pool, pool.checkout() as session:        # OS sandbox required, limits on, warm worker
    session.feed_run("const prices = {A1: 3.5}")
    session.feed_run("prices[sku] * await rate()",         # 7.0: state persists between feeds
                     inputs={"sku": "A1"}, external_lookup={"rate": lambda: 2})
    session.feed_run("new Array(2 ** 32 - 1).fill(0)")     # PydenoCrashedError. Your process is fine.
If you know Monty, you already know Pydeno: the same Pydeno / checkout / feed_run /
feed_start / dump shape, for JavaScript. Where Monty runs a Python subset, pydeno runs real, modern
JavaScript (V8, the engine behind Chrome and Node), so model-written code behaves like JavaScript and real
libraries (Vega, ECharts, three.js, d3, pptxgenjs) run unmodified.
Which one? Use Monty by default: for plain logic it is smaller, starts in microseconds and needs no process. Reach for pydeno when the code needs the JavaScript ecosystem: rich UI, charts, graphs, 3D and documents. They also work side by side (see the comparison).
| 🤖 Built for agents | One call runs a snippet and drives your tools; pause at every tool call for approvals; dump a session to a signed journal and resume it anywhere. |
| 🔒 Secure by default | OS sandbox required (no silent downgrade), no filesystem, network, processes or environment, host errors redacted, every limit on, one worker per session. |
| ⚡ Fast by default | Pre-started workers: a session checkout takes about a tenth of a millisecond; a warm eval about 30 microseconds. |
| 🧱 Contained | A V8 abort, a hang or a memory blow-up kills a disposable worker, never your process. |
| 🧪 Attacked on purpose | Hostile-guest probes, assume-breach syscall sweeps against the real kernel, and an independent review of every change that touches the boundary. |
Quickstart
pip install pydeno # or: uv pip install pydeno (Python 3.10+, macOS or Linux)
from pydeno import Pydeno

with Pydeno() as pool:
    with pool.checkout() as session:
        session.feed_run("const x = 20")
        print(session.feed_run("x + 1"))                                                          # 21
        print(session.feed_run("await lookup(7)", external_lookup={"lookup": lambda i: i * 6}))   # 42
from pydeno import AsyncPydeno

async with AsyncPydeno() as pool:
    async with pool.checkout() as session:
        await session.feed_run("1 + 1")                                                           # 2
Defaults: sandbox="require" (pydeno.sandbox_status() explains a refusal), jitless V8, host errors redacted,
30 s per feed, 512 MiB, 1000 external calls per session, and a worker never serves two sessions. The
front-door guide maps every Monty name and limit.
One door, the same names as Monty. Pydeno and AsyncPydeno are the default path for everything; you
should not need another class to run untrusted code.
| You want | Call |
|---|---|
| A sandboxed session, warm and fast | pool.checkout(limits=...) |
| Run a snippet, state persists | session.feed_run(code, inputs=..., external_lookup=...) |
| Pause at every tool call (approvals) | session.feed_start(...), then snapshot.resume(value=...) / resume(error=...) |
| Save and continue elsewhere | session.dump(), then session.load_session(state) / load_snapshot(state, ...) (signed, replayed) |
| Bound it | limits={"max_feed_duration_secs": ..., "max_memory": ...} (safe defaults already on) |
| Sync or async | Pydeno or AsyncPydeno, same methods |
The front-door guide maps every Monty name and limit. The lower-level
classes (IsolatedRuntime, AgentSandbox, SandboxPool) stay available under
Which runtime?.
From a shell, the same sandboxed worker (command line guide):
pydeno '[1, 2, 3].map(x => x * 2)' # prints [2, 4, 6]; exit code 1 on a JavaScript error
Code mode for AI agents
Code mode lets the model write one program that calls your tools, instead of one tool call per turn. pydeno gives that program a safe place to run.
from pydeno import Pydeno

TOOLS = {"search_orders": search_orders, "get_customer": get_customer}      # your Python functions

with Pydeno() as pool, pool.checkout(limits={"max_feed_duration_secs": 10, "max_memory": 256 * 2**20}) as s:
    answer = s.feed_run(
        model_written_javascript,       # e.g. loops over orders, calls get_customer in Promise.all, aggregates
        external_lookup=TOOLS,          # the ONLY way out, with a total call budget
        print_callback=lambda stream, text: log(stream, text),
    )
- Approval flows:
feed_startreturns a snapshot at every tool call; inspectsnapshot.function_nameandsnapshot.args, thenresume(value=...)orresume(error=...).dump()it and continue in another process. - Typed declarations for your prompt: your tools become
tools.*functions with TypeScript stubs; JSON-Schema tools and a lazy tool catalog keep the prompt small even with hundreds of tools. - Agent frameworks:
JSCodeModeis the JavaScript counterpart of pydantic-ai's Monty-based code mode, and an allow-listed, SSRF-safehttp_fetchtool is included. - Results you can bound:
execute()returns anExecutionResult(stdout, stderr, result, error) with ordered, size-capped console output, so one runawayconsole.logcannot flood your logs or your context window.
A gate between the model and the sandbox
A gate sees the exact code that is about to run and can refuse it before any worker is touched. Use it to reject obvious misuse cheaply and to give the model a precise reason it can act on. The isolated worker stays the boundary.
from pydeno import GateContext, GateDenied, Pydeno, SourcePolicy, Verdict, all_of, static_gate

static = static_gate(SourcePolicy(forbid_eval=True, forbid_function=True, forbid_dynamic_import=True))

def my_check(source: str, context: GateContext) -> Verdict:     # your own policy, classifier, ...
    if "while (true)" in source:
        return Verdict(False, "Use a bounded loop.", ("unbounded-loop",))
    return Verdict(True, "")

with Pydeno(gate=all_of(static, my_check), strict_eval=True) as pool, pool.checkout() as session:
    print(session.feed_run("[1, 2, 3].map(x => x * 2)"))       # [2, 4, 6]
    try:
        session.feed_run("eval('2 + 2')")
    except GateDenied as denied:
        print(denied.top_label, "|", denied.reason)            # forbidden-eval | 1:1 [forbidden-eval] eval is not allowed here...
The gate fails closed. If it raises, times out or answers with anything but a Verdict, the run is blocked with
GateUnavailable, which is retryable. A denied call uses no budget and leaves no journal entry.
gate_check(gate, code) runs the same check in your own process. See the
gate guide, which also covers the limits of a gate.
Security
pydeno assumes the code is hostile and the engine can have bugs. Each layer assumes the one above has failed.
The threat model is in SECURITY.md; the details are in the isolation guide.
| Layer | What it does |
|---|---|
| Separate process | Empty environment, own session. A V8 abort, hang or out-of-memory kills the worker; the parent raises a typed error. |
| OS sandbox, applied before the engine exists | macOS: Seatbelt. Linux: Landlock, a private empty root (mount, network, IPC, UTS namespaces) and a seccomp-bpf filter. sandbox="require" refuses to start unless every layer applied; the worker proves its own confinement with a self-test first. |
| No privileges | A worker started as root drops to nobody with an empty capability set; no_new_privs is set. |
| Smaller engine surface | V8 runs --jitless by default. SharedArrayBuffer, Atomics, WeakRef and FinalizationRegistry are removed; there is no Deno, process or require. |
| No code from strings (opt-in) | strict_eval=True: eval and new Function throw in the guest, so a string that reaches them is never compiled. A guard for trusted code against injection, not a boundary against hostile code (that is the process and OS sandbox); it removes no engine code and does not cover WebAssembly with jitless=False. |
| Limits enforced from outside | Wall-clock deadline, CPU cap, memory ceiling, buffer cap, host-call budgets, message and console size. The parent kills a worker that breaks a limit. |
| The worker is untrusted input | Every frame goes through a strict native decoder with size, depth and node budgets. A worker that sends nonsense is killed. |
| Capability tokens, fail-closed binds | A bound function is reachable only through an unguessable token. A guest that tampers with the scope before a bind makes the bind fail, never silently do nothing. |
| Tenant separation | One worker per session, never reused; each session's tool threads are its own; thread-locals and contexts never cross sessions. |
| Signed, replayable sessions | A journal is HMAC-signed, bound to its owner and release, and replays deterministically; a restored session cannot refund a spent tool budget. |
How we check it.
- A battery of hostile-guest probes (
scripts/autoresearch/metric_security.py): poisoned prototypes, forged frames, deadline bypasses, memory bombs, state leaking between commands, console escape injection. The goal is zero, and every newly found attack class becomes a probe first. - Independent review of every change that touches the worker, wire, bridge, supervision, sandbox policy or journals. Reviews have repeatedly found real defects, including in the fixes themselves, which is why they are mandatory. The findings table, misses included, is the security report.
- Assume-breach syscall sweeps against the real kernel, a verified seccomp program, fuzzing, hostile-worker fakes, and Linux on many distros and both CPU architectures (details below).
What we do not claim. A V8 bug is contained in the worker, not prevented. V8 is a large engine we cannot
audit end to end, which is why the layers around it exist. We also cannot lock the engine down completely:
real libraries such as three.js, Vega and ECharts need much of the language, so a restriction becomes a
default only when those libraries still run (strict_eval stays opt-in for that reason). The containment is
the process and the OS sandbox, not a minimal engine; there has been no independent outside security review
yet (it is planned before 1.0, see the roadmap). The in-process Runtime is not safe for
hostile code: use Pydeno / IsolatedRuntime. Windows has no isolated worker (and is not tested; see How it was tested). For multi-tenant use, put the
whole process in a locked-down container or microVM (deployment guidance).
Found a way out? Please report it privately, as described in SECURITY.md.
Why pydeno is harder to break than most sandboxes
Running untrusted JavaScript has a long history of sandboxes that were broken. The same few design mistakes keep appearing, and each one is something pydeno was built to avoid:
| What such approaches miss | Why it gets broken | What pydeno does instead |
|---|---|---|
| One in-process barrier. The guest runs in your process behind language-level checks (wrapped objects, proxies, blocklists). | Every object, prototype and built-in that reaches the guest is a possible path back to the host. One missed object is a full escape, and new ones keep being found. | The guest never shares a process with your app. A worker with an empty environment runs under an OS sandbox applied before the JavaScript engine exists, and the parent treats everything the worker sends as untrusted input. |
| An engine isolate and nothing around it. Separate heaps in one process. | An isolate separates JavaScript objects, not the process: an engine bug, a crash, a hang or a memory bomb lands in your process. | A crash, hang or memory blow-up kills a disposable worker. Deadlines and memory ceilings are enforced from outside by the parent, and sandbox="require" refuses to start unless every OS layer is in force. |
| A thin subprocess wrapper. The guest and the protocol share a global scope and the same output stream, with no limits. | The guest can corrupt or forge the protocol, overwrite the code that serialises results, or hang the caller; there is no timeout, memory cap or output cap. | The protocol channel is separate from the guest's output. There is no Deno, process or require; serialisation is native code the guest cannot reach; the parent kills a worker that breaks a limit. These attacks are probes in scripts/autoresearch/metric_security.py. |
| Silent downgrade. The sandbox quietly becomes "no sandbox" when a kernel feature is missing. | Nobody notices, so a hardened deployment can be running unconfined. | sandbox="require" is the default and fails closed. The worker proves its own confinement with a startup self-test (it tries to read, write, connect, spawn and signal, and refuses to start if any of them works). |
| No resource limits, or limits the guest can outlast. | One loop, one allocation or one flood of output takes the host or the other tenants down. | Wall-clock, CPU, memory, buffer, call and output limits are enforced from outside, with hard kills; a guest that keeps calling your functions cannot hold a deadline open. |
| Host functions that can be tampered with. The guest changes the scope before the host installs a tool. | The tool silently does nothing, or guest code runs during the install, and the host believes the tool is in place. | Binds fail closed: a tampered scope makes the bind raise, never silently do nothing. Tools are reachable only through unguessable capability tokens. |
| State shared across tenants. Reused workers, shared pools and shared threads. | Data leaks between users, one tenant starves the others, or a restored session gets more than it should. | One worker per session, never reused; each session's tool threads are its own; per-pool caps; signed, owner-bound journals that cannot refund a spent budget. |
| Trusting the result. Output goes straight to a terminal, a log or a model. | Escape sequences and invisible characters in console or error text attack whatever reads them. | Captured console and error text are bounded and stripped of control, escape and invisible characters, and host errors are redacted by default. |
What this does not mean. pydeno is not unbreakable. It contains the engine, it does not shrink it: a V8 bug is contained in the worker, not prevented, and V8 is large. A small interpreter with a minimal trusted base has a real advantage for code that is mostly Python logic. pydeno has had no outside security review yet; it has had an independent review of every change that touches the boundary, and that process has repeatedly found real defects, including in fixes. We publish the misses as well as the catches in the security report.
Speed
Measured on macOS arm64 with release builds, using paired A/B runs; reproduce with
benches_py/alternatives_bench.py and
scripts/autoresearch/metric_speed.py. Numbers vary with the machine.
A warm call on a live sandbox (eval("1 + 1")) |
about 30 µs |
Check out a session from the warm pool (Pydeno().checkout()) |
about 0.1 ms; a raw SandboxPool checkout about 0.04 ms |
Check out and run a first feed_run |
about 1.5 ms |
| A cold start (new sandboxed worker and first call) | about 50 ms; the pool hides it |
| Move a 2 MB structured result across the boundary | about 18 ms each way (native codec) |
Jitless V8 (the default) makes compute-heavy code roughly 1.5 to 8 times slower than with the JIT;
jitless=False trades that back for a larger attack surface, and still runs behind the full OS sandbox.
How it compares
| pydeno | Monty | A Deno subprocess wrapper | |
|---|---|---|---|
| Language | Full modern JavaScript | A subset of Python | Full JavaScript |
| Isolation | Process + OS sandbox + limits, self-tested at start | A small interpreter with no I/O except your functions | Deno's permission system only |
| Limits enforced for you | Memory, CPU, time, buffers, calls, output | Yes | None |
| Pausing, signed resumable sessions | Yes | Yes | No |
| Start-up | Pool checkout about 0.1 ms; cold about 50 ms | Pool checkout microseconds | About 13 ms (measured) |
| Trusted code base | Large (V8), contained | Small, auditable | Large (Deno), one barrier |
Monty is the better choice when the model's code is mostly Python logic and you want the smallest trusted base; pydeno is the choice when you need JavaScript and its ecosystem. They combine well (see the showcase). The full, frank comparison, including what pydeno cannot do and measured numbers, is on the alternatives page.
Advanced: the building blocks
Pydeno is built from these, which stay available unchanged.
Tools the guest can call, with a total budget:
from pydeno import IsolatedRuntime, ToolBridge

bridge = ToolBridge({"get_weather": get_weather, "send_email": send_email}, max_calls=50)

with IsolatedRuntime(sandbox="require") as rt:
    bridge.attach(rt)
    rt.eval("tools.get_weather('Zurich')")
The call that exceeds max_calls never reaches your Python function; the guest gets a catchable
ToolBudgetError. A Python exception inside a tool reaches JavaScript as a real Error whose name is the
exception's class, so the model's code can branch on it. Host errors are redacted by default.
Make the easy path the safe one (the module-level helpers then use a sandboxed worker):
import pydeno

pydeno.configure_default_runtime(isolated=True, sandbox="require")
pydeno.eval("1 + 1")
Run real libraries. Many assume browser basics a bare isolate lacks. Opt in to a small, pure-JavaScript set
(virtual-time timers, TextEncoder, btoa, Blob, EventTarget, AbortController, structuredClone) that
never defines window or document:
from pydeno import IsolatedRuntime, RuntimeConfig, WEB_POLYFILLS

rt = IsolatedRuntime(RuntimeConfig(bootstrap=WEB_POLYFILLS))
Async code: AsyncPydeno, AsyncIsolatedRuntime and AsyncAgentSandbox never block the event loop and use no
thread per runtime.
Showcase: Python and JavaScript, both sandboxed
A model that writes code wants the best language for each half of the job: Python for wrangling data, JavaScript for what only the JS ecosystem does well. Pair pydeno with Monty (Pydantic's Python sandbox) and run both without trusting either, sharing one set of host tools and one call budget:
with Monty() as pool, pool.checkout() as py:                      # the model's Python, in Monty
    analysis = py.feed_run(model_python, external_lookup={"fetch_sales": fetch_sales})

with IsolatedRuntime(RuntimeConfig(bootstrap=WEB_POLYFILLS), sandbox="require") as js:
    js.bind_function("getAnalysis", lambda: analysis)             # hand the result across
    js.bind_function("fetch_sales", fetch_sales)                  # the same tool, same budget
    svg = await js.eval_async(model_javascript)                   # the model's JS, in pydeno
1. Python half, in Monty
  [python] best region: East (1750)
  [python] refused: PermissionError: Permission denied: '/etc/passwd'
2. JavaScript half, in pydeno
  [js]     refused: Evaluation failed: ReferenceError: fetch is not defined
  [js]     sandbox: seatbelt
3. wrote sales.svg (11021 bytes); tool calls used: 2 of 5
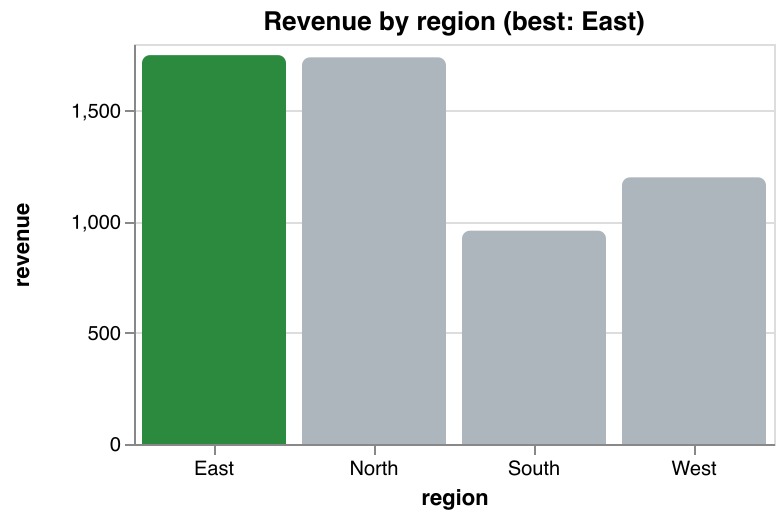
Python crunched the numbers; JavaScript drew the chart with Vega-Lite;
each sandbox refused its own attempt to reach outside, and both drew on the same five-call tool
budget. Full runnable example: examples/monty_and_pydeno.py
(notebook).
More of the same: Python prepares, JavaScript builds
Monty is excellent at the data half, and the JavaScript ecosystem has libraries nothing in Python matches. Each example below is a complete, tested program: the model's Python runs in Monty, the model's JavaScript runs in pydeno, neither can reach your files, network or environment, and each test checks the answer against an independent computation (and Monty's against CPython's).
| Example | Monty (Python) does | pydeno (JavaScript) does | Produces |
|---|---|---|---|
| 3D terrain | layered value-noise heightmap, slope analysis, tree placement | three.js: mesh, normals, vertex colours by slope, instanced trees, raycast line-of-sight | .glb 3D model |
| Orbits | symplectic N-body integrator (figure-eight choreography), energy drift | three.js: speed-coloured tube trails, closest-approach analysis | .glb 3D model |
| Julia relief | Monty's own julia example: escape-time counts for every grid point |
three.js: a mountain range along the fractal's boundary, painted by escape time | .glb 3D model |
| City sun analysis | procedural city layout and zoning | three.js: extruded buildings, a raycast from every roof to the sun, shade ranking | .glb with per-building sunlight |
| Dependency network | synthetic package graph, PageRank, components | d3: force layout run to convergence, Voronoi cells, treemap | one self-contained SVG |
| Dashboard | a year of metrics: moving average, z-score anomalies, correlations, regression | ECharts: four-panel dashboard, server-side | HTML page with inline SVG, no scripts |
| Geospatial | fleet GPS tracks, cleaning and resampling | turf.js: buffer union, hulls, Voronoi service zones, nearest depot | GeoJSON and an SVG map |
| SQL to chart | answers a business question through a read-only SQL tool | Vega-Lite: bars, stacked bars, cohort heatmap | SVG charts |
| Spreadsheet to deck | analyses a sheet through a read-only wrapper | pptxgenjs: native charts, tables, narrative | .pptx board deck |


Left to right: the terrain, dependency-network and dashboard outputs. Every example's rendered output is in the gallery.
How fast are they together? One warm worker, median of three, on an Apple-silicon Mac, with V8 in
its secure default (jitless) and with the JIT turned on:
| Example | jitless (default) | V8 JIT on | JIT speed-up |
|---|---|---|---|
| three.js terrain (129x129 grid) | 879 ms | 180 ms | 4.9x |
| three.js N-body orbits (3000 steps) | 247 ms | 172 ms | 1.4x |
| three.js city sun analysis (6x6 blocks) | 210 ms | 27 ms | 7.9x |
| d3 network layout (200 packages) | 1,619 ms | 198 ms | 8.2x |
| ECharts dashboard (365 days x 4 regions) | 64 ms | 42 ms | 1.5x |
| turf geospatial (8 vehicles) | 1,937 ms | 347 ms | 5.6x |
| SQL question to Vega-Lite chart (4000 orders) | 18 ms | 17 ms | 1.1x |
| spreadsheet to PowerPoint (1000 rows) | 70 ms | 31 ms | 2.3x |
Most turns finish in well under a second even in the secure mode; Monty's data half stays within
about 1.1x of plain CPython. The JIT matters for compute-heavy JavaScript (layouts, raycasting), and
it is exactly the part of V8 where most exploits live, which is why it is off by default. If you
trust the code a little more, IsolatedRuntime(jitless=False) buys the second column and still
runs behind the full OS sandbox. Reproduce with
benches_py/monty_three_bench.py.
How it works
flowchart LR
    app["Your Python app"] -- "eval, tools" --> parent["IsolatedRuntime<br/>(supervisor)"]
    parent <-->|"validated frames only"| worker
    subgraph worker["Worker process: sandboxed before V8 starts"]
        v8["V8 (jitless)<br/>guest JavaScript"]
    end
    v8 -. "bound functions only" .-> parent
    parent --> tools["Your tools"]
The worker is a separate process with an empty environment, its own session, no privileges, and an OS sandbox applied before the JavaScript engine exists. The parent enforces the deadline, memory and call budgets from outside and treats everything the worker sends as untrusted input.
Which runtime?
IsolatedRuntime |
Runtime (in-process) |
|
|---|---|---|
| Use it for | Anything a model or a user supplied | Code you wrote or reviewed |
| A hostile builtin can abort or hang your process | No: it kills the worker | Yes (new Array(2 ** 32 - 1).fill(0)) |
timeout= always enforced |
Yes (hard kill from outside) | Not for every builtin (e.g. sparse-array sort) |
| OS sandbox | Yes | No |
| Start-up | pool checkout ~0.1 ms, cold ~50 ms | microseconds |
| A host tool call | Crosses a process boundary | In process, ~12-17 µs (BENCHMARKS.md) |
How it was tested
The sandbox is tested the way an attacker would try it: from inside, and against the real kernel.
Not tested on Windows. The sandboxed runtimes (IsolatedRuntime, Pydeno, agent sandboxes) are
POSIX-only (Linux and macOS) and are not supported on Windows, so their tests do not run there and
CI reports the Windows cells as experimental. Only the in-process Runtime loads on Windows, it is
not safe for hostile code, and it is not covered by the test suite described below.
- Assume-breach syscall sweeps. A sandboxed process fires every syscall in the kernel's table with garbage arguments, from a fresh process each time, and records what is still reachable. Dangerous calls are fired for real (inside a container, never on a host).
- The seccomp program is verified, not trusted. A BPF interpreter in the tests runs the filter's
decision logic on any platform, and every syscall number in it is checked against the Linux
kernel's own tables (regenerated from a pinned kernel tag by
scripts/gen_syscall_tables.py). - A capability checklist. What untrusted code tries first (read or write a file, reach the
network, spawn a process, read the environment; Deno, Node and browser globals; the runtime's own
plumbing), through both
evalandeval_async, plus a check that nothing reached the host. - Hostile peers. Fake workers that stop reading, send malformed or oversized frames, flood hash tables or lie about types; fuzzing with Hypothesis; and a port of pydantic/monty's security suite (the cases an in-process runtime cannot survive are pinned as strict expected failures).
- Two codecs, tested against each other. The wire codec is native (Rust) with a readable Python reference; hundreds of tests, including generated frames, require identical results and errors.
- Real libraries, inside the sandbox. pptxgenjs, three.js (GLB export), Vega-Lite and dagre give
the same results as an unsandboxed runtime, with their bytes pinned in
vendor/libs/; about 25 more (d3, ECharts, jsPDF, Tailwind v4, Prettier, ...) were checked by hand. - Many kernels. The Linux suite runs on 12 distro images (Debian, Ubuntu, Fedora, AlmaLinux,
Amazon Linux; Python 3.10 to 3.14) on both x86_64 and aarch64, and under simulated kernels that
lack Landlock, seccomp or both, to prove the sandbox degrades honestly and
sandbox="require"fails closed. See.github/workflows/test.yml. - Zero skips. Platform-specific tests are deselected, never skipped; CI enforces a skip budget of zero so an unrun test cannot hide.
- The worker proves its own confinement. Before any guest code exists it tries to read a file, write one, spawn a process, connect out, signal its parent and (on macOS) read the parent's environment and the machine's hardware ID; a complete sandbox that lets one through refuses to start. Each probe is also checked in reverse: it must report a breach in an unsandboxed process.
- Independent review, and what it found. Three AI reviewers (each given a separate slice of the sandbox and told to reproduce before reporting), GitHub Copilot, and research into how other sandboxes were attacked. The result is a findings table that lists the misses as well as the catches, including a macOS leak of the host's environment, a bridge bug that let a guest abort the process, and a V8 x86_64 startup trap that only a native x86_64 run revealed. Read it in the security report.
- An autonomous pentest agent, run against the source. Before 0.8 we ran Strix (an open-source AI pentest agent) as a white-box review of a clean export of the code, in standard mode, locally, with no outside host reachable and a hard budget cap. It found no host escape and no capability-token bypass in the paths it reviewed. What it did report went through the same path as every other review finding: a failing test first, the smallest fix, a review by a different model. Its findings are not published; that is deliberate for a public repository. It is one more reviewer, not a proof: it read the code and did not exercise the native layer, so the OS-level checks above still carry that part. It is set up to run on a schedule (how).
- A probe battery that must stay at zero.
scripts/autoresearch/metric_security.pyruns hostile guests and hostile callers (limits, tampered binds, forged journals, oversized values, terminal escapes) and has to report zero violations before anything merges to the release branch.
Integrations
- FastMCP tool bridge: expose FastMCP tools to sandboxed JS via
bind_functionand an in-processfastmcp.Client - pydantic-ai code mode (
JSCodeMode): the JavaScript counterpart of pydantic-ai's Monty-based code mode. The agent gets onerun_javascripttool; your other tools become typedtools.*functions the model's code calls withawaitandPromise.all, with retries, usage limits and approvals mapped onto pydantic-ai's own. Runs offline:examples/pydantic_ai_agent.py.pip install "pydeno[pydantic-ai]" llmplugin (llm-pydeno): aPyDenotoolbox for thellmCLI. Onerun_javascripttool runs the model's code in a sandboxed session that keeps state between calls and returnsstdout,stderr,resultanderrorwith size caps. A separate package;pydenodoes not depend onllm.- Agent sessions (
AgentSandbox): state across turns, pause and resume at every tool call (approval flows), a signed replay journal you candump()andload(), and the tool descriptions and.d.tsfor your prompt - ToolBridge: several Python tools with a total call budget, typed errors the model's JS can branch on, and
console.logrouted back to Python - Monty + pydeno: the model's Python runs in Monty, its JavaScript in pydeno, both sandboxed, sharing one tool and one call budget; Python computes, a Vega-Lite chart is drawn in JS
- Vendored npm libraries: run real npm document-generation libraries (
pptxgenjs,pdf-lib) from their browser bundles inside the sandbox; see the guide - Arrow IPC dataframes: move 100k+ row tables into the sandbox as Arrow IPC
bytesinstead of JSON objects (5 ms vs 253 ms); see the guide
Documentation
- Security policy and threat model · the isolation guide
- Quick Start · Concepts · Guides · Use cases · API reference
- Agent skill: an Agent Skills
SKILL.mdthat teaches coding agents (Claude Code and others) to use pydeno correctly. Copyskills/pydeno/into your agent's skills directory, e.g..claude/skills/ - Benchmarks · Changelog
Status and contributing
pydeno is experimental: expect breaking changes between versions. Found a way out of the
sandbox? Please report it privately, as described in SECURITY.md. Everything else:
issues and pull requests are welcome; start with
docs/contributing/.
Licensed under the MIT License.
Acknowledgements
pydeno began as a fork of jsrun by Xin Fu, which had the
original idea of a Python library that runs JavaScript on a Rust runtime built on deno_core. We took
that idea and its foundations, then changed a great deal: the sandboxed worker process and OS
confinement, the tool boundary, the wire codec, the resource limits, and most of the tests are new.
Thank you to jsrun for the starting point. The MIT licence and original copyright are kept,
and docs/contributing/upstream-divergence.md records
what came from where.
Thanks also to Monty by Pydantic, whose design for running agent-written code (limits, host functions, a public challenge to break it) shaped how we think about this problem; the two sandboxes work well side by side.
1 maintainer

Metadata
1 maintainer
Release files for pydeno 0.13.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| pydeno-0.13.2.tar.gz | 4.2 MB | Details |
Built distributions (wheels)
Total release size: 446.8 MB
Release files / pydeno-0.13.2.tar.gz
| Download URL | pydeno-0.13.2.tar.gz |
|---|---|
| Size | 4.2 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
272eeaf2124e05df5fc18dd7debe573c75cafbcb07cbf4cb9295c8a65cb9cce6
|
|
BLAKE2b-256 checksum How to use checksums |
bb68df4f445e5603e59e326da2807b029ef920cb755506363e25b7f93a0bb9bf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-pp311-pypy311_pp73-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.13.2-pp311-pypy311_pp73-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.9 MB |
| Tags | Linux glibc 2.28+ x86-64 PyPy 3.11 PyPy 3.11 7.3 |
|
SHA-256 checksum How to use checksums |
2e0e194ff3c54812ceaeef83ab9b7ad0f52135668bf9859803b485f32674d71a
|
|
BLAKE2b-256 checksum How to use checksums |
04d50667b774222993796016d65c8d68080d3efba60e489a5fbacece78575560
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-pp311-pypy311_pp73-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.13.2-pp311-pypy311_pp73-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.3 MB |
| Tags | Linux glibc 2.28+ ARM64 PyPy 3.11 PyPy 3.11 7.3 |
|
SHA-256 checksum How to use checksums |
003ee60f3c90fd659d3957dca0630ddc37de1eb62789a771685ac596286a2960
|
|
BLAKE2b-256 checksum How to use checksums |
da364e164d74a8b091cf52a20284537b53dbbda126df5a26c17005f5ecec498f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp315-cp315-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.13.2-cp315-cp315-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.9 MB |
| Tags | CPython 3.15 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
52417ba5dc86e08ad2b9db8f3fd1888ce751591bc95c477095b79a1451ac85e3
|
|
BLAKE2b-256 checksum How to use checksums |
39ccfe8c99ee69563679dd47b6cae93f22d6b6ddf329fe70fa76e762ec97b518
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp315-cp315-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.13.2-cp315-cp315-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.3 MB |
| Tags | CPython 3.15 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
28380b77b3941319c93aa3eba78360725ab8f9ac7b6c3d544ecde452ee98e593
|
|
BLAKE2b-256 checksum How to use checksums |
f390118dddc683321a06cc47eef5b8b5cc15f11f47598c5a7fd1854c2bbe7597
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp314-cp314-win_amd64.whl
| Download URL | pydeno-0.13.2-cp314-cp314-win_amd64.whl |
|---|---|
| Size | 19.2 MB |
| Tags | CPython 3.14 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
ac49887715f30c1b4482f2a55b61bb8687107f83ec6f730e7e3088e79e0c4bf4
|
|
BLAKE2b-256 checksum How to use checksums |
e2c9bcfaac49e327f77bc3a3612b107aec51800ee4b257741da2e592094327a7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp314-cp314-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.13.2-cp314-cp314-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.9 MB |
| Tags | CPython 3.14 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
98657f3ba48b71d36ef3e93a55f90622c0264724bac5c14b8fa00641ea048f58
|
|
BLAKE2b-256 checksum How to use checksums |
acf57ee073b47547ce84e4adfab46e91a5964fa0a111b29bd3549873b10b0644
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp314-cp314-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.13.2-cp314-cp314-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.3 MB |
| Tags | CPython 3.14 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
17c372a83e3536611ae53ffcfaee0e78d2e2a5ba6b62e878362453b88e84910e
|
|
BLAKE2b-256 checksum How to use checksums |
15e305e1682bf72165a9e0bb3c0b40cad72a437fdc98c7027d9e2a940d921039
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp314-cp314-macosx_11_0_arm64.whl
| Download URL | pydeno-0.13.2-cp314-cp314-macosx_11_0_arm64.whl |
|---|---|
| Size | 17.9 MB |
| Tags | CPython 3.14 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
60297a739ac226bdf01a67c1f2237340ac6c16dcf8f4cb507f69ecdc4e83dd24
|
|
BLAKE2b-256 checksum How to use checksums |
bc03f2a780e822d84ef51ee4d204c4eb0de9a87dbe76d58fdb24677d37536dd6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp313-cp313-win_amd64.whl
| Download URL | pydeno-0.13.2-cp313-cp313-win_amd64.whl |
|---|---|
| Size | 19.2 MB |
| Tags | CPython 3.13 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
7bf3378a27e0d99dfa069e3eda312026bd9570ca8e99e29d5d28e2057bbdd337
|
|
BLAKE2b-256 checksum How to use checksums |
c57a53e129ae3b7480dbae8d66f9838be020c880a172ce76050512c07e1dfeb3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp313-cp313-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.13.2-cp313-cp313-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.9 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
1b627f7d7cc02791fa71e03cbdb4ac1614f2b7afd54d73c0cc2d4578bb3d4aca
|
|
BLAKE2b-256 checksum How to use checksums |
647bf78f562637899485cecbac784655add04e0996d88e3f24fd229be2711dbe
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp313-cp313-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.13.2-cp313-cp313-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.3 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
03655add2e6b29db9bd8ea03007c3c011b2ebe68505ee6cd9d366b534bd89c59
|
|
BLAKE2b-256 checksum How to use checksums |
f71f411817714037275fe5aa484e29b5ebf708f7b6abe48f264494b85271b9bf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp313-cp313-macosx_11_0_arm64.whl
| Download URL | pydeno-0.13.2-cp313-cp313-macosx_11_0_arm64.whl |
|---|---|
| Size | 17.9 MB |
| Tags | CPython 3.13 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
01f7192c4cf91be822aa24da40e4c17c27e0758a58db229e420ea7186df3a01a
|
|
BLAKE2b-256 checksum How to use checksums |
e6b98a8806791a1bce43d6d70cf43b318089ba861b4fcbd8b70b04a520ffa726
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp312-cp312-win_amd64.whl
| Download URL | pydeno-0.13.2-cp312-cp312-win_amd64.whl |
|---|---|
| Size | 19.2 MB |
| Tags | CPython 3.12 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
42c9efce4ab79c2cba37c23776dc7143a4e8e715d32947b0541df8dc8b116add
|
|
BLAKE2b-256 checksum How to use checksums |
3dc05c802b3384a3ab976855aa36c9d31ffddd2c524568ad9121f3c0e0322d05
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp312-cp312-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.13.2-cp312-cp312-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.9 MB |
| Tags | CPython 3.12 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
796d2c324502a7e44716dea76167be706b3c40e10b308abb857827ba78f6e5ea
|
|
BLAKE2b-256 checksum How to use checksums |
fc552c69636a8afeb9f30e0d7637f63c342b48f6394d98f4262c6128e4ab46fd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp312-cp312-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.13.2-cp312-cp312-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.3 MB |
| Tags | CPython 3.12 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
92779a80b1d4b05848179cef2bec25902eed923a8c32a014ffc20bb08de666c1
|
|
BLAKE2b-256 checksum How to use checksums |
34f368449350ebf9b20dfb962e01e2d0a5f0244a11a4adabdd80e7eea3852341
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp312-cp312-macosx_11_0_arm64.whl
| Download URL | pydeno-0.13.2-cp312-cp312-macosx_11_0_arm64.whl |
|---|---|
| Size | 17.9 MB |
| Tags | CPython 3.12 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
f171457575d9c028afdc68c515fd6bd17b9a93b941887fb4a8803b670ff52188
|
|
BLAKE2b-256 checksum How to use checksums |
1e86c97d094db76ef149abc7d9692fc8f65631f8110d62efd239a1e49de89eda
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp311-cp311-win_amd64.whl
| Download URL | pydeno-0.13.2-cp311-cp311-win_amd64.whl |
|---|---|
| Size | 19.2 MB |
| Tags | CPython 3.11 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
05e083cf7fd8a95add252205215d29f01638a5e5cfa235aa814f36d5142e5c90
|
|
BLAKE2b-256 checksum How to use checksums |
440005745919590ef7138180f3cc459464089c61f371013562a49465292e56c3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp311-cp311-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.13.2-cp311-cp311-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.9 MB |
| Tags | CPython 3.11 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
fe522454dbf623817c18c90d233158a12cdeb64085714e8d395c497fba124ff8
|
|
BLAKE2b-256 checksum How to use checksums |
78e5f7eeb073e0cce049016025e1cc6c7a024c7c90074c175346becf0b0db123
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp311-cp311-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.13.2-cp311-cp311-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.3 MB |
| Tags | CPython 3.11 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
5c1e4ed8550f982e90774becc3b9b4a35b87d8abc9eace62bf52cefdf3b559f5
|
|
BLAKE2b-256 checksum How to use checksums |
4f472ba5c5a8e63ca0ace469f51fe171e3f4c561624cbda2ceeab391f04ad20e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp311-cp311-macosx_11_0_arm64.whl
| Download URL | pydeno-0.13.2-cp311-cp311-macosx_11_0_arm64.whl |
|---|---|
| Size | 17.9 MB |
| Tags | CPython 3.11 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
0f1dacb6692fbb8370a01f7a5eb93abf495579233a6f0a3803063091099f15a6
|
|
BLAKE2b-256 checksum How to use checksums |
66ecbf6c123db5bbada0402dfeb167c0a6540f78d7bf1be2666a0e394223327f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp310-cp310-win_amd64.whl
| Download URL | pydeno-0.13.2-cp310-cp310-win_amd64.whl |
|---|---|
| Size | 19.2 MB |
| Tags | CPython 3.10 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
daad7bb4bde9833dc41984d5357b220de1700af06b88254e0e3a23628e540b0e
|
|
BLAKE2b-256 checksum How to use checksums |
3262cc39ddb52ae0a6c9af6c2deea3d9a6f3623d06b5dc9f1aa4df3f2a967e50
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp310-cp310-manylinux_2_28_x86_64.whl
| Download URL | pydeno-0.13.2-cp310-cp310-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 19.9 MB |
| Tags | CPython 3.10 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
a095e88cafc345110c71811f89246f061c267639dd96850fc4668e9dfdfded49
|
|
BLAKE2b-256 checksum How to use checksums |
167c9d4f6c807958ce256bb0dc77c497f0339ccc7b02bf5cc05c3a9fbb6ee55a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency logRelease files / pydeno-0.13.2-cp310-cp310-manylinux_2_28_aarch64.whl
| Download URL | pydeno-0.13.2-cp310-cp310-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 19.3 MB |
| Tags | CPython 3.10 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
436cf70124f28d92b552a4b0ff965b66b825843d100fc7c7d96269a6e1703ff1
|
|
BLAKE2b-256 checksum How to use checksums |
8af8ffc035119dc169a28ee8f7512a9f737e37e381bb28323126fd6e6adb84e9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 10, 2026.
Transparency log













