


Malware Family Analysis Report Showcase
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
 |
| Family | Summary | Signature Behaviors | Report |
|---|---|---|---|
| DroidKungFu | Privilege escalation with C2 control. | 1. Gain unlimited access to a device. 2. Install/Uninstall additional apps. 3. Forward confidential data. |
View |
| GoldDream | SMS/call log exfiltration with remote C2 commands. | 1. Monitor SMS messages and phone calls. 2. Upload SMS messages and phone calls to remote servers. |
View |
| SpyNote | Credential theft and device surveillance via RAT. | 1. Take screenshots. 2. Simulate user gestures. 3. Log user input. 4. Communicate with C2 servers. |
View |
| DawDropper | Dropper that installs banking trojans for financial theft. | 1. Download APKs from remote servers. 2. Install additional APKs. |
View |
| SLocker | Android ransomware locking/encrypting devices. | 1. Lock the device with an overlay screen. | View |
| PhantomCard | NFC relay–based financial fraud. | 1. Communicate with C2 servers. 2. Read the payment data of NFC cards. 3. Captures PINs of NFC cards through deceptive screens. |
View |
| ToxicPanda | Banking trojan enabling on-device fraud. | 1. Abuse Accessibility. 2. Remote device control. 3. Intercept OTP. |
View |
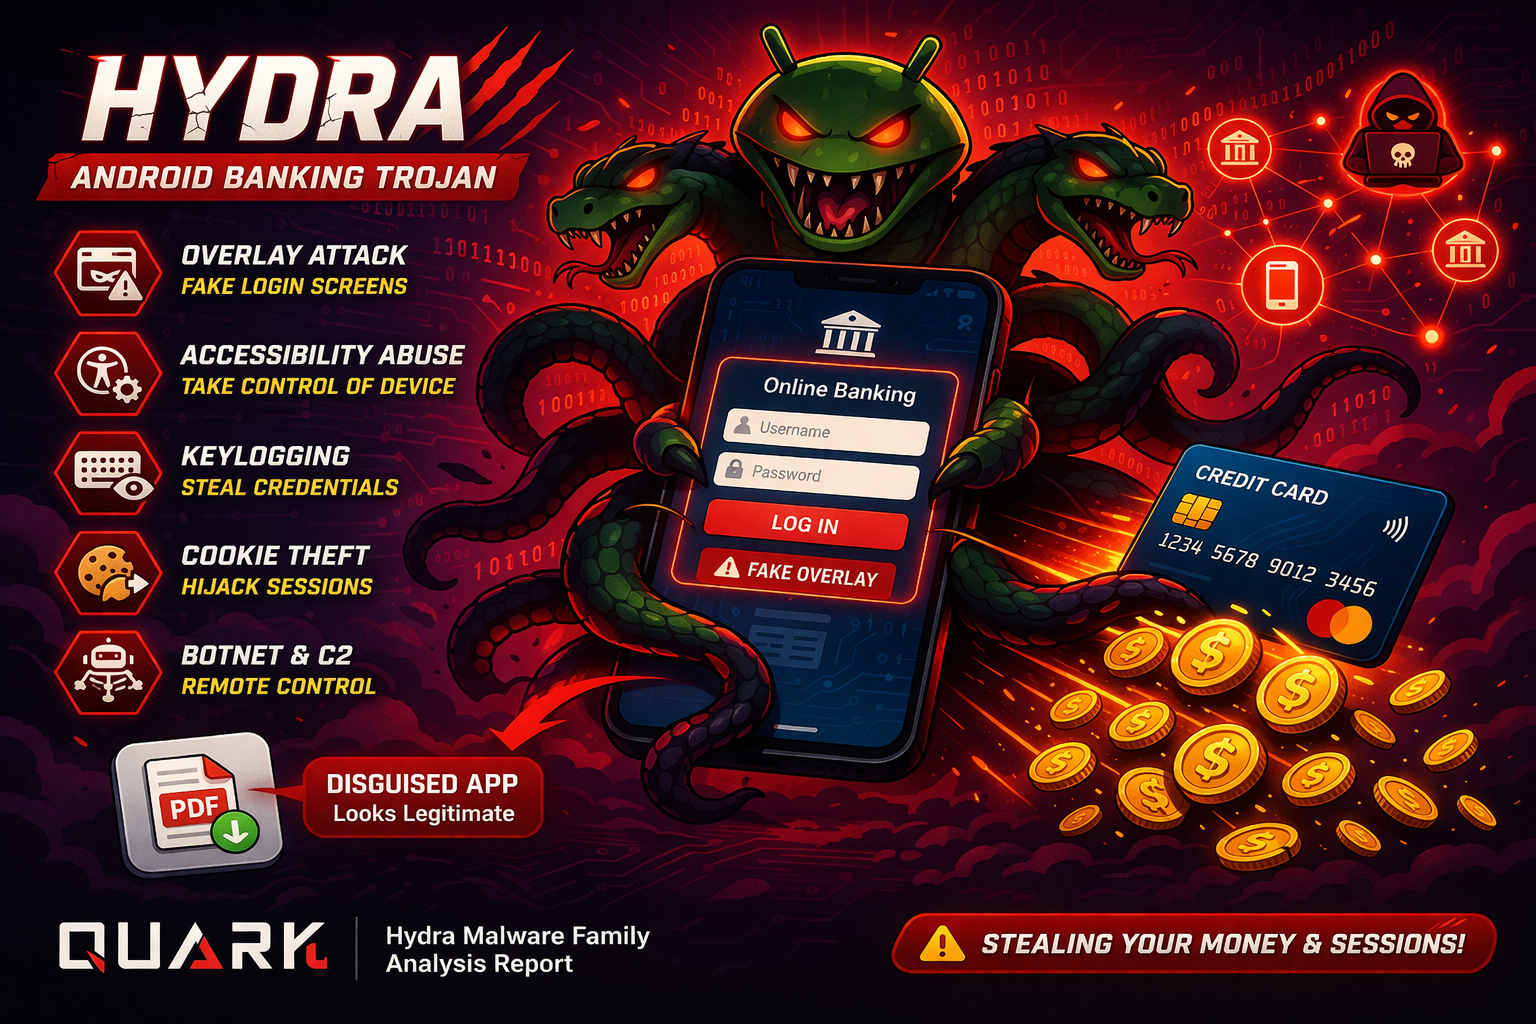
| Hydra | Banking trojan using overlay attacks. | 1. Overlay credential theft. 2. Accessibility abuse. 3. Steal OTP/cookies. |
View |
| SharkBot | Banking trojan targeting financial credentials and transactions. | 1. Abuse Accessibility services. 2. Perform overlay attacks to steal credentials. 3. Intercept SMS messages (OTP). |
View |
| Antidot | Banking trojan disguised as legitimate updates for financial data theft. | 1. Intercept SMS messages (OTP). 2. Log user input (keylogging). 3. Enable remote control via C2. |
View |
| Arsink | Banking trojan focusing on credential and financial data exfiltration. | 1. Steal sensitive data from device. 2. Intercept SMS messages (OTP). |
View |
| TrickMo | Banking trojan using overlay attacks and accessibility abuse for credential theft. | 1. Overlay attacks to steal banking credentials. 2. Intercept SMS for 2FA bypass. 3. Screen recording and accessibility abuse. 4. Dynamic payload loading via reflection. |
View |
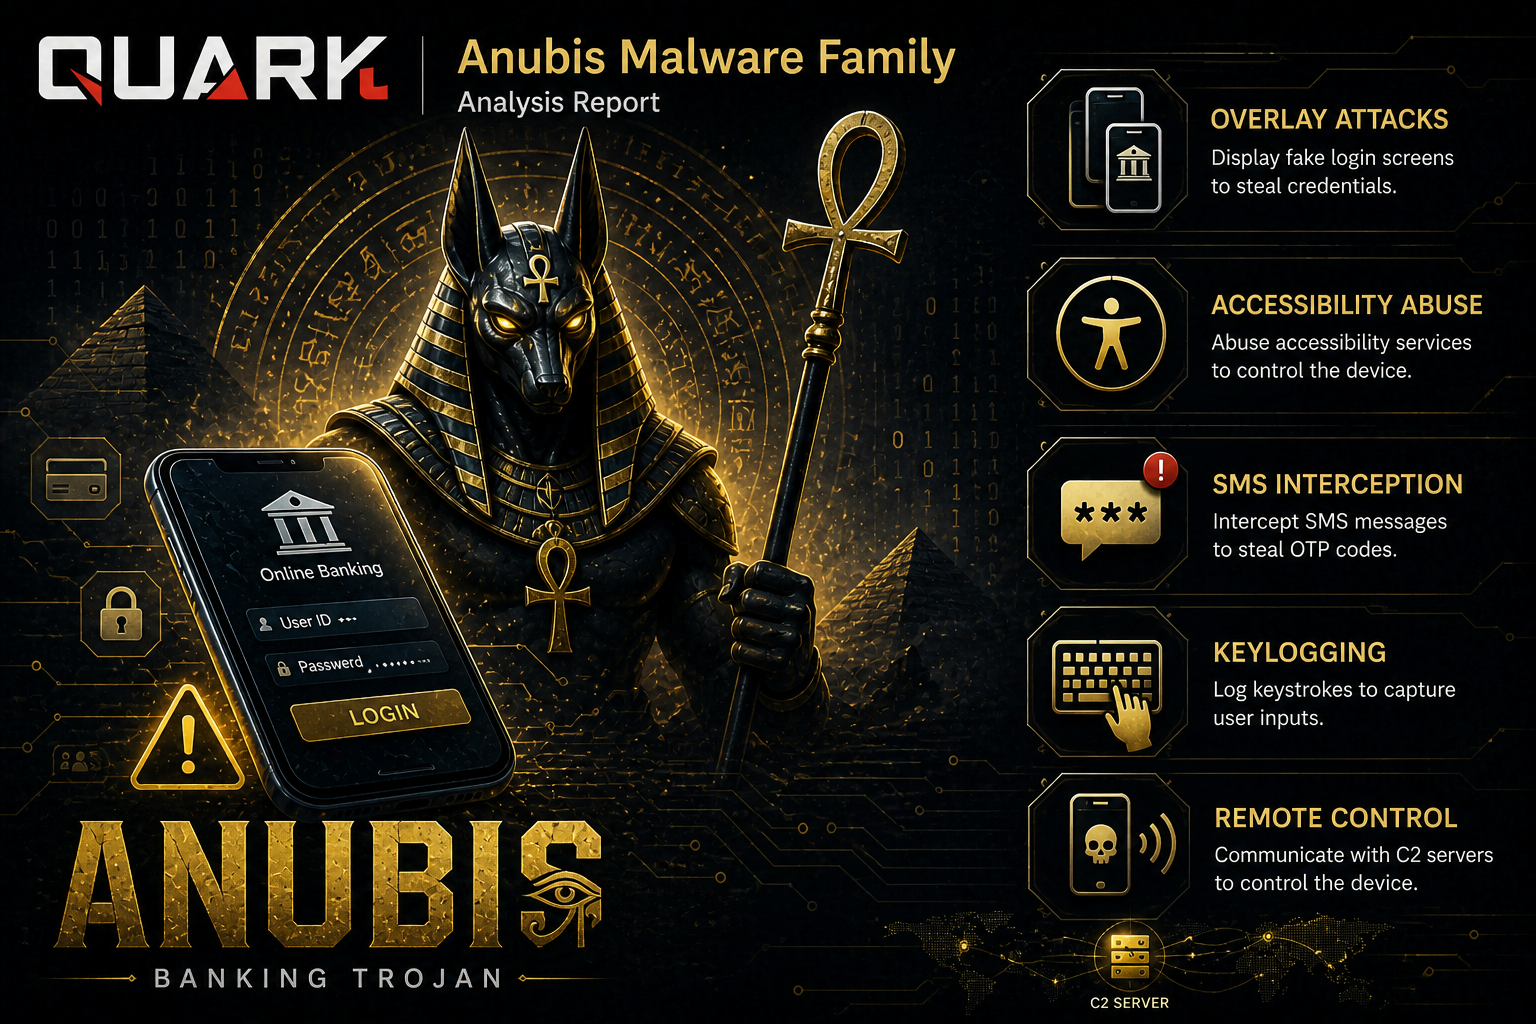
| Anubis | Banking trojan with RAT capabilities. | 1. Overlay credential theft. 2. Keylogging. 3. Intercept SMS (OTP). 4. Remote control via C2. |
View |
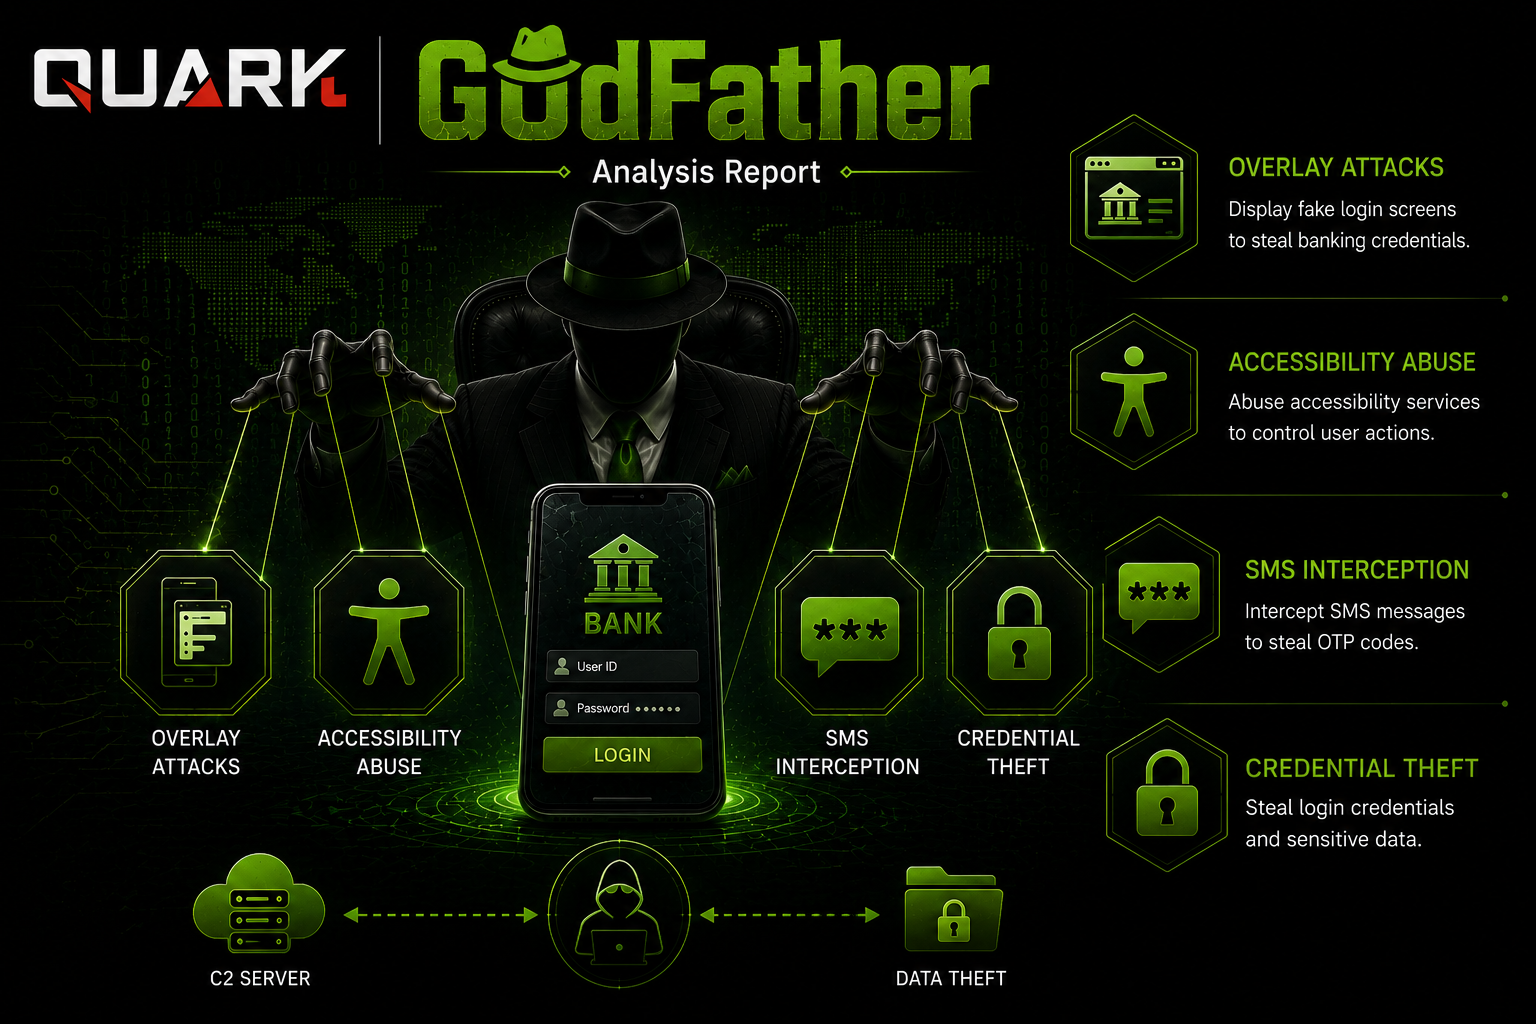
| GodFather | Banking trojan targeting financial credentials through overlay and accessibility abuse. | 1. Perform overlay attacks to steal credentials. 2. Abuse Accessibility services. 3. Intercept SMS messages (OTP). 4. Steal banking credentials and sensitive data. |
View |
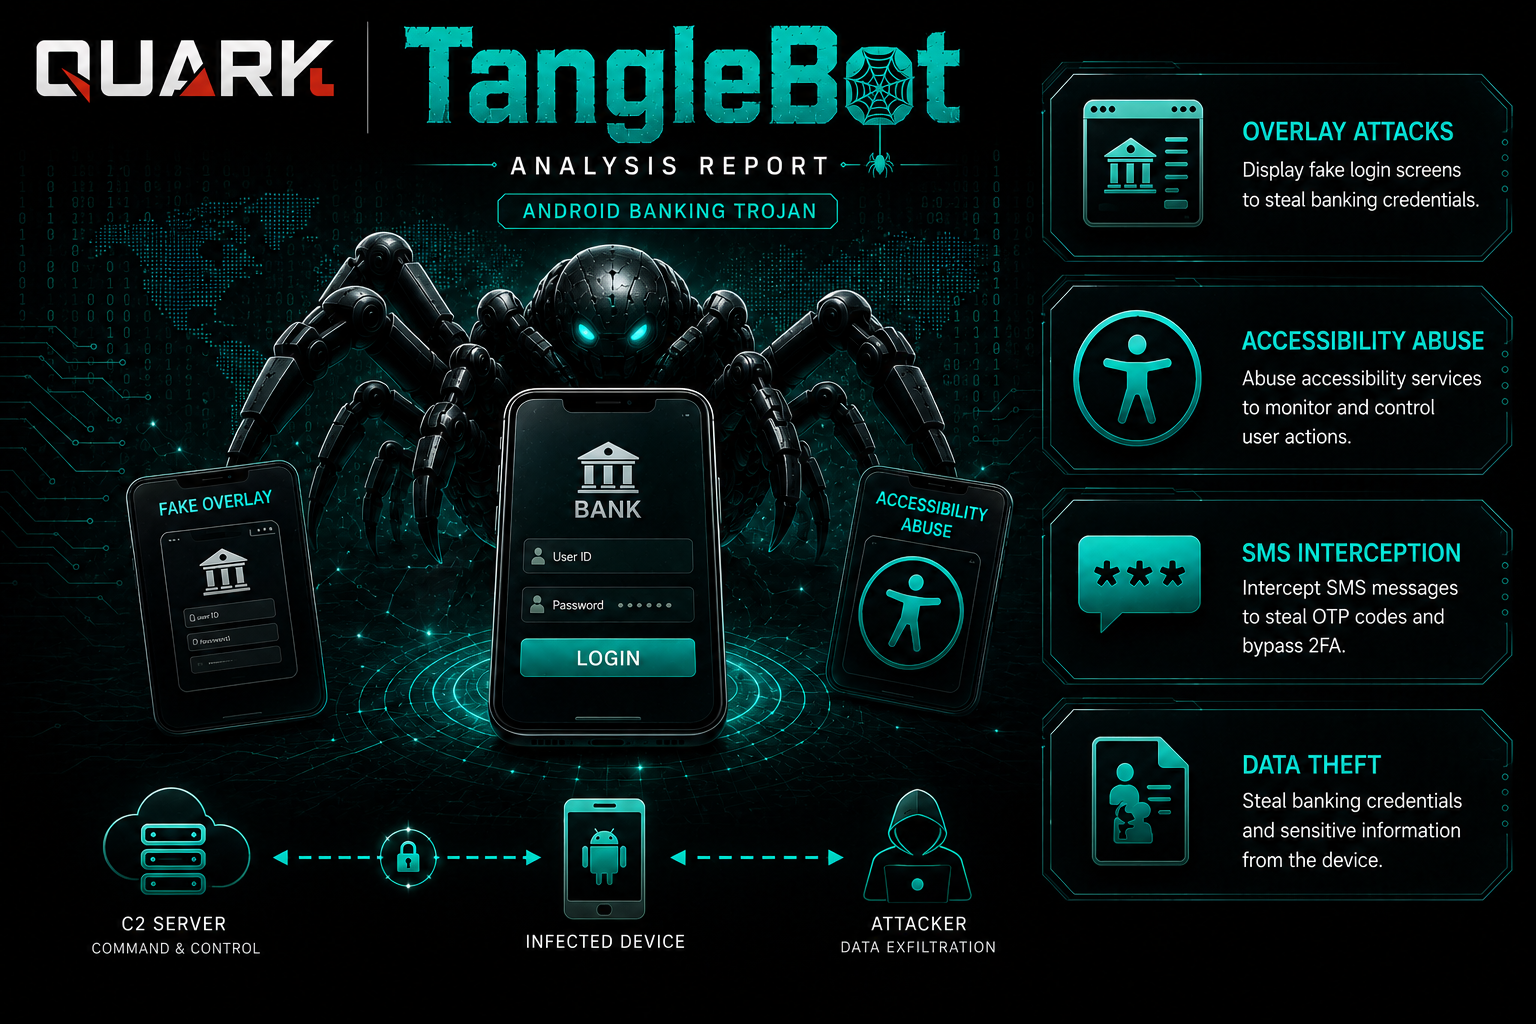
| TangleBot | SMS-based Android malware stealing personal and financial data. | 1. Spread through SMS phishing links. 2. Control device interactions and overlay screens. 3. Access SMS, contacts, call logs, camera, and microphone. 4. Steal account and financial information. |
View |
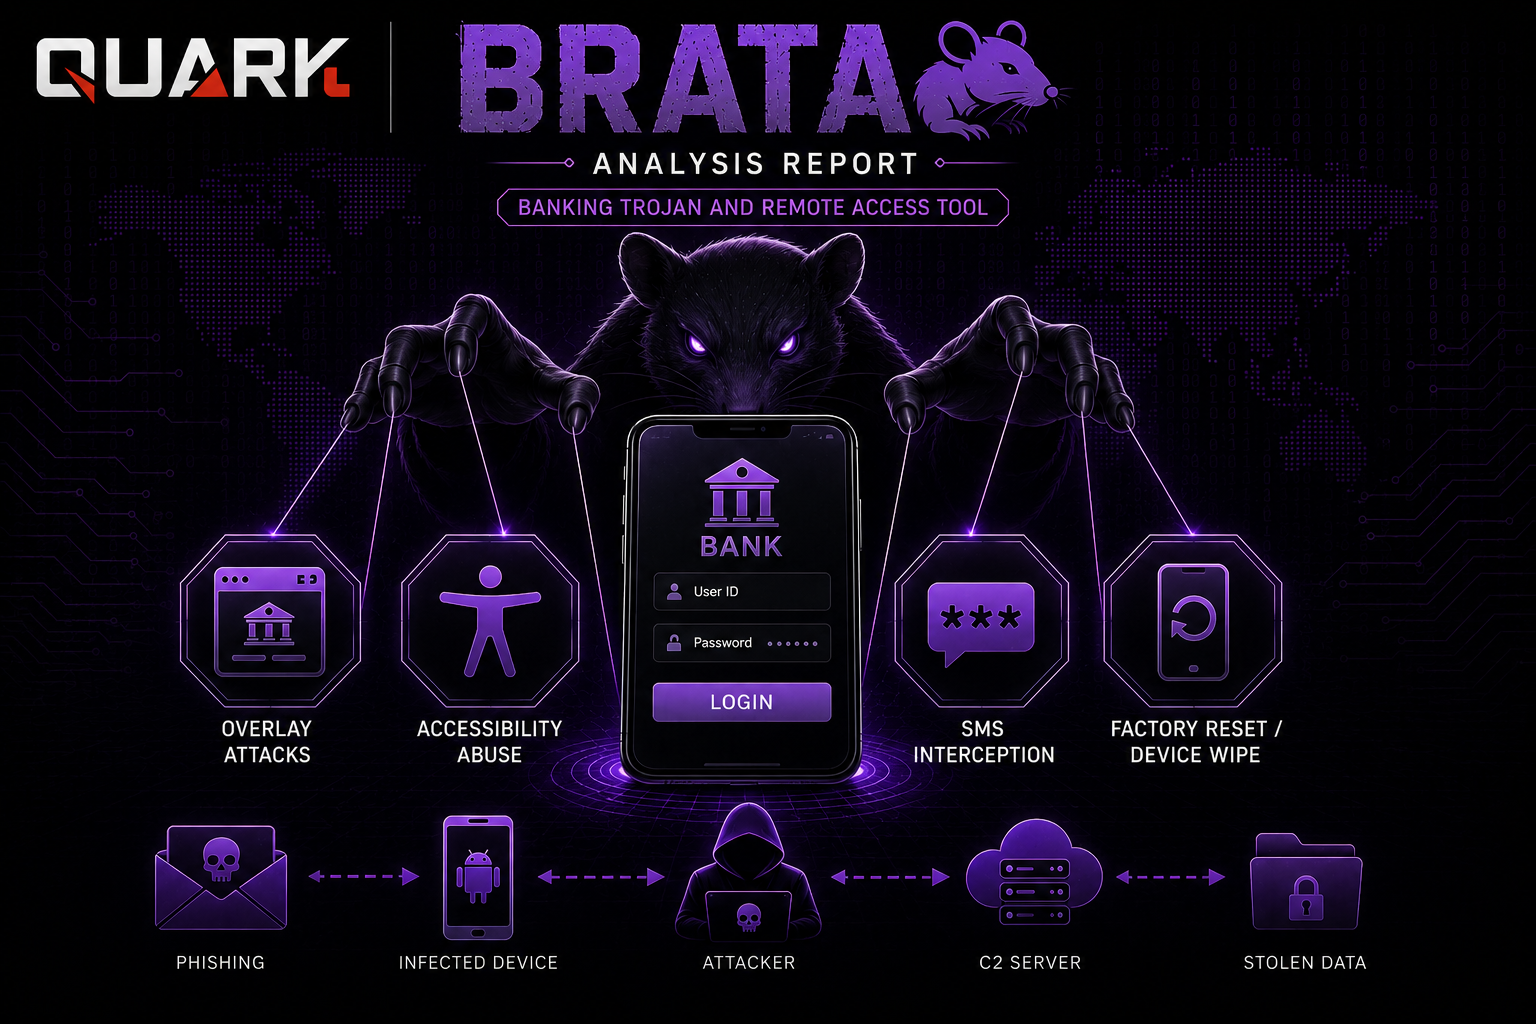
| BRATA | Banking trojan with remote control and anti-analysis capabilities. | 1. Perform overlay attacks to steal banking credentials. 2. Abuse Accessibility services for device control. 3. Intercept SMS messages (OTP). 4. Execute factory reset or device wipe commands. |
View |
| Cerberus | Banking trojan targeting financial credentials through overlay and device control. | 1. Perform overlay attacks to steal credentials. 2. Abuse Accessibility services. 3. Log user input (keylogging). 4. Enable remote control via C2. |
View |
| SuperCardX | NFC relay malware enabling contactless payment fraud. | 1. Read NFC payment card data. 2. Relay NFC transactions to attacker-controlled devices. 3. Communicate with C2 servers. 4. Facilitate unauthorized contactless payments. |
View |
| NGate | NFC-based malware enabling relay attacks and payment fraud. | 1. Read NFC payment card data. 2. Relay NFC communications to attacker-controlled devices. 3. Communicate with C2 servers. 4. Facilitate unauthorized contactless payments. |
View |
| AhRat | Android RAT capable of surveillance and data theft. | 1. Record audio from the device. 2. Steal files and sensitive data. 3. Remote access via C2. 4. Execute remote commands. |
View |
| AndroRat | Android remote access trojan for device surveillance. | 1. Record audio and capture video. 2. Track device location. 3. Steal files and device information. 4. Execute remote commands. |
View |
| Sova | Android banking trojan distributed as trojanised carrier apps for credential theft and SMS fraud. | 1. Read device identifiers via the C2 ping-response handler. 2. Inject outbound SMS on operator command. 3. Place phone calls without user consent. |
View |
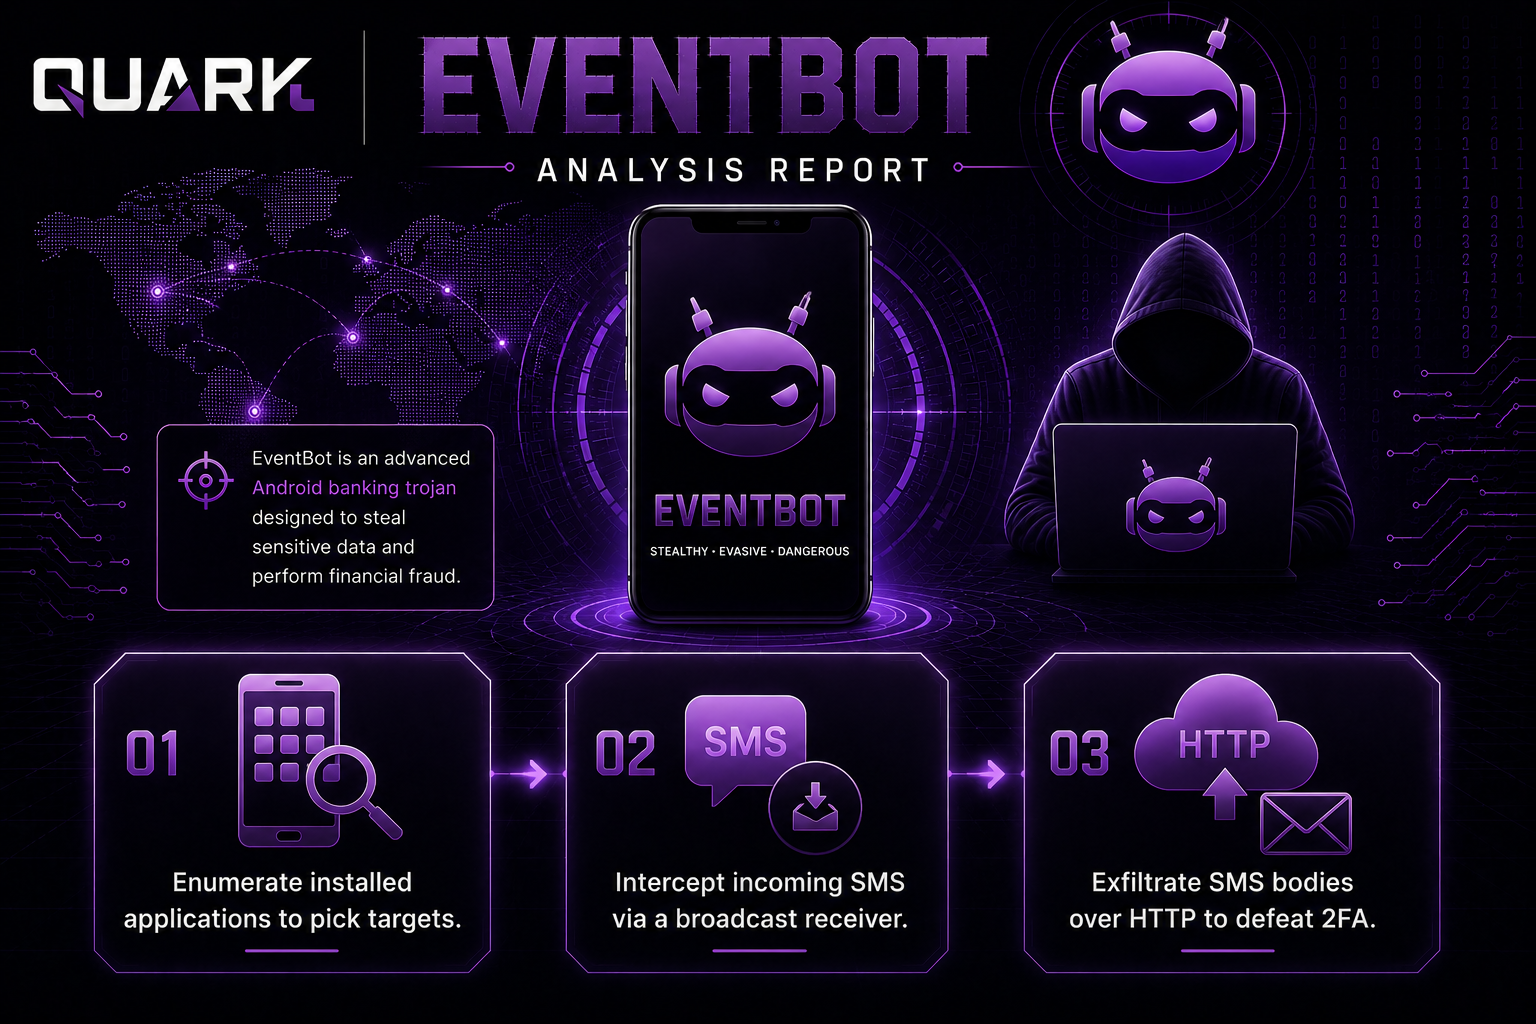
| EventBot | Banking trojan and infostealer targeting 200+ financial apps. | 1. Enumerate installed applications to pick targets. 2. Intercept incoming SMS via a broadcast receiver. 3. Exfiltrate SMS bodies over HTTP to defeat 2FA. |
View |
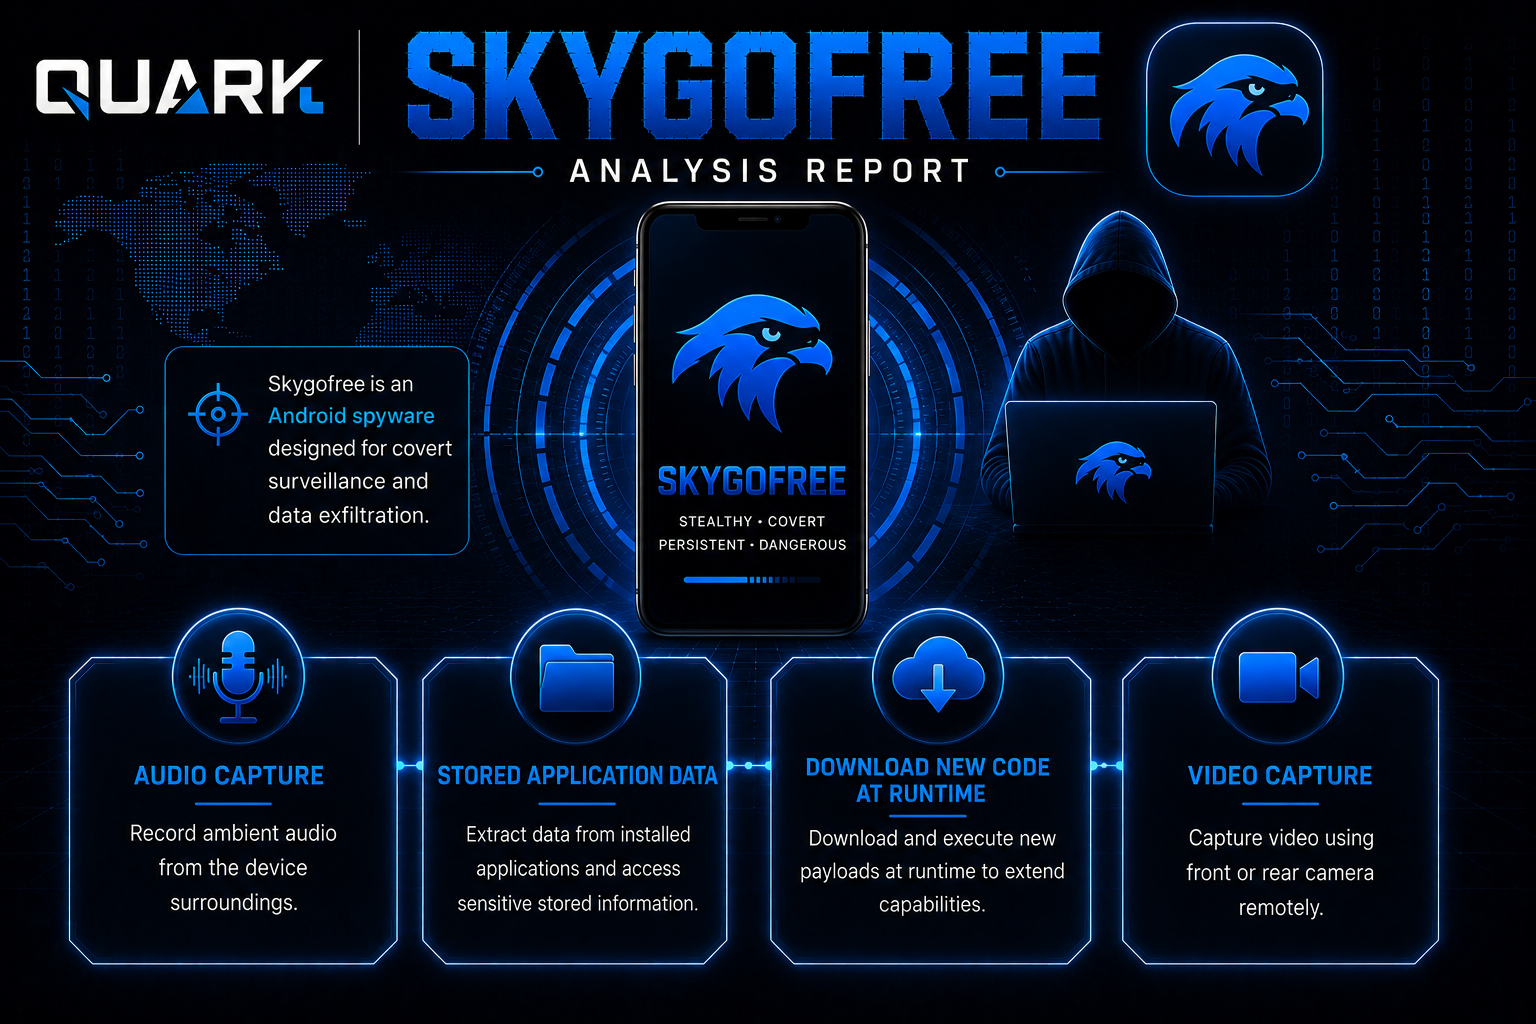
| Skygofree | Android spyware designed for surveillance and sensitive data collection. | 1. Capture audio. 2. Access stored application data. 3. Download new code at runtime. 4. Capture video. |
View |
| Chrysaor | Android build of the Pegasus spyware developed by NSO Group. | 1. Capture audio. 2. Check Internet connectivity. |
View |
| Dendroid | Commercial Android RAT sold on underground forums. | 1. Capture audio. 2. Access data from the local system. 3. Gather SMS messages. |
View |
| RuMMS | Android SMS-stealing family spread through SMS phishing links. | 1. Discover network configuration. 2. Gather SMS messages. |
View |
| Exodus | Android surveillanceware delivered through decoy mobile-operator service apps. | 1. Discover installed applications. 2. Discover network configuration. 3. Gather call log data. |
View |
| BrainTest | Android malware found in a Google Play game that runs root exploits and pulls further code from its server. | 1. Download new code at runtime. | View |
| Herodotus | Android banking trojan built for device takeover, sold as malware-as-a-service. | 1. Access data from the local system. | View |
Quick Start
Step 1. Install via PyPi
Install the latest version of Quark Engine:
$ pip3 install -U quark-engine
Step 2. Download Latest Rules
Fetch the latest rule database:
$ freshquark
Step 3. Run Summary Report
Analyze an APK with the downloaded rules and generate a summary report:
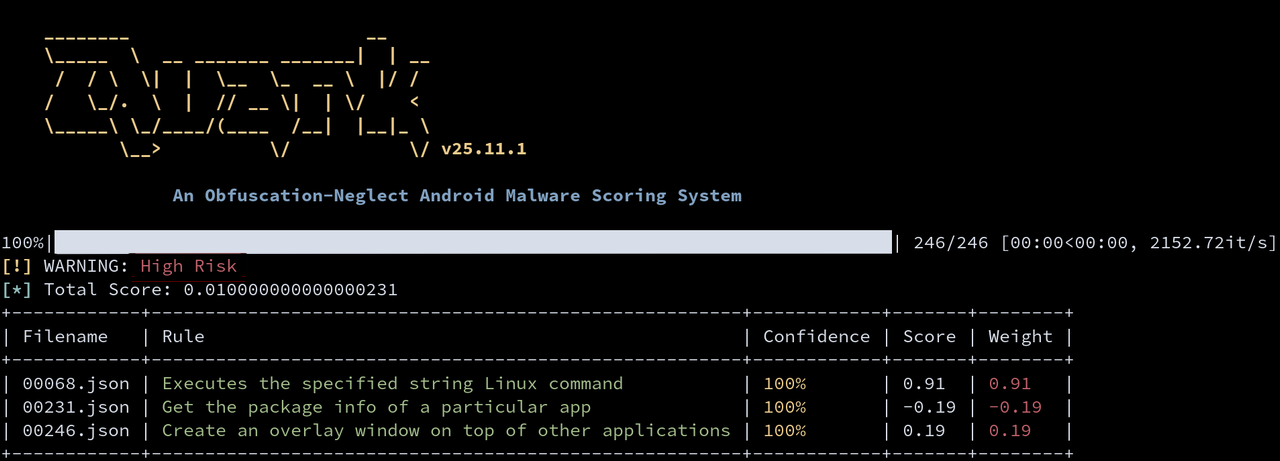
$ quark -a <apk_file> -s
Step 4. View Results
Example output:
Quark-Engine Skills
Quark-Engine also ships two Claude Code skills:
/quark:analysis— analyze an APK with Quark-Engine/quark:rule-gen— generate a Quark rule from decompiled code
To install, run these commands inside Claude Code after installing Quark-Engine:
/plugin marketplace add ev-flow/quark-engine
/plugin install quark@quark-engine
The skills then should appear.
Acknowledgments
The Honeynet Project
Google Summer Of Code
Quark-Engine has been participating in the GSoC under the Honeynet Project!
- 2021:
Stay tuned for the upcoming GSoC! Join the Honeynet Slack chat for more info.
Core Values of Quark Engine Team
- We love battle fields. We embrace uncertainties. We challenge impossibles. We rethink everything. We change the way people think. And the most important of all, we benefit ourselves by benefit others first.


Release files for quark-engine 26.11.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| quark_engine-26.11.1.tar.gz | 123.3 kB | Without provenance | Details for quark_engine-26.11.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| quark_engine-26.11.1-py3-none-any.whl | Python 3 | none | any | Details for quark_engine-26.11.1-py3-none-any.whl |
Total release size: 264.9 kB
Release files / quark_engine-26.11.1.tar.gz
| Download URL | quark_engine-26.11.1.tar.gz |
|---|---|
| Size | 123.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
b965d570c2d8d515b0c34cd8fb2f7c2742d3d2dbe5800a71ffc448014f33adbd
|
|
BLAKE2b-256 checksum How to use checksums |
0a8f2d70ff5ca3725917b88559341c61fd2525b6d7e92dcd1041079f043ef793
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.15.2
|
Release files / quark_engine-26.11.1-py3-none-any.whl
| Download URL | quark_engine-26.11.1-py3-none-any.whl |
|---|---|
| Size | 141.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
7a1af52582c63ed6f2397b1b0fadd450bdc7f6588e4c6e5519c8a07b07fbc314
|
|
BLAKE2b-256 checksum How to use checksums |
ccca877b762dc02f4ecac5e07bd066f459d1f0f5e0183f36c6538c78e7a22bb8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.15.2
|
Security for quark-engine 26.11.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














