
rpi-hwid — Raspberry Pi hardware identity


What is this Raspberry Pi wearing, what powers it, and what is soldered to it?
rpi-hwid answers from the Pi itself, out of evidence the firmware and kernel
already expose but nothing collects: HAT ID EEPROMs (including the ones the
firmware never reads), the Pi 5's own verdict on its USB-C supply, the PMIC's
input and RTC-cell voltages, the fan header, the USB tree, and which network
interfaces are soldered down.
Around that probe: separate modules for an FPGA board (NeTV2, Acorn, Arty, Cynthion) or a Tiny Tapeout demo board attached to the Pi; a collector that runs the lot over ssh across a fleet, one JSON document per host; and a label generator that turns those documents into sticker sheets carrying only what cannot change — serial numbers, MAC addresses, Device DNA, an ECP5's TraceID. The same probe runs unchanged on an Orange Pi PC.
The labels
rpi-hwid labels --data DIR --out labels.pdf lays out 63.5 × 38.1 mm labels, 21
to an A4 sheet (the Avery L7160 grid), from a directory of collected documents.
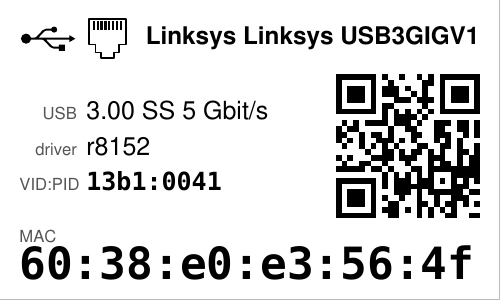
Every label carries only what cannot change, and every identifier that might
otherwise be typed is also a QR code. Cropped from a rendered sheet:
 |
 |
 |
| Pi 5 with a Waveshare PoE M.2 HAT+ (B); the radio is disabled, so no wlan MAC |
Pi Zero W with the Waveshare PoE- ETH-USB-HUB-HAT; the bonnet's RTL8152 is its eth MAC |
Orange Pi PC; eth MAC derived by U-Boot from the SoC serial, no radio |
 |
 |
 |
| NeTV2, carrying the Device DNA and the name derived from it |
Arty A7-35T, with its Digilent serial and its flash's unique id |
An Acorn CLE-215+ under gateware that hides its PCIe id: named by its die |
 |
||
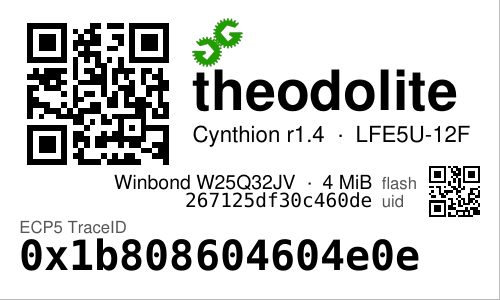
| Cynthion r1.4, an ECP5 board, keyed on the die's TraceID; its flash UID sits below |
||
 |
 |
 |
| TT06 chip on a TT06+ demo board |
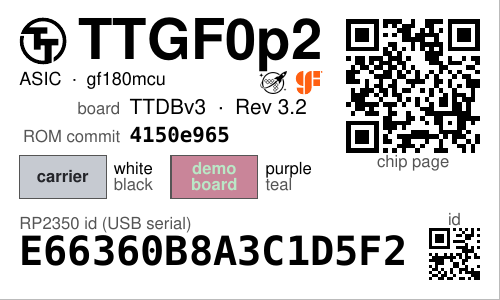
TTGF0p2 on a DBv3 board; wafer.space ran it on GlobalFoundries |
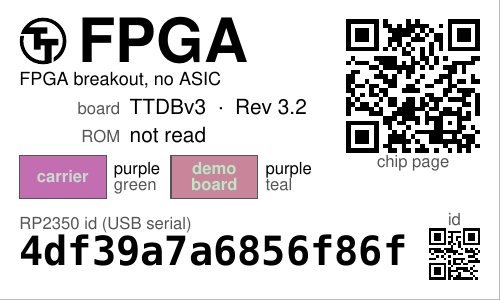
An FPGA breakout standing in for the ASIC, on the same DBv3 board |
 |
 |
 |
| ASIX AX88179 USB 3.0 gigabit adapter |
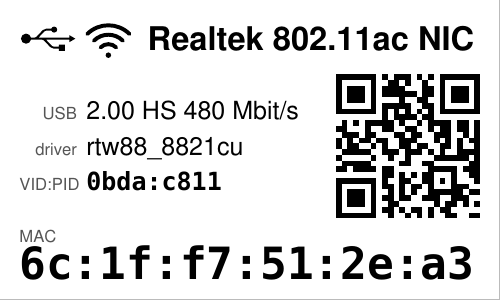
Realtek 802.11ac USB WiFi adapter |
Linksys USB3GIGV1 USB 3.0 gigabit adapter |
Print at 100 % — "fit to page" shrinks the grid and every label lands off its sticker. The layouts band by band, the other options, the derived board names and the artwork are in docs/LABELS.md.
Install
uv tool install 'rpi-hwid[labels]'     # everything, including the label generator
pip install rpi-hwid                   # probe, collector, names: no dependencies at all
Or as a Debian package on Raspberry Pi OS or Debian bookworm, trixie or sid, from the signed apt repository at https://mith.ro/rpi-hwid/ (the page has the three-line setup for each suite):
sudo apt install python3-rpi-hwid # provides the rpi-hwid command
Nothing needs installing on the Pi being probed. The probe is one dependency-free
file that runs on any python3 3.5 or later, so it can be sent over ssh on stdin:
ssh pi@host 'python3 -' < src/rpi_hwid/probe.py
ssh pi@host 'python3 - --json' < src/rpi_hwid/probe.py
On the Pi it wants passwordless sudo for the firmware tools (dtparam and
vcgencmd). The 40-pin header is read straight from /dev/i2c-*, so it needs
neither sudo nor i2c-tools — only membership of the i2c group. Without any
of it the probe still reports what it can.
Quick start
A Pi 5 powered through a PoE splitter, with a USB Ethernet adapter:
$ rpi-hwid probe
Raspberry Pi 5 Model B Rev 1.0  serial d88100008543dc30  rev c04170
  header : nothing identifiable on the header
  signal : USB-C as the firmware sees it: max_current 900 mA, no PD contract; 5 V input 4.83 V
  signal : fan header: disabled
  signal : RTC battery: none (0.00 V)
  signal : power port: throttled=0x0
  power  : external supply on USB-C advertising 900 mA by resistor: a PoE splitter or a USB-A lead
  onboard: eth    2c:cf:67:16:bd:98  macb
  onboard: wlan   2c:cf:67:16:bd:99  brcmfmac
  usb net: 0b95:1790 ASIX Elec. Corp. AX88179  00:0e:c6:82:b5:e1  ethernet
Revision codes decode offline, on any machine:
$ rpi-hwid revision c04170 9000c1 a020d3
c04170: Raspberry Pi 5, 4 GB, Rev 1.0, BCM2712
9000c1: Raspberry Pi Zero W, 512 MB, Rev 1.1, BCM2835
a020d3: Raspberry Pi 3 Model B+, 1 GB, Rev 1.3, BCM2837
The commands
rpi-hwid probe [--json] [--fpga] [--jtag] [--flash] [--tinytapeout]
                                                      on a Pi: what is this?
rpi-hwid fpga [--json] [--jtag] [--flash]             on a Pi: which FPGA board?
rpi-hwid tinytapeout [--json] [--no-repl]             on a Pi: which Tiny Tapeout board?
rpi-hwid collect --out DIR [-J JUMP] [--fpga] [--tinytapeout] HOST…
                                                      over ssh: one JSON per host
rpi-hwid labels --data DIR --out labels.pdf           print-ready labels from that data
rpi-hwid name --netv2 DNA… | --arty SERIAL…           the derived board names
rpi-hwid revision CODE…                               decode Pi revision codes
Reference
- docs/PROBE.md — what each signal proves, how the power verdict is reached, the Orange Pi, and the FPGA and Tiny Tapeout modules.
- docs/COLLECT.md — collecting a fleet over ssh, the JSON document the rest of the package consumes, and reading it from Python.
- docs/LABELS.md — the derived names, the five label layouts, the label options and the artwork.
- docs/DEVELOPING.md — contributor notes.
- RELEASING.md — how a version reaches PyPI and apt.
Development
uv sync --all-extras --group dev
uv run ruff check && uv run mypy && uv run pytest
The rest — the Python 3.5 rule for the probe files, what the tests need installed, regenerating the images, building the Debian package — is in docs/DEVELOPING.md, and how a version reaches PyPI and apt is in RELEASING.md.
Origin
Worked out on a fleet of Pi Zero W, 3B+, 4 and 5 hosts carrying NeTV2, Acorn and Arty boards, powered by a mix of Waveshare PoE HATs and external PoE splitters, plus Orange Pi PCs on the welland.fpgas.online pool, in September 2026. The rules above are what those boards showed; a board that behaves differently is a bug report. The Tiny Tapeout module was written from the SDK's public sources (tt-micropython-firmware, tt-demo-pcb, tt-support-tools) and tested against an emulated board; a report from a real demo board is welcome.
1 maintainer

Release files for rpi-hwid 0.0.post178
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| rpi_hwid-0.0.post178.tar.gz | 1.2 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| rpi_hwid-0.0.post178-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.4 MB
Release files / rpi_hwid-0.0.post178.tar.gz
| Download URL | rpi_hwid-0.0.post178.tar.gz |
|---|---|
| Size | 1.2 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
c990ef5c19562a02d2aa58debfad3214c495deb75be5f67093f678d6dd2a488d
|
|
BLAKE2b-256 checksum How to use checksums |
6a81669be180e902674787fafd9f585f9dd72ae9b12cda4e222e981fcc994acb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 24, 2026.
Transparency logRelease files / rpi_hwid-0.0.post178-py3-none-any.whl
| Download URL | rpi_hwid-0.0.post178-py3-none-any.whl |
|---|---|
| Size | 229.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
695fad9f8982bf3d784d511947fe28f51a080787d8f6710492b2040df4455a8e
|
|
BLAKE2b-256 checksum How to use checksums |
df34faaaac1ddd30d79eba0e8d10c0151b0d5dec7e7a9a0605c0d572aaca29f3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 24, 2026.
Transparency log













