


sanger
A lightweight toolkit for Sanger sequencing data: chromatogram visualization, alignment & mutation calling, quality control, base-calling, trimming, assembly and export — usable as a CLI, a Python library, or an MCP server for LLM agents.
Quick start
pip install sanger
sanger mut -q read.ab1 -s ref.fa -o out --plot
from sanger import Chromatogram, parse_fasta

cg = Chromatogram.from_abi("./data/B5-M13R_B07.ab1")
print(cg.length, cg.mean_quality, cg.gc_percent)   # 1141 50.2 52.0
ref = parse_fasta("./data/ref.fa")
print(cg.qc())                                    # QC metrics (CRL, SNR)
print(cg.to_vcf(ref))                             # variant calling -> VCF
cg.plot(region=(55, 90))                          # render a region
Examples
The gallery below is produced from the bundled real ABI sample
(data/B5-M13R_B07.ab1 vs data/ref.fa) by python -m scripts.make_readme_examples.
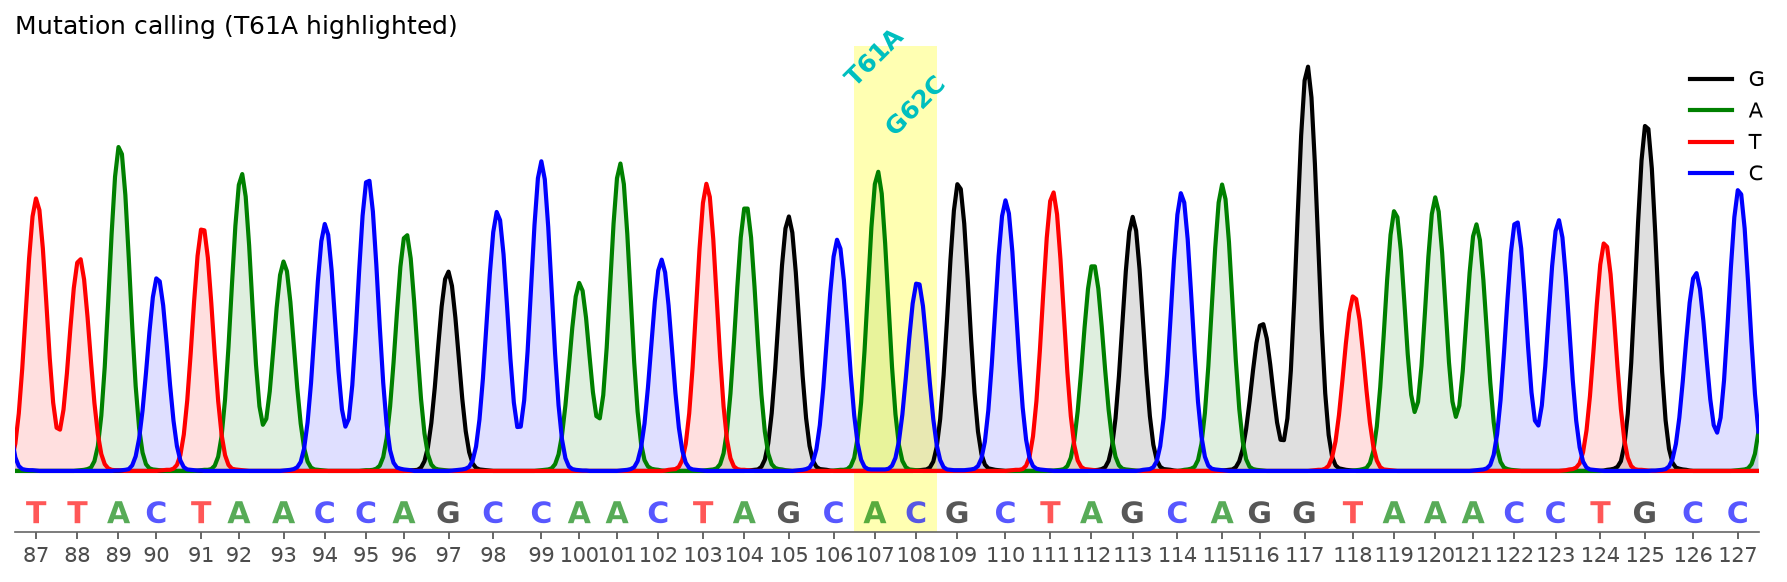
Mutation calling — the SNP T61A is highlighted and annotated.
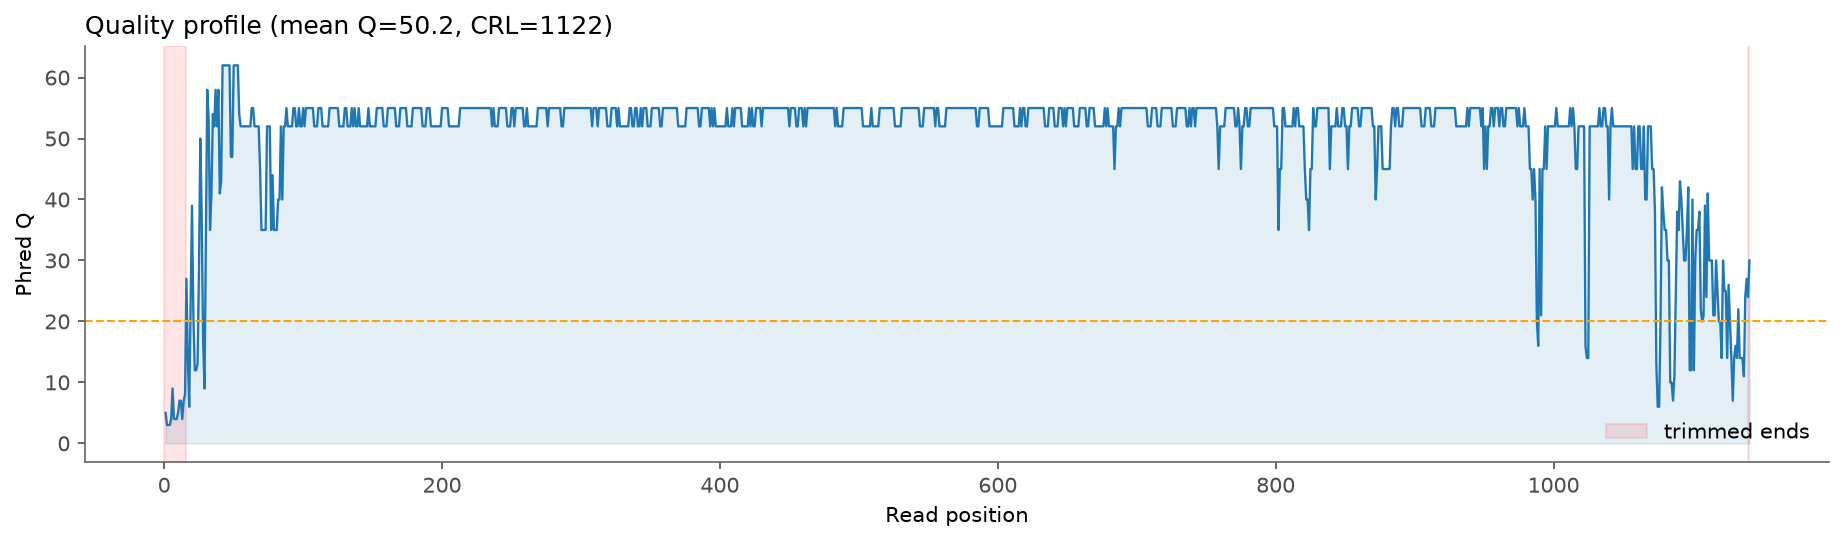
Quality control — per-base Phred quality, CRL and Mott trimming.
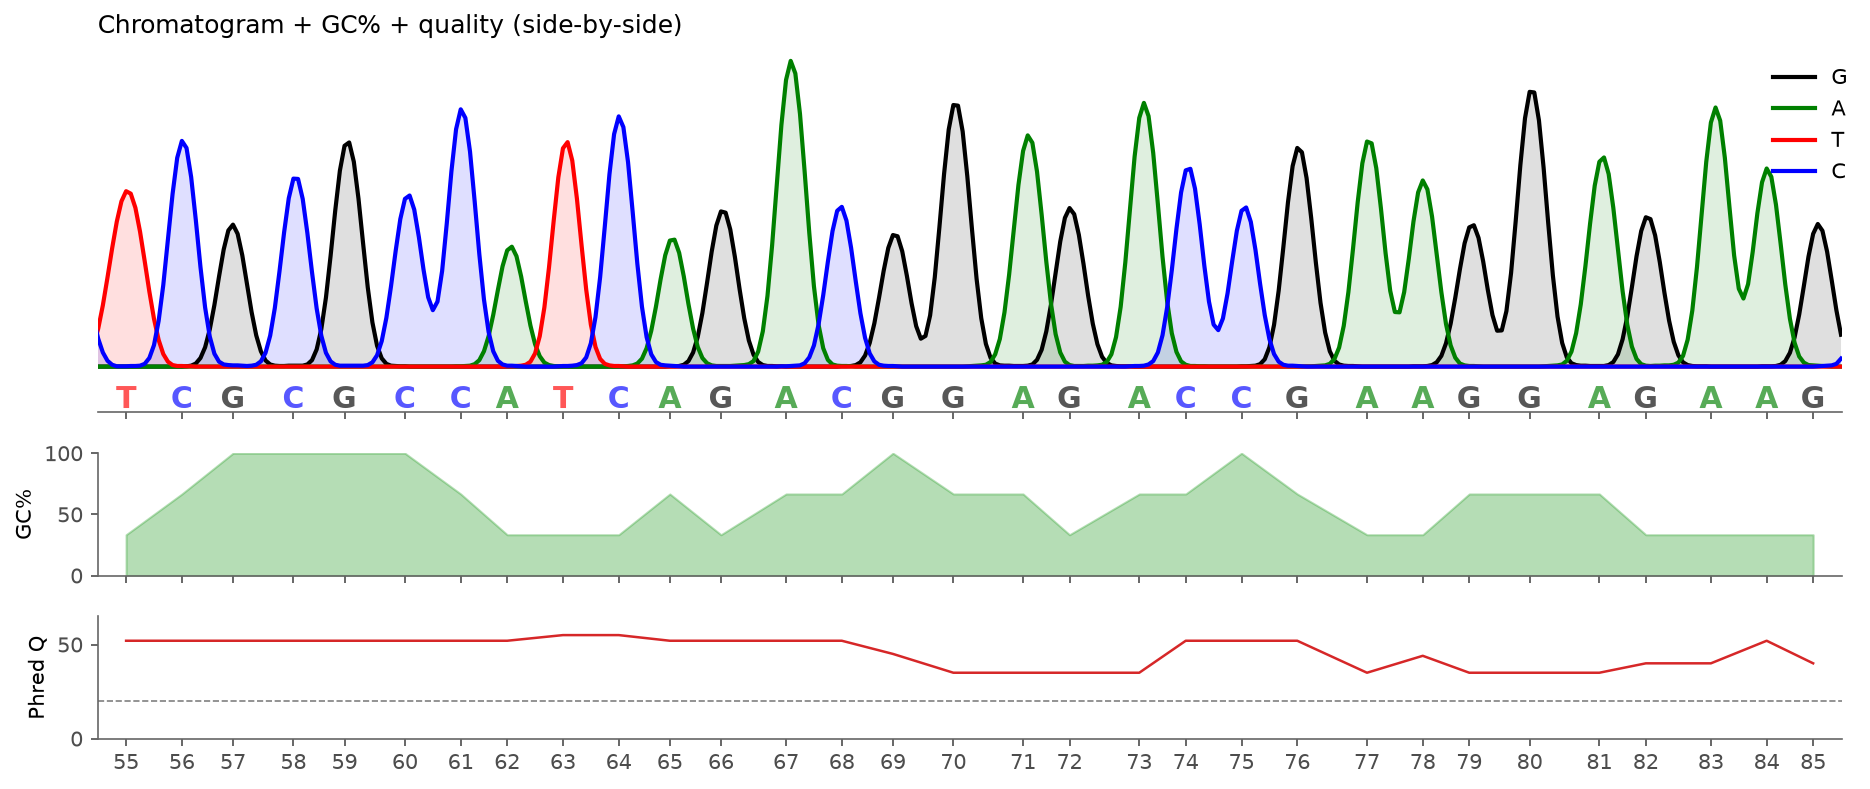
Side-by-side panels — chromatogram + GC% + quality on a shared axis.
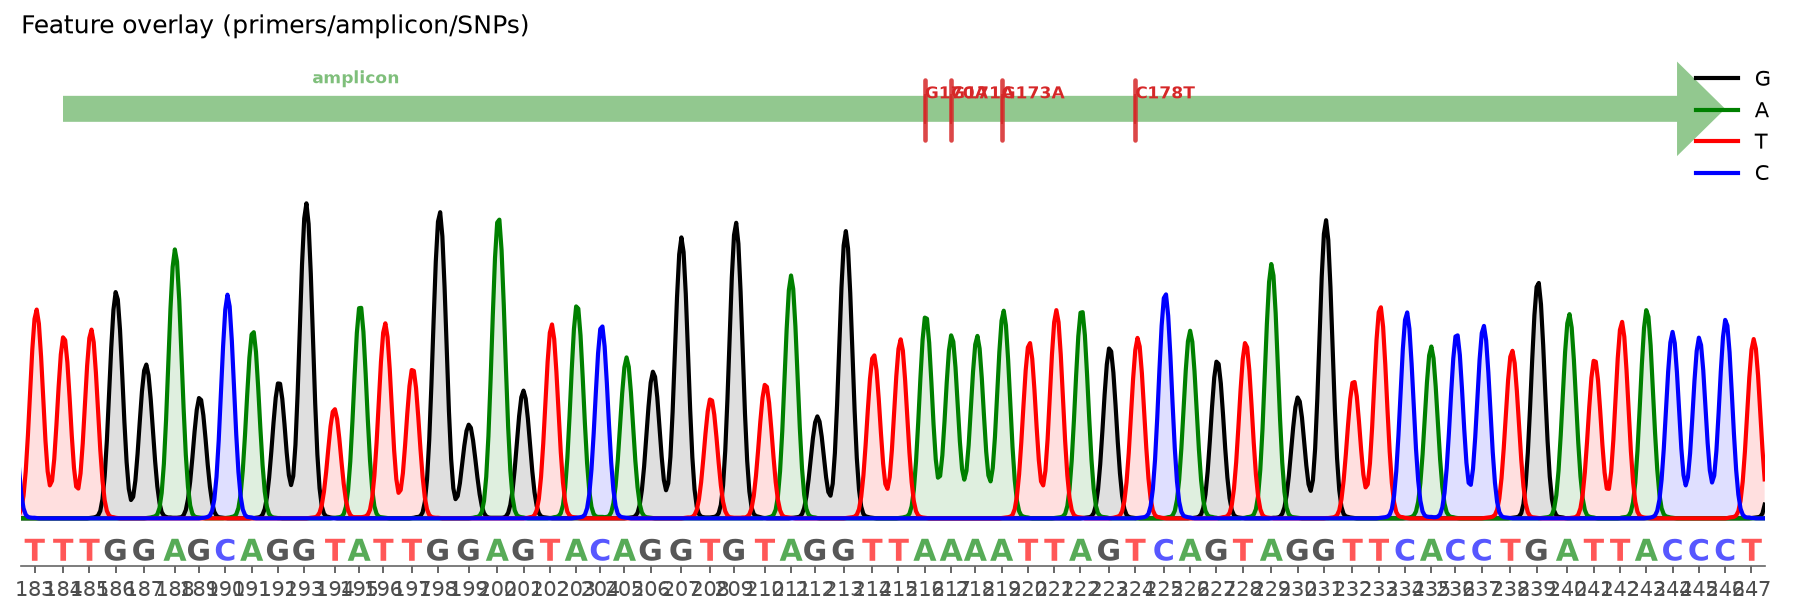
Feature overlay — primers, amplicon and SNPs on the trace.
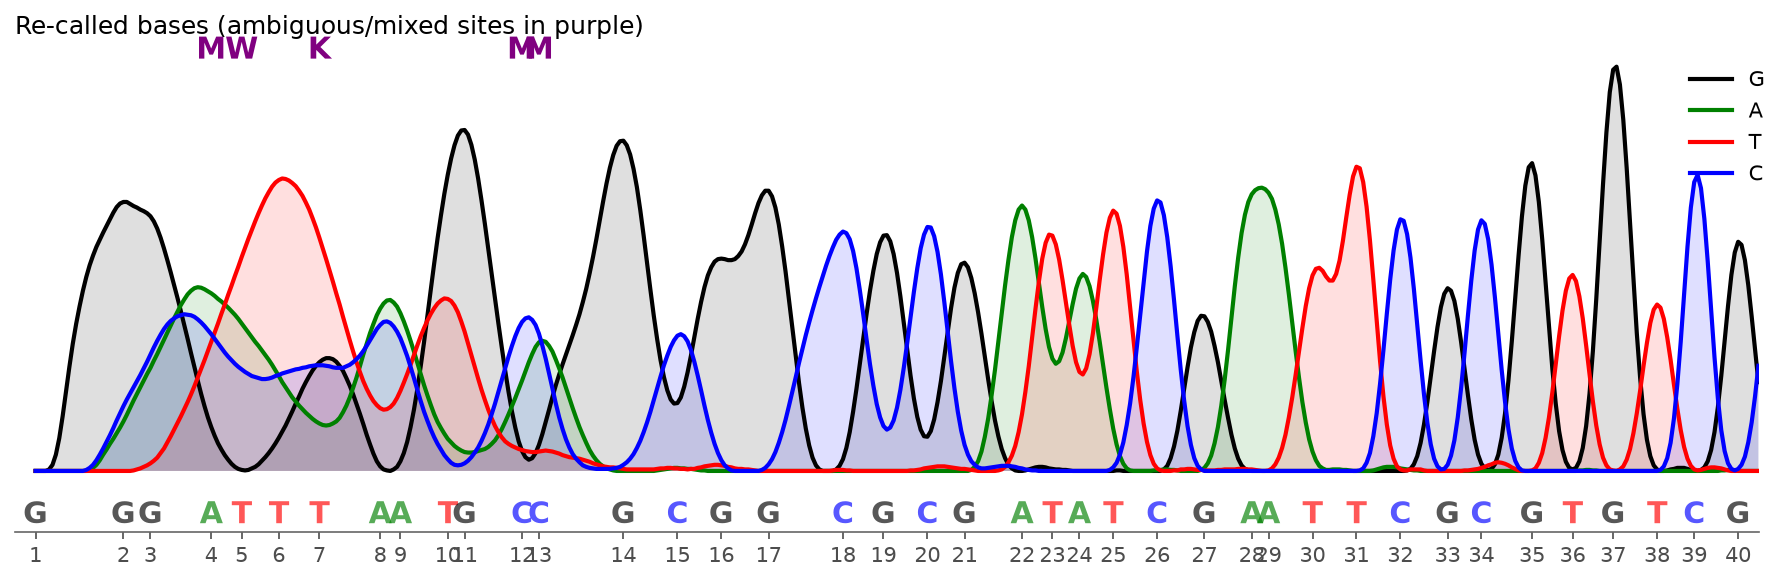
Re-called bases — mixed/heterozygous sites are marked (M/W/K).
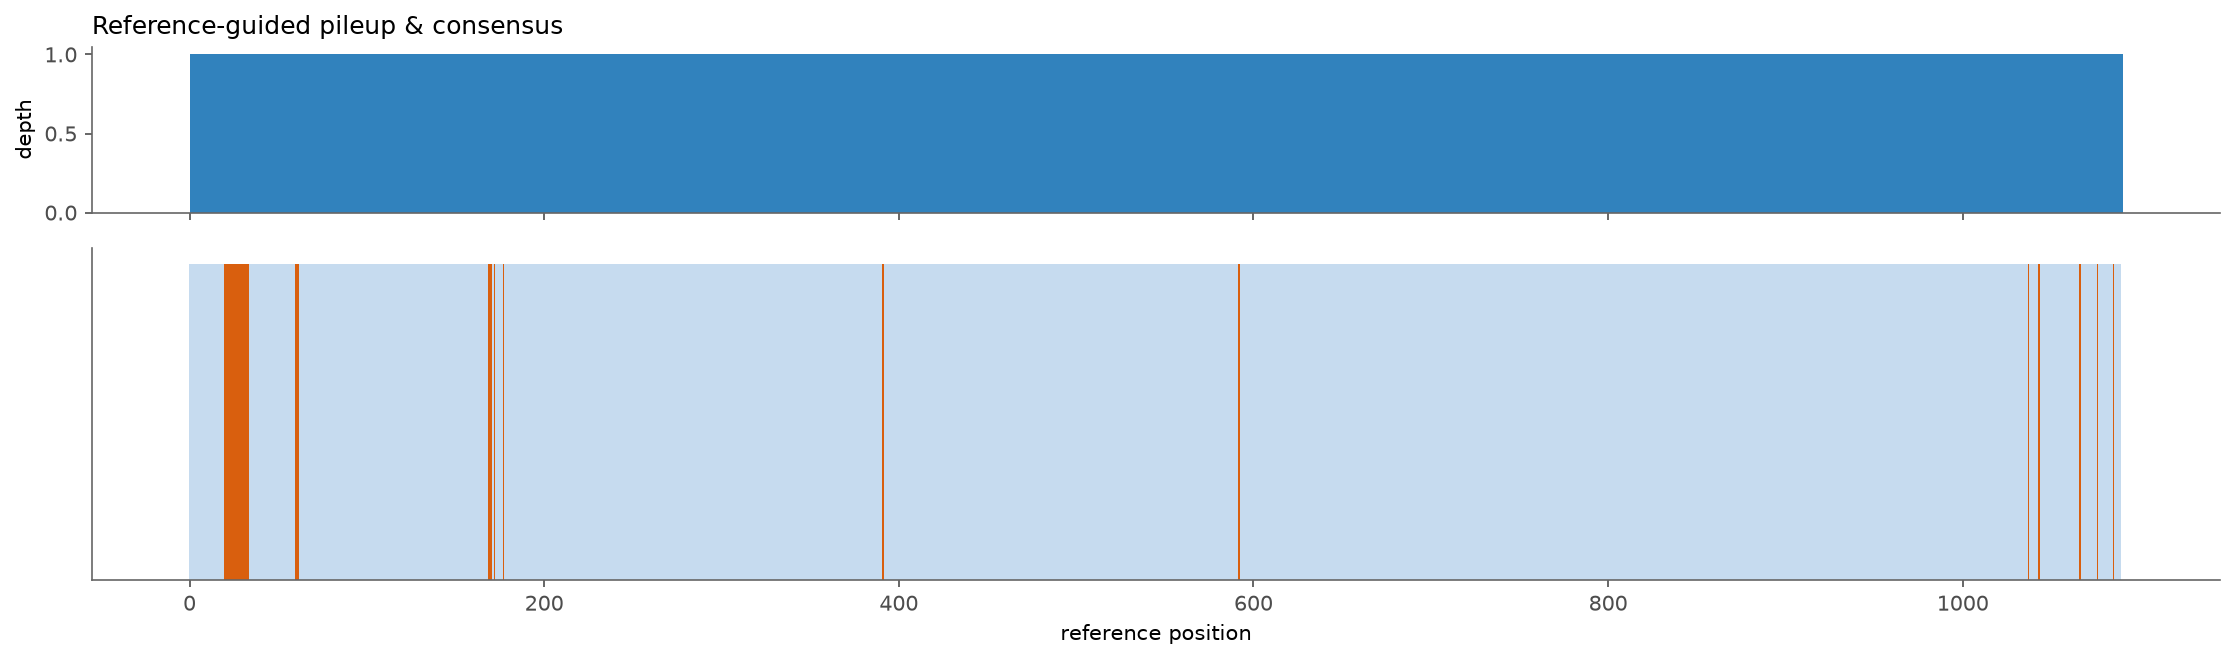
Assembly — pileup depth and consensus against a reference.
Installation
The default install pulls only numpy, click and rich-click — no C
compiler and no plotting library required. Parsing, QC, alignment (a bundled
Cython Smith-Waterman with a NumPy fallback), analysis and export all work out
of the box.
pip install sanger
Optional extras:
pip install "sanger[plot]"     # matplotlib -> chromatogram figures
pip install "sanger[viewer]"   # DNA Features Viewer integration
pip install "sanger[agent]"    # MCP server for LLM agents
pip install "sanger[all]"      # everything
The bundled Cython Smith-Waterman accelerator (sanger._swalign,
self-contained, no ssw dependency) is compiled automatically when a C
compiler is present at build time; otherwise the NumPy fallback is used.
From source:
git clone git@github.com:y9c/sanger.git
cd sanger
make init       # install dependencies
make test       # run the test-suite
Command-line interface
Built on rich-click, with themed command groups (sanger --help):
sanger mut            mutation calling & reporting
sanger qc             per-read quality-control metrics
sanger track          split / join / slice chromatogram trace files
sanger edit           trim, strip primers, reverse-complement
sanger basecall       re-call bases from raw four-channel traces
sanger assemble       reference-guided pileup & consensus
sanger analyze        sequence biology (translate, motifs, restriction)
sanger export         FASTA / VCF / JSON / batch summary
sanger plot           chromatogram rendering (+ features / DNA viewer)
Examples:
sanger mut -q read.ab1 -s ref.fa -o out --plot        # mutation report + figure
sanger qc r1.ab1 r2.ab1                               # QC table
sanger track split read.ab1 -c 20,40 -f tsv           # split traces
sanger edit trim read.ab1 -c 0.05 -o out              # Mott quality trim
sanger edit strip-primers read.ab1 -f AAAA -r CCCA    # primer removal
sanger basecall call read.ab1 -r 0.45                 # re-call bases
sanger basecall hetero read.ab1                       # mixed/heterozygous sites
sanger assemble consensus a.ab1 b.ab1 -r ref.fa       # reference-guided consensus
sanger analyze rest read.ab1                          # restriction sites
sanger analyze translate read.ab1 -f 1                # protein translation
sanger export vcf -q read.ab1 -s ref.fa               # VCF of variants
sanger export batch *.ab1 -o out -f csv               # batch QC table
sanger plot dnaviewer read.ab1 --start 50 --end 100   # with DNA Features Viewer
Python API
The high-level Chromatogram object is the easiest way
to work with the toolkit; the low-level modules remain available for custom work.
from sanger import Chromatogram, parse_fasta

cg = Chromatogram.from_abi("./data/B5-M13R_B07.ab1")
ref = parse_fasta("./data/ref.fa")
Common operations
Mutation calling & quality filtering
from sanger.quality import QualityFilter

snps = cg.call_mutations(ref)
confident = QualityFilter(min_base_qual=20, min_local_qual=20).filter(snps)
print([f"{s.ref_base}{s.ref_pos}{s.cf_base}" for s in confident])
QC metrics (incl. continuous read length)
m = cg.qc()
print(m["mean_qual"], m["trim_start"], m["trim_end"], m["crl"], m["snr"])
Re-call bases from raw traces + mixed/heterozygous sites
res = cg.basecall()
print(res.sequence)
for pos, major, minor, frac in res.heterozygotes(min_ratio=0.2):
    print(pos, major, minor, frac)
Trim / reverse-complement / orientation
trimmed = cg.trim().trim_leading_ns()     # Mott trim then drop leading Ns
rc      = cg.reverse_complement()
ori     = cg.detect_orientation(ref)      # +1 forward, -1 reverse-complement
Sequence-level analysis
print(cg.analyze("translate", frame=1))            # protein translation
print(cg.analyze("restriction"))                    # {'EcoRI': [27], ...}
print(cg.analyze("motif", motif="AATT"))            # motif positions
Export
print(cg.to_fasta())
print(cg.to_vcf(ref))
cg.export("out")                                    # write FASTA to disk
Feature overlay (for external tools)
from sanger import ChromatogramFeature
from sanger.features import plot_features

feat = ChromatogramFeature(start=90, end=130, strand=+1, label="primer F")
fig, ax = cg.plot(region=(80, 140))
plot_features(cg.to_record, ax, features=[feat])
Side-by-side with another tool's output (shared x-axis)
from sanger.composite import side_by_side

def my_panel(ax, trace_x, peaks, seq, record, start=None):
    ax.bar(range(len(seq)), [1.0] * len(seq), color="0.66")
    ax.set_ylabel("my tool signal")

fig, (ax_chrom, ax_panel) = side_by_side(cg.to_record, my_panel, region=(10, 40))
Consensus / assembly from many reads
from sanger import parse_abi
from sanger.assembly import pileup, consensus

reads = [parse_abi(f) for f in ["a.ab1", "b.ab1", "c.ab1"]]
table = pileup(reads, ref, quality_threshold=20)
print(consensus(table))
Plot together with DNA Features Viewer (needs sanger[viewer])
from sanger import ChromatogramFeature
from sanger.dnalink import plot_combined

feats = [ChromatogramFeature(start=90, end=130, strand=+1, label="primer F")]
fig, (ax_feat, ax_chrom) = plot_combined(cg.to_record, features=feats, region=(55, 90))
Chromatogram object
A terse, idiomatic workflow in one object:
from sanger import Chromatogram

cg = Chromatogram.from_abi("./data/B5-M13R_B07.ab1")
cg.length, cg.mean_quality, cg.gc_percent, cg.channels   # 1141 50.2 52.0 GATC
cg.qc()                            # QC metrics (CRL, SNR)
cg.basecall()                      # re-call bases from raw traces
cg.call_mutations(ref)             # variant calling
cg.trim().trim_leading_ns()        # quality trimming
cg.reverse_complement()            # reverse-strand view
cg.analyze("restriction")          # restriction-site scan
cg.plot(region=(55, 90))           # render a region
cg.to_fasta(), cg.to_vcf(ref)      # export
cg.export("out")                   # write to disk
Agent / MCP
sanger ships a Model Context Protocol server so LLM agents and MCP clients can call the toolkit as tools:
pip install "sanger[agent]"     # adds mcp>=2
sanger-mcp                        # run the MCP server over stdio
python -m sanger.mcp_server       # identical
| Tool | Purpose |
|---|---|
read_chromatogram(path) |
parse an ABI → summary (length, GC%, quality, CRL) |
qc_metrics(path) |
full per-read QC metrics (incl. CRL, signal, SNR) |
call_mutations(query ab1, subject fa) |
variants vs a reference (SNPs/indels) |
re_call_bases(path) |
re-call bases from raw traces + heterozygotes |
analyze_sequence(path, kind) |
translate / motifs / restriction / GC |
trim_read(path, mode) |
quality-trim a read |
export_sequence(path, outdir) |
write FASTA or VCF |
plot_chromatogram(path, out, start, end) |
render a chromatogram PNG |
Register it in an MCP client's config, e.g.:
{ "mcpServers": { "sanger": { "command": "sanger-mcp" } } }
ChangeLog
- Replace the external
sswaligner with a bundled Cython Smith-Waterman (+ NumPy fallback) — no external alignment dependency. - Reverse-complement the chromatogram file (inspired by Snapgene).
- Add per-base quality filtering, continuous read length (CRL), signal/SNR QC.
- Add base-calling from raw four-channel traces + heterozygote (mixed-base) calling.
- Add feature overlay API and DNA Features Viewer integration.
- Add split / join / slice trace operations with provenance (
offset). - Add reference-guided pileup & consensus (assembly module).
- Add FASTA / VCF / JSON / batch export.
- Fix false-positive mutations from lowercase reference bases (case-insensitive).
- Build the CLI with rich-click (themed groups, short options,
--version).
TODO
- call mutation by alignment and plot Chromatogram graphic
- add a doc
- change x-axis by peak location
- fix bug that chromatogram switches position after trim
- wrap as a CLI app
- return quality score in output (quality module + report)
- fix selected base not being centred (center_region)
- fix
plot_chromatographrendering bug (full-region bounds, channels) - add projection/assembly (assembly module)
- preserve trimmed-origin positions when slicing/joining (offset provenance)
1 maintainer

Metadata
1 maintainer
Release files for sanger 0.1.5
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| sanger-0.1.5.tar.gz | 133.4 kB | With provenance | Details |
Built distributions (wheels)
Total release size: 4.1 MB
Release files / sanger-0.1.5.tar.gz
| Download URL | sanger-0.1.5.tar.gz |
|---|---|
| Size | 133.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5f3c128a60af40f2b8fb50f7e0f90d3143638b2b37289970b78ef8da0df2ceed
|
|
BLAKE2b-256 checksum How to use checksums |
4304cfcf8411cad3fc1a8e0ce066f119da6f7bf9b9a5161d19edabfb0e0728cd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp314-cp314-musllinux_1_2_x86_64.whl
| Download URL | sanger-0.1.5-cp314-cp314-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 245.1 kB |
| Tags | CPython 3.14 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
ccc93df48549695b76b31ddaf967fdd0aac4f0144afa2724fdd7840504d1c0d0
|
|
BLAKE2b-256 checksum How to use checksums |
55e7e136c4a68f3bd4cb1c686bc5582a19b42179c3a597b4cff2dfc3b19d22f9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp314-cp314-manylinux1_x86_64.manylinux_2_28_x86_64.manylinux_2_5_x86_64.whl
| Download URL | sanger-0.1.5-cp314-cp314-manylinux1_x86_64.manylinux_2_28_x86_64.manylinux_2_5_x86_64.whl |
|---|---|
| Size | 245.2 kB |
| Tags | CPython 3.14 Linux glibc 2.28+ x86-64 Linux glibc 2.5+ x86-64 |
|
SHA-256 checksum How to use checksums |
982961e2b1469d9b97fb621972efdb7f2d1e2cd58016c2f42a054a40050837fb
|
|
BLAKE2b-256 checksum How to use checksums |
9b5914cb557315314a336c922f1879e0b929956f372d0ea8724482fe41ffb42b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp314-cp314-macosx_11_0_arm64.whl
| Download URL | sanger-0.1.5-cp314-cp314-macosx_11_0_arm64.whl |
|---|---|
| Size | 152.0 kB |
| Tags | CPython 3.14 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
1ebafdbfd64f286c4f6c51c9cf1d75073d6f6525407b98252bf2580a530067d5
|
|
BLAKE2b-256 checksum How to use checksums |
f2e88b921e3b1b5416d731d8cd7cbedb5bfb8af43cdd8ccb94137a4444c510f5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp314-cp314-macosx_10_15_x86_64.whl
| Download URL | sanger-0.1.5-cp314-cp314-macosx_10_15_x86_64.whl |
|---|---|
| Size | 151.2 kB |
| Tags | CPython 3.14 macOS 10.15+ x86-64 |
|
SHA-256 checksum How to use checksums |
6a84813570495f2f8bf5025615b62a05da2300588d1fe2cc2e377e5498f59c54
|
|
BLAKE2b-256 checksum How to use checksums |
29a80baeb43bf227d312fb9037550fa1ed1371af07c635d0a005b3f2b7f41c96
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp313-cp313-musllinux_1_2_x86_64.whl
| Download URL | sanger-0.1.5-cp313-cp313-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 246.0 kB |
| Tags | CPython 3.13 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
e51f2925a77c84a318cf554bb0a687ae6a89777d493c26f3d3a1cda520feeb90
|
|
BLAKE2b-256 checksum How to use checksums |
2dbdc334669994453e0ef6c1132ebb1b1a9633a57547350bb16511713a0fce76
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp313-cp313-manylinux1_x86_64.manylinux_2_28_x86_64.manylinux_2_5_x86_64.whl
| Download URL | sanger-0.1.5-cp313-cp313-manylinux1_x86_64.manylinux_2_28_x86_64.manylinux_2_5_x86_64.whl |
|---|---|
| Size | 246.2 kB |
| Tags | CPython 3.13 Linux glibc 2.28+ x86-64 Linux glibc 2.5+ x86-64 |
|
SHA-256 checksum How to use checksums |
70698c94a5b010c1e58ab4b810e8043a7146c84a4e1ea6f0e031f831cb6b853e
|
|
BLAKE2b-256 checksum How to use checksums |
661890043bdae37e243bc6ed3606d8e4a4701daaf8bfcbc4864ef61e7f483dd7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp313-cp313-macosx_11_0_arm64.whl
| Download URL | sanger-0.1.5-cp313-cp313-macosx_11_0_arm64.whl |
|---|---|
| Size | 151.8 kB |
| Tags | CPython 3.13 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
73a0fd77d725611fb3222178926a27cdbbe4a4cc663f8cb2fd9fb22ea36f022a
|
|
BLAKE2b-256 checksum How to use checksums |
cab3d54ffcce3b85bcc9ce9da25e3eedd9f95cb1cd10a91dcbe2a28daecba698
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp313-cp313-macosx_10_13_x86_64.whl
| Download URL | sanger-0.1.5-cp313-cp313-macosx_10_13_x86_64.whl |
|---|---|
| Size | 151.1 kB |
| Tags | CPython 3.13 macOS 10.13+ x86-64 |
|
SHA-256 checksum How to use checksums |
d7e49580297469c674fb1270a0bb0b80f95098ade53cad756cf2f2445e288124
|
|
BLAKE2b-256 checksum How to use checksums |
e3d9566a556b6f92cfb1faae5ab33019c1b0ef5d7bf7649bac513c920c017e7d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp312-cp312-musllinux_1_2_x86_64.whl
| Download URL | sanger-0.1.5-cp312-cp312-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 249.3 kB |
| Tags | CPython 3.12 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
33641b5db05f8b1814477b040250618933175b04af9ab8e52053dfd917c1e3fc
|
|
BLAKE2b-256 checksum How to use checksums |
08dbca2ac99a3e86273572bd07f35779ccb5d799202baf0f0234876ee6112e8d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp312-cp312-manylinux1_x86_64.manylinux_2_28_x86_64.manylinux_2_5_x86_64.whl
| Download URL | sanger-0.1.5-cp312-cp312-manylinux1_x86_64.manylinux_2_28_x86_64.manylinux_2_5_x86_64.whl |
|---|---|
| Size | 249.5 kB |
| Tags | CPython 3.12 Linux glibc 2.28+ x86-64 Linux glibc 2.5+ x86-64 |
|
SHA-256 checksum How to use checksums |
ce0ef5f710c404c5b5e2a3685a8cdb99033d8f479bc00cb0bc0ca01cd311aa76
|
|
BLAKE2b-256 checksum How to use checksums |
338eba3d8894be8b6457a5097a96865c5887483e8778cd3193df800199be70f3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp312-cp312-macosx_11_0_arm64.whl
| Download URL | sanger-0.1.5-cp312-cp312-macosx_11_0_arm64.whl |
|---|---|
| Size | 152.3 kB |
| Tags | CPython 3.12 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
a88636ad5ec7c3f2f315af44011053695ec0495e750b0c398b71514c932bfce2
|
|
BLAKE2b-256 checksum How to use checksums |
6c42a76cfc3faa76be59d6483109e4c78d8bb05989af15be1f8a3439d6a31e66
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp312-cp312-macosx_10_13_x86_64.whl
| Download URL | sanger-0.1.5-cp312-cp312-macosx_10_13_x86_64.whl |
|---|---|
| Size | 151.5 kB |
| Tags | CPython 3.12 macOS 10.13+ x86-64 |
|
SHA-256 checksum How to use checksums |
ac8d9b770a7455822e650c7f2d2a85d93f81e8886bdbe8bde72e72b03a169ca3
|
|
BLAKE2b-256 checksum How to use checksums |
36b7b111a2aaa9a3210711e447ef0e58eb0c36a1a60e4df68f2c539f3b161b7e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp311-cp311-musllinux_1_2_x86_64.whl
| Download URL | sanger-0.1.5-cp311-cp311-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 242.2 kB |
| Tags | CPython 3.11 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
62f042e09c2587d08fa4d27669230841315f4a792f4a4f2a8104951b2b11ce68
|
|
BLAKE2b-256 checksum How to use checksums |
3c797cbe5b39da6b8bc6b3c246b100d9747c94852c624b8b9d7faf756b348cfd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp311-cp311-manylinux1_x86_64.manylinux_2_28_x86_64.manylinux_2_5_x86_64.whl
| Download URL | sanger-0.1.5-cp311-cp311-manylinux1_x86_64.manylinux_2_28_x86_64.manylinux_2_5_x86_64.whl |
|---|---|
| Size | 242.3 kB |
| Tags | CPython 3.11 Linux glibc 2.28+ x86-64 Linux glibc 2.5+ x86-64 |
|
SHA-256 checksum How to use checksums |
22052d6bf9fce62530aca6586fb690af58d5dbdebade43b684ecf04c091bfb9e
|
|
BLAKE2b-256 checksum How to use checksums |
395ecea24e176d8c52ae5aa554bf514996babff1e3db9d6a2a5bae30529f28f7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp311-cp311-macosx_11_0_arm64.whl
| Download URL | sanger-0.1.5-cp311-cp311-macosx_11_0_arm64.whl |
|---|---|
| Size | 152.5 kB |
| Tags | CPython 3.11 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
efd1263f0c18a8106be476c615ce442ac6138ab97bd2e817d479b38fe274d829
|
|
BLAKE2b-256 checksum How to use checksums |
2751293d0d10c0daf85b4cfb3e9ced40e6a13c61523d92db28ba9ea6bc7739a6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp311-cp311-macosx_10_9_x86_64.whl
| Download URL | sanger-0.1.5-cp311-cp311-macosx_10_9_x86_64.whl |
|---|---|
| Size | 151.1 kB |
| Tags | CPython 3.11 macOS 10.9+ x86-64 |
|
SHA-256 checksum How to use checksums |
9f804fd3ef414ecf9e168ac6c27a490d0dffc9de8dea8a4f0aead24131d74058
|
|
BLAKE2b-256 checksum How to use checksums |
4da3a061f488bb67bc433344d269239c03b4a6a3763e5d3a2e46678b1d79f76e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp310-cp310-musllinux_1_2_x86_64.whl
| Download URL | sanger-0.1.5-cp310-cp310-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 237.1 kB |
| Tags | CPython 3.10 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
eba8012d3368f0682fdfea4cf5af056c1fbfce9d031a700ea7e012d78a91be45
|
|
BLAKE2b-256 checksum How to use checksums |
717e6dff801536e54b6985e1104a25c1e845ac43314aa86235aa98ed7a7fc513
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp310-cp310-manylinux1_x86_64.manylinux_2_28_x86_64.manylinux_2_5_x86_64.whl
| Download URL | sanger-0.1.5-cp310-cp310-manylinux1_x86_64.manylinux_2_28_x86_64.manylinux_2_5_x86_64.whl |
|---|---|
| Size | 237.5 kB |
| Tags | CPython 3.10 Linux glibc 2.28+ x86-64 Linux glibc 2.5+ x86-64 |
|
SHA-256 checksum How to use checksums |
a85b1dcc21eee4f71bd91df14cc6fb896418c64bc8e2beaf0982d9f0933d8e40
|
|
BLAKE2b-256 checksum How to use checksums |
b9d9b92b95bc9938178111c487d79fdc230578dccb901a428a4410973f7275af
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp310-cp310-macosx_11_0_arm64.whl
| Download URL | sanger-0.1.5-cp310-cp310-macosx_11_0_arm64.whl |
|---|---|
| Size | 152.9 kB |
| Tags | CPython 3.10 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
3bc0c95e7ff93af9dfbdf0def8030b40871192bc4ee2688a66c038c78a9958ba
|
|
BLAKE2b-256 checksum How to use checksums |
c434ac8f27d3e04993279b14ab653d4a07af322147b8e7c1e92ed114d6082225
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logRelease files / sanger-0.1.5-cp310-cp310-macosx_10_9_x86_64.whl
| Download URL | sanger-0.1.5-cp310-cp310-macosx_10_9_x86_64.whl |
|---|---|
| Size | 151.5 kB |
| Tags | CPython 3.10 macOS 10.9+ x86-64 |
|
SHA-256 checksum How to use checksums |
2f4c5d9c7e452b4d2a831dee9909e10a6f627d36b3ac23e8d7be0388cd089b67
|
|
BLAKE2b-256 checksum How to use checksums |
a9954c93b7310daefad54395d5ceeb2c588141ff8122661b193140584f976cdc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logSecurity for sanger 0.1.5
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 21 files in this release have been uploaded with provenance metadata.
Attestation for sanger-0.1.5.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 27, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














