

Code scanning at ludicrous speed.


Semgrep is a fast, open-source, static analysis tool that searches code, finds bugs, and enforces secure guardrails and coding standards. Semgrep supports 30+ languages and can run in an IDE, as a pre-commit check, and as part of CI/CD workflows.
Semgrep is semantic grep for code. While running grep "2" would only match the exact string 2, Semgrep would match x = 1; y = x + 1 when searching for 2. Semgrep rules look like the code you already write; no abstract syntax trees, regex wrestling, or painful DSLs.
Note that in security contexts, Semgrep Community Edition will miss many true positives as it can only analyze code within the boundaries of a single function or file. If you want to use Semgrep for security purposes (SAST, SCA, or secrets scanning), the Semgrep AppSec Platform is strongly recommended since it adds the following critical capabilities:
- Improved core analysis capabilities (cross-file, cross-function, data-flow reachability) that greatly reduce false positives by 25% and increase detected true positives by 250%
- Contextual post-processing of findings with Semgrep Assistant (AI) to further reduce noise by ~20%. In addition, Assistant enriches findings with tailored, step-by-step remediation guidance that humans find actionable >80% of the time.
- Customizable policies and seamless integration into developer workflows, giving security teams granular control over where, when, and how different findings are presented to developers (IDE, PR comment, etc.)
The Semgrep AppSec Platform works out-of-the-box with 20000+ proprietary rules across SAST, SCA, and secrets. Pro rules are written and maintained by the Semgrep security research team and are highly accurate, meaning AppSec teams can feel confident bringing findings directly to developers without slowing them down.
Semgrep analyzes code locally on your computer or in your build environment: by default, code is never uploaded. Get started →.
Language support
Semgrep Code supports 30+ languages, including:
Apex · Bash · C · C++ · C# · Clojure · Dart · Dockerfile · Elixir · HTML · Go · Java · JavaScript · JSX · JSON · Julia · Jsonnet · Kotlin · Lisp · Lua · OCaml · PHP · Python · R · Ruby · Rust · Scala · Scheme · Solidity · Swift · Terraform · TypeScript · TSX · YAML · XML · Generic (ERB, Jinja, etc.)
Semgrep Supply Chain supports 12 languages across 15 package managers, including:
C# (NuGet) · Dart (Pub) · Go (Go modules, go mod) · Java (Gradle, Maven) · Javascript/Typescript (npm, Yarn, Yarn 2, Yarn 3, pnpm) · Kotlin (Gradle, Maven) · PHP (Composer) · Python (pip, pip-tool, Pipenv, Poetry) · Ruby (RubyGems) · Rust (Cargo) · Scala (Maven) · Swift (SwiftPM)
For more information, see Supported languages.
Getting started 🚀
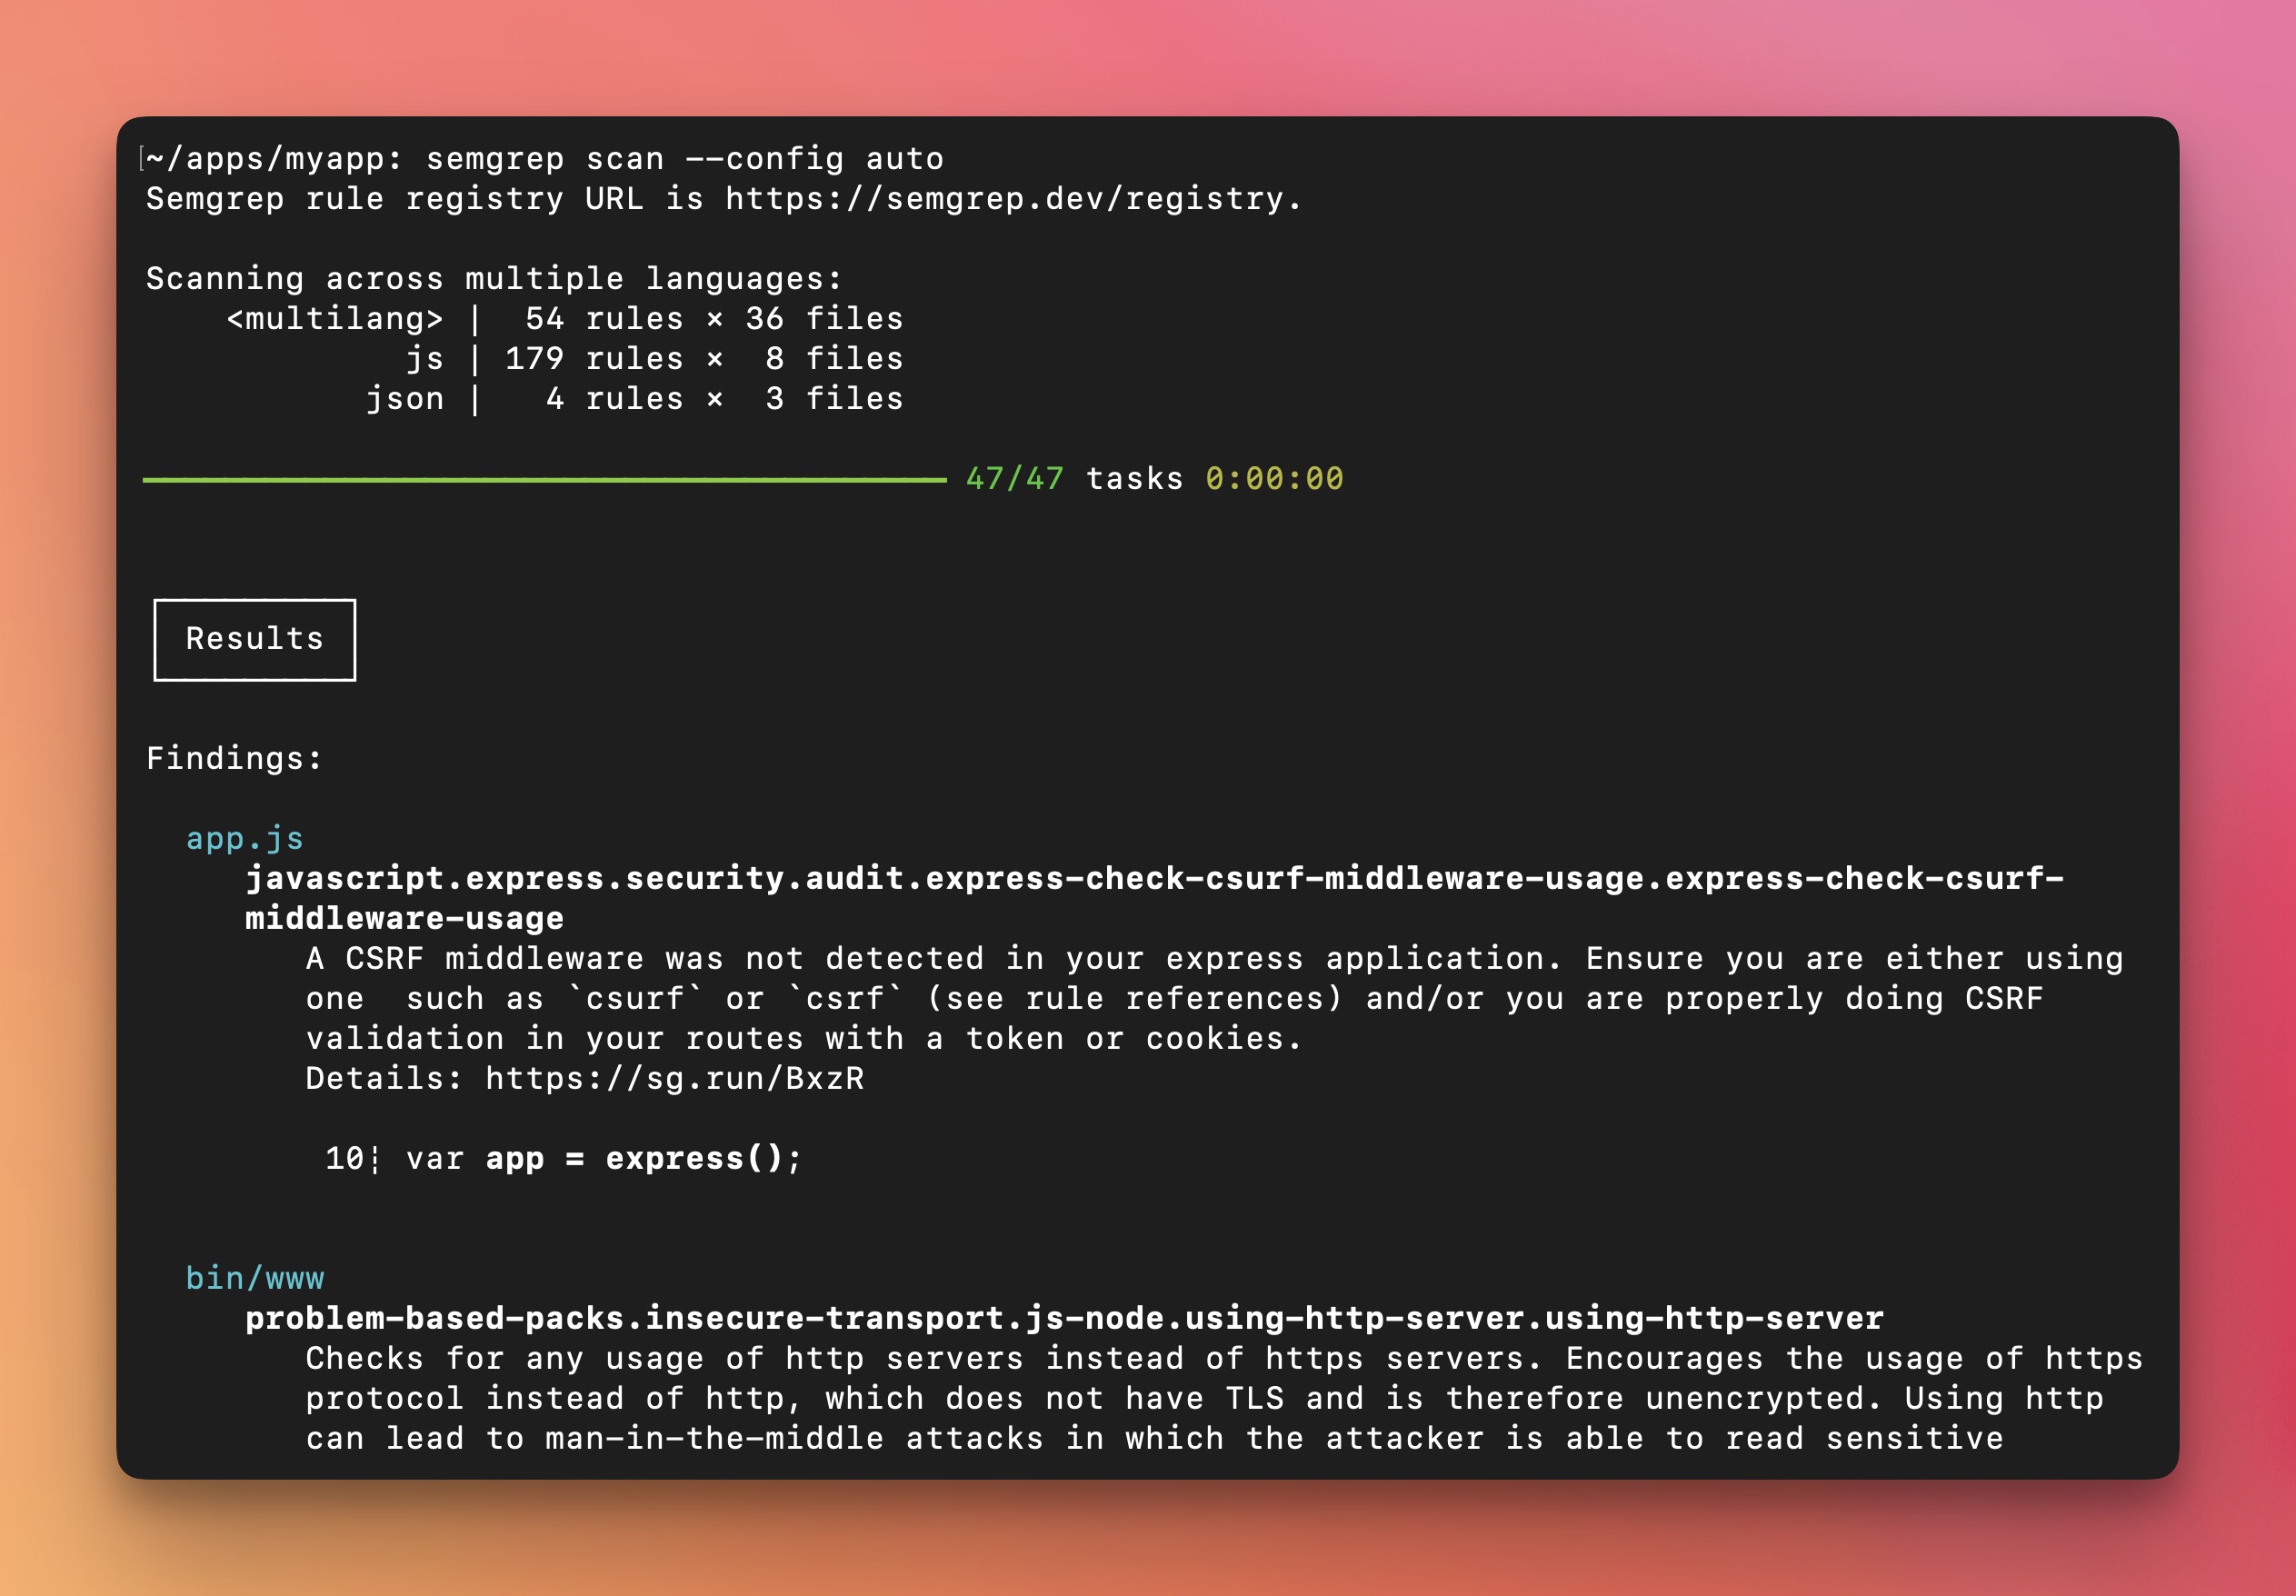
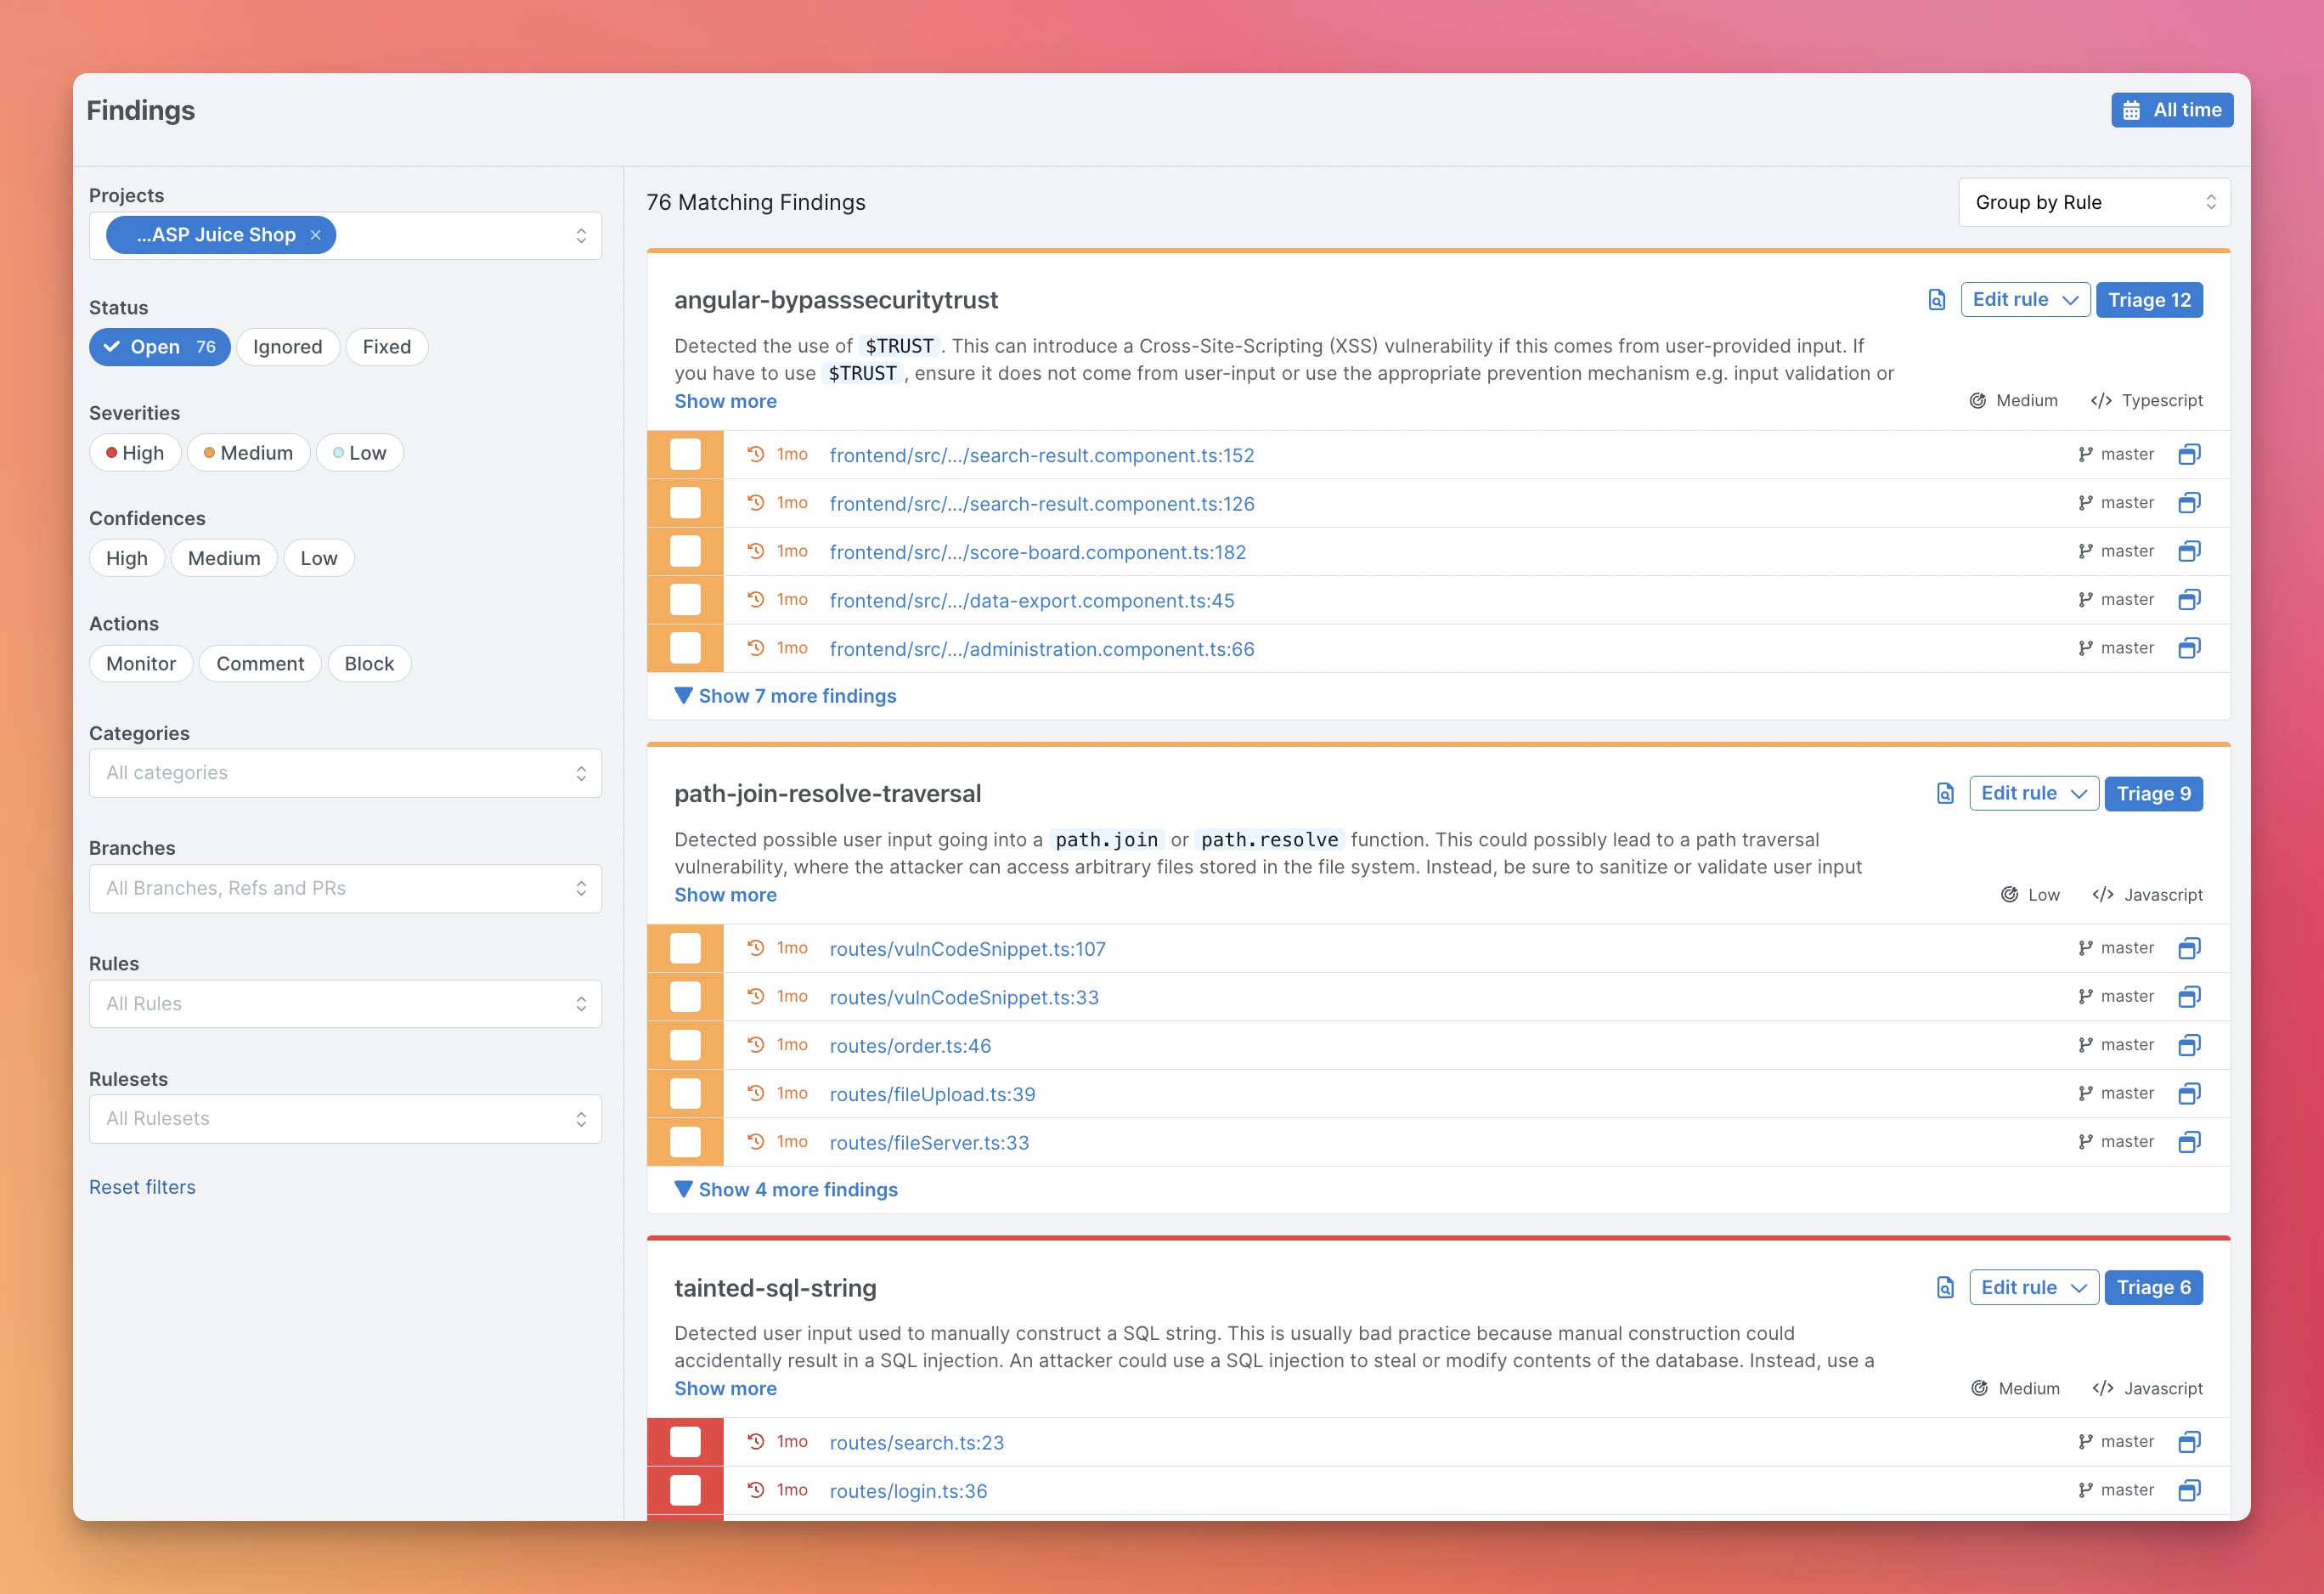
For new users, we recommend starting with the Semgrep AppSec Platform because it provides a visual interface, a demo project, result triaging and exploration workflows, and makes setup in CI/CD fast. Scans are still local and code isn't uploaded. Alternatively, you can also start with the CLI and navigate the terminal output to run one-off searches.
Option 1: Getting started from the Semgrep Appsec Platform (Recommended)
-
Register on semgrep.dev
-
Explore the demo findings to learn how Semgrep works
-
Scan your project by navigating to
Projects > Scan New Project > Run scan in CI -
Select your version control system and follow the onboarding steps to add your project. After this setup, Semgrep will scan your project after every pull request.
-
[Optional] If you want to run Semgrep locally, follow the steps in the CLI section.
Notes:
If there are any issues, please ask for help in the Semgrep Slack.
Option 2: Getting started from the CLI
-
Install Semgrep CLI
# For macOS $ brew install semgrep # For Ubuntu/WSL/Linux/macOS $ python3 -m pip install semgrep # To try Semgrep without installation run via Docker $ docker run -it -v "${PWD}:/src" semgrep/semgrep semgrep login $ docker run -e SEMGREP_APP_TOKEN=<TOKEN> --rm -v "${PWD}:/src" semgrep/semgrep semgrep ci -
Run
semgrep loginto create your account and login to Semgrep. This step is optional, but logging into Semgrep gets you access to:- Semgrep Supply Chain: A dependency scanner that detects reachable vulnerabilities in third party libraries
- Semgrep Code's Pro rules: 600+ high confidence rules written by Semgrep's security research team
- Semgrep Code's Pro engine: An advanced code analysis engine, designed to detect complex vulnerabilities, and reduce false positives
-
Go to your app's root directory and run
semgrep ci. This will scan your project to check for vulnerabilities in your source code and its dependencies. -
Try writing your own query interactively with
-e. For example, a check for Python == where the left and right hand sides are the same (potentially a bug):$ semgrep -e '$X == $X' --lang=py path/to/src
Semgrep Ecosystem
The Semgrep ecosystem includes the following:
-
Semgrep Community Edition - The open-source program analysis engine at the heart of everything. Suitable for ad-hoc use cases with a high tolerance for false positives - think consultants, security auditors, or pentesters.
-
Semgrep AppSec Platform - Easily orchestrate and scale SAST, SCA, and Secrets scanning across an organization, with no risk of overwhelming developers. Customize which findings developers see, where they see them, and integrate with CI providers like GitHub, GitLab, CircleCI, and more. Includes both free and paid tiers.
-
Semgrep Code (SAST) - Make real progress on your vulnerability backlog with SAST that minimizes noise and empowers developers to quickly fix issues on their own, even if they have no security knowledge. Easy to deploy secure guardrails and tailored, step-by-step remediation guidance mean developers actually fix issues since they don't feel slowed down.
-
Semgrep Supply Chain (SSC) - A high-signal dependency scanner that detects reachable vulnerabilities in open source third-party libraries and functions.
-
Semgrep Secrets (Secrets scanning) - Secrets detection that uses semantic analysis, improved entropy analysis, and validation to accurately surface sensitive credentials in the developer workflow.
-
Semgrep Assistant (AI) - Assistant is an AI-powered AppSec engineer that helps both developers and AppSec teams prioritize, triage, and remediate Semgrep findings at scale. Humans agree with Assistant auto-triage decisions 97% of the time, and rate generated remediation guidance as helpful 80% of the time. For an overview of how Assistant works, read this overview.
-
-
Semgrep MCP Server - A Model Context Protocol (MCP) server that lets AI coding assistants run Semgrep scans directly. Integrates with Cursor, VS Code, Windsurf, Claude Desktop, and more. Run
semgrep mcpto start it locally.- Hooks - Automatically trigger Semgrep scans as you code.
- Skills / Prompts - Built-in MCP prompts like
write_custom_semgrep_rulehelp AI assistants write accurate Semgrep rules. - Claude Code plugin - Available on the official marketplace and via the semgrep/mcp-marketplace repo:
/plugin marketplace add semgrep/mcp-marketplace - Cursor plugin - Available on the official marketplace and via the semgrep/cursor-plugin repo.
Additional resources:
- Semgrep Playground - An online interactive tool for writing and sharing rules.
- Semgrep Registry - 2,000+ community-driven rules covering security, correctness, and dependency vulnerabilities.
Join hundreds of thousands of other developers and security engineers already using Semgrep at companies like GitLab, Dropbox, Slack, Figma, Shopify, HashiCorp, Snowflake, and Trail of Bits.
Semgrep is developed and commercially supported by Semgrep, Inc., a software security company.
Semgrep Rules
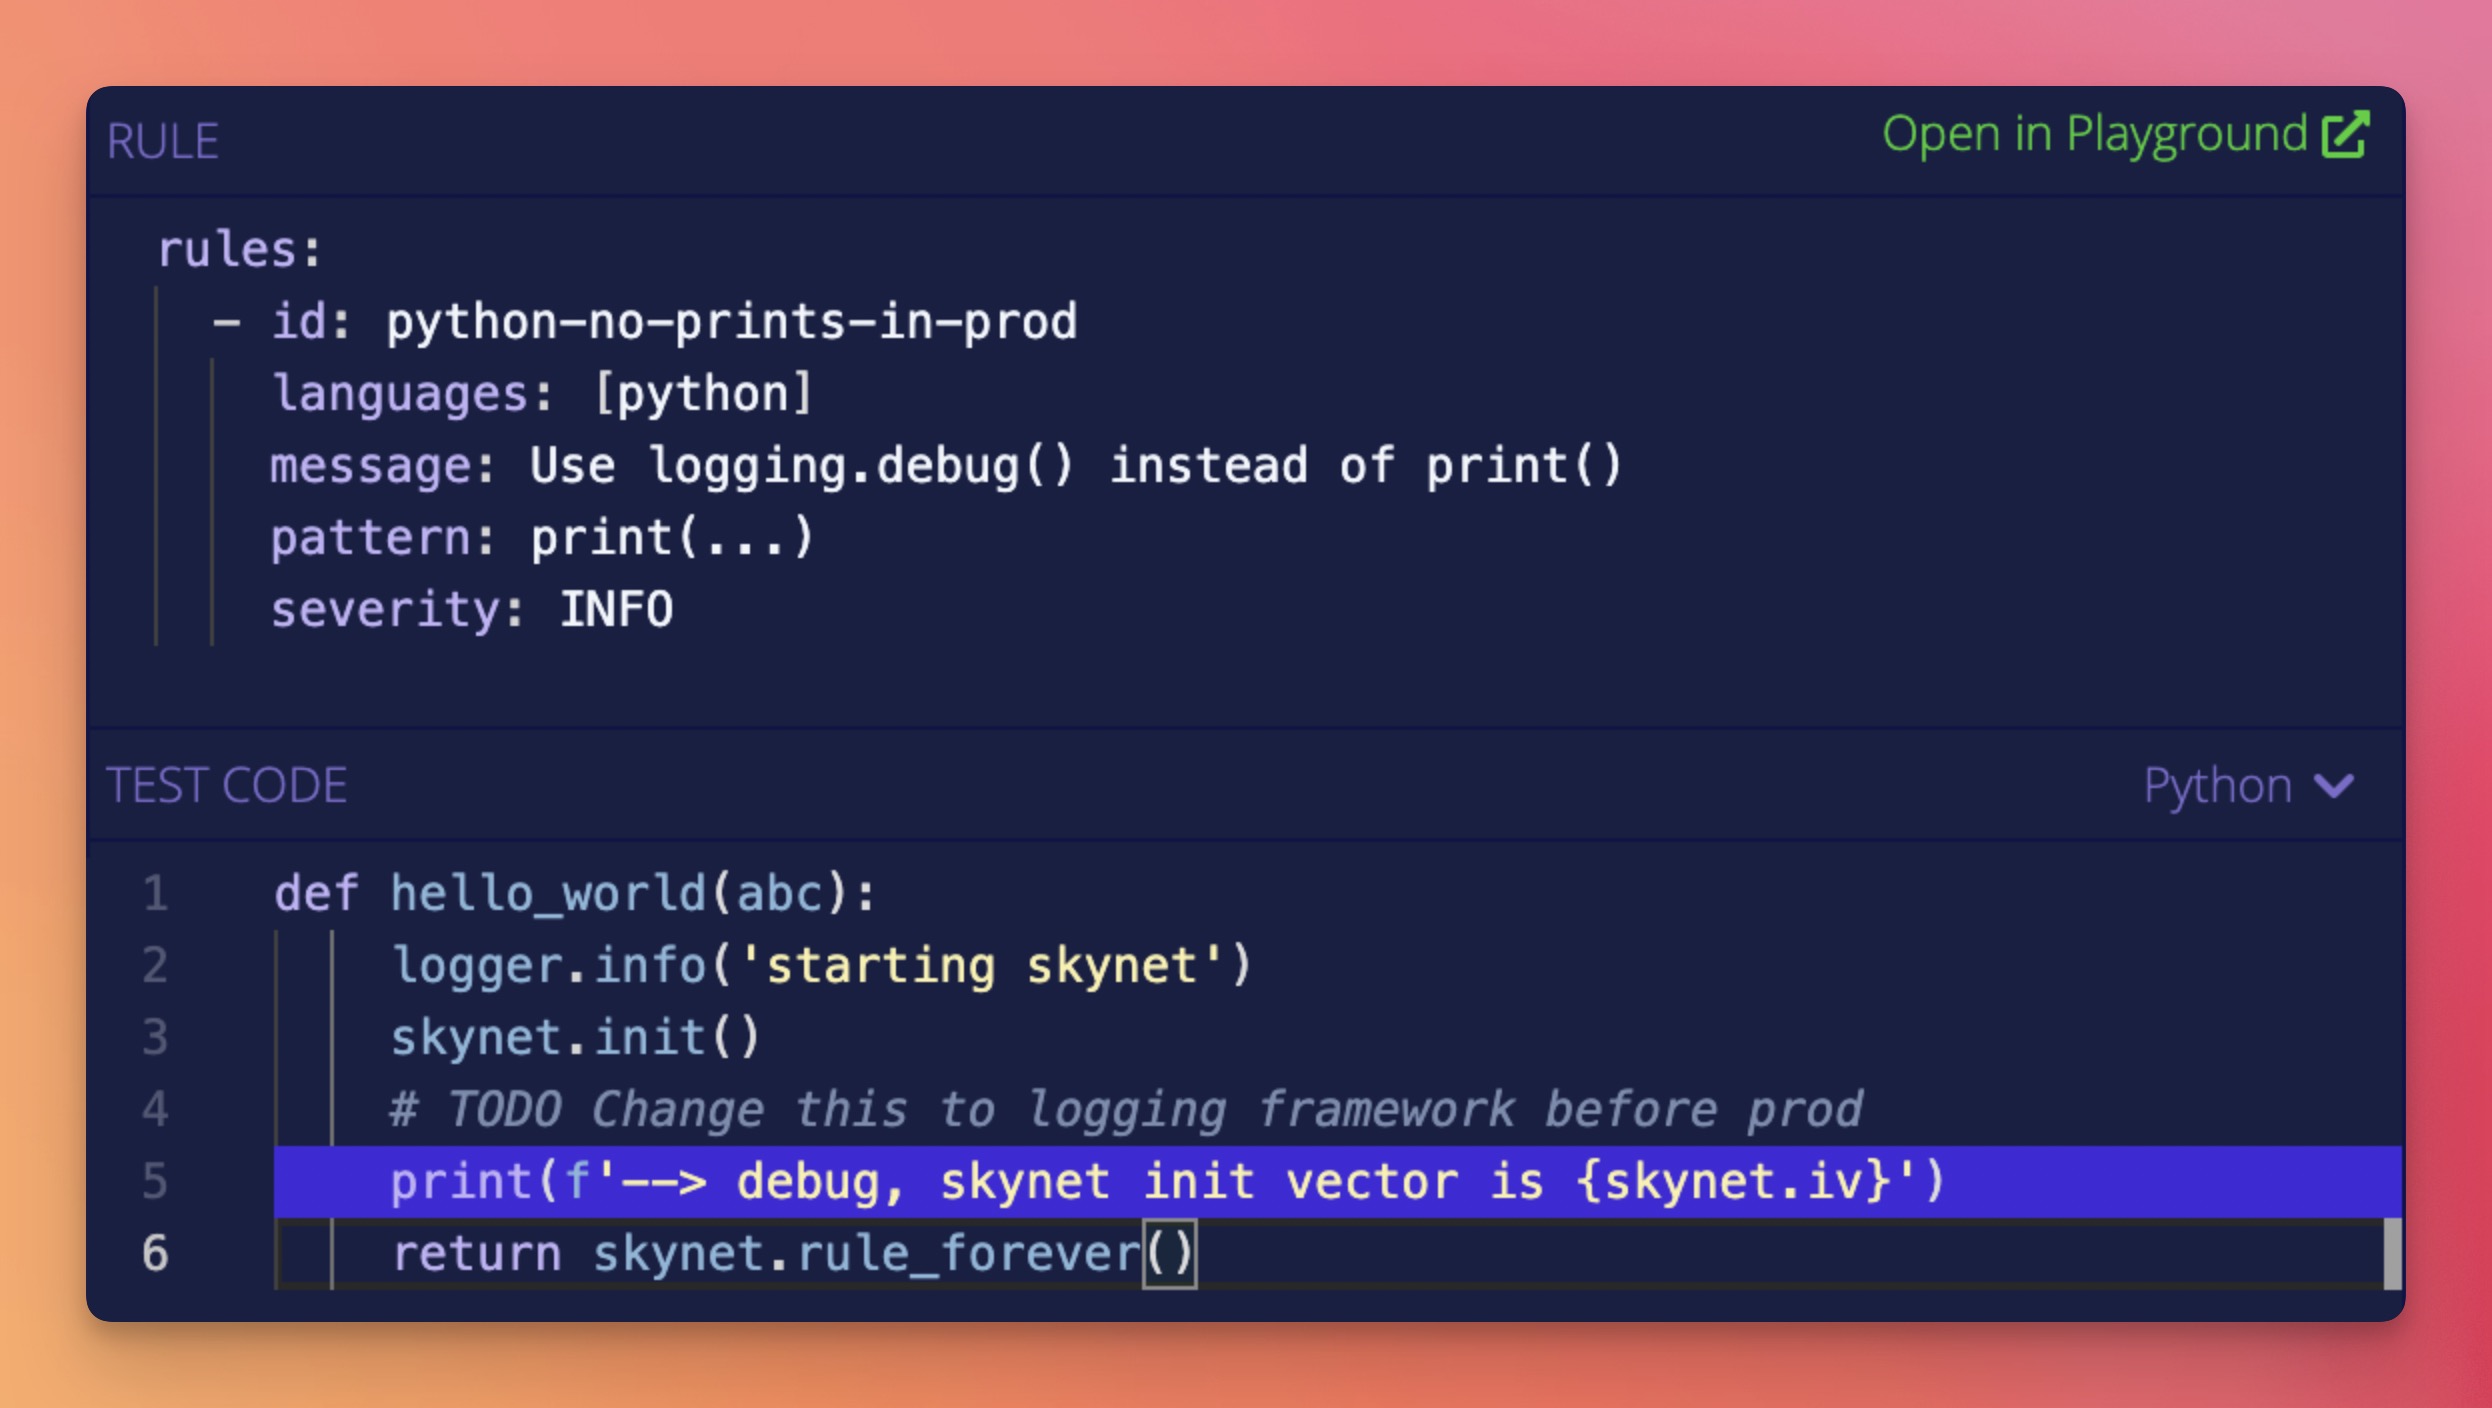
Semgrep rules look like the code you already write; no abstract syntax trees, regex wrestling, or painful DSLs. Here's a quick rule for finding Python print() statements.
Run it online in Semgrep’s Playground by clicking here.
Examples
Visit Docs > Rule examples for use cases and ideas.
| Use case | Semgrep rule |
|---|---|
| Ban dangerous APIs | Prevent use of exec |
| Search routes and authentication | Extract Spring routes |
| Enforce the use secure defaults | Securely set Flask cookies |
| Tainted data flowing into sinks | ExpressJS dataflow into sandbox.run |
| Enforce project best-practices | Use assertEqual for == checks, Always check subprocess calls |
| Codify project-specific knowledge | Verify transactions before making them |
| Audit security hotspots | Finding XSS in Apache Airflow, Hardcoded credentials |
| Audit configuration files | Find S3 ARN uses |
| Migrate from deprecated APIs | DES is deprecated, Deprecated Flask APIs, Deprecated Bokeh APIs |
| Apply automatic fixes | Use listenAndServeTLS |
Extensions
Visit Docs > Extensions to learn about using Semgrep in your editor or pre-commit. When integrated into CI and configured to scan pull requests, Semgrep will only report issues introduced by that pull request; this lets you start using Semgrep without fixing or ignoring pre-existing issues!
Documentation
Browse the full Semgrep documentation on the website. If you’re new to Semgrep, check out Docs > Getting started or the interactive tutorial.
Metrics
Using remote configuration from the Registry (like --config=p/ci) reports pseudonymous rule metrics to semgrep.dev.
When using configs from local files (like --config=xyz.yml), metrics are sent only when the user is logged in.
To disable Registry rule metrics, use --metrics=off.
The Semgrep privacy policy describes the principles that guide data-collection decisions and the breakdown of the data that are and are not collected when the metrics are enabled.
More
- Frequently asked questions (FAQs)
- Contributing
- Build instructions for developers
- Ask questions in the Semgrep community Slack
- CLI reference and exit codes
- Semgrep YouTube channel
- License (LGPL-2.1)
- Licensing Semgrep
Upgrading
To upgrade, run the command below associated with how you installed Semgrep:
# Using Homebrew
$ brew upgrade semgrep

# Using pipx
$ pipx upgrade semgrep

# Using uv tool command
$ uv tool upgrade semgrep

# Using Docker
$ docker pull semgrep/semgrep:latest
3 maintainers


Metadata
3 maintainers
Release files for semgrep 1.181.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| semgrep-1.181.0.tar.gz | 520.6 kB | Details |
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-win_amd64.whl | CPython 3.11, CPython 3.12, Python 3.11, Python 3.10, Python 3.14, Python 3.13, Python 3.12, CPython 3.10, CPython 3.13, CPython 3.14 | none | Windows x86-64 | Details |
| semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_x86_64.whl | Python 3.14, CPython 3.12, CPython 3.11, Python 3.13, Python 3.12, Python 3.11, Python 3.10, CPython 3.13, CPython 3.14, CPython 3.10 | none | Linux musl 1.2+ x86-64 | Details |
| semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_aarch64.whl | CPython 3.11, CPython 3.12, Python 3.10, Python 3.14, Python 3.13, Python 3.12, CPython 3.10, Python 3.11, CPython 3.13, CPython 3.14 | none | Linux musl 1.2+ ARM64 | Details |
| semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_x86_64.whl | CPython 3.14, CPython 3.10, Python 3.14, Python 3.13, CPython 3.12, CPython 3.11, Python 3.12, Python 3.11, Python 3.10, CPython 3.13 | none | Linux glibc 2.34+ x86-64 | Details |
| semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_aarch64.whl | CPython 3.12, Python 3.10, CPython 3.11, Python 3.13, Python 3.12, Python 3.11, CPython 3.13, CPython 3.14, CPython 3.10, Python 3.14 | none | Linux glibc 2.34+ ARM64 | Details |
| semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-macosx_11_0_arm64.whl | CPython 3.14, CPython 3.11, CPython 3.12, Python 3.11, Python 3.10, Python 3.14, Python 3.13, Python 3.12, CPython 3.10, CPython 3.13 | none | macOS 11.0+ ARM64 | Details |
| semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-macosx_10_14_x86_64.whl | CPython 3.11, CPython 3.12, Python 3.11, Python 3.10, Python 3.14, Python 3.13, Python 3.12, CPython 3.10, CPython 3.13, CPython 3.14 | none | macOS 10.14+ x86-64 | Details |
Total release size: 453.9 MB
Release files / semgrep-1.181.0.tar.gz
| Download URL | semgrep-1.181.0.tar.gz |
|---|---|
| Size | 520.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
4c0905288ccf9ee5330e766f1c677a31642a4cc0aac5a95097e7563f3f3a92fa
|
|
BLAKE2b-256 checksum How to use checksums |
d8840d55c4c7cb761570f69c9b05eb515886dcbd550ec9da2d6537bc7ca660b5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Release files / semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-win_amd64.whl
| Download URL | semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-win_amd64.whl |
|---|---|
| Size | 58.1 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
c3d7295bfd26f994231d82145888bd0a73ef0ad66ffb0c0341f0350a90ac3136
|
|
BLAKE2b-256 checksum How to use checksums |
53d0c35c85e860b722b86108ecef78c104558d65fddb6d00e6e83be54b4b263b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 14, 2026.
Transparency logRelease files / semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_x86_64.whl
| Download URL | semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 77.1 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Linux musl 1.2+ x86-64 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 |
|
SHA-256 checksum How to use checksums |
9ef478d031105158e97a4491ecd349ecea011193e6b4be618d515a0a71bb6884
|
|
BLAKE2b-256 checksum How to use checksums |
7d5b153698c00a6fc51267710f5c3efdc454dfe5d8ae0e928932bd72398f74f8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 14, 2026.
Transparency logRelease files / semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_aarch64.whl
| Download URL | semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 79.5 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Linux musl 1.2+ ARM64 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 |
|
SHA-256 checksum How to use checksums |
3defc5f3e0a76c5735c0edc1a1ccb903471b0558d8687bcb22ad75bb20923afe
|
|
BLAKE2b-256 checksum How to use checksums |
9bc8d7767f2f8abf70d6b479afe31f64b063e77444b7653a83ac3e99586fa725
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 14, 2026.
Transparency logRelease files / semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_x86_64.whl
| Download URL | semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_x86_64.whl |
|---|---|
| Size | 70.5 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Linux glibc 2.34+ x86-64 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 |
|
SHA-256 checksum How to use checksums |
c142ec04a2ed144970cb0a92f6877651dd3c088505eec737bb7f4db7ae5f0ffa
|
|
BLAKE2b-256 checksum How to use checksums |
b01daed54e9cea5491f0dd54286126216f97ef817a356734d3c9d5e40c124c34
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 14, 2026.
Transparency logRelease files / semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_aarch64.whl
| Download URL | semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_aarch64.whl |
|---|---|
| Size | 72.6 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Linux glibc 2.34+ ARM64 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 |
|
SHA-256 checksum How to use checksums |
6dedd7d72dd7f7bd314439f469e143d57d84508c57c29246793378cccc2b90dc
|
|
BLAKE2b-256 checksum How to use checksums |
88c5f5346177cafd8c3a68d6e133f9d579c39c47ec9aad2c4b93135bc609908f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 14, 2026.
Transparency logRelease files / semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-macosx_11_0_arm64.whl
| Download URL | semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-macosx_11_0_arm64.whl |
|---|---|
| Size | 49.8 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
05d79ad777fae86f6d914a67bedec1b9e2c3e637f61d49a4ef557e2bf69fed01
|
|
BLAKE2b-256 checksum How to use checksums |
c4ee80b356194e13f6c533143ff16e646f0131c550c72a4c399474f686ad005f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 14, 2026.
Transparency logRelease files / semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-macosx_10_14_x86_64.whl
| Download URL | semgrep-1.181.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-macosx_10_14_x86_64.whl |
|---|---|
| Size | 45.8 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 macOS 10.14+ x86-64 |
|
SHA-256 checksum How to use checksums |
9af2325bfd58fa24936a7776277da067d563f6bb5dbe2184d7fb923e1a2b6134
|
|
BLAKE2b-256 checksum How to use checksums |
3caf90430a8162e20174d11715ec4dd97ff7f44e5efc90fc74a5182c78741aeb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 14, 2026.
Transparency log













