



Ask another session to review a change, report progress, or pick up a task. session-peer uses native agent inboxes and queues; the receiving agent decides how to respond.
Demo
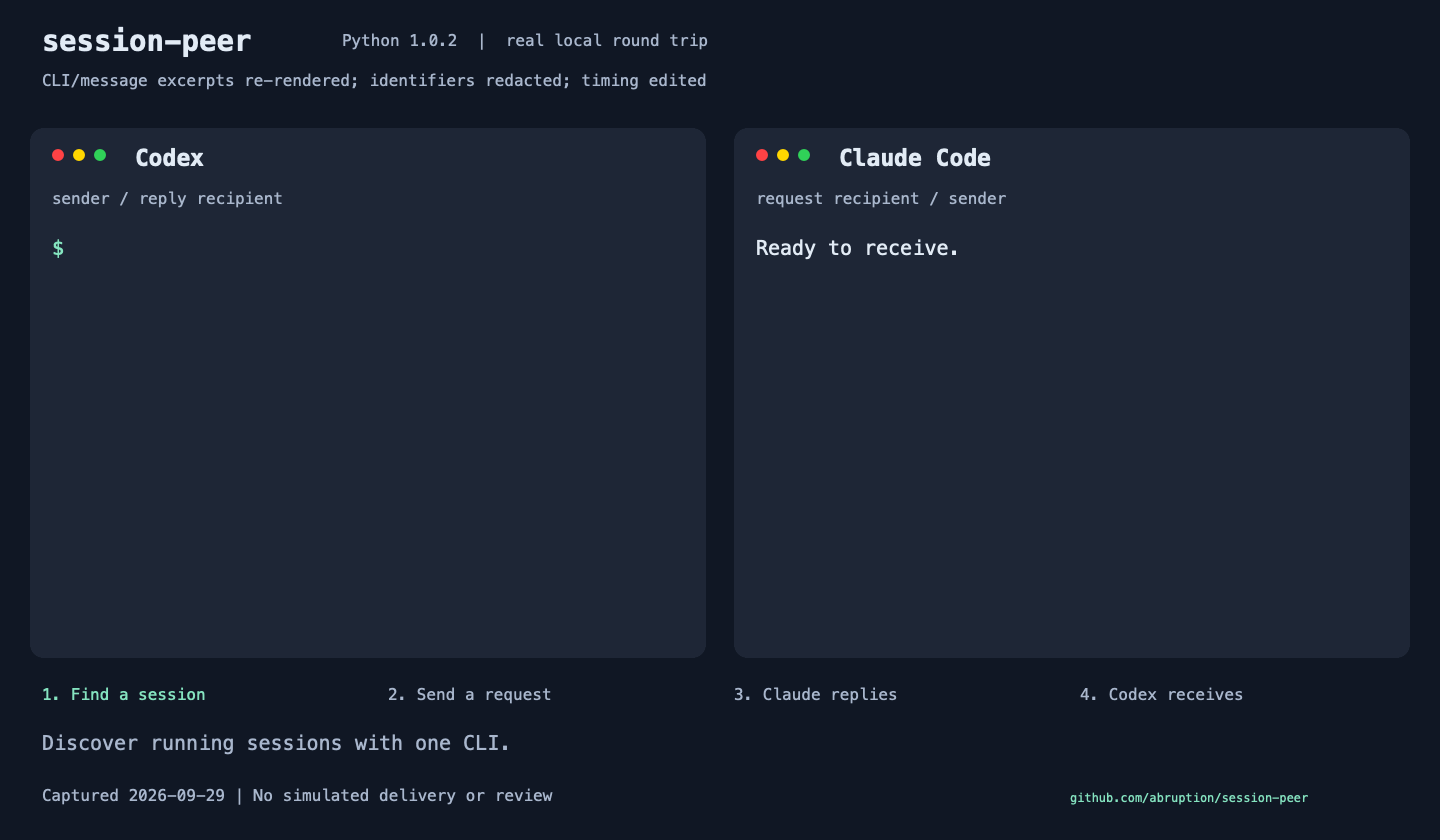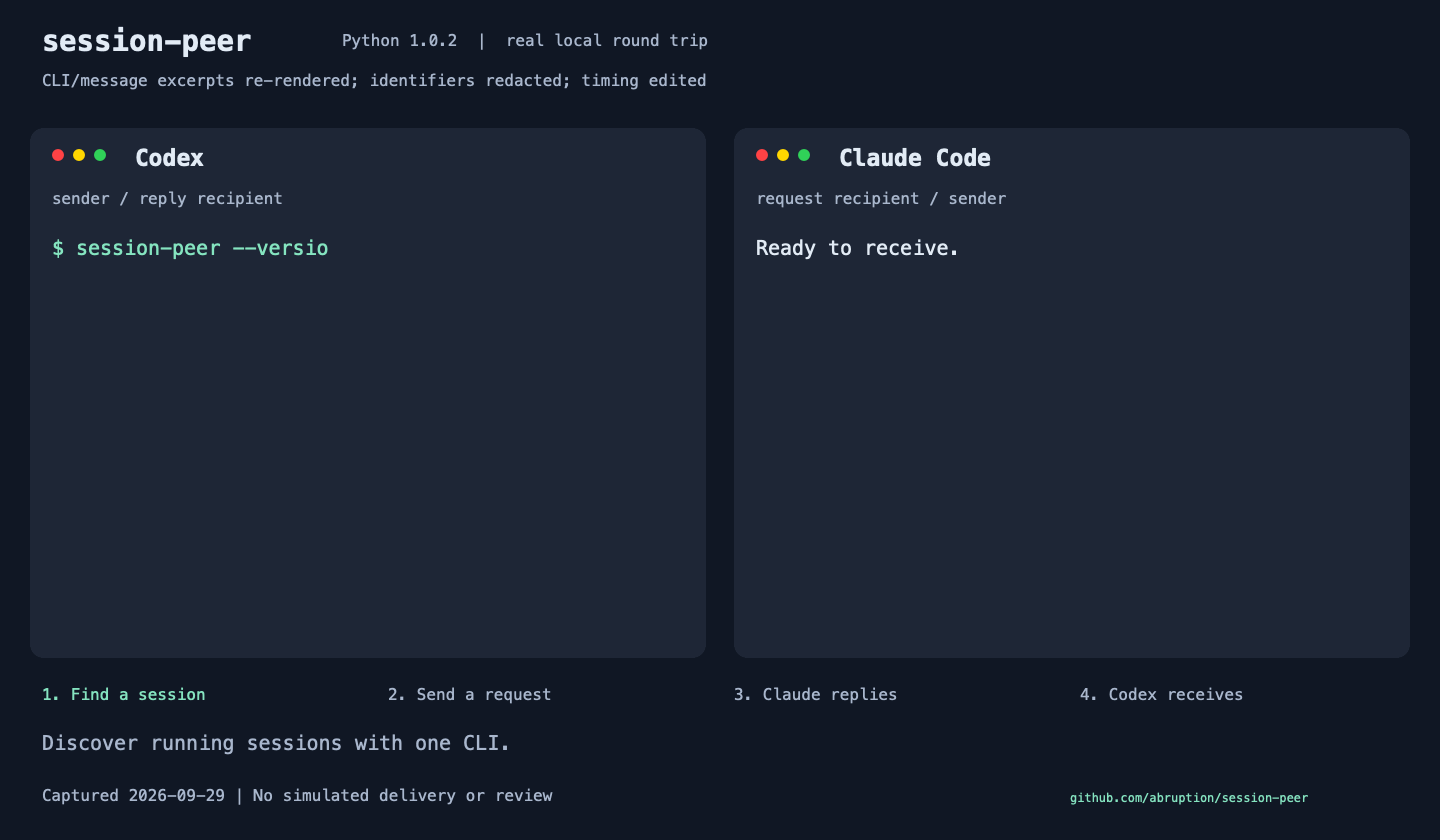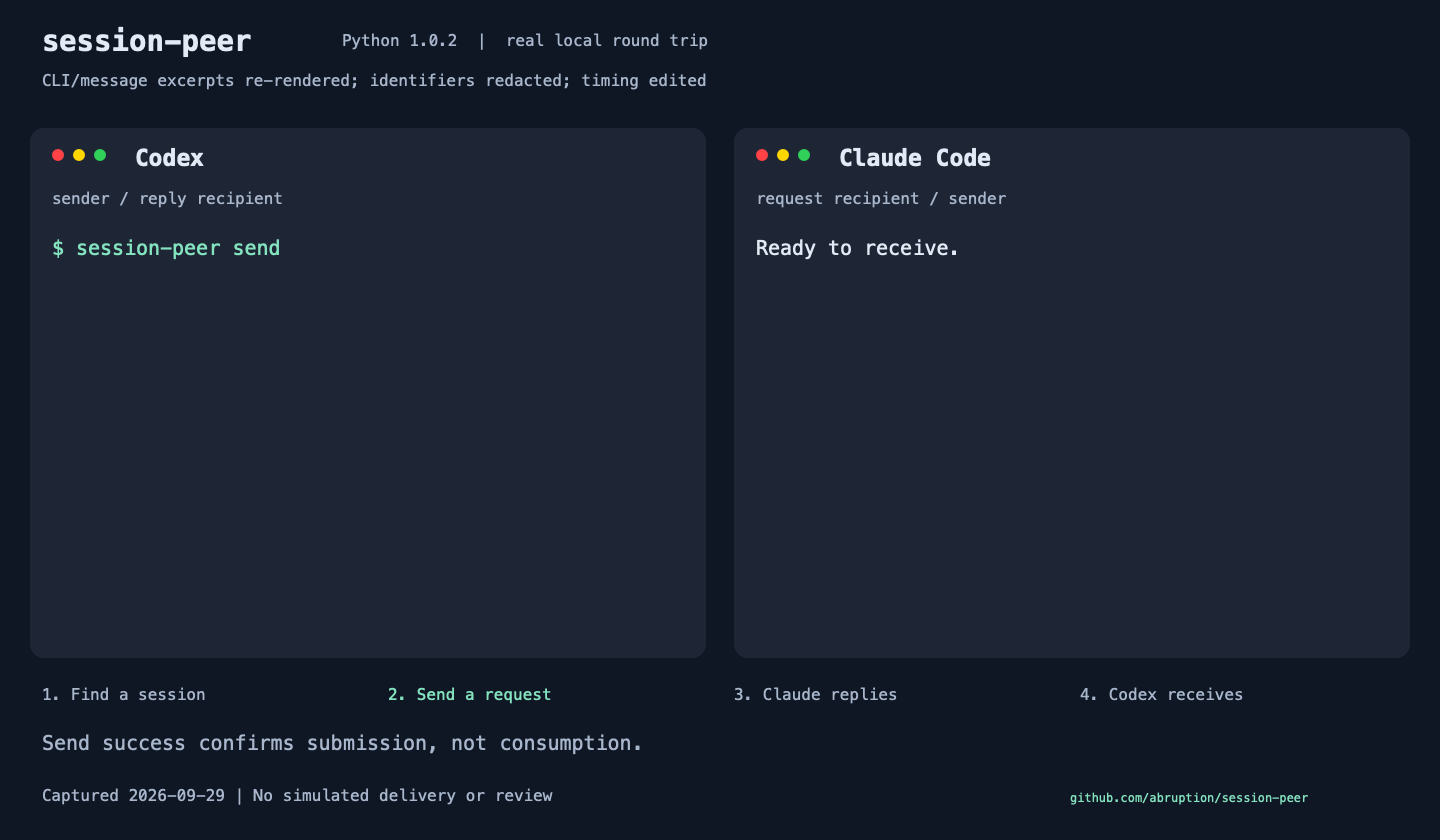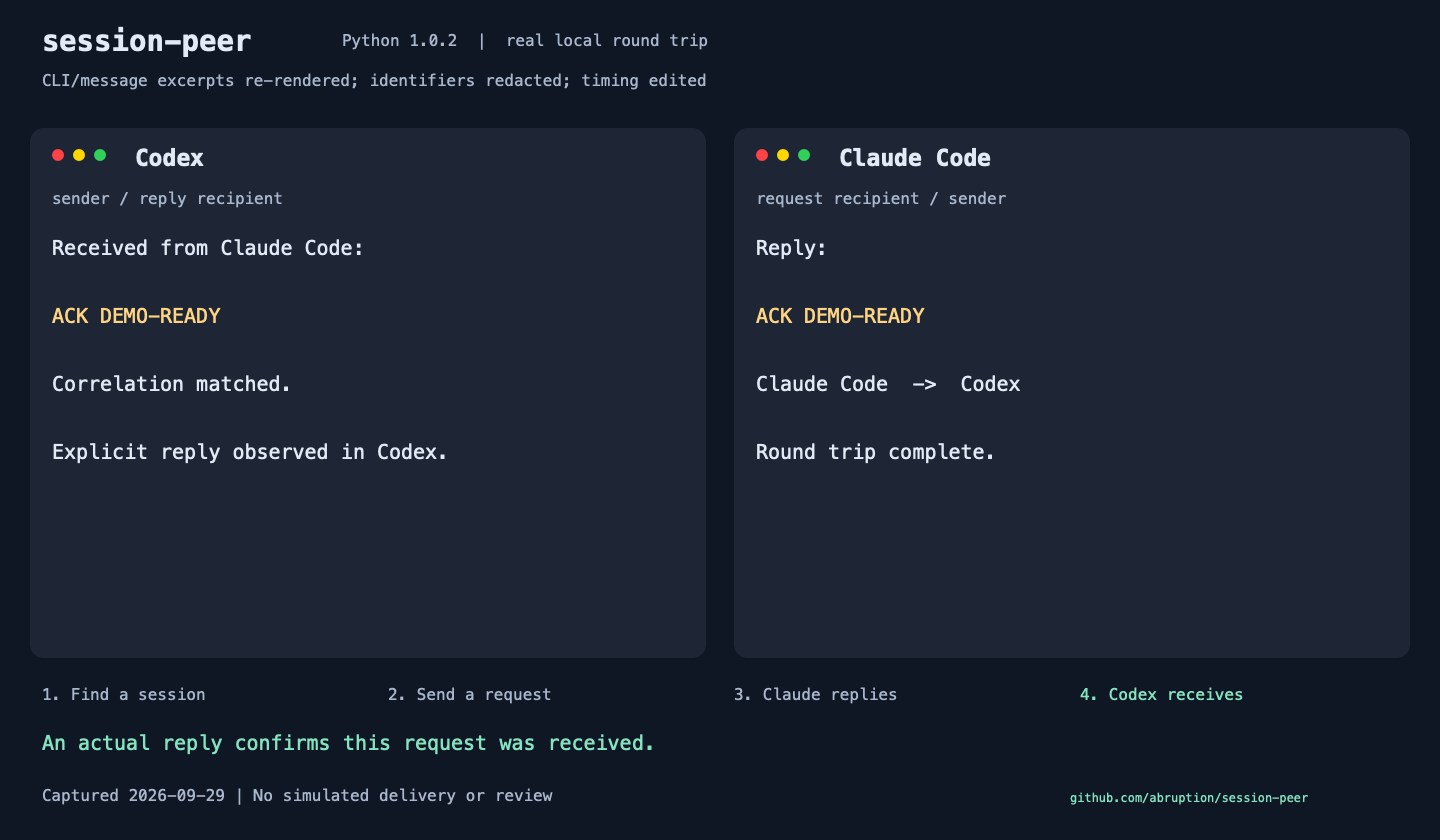
A real local request and reply using session-peer 1.0.2: Codex contacts Claude Code
and receives ACK DEMO-READY. CLI and message excerpts are anonymized and re-rendered
in this ~22-second animation, not a screen recording; send success alone is not an ACK.
Quick Start
Install
Python 3.9+. The core local/SSH CLI has no third-party Python dependencies. Version covered by this README: 1.1.1.
Maintenance release prepared on 2026-10-12; see the release notes. This patch updates documentation and development-only tests, not runtime behavior. Package publication and operational deployment are separate.
Experimental handoff is opt-in: local POSIX Claude supports receipt ACKs; Codex and SSH support correlation-only submission, not ACK observation. See the handoff guide for the shipped scope and remaining acceptance gates.
pipx install session-peer
session-peer --version
session-peer list
Use uv tool install session-peer instead if you prefer uv. Native Windows,
virtual-environment pip, and standalone/SSH installation variants are in the
installation guide.
For SSH discovery, replace the example host worker with your host or alias.
Then replace the fictional session name and full UUID with the listed destination:
session-peer list --host worker
session-peer send --to api-worker --message "Report progress"
session-peer send --host worker --to 'codex:00000000-0000-4000-8000-000000000001' --message "Review the change"
The SSH destination needs Python and the target agent's native inbox or queue,
but not an installed session-peer CLI. For a custom Codex home, pass the listed
codexHome with --codex-home; use --dry-run to validate without sending.
Use the destination account that owns the session (--host USER@HOST).
SSH access and receiver permissions still apply.
posted / queued confirms submission, not consumption, ACK, or completion.
Ask for an explicit reply when needed. Ordinary sends refuse inactive Codex destinations
by default and do not start them. Never automatically retry an uncertain send.
The optional agent skill is installed separately from the runtime; see the installation guide for its Skills CLI command.
Update
Use the same manager that installed the runtime:
pipx upgrade session-peer
# or: uv tool upgrade session-peer
# or, in its virtual environment: python -m pip install --upgrade session-peer
For local installations, session-peer update replaces standalone runtime files;
package-managed installs receive upgrade guidance instead. It never updates agent skills:
use their original installer (Skills CLI, or install.sh only for an installer-owned compatibility copy). The compatibility copy is separate from the independently released skill; existing manager-owned skills are preserved.
See update details and remote limitations.
Docs
- Documentation map: user, integration, operator, and development guides.
- CLI reference: options, JSON, installation variants, and migration.
- Diagnostics and replies · Multiple Codex homes.
- AI-assisted setup · Project site · Release notes.
- Release process.
Paired devices / encrypted Relay
require Unix, Python 3.11+, and session-peer[relay], with pinned identities and
explicit receiver policy. Package publication does not guarantee hosted-service availability.
The blind Relay cannot decrypt application message content.
MCP / Codex plugin requires Python 3.10+
and session-peer[mcp]; MCP wake requires both send and wake capabilities.
Wake runs only when explicitly requested
and can start a turn, consume usage, and change project files.
The Antigravity bridge remains experimental.
English is canonical; Korean, Japanese, and Simplified Chinese guides are kept aligned. Translations do not change the CLI output language.
License
MIT.
Support and security
Use GitHub Issues for bugs and features. Report vulnerabilities privately under the security policy, not in public issues. Redact secrets, conversation text, session IDs, and personal paths from shared diagnostics.
For private questions or an alternative security contact, email
support@abruption.dev with [session-peer] in the subject.
Support is best effort, with no guaranteed response time. Emails are reviewed manually, never automatically published as issues.
English and Korean reports are welcome.
1 maintainer

Metadata
1 maintainer
Release files for session-peer 1.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| session_peer-1.1.1.tar.gz | 999.2 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| session_peer-1.1.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.2 MB
Release files / session_peer-1.1.1.tar.gz
| Download URL | session_peer-1.1.1.tar.gz |
|---|---|
| Size | 999.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
aeded50e82f4529de3def1a885a18889f4a1a83890376581728586e7ada210c0
|
|
BLAKE2b-256 checksum How to use checksums |
1c5fd5fe11ba361f46f55586a1f6864e631332b4460a080d24e2acb1078b1b6a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 12, 2026.
Transparency logRelease files / session_peer-1.1.1-py3-none-any.whl
| Download URL | session_peer-1.1.1-py3-none-any.whl |
|---|---|
| Size | 185.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
209004ab6b299182f8e6f18b70bd2074f6437f387c0b85a8739df696b0025cdd
|
|
BLAKE2b-256 checksum How to use checksums |
7269e94c20feb6453f65f36e5f80165d494741d2b845ea0d10b96ef6fde65fa0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 12, 2026.
Transparency log













