
shpe


Important Note for Editor: This extension/plugin requires the core Python CLI tool to function. Please make sure you run
pip install shpein your environment!
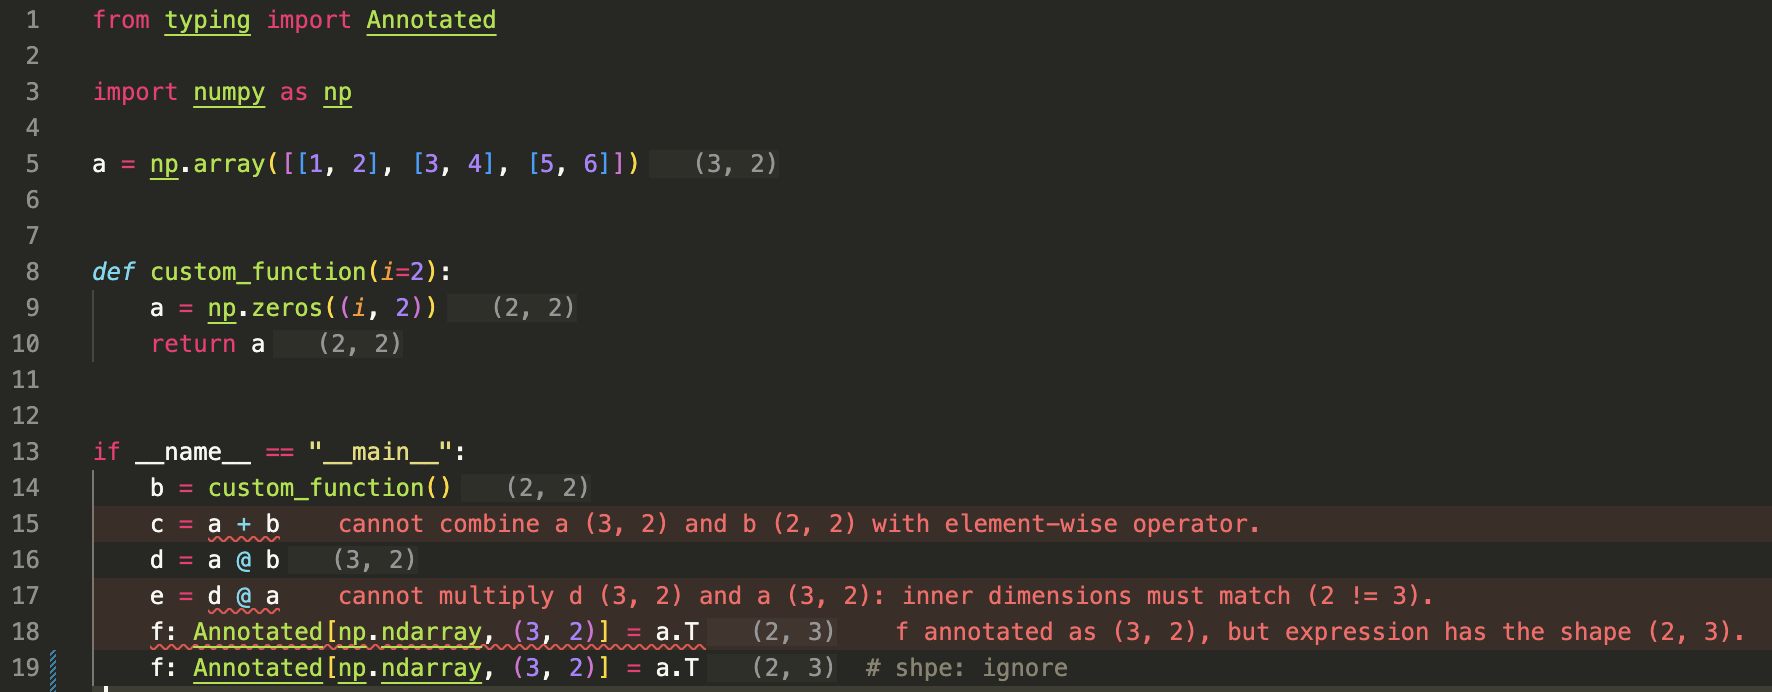
A lightweight static analyzer for tracking and validating NumPy tensor shapes. It automatically infers and shows shapes, so you do not need manual shape comments anymore. It catches shape errors directly in your editor before you even run your code, and you can also integrate it into your CI/CD pipeline.
VS Code Demo
Install
Requires Python 3.12+.
pip install shpe
or with uv:
uv add shpe
Search for shpe in the VS Code Marketplace or PyCharm Marketplace.
CLI
import numpy as np

a = np.zeros((3, 2))
b = np.ones((2, 2))
c = a + b
shpe examples/intro.py
examples/intro.py:15: [Elementwise] cannot combine a (3, 2) and b (2, 2) with element-wise operator.
examples/intro.py:17: [MatMul] cannot multiply d (3, 2) and a (3, 2): inner dimensions must match (2 != 3).
examples/intro.py:18: [Annotation] f annotated as (3, 2), but expression has the shape (2, 3).

Found 3 error(s) across 1 file(s).
Pass files or directories (*.py). --show-shapes prints inferred shapes and scalars. Exit code 1 if any shape error is reported. Skip a line with # shpe: ignore.
examples/demo.py shows more of what is inferred and what is not.
What is checked
- Array creation (
np.array,np.zeros,np.ones, random helpers, …) Annotated[np.ndarray, (rows, cols)]vs the inferred expression- Element-wise
+ - * /(broadcast) and@(matmul) - Subset of NumPy functions (
reshape,transpose,sum, ...) - Simple user functions and classes
If shpe is uncertain, it does not infer a shape. No control flow (if / for / while), no recursion, and only a subset of NumPy. Inplace updates such as a.resize(...) are not modeled.
Bugs and requests: GitHub Issues.
Development
See CONTRIBUTING.md and docs/architecture.md.
1 maintainer

Metadata
1 maintainer
Release files for shpe 0.2.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| shpe-0.2.3.tar.gz | 400.3 kB | With provenance | Details for shpe-0.2.3.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| shpe-0.2.3-py3-none-any.whl | Python 3 | none | any | Details for shpe-0.2.3-py3-none-any.whl |
Total release size: 428.5 kB
Release files / shpe-0.2.3.tar.gz
| Download URL | shpe-0.2.3.tar.gz |
|---|---|
| Size | 400.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5d5015996ac4ed2f3511f61d2e7ae486524c22b6936a47c04655ae92bf358f40
|
|
BLAKE2b-256 checksum How to use checksums |
ec1dc8c9e7416e2c10aeb68b95f471ae136b3f0ed6e6d0f66f05a33ed9c6e8c5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / shpe-0.2.3-py3-none-any.whl
| Download URL | shpe-0.2.3-py3-none-any.whl |
|---|---|
| Size | 28.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
11f54bec41b37a43f58dddc96b2f1e4cfe5582f837a30bab91d4d03eb901ea30
|
|
BLAKE2b-256 checksum How to use checksums |
5504fb2d9bd1e0e3eae8b0ec23820236e4b7169e396356aed0c1f7d87b6a9264
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logSecurity for shpe 0.2.3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for shpe-0.2.3.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














