
The refactorable warehouse. Verify early, test properly, and refactor safely.
Website · Docs · Quickstart · Roadmap
Change your warehouse as often as your code. SQLBuild brings compile-time checks, tests and safe renames to your SQL, so change stops being risky. It is a free, open-source framework for SQL and Python data pipelines, and it keeps its state in append-only tables in your own warehouse: no external state database, no manifest files and no paid tier.
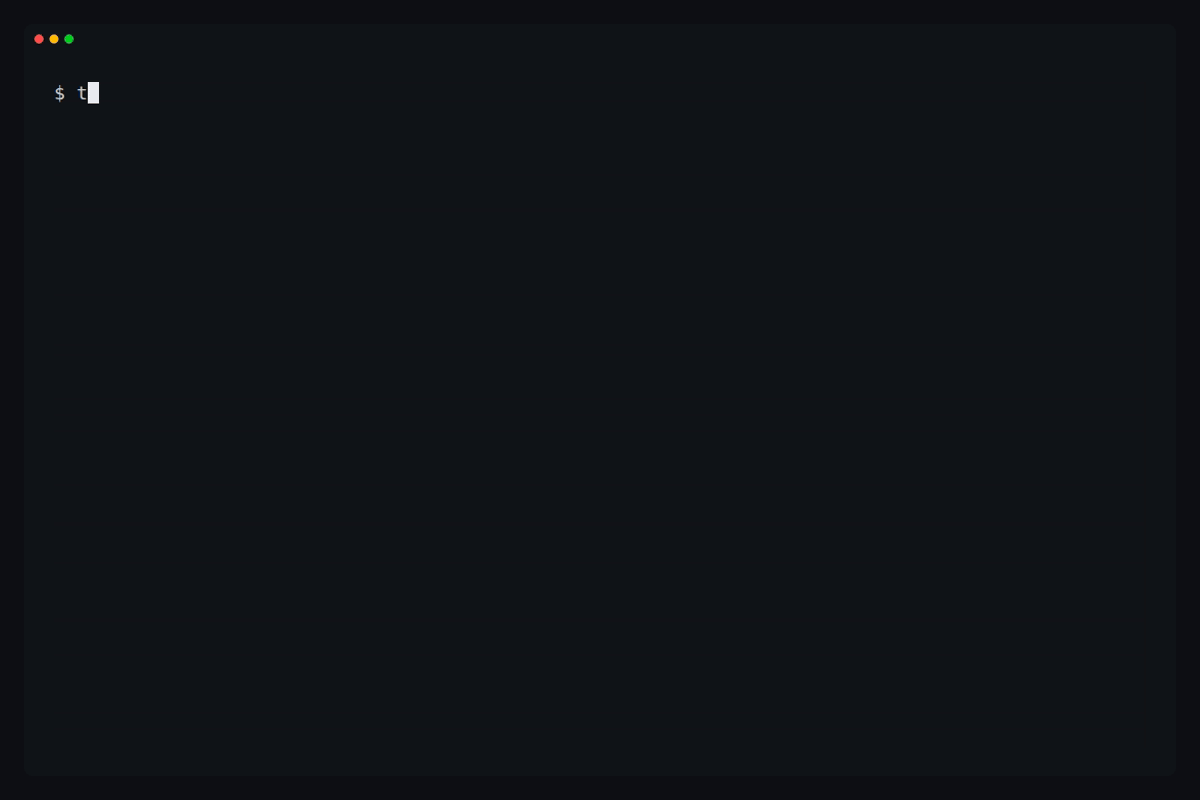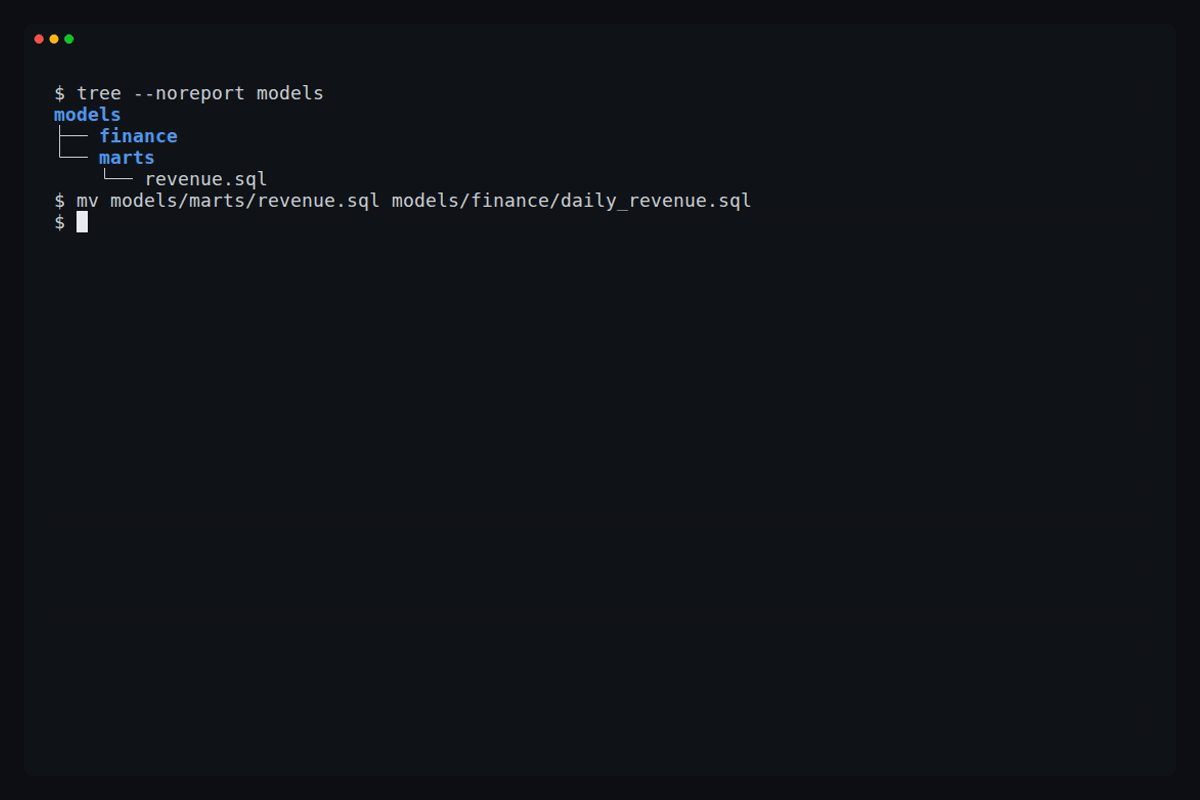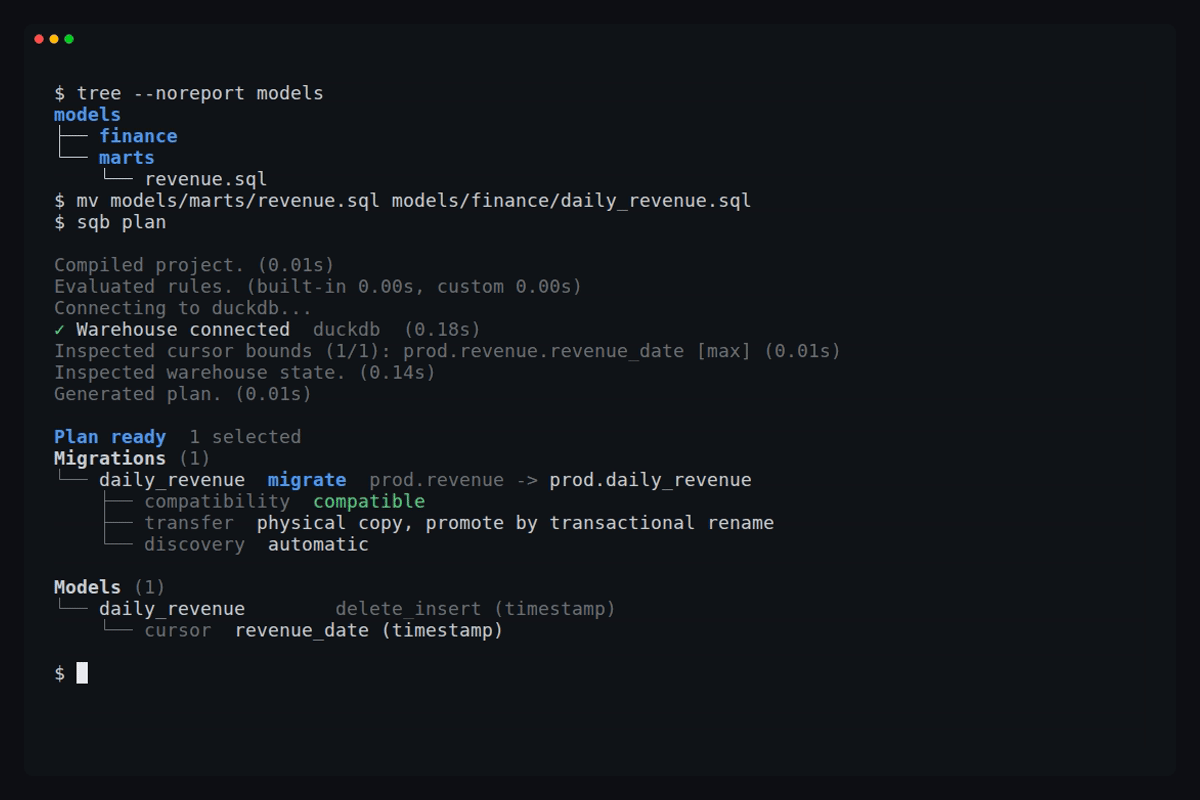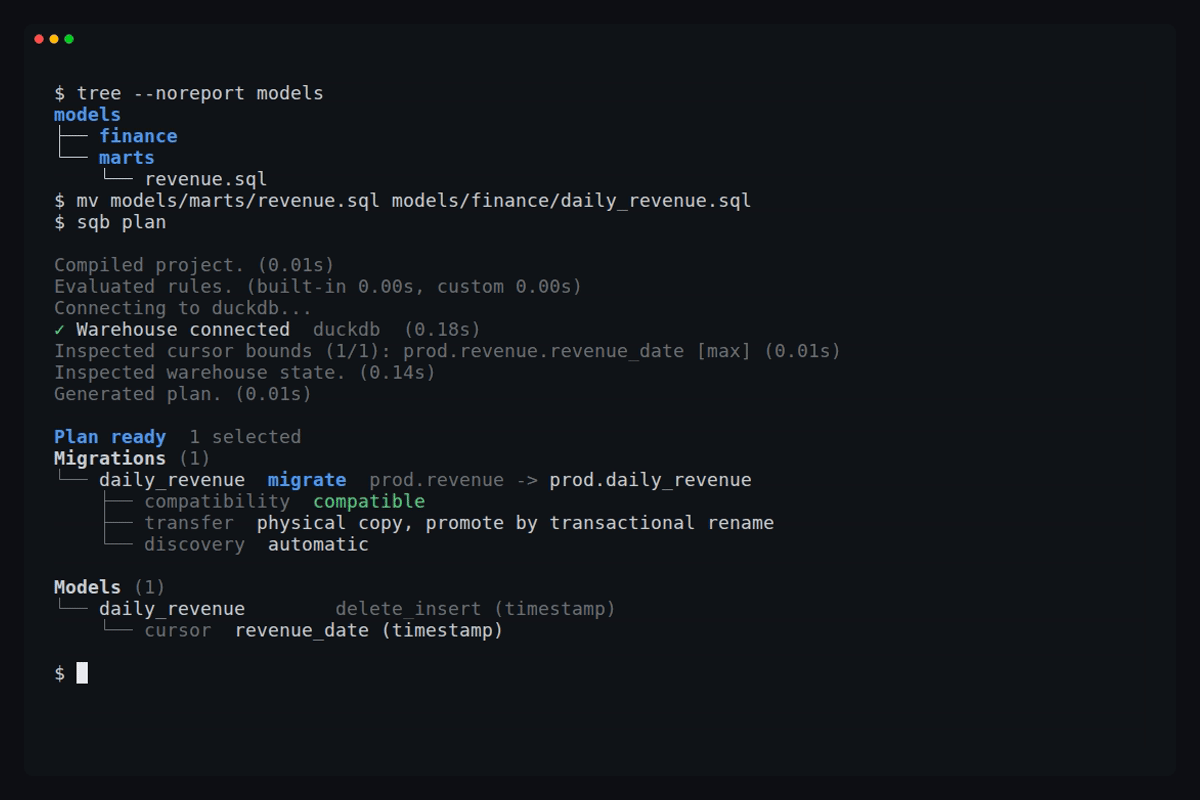
Move an incremental model to a new folder and name, and sqb plan migrates its table instead of
rebuilding it.
Quick start
pip install sqlbuild
sqb playground waffle-shop
cd waffle-shop
sqb plan
sqb build
sqb test
The playground runs on local DuckDB, with no warehouse credentials.
What it does
Catch mistakes before anything runs
- Compile-time checks. SQLBuild resolves references, validates SQL, infers column types, checks contracts and computes column lineage, all offline. A typo'd column fails in seconds, not halfway through a warehouse run.
- Your conventions as rules. Built-in and custom Python rules turn review comments into compile errors: for example, marts can't read sources directly, or every final model declares its key.
Prove it works
- Tests across models. SQL tests mock the sources and check the result through every model in between, with macros as test helpers. Macro, UDF and table-function tests are built in.
- End-to-end scenarios. Build the real graph against fixture data, capture fixtures from the warehouse, and replay them locally on DuckDB in CI. See scenarios.
- Audits and diffs. Audits run before data reaches the target table, and data diffs compare dev against prod or any query.
Change it without rebuilding everything
- Renames keep their history. Rename or move an incremental or snapshot model and SQLBuild migrates the existing table instead of rebuilding it.
- Replay on change. When a model's SQL changes, choose how far back to reprocess, from only the
new data to the last 14 days to a full rebuild, with
replay_on_change. - Macros don't have to be global. Keep macros, enums and constants next to the models that use
them, and preview what a move would break with
sqb scope. See declaration scopes. - Tidy up safely. The janitor archives stale tables before anything is deleted.
Ingestion with Python loaders, and Python tasks, assets and checks, run in the same graph as your SQL models. See the docs for everything else.
In the terminal
Each demo runs on local DuckDB with the projects in website/examples. The
tapes that record them are in website/recordings.
A renamed column breaks the contract
daily_revenue declares contract enforced. Renaming waffles_sold to units_sold in the
SELECT fails at compile time, before anything reaches the warehouse.
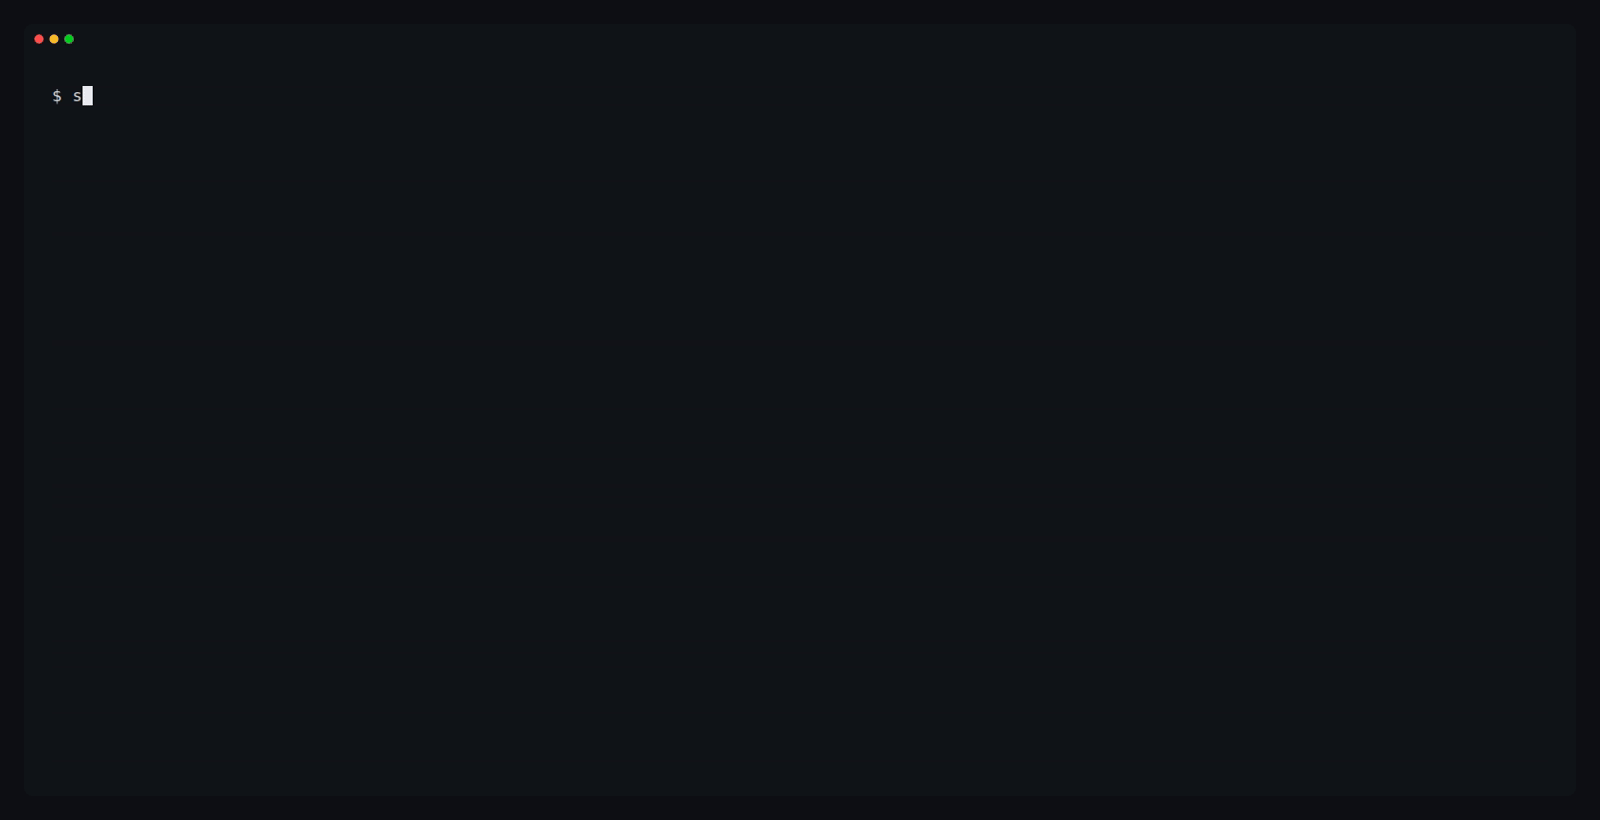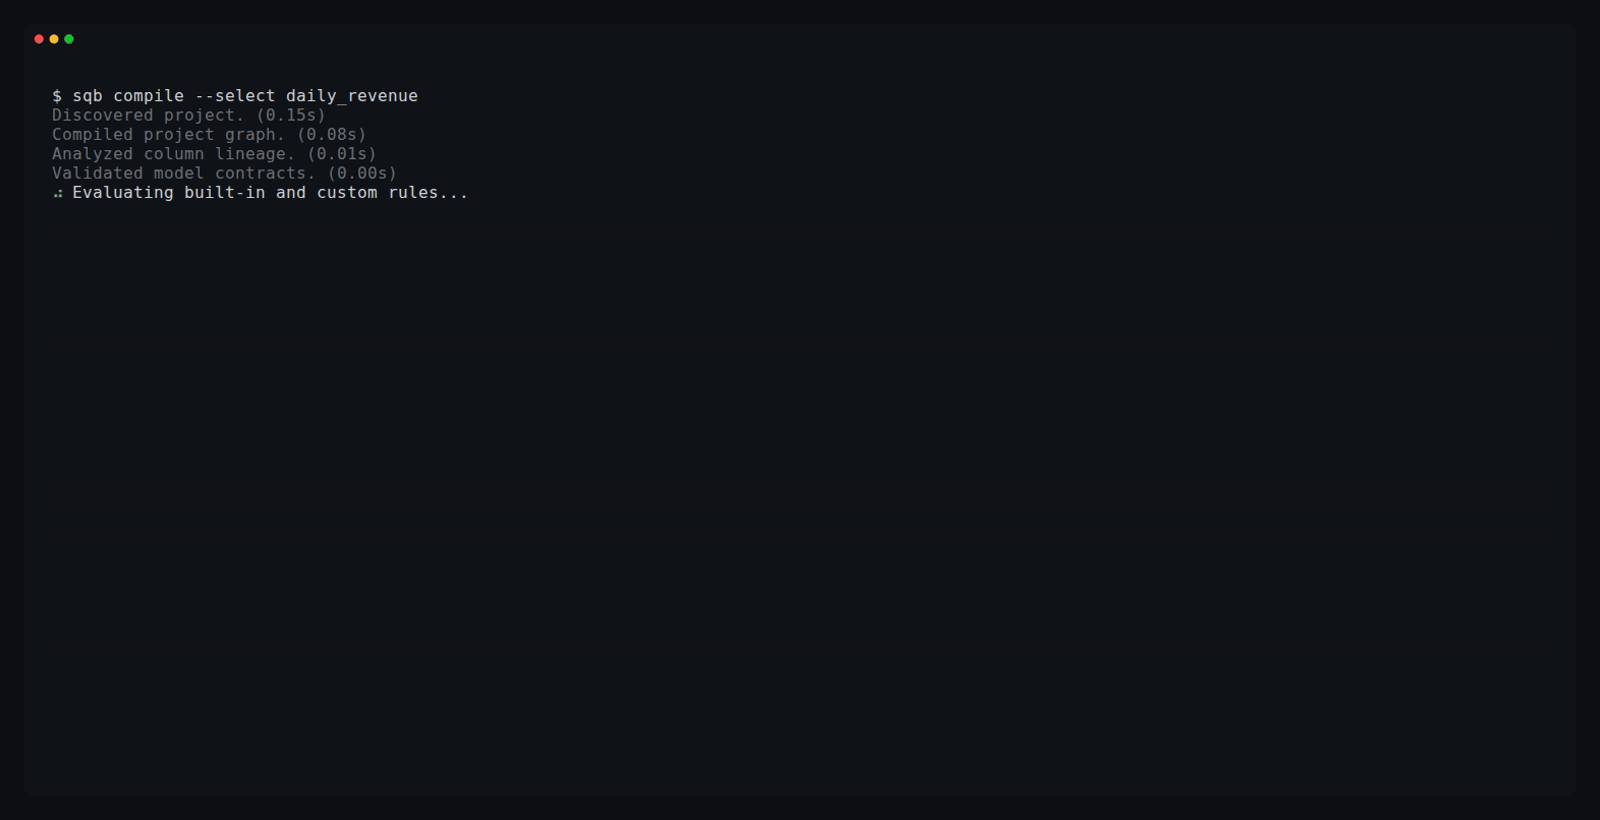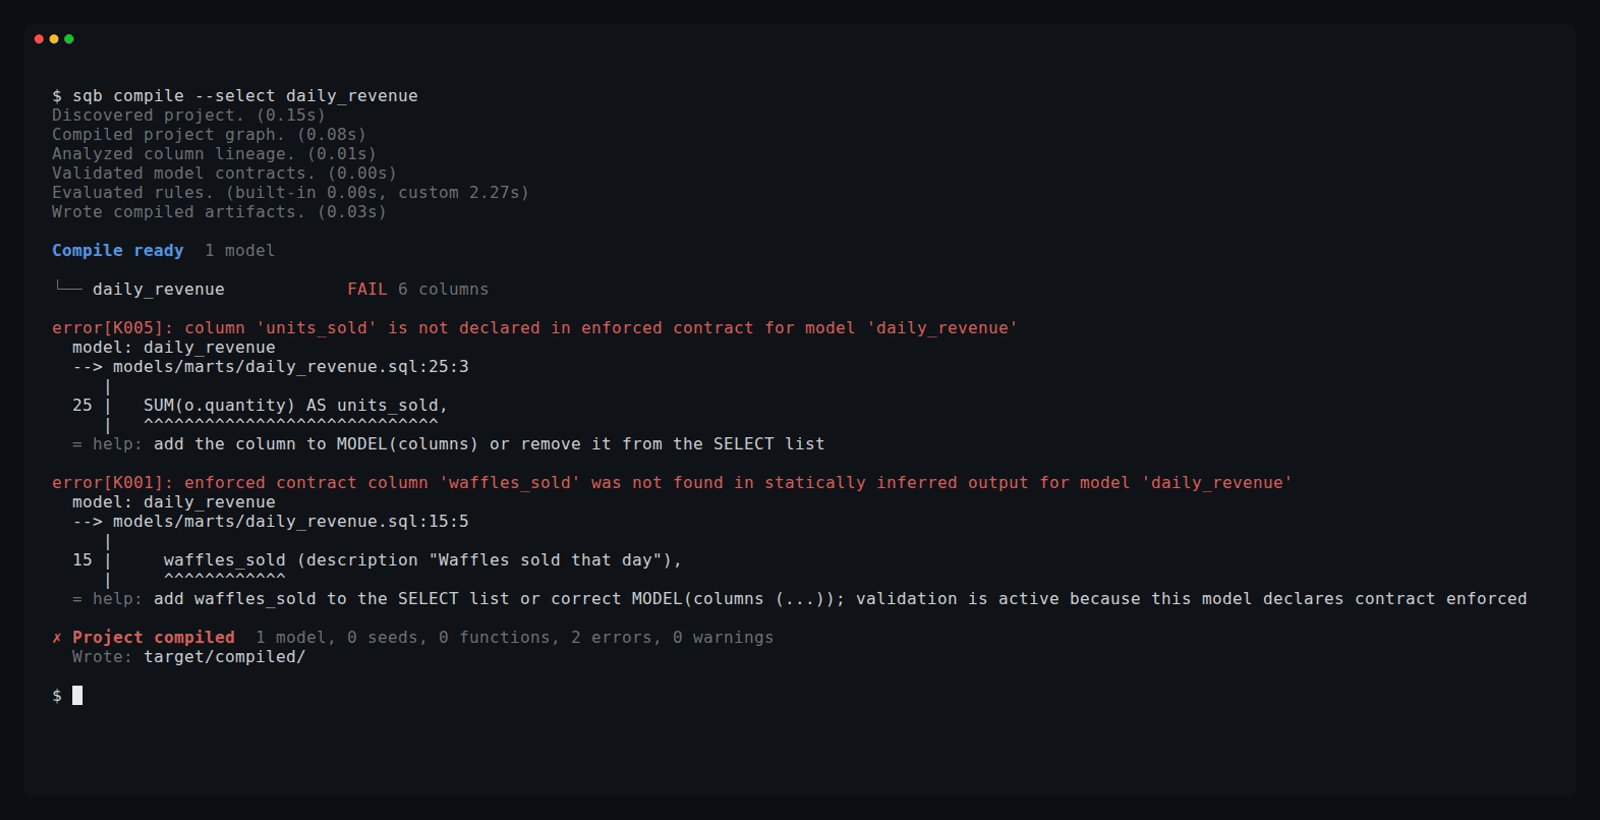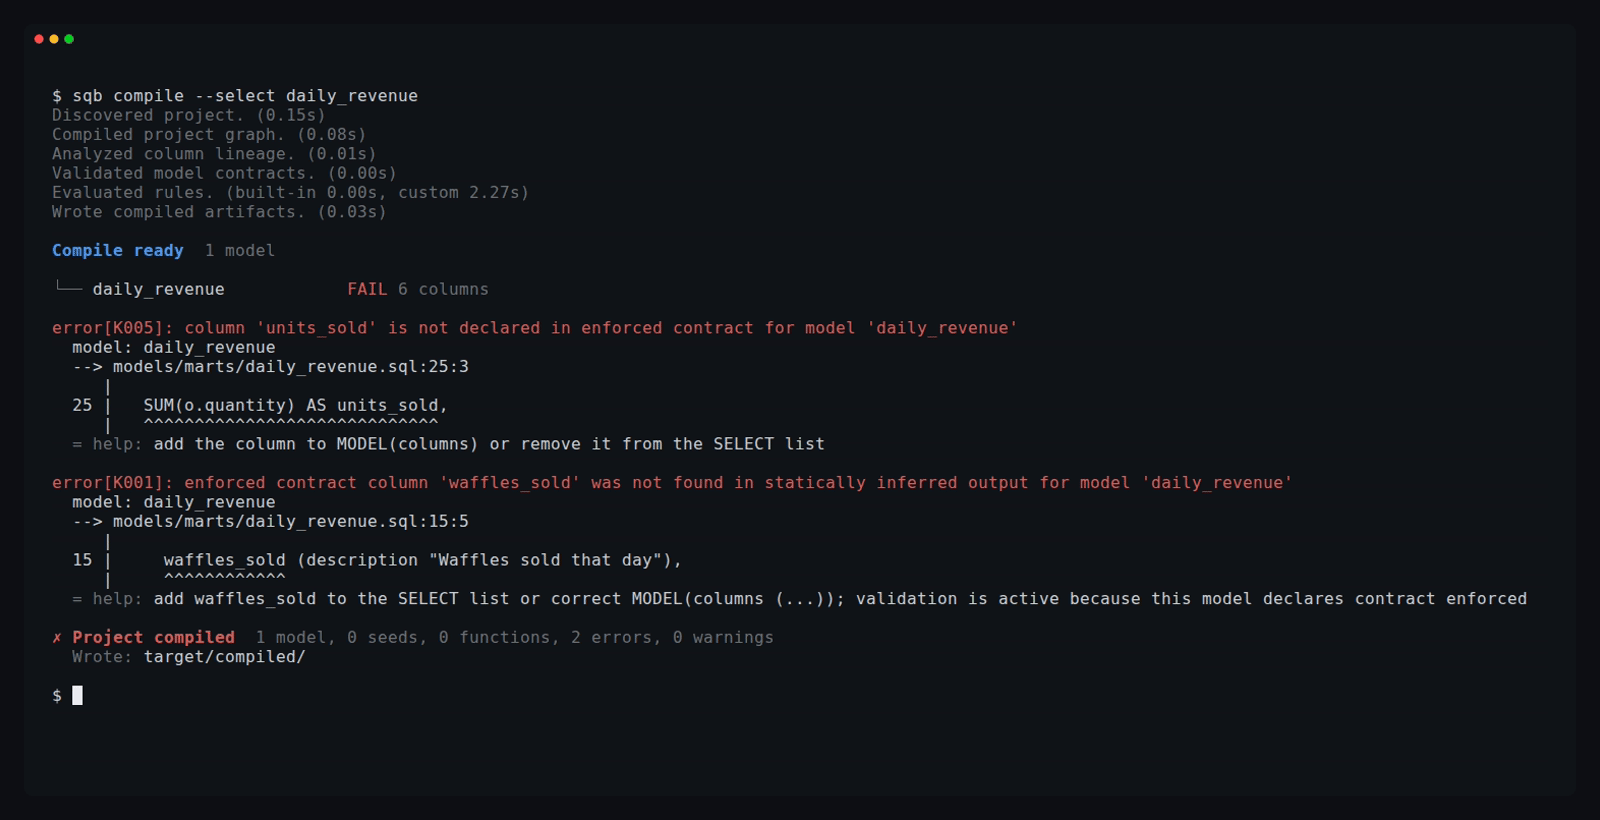
Both sides are reported: the new column isn't in the contract, and the declared one is gone.
Your own conventions as compile errors
Rules are Python functions in your project. This one, from
rules/layers.py, says marts must read sources
through staging:
from sqlbuild.rules import Finding, Model, RuleContext, rule


@rule(
    code="XSQBRARCH001",
    message="Marts must read sources through staging",
    remediation="Reference a staging model with __ref() instead.",
)
def marts_use_staging(*, model: Model, ctx: RuleContext) -> list[Finding]:
    layer = ctx.project.tree.relative_parts(path=model.path, under="models")[0]
    sql = ctx.sql.for_model(model).authored.source
    if layer != "marts" or "__source(" not in sql:
        return []
    line = sql[: sql.index("__source(")].count("\n") + 1
    return [ctx.finding(subject=model, line=line)]
A mart that reads __source("raw__payments") directly now fails, and so does the unit test that
has no mock for it:
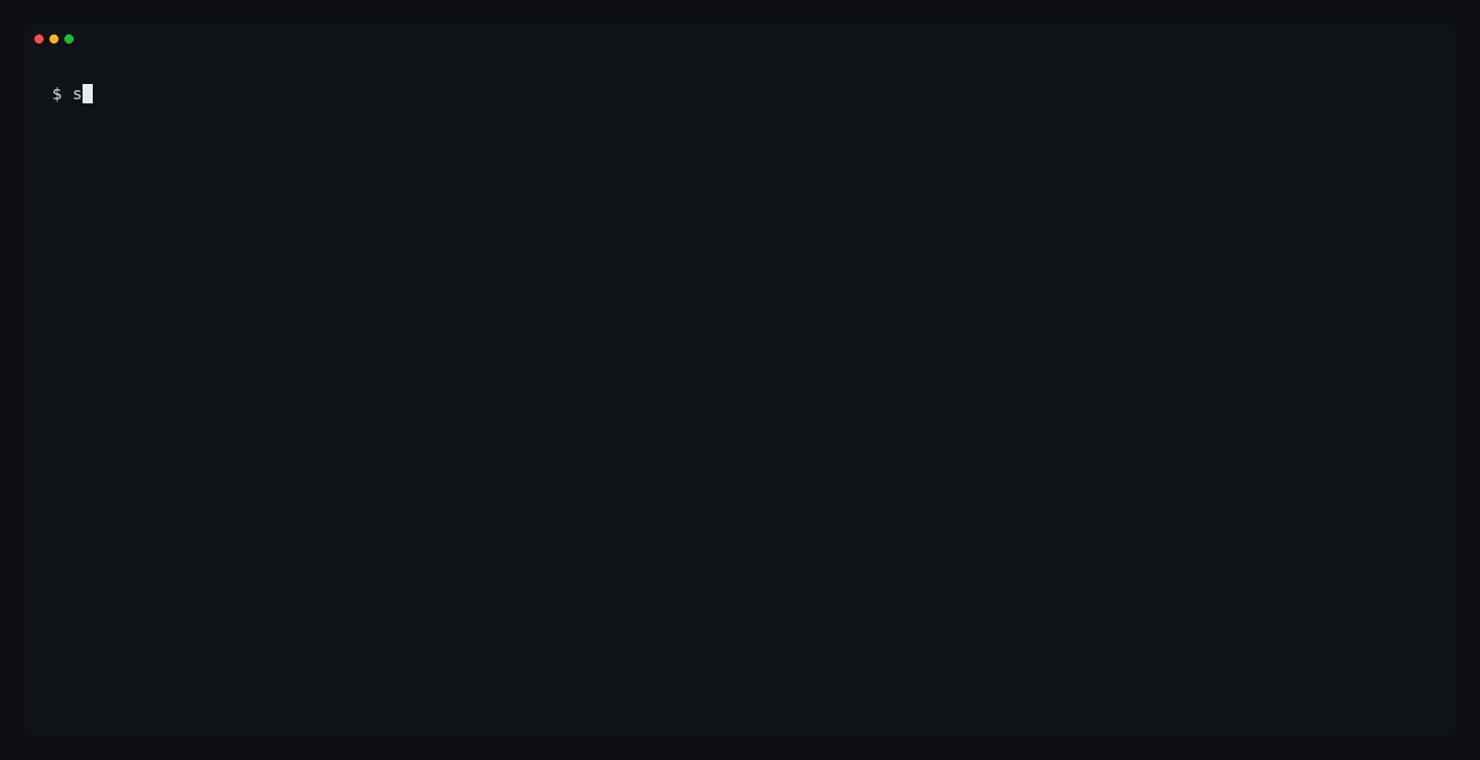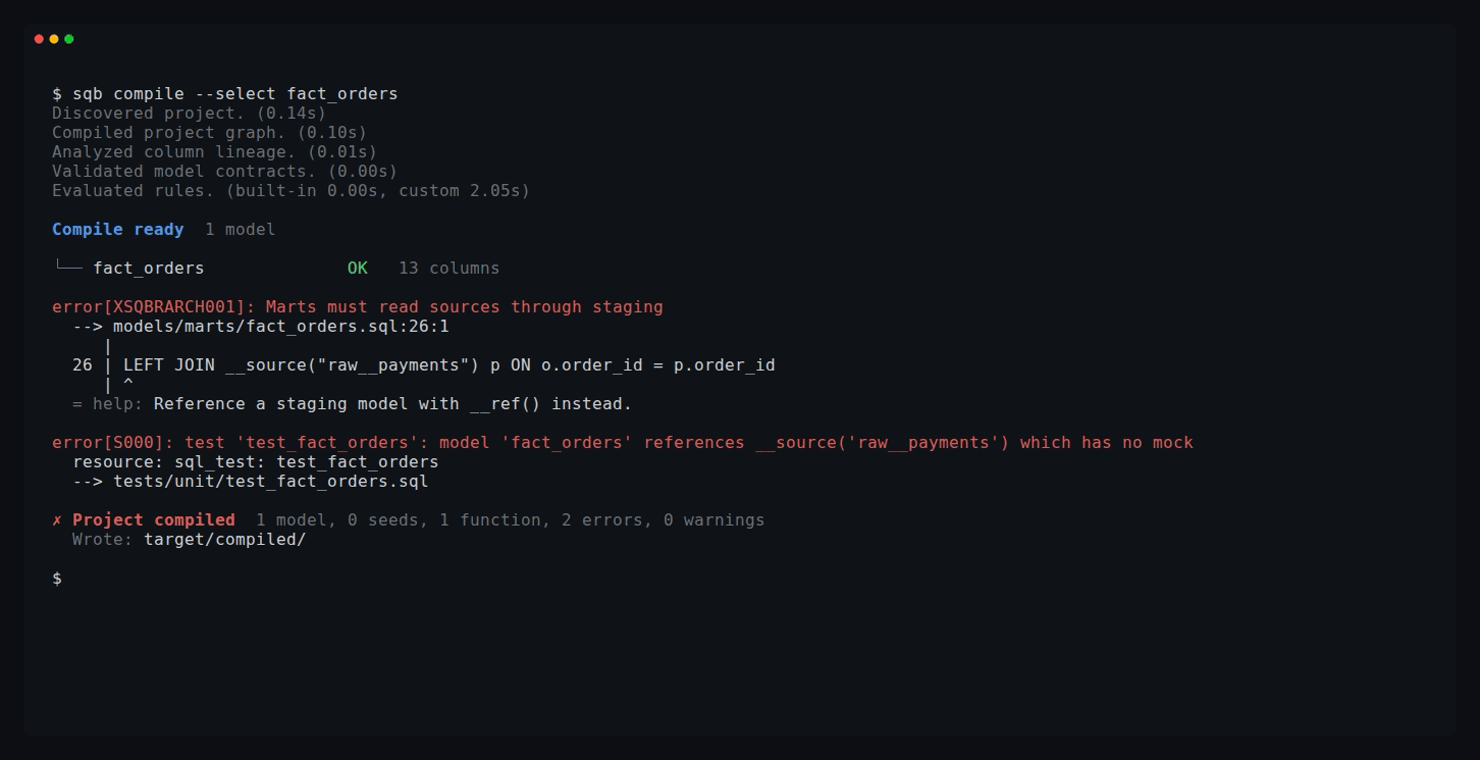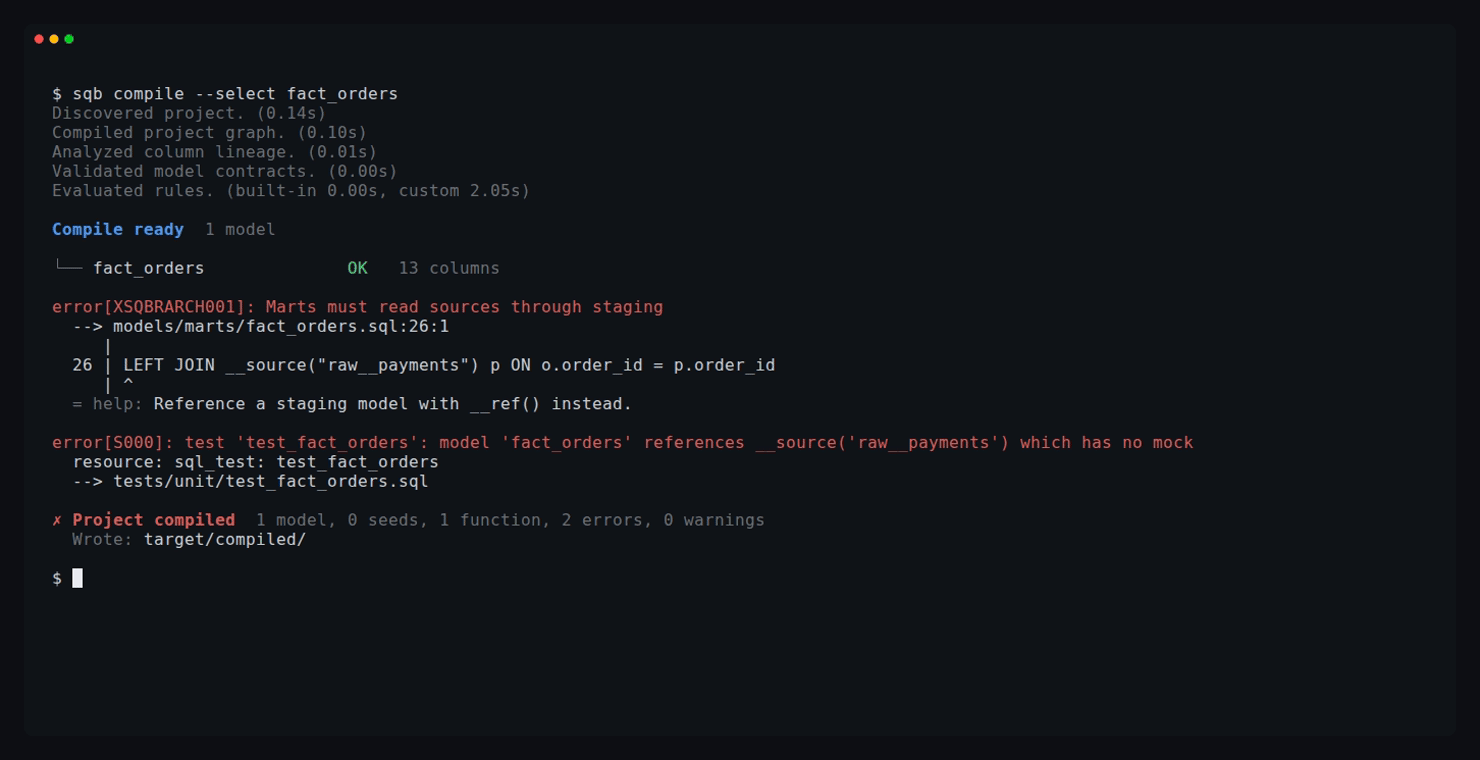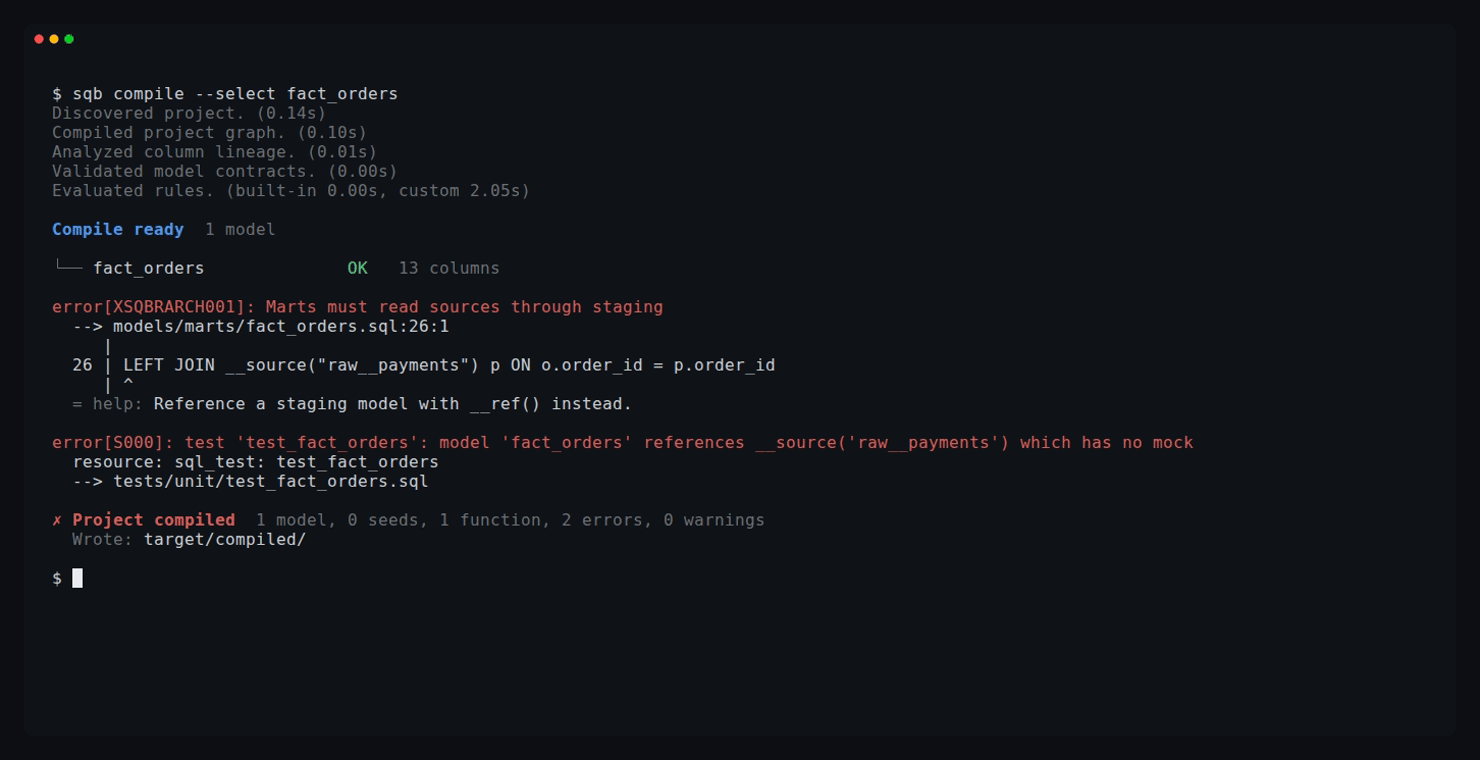
See rules.
See what a move would break
sqb scope --as-path previews moving a model before you move it.
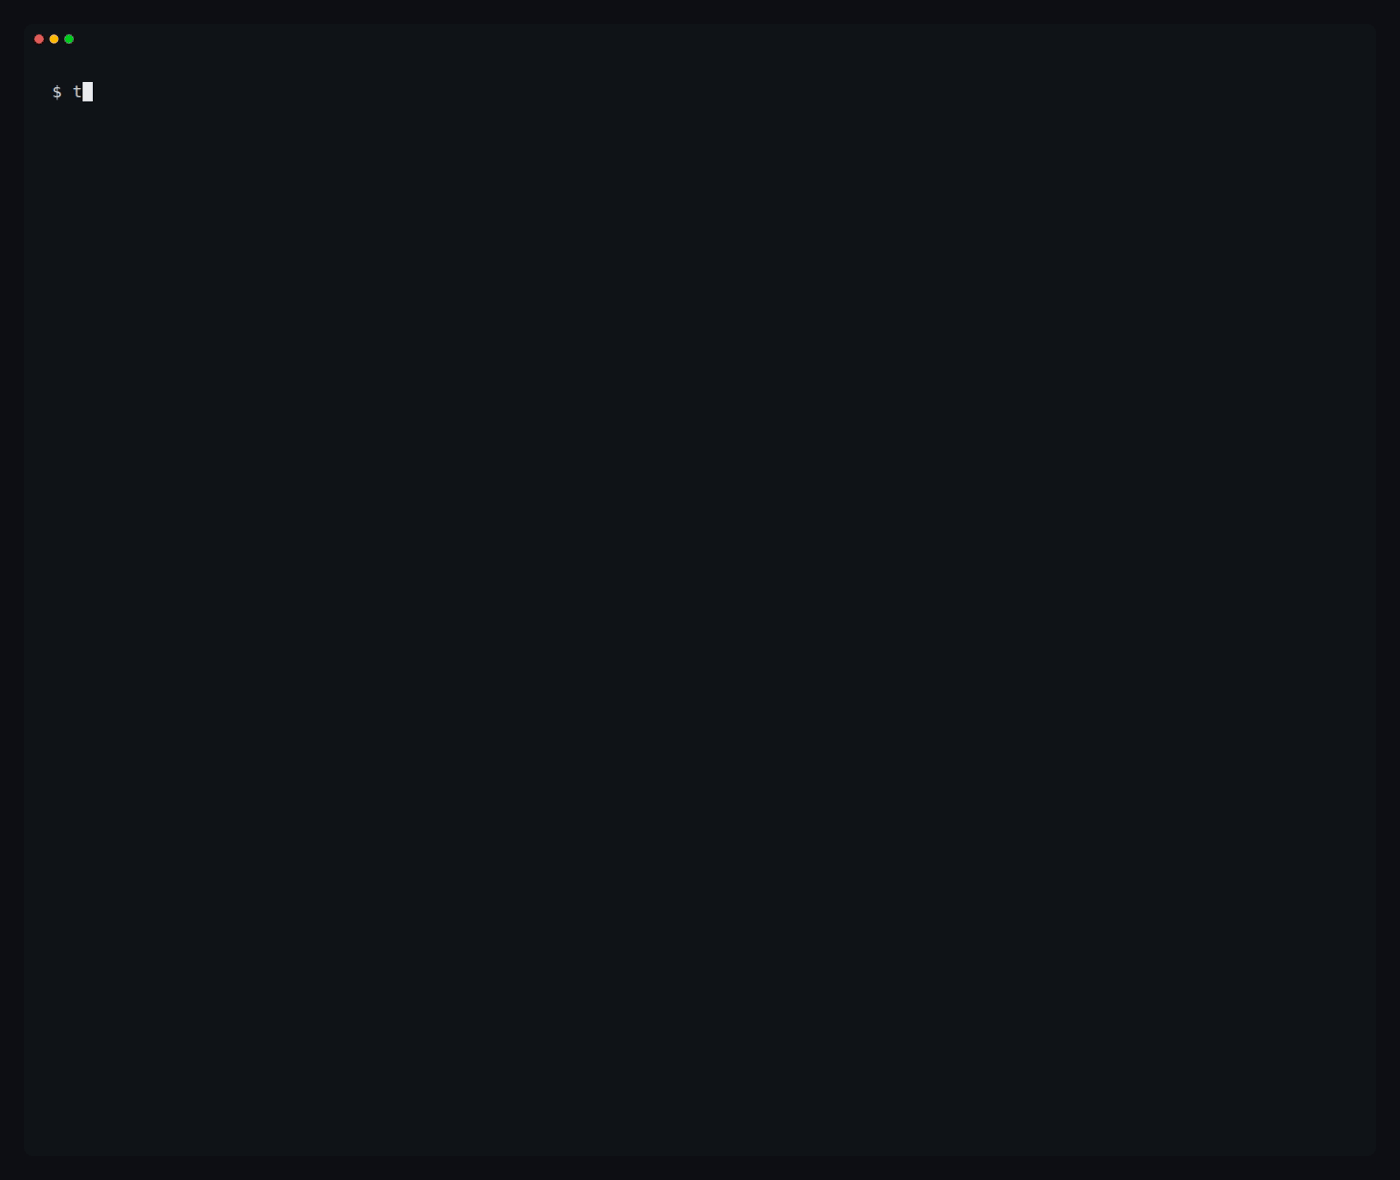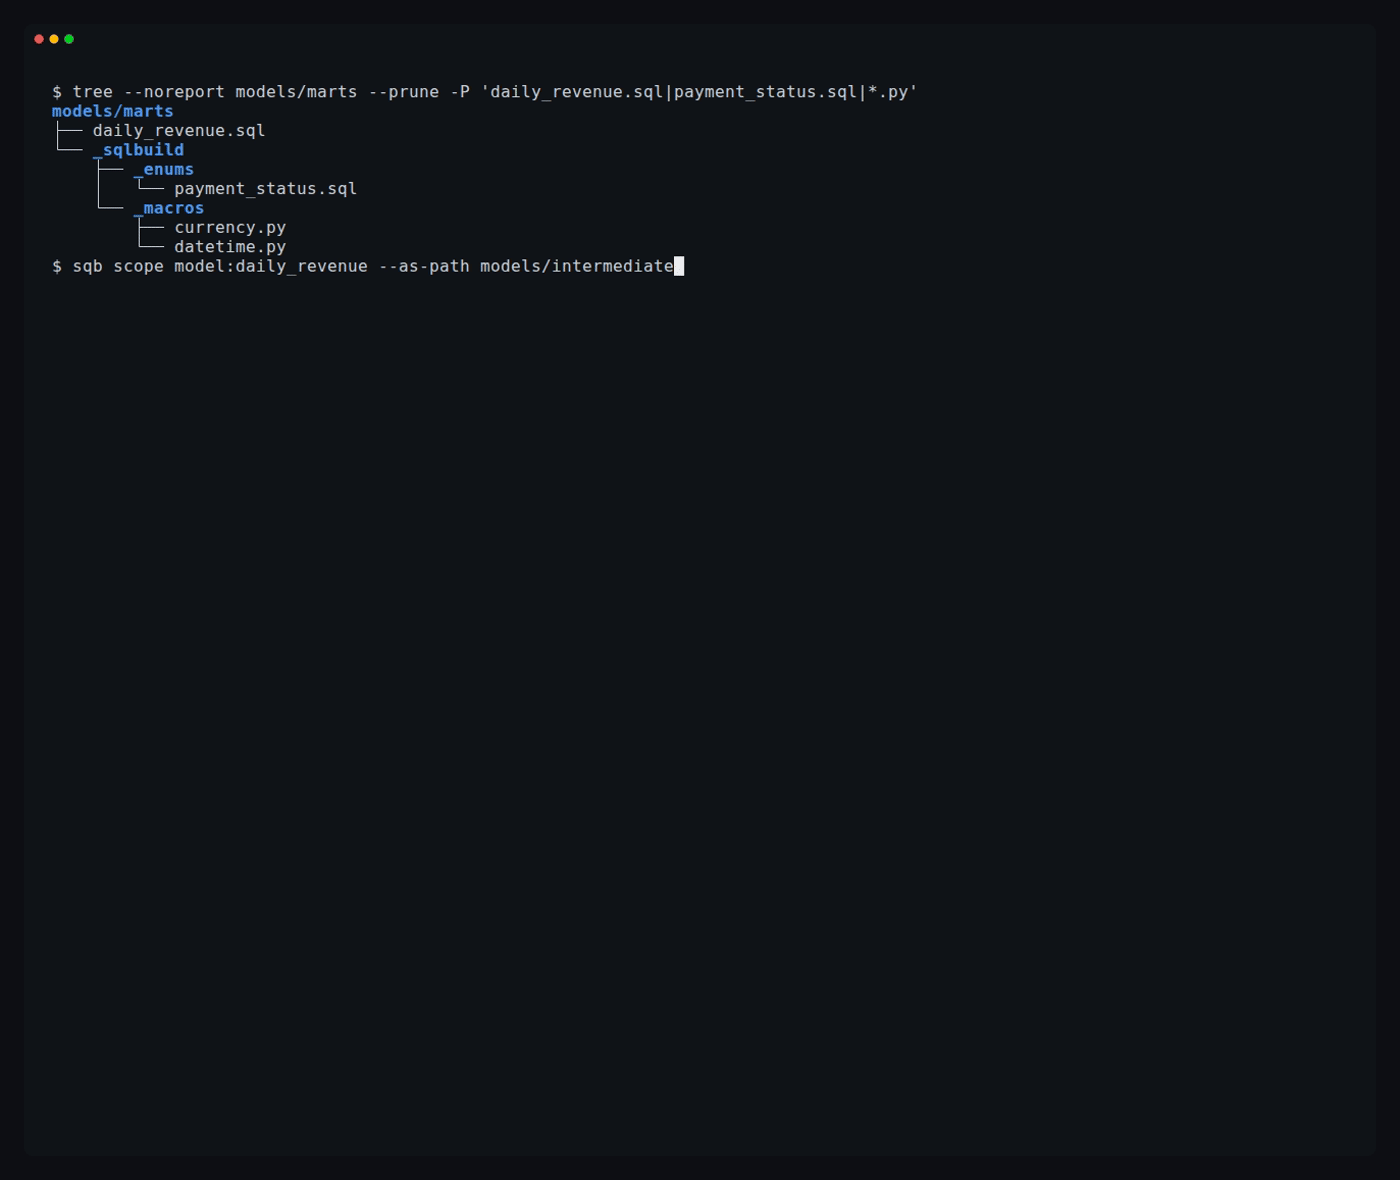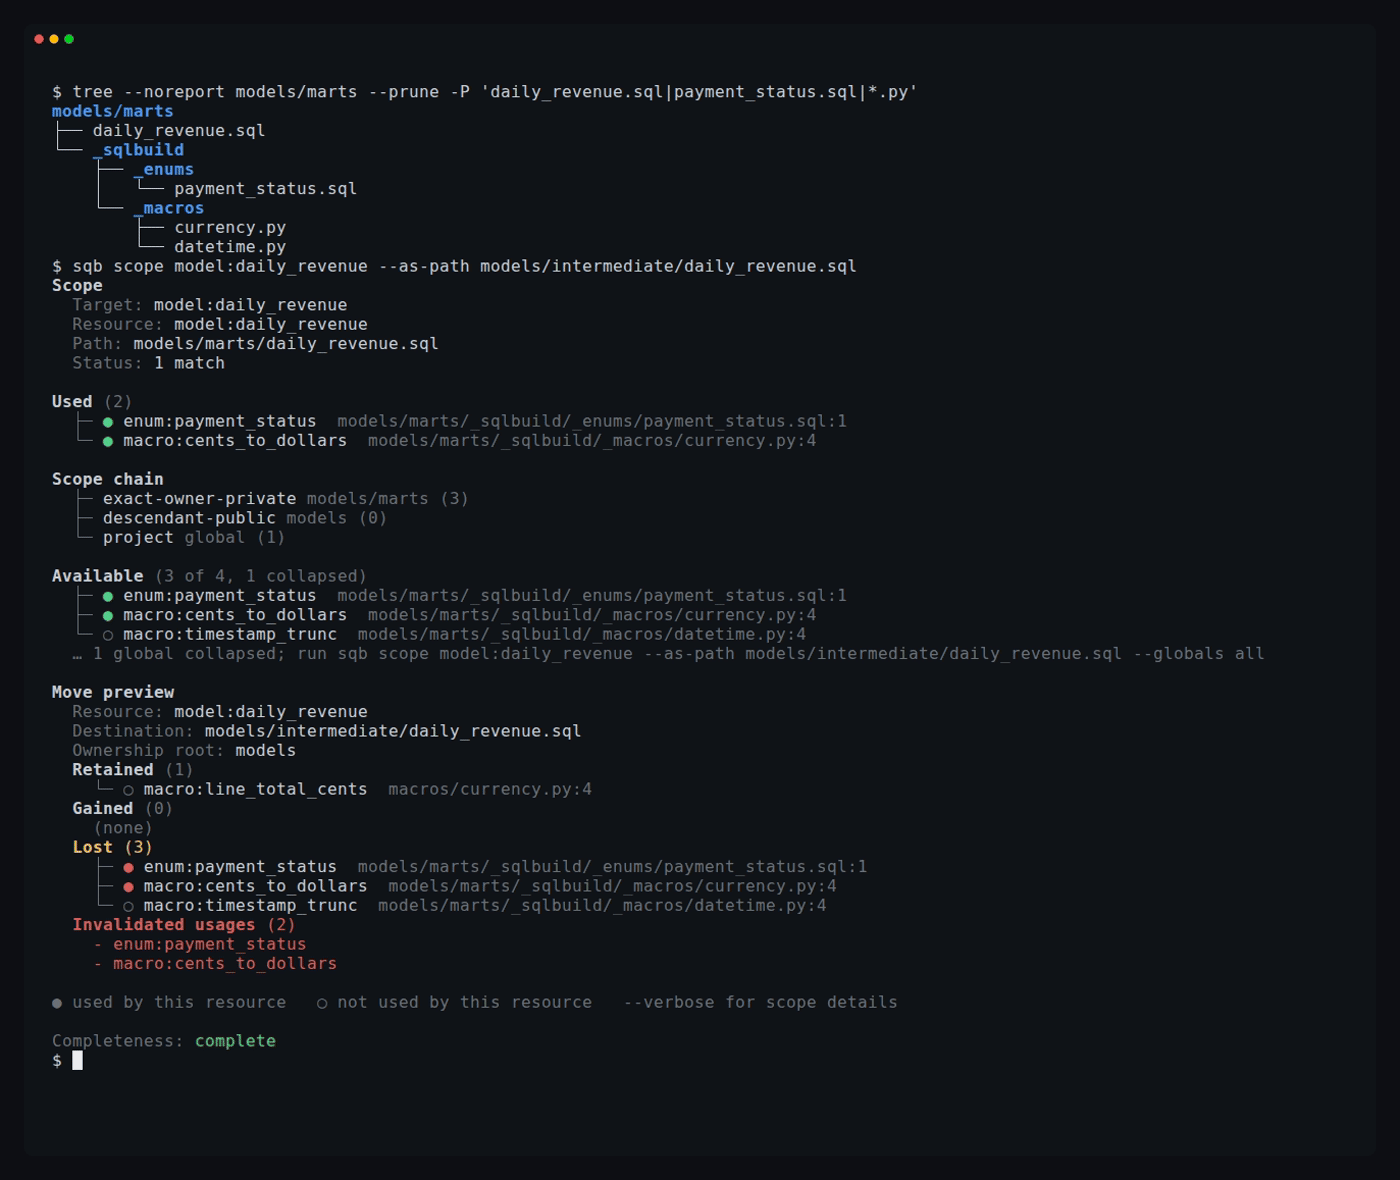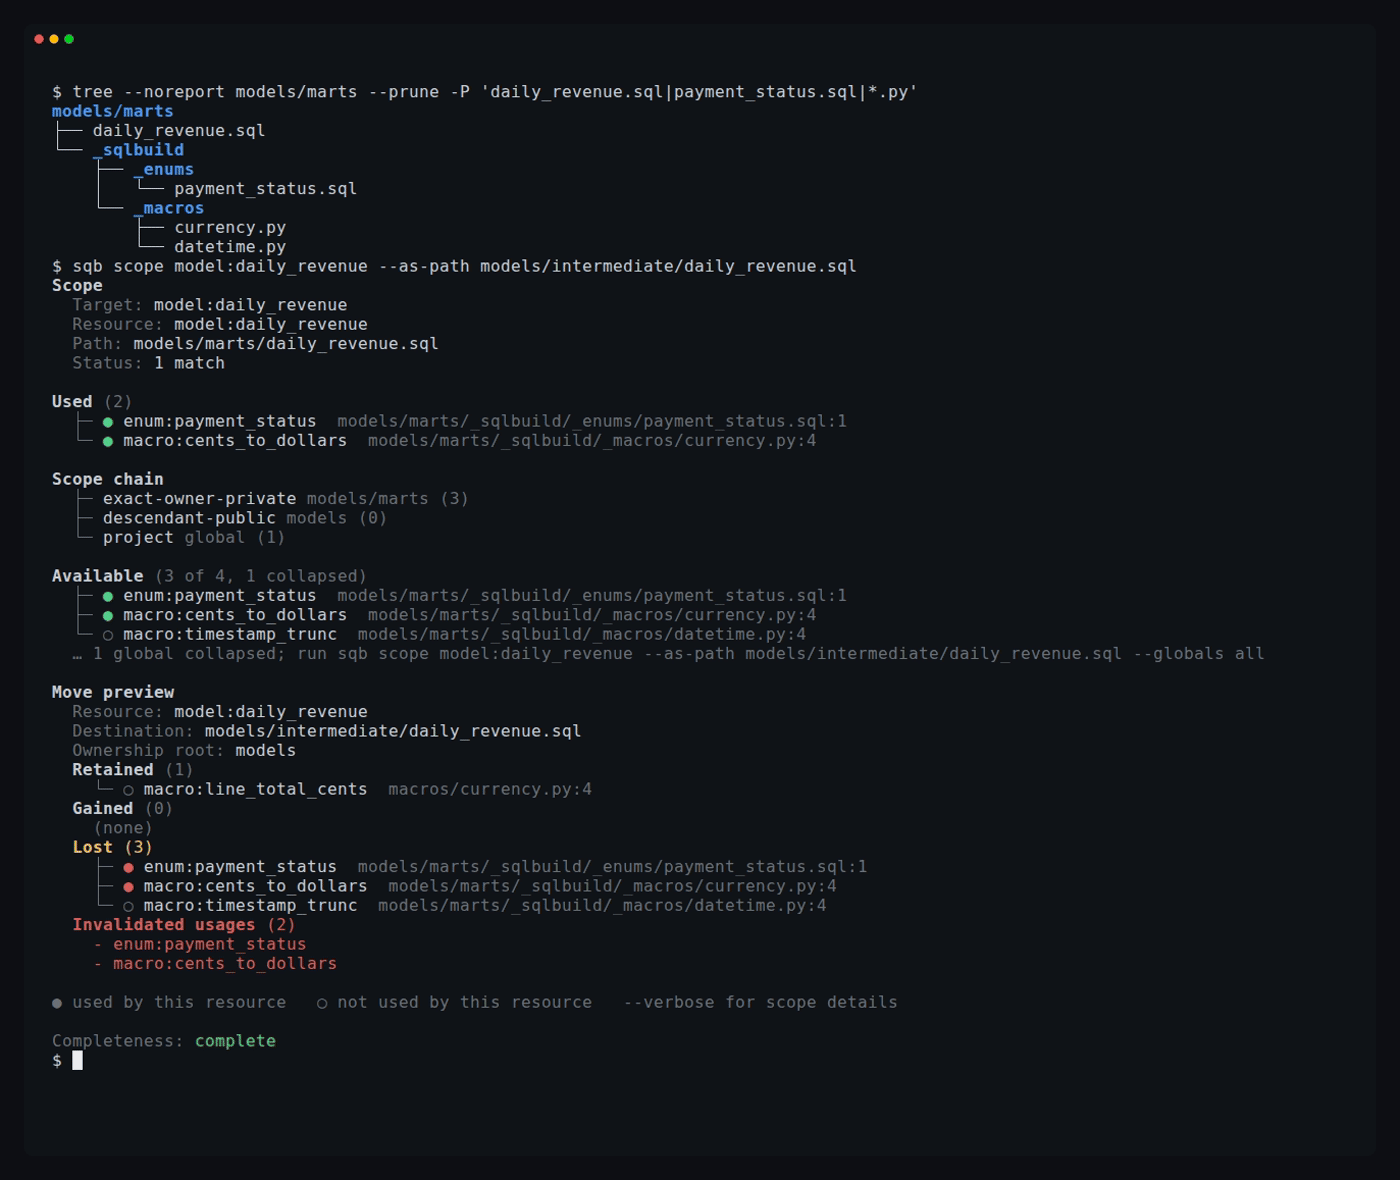
Look at Lost and Invalidated usages: the model uses an enum and a macro that are private to
models/marts, so moving it would break both.
Example
A model is a SQL file with a MODEL() header and a SELECT:
MODEL (
  materialized table,
  columns (
    order_id (audits [not_null, unique]),
  ),
  tags [marts],
);

SELECT
  o.order_id,
  o.customer_id,
  p.amount_cents AS total_cents
FROM __ref("stg_orders") o
JOIN __ref("stg_payments") p USING (order_id)
A test mocks the sources and asserts on the model, resolving every model in between from its real SQL:
TEST();

WITH
__source__raw__orders AS (
  @mock_orders()
),
__source__raw__payments AS (
  SELECT
    1 AS payment_id,
    1 AS order_id,
    1500 AS amount_cents,
    'credit_card' AS method
),
__expected__fact_orders AS (
  SELECT 1 AS order_id, 100 AS customer_id, 1500 AS total_cents
)
SELECT 1
Warehouses
| Warehouse | Status |
|---|---|
| Snowflake | Supported |
| DuckDB | Supported |
| MotherDuck | Supported |
| PostgreSQL | Supported |
| BigQuery | Beta |
| Databricks | Beta |
| SQL Server | Beta |
Snowflake is the main target. Beta adapters build, test and plan, but have had less production use so far. See adapters.
Free and independent
SQLBuild is Apache 2.0 and will stay free: no paid tier, no commercial edition, and no feature held back for one. Its state lives in your warehouse, next to your data. See the roadmap for what's next.
Contributing
Contributions are welcome. See CONTRIBUTING.md.
License
SQLBuild is licensed under the Apache License 2.0.
1 maintainer

Metadata
1 maintainer
Release files for sqlbuild 0.124.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| sqlbuild-0.124.2.tar.gz | 1.8 MB | With provenance | Details |
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| sqlbuild-0.124.2-cp312-abi3-win_amd64.whl | CPython 3.12 | abi3 | Windows x86-64 | Details |
| sqlbuild-0.124.2-cp312-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl | CPython 3.12 | abi3 | Linux glibc 2.17+ x86-64 | Details |
| sqlbuild-0.124.2-cp312-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl | CPython 3.12 | abi3 | Linux glibc 2.17+ ARM64 | Details |
| sqlbuild-0.124.2-cp312-abi3-macosx_11_0_arm64.whl | CPython 3.12 | abi3 | macOS 11.0+ ARM64 | Details |
| sqlbuild-0.124.2-cp312-abi3-macosx_10_12_x86_64.whl | CPython 3.12 | abi3 | macOS 10.12+ x86-64 | Details |
Total release size: 80.0 MB
Release files / sqlbuild-0.124.2.tar.gz
| Download URL | sqlbuild-0.124.2.tar.gz |
|---|---|
| Size | 1.8 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
e7d934391ce06dfaf8f590851ce1779f3f5968b3f06618beb9a1ede7cb2d8e15
|
|
BLAKE2b-256 checksum How to use checksums |
6a62571095caa61574fd4072d6d04f09a498bbbf8345df788c7d3523d5f74860
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 28, 2026.
Transparency logRelease files / sqlbuild-0.124.2-cp312-abi3-win_amd64.whl
| Download URL | sqlbuild-0.124.2-cp312-abi3-win_amd64.whl |
|---|---|
| Size | 16.5 MB |
| Tags | CPython 3.12 Windows x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
2a853c7c26b8e7468aa92689271ca4fbb878c659b259c767431f7baea3b8a2fd
|
|
BLAKE2b-256 checksum How to use checksums |
b29b3d5b7c8486d32fadb63c9ac73264904e53bc13cb211e85f707c506d04600
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 28, 2026.
Transparency logRelease files / sqlbuild-0.124.2-cp312-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | sqlbuild-0.124.2-cp312-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 15.8 MB |
| Tags | CPython 3.12 Linux glibc 2.17+ x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
172a7160820221a20aecfdd2e46cead76a8e9281f21d969e47ceb0e7bf044058
|
|
BLAKE2b-256 checksum How to use checksums |
10c57ef3f1d1fc24715f7bfaed2bd5f691e499ca5680454d4a271e1a80b25ef8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 28, 2026.
Transparency logRelease files / sqlbuild-0.124.2-cp312-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | sqlbuild-0.124.2-cp312-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 15.2 MB |
| Tags | CPython 3.12 Linux glibc 2.17+ ARM64 abi3 |
|
SHA-256 checksum How to use checksums |
cfef847530c755ed59f29226e1d746b8567a8f4b1a08101f0ff3a7a25fd4dfe9
|
|
BLAKE2b-256 checksum How to use checksums |
a245c2a4be2b2d1de7097e01740bb0965f2b49c5b1644927e0a3ac4bf1b3665c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 28, 2026.
Transparency logRelease files / sqlbuild-0.124.2-cp312-abi3-macosx_11_0_arm64.whl
| Download URL | sqlbuild-0.124.2-cp312-abi3-macosx_11_0_arm64.whl |
|---|---|
| Size | 15.1 MB |
| Tags | CPython 3.12 abi3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
b6620fa0478b3b428d6f2bdb8fdb0cfbbb23f21d63cbe8ff2ebf5a35b64d59d0
|
|
BLAKE2b-256 checksum How to use checksums |
1f1f064d645f5fc43982d6363d3e0b3b5fb809db011b78af7022bca73a313c8b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 28, 2026.
Transparency logRelease files / sqlbuild-0.124.2-cp312-abi3-macosx_10_12_x86_64.whl
| Download URL | sqlbuild-0.124.2-cp312-abi3-macosx_10_12_x86_64.whl |
|---|---|
| Size | 15.4 MB |
| Tags | CPython 3.12 abi3 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
9aa2e0d492c97bd6a1adcfb20e1b6a812910899bdc2fc832d6b62ebc61cf024a
|
|
BLAKE2b-256 checksum How to use checksums |
e150c2e3057a27e1bf53e1b78cff8e4b905a5312d6f9ec14af1d67b32e06171a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 28, 2026.
Transparency logSecurity for sqlbuild 0.124.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 6 files in this release have been uploaded with provenance metadata.
Attestation for sqlbuild-0.124.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 28, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














