
timesift 
choosing the time scale of a sensor record


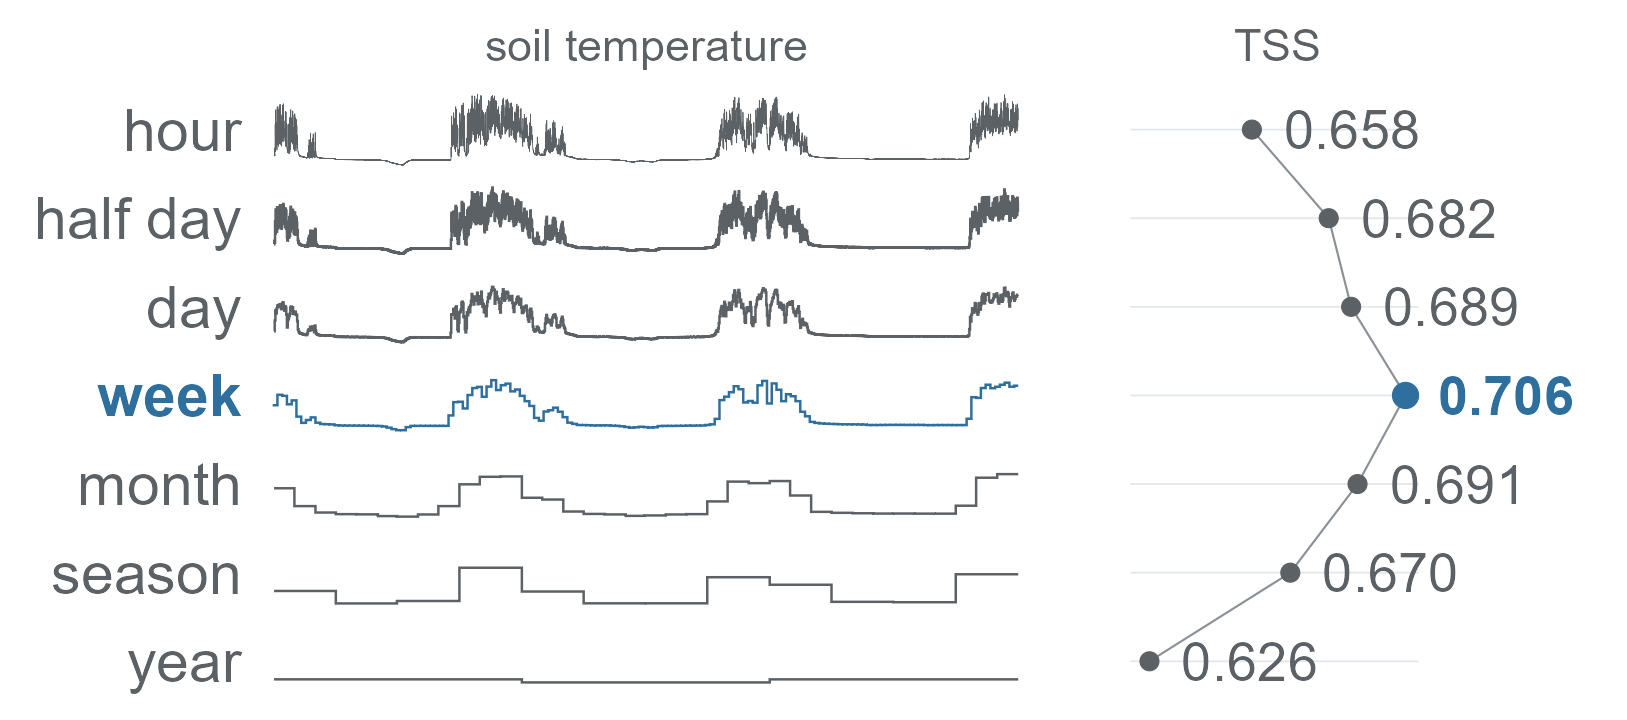
timesift finds the time scale at which a long sensor record best predicts something, such as whether a plant species grows at the plot where a soil temperature logger recorded every hour for three years.
Before a model is fitted, a record like that is usually reduced once, to monthly means or growing-degree-days, and the reduction is rarely revisited. timesift makes it an argument. Each time scale is a grain: the record is cut into calendar bins, a real week or a real month, and each bin is reduced to a statistic such as its mean. The package builds the record at every grain you name, fits each learner on every grain it can read, and scores every pairing on the same held-out folds and the same cells. You can then compare the grains cell by cell, choose one inside the training data, or combine them into an ensemble.
timesift supports:
- Calendar grains and lookbacks. From the readings as recorded through half-days, days, weeks,
months, seasons and years, with day-level statistics such as the coldest and warmest day of each
bin, and
lookback()spans that end at each target's own date. - The learners species distribution modelling uses. Elastic net, stepwise GLM, CART, random forest, boosting, Maxent, surface range envelope, MARS, flexible discriminant analysis, GAM and a one-layer network, plus convolutional and fully connected networks through torch, and any learner of your own.
- Report evaluation scores. The grain and the ensemble weights are chosen inside each outer training fold, so the held-out score covers the choosing too.
- Thin presences. With few presences, the TSS read at its best threshold overstates skill.
tss_inflation()measures the overstatement for your design, andimplied_skill()turns a reported TSS into the skill it is consistent with. - Python and R. This package and the R package call one C++ core, so they give the same arrays and the same baseline fits.
Every learner core is timesift's own code, written from the published method and pinned in the test fixtures against the reference package a species modeller already uses: glmnet, MASS, rpart, earth, mda, mgcv, nnet, maxnet and biomod2. Both test suites assert the same stored digests of the binned record, so a difference between the languages fails a check. A methods section cites the package version, which fixes every core and its defaults.
Installation
pip install timesift
Wheels are built for CPython 3.11, 3.12 and 3.13 on Linux, Windows and macOS. On another interpreter pip builds from the source distribution, which needs a C++17 compiler.
At runtime the package needs only NumPy. The optional parts are extras:
| Extra | Adds | For |
|---|---|---|
torch |
PyTorch | cnn(), rescnn() and mlp() |
contrasts |
SciPy | grain_contrasts() |
plot |
Matplotlib | plot() |
grid |
xarray | project() and range_change() |
pip install "timesift[torch,contrasts,plot]"
A function that needs one of them raises an error naming the package to install when it is missing.
Usage
- Bring two tables:
targets, one row per thing to predict with its response, andseries, the time-stamped readings belonging to those rows. - Call
timesift()with the response columns, the identifier both tables carry, the time column and the grains to compare. - Read the scores, then call
fit.predict()on new rows.
simulate_records() draws a record with a known answer to try this on: 150 sensors with a reading
every three hours for a year, and four responses that depend on the record's seasonal level.
import timesift as ts

sim = ts.simulate_records(n=150, mechanism="season", variables=4,
                          prevalence=0.3, auc=0.9)
targets = {"unit": sim.y.units}
targets.update(zip(sim.y.variables, sim.y.values.T))

fit = ts.timesift(targets, sim.readings, y=list(sim.y.variables),
                  id="unit", time="time",
                  sift=ts.grains("day", "week", "month", "season"))
print(fit)
The printed run lists every candidate with its score on the outer folds, then the selected and
ensemble rows. A candidate is one grain paired with one learner; elasticnet() is the learner
when none is named. The selected and ensemble rows are the numbers to report: the candidate
and the ensemble weights were chosen inside each outer training fold and then scored once on the
held-out fold.
targets and series are mappings of column name to array, which a pandas data frame satisfies.
y selects over its own table by a column name, a list of names, a glob such as "sp_*", or a
function of a name. A table with a missing reading in a bin is refused, and coverage() shows
which unit and bin lack readings. A time column that carries a zone bins by that zone's clock.
fit.predict(new_targets, new_series) rebuilds each member's grain for the new rows and predicts
through the ensemble fitted on every target. type="binary" cuts each response into presence and
absence at a threshold learned from the out-of-fold predictions.
Working across R and Python
The binning, the statistics and the elastic net are one implementation, so the same input gives
the same arrays and the same coefficients in both languages. The fold builders draw on each
language's own random stream, so the same seed gives different folds; write_folds() saves a fold
map and read_folds() reads it in the other language.
The contract between R and Python
lists what each language carries.
Documentation
Start with Choosing how a record is read: one path from two tables to a scored comparison and predictions.
- Python reference: every function, grouped by job.
- Representing a record, Learners, Finding the grain and Ensembles, thresholds and maps: the concepts, with R code that the Python functions of the same name follow.
- Troubleshooting: the errors a run raises and how to fix them.
Getting help
Questions and bug reports go to the issue tracker. With a bug report, include a small example that reproduces it.
Contributing
Building from a checkout, the test suites and the rules for the shared fixtures are in CONTRIBUTING.md.
Support
"Software is like sex: it's better when it's free." — Linus Torvalds
I'm a PhD student who builds R packages in my free time because I believe good tools should be free and open. I started these projects for my own work and figured others might find them useful too.
If this package saved you some time, buying me a coffee is a nice way to say thanks. It helps with my coffee addiction.

License
MIT
Citation
Download the citation as BibTeX or RIS, or use GitHub's "Cite this repository" on the repository.
1 maintainer

Metadata
1 maintainer
Release files for timesift 0.6.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| timesift-0.6.1.tar.gz | 1.5 MB | With provenance | Details for timesift-0.6.1.tar.gz |
Built distributions (wheels)
Total release size: 6.4 MB
Release files / timesift-0.6.1.tar.gz
| Download URL | timesift-0.6.1.tar.gz |
|---|---|
| Size | 1.5 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
fa5559822740e854884b5c545e644884067a87c29ddaa2006cf592d25dfd1387
|
|
BLAKE2b-256 checksum How to use checksums |
07f30facd4ffde7bb2ad5ef2395e6d0809d0aa4d66112914e54da4cf7af52c0a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / timesift-0.6.1-cp313-cp313-win_amd64.whl
| Download URL | timesift-0.6.1-cp313-cp313-win_amd64.whl |
|---|---|
| Size | 684.5 kB |
| Tags | CPython 3.13 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
e4137c7179e16add3ef6231a2c49f5c9a6a146f44ebf206806f9be9ccf591eb0
|
|
BLAKE2b-256 checksum How to use checksums |
e92c6ab13dca3162270137fc1563ba869c1be5c3a8d3f9167d6af00eafe9dc92
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / timesift-0.6.1-cp313-cp313-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | timesift-0.6.1-cp313-cp313-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 497.7 kB |
| Tags | CPython 3.13 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
51346c70cf44f40c4397a53f9560b6d27fb03ace1f6b5a14adafb071fbeea837
|
|
BLAKE2b-256 checksum How to use checksums |
d4bf2c92c43cb8042c97c5f663a374d0a3916d90ca04fbf611c0df5a16f95b1d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / timesift-0.6.1-cp313-cp313-macosx_11_0_arm64.whl
| Download URL | timesift-0.6.1-cp313-cp313-macosx_11_0_arm64.whl |
|---|---|
| Size | 451.8 kB |
| Tags | CPython 3.13 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
cbb2c69bb2756418a285a40d67e0c76dcc01e4adfe9e5495534260c1741c89ee
|
|
BLAKE2b-256 checksum How to use checksums |
76c544328d071b32549b5e4772e6f10b81a3567452c6d4adb7b34f0b67d25e8d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / timesift-0.6.1-cp312-cp312-win_amd64.whl
| Download URL | timesift-0.6.1-cp312-cp312-win_amd64.whl |
|---|---|
| Size | 684.6 kB |
| Tags | CPython 3.12 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
dac3ad6fc353a6ad0bf9cb2f9e6486fb378714b355b1448efae98e2ab7162fb1
|
|
BLAKE2b-256 checksum How to use checksums |
2aac9b656e14fb9f269fe5197b79f1dd17da0ef734d272f1fed0e1ca8c972cf1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / timesift-0.6.1-cp312-cp312-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | timesift-0.6.1-cp312-cp312-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 497.8 kB |
| Tags | CPython 3.12 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
c829059d09dc0ca74eea086a0b22f7cdb3df3a41a04bc4052b909d023403198e
|
|
BLAKE2b-256 checksum How to use checksums |
663506f81cd8df07d08c10cfcc45d4fb320cbbdfe06f15151d9c829dddb81c2c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / timesift-0.6.1-cp312-cp312-macosx_11_0_arm64.whl
| Download URL | timesift-0.6.1-cp312-cp312-macosx_11_0_arm64.whl |
|---|---|
| Size | 451.8 kB |
| Tags | CPython 3.12 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
3bca48957206cbdb53949e42d71f5f02d3272a87e7314b28f5c5268c27ad315f
|
|
BLAKE2b-256 checksum How to use checksums |
777087306224d3b04d720ec1cf2602a7e27316054964577136d5dda2216e7518
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / timesift-0.6.1-cp311-cp311-win_amd64.whl
| Download URL | timesift-0.6.1-cp311-cp311-win_amd64.whl |
|---|---|
| Size | 684.0 kB |
| Tags | CPython 3.11 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
827c6de6c05320ce49d9a4f6fe051f2ac55cc70ccf933b687d6f2d4bdfae1c1f
|
|
BLAKE2b-256 checksum How to use checksums |
4693b7f8bce0dc23e9d90b2d31780873e01b5f8d9ae828c8f5db0418c30d3e2b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / timesift-0.6.1-cp311-cp311-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | timesift-0.6.1-cp311-cp311-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 498.3 kB |
| Tags | CPython 3.11 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
5ff1728eb7b54e515942493e25b493e0bfb3c32191b7fd4031f263c47a6630fe
|
|
BLAKE2b-256 checksum How to use checksums |
d4c0a3a7e2003e25302a9b1fdb5549bdfee607f946c8d1e7127bf51302241b70
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / timesift-0.6.1-cp311-cp311-macosx_11_0_arm64.whl
| Download URL | timesift-0.6.1-cp311-cp311-macosx_11_0_arm64.whl |
|---|---|
| Size | 452.8 kB |
| Tags | CPython 3.11 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
e898aec895e86123f8f10154df2747b9f9886c25ebb8650f403685f38f8497fa
|
|
BLAKE2b-256 checksum How to use checksums |
95b4ca3de088ca69582c6a4ce52c7c8f5a440511a3b9d728df7dcba6646cf020
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logSecurity for timesift 0.6.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 10 files in this release have been uploaded with provenance metadata.
Attestation for timesift-0.6.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














