
vdjmatch — TCR peptide–MHC annotation



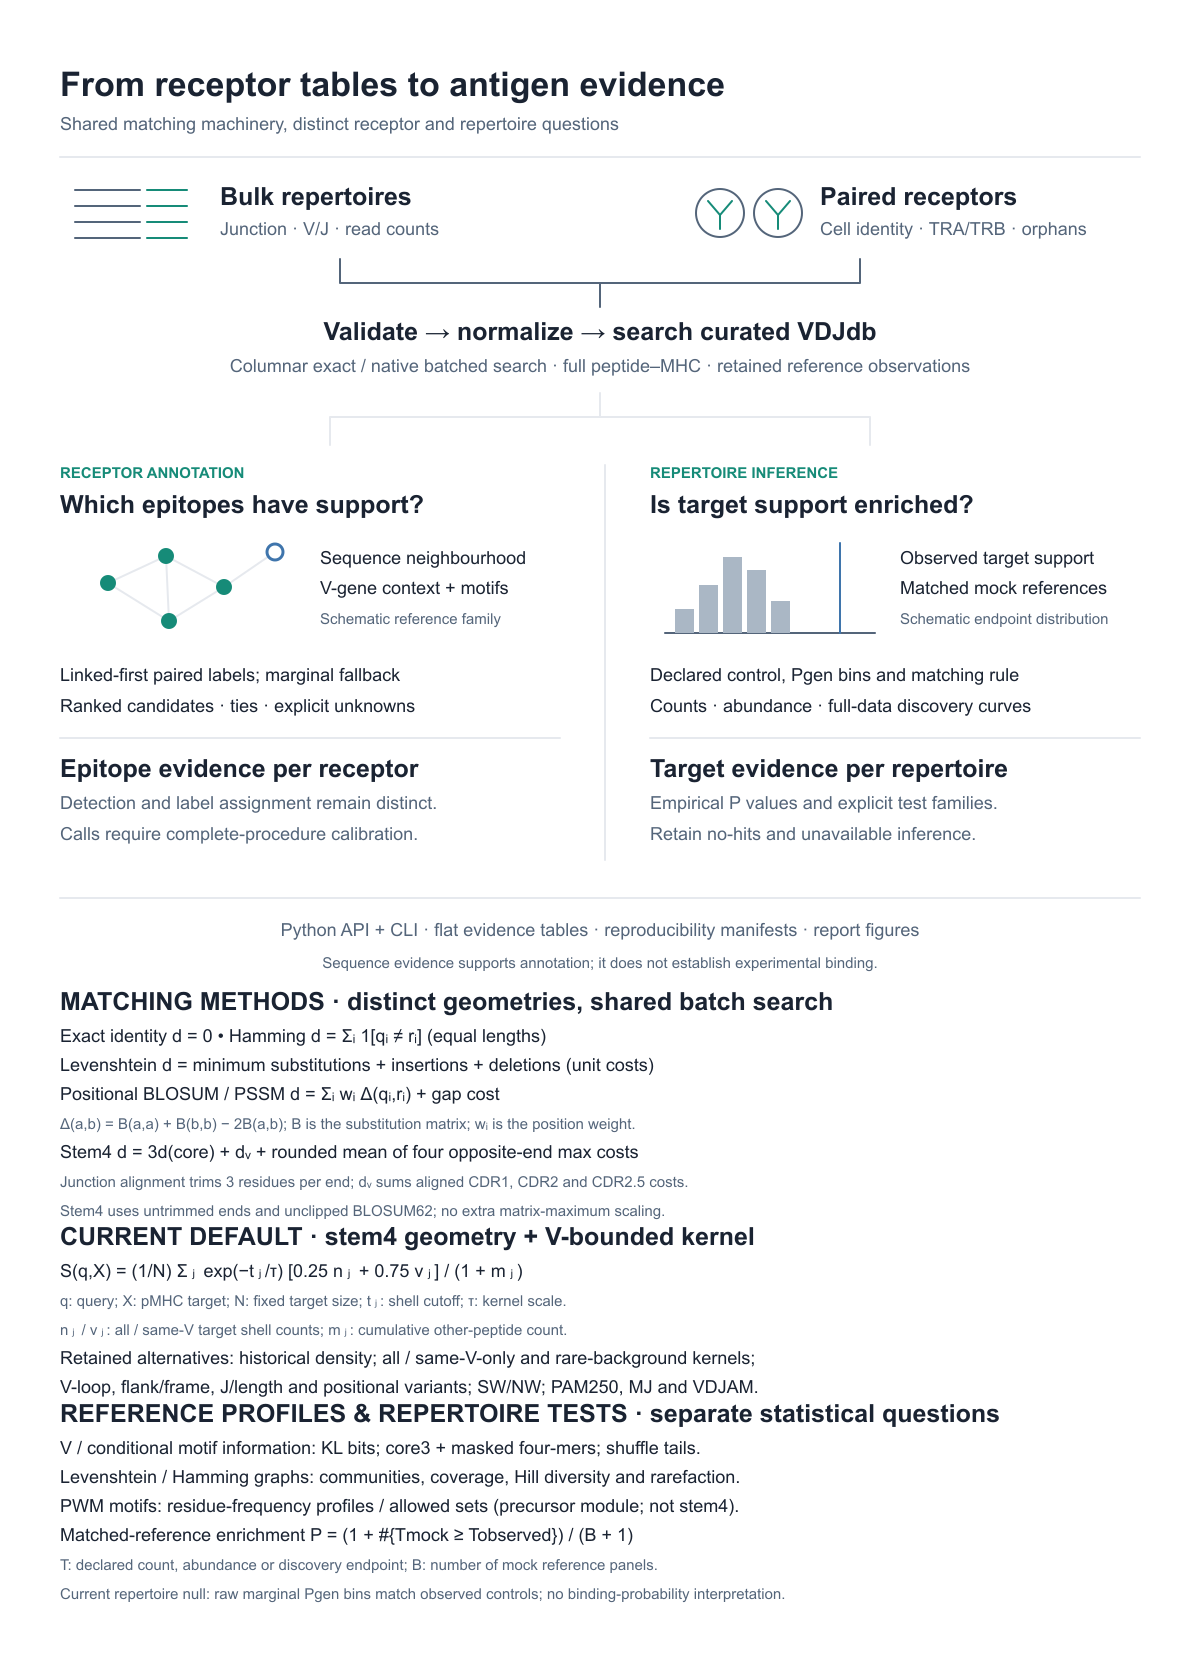
vdjmatch annotates selected T-cell receptors and repertoires against
VDJdb, preserving query identities and
reporting peptide–MHC candidates, competing evidence and optional background calibration.
Native sequence search uses seqtree;
repertoire ingestion reuses published vdjtools readers.
Requires released seqtree>=1.3.2 and vdjtools>=5.6.0, including allocation-aware
native thread validation.
Quick start
python -m pip install vdjmatch
vdjmatch annotate sample.tsv --threads 4 -o annotation
Use AIRR junction_aa (including conserved anchors) and V calls. The curated
VDJdb reference is fetched on first use; add --vdjdb reference.zip for offline
input. Single TRA/TRB receptors and paired receptors are supported. Exact hits
are retained by default. Scores describe sequence evidence, not proof of binding.
For a small offline example, download the examples directory and run
sh examples/annotate.sh annotation-demo from the repository root.
Documentation
| Need | Guide |
|---|---|
| Learn the workflow | Getting started · Rendered notebooks |
| Annotate a cohort or use an offline reference | How-to guides · Runnable examples |
| Look up inputs, options and outputs | CLI reference · Python API |
| Understand methods and formulas | Scoring · Evidence and calibration |
| Test repertoire enrichment | Matching, nulls and count units |
| Estimate precursor frequency | Method · Experimental compendium |
The legacy Java/Groovy implementation remains on legacy-java
and Java tag 1.3.1, with
JitPack artifact com.github.antigenomics:vdjmatch:1.3.1.
License
ISALGO LAB Academic and Non-Commercial Research License v1.0. See LICENSE.
1 maintainer

Metadata
1 maintainer
Release files for vdjmatch 1.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| vdjmatch-1.2.0.tar.gz | 2.0 MB | With provenance | Details for vdjmatch-1.2.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| vdjmatch-1.2.0-py3-none-any.whl | Python 3 | none | any | Details for vdjmatch-1.2.0-py3-none-any.whl |
Total release size: 2.9 MB
Release files / vdjmatch-1.2.0.tar.gz
| Download URL | vdjmatch-1.2.0.tar.gz |
|---|---|
| Size | 2.0 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
870fcc10f7939353af51eeb7f4788c9674827e8578c8e921f2724439907edd63
|
|
BLAKE2b-256 checksum How to use checksums |
5978c6f7f3de22483f118ab0534fa4c4ac99928e60ec568c9f5ec1ddee42b378
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 2, 2026.
Transparency logRelease files / vdjmatch-1.2.0-py3-none-any.whl
| Download URL | vdjmatch-1.2.0-py3-none-any.whl |
|---|---|
| Size | 879.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
773e6eeac3b2b7e09a11d9454b840873b07320b79077ad1109ce31219dbed44b
|
|
BLAKE2b-256 checksum How to use checksums |
f37878b7d75e0ca607a5415b5bf62bc8eb0ee1df1cdb14b017c6641ed147aef2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 2, 2026.
Transparency logSecurity for vdjmatch 1.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for vdjmatch-1.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 2, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














