
WHAXON
One platform. Every layer of security.



WHAXON turns your pentest tools into a pipeline. One catalog, three interfaces (terminal, desktop, web). Three things it does that most tools do not:
- Deterministic auto-chaining. When nmap finds an HTTP port on
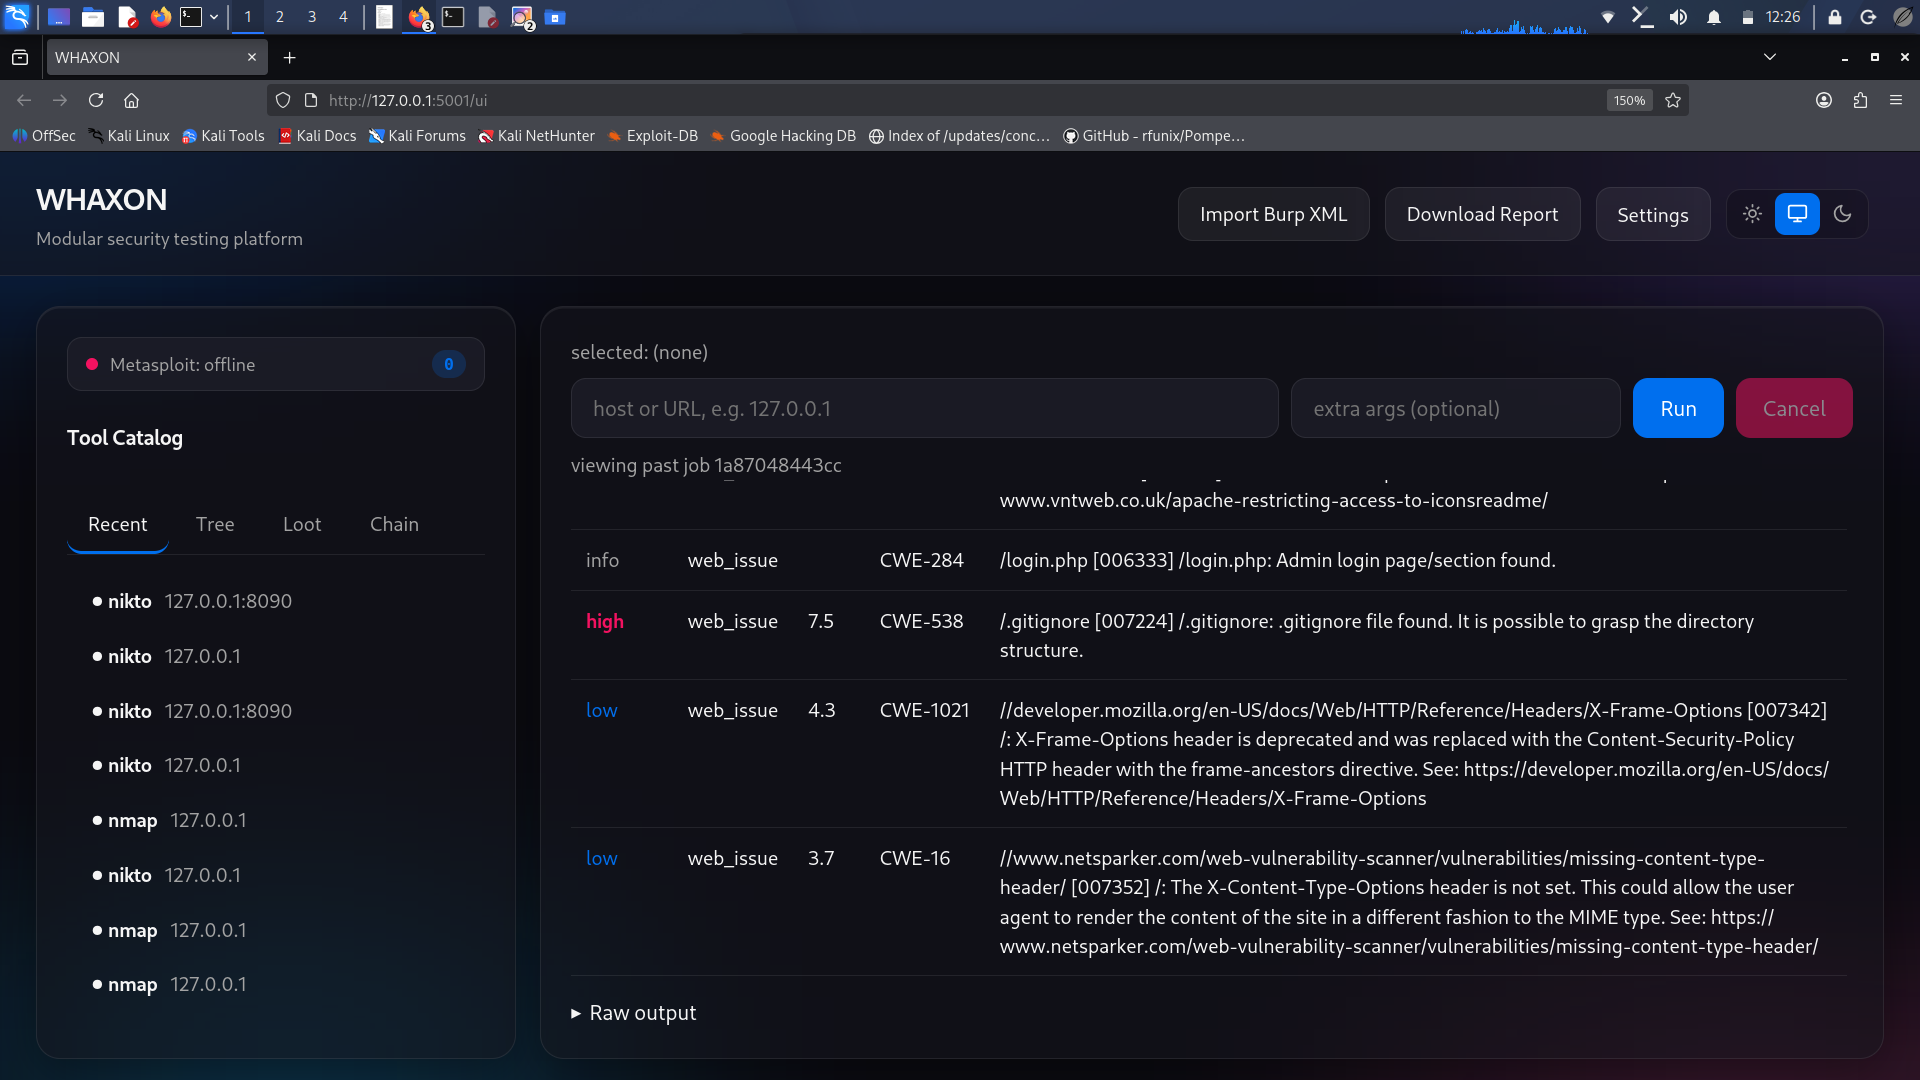
127.0.0.1:8090, WHAXON queues nikto against that specific port automatically. Rule-based, no LLM in the loop — just a rule that fires on findings. Turn it off withWHAXON_AUTOCHAIN=false. - Cross-tool correlation. nmap says port 8090 is open. nikto says
/login.phpis on 8090. WHAXON emits aweb_login_surfacefinding that says both, because that is what a pentester wants to know. Eight rules today, all deterministic, all testable offline. - AI with hard guardrails. An optional AI layer proposes the next action. A deterministic executor validates every proposal before anything runs: catalog check, scope check, target lock, dedup guard, stagnation stop. The planner proposes; the executor disposes.
Status
v0.3 — adapter architecture, deterministic automation, cross-tool correlation, optional AI with executor guardrails, three working interfaces.
Working now
| Feature | Status |
|---|---|
| Headless core (catalog + runner + event bus) | Working |
| Terminal interface (Textual) | Working |
| Desktop interface (PySide6 + QWebEngineView) | Working |
| Web interface (Flask + SSE + Basic auth) | Working |
Production WSGI server (whaxon serve --daemon) |
Working |
| Tool catalog with argument templates | Working (11 tools) |
| Adapter layer | Working (14 adapters) |
| Enriched findings (CVSS, CWE, impact, remediation) | Working |
| Fail-closed scope enforcement | Working |
| Deterministic auto-chain (nmap -> nikto per web port) | Working |
| Correlation engine | Working (8 rules) |
| Pivot chain graph + rendering | Working |
| Burp XML import | Working |
| SQLite persistence across all interfaces | Working |
| Reports (per-job MD/HTML/PDF + engagement MD/JSON/PDF) | Working |
| Evidence attachments | Working |
| Metasploit RPC integration | Working |
| AI layer (Ollama / OpenAI / Anthropic / Google) | Working, opt-in |
| Plugin API (entry-point adapters) | Working |
| Published to PyPI | |
| Test suite | 517 passing |
Planned
| Feature | Priority |
|---|---|
| Web UI file upload for Burp XML | Near term |
| Multi-user auth + projects | Medium term |
| Demo GIF + video walkthrough | Near term |
Try WHAXON in 60 seconds
pip install whaxon
whaxon init --demo
whaxon run nmap scanme.nmap.org --extra "-F -T4"
That last command scans — a public host Nmap's authors maintain specifically for people to test their scanners against. You get:
[2 findings]
  [MEDIUM  ] open_port  22/tcp  open  ssh    OpenSSH 6.6.1p1
  [INFO    ] open_port  80/tcp  open  http   Apache httpd 2.4.7

job: 9a52ab3c5b7b
report: whaxon report 9a52ab3c5b7b
Then:
whaxon findings scanme.nmap.org        # every finding against that target
whaxon report 9a52ab3c5b7b --open      # view the report
The demo scope permits only , , and . Try and it will refuse — that is what fail-closed scope looks like.
Install
pip install whaxon
Optional extras:
pip install "whaxon[tui]"           # Terminal UI (Textual)
pip install "whaxon[gui]"           # Desktop app (PySide6)
pip install "whaxon[web]"           # Web interface (Flask)
pip install "whaxon[metasploit]"    # Metasploit RPC client
pip install "whaxon[tui,gui,web]"   # Everything
Then:
whaxon init                # create data/ with strict default scope
whaxon tui                 # Terminal UI (Textual)
whaxon gui                 # Desktop app (PySide6)
whaxon serve --daemon      # Production web server
whaxon web                 # Web, foreground (dev)
Quick start (from source)
git clone https://github.com/andreipath26/WHAXON.git
cd WHAXON
python3 -m venv .venv
source .venv/bin/activate
pip install -e ".[tui,gui,web]"
Requires Python 3.11+.
whaxon init                # create data/ with strict default scope
whaxon tui                 # Terminal UI (Textual)
whaxon gui                 # Desktop app (PySide6)
whaxon serve --daemon      # Production web server
whaxon web                 # Web, foreground (dev)
Web UI: http://127.0.0.1:5001/ui
Configuration
| Variable | Default | Purpose |
|---|---|---|
WHAXON_HOST |
127.0.0.1 |
Bind address |
WHAXON_PORT |
5001 |
Port |
WHAXON_DATA |
data |
Data directory |
WHAXON_AUTH_USER |
whaxon |
Basic auth username |
WHAXON_AUTH_PASS |
whaxon |
Basic auth password (hashed at startup) |
WHAXON_AUTH_PASS_HASH |
(unset) | Pre-hashed password; takes priority over WHAXON_AUTH_PASS |
WHAXON_AUTOCHAIN |
true |
nmap -> nikto auto-chain on web ports |
WHAXON_MSF_AUTOCHAIN |
false |
Run post modules after a Metasploit exploit session opens |
WHAXON_MSF_TIMEOUT |
(unset) | Timeout for Metasploit RPC calls |
WHAXON_AI_SCOPE_EXPANSION |
strict |
AI scope-expansion policy. v1 ships strict only. |
WHAXON_AI_ENABLED |
false |
Master switch for the AI planner layer |
WHAXON_AI_PROVIDER |
null |
null / rules / ollama / openai / anthropic / google |
WHAXON_AI_MODEL |
per-backend | Model name for the selected provider |
WHAXON_AI_MAX_STEPS |
12 |
Step budget per AI run |
WHAXON_AI_MIN_CONFIDENCE |
0.55 |
Actions below this confidence become ask_human |
WHAXON_OLLAMA_HOST |
http://127.0.0.1:11434 |
Ollama backend endpoint |
WHAXON_OPENAI_HOST |
(OpenAI default) | OpenAI-compatible endpoint override |
WHAXON_ANTHROPIC_HOST |
(Anthropic default) | Anthropic endpoint override |
WHAXON_GOOGLE_HOST |
(Google default) | Google/Gemini endpoint override |
Change the auth credentials before exposing WHAXON on any network.
Adapters
Every tool can have an adapter — a Python class that parses its output and enriches findings.

Built-in: nmap, nikto, sqlmap, burp, hashcat, impacket, msf.
Catalog tools without an adapter still run; their output just isn't enriched.
See docs/adapters.md for the built-in adapter layer.
For shipping an adapter as a separate pip package, see docs/plugins.md.
Scope
Fail-closed. Missing data/scope.json gets a strict default on first load. Unreadable config raises.
whaxon scope --show
whaxon scope --check <target>
whaxon scope --set scope.json
whaxon scope --enable / --disable
whaxon scope --clear
See docs/scope.md.
Interfaces
- Terminal (
whaxon tui):rrun,xcancel,gchain,ssave report,Ctrl+Qquit. - Desktop (
whaxon gui): native window hosting the web UI in aQWebEngineView. - Web (
whaxon serve --daemon): Flask + SSE. API + browser UI at/ui. - CLI: 21 subcommands — see docs/interfaces.md.
Reports
whaxon report <job_id>                              # Per-job, Markdown
whaxon report <job_id> --format html                # Per-job, HTML
whaxon report <job_id> --format pdf --out scan.pdf  # Per-job, PDF
whaxon report --engagement default --format md      # Engagement, Markdown
whaxon report --all --format whaxon                 # Engagement, signed .whaxon
curl -u whaxon:whaxon "http://127.0.0.1:5001/api/report?format=md"   # Engagement via HTTP
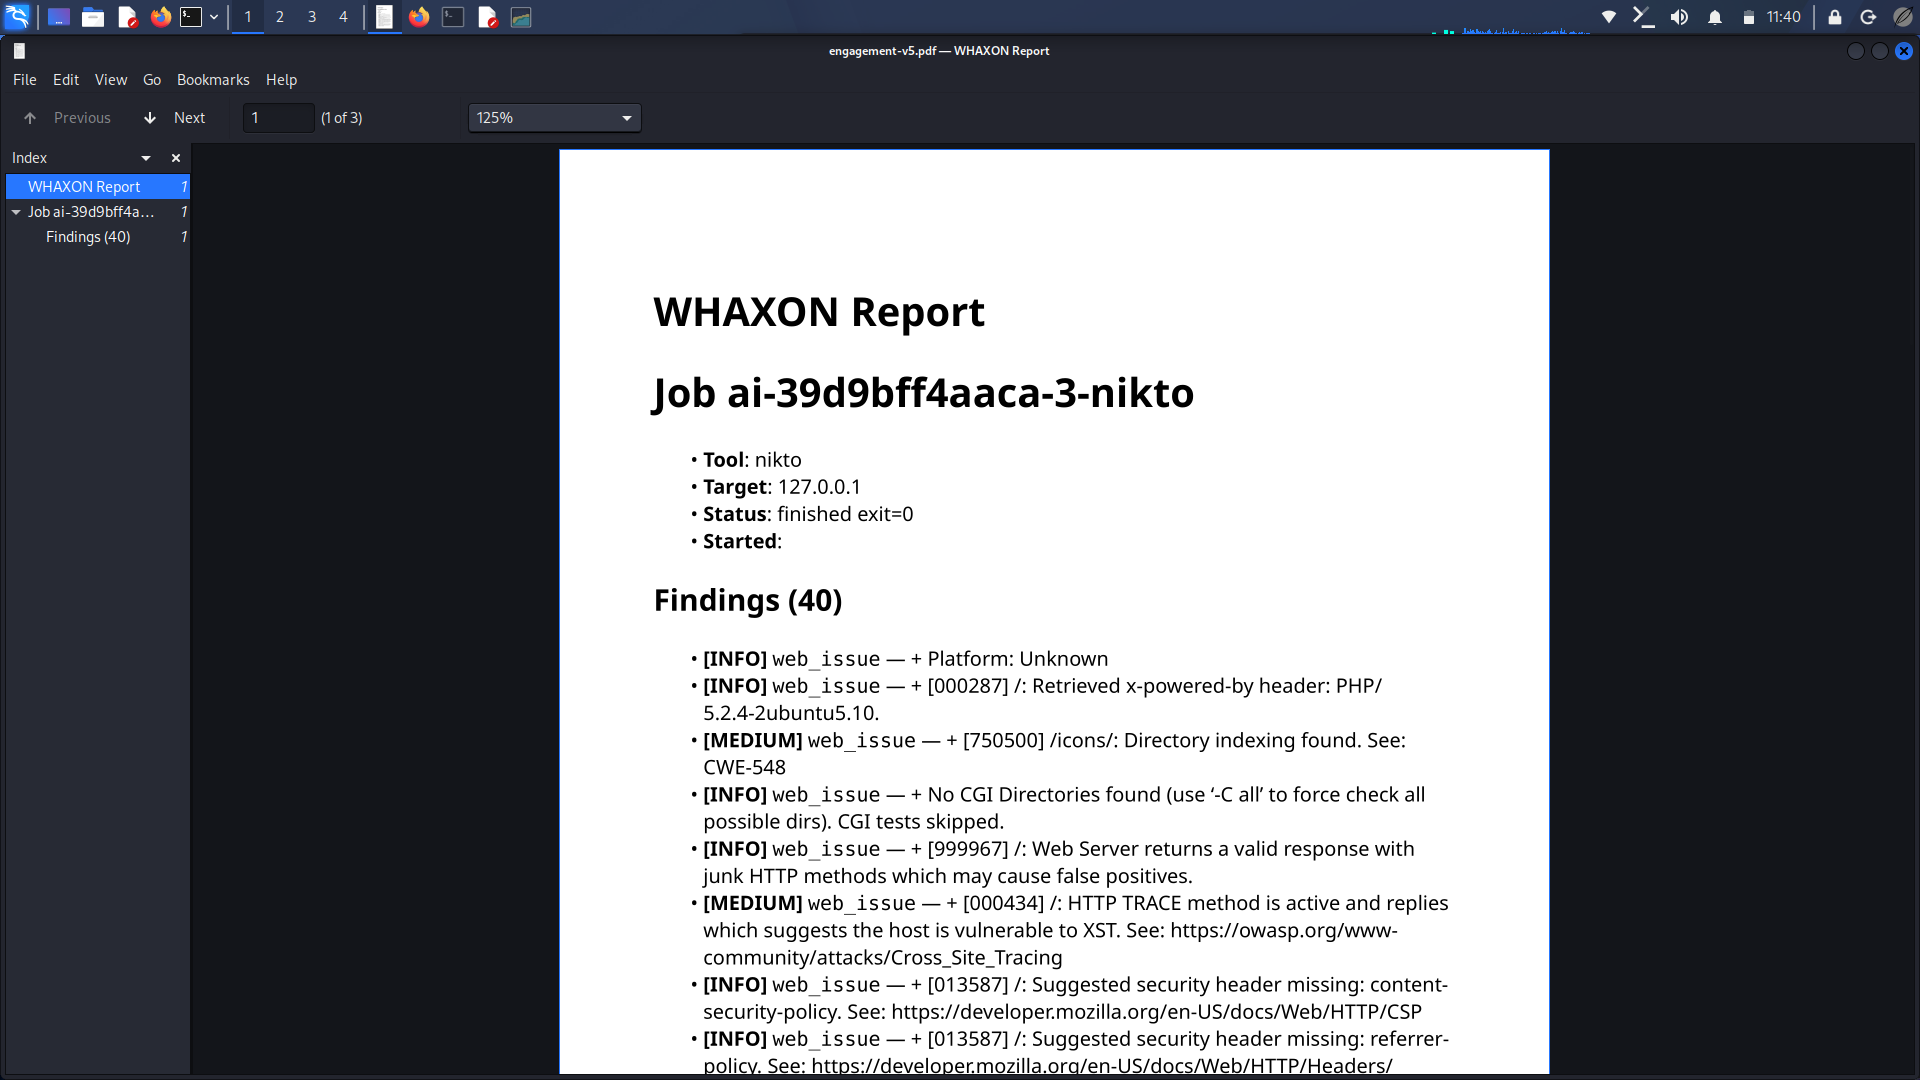
HTML output is escaped — a raw_line with <script> can't execute in a browser.
Testing
python -m pytest tests/ -q
517 tests passing.
Documentation
docs/ — getting started, architecture, adapters, plugins, tools, scope, interfaces, findings, reports, API, deployment, troubleshooting, changelog.
Responsible use
Authorized testing only. Use on systems you own or have explicit permission to assess.
Licensing
AGPL-3.0-or-later. See LICENSE-COMMERCIAL.md and LICENSE-ENTERPRISE.md.
1 maintainer

Metadata
1 maintainer
Release files for whaxon 0.7.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| whaxon-0.7.3.tar.gz | 208.4 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| whaxon-0.7.3-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 432.0 kB
Release files / whaxon-0.7.3.tar.gz
| Download URL | whaxon-0.7.3.tar.gz |
|---|---|
| Size | 208.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
9526a6539e2845f40d907fc689ed87e1b27af49003a676be6ecea729e44b5d71
|
|
BLAKE2b-256 checksum How to use checksums |
4602521b8415bf2f80f18eb5d61a85e2fe65c7e20af13706eaa7ea3a0dd58d52
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.13.15
|
Release files / whaxon-0.7.3-py3-none-any.whl
| Download URL | whaxon-0.7.3-py3-none-any.whl |
|---|---|
| Size | 223.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
47018674b0628f9b2b8b9ee5dd8b8f5d19d77e2a90922da1944ef2b77efe0add
|
|
BLAKE2b-256 checksum How to use checksums |
a181b730d5129a104862dab9954e86f77b6545c7d1e33d8dbe30191f9a62907d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.13.15
|
Security for whaxon 0.7.3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














