
This release is a pre-release and may not be stable for production use.
Workfold


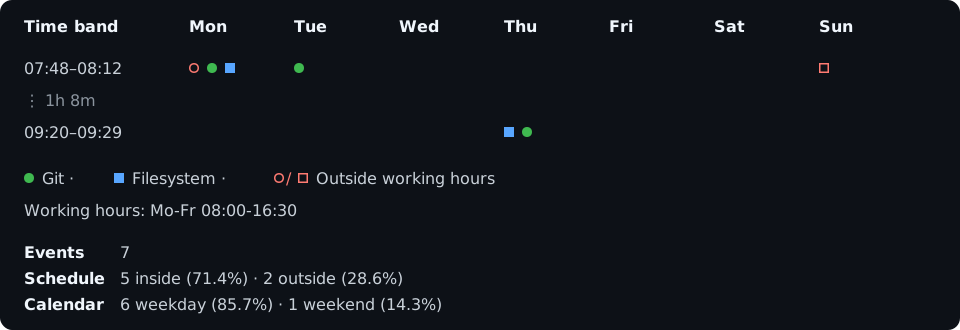
Workfold folds local Git and filesystem timestamps onto one representative Monday-to-Sunday week. It highlights activity outside your intended working hours without pretending that timestamped events are hours worked.
Workfold is local, private by design, terminal-only, and currently alpha.
Install
pip install workfold
workfold --help
For an isolated installation, use uv tool install workfold or
pipx install workfold. Standalone binaries are available from
GitHub releases.
Quick start
Run workfold inside a Git repository to see the current ISO week:
workfold
The four selectors you will use most are:
workfold . -t 2w3d                    # rolling elapsed window
workfold . -t 2026-W31                # one ISO week
workfold . -m fs                      # current filesystem metadata
workfold . -m both -p full -t all     # exhaustive local view
workfold . -m git -p portable -t all  # evidence stored in Git objects
workfold . -e git:tag:tagger fs:file:modified
They control separate parts of the request:
| Selector | Purpose | Values |
|---|---|---|
-t, --time |
Date scope | this-week, 2w3d, YYYY-Www, DATE..DATE, all |
-m, --mode |
Evidence source | git, fs, both |
-p, --profile |
Evidence preset | standard, portable, full |
-e, --events |
Exact event scope (alternative to mode/profile) | IDs and wildcards |
The profiles answer different questions:
standard: What does the ordinary activity pattern look like?portable: What dated evidence is stored inside Git objects?full: What can this machine still discover for the selected mode and time?
For exact control, -e/--events accepts identifiers such as
git:commit:author, git:tag:tagger, and fs:file:modified; quote wildcards
such as 'git:*'. -l/--list appends bounded event details. Paths must appear
before either space-separated selector, or after an option-terminating --.
Schedules support daily intervals, breaks, overnight shifts, and all:
workfold . --hours 'Mo-Thu 08:00-16:30; Fr 08:00-14:00'
workfold . --hours 'Mo-Fr 22:00-06:00'
workfold . --hours all
See the usage guide for clustering, fixed bands, identity markers, day hiding, grids, exact event selection, configuration, and every CLI option.
Configuration
Put personal defaults in the platform configuration directory, or project
defaults in workfold.toml:
timezone = "Europe/Berlin"
hours = "Mo-Thu 08:00-16:30; Fr 08:00-14:00"
mode = "git"
profile = "portable"
cluster-anchor = "midnight"
band-label = "start"
show-empty-bands = true
grid = "vertical"
hide-empty-days = ["weekend"]
Python projects may use [tool.workfold] in pyproject.toml instead. Values
resolve as built-in → global → nearest project → CLI. Inspect the result and
each value's origin without collecting timestamps:
workfold . --show-config
Use --config FILE for one exact file or --no-config for built-ins plus CLI
only. The usage guide
documents locations, discovery, merging, and every supported key.
Reading the chart
- Circles are Git events; squares are filesystem events.
- Green/blue and filled markers are inside the schedule; red and hollow markers are outside. Colorless output preserves the shape distinction.
- One symbol is one event; busy cells use exact
×Ncounts. - Empty time is compressed, and
⋮reports a meaningful gap. - Identity-marker mode replaces Git circles with codes mapped in the key.
The summary independently splits all events by schedule and by calendar day. Weekend events can therefore also be outside working hours.
Accuracy and privacy
- Events are discrete timestamp observations, not work sessions or duration.
- Collection is local: Workfold does not contact a Git host or telemetry service.
- Git history can be rewritten; reflogs can expire; filesystem metadata is a mutable snapshot and birth time depends on platform and filesystem support.
- Coverage reports unavailable, unsupported, and unreadable evidence that can prevent a complete answer. Known timestamps outside the requested time or identity scope are not counted as coverage outcomes.
See the documentation for every CLI option, collector semantics, coverage guarantees, and platform notes.
Development
The Python package lives directly in workfold/; there is no src/ wrapper.
nix develop
uv sync --locked --extra dev
uv run --locked pytest
uv run --locked ruff check .
uv run --locked ruff format --check .
uv run --locked pyright
Use nix run .#docs-dev for the documentation site and
nix run .#docs-check to validate it. The
architecture guide
documents the package boundaries, dependency rules, data pipeline, and test
layout.
1 maintainer

Metadata
1 maintainer
Release files for workfold 0.1.0a5
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| workfold-0.1.0a5.tar.gz | 306.1 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| workfold-0.1.0a5-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 555.5 kB
Release files / workfold-0.1.0a5.tar.gz
| Download URL | workfold-0.1.0a5.tar.gz |
|---|---|
| Size | 306.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
de8098ee020f49a8c75d23fbc0683bc826dae23e865c819b0e093e320c784d3c
|
|
BLAKE2b-256 checksum How to use checksums |
9ebee2e0a30ec4431d670e380eaf20d74f0151acc26356614a3348f837a0ef6b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 16, 2026.
Transparency logRelease files / workfold-0.1.0a5-py3-none-any.whl
| Download URL | workfold-0.1.0a5-py3-none-any.whl |
|---|---|
| Size | 249.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
90e9afa4b28edbeb764eb816ce787de1c76d599f010b425469d60ac69bf25eb2
|
|
BLAKE2b-256 checksum How to use checksums |
8162f92a64cb0d34683c780b7baa60959a13227b45332b9e5e38583d582e18f5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 16, 2026.
Transparency logSecurity for workfold 0.1.0a5
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for workfold-0.1.0a5.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 16, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














