


Like pip freeze but lists only the packages that are not dependencies of installed packages.
Free software: GNU General Public License v3
Documentation: https://pip-chill.readthedocs.io.
Features
Generates a requirements file without any packages that depend on other packages in the file.
Usage
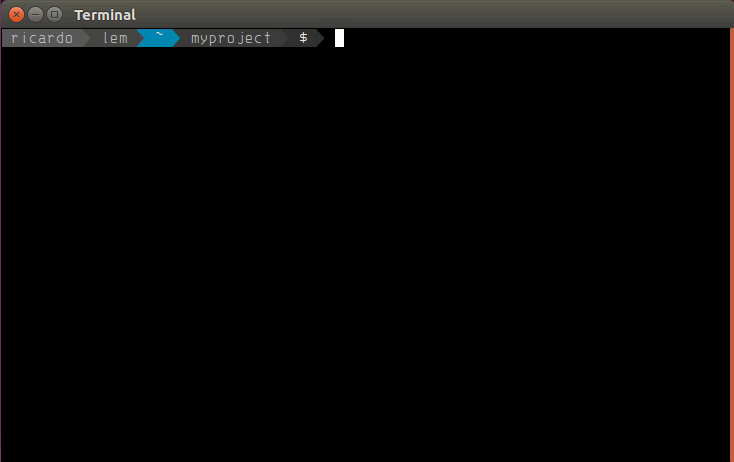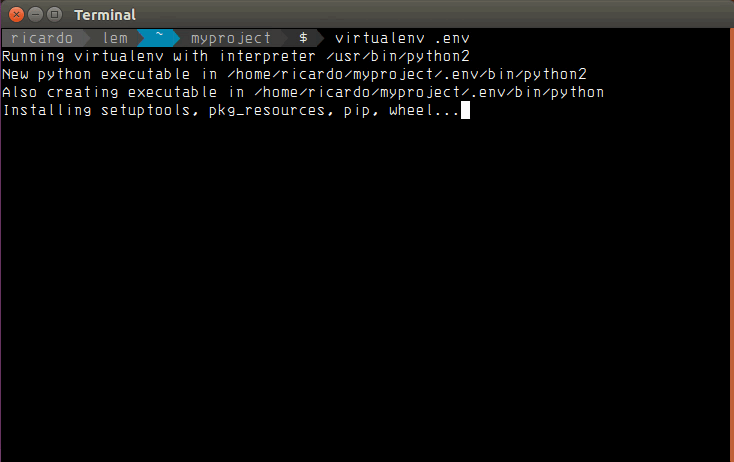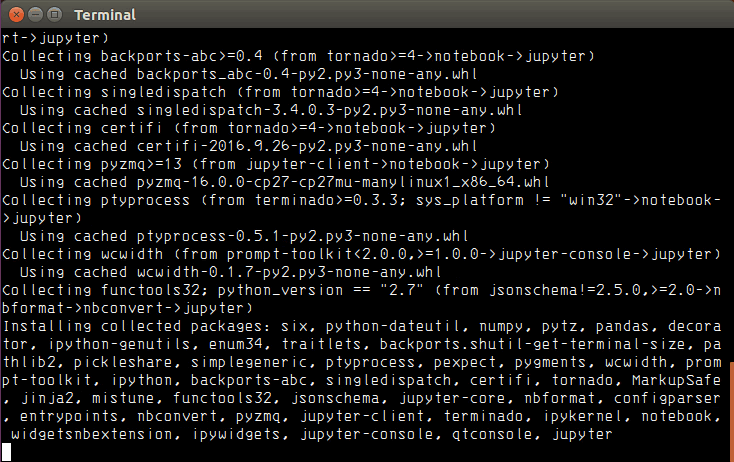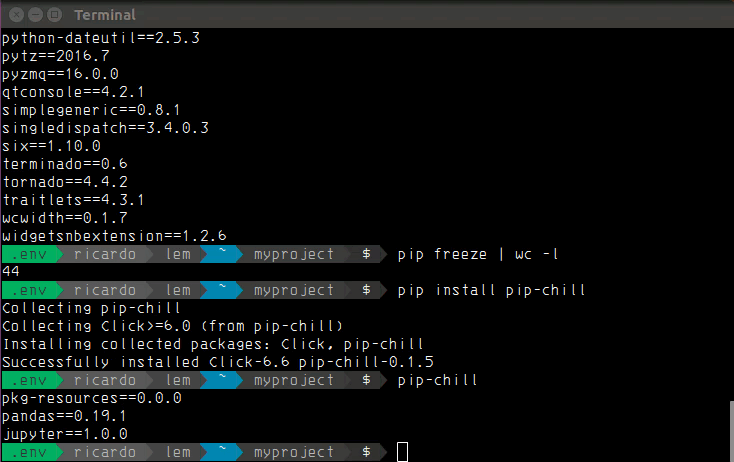
Suppose you have installed in your virtualenv a couple packages. When you run pip freeze, you’ll get a list of all packages installed, with all dependencies. If one of the packages you installed ceases to depend on an already installed package, you have to manually remove it from the list. The list also makes no distinction about the packages you actually care about and packages your packages care about, making the requirements file bloated and, ultimately, inaccurate.
On your terminal, run:
$ pip-chill
bandit==1.7.0
bumpversion==0.6.0
click==7.1.2
coverage==5.3.1
flake8==3.8.4
nose==1.3.7
pip-chill==1.0.1
pytest==6.2.1
...
Or, if you want it without version numbers:
$ pip-chill --no-version
bandit
bumpversion
click
coverage
flake8
nose
pip-chill
pytest
...
Or, if you want it without pip-chill:
$ pip-chill --no-chill
bandit==1.7.0
bumpversion==0.6.0
click==7.1.2
coverage==5.3.1
flake8==3.8.4
nose==1.3.7
pytest==6.2.1
...
Or, if you want to list package dependencies too:
$ pip-chill -v
bandit==1.7.0
bumpversion==0.6.0
click==7.1.2
coverage==5.3.1
flake8==3.8.4
nose==1.3.7
pip-chill==1.0.1
pytest==6.2.1
sphinx==3.4.3
tox==3.21.1
twine==3.3.0
watchdog==1.0.2
# alabaster==0.7.12 # Installed as dependency for sphinx
# appdirs==1.4.4 # Installed as dependency for virtualenv
# attrs==20.3.0 # Installed as dependency for pytest
# babel==2.9.0 # Installed as dependency for sphinx
# bleach==3.2.1 # Installed as dependency for readme-renderer
# bump2version==1.0.1 # Installed as dependency for bumpversion
# certifi==2020.12.5 # Installed as dependency for requests
# chardet==4.0.0 # Installed as dependency for requests
# colorama==0.4.4 # Installed as dependency for twine
# distlib==0.3.1 # Installed as dependency for virtualenv
# docutils==0.16 # Installed as dependency for readme-renderer, sphinx
# filelock==3.0.12 # Installed as dependency for tox, virtualenv
# gitdb==4.0.5 # Installed as dependency for gitpython
...
Credits
This package was created with Cookiecutter and the audreyr/cookiecutter-pypackage project template.
1 maintainer

Metadata
1 maintainer
Release files for pip-chill 1.0.5
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| pip_chill-1.0.5.tar.gz | 18.5 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| pip_chill-1.0.5-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 25.2 kB
Release files / pip_chill-1.0.5.tar.gz
| Download URL | pip_chill-1.0.5.tar.gz |
|---|---|
| Size | 18.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
e79bc514abfe144f2ef52290f59677d279cb05b4084fa9f814bbe5cc0ea04c1c
|
|
BLAKE2b-256 checksum How to use checksums |
1cb6bf36516940f5069384ae0908c5b8c334acf3a6b047471ef80dd9f1acf2ed
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.2.0 CPython/3.14.3
|
Release files / pip_chill-1.0.5-py3-none-any.whl
| Download URL | pip_chill-1.0.5-py3-none-any.whl |
|---|---|
| Size | 6.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
732fae3d695950f6e47ad849480fdfd0fb95fa2f2eed5d9c22354f44adad9f7b
|
|
BLAKE2b-256 checksum How to use checksums |
28717f572eea37680aa1e37cbfc82a5cfb3cfc4cd8b0d8425c15e5723c4e4165
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.2.0 CPython/3.14.3
|
Security for pip-chill 1.0.5
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














