
A11
Build AI applications like normal software.
A11 is the open-source runtime for connecting models, tools and interfaces while keeping your architecture. It gives ordinary asynchronous code named streams, concurrency, tools and local-to-remote execution, and exposes the running application to Studio.
The Python API runs on a native C++20 runtime. TypeScript, Kotlin, C++ and Flow use the same action boundary where an application needs another language or process.
- Named streams instead of mixed provider events. Read model text, reasoning, tool activity, progress, and durable interaction state from separate ports.
- The same action contract locally and remotely. Move a handler to a GPU host, browser, or service without changing its inputs and outputs.
- Deterministic runtime composition with Flow. Check and load compositions at runtime with defined concurrency, draining, deadlines, cancellation, and error propagation.
Run the first action · Try the live research agent · Read the documentation · Star A11
Try A11 live
The hosted parallel research agent plans a topic, searches the web for each brief, reviews the returned evidence concurrently, and streams a cited report to the browser. Its default model and search backends need no visitor account or API key.
Run your first streaming action
Install the core runtime on Python 3.11 or later:
python -m venv .venv
source .venv/bin/activate
pip install a11-kit
Save this as quickstart.py. The function signature becomes an action schema,
and its asynchronous iterator becomes a named streaming output:
import asyncio
from collections.abc import AsyncIterator

import a11


REGISTRY = a11.ActionRegistry()


@REGISTRY.action(name="split-words", output="words")
async def split_words(text: str) -> AsyncIterator[str]:
    """Emit the words in a line as they become available."""
    for word in text.split():
        yield word


async def main() -> None:
    action = REGISTRY.make_action("split-words")
    await action["text"].finalize("named streams arrive early")
    action.run()

    async for word in action["words"]:
        print(word)
    await action.wait()


asyncio.run(main())
Run it:
python quickstart.py
The output port streams four values and then closes successfully. The same
REGISTRY can be served over WebSocket, HTTP SSE, or WebRTC; callers still use
the text and words ports.
Add model providers when the application needs them. With Ollama already running locally:
pip install "a11-kit[llm]"
a11 chat --provider ollama --no-voice --no-shell-tools
a11 chat reuses a gateway at the default endpoint, or starts one for the
duration of the chat with the current directory as its coding workspace.
--cwd PATH selects another workspace for a new gateway. An explicit
--gateway URL must be reachable.
In a coding chat, /sandbox unrestricted grants host filesystem access and
disables kernel process confinement. /sandbox workspace-write or
/sandbox read-only restores confinement. Approval remains a separate setting
(/approval suggest|auto). Sandbox changes affect subsequent tool calls for
all clients of that gateway, not already-running processes.
Studio and IDE clients can call the UI-only configure_coding_agent action
with sandbox_mode (read-only, workspace-write, or unrestricted) and/or
approval_mode (suggest or auto). Omitted fields keep their current values;
the result contains approval_mode, sandbox_ceiling, and network. This
control is excluded from the coding agent's model-facing action list.
Input questions appear above the TUI composer. Use Up/Down to select and Enter
to answer, or type a response when free text is allowed. An output-area status
line shows Working during model calls and Waiting for input while a
question is pending.
Add capabilities incrementally
Streaming. An asynchronous iterator yields values before it finishes. Named outputs give model text, reasoning, progress and structured values their own interfaces. The caller reads those streams and checks the action's final status separately.
Concurrency. Use ordinary Python tasks or C++ runtime primitives for independent work. Use nested A11 actions when the runtime should understand a parent/child relationship and propagate cancellation.
Tools. Expose registered actions to model calls through the SDK, or serve the same registry through MCP. The application still owns validation, authorization and policy.
Remote execution. Serve a registry from another process or machine. The caller configures a connection and calls the action; the handler's input and output contract stays stable.
Flow is available when an application needs a composition expressed as data. It is optional: model APIs, MCP, LangGraph and existing application code can remain part of the stack.
Inspect the work with Studio
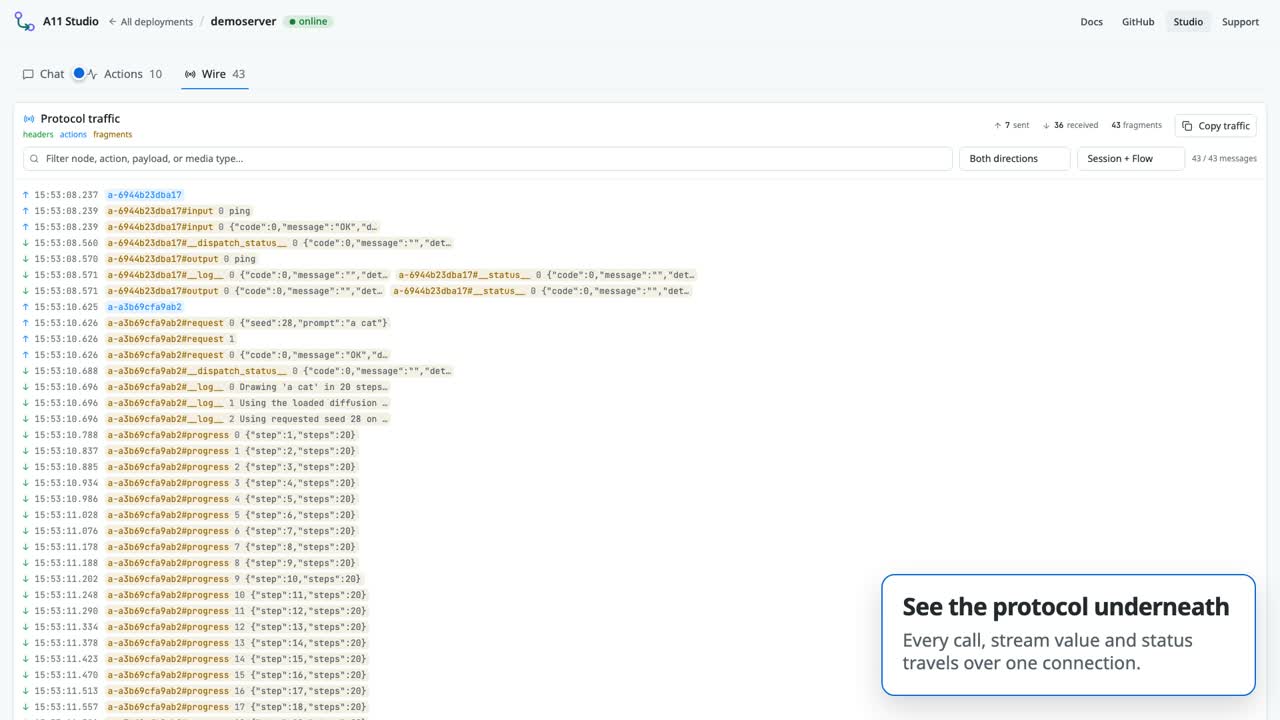
Open Studio to explore an endpoint's action schemas, run calls and inspect streamed outputs, logs, timings, failures and cancellation.
Explore complete applications
- Deep research plans a topic, searches the web in parallel and streams a cited synthesis.
- Model interactions present one streaming interface across Claude, Gemini, Ollama and OpenAI-compatible providers.
- The
a11 chat --voice-model ...path keeps audio capture, transcription and model interaction on separate streams. - Generative media streams progress independently from generated image bytes.
- Browser tools let a model call typed actions implemented inside an existing page.
Each guide names its provider, model and hardware prerequisites. Local actions and remote transports do not require a model.
Install only what the application needs
The Python distribution is a11-kit, imported as a11. Provider integrations
are optional extras such as a11-kit[ollama], a11-kit[claude] and
a11-kit[openai]. Browser and TypeScript applications use:
npm install @curiositystack/a11
The standalone C++20 runtime needs no Python installation. Build and link it through its exported CMake targets using the instructions below.
Go deeper
- Build a parallel research agent in Python.
- Stream one model interface across Claude, Gemini, and Ollama.
- Turn an application action into an LLM tool.
- Move a local action behind a remote service.
- Compose allowed actions safely at runtime.
Questions and rough edges are useful project signals: start a discussion, report friction, or tell us about an integration.
Building the C++ runtime
A11's runtime is a standalone C++20 library you can build and link without Python. The steps below are self-contained; for the editable Python build, wheel matrix, testing workflow, and architecture, see BUILDING.md.
1. Install the tools, then build the C++ libraries. A11 links a pinned set
of statically-built libraries (Boost, OpenSSL, libcurl, nghttp2, hiredis,
nlohmann-json, uvw) rather than system copies; scripts/bootstrap_wheel_deps.sh builds them
into a per-architecture prefix. From Homebrew you install only the tools (a C++20
compiler, CMake ≥ 3.28, Ninja; Linux tool package names vary):
brew install cmake googletest ninja pkg-config

export A11_DEPS_PREFIX="$HOME/.cache/a11-deps/$(uname -m)"
export CMAKE_PREFIX_PATH="$A11_DEPS_PREFIX"
export OPENSSL_ROOT_DIR="$A11_DEPS_PREFIX"
export PKG_CONFIG_PATH="$A11_DEPS_PREFIX/lib/pkgconfig"
export MACOSX_DEPLOYMENT_TARGET=14.4   # macOS only
scripts/bootstrap_wheel_deps.sh
CMake still fetches the pinned Abseil (and libdatachannel, for WebRTC) automatically. See BUILDING.md for the full rundown.
2. Configure, build, and install to a prefix (the exports above point CMake at the dependency prefix):
cmake -S . -B build -G Ninja \
  -DCMAKE_BUILD_TYPE=Release \
  -DA11_BUILD_PYTHON=OFF \
  -DCMAKE_OSX_DEPLOYMENT_TARGET=14.4 \
  -DCMAKE_INSTALL_PREFIX="$PWD/install"

cmake --build build -j
cmake --install build
On macOS, pass -DCMAKE_OSX_DEPLOYMENT_TARGET=14.4 as shown — it must match the
value the prefix was bootstrapped with. Setting it as a cache variable here (not
only via the MACOSX_DEPLOYMENT_TARGET environment export, which CMake may not
pick up) is what enables the Boost.Fiber futex spinlock; a lower target compiles
Boost.Fiber without futex support and fails with
"futex not supported on this platform". The flag is ignored on Linux.
3. Use it from your own CMake project. The install exports a CMake package
named a11 with per-component targets (a11::service links the whole runtime).
Point your consumer's CMAKE_PREFIX_PATH at both the install prefix and the
dependency prefix from step 1, so the transitive static Boost/OpenSSL/... resolve:
find_package(a11 CONFIG REQUIRED)

add_executable(my_agent main.cc)
target_link_libraries(my_agent PRIVATE a11::service)
target_compile_features(my_agent PRIVATE cxx_std_20)
#include <cstddef>
#include <iostream>
#include <memory>
#include <optional>
#include <string>
#include <vector>

#include <absl/log/log.h>
#include <absl/status/status.h>
#include <absl/status/status_macros.h>
#include <absl/strings/str_split.h>

#include "a11/actions/registry.h"
#include "a11/nodes/async_node.h"

namespace {

using a11::actions::Action;
using a11::actions::ActionPortSchema;
using a11::actions::ActionRegistry;
using a11::actions::ActionSchema;
using a11::nodes::AsyncNode;

ActionSchema SplitWordsSchema() {
  return ActionSchema{
      .name = "split-words",
      .inputs = {{"text", ActionPortSchema{
                             .name = "text", .type = "text/plain"}}},
      .outputs = {{"words", ActionPortSchema{
                               .name = "words", .type = "text/plain"}}},
  };
}

absl::Status SplitWords(std::shared_ptr<Action> action) {
  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> input,
                        action->GetInput("text"));
  ABSL_ASSIGN_OR_RETURN(
      std::optional<std::string> text,
      input->NextObject<std::string>().Await());
  if (!text.has_value()) {
    return absl::FailedPreconditionError("text input ended before a value");
  }

  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> output,
                        action->GetOutput("words"));
  std::vector<std::string> words =
      absl::StrSplit(*text, absl::ByAnyChar(" \t\n"), absl::SkipWhitespace());
  if (words.empty()) {
    return output->Finalize({.wait = true}).Await().status();
  }
  for (size_t index = 0; index + 1 < words.size(); ++index) {
    ABSL_RETURN_IF_ERROR(output->Put(words[index]).Await().status());
  }
  return output->Finalize(words.back(), {.wait = true}).Await().status();
}

absl::Status RunExample() {
  auto registry = std::make_shared<ActionRegistry>();
  ABSL_RETURN_IF_ERROR(registry->RegisterSync(
      "split-words", SplitWordsSchema(), SplitWords));
  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<Action> action,
                        registry->MakeAction("split-words"));

  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> input,
                        action->GetInput("text"));
  ABSL_RETURN_IF_ERROR(
      input->Finalize(std::string("named streams arrive early"),
                      {.wait = true})
          .Await()
          .status());
  ABSL_RETURN_IF_ERROR(action->Run().status());

  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> output,
                        action->GetOutput("words"));
  while (true) {
    ABSL_ASSIGN_OR_RETURN(std::optional<std::string> word,
                          output->NextObject<std::string>().Await());
    if (!word.has_value()) break;
    std::cout << *word << '\n';
  }
  return action->Wait().Await().status();
}

}  // namespace

int main() {
  const absl::Status status = RunExample();
  if (!status.ok()) {
    LOG(ERROR) << status;
    return 1;
  }
  return 0;
}
This is the same split-words action as the Python quickstart: the registry
owns its schema and handler, the input carries one complete value, and the
output emits words as a stream. Reading the output before Wait() drains it
while the handler is running and preserves backpressure.
Configure your project with -DCMAKE_PREFIX_PATH=/path/to/install so
find_package locates it. The generated C++ API reference is published
alongside the docs.
1 maintainer

Metadata
1 maintainer
Release files for a11-kit 0.7.14
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| a11_kit-0.7.14.tar.gz | 2.9 MB | With provenance | Details for a11_kit-0.7.14.tar.gz |
Built distributions (wheels)
Total release size: 156.2 MB
Release files / a11_kit-0.7.14.tar.gz
| Download URL | a11_kit-0.7.14.tar.gz |
|---|---|
| Size | 2.9 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
74ae62dde18fcceeb4f2f9679a78def85dabef51cddc2359c616cbde319a28e5
|
|
BLAKE2b-256 checksum How to use checksums |
db30819ef34994b43e7716418d2bd98b6bd319a4050f0ea53b4003777888fec2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / a11_kit-0.7.14-cp314-cp314-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.14-cp314-cp314-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 14.0 MB |
| Tags | CPython 3.14 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
58059356164822d4b5e1c118e2a7ce975895306f9b0dc870c8ae1cb8b7ce8c28
|
|
BLAKE2b-256 checksum How to use checksums |
39e96a81f4dc4ec50c48bd7f604d8ade107d861963526be35afa2a1f2ccbd7b5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / a11_kit-0.7.14-cp314-cp314-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.14-cp314-cp314-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 13.2 MB |
| Tags | CPython 3.14 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
33ff60e4e20fb3c5921a4f277c3a94c677c6c92febc1244bbd5fe1a923e9a765
|
|
BLAKE2b-256 checksum How to use checksums |
5b0d158d78a77dfb307b175cd886d1ffd3b80603db885b34b4b0f5e99c21acf1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / a11_kit-0.7.14-cp314-cp314-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.14-cp314-cp314-macosx_14_0_arm64.whl |
|---|---|
| Size | 11.1 MB |
| Tags | CPython 3.14 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
103dad9718bc6da3e4d9e0ae6e3cb8df6701d53af5df9da4a68680df18897f94
|
|
BLAKE2b-256 checksum How to use checksums |
07081baed9a2d5b2f7a2145511e1929285aafc7ca73976cdd5e71d5c5f9f78f5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / a11_kit-0.7.14-cp313-cp313-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.14-cp313-cp313-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 14.0 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
d4aa438d7669686f8c5a7ab3d7b8ed034a79722e68c1fae126b168658ee2761d
|
|
BLAKE2b-256 checksum How to use checksums |
0110c662ee85060186735d96e2dc98137e502475ebbf19c5fb2b4390ee3d84c5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / a11_kit-0.7.14-cp313-cp313-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.14-cp313-cp313-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 13.2 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
3aeda656a7f364e08e225f60287da66282849e2ae232d6d6b31715afe493228f
|
|
BLAKE2b-256 checksum How to use checksums |
a7771140abea2d6432295e57423c9a0d8da3ee0d27fc0d8879b46999ba8eb247
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / a11_kit-0.7.14-cp313-cp313-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.14-cp313-cp313-macosx_14_0_arm64.whl |
|---|---|
| Size | 11.1 MB |
| Tags | CPython 3.13 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
7e8315e2fd86e1a6fe84bae38b4198dbb479e058666369d32f35f0d57cf78309
|
|
BLAKE2b-256 checksum How to use checksums |
e73a35b96a9c62fcf6bda30be6cb89140ef6c653d1706dab5611122725e78a97
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / a11_kit-0.7.14-cp312-cp312-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.14-cp312-cp312-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 14.0 MB |
| Tags | CPython 3.12 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
b8058f7d239fa3912a2a817dee13d71089441d6cbcd6ba03668c7533fb504ef8
|
|
BLAKE2b-256 checksum How to use checksums |
0a1caf4749a5a8d8d11449261269425be44eda27fbf75b836595e630c8810d45
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / a11_kit-0.7.14-cp312-cp312-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.14-cp312-cp312-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 13.2 MB |
| Tags | CPython 3.12 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
505f2d5e4677481e48118f0cb2e8fa1bc205f120a21f594c72ca1ce3a51cf5b2
|
|
BLAKE2b-256 checksum How to use checksums |
2223dbcfe2437e072179ea7a3fc23aea0a3ce02a88dd5a4ec68b19ac3bc71b67
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / a11_kit-0.7.14-cp312-cp312-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.14-cp312-cp312-macosx_14_0_arm64.whl |
|---|---|
| Size | 11.1 MB |
| Tags | CPython 3.12 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
aeb762cdf9de0cf0fb02d5728dc9f5f6deb5738d24924c5868b9225a6ad0297d
|
|
BLAKE2b-256 checksum How to use checksums |
6bf2725eebe403d0d13ed3d7f182f8bc6813147dbc3357ef205488578c94dbda
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / a11_kit-0.7.14-cp311-cp311-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.14-cp311-cp311-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 14.0 MB |
| Tags | CPython 3.11 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
00672308f1d9f69abcea6cca64004fc9b73ce50dc01fa448a5b6fd71534e90ab
|
|
BLAKE2b-256 checksum How to use checksums |
144d240fe8ddcb62de125e5607dd1b9850a4ab07ce558a6a1f469e5144bfe5b4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / a11_kit-0.7.14-cp311-cp311-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.14-cp311-cp311-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 13.2 MB |
| Tags | CPython 3.11 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
489276ce2e00d8dce2f3de981053e4d6e64bb85f7050757ca2a752c9bd5b1a87
|
|
BLAKE2b-256 checksum How to use checksums |
eed2973f70e9cc3346dd06e0f0eb743e1f2eacb230b788f1b690ae8918538493
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / a11_kit-0.7.14-cp311-cp311-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.14-cp311-cp311-macosx_14_0_arm64.whl |
|---|---|
| Size | 11.1 MB |
| Tags | CPython 3.11 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
451e615b2c7227fdaca4ef6026ae18f51c9be4ea7996b1163f04ba7e78852fe7
|
|
BLAKE2b-256 checksum How to use checksums |
8e7bfb52bce40b76d4d2fe34942a86440f8822765ade8a19bc53d7421a0114ee
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logSecurity for a11-kit 0.7.14
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 13 files in this release have been uploaded with provenance metadata.
Attestation for a11_kit-0.7.14.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














