
This release has been yanked by its maintainers, and will be ignored by installers, except when explicitly specified.
Consider using release 0.115.4 instead.
Reason given by maintainers: Security fixes; upgrade to 0.114.0 or later
agent-bom
AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach.
For AppSec and platform engineers. Self-host free; local scans need no account. Credential references are names, not secret values. Recorded relationships do not prove exploitation or successful data access.
With uv installed, run from the repository you want to inspect:
uvx agent-bom scan . --no-discover -f html -o agent-bom-report.html
Open agent-bom-report.html for inventory, findings, recorded exposure,
evidence coverage and fix guidance. --no-discover keeps discovery within the
selected project. No MCP configuration? Package findings remain useful;
agent/tool relationships need discovered configuration or an explicit inventory.
Review coverage warnings beside the verdict; incomplete evidence is not clean.
What this scan does and does not establish.
Apply a reviewed fix, update the lockfile, and rerun uvx agent-bom scan .
in the same repository. Run uvx agent-bom doctor if the first scan cannot start.
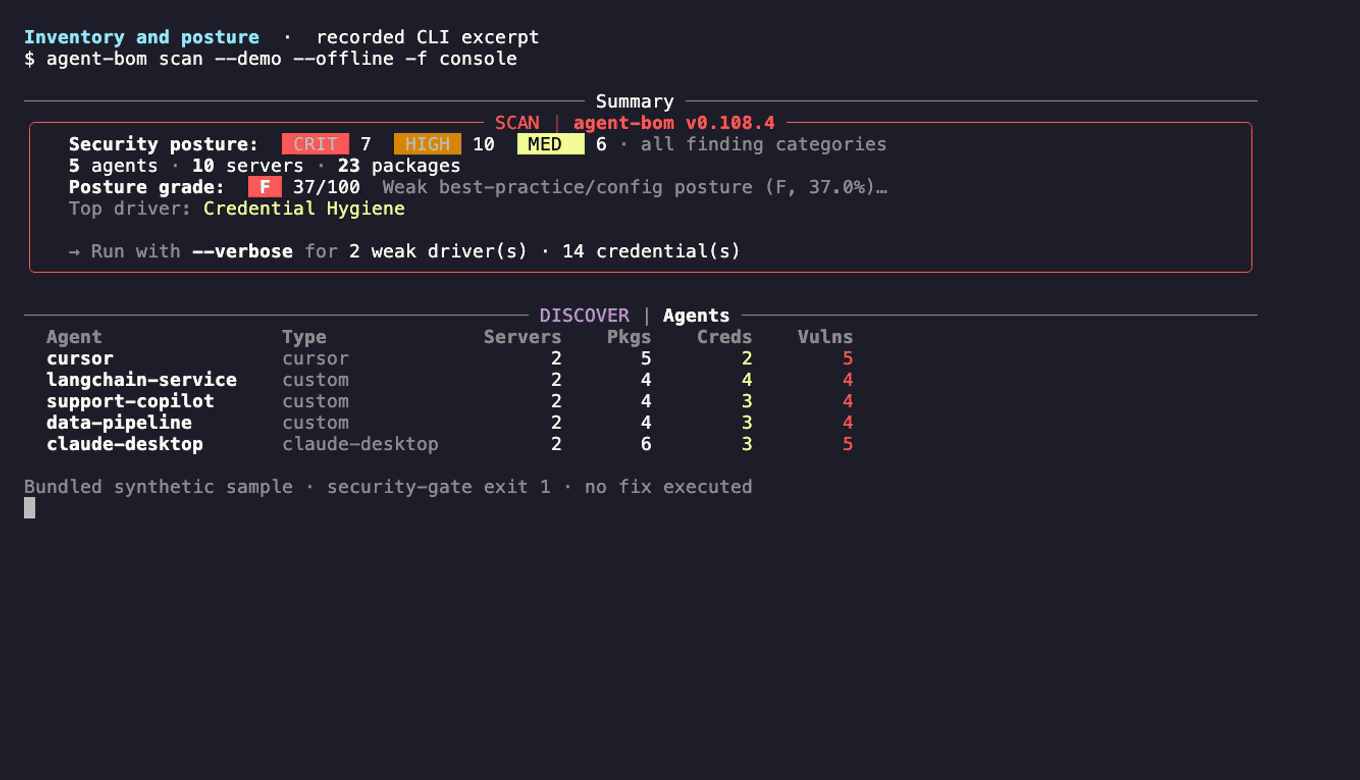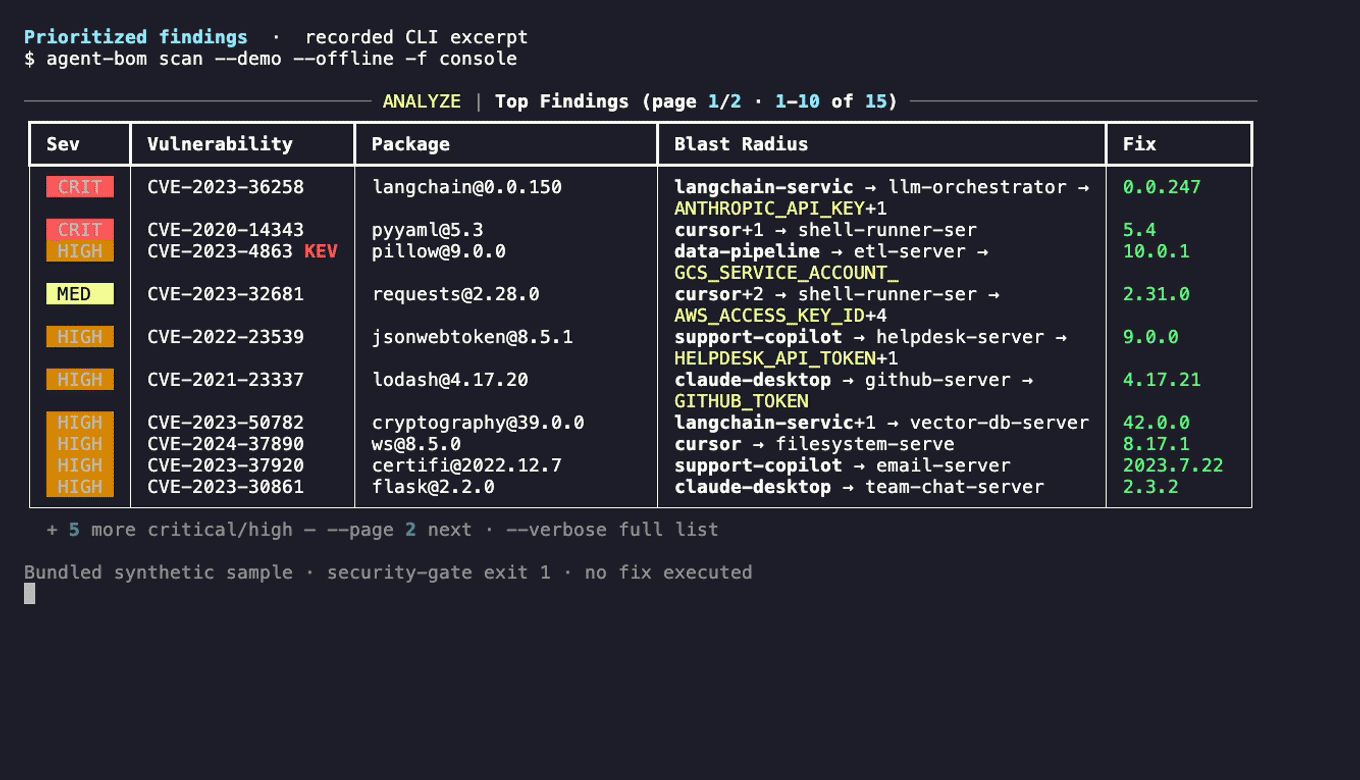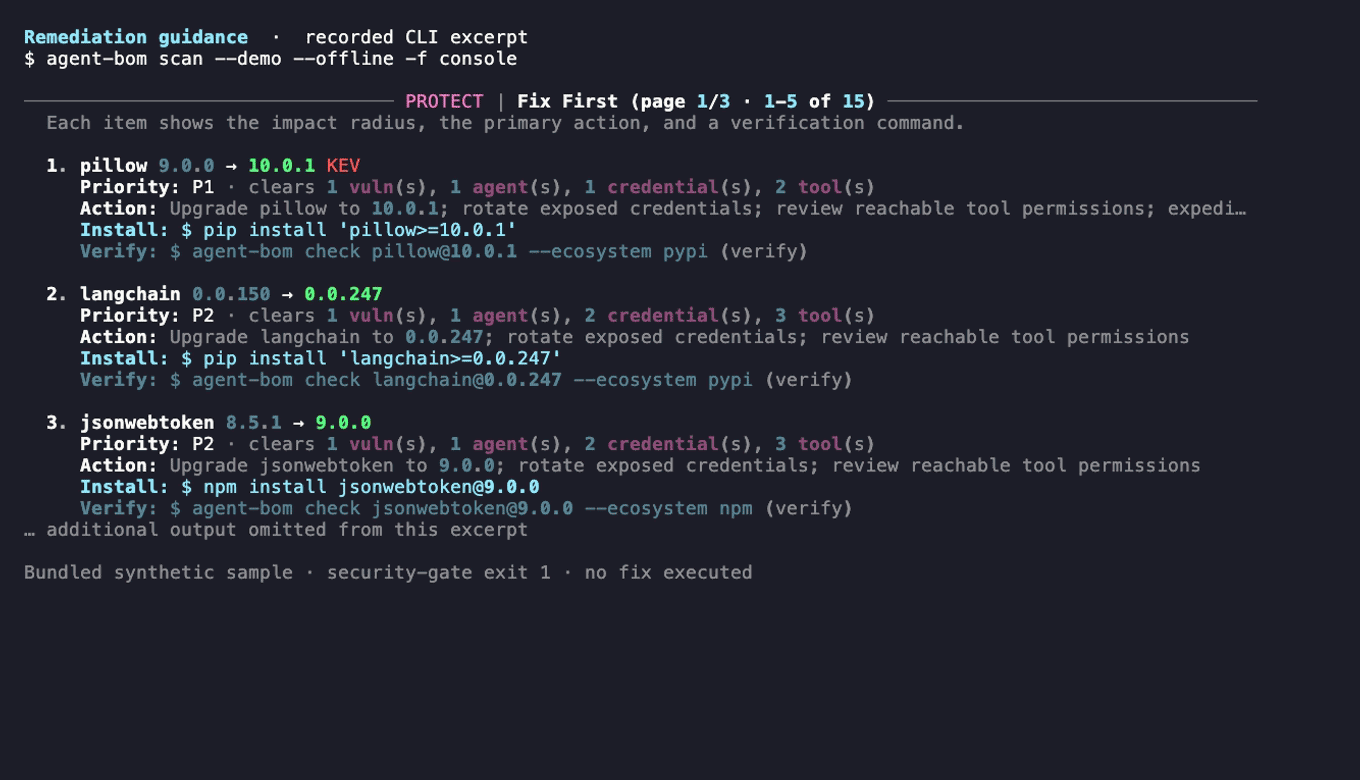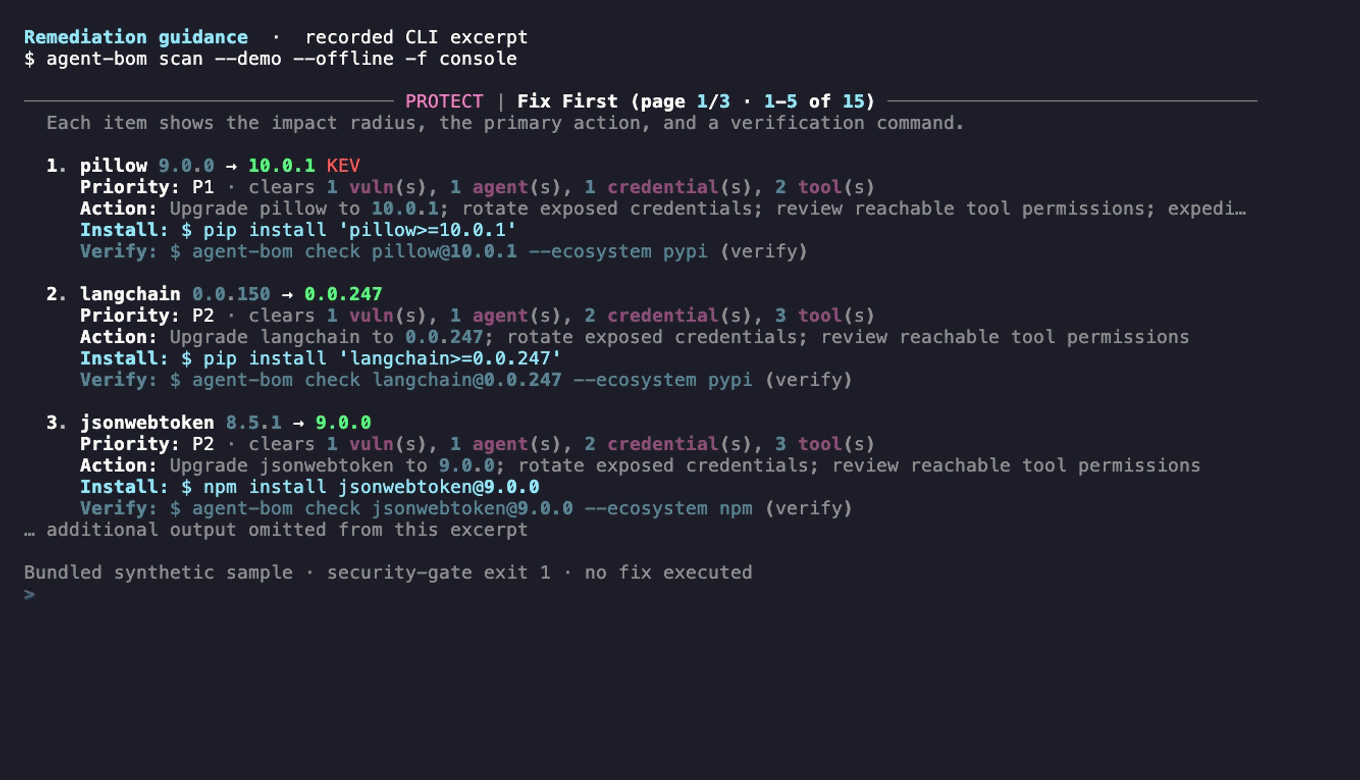
For a deterministic sample, use the built-in offline demo. It deliberately
contains blocking findings, so status 1 is the expected security verdict;
the printed report is complete.
uvx agent-bom scan --demo --offline
The demo uses a curated sample for reproducible output within a release; advisory and severity updates can change later releases.
For the installed-command examples below, run pip install agent-bom in a
virtual environment. If you want an inspectable sample before scanning your own repo:
agent-bom samples first-run
agent-bom scan --inventory agent-bom-first-run/inventory.json -p agent-bom-first-run --enrich
The bundled first-run stack includes agent inventory, MCP server definitions,
placeholder credential environment variable names, Python/npm manifests, and a
prompt file. See docs/FIRST_RUN.md in the repository for the guided flow.
See the terminal demo
Follow one component
In the self-hosted dashboard, open Inventory → component → Findings → Compliance. The views retain the exact component and scan snapshot, expose recorded relationships and source evidence, and export loaded evidence with completeness receipts. Control mappings do not establish evaluated passes or certification.
From a source checkout, run the connected-BOM example. It retains before/after SQLite snapshots: a changed dependency input removes one pinned advisory finding while an unrelated synthetic cloud check remains failed. This bounded example does not change a deployment or qualify a cloud account.
Recommended starting points
pip install agent-bom

agent-bom scan .                                 # Repo + MCP + package blast radius
agent-bom quickstart --dry-run --offline          # Sample-data and API/UI next steps
agent-bom samples first-run                      # Inspectable sample AI stack
agent-bom check flask@2.2.0 --ecosystem pypi     # Pre-install package verdict
agent-bom image nginx:latest                     # Container image scan
agent-bom scan . --remediate remediation.md       # Fix-first remediation plan
pip install 'agent-bom[ui]'                      # once, if you want the dashboard
agent-bom serve --persist ~/.agent-bom/control-plane.db  # restart-safe local control plane
The base wheel is the scanner/CLI path and includes MCP server mode
(agent-bom mcp server). Install optional surfaces explicitly:
pip install 'agent-bom[ui]' for the local API/dashboard process. Use
pip install 'agent-bom[all]' for supported first-run extras; MLflow remains
separate until its upstream CVE backlog is fixed. If an extra is missing, the
command exits with the matching install hint.
Self-hosted pilot:
curl -fsSL https://raw.githubusercontent.com/koda-ai-studio/agent-bom/main/deploy/docker-compose.pilot.yml -o docker-compose.pilot.yml
docker compose -f docker-compose.pilot.yml up -d
# Dashboard -> http://localhost:3000
For production, configure the database, identity and ingress settings in a release checkout. Follow the required secret bootstrap and wait for all four target Secrets before installing the workload:
helm upgrade --install agent-bom deploy/helm/agent-bom \
  --namespace agent-bom --create-namespace \
  -f deploy/helm/agent-bom/examples/eks-production-values.yaml
Product views
Dashboard
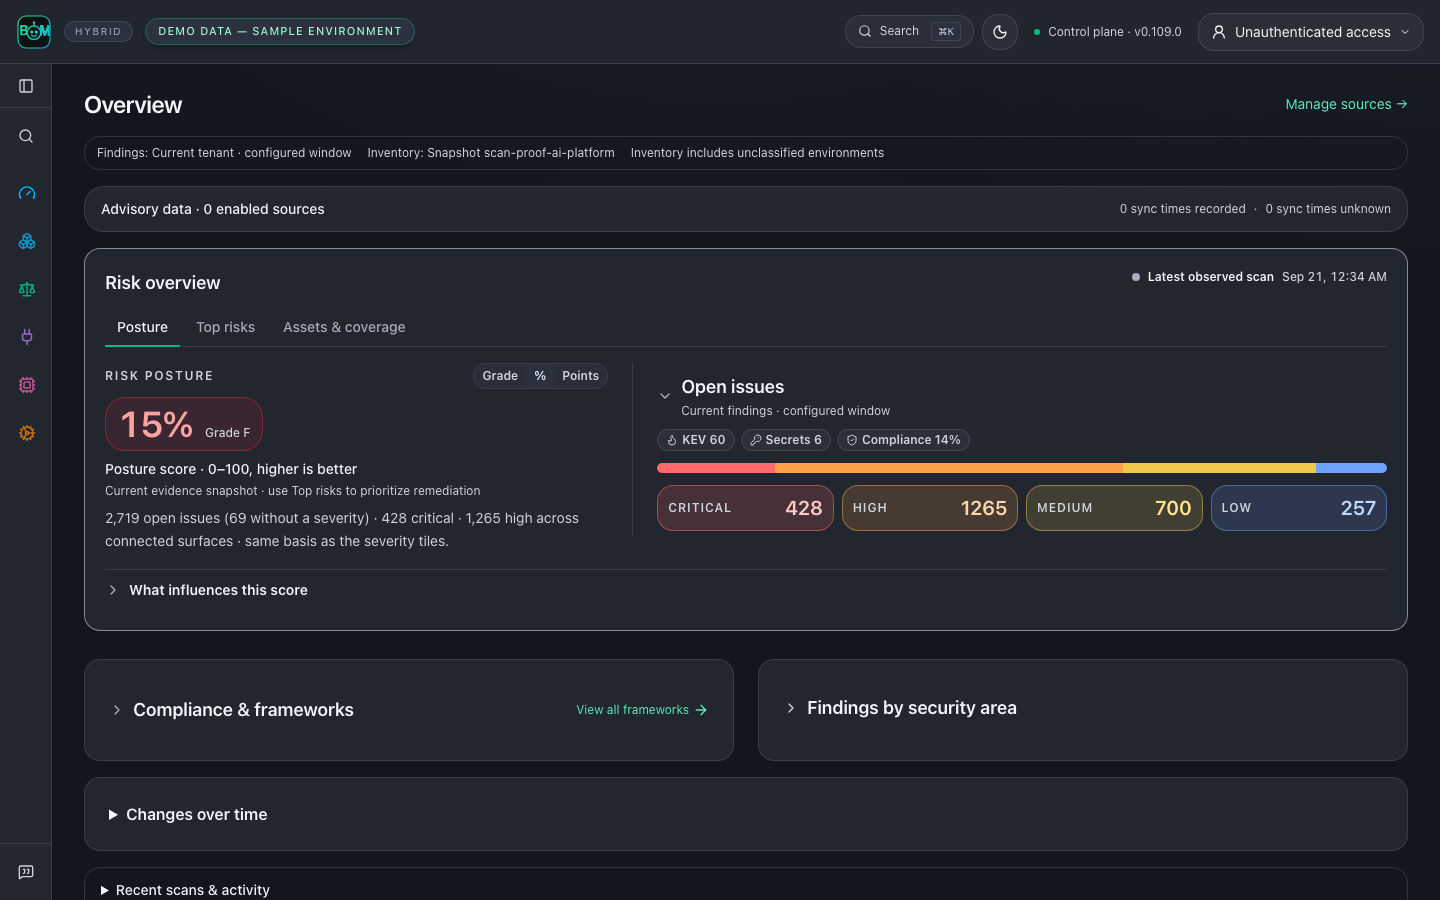
Follow an agent to its findings
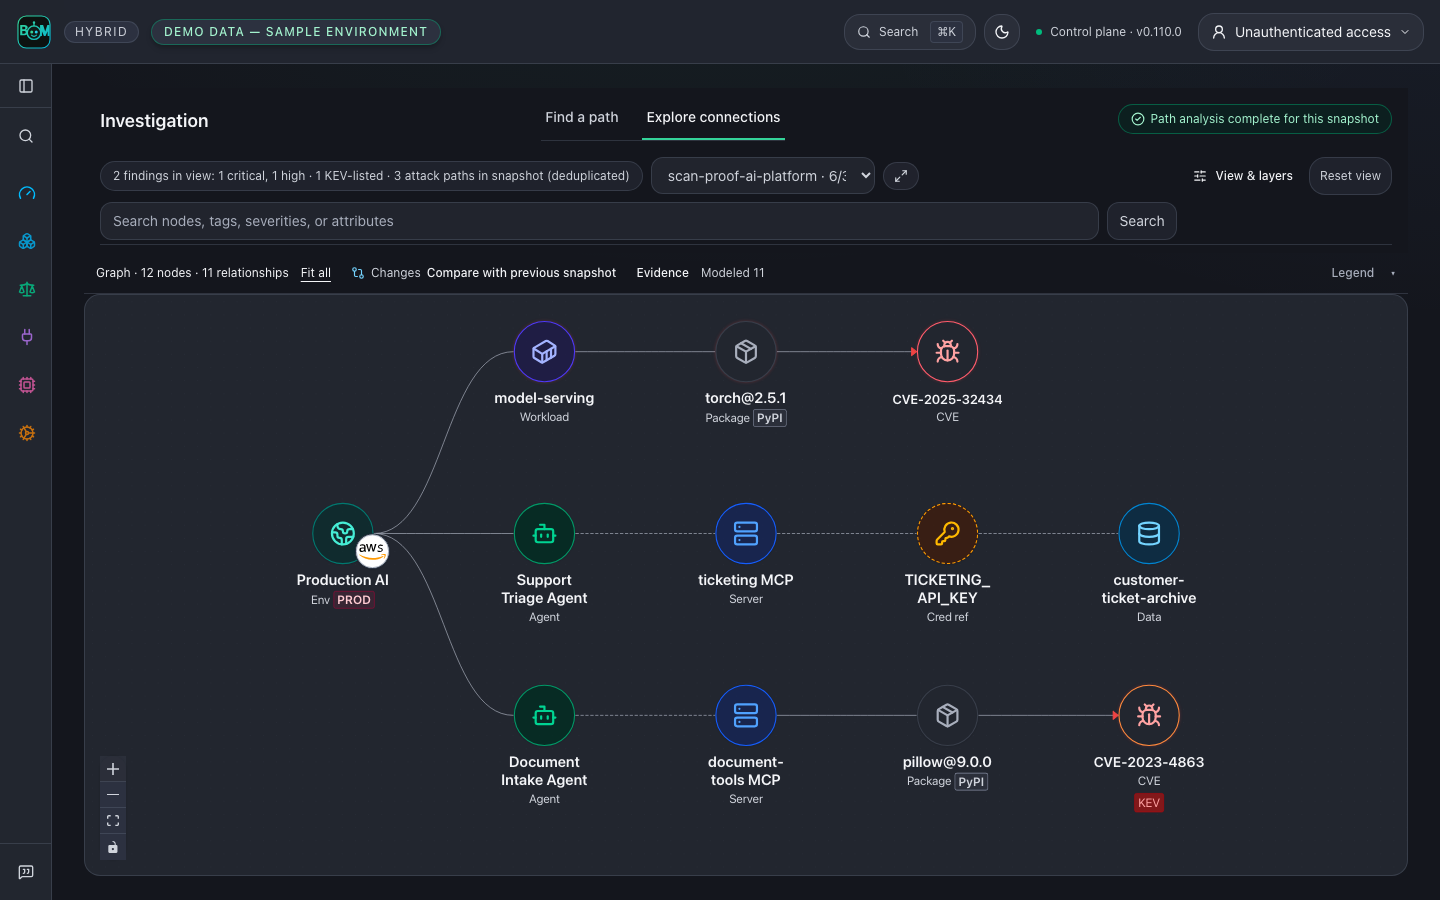
Follow Document Intake Agent → document-tools MCP → pillow@9.0.0 → CVE-2023-4863. This is a fictional sample estate; dashed access and credential links are modeled, not observed execution.
Inspect why two records are linked
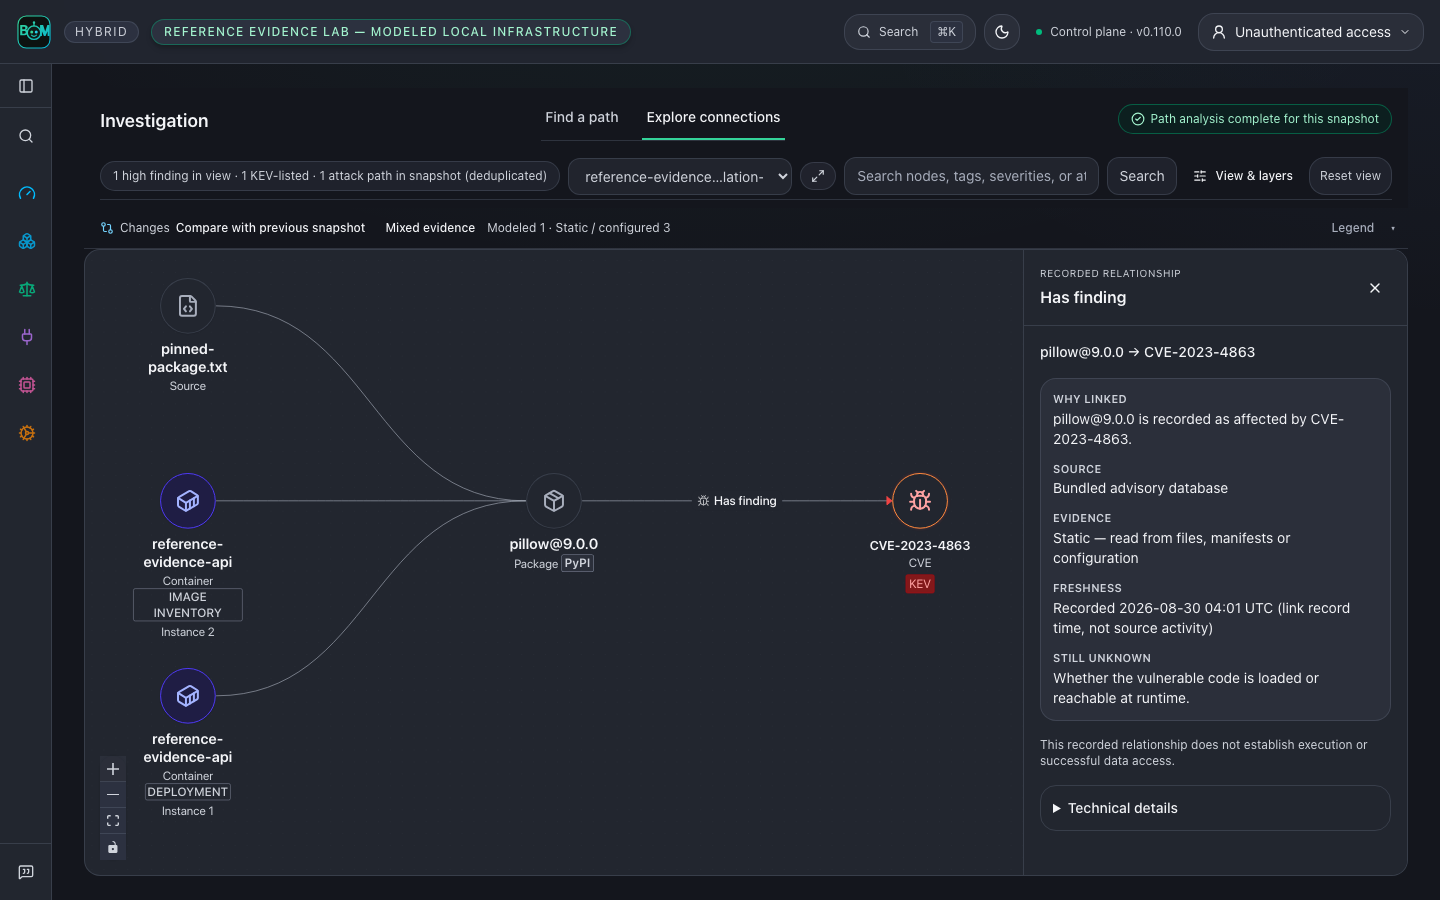
Real parsers, modeled local infrastructure: a repository pin, image SBOM and Kubernetes workload resolve to one package. The image inventory and deployment occurrence stay distinct. Select an arrow to inspect its source and evidence; a graph path does not prove execution or exploitation.
Explore the reference evidence lab · Graph guide
What it scans
- Agents + MCP — MCP clients, servers, tools, transports, trust posture
- Skills + instructions —
CLAUDE.md,AGENTS.md,.cursorrules,.windsurfrules,skills/* - Package risk — supply-chain scanning across 15 package ecosystems (including
mix.lock/pubspec.lockfor Hex and Pub) with OSV/GHSA enrichment and blast radius - AI models + datasets — malicious-model detection via safe pickle-opcode disassembly (no execution), model/dataset cards, and target-scoped PII/PHI dataset-file scanning
- Container images + IaC — native OCI parsing plus Dockerfile, Terraform, CloudFormation, Helm, and Kubernetes coverage
- Cloud estate — read-only, gated asset inventory across AWS/Azure/GCP plus AI/GPU posture and CIS benchmarks
- Identity (NHI) — non-human identity discovery (Okta/Entra), credential-expiry posture, and access-review campaigns
- LLM cost — spend forecasting, budget runway, chargeback/allocation, and seasonal-aware spend-anomaly detection
- Secrets + runtime — MCP proxy/gateway, inline firewall enforcement, A2A/MCP auth posture, Shield SDK, secrets, and redaction surfaces
- Compliance + evidence — mapped governance plus ZIP evidence bundles for auditors
Supported sources
Discovery and scanning read from these sources today; the last row lists where evidence can be sent. The list is generated from a code-backed manifest (docs/images/integrations-manifest.json); a test fails if it names anything without an implementation.
| Area | Integrations |
|---|---|
| AI clients + IDEs | Claude, Codex, Cursor, GitHub Copilot, Windsurf, Cortex Code, Gemini CLI, JetBrains AI, Junie, Amazon Q, Cline, Roo Code, Continue, Zed, Goose, Snowflake CLI, Docker MCP Toolkit, Tabnine, Sourcegraph Cody, Aider, Void, Aide, Trae, Pieces, OpenClaw, mcp-cli |
| AI platforms + model hubs | OpenAI, Hugging Face, Ollama, MLflow, W&B, Langfuse, LangSmith |
| GPU + neo clouds | CoreWeave, Nebius, Lambda, RunPod, Vast.ai, Crusoe, GPU containers + K8s GPU nodes |
| Hyperscalers + Kubernetes | AWS, Azure, GCP, Kubernetes |
| Data + vector stores | Snowflake, Databricks, Supabase, Pinecone, Qdrant, Weaviate, Chroma, Milvus |
| Identity + SaaS + dev | Okta, GitHub Actions, Vercel, Microsoft Entra ID, Jira, ServiceNow, Slack, Jamf |
| Evidence out | ClickHouse, BigQuery, S3, GCS, Azure Blob, Jira tickets, Slack alerts, Vanta, Drata, OCSF syslog |
Product names and logos are trademarks of their owners, used only to identify supported evidence sources. Their use does not imply endorsement or partnership.
Key features
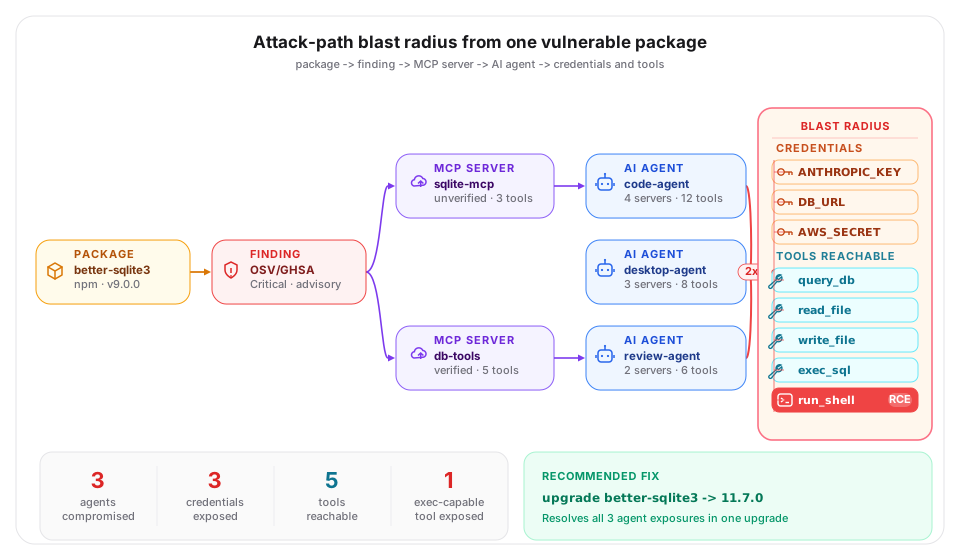
- Blast radius + attack-path fusion — multi-hop exposure paths over one
UnifiedGraph, from package → finding → MCP server → credentials → connected agents - CWE-aware impact — RCE shows credential exposure, DoS does not; symbol-level CVE reachability joins CWE/CVE/CPE advisory context when OSV/GHSA carry affected symbols (Python, npm, Go)
- Portable outputs — SARIF, CycloneDX, SPDX, OCSF, HTML, graph, JSON, ZIP evidence bundles, and more
- MCP server mode — start with 8 scan-profile tools; use
agent-bom mcp server --profile fullfor the complete catalog of 99 MCP tools, 7 resources, and 8 workflow prompts in Claude, Cursor, Windsurf, and Cortex CoCo / Cortex Code - Skill bundle identity — stable bundle hashes for skill and instruction file review
- Dependency confusion detection — flags internal naming patterns
- VEX generation — auto-triage with CWE/CVE/CPE-aware reachability (package + function-level when advisory symbols exist)
Discovery and static/cloud scanning are read-only by default. Explicit disk side-scans create temporary cloud resources and need additional permissions. Proxy, gateway, Shield, and control-plane write tools are separate, explicit runtime or authenticated operations. See the permission and network boundaries before enabling cloud scans or outbound integrations.
How the data moves
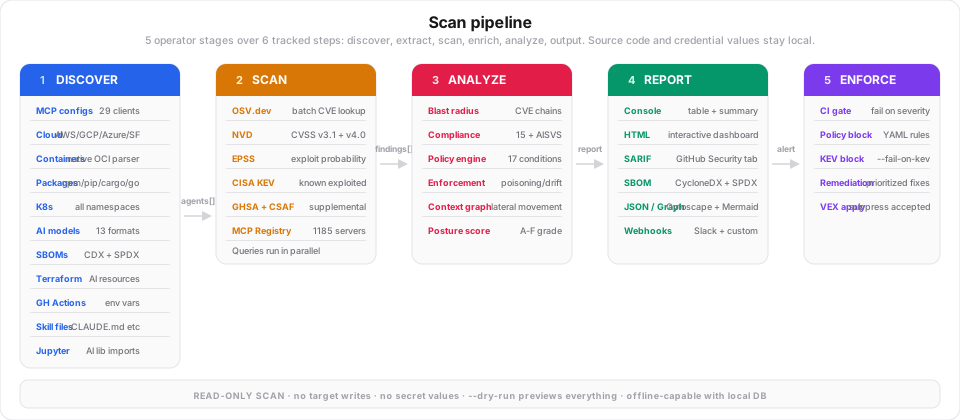
Blast radius
Links
1 maintainer

Metadata
1 maintainer
Release files for agent-bom 0.113.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| agent_bom-0.113.0.tar.gz | 12.6 MB | With provenance | Details for agent_bom-0.113.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| agent_bom-0.113.0-py3-none-any.whl | Python 3 | none | any | Details for agent_bom-0.113.0-py3-none-any.whl |
Total release size: 22.8 MB
Release files / agent_bom-0.113.0.tar.gz
| Download URL | agent_bom-0.113.0.tar.gz |
|---|---|
| Size | 12.6 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
7f41bd1ac0d7d553dea5757fde17fb5b97506955aa770ba97cf2128a8a64a901
|
|
BLAKE2b-256 checksum How to use checksums |
cff7c0ebe5c94da0fca7038f46fb86f382d8fc69796b86fbd0e0a62e872ca697
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 2, 2026.
Transparency logRelease files / agent_bom-0.113.0-py3-none-any.whl
| Download URL | agent_bom-0.113.0-py3-none-any.whl |
|---|---|
| Size | 10.1 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
01e071b21831091eace3832101b027c7f17fff467590be7ba88ebff41309dd25
|
|
BLAKE2b-256 checksum How to use checksums |
3e5fe752348650eba5372f9a9cc81f5b7f022d4ad9bda120c5dbb7a5b2b1e70c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 2, 2026.
Transparency logSecurity for agent-bom 0.113.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for agent_bom-0.113.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 2, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














