
AI Ledger
See what your coding agents did, what it cost, and where they got stuck.
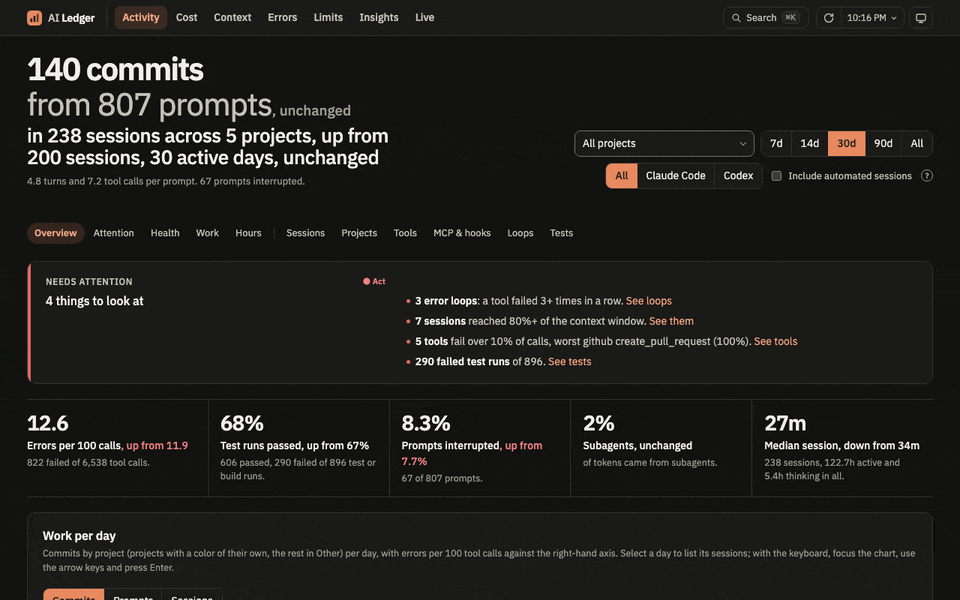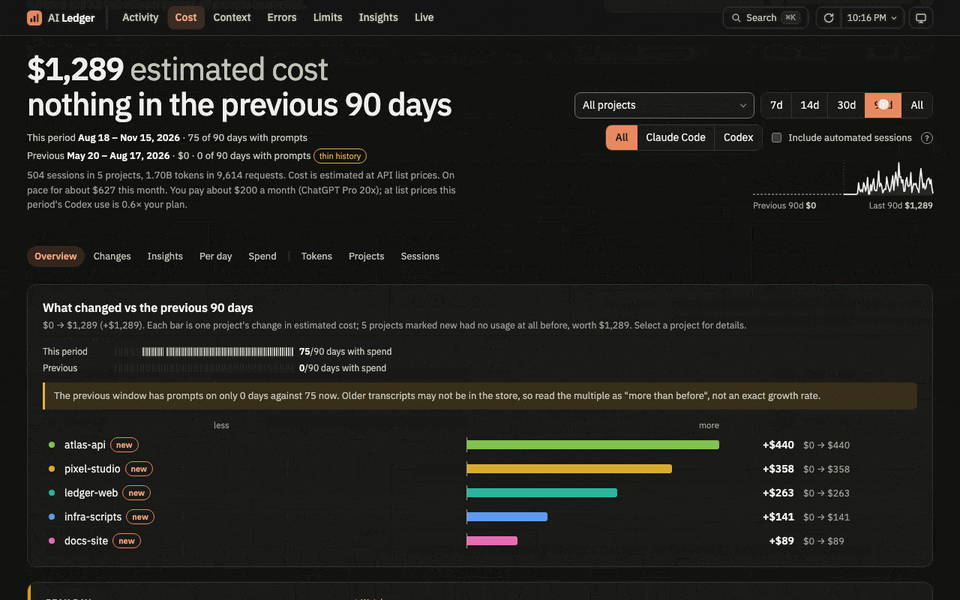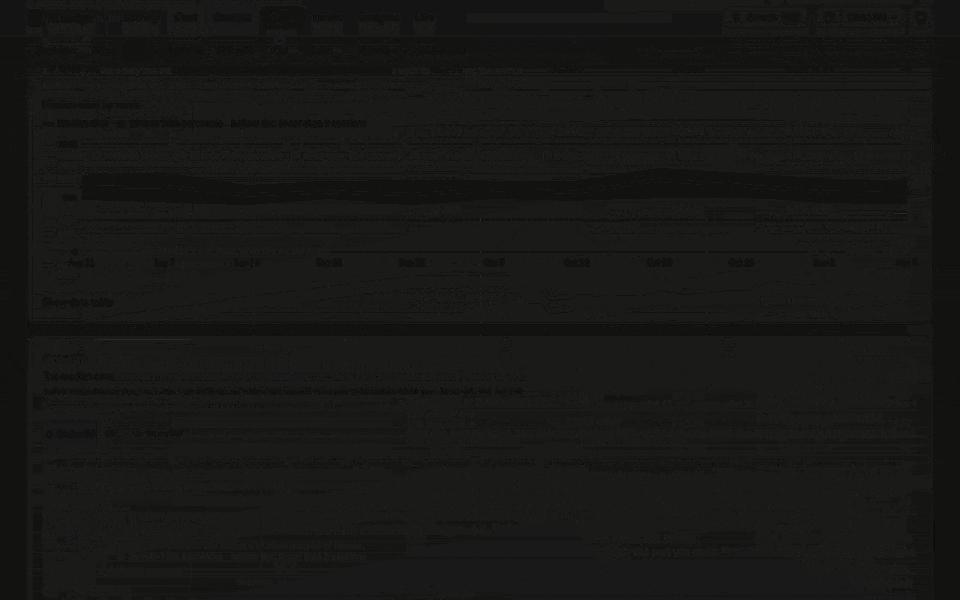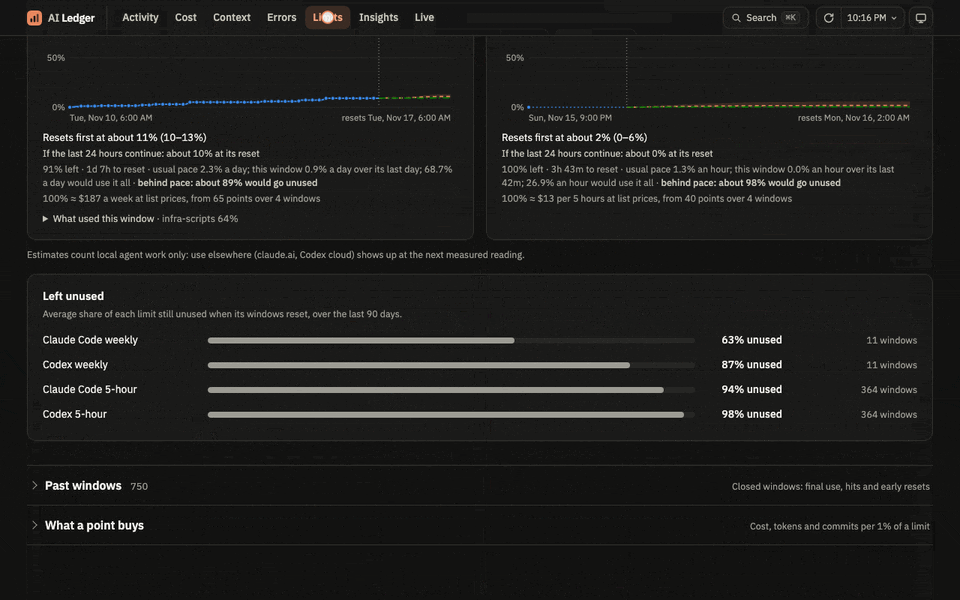
AI Ledger reads your Claude Code and Codex transcripts and turns them into seven local dashboards. Your agents delete old transcripts; AI Ledger keeps every line.
Quick start
uvx ai-ledger # opens http://127.0.0.1:8765/ in your browser
Needs uv. Runs on macOS and Linux. Your data stays on your machine (see Privacy).
What you get
| Page | Shows |
|---|---|
| Activity | What got done per day or week, by project, and what needs your attention. |
| Cost | Estimated spend at API list prices, per project, model and session, compared with your plan. |
| Context | How full the context window gets, how fast it grows, and what fills it. |
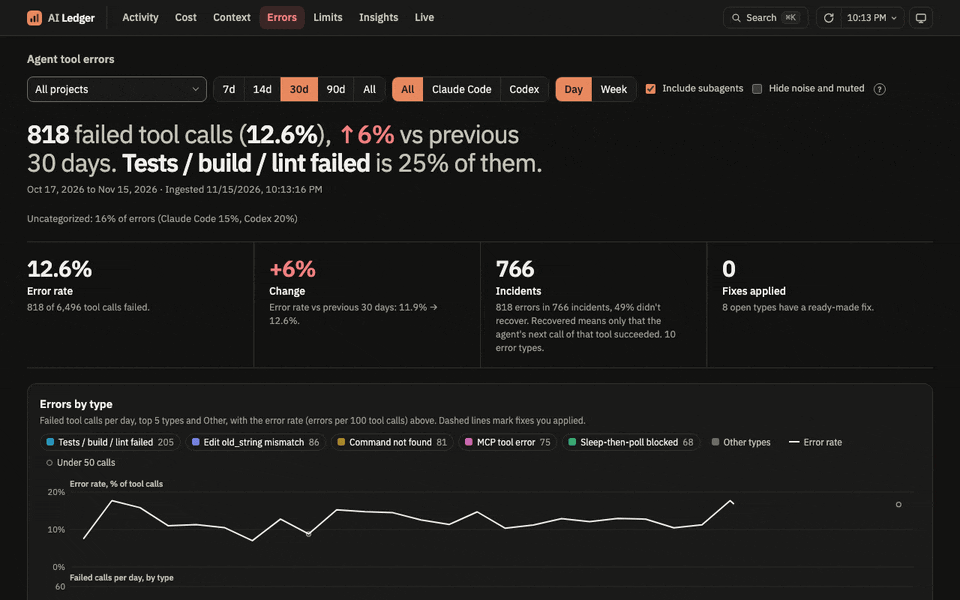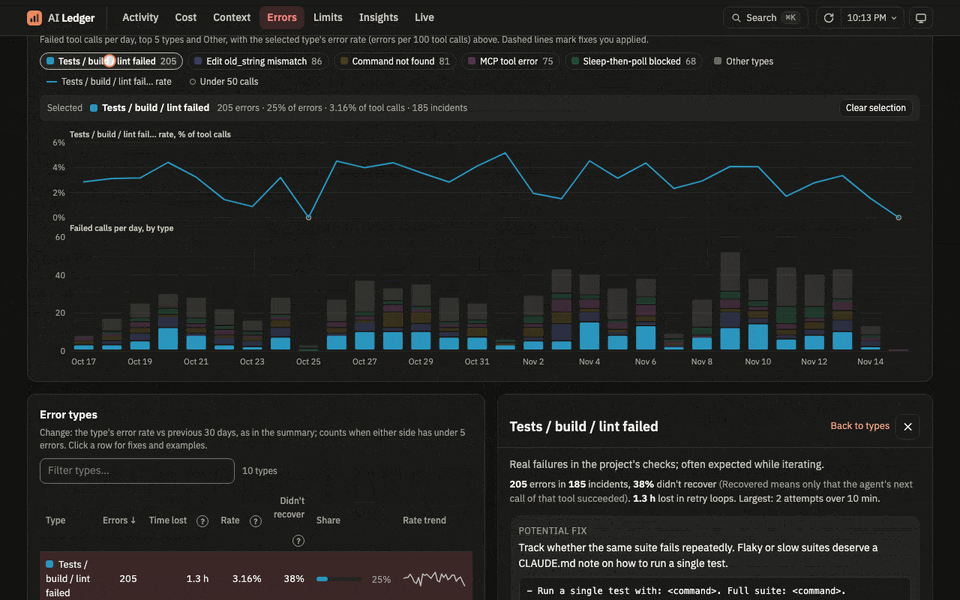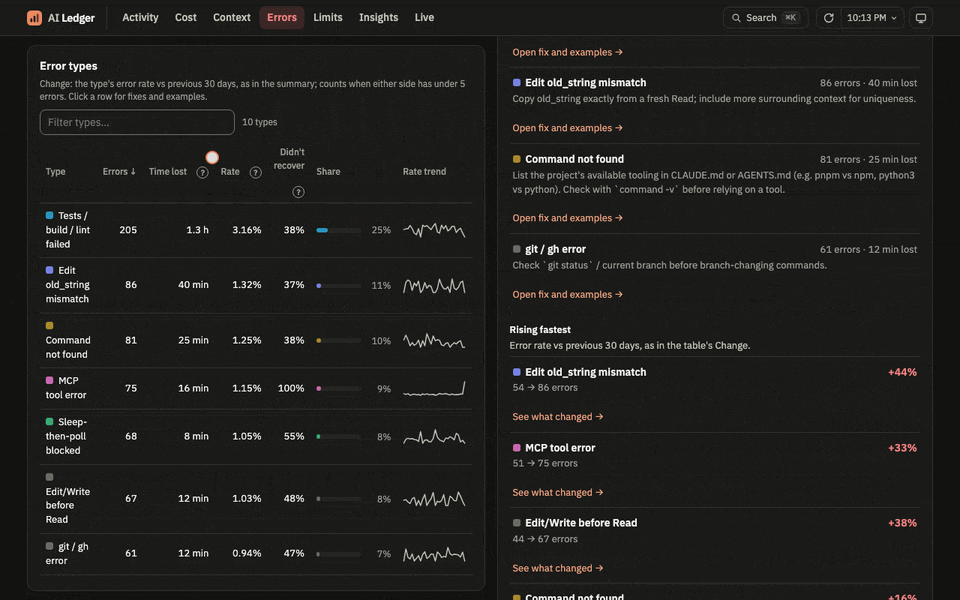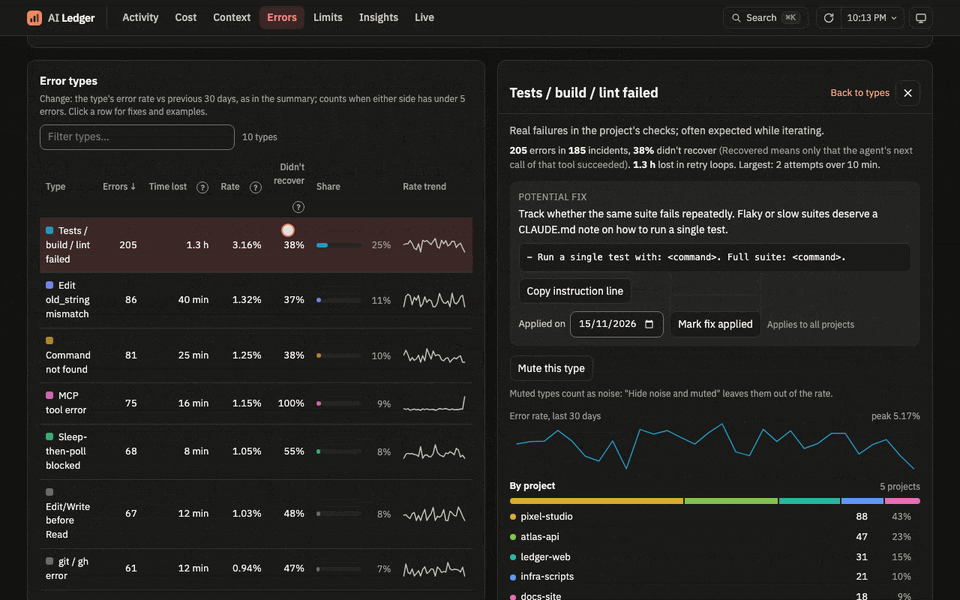
| Errors | Failed tool calls by type, the time they cost, and a fix to paste into CLAUDE.md or AGENTS.md. |
| Limits | Each plan limit window, what used it, and a forecast to its reset. |
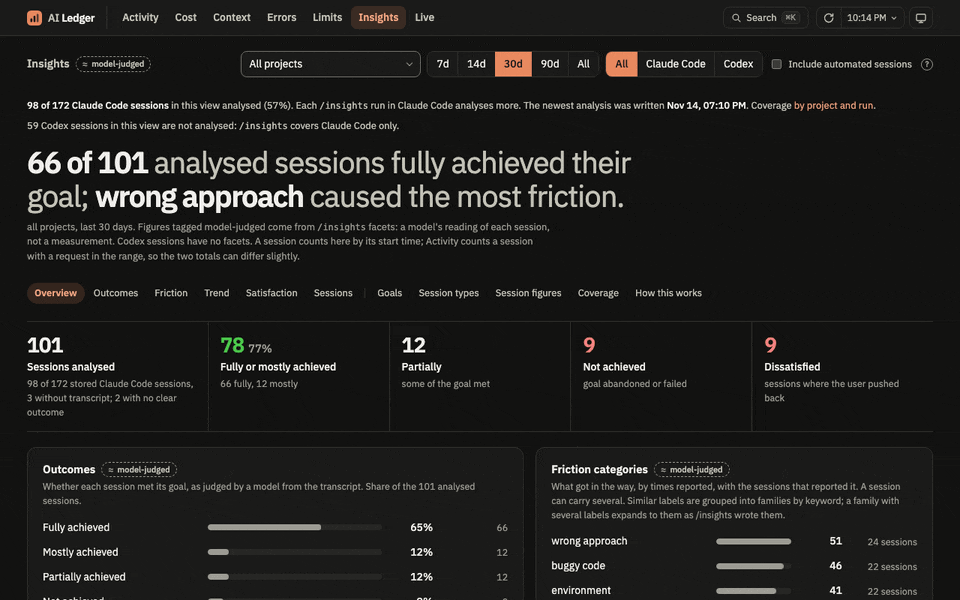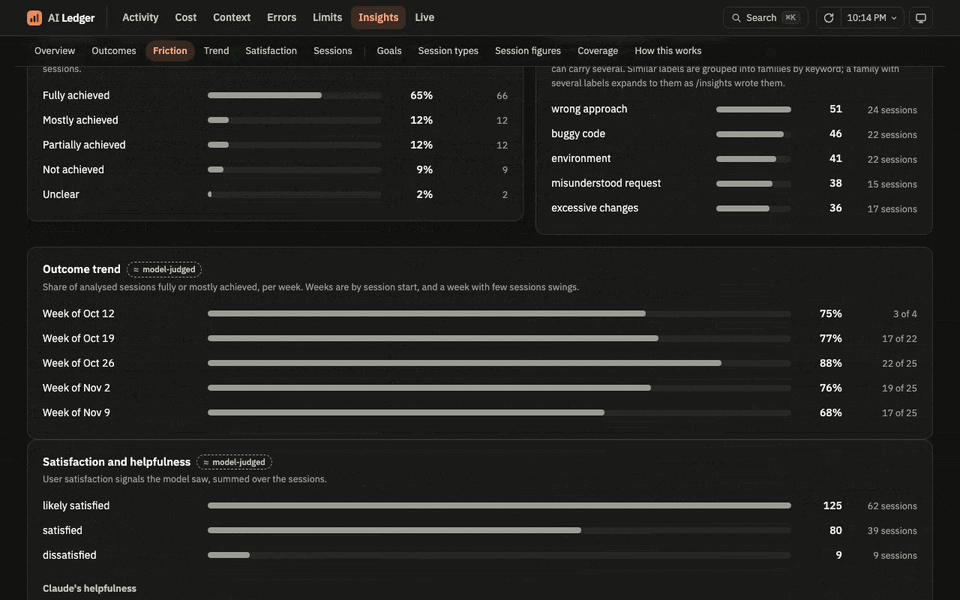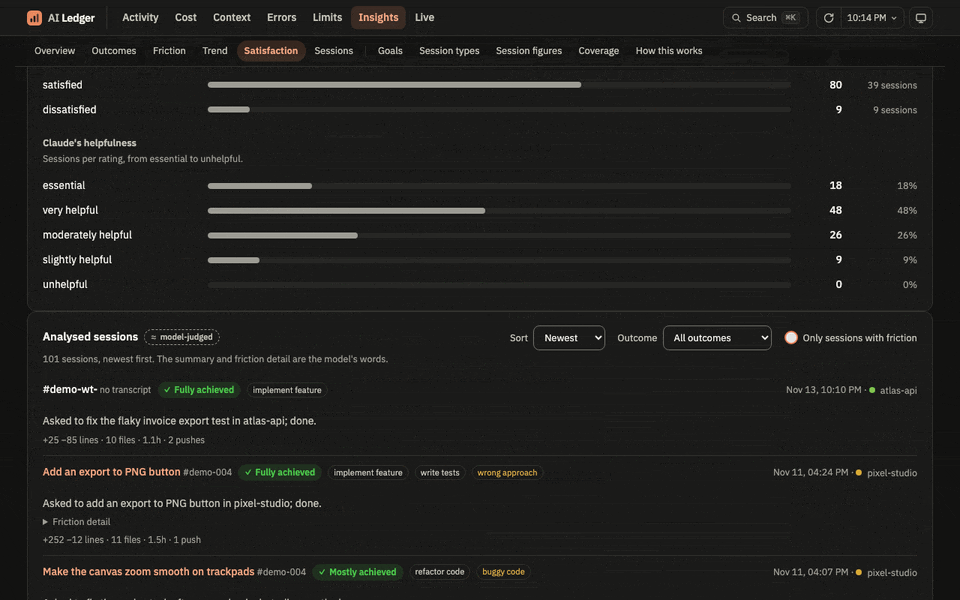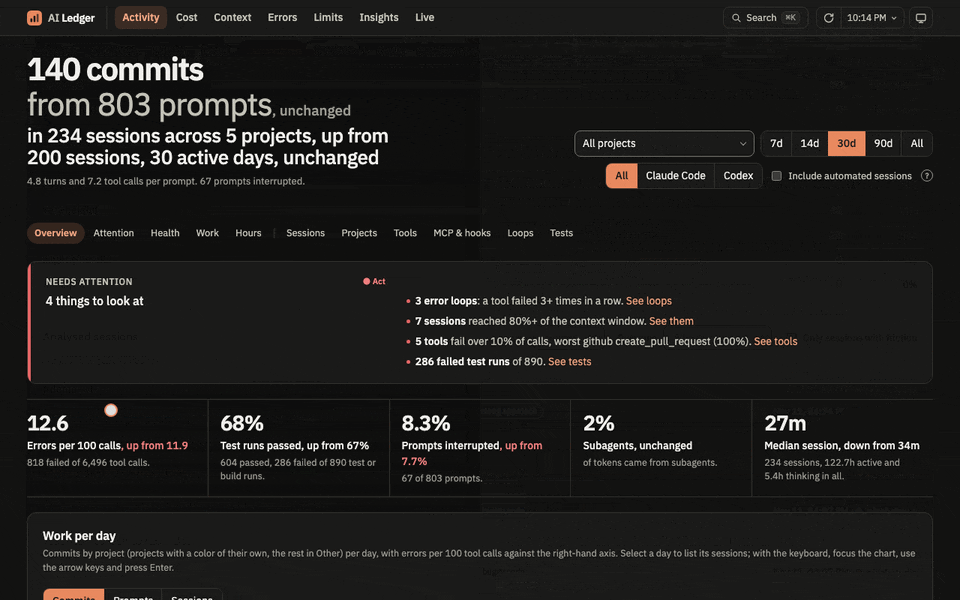
| Insights | How Claude Code's /insights judged your sessions. |
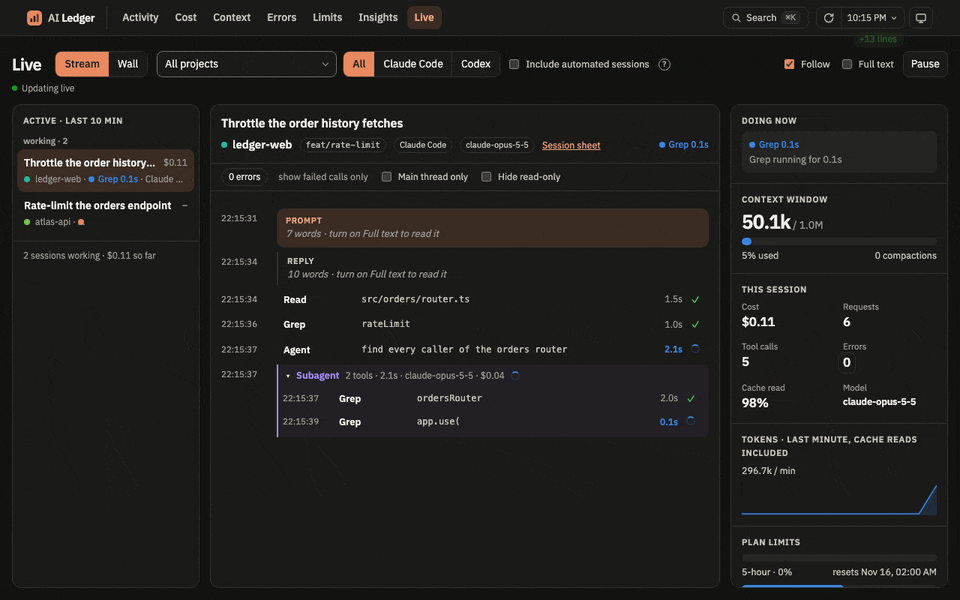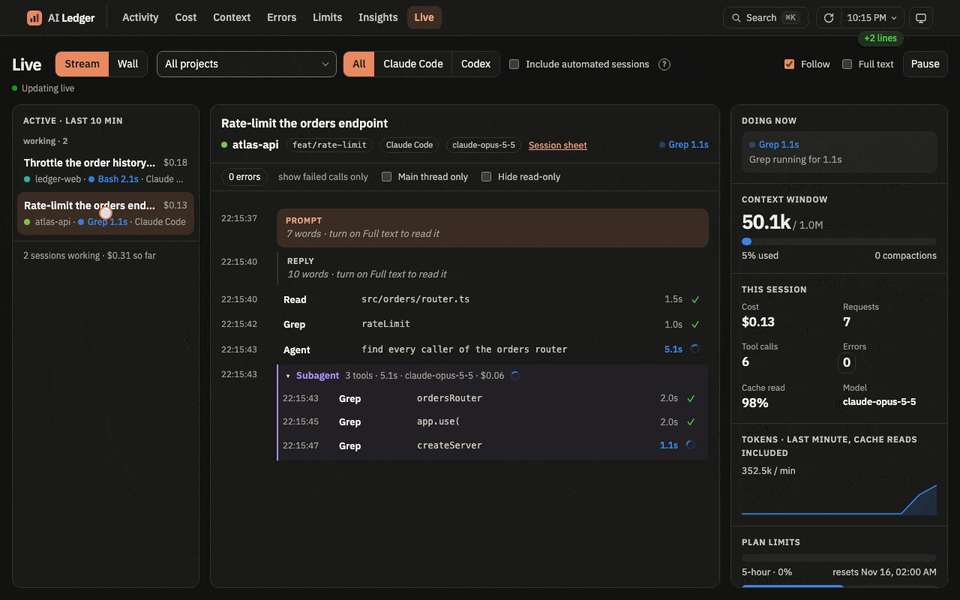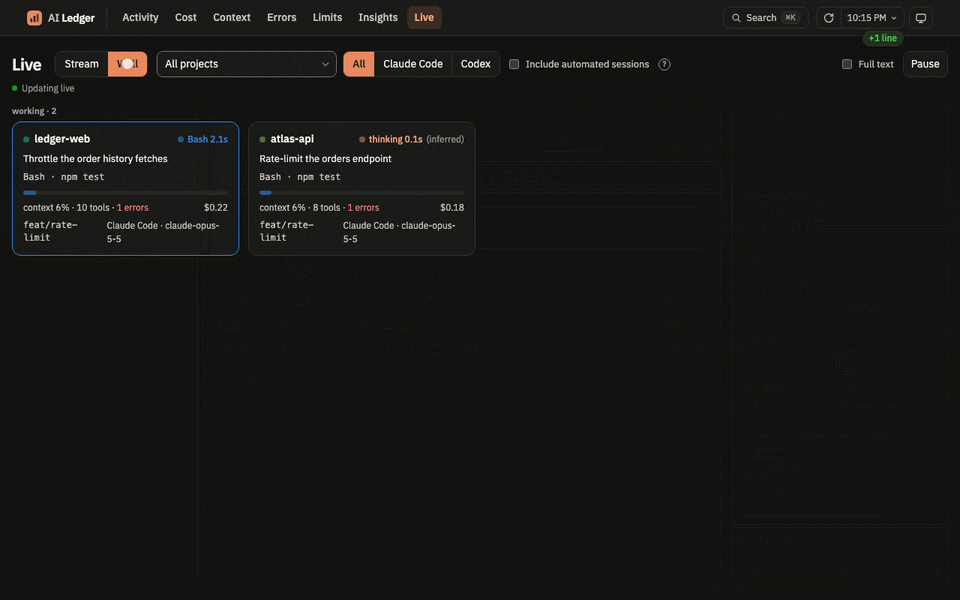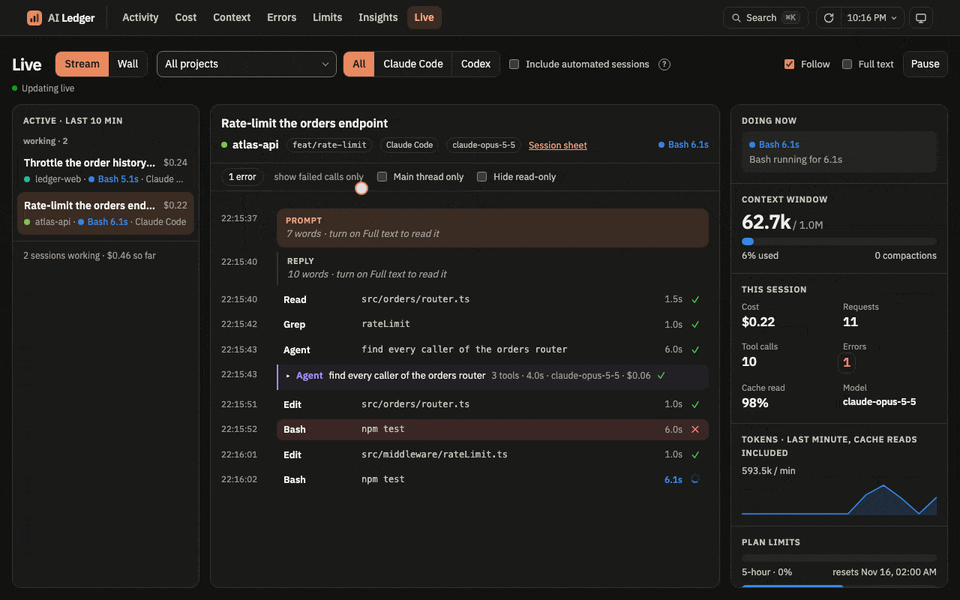
| Live | Every active session as it runs, sorted by who needs you first. |
| Project | One project across all of the above, opened from the Page link on the navigation's project filter, its sheet, or its name in the command palette. |
Press Cmd+K to jump anywhere, for example >errors #myproject #7d. Right-click a project, session, tool or error type for its actions, such as copying a session's resume command. Every page works by keyboard and screen reader, and each chart has a data table.
The user guide describes each page in detail.
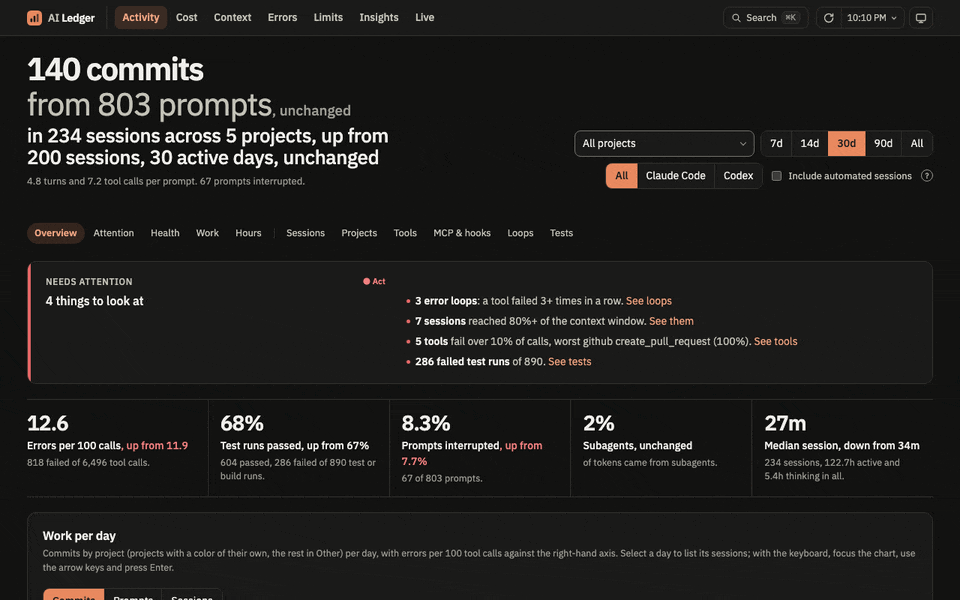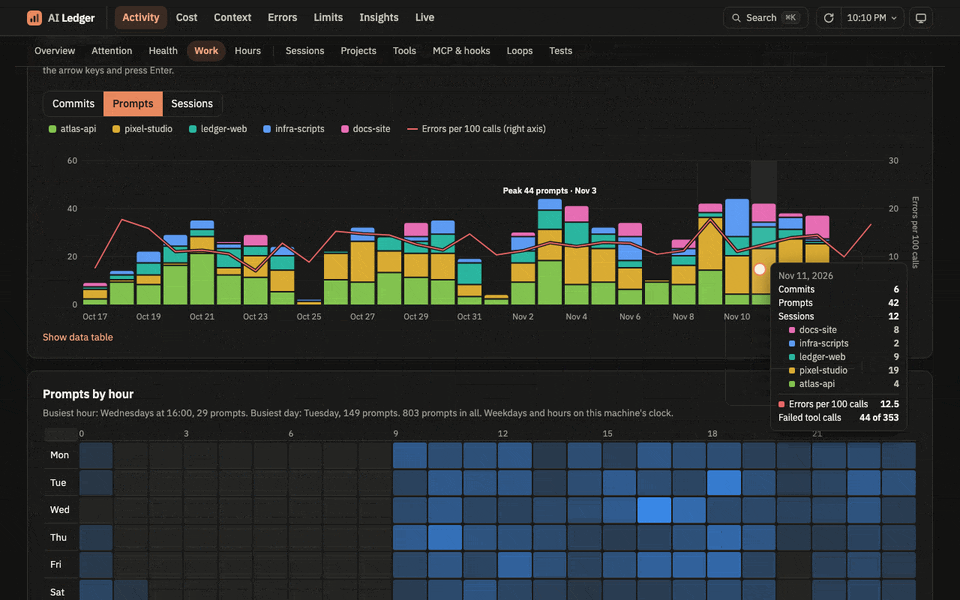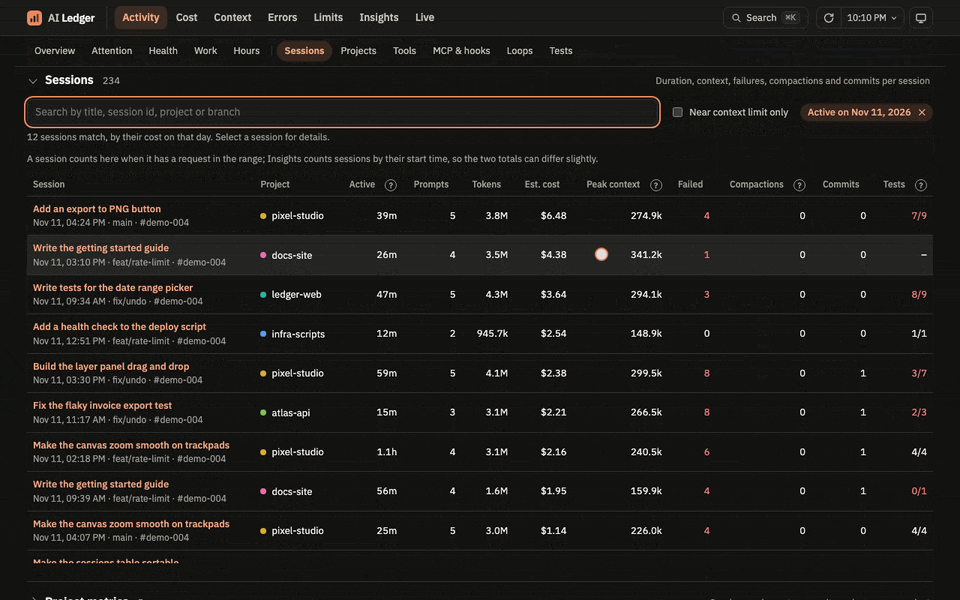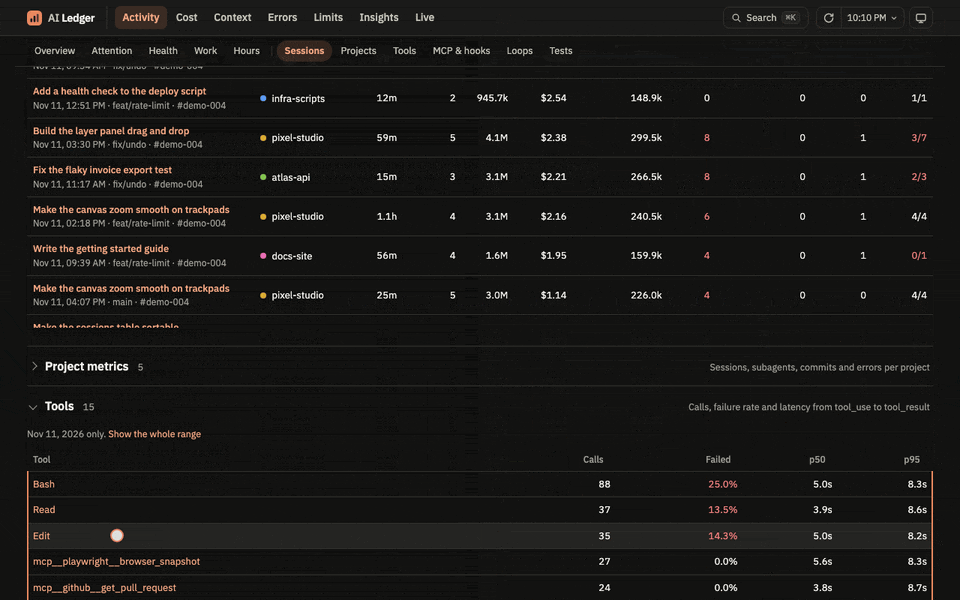 | 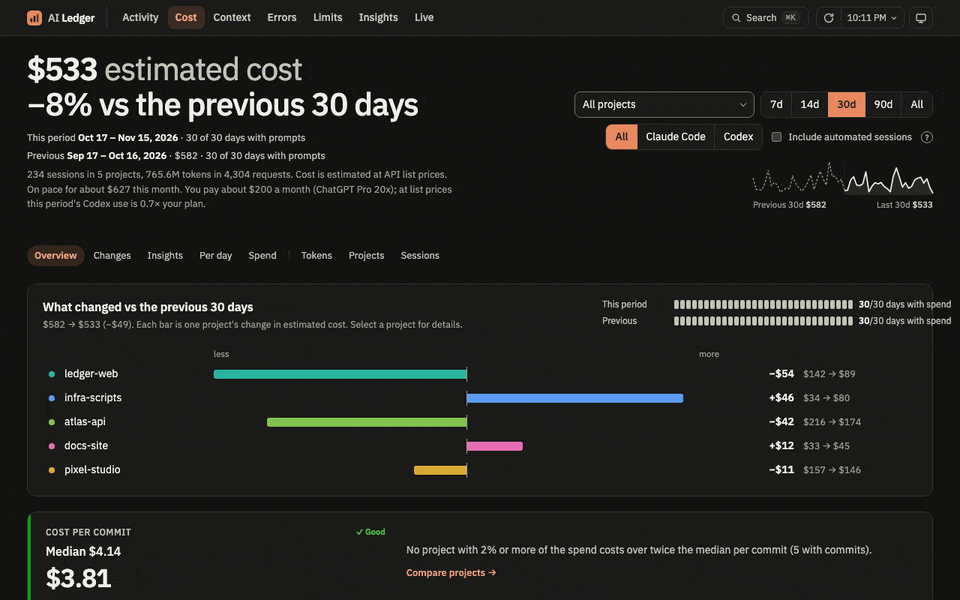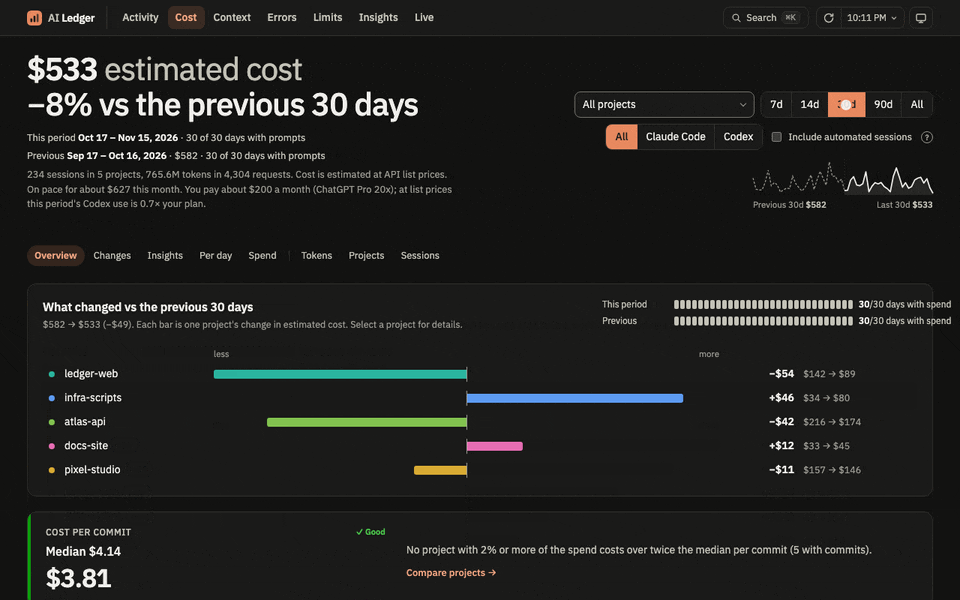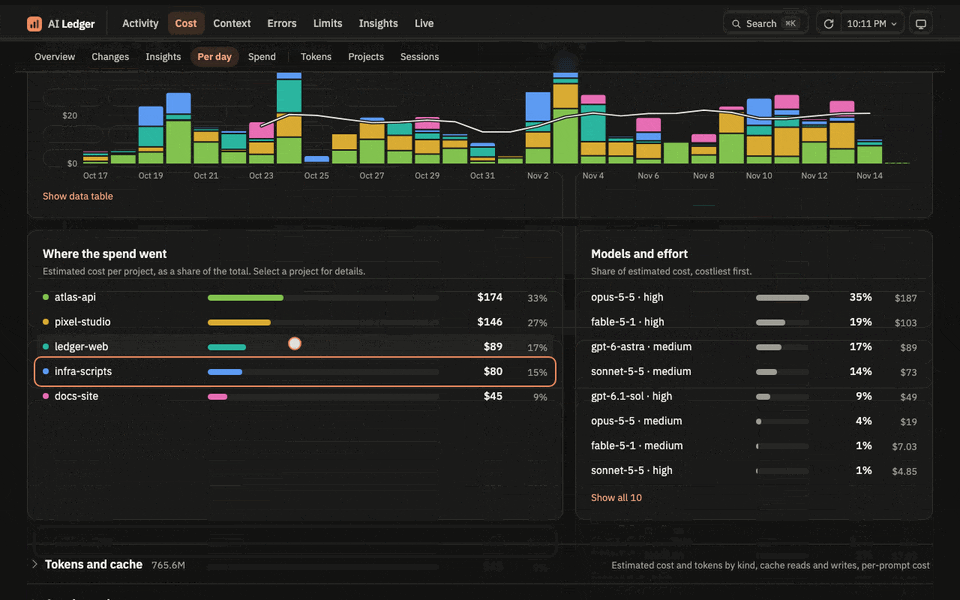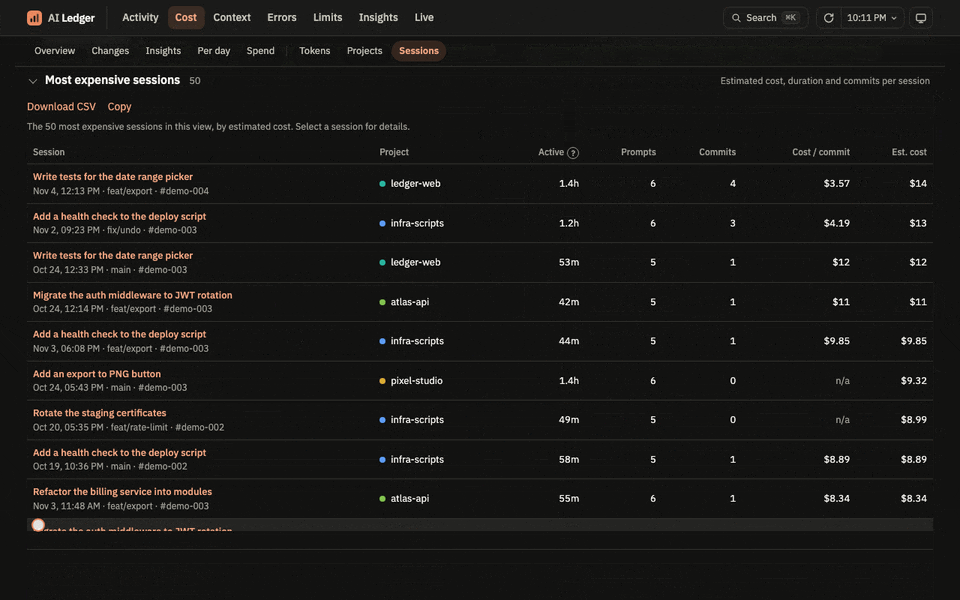 |
 | 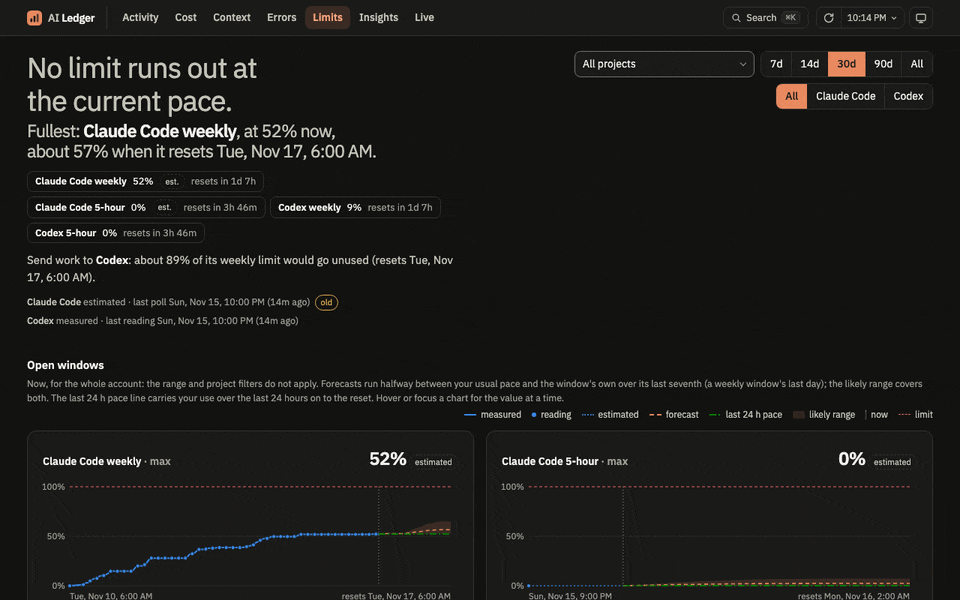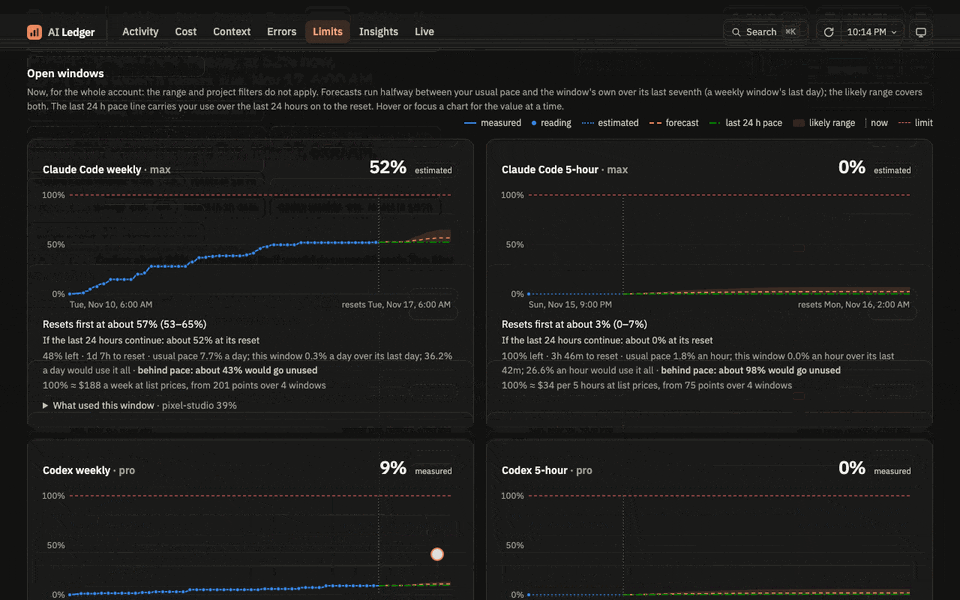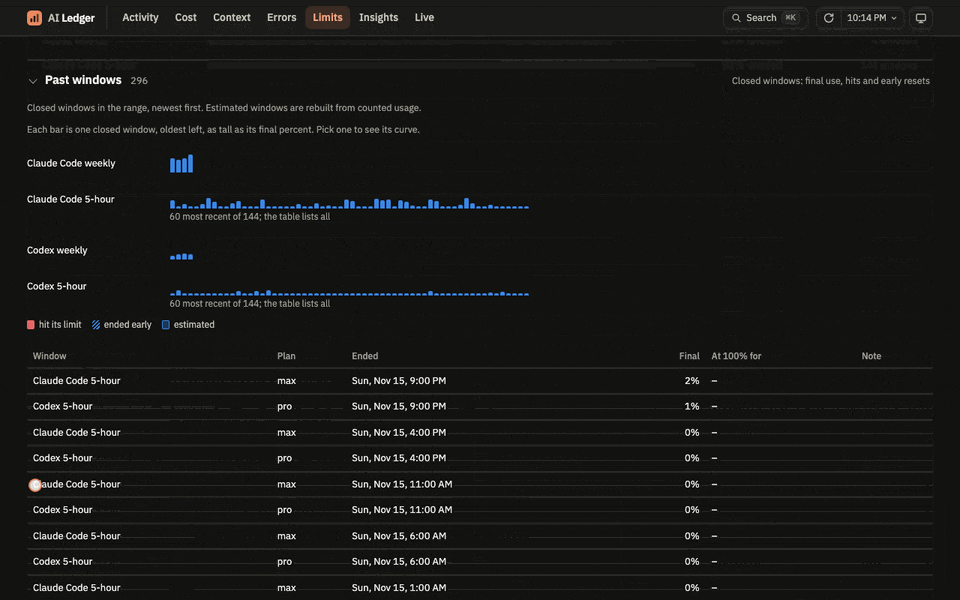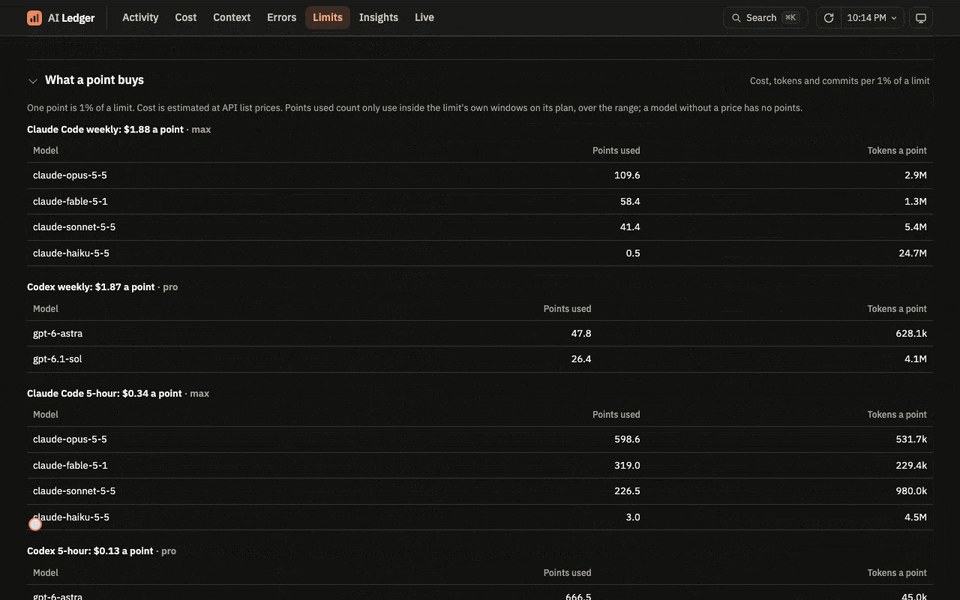 |
 |  |
Install
uv tool install ai-ledger
ai-ledger                   # serve on http://127.0.0.1:8765/ and open it
uv tool upgrade ai-ledger   # new version and new prices
The first start reads every transcript, about 4 minutes for 3.4 GB. After that, the app picks up new lines every 60 seconds.
| Option | Default |
|---|---|
--port |
8765 |
--no-open |
off (opens the browser) |
--projects |
~/.claude/projects |
--codex |
~/.codex |
--usage-data |
~/.claude/usage-data |
--db |
~/Library/Application Support/ai-ledger/ai-ledger.duckdb (macOS), ~/.local/share/ai-ledger/ai-ledger.duckdb (Linux) |
With the app stopped, ai-ledger ingest reads new lines once and ai-ledger rebuild recomputes the derived tables. After an upgrade that asks for it, run ai-ledger rebuild once.
To set your own model prices or plan prices, or to hide more automated projects, see Configuration.
Privacy
- The server listens on
127.0.0.1only, and refuses requests that another site makes from your browser. - The store keeps every transcript line, including any secrets that appeared in a session. Only your user can read it. Do not share it.
- On macOS, the Limits page sends your Claude Code OAuth token from the Keychain to Anthropic's usage endpoint every 5 minutes. The token goes nowhere else and is never stored or logged. On Linux, Limits estimates from transcripts.
- Live's Full text puts transcript content on screen, secrets included. Turn it off before you share your screen.
- Your browser loads the font from Google Fonts. No transcript data goes with it.
Contributing
See CONTRIBUTING.md.
License
1 maintainer

Metadata
1 maintainer
Release files for ai-ledger 0.4.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| ai_ledger-0.4.0.tar.gz | 427.9 kB | With provenance | Details for ai_ledger-0.4.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| ai_ledger-0.4.0-py3-none-any.whl | Python 3 | none | any | Details for ai_ledger-0.4.0-py3-none-any.whl |
Total release size: 874.1 kB
Release files / ai_ledger-0.4.0.tar.gz
| Download URL | ai_ledger-0.4.0.tar.gz |
|---|---|
| Size | 427.9 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
260f984dba4fd21b3d227bfa55aaaf80408e9479a733b52b3a5b6fd7553a8c6c
|
|
BLAKE2b-256 checksum How to use checksums |
fe1944a9962528e6272a178bc45be1a706d064f8676c382e04189bf454e0dc56
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 15, 2026.
Transparency logRelease files / ai_ledger-0.4.0-py3-none-any.whl
| Download URL | ai_ledger-0.4.0-py3-none-any.whl |
|---|---|
| Size | 446.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
e3ff59ffde5034a6d03d57fba3f91b86a25d3bdedc4db6cacd8ac3fda78f600e
|
|
BLAKE2b-256 checksum How to use checksums |
57475c399d67749f1191e4c2c92aa3a8b957b62585ae8167b474e27195bdb5ac
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 15, 2026.
Transparency logSecurity for ai-ledger 0.4.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for ai_ledger-0.4.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 15, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














