
Document analysis for LLM pipelines, fully offline.


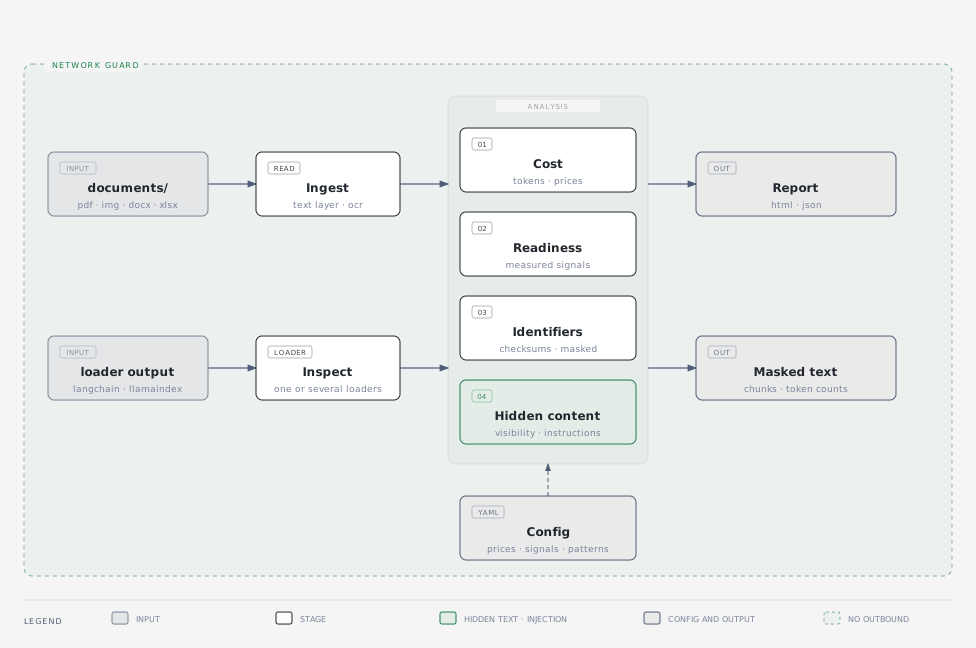
complydoc inspects documents, and the output of document loaders, before they are sent to an LLM. It measures what processing them will cost, how reliably text can be read off each page, which personal and financial identifiers they contain, and whether anything hidden in a file is addressed to a model.
Quickstart
uv tool install complydoc
complydoc audit ./documents
import complydoc as cd

report = cd.full_audit("./documents")
print(report.overall.score)
cd.write_html(report, "report.html")
Output from a LangChain or LlamaIndex loader, or several loaders over a folder:
from langchain_community.document_loaders import PDFPlumberLoader, PyPDFLoader

report = cd.inspect_documents(PyPDFLoader("contract.pdf"))

report = cd.compare_loaders(
    {"pypdf": PyPDFLoader, "pdfplumber": PDFPlumberLoader, "docling": cd.parsers.docling()},
    paths="./contracts",
    facts=["Payment is due within thirty days"],
)
report.to_pandas("loaders")
OCR and name detection are optional extras. complydoc doctor shows what is installed.
What it reports
- Token cost: text and vision tokens per document, priced across models and three extraction paths (text layer, OCR, vision).
- Extraction readiness: measured signals such as text layer coverage, tables, columns, rotation, scan resolution, garbled characters, glyph codes and repeated headers.
- Identifiers: personal and financial identifiers in UK, US and EU formats, checksum-validated where a checksum exists, masked in every output.
- Hidden content and prompt injection: text a reader does not see and a model does (white or invisible text, hidden formatting, Unicode tag characters), and passages that read as instructions to a model.
- Loader inspection and comparison: what a loader extracted, the metadata it attached, the network connections it attempted, and where several loaders disagree, over a single input or a folder, with failures, load time and estimated parser cost per loader.
- Expected facts: whether passages you expect appear in each loader's text, as exact or fuzzy matches.
- Parser presets: Docling, Unstructured, LlamaParse and Azure Document Intelligence;
hosted parsers run only with
allow_network=True. - Tables: every part of a report as a pandas DataFrame, and a summary in Jupyter.
- Masked text: the documents' text with identifiers covered, chunked and counted in tokens.
How it works
- Offline: outbound sockets and DNS lookups are blocked for the whole run, and each report records that the guard was armed.
- Unmeasured values: a signal that cannot be measured is reported as unmeasured and left out of scores.
- Evidence tiers: every finding states how it was established, whether by checksum, corroboration, pattern or model.
- Configurable: prices, signal weights and detection patterns are YAML files.
- One report: a self-contained HTML file and a JSON file with a versioned schema.
Resources
- Documentation: guides and design notes
- Command line reference
- Python API reference
- Report JSON
- Changelog
- Contributing
License
MIT
1 maintainer

Release files for complydoc 0.4.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| complydoc-0.4.0.tar.gz | 3.7 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| complydoc-0.4.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 6.6 MB
Release files / complydoc-0.4.0.tar.gz
| Download URL | complydoc-0.4.0.tar.gz |
|---|---|
| Size | 3.7 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
069977e085abb91a2f7ba77b24fae3a88d4469924c19f02d42e119f560350ef1
|
|
BLAKE2b-256 checksum How to use checksums |
75b6793140026053ff1116c0298156c6dec59e29cd6971e467a1e7c64240ba58
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 14, 2026.
Transparency logRelease files / complydoc-0.4.0-py3-none-any.whl
| Download URL | complydoc-0.4.0-py3-none-any.whl |
|---|---|
| Size | 2.9 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
262ed3364954601323552464410a7dee61227c256777ca68067e6e93647ab5bf
|
|
BLAKE2b-256 checksum How to use checksums |
de6545f56982e4f2bb560fdad18c71537833995097042ab2663092410b7acedb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 14, 2026.
Transparency log













