
grip
Pass the whiteboard defense before you push.


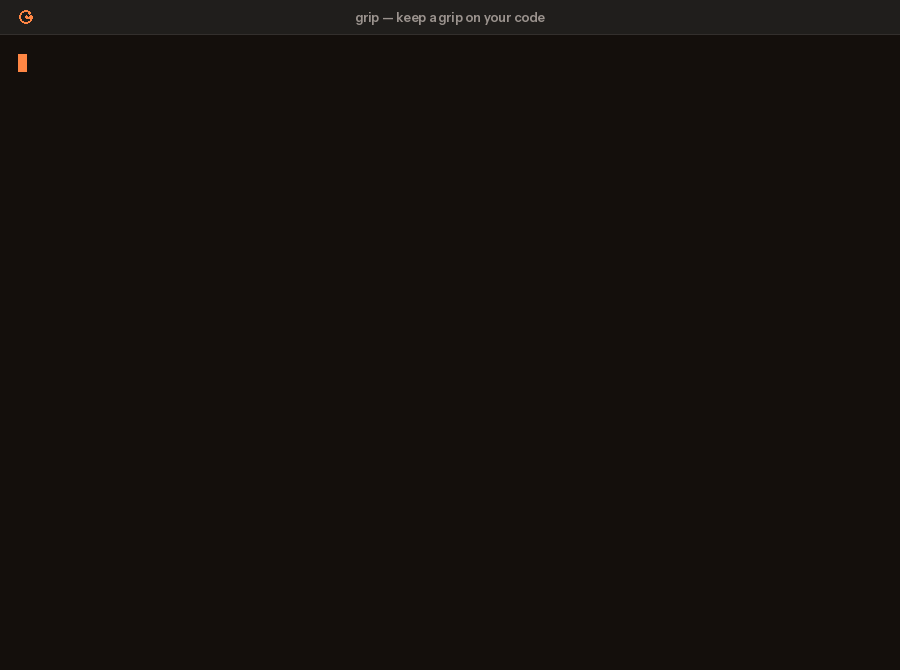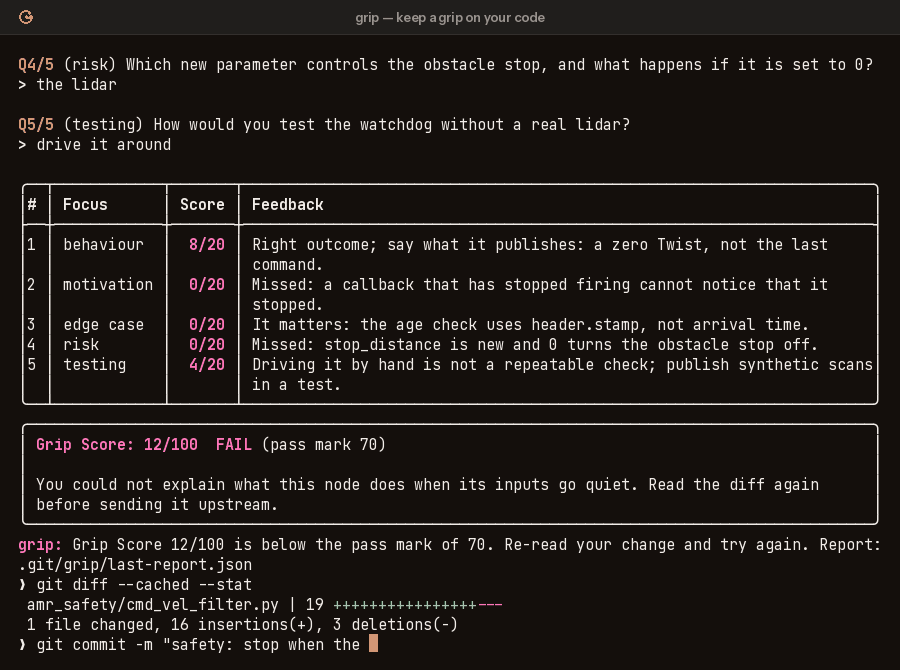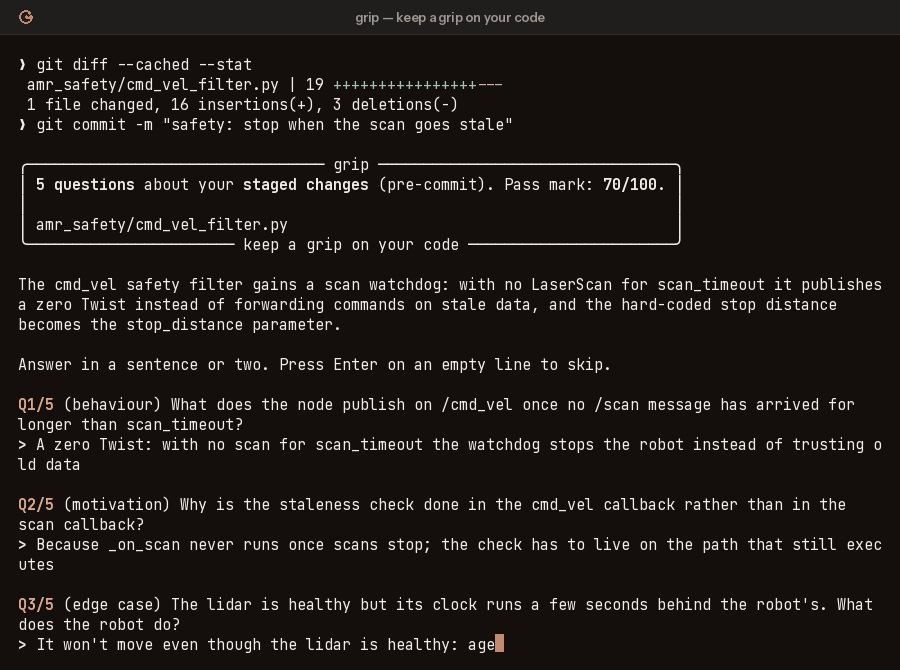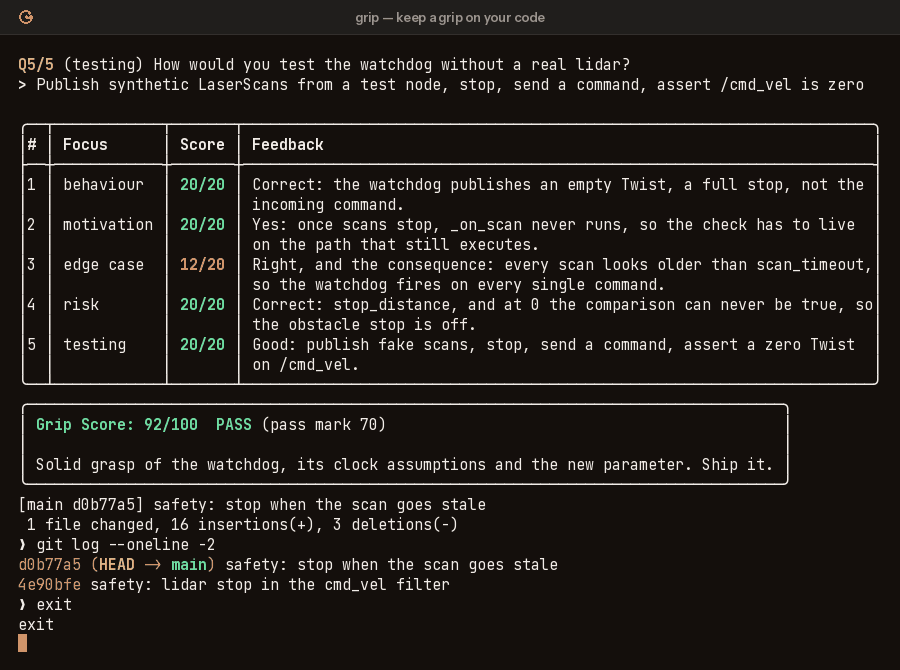
grip is a git hook that asks you five questions about your own diff before it leaves your machine: what it does, why it is built this way, where it fails, what could go wrong, how you know it works. A model writes the questions and a hidden rubric from the diff, then grades your answers. Score below your team's pass mark and the push is blocked.
It checks the developer, not the code: you can ship code a model wrote, as long as you can explain and defend it.
Features
- Five questions from your diff, graded against a hidden rubric into a Grip Score out of 100. Never line numbers or trivia.
grip whiteboard: your change drawn as parts and arrows in the browser, with the questions pinned to it, including what a malicious actor could do.- Works with what you have: reuse Claude Code, Codex or Gemini CLI as the model (no API key), or use Anthropic, any OpenAI-compatible API, or Ollama locally.
- Inside coding agents:
/gripin Claude Code, Codex, Gemini CLI, Cursor and others, and a gate that keeps the agent from pushing until you pass. - Out of the way when it should be: a passed diff is remembered,
grip skiplets one push through, CI and non-interactive runs are skipped.
Installation
pipx install grip-hook # or: uv tool install grip-hook
Python 3.11 or newer, on Linux, macOS or Windows. This installs the grip command and a
git grip alias.
Quick start
cd your-repo
grip init        # writes .grip.toml, installs the pre-push hook
git push         # grip asks five questions first
grip init picks Claude Code, Codex or Gemini CLI as the model when one is installed.
Otherwise set ANTHROPIC_API_KEY, or see Providers.
Other commands you will use:
grip quiz                  # quiz your staged changes now, no hook needed
grip whiteboard            # defend the change in the browser
grip quiz --provider fake  # try it offline with a scripted grader
grip skip                  # let the next push through
grip status                # hooks, last score, configuration
The walkthrough follows one real change from
git commit to an accepted push.
Configuration
.grip.toml at the root of the repository, committed so the team shares one bar:
passing_score = 70        # 0-100
difficulty = "normal"     # easy | normal | hard
provider = "claude-code"  # auto | anthropic | claude-code | codex | gemini | openai | ollama
Every option, environment variables and the pre-commit framework hook are in the configuration reference.
Documentation
guilyx.github.io/grip: getting started, a walkthrough, coding agents, the whiteboard, how grip works inside, and the honest numbers on what the score does and does not measure.
Contributing
Issues and pull requests are welcome. See CONTRIBUTING.md for the development setup and SECURITY.md for reporting vulnerabilities and what data grip sends. This project follows a code of conduct.
Citation
If grip is part of a study or a course, please cite it; GitHub's "Cite this repository" button reads CITATION.cff.
License
BSD-3-Clause. Copyright (c) 2026, Erwin L.
1 maintainer

Metadata
1 maintainer
Release files for grip-hook 0.2.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| grip_hook-0.2.2.tar.gz | 118.5 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| grip_hook-0.2.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 207.2 kB
Release files / grip_hook-0.2.2.tar.gz
| Download URL | grip_hook-0.2.2.tar.gz |
|---|---|
| Size | 118.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
47481eb441fea0eaee7acf257dbdfdd4148e9ad442b18889dd8b30df262c5781
|
|
BLAKE2b-256 checksum How to use checksums |
b325761dd9bb4074cb35dd1f2640bced3e914b3a9a9b86ab8b1bafeaa0ba855a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / grip_hook-0.2.2-py3-none-any.whl
| Download URL | grip_hook-0.2.2-py3-none-any.whl |
|---|---|
| Size | 88.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
ca9a5f541261f26be40c28bf29a4bdbaa7f0076c42b70171a9fbf82aff131dfa
|
|
BLAKE2b-256 checksum How to use checksums |
ad102d3d4fa3d4f729fee64e86763a93f42d088794909301bc4abe6d3be2f07d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logSecurity for grip-hook 0.2.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for grip_hook-0.2.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














