
napari-copick


A plugin for collaborative annotation in cryoET using copick
This napari plugin was generated with Cookiecutter using @napari's cookiecutter-napari-plugin template.
Installation
You can install napari-copick via pip:
pip install napari-copick
To install latest development version:
pip install git+https://github.com/copick/napari-copick.git
Usage
Using a copick config file
napari-copick run --config path/to/copick_config.json
Using dataset IDs from CZ cryoET Data Portal
napari-copick run --dataset-ids 10440 10441 --overlay-root /path/to/overlay_root
You can specify multiple dataset IDs separated by spaces.
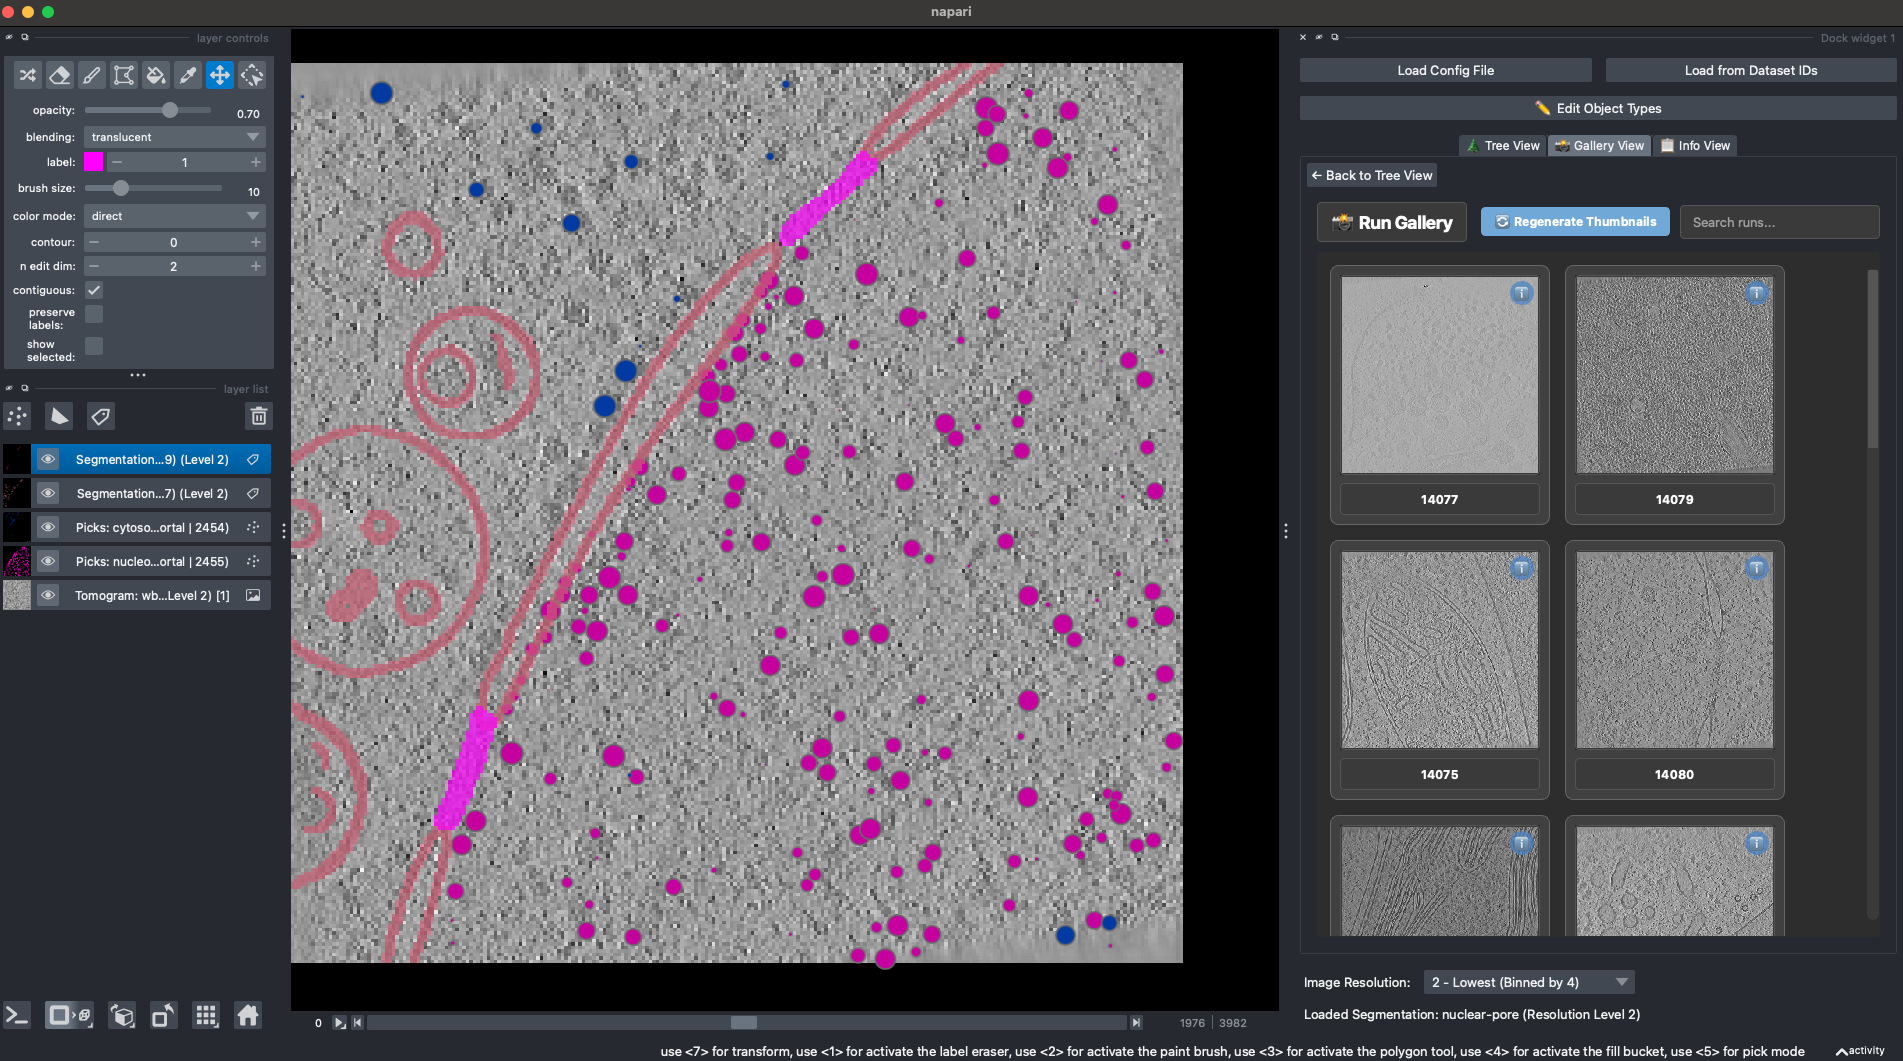
GUI Usage
The plugin provides an intuitive interface with two loading options:
- Load Config File: Opens a file dialog to select a copick configuration JSON file
- Load from Dataset IDs: Opens a dialog to enter CZ cryoET Data Portal dataset IDs and overlay root path
After loading, you'll see a hierarchical tree of the project structure that you can navigate to access tomograms, segmentations, and picks.
Tomogram Handling
napari-copick now handles multiscale zarr arrays directly:
- Automatically detects and loads all available resolution levels
- Creates a proper multiscale image stack using napari's native multiscale API
- Uses dask for efficient lazy loading of large tomogram data
- Applies appropriate scaling factors based on the voxel size metadata
This direct zarr handling provides better performance and more flexibility compared to relying on external plugins.
Contributing
Contributions are very welcome. Tests can be run with tox, please ensure the coverage at least stays the same before you submit a pull request.
License
Distributed under the terms of the MIT license, "napari-copick" is free and open source software
Issues
If you encounter any problems, please file an issue along with a detailed description.
Code of Conduct
This project adheres to the Contributor Covenant code of conduct. By participating, you are expected to uphold this code. Please report unacceptable behavior to opensource@chanzuckerberg.com.
Reporting Security Issues
If you believe you have found a security issue, please responsibly disclose by contacting us at security@chanzuckerberg.com.
1 maintainer

Metadata
1 maintainer
Release files for napari-copick 1.10.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| napari_copick-1.10.0.tar.gz | 1.1 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| napari_copick-1.10.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.2 MB
Release files / napari_copick-1.10.0.tar.gz
| Download URL | napari_copick-1.10.0.tar.gz |
|---|---|
| Size | 1.1 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
d4aeda6900d6a816c803ac1b17a66511c844726b90ea38edbfe4b533d3de23ba
|
|
BLAKE2b-256 checksum How to use checksums |
b95787e3b073f0e80e562db800f54ed09a8f4feee83101539d939be6ac63c121
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / napari_copick-1.10.0-py3-none-any.whl
| Download URL | napari_copick-1.10.0-py3-none-any.whl |
|---|---|
| Size | 71.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
1ba0a55b5240ba5a28debf6fcf8e0ec34bfe6e3afd31093e733cc2085c0329fe
|
|
BLAKE2b-256 checksum How to use checksums |
1b0d89580275a8e6c0268f6283c2ccc661bded1919ad668996c932e819f83a2d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency log













