

Code scanning at ludicrous speed.


Semgrep is a fast, open-source, static analysis tool that searches code, finds bugs, and enforces secure guardrails and coding standards. Semgrep supports 30+ languages and can run in an IDE, as a pre-commit check, and as part of CI/CD workflows.
Semgrep is semantic grep for code. While running grep "2" would only match the exact string 2, Semgrep would match x = 1; y = x + 1 when searching for 2. Semgrep rules look like the code you already write; no abstract syntax trees, regex wrestling, or painful DSLs.
Note that in security contexts, Semgrep Community Edition will miss many true positives as it can only analyze code within the boundaries of a single function or file. If you want to use Semgrep for security purposes (SAST, SCA, or secrets scanning), the Semgrep AppSec Platform is strongly recommended since it adds the following critical capabilities:
- Improved core analysis capabilities (cross-file, cross-function, data-flow reachability) that greatly reduce false positives by 25% and increase detected true positives by 250%
- Contextual post-processing of findings with Semgrep Assistant (AI) to further reduce noise by ~20%. In addition, Assistant enriches findings with tailored, step-by-step remediation guidance that humans find actionable >80% of the time.
- Customizable policies and seamless integration into developer workflows, giving security teams granular control over where, when, and how different findings are presented to developers (IDE, PR comment, etc.)
The Semgrep AppSec Platform works out-of-the-box with 20000+ proprietary rules across SAST, SCA, and secrets. Pro rules are written and maintained by the Semgrep security research team and are highly accurate, meaning AppSec teams can feel confident bringing findings directly to developers without slowing them down.
Semgrep analyzes code locally on your computer or in your build environment: by default, code is never uploaded. Get started →.
Language support
Semgrep Code supports 30+ languages, including:
Apex · Bash · C · C++ · C# · Clojure · Dart · Dockerfile · Elixir · HTML · Go · Java · JavaScript · JSX · JSON · Julia · Jsonnet · Kotlin · Lisp · Lua · OCaml · PHP · Python · R · Ruby · Rust · Scala · Scheme · Solidity · Swift · Terraform · TypeScript · TSX · YAML · XML · Generic (ERB, Jinja, etc.)
Semgrep Supply Chain supports 12 languages across 15 package managers, including:
C# (NuGet) · Dart (Pub) · Go (Go modules, go mod) · Java (Gradle, Maven) · Javascript/Typescript (npm, Yarn, Yarn 2, Yarn 3, pnpm) · Kotlin (Gradle, Maven) · PHP (Composer) · Python (pip, pip-tool, Pipenv, Poetry) · Ruby (RubyGems) · Rust (Cargo) · Scala (Maven) · Swift (SwiftPM)
For more information, see Supported languages.
Getting started 🚀
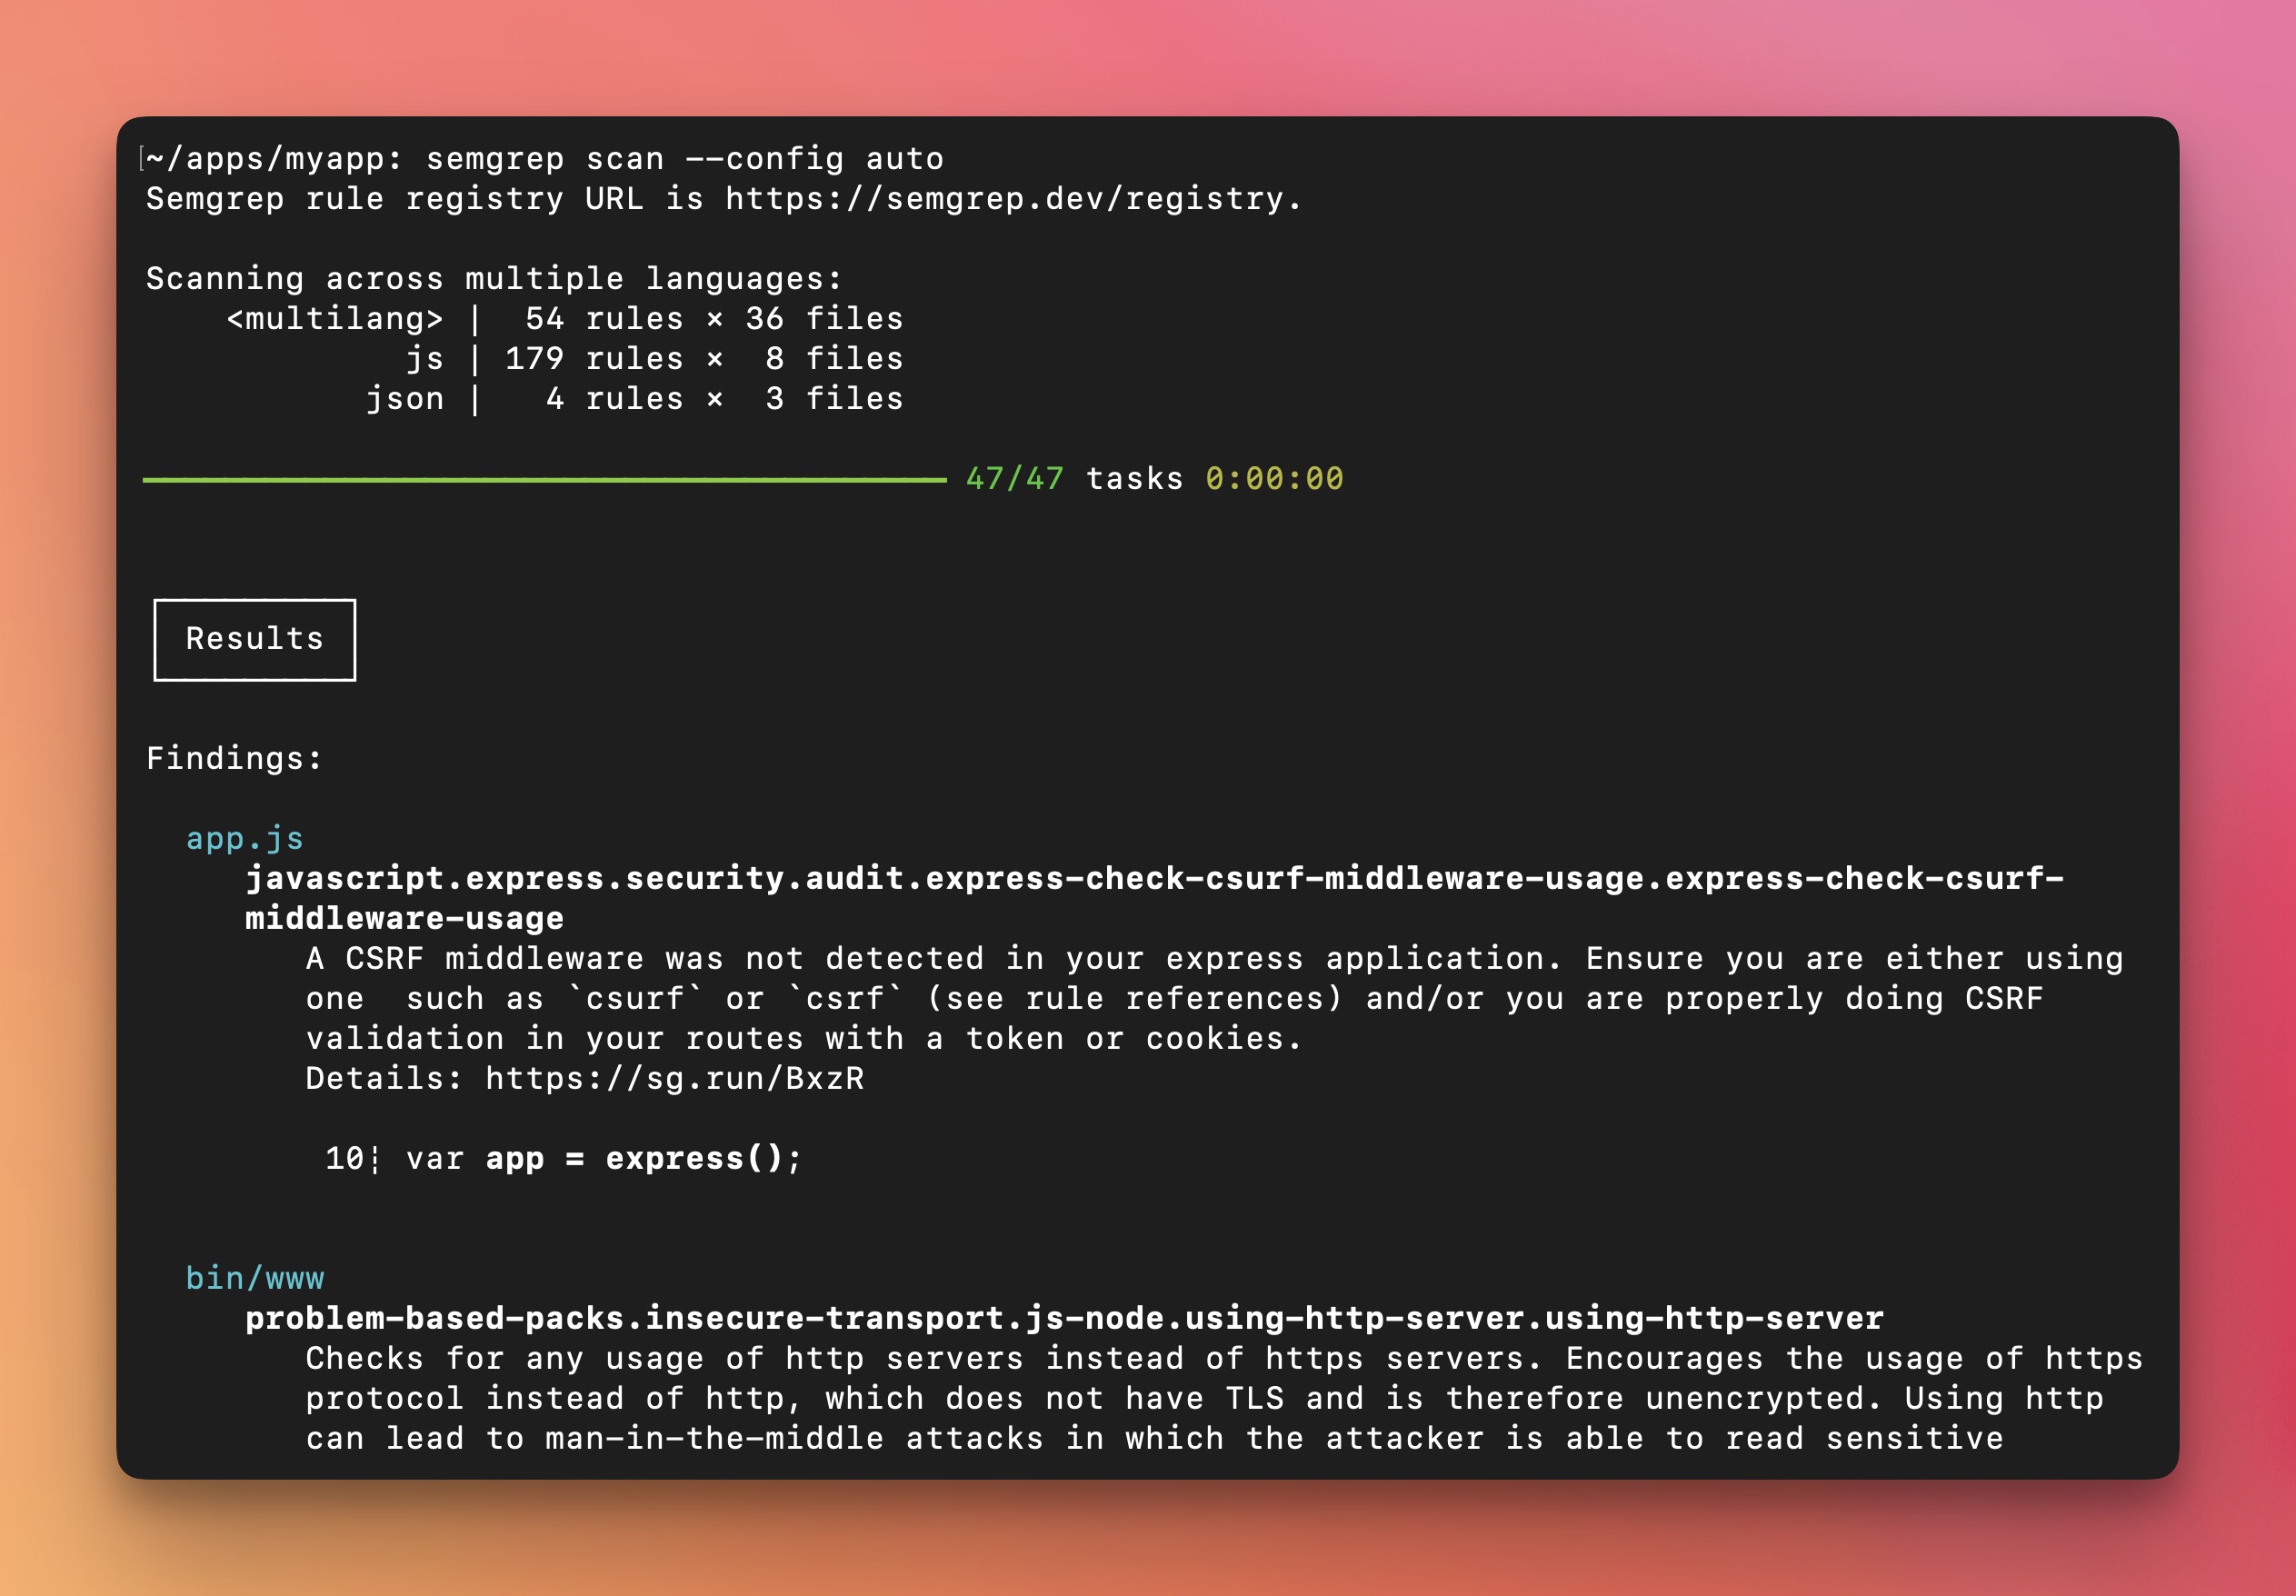
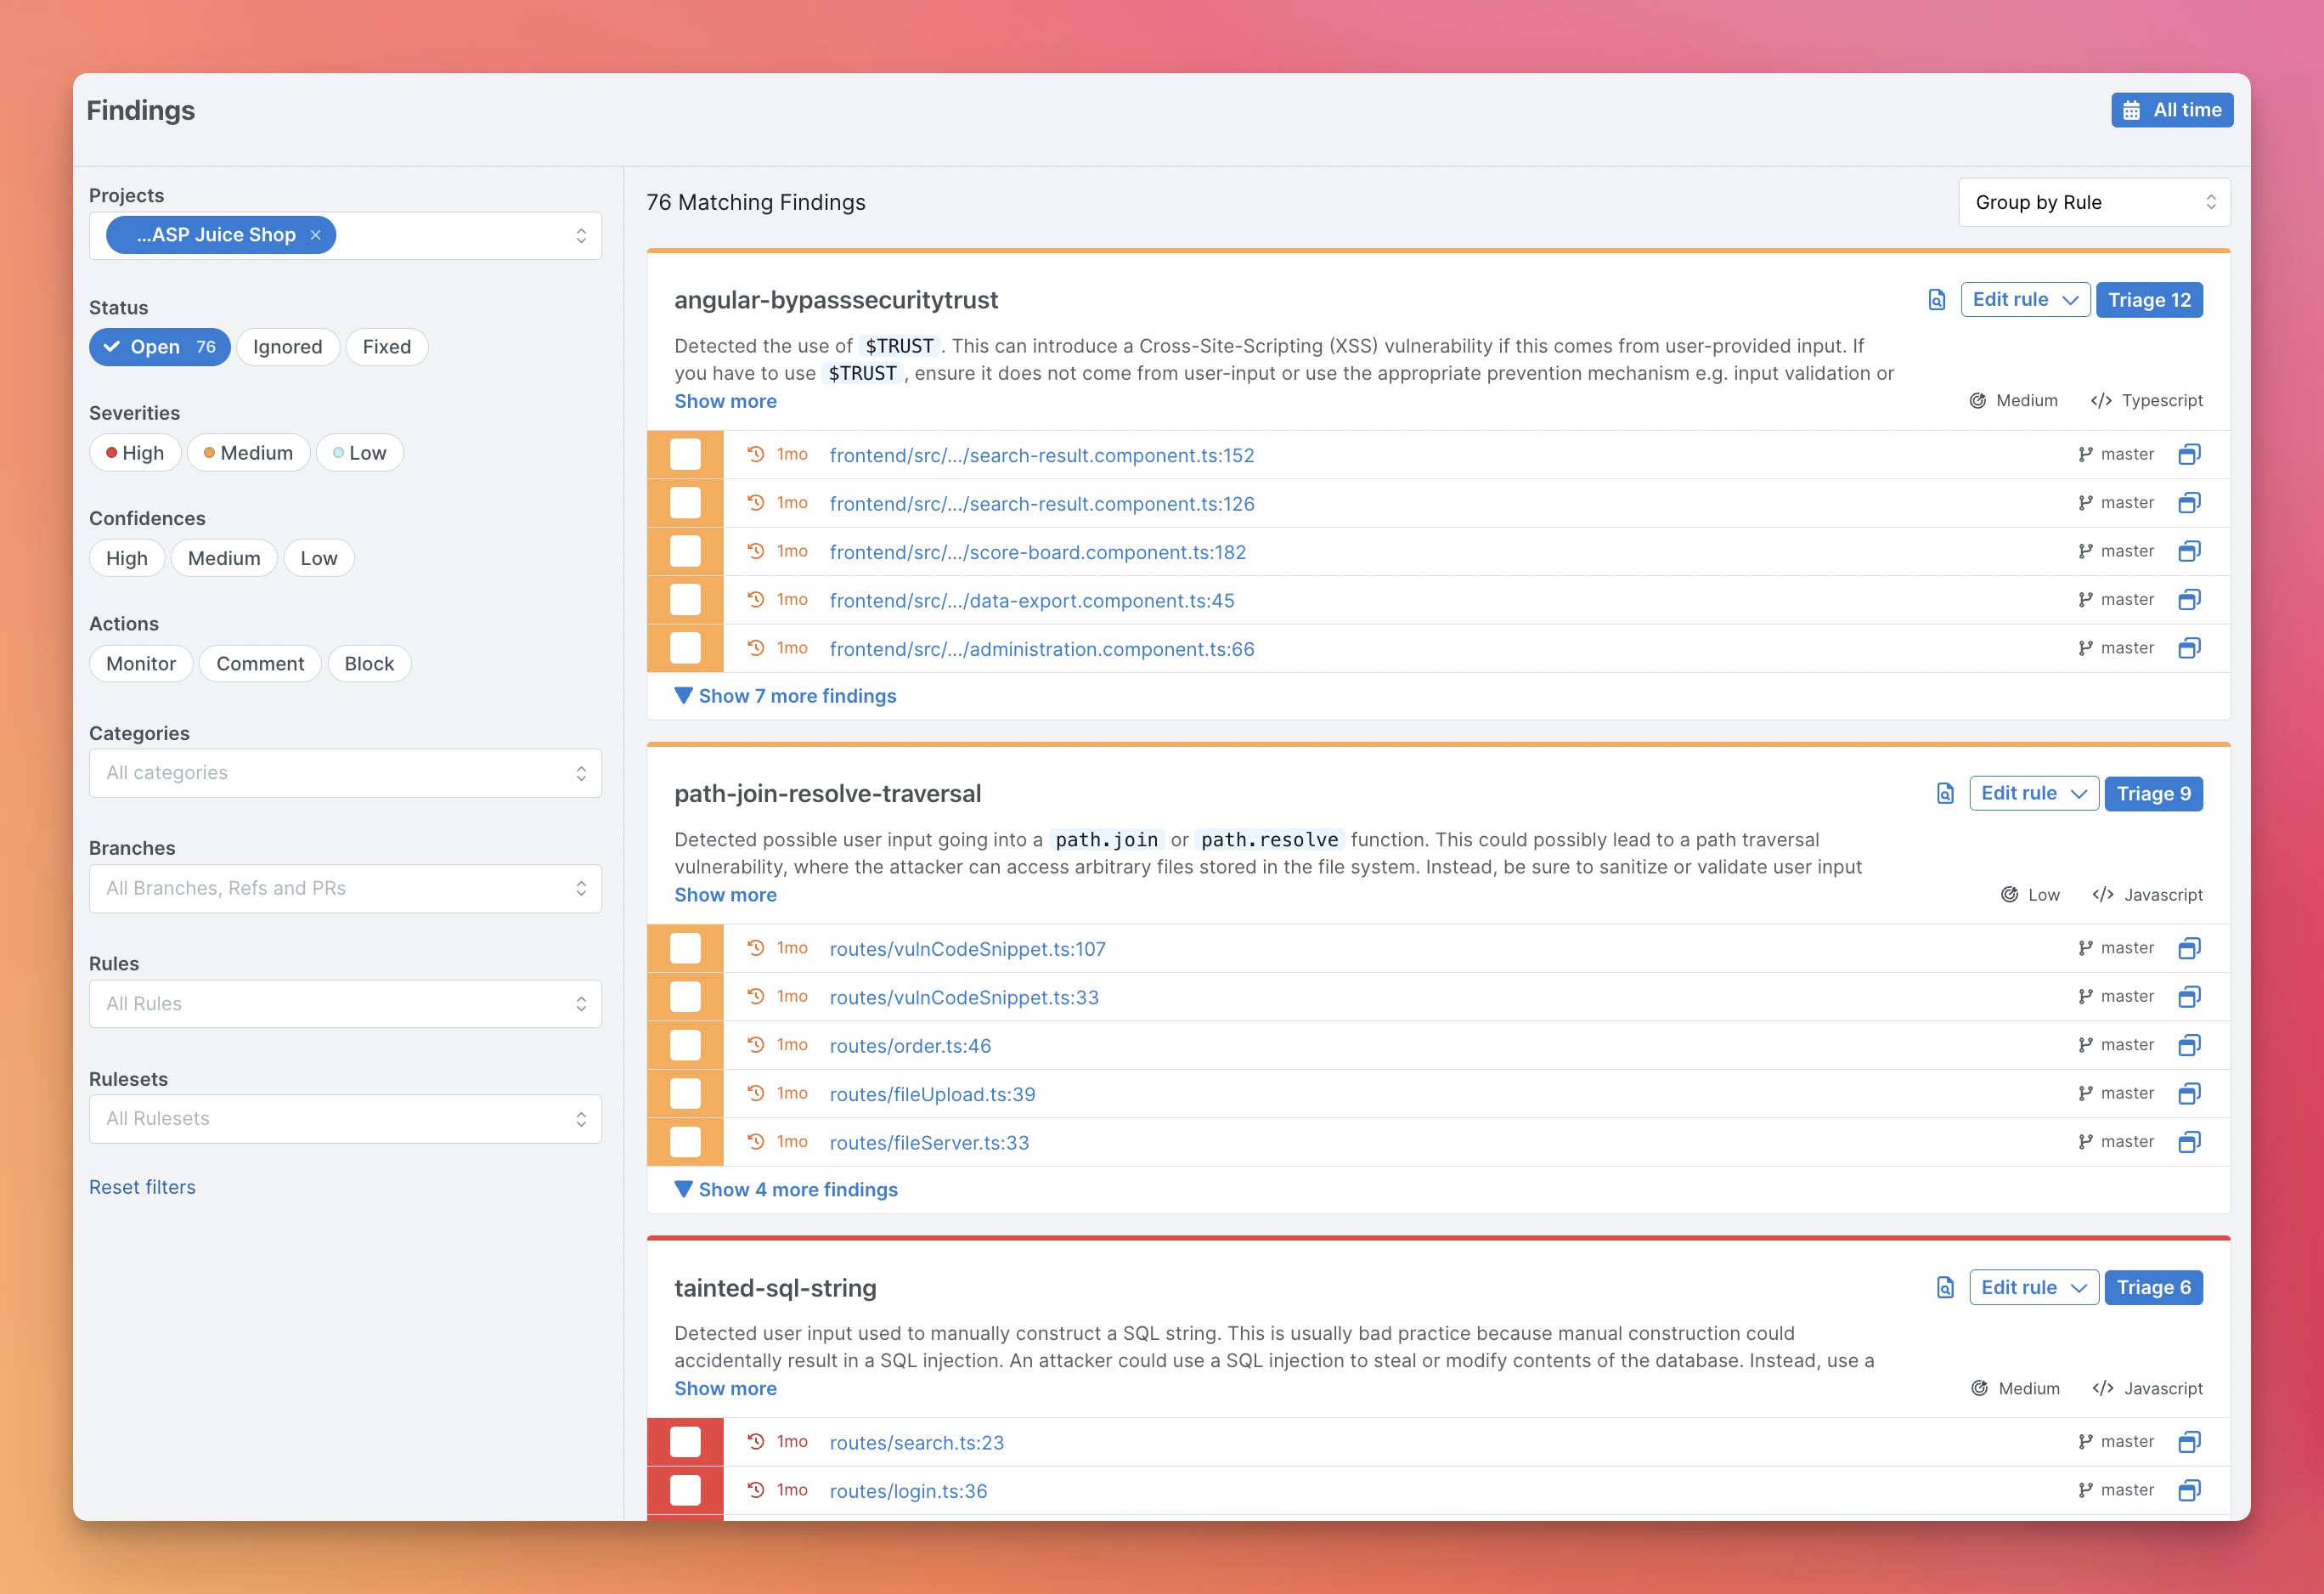
For new users, we recommend starting with the Semgrep AppSec Platform because it provides a visual interface, a demo project, result triaging and exploration workflows, and makes setup in CI/CD fast. Scans are still local and code isn't uploaded. Alternatively, you can also start with the CLI and navigate the terminal output to run one-off searches.
Option 1: Getting started from the Semgrep Appsec Platform (Recommended)
-
Register on semgrep.dev
-
Explore the demo findings to learn how Semgrep works
-
Scan your project by navigating to
Projects > Scan New Project > Run scan in CI -
Select your version control system and follow the onboarding steps to add your project. After this setup, Semgrep will scan your project after every pull request.
-
[Optional] If you want to run Semgrep locally, follow the steps in the CLI section.
Notes:
If there are any issues, please ask for help in the Semgrep Slack.
Option 2: Getting started from the CLI
-
Install Semgrep CLI
# For macOS # preferred: install through pipx (https://pipx.pypa.io/stable/how-to/install-pipx.html) pipx install semgrep # preferred: install through uv (https://docs.astral.sh/uv/getting-started/installation/) uv tool install semgrep # best-effort: install through homebrew (maintained on a best-effort basis; often lags behind the latest release) brew install semgrep # For Ubuntu/WSL/Linux/macOS $ python3 -m pip install semgrep # To try Semgrep without installation run via Docker $ docker run -it -v "${PWD}:/src" semgrep/semgrep semgrep login $ docker run -e SEMGREP_APP_TOKEN=<TOKEN> --rm -v "${PWD}:/src" semgrep/semgrep semgrep ci -
Run
semgrep loginto create your account and login to Semgrep. This step is optional, but logging into Semgrep gets you access to:- Semgrep Supply Chain: A dependency scanner that detects reachable vulnerabilities in third party libraries
- Semgrep Code's Pro rules: 600+ high confidence rules written by Semgrep's security research team
- Semgrep Code's Pro engine: An advanced code analysis engine, designed to detect complex vulnerabilities, and reduce false positives
-
Go to your app's root directory and run
semgrep ci. This will scan your project to check for vulnerabilities in your source code and its dependencies. -
Try writing your own query interactively with
-e. For example, a check for Python == where the left and right hand sides are the same (potentially a bug):$ semgrep -e '$X == $X' --lang=py path/to/src
Semgrep Ecosystem
The Semgrep ecosystem includes the following:
-
Semgrep Community Edition - The open-source program analysis engine at the heart of everything. Suitable for ad-hoc use cases with a high tolerance for false positives - think consultants, security auditors, or pentesters.
-
Semgrep AppSec Platform - Easily orchestrate and scale SAST, SCA, and Secrets scanning across an organization, with no risk of overwhelming developers. Customize which findings developers see, where they see them, and integrate with CI providers like GitHub, GitLab, CircleCI, and more. Includes both free and paid tiers.
-
Semgrep Code (SAST) - Make real progress on your vulnerability backlog with SAST that minimizes noise and empowers developers to quickly fix issues on their own, even if they have no security knowledge. Easy to deploy secure guardrails and tailored, step-by-step remediation guidance mean developers actually fix issues since they don't feel slowed down.
-
Semgrep Supply Chain (SSC) - A high-signal dependency scanner that detects reachable vulnerabilities in open source third-party libraries and functions.
-
Semgrep Secrets (Secrets scanning) - Secrets detection that uses semantic analysis, improved entropy analysis, and validation to accurately surface sensitive credentials in the developer workflow.
-
Semgrep Assistant (AI) - Assistant is an AI-powered AppSec engineer that helps both developers and AppSec teams prioritize, triage, and remediate Semgrep findings at scale. Humans agree with Assistant auto-triage decisions 97% of the time, and rate generated remediation guidance as helpful 80% of the time. For an overview of how Assistant works, read this overview.
-
-
Semgrep MCP Server - A Model Context Protocol (MCP) server that lets AI coding assistants run Semgrep scans directly. Integrates with Cursor, VS Code, Windsurf, Claude Desktop, and more. Run
semgrep mcpto start it locally.- Hooks - Automatically trigger Semgrep scans as you code.
- Skills / Prompts - Built-in MCP prompts like
write_custom_semgrep_rulehelp AI assistants write accurate Semgrep rules. - Claude Code plugin - Available on the official marketplace and via the semgrep/mcp-marketplace repo:
/plugin marketplace add semgrep/mcp-marketplace - Cursor plugin - Available on the official marketplace and via the semgrep/cursor-plugin repo.
Additional resources:
- Semgrep Playground - An online interactive tool for writing and sharing rules.
- Semgrep Registry - 2,000+ community-driven rules covering security, correctness, and dependency vulnerabilities.
Join hundreds of thousands of other developers and security engineers already using Semgrep at companies like GitLab, Dropbox, Slack, Figma, Shopify, HashiCorp, Snowflake, and Trail of Bits.
Semgrep is developed and commercially supported by Semgrep, Inc., a software security company.
Semgrep Rules
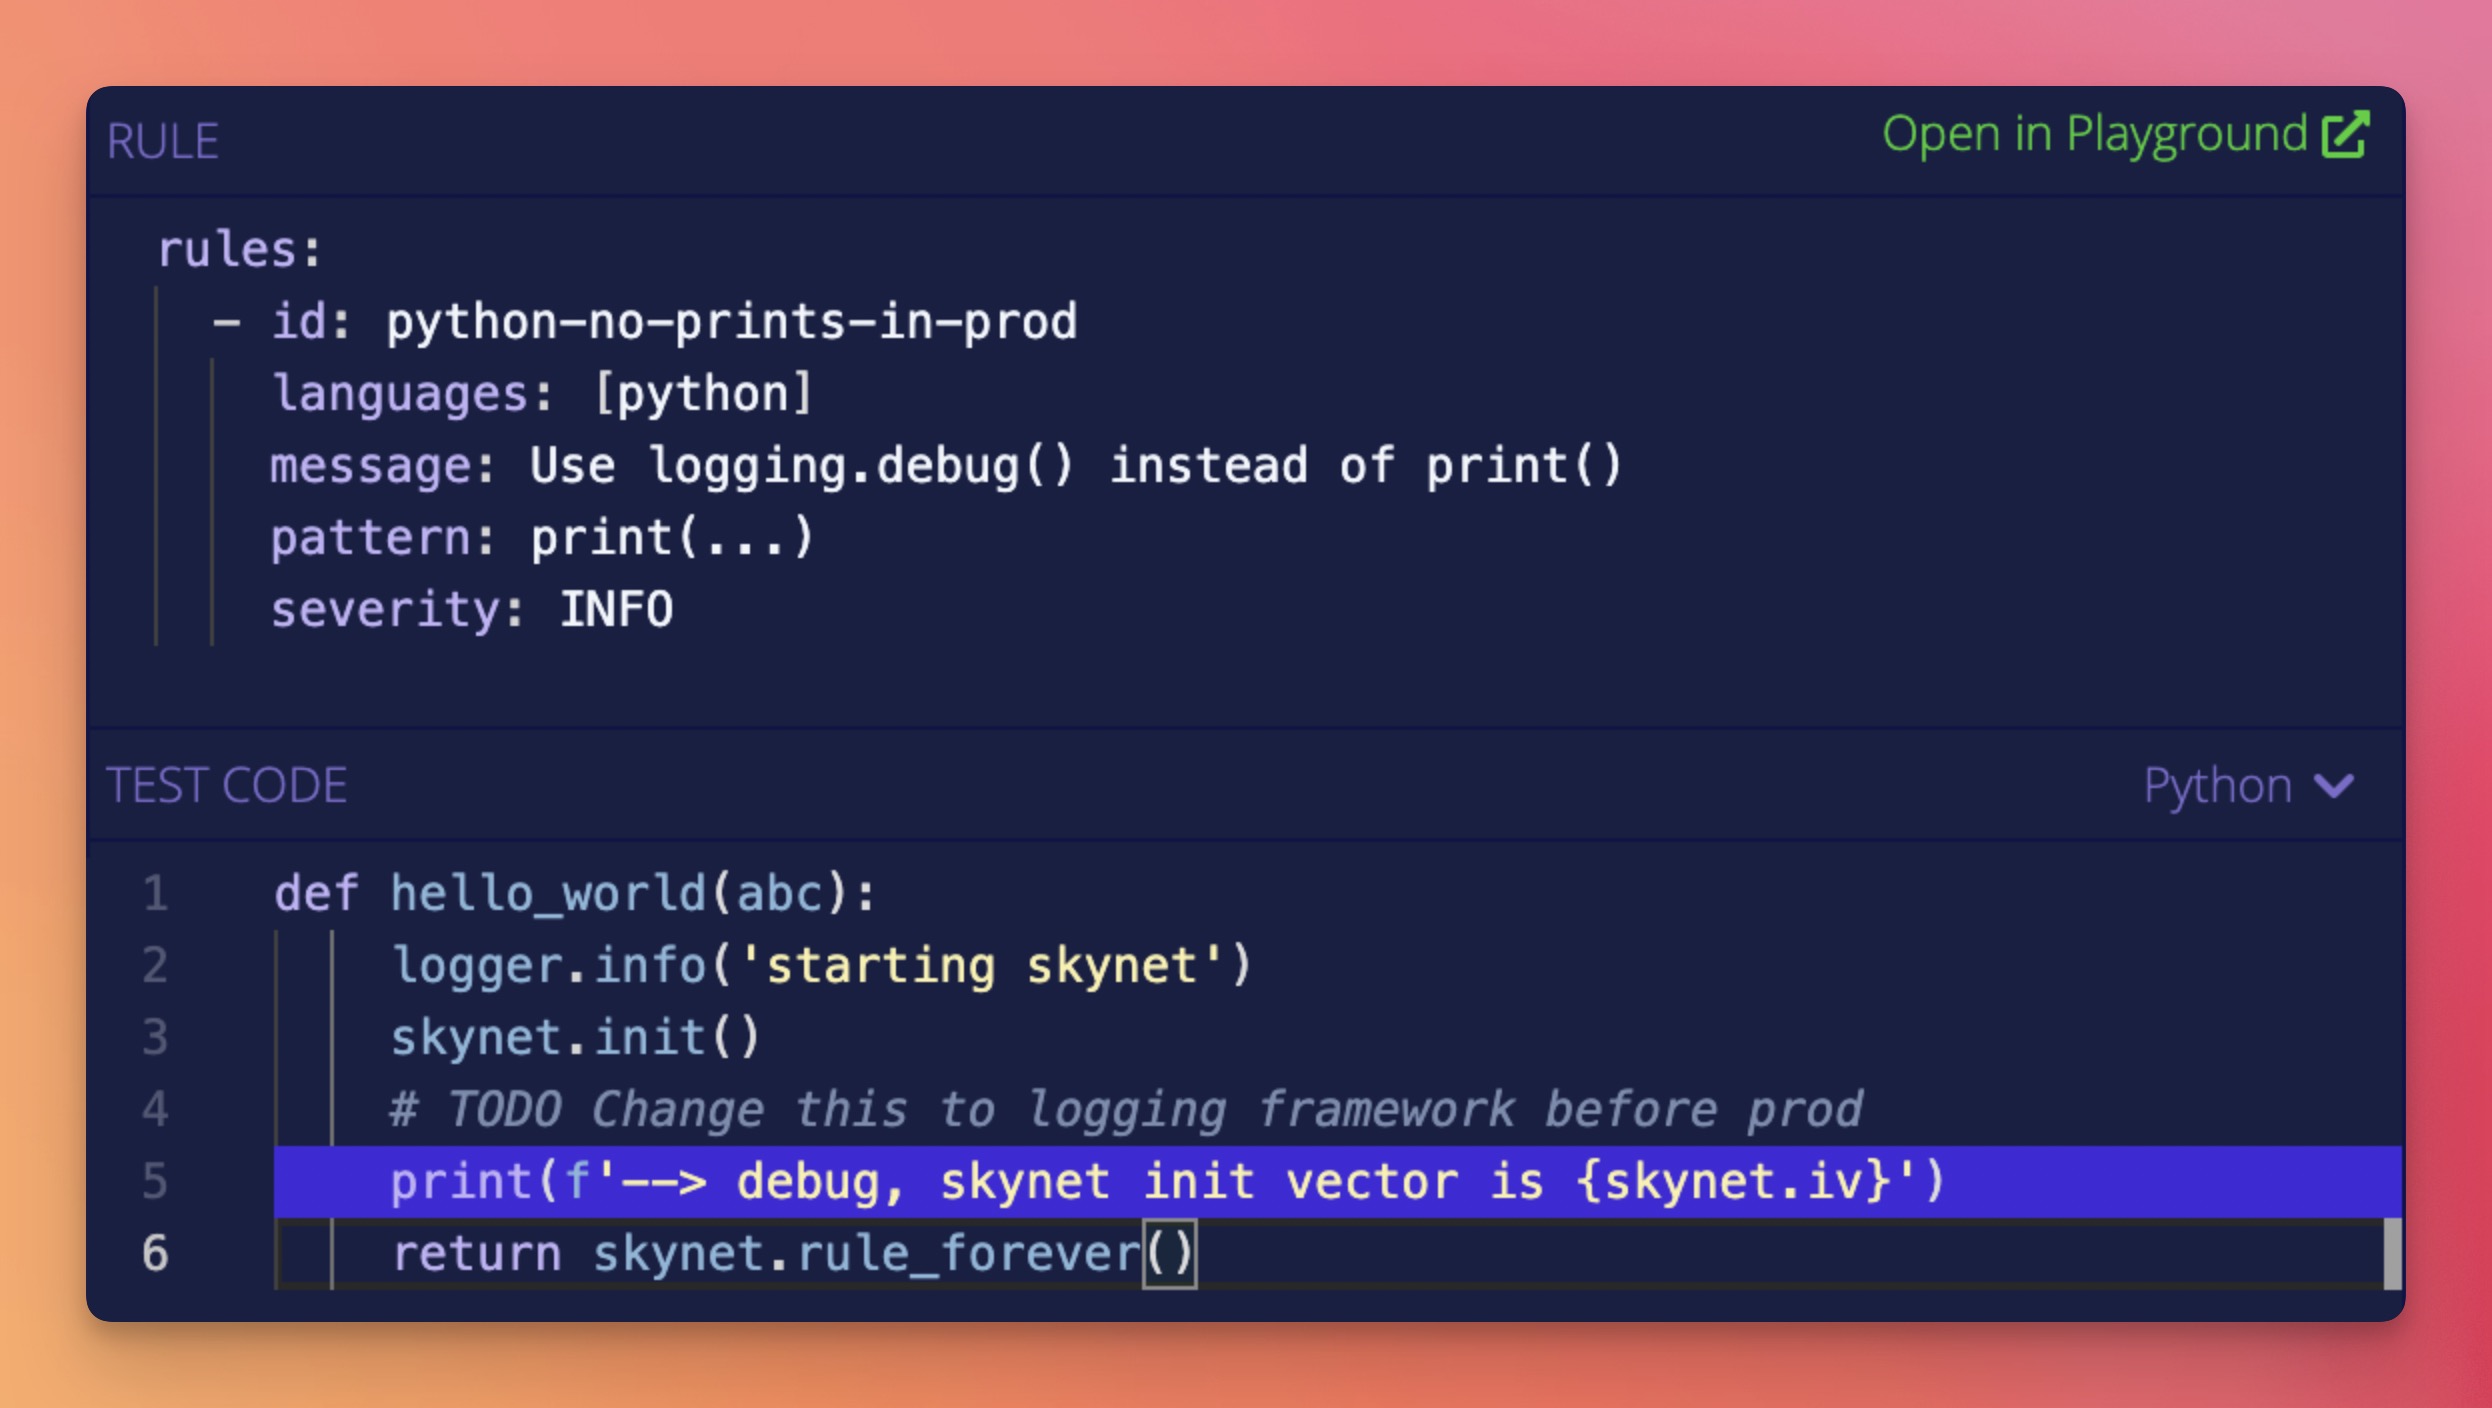
Semgrep rules look like the code you already write; no abstract syntax trees, regex wrestling, or painful DSLs. Here's a quick rule for finding Python print() statements.
Run it online in Semgrep’s Playground by clicking here.
Examples
Visit Docs > Rule examples for use cases and ideas.
| Use case | Semgrep rule |
|---|---|
| Ban dangerous APIs | Prevent use of exec |
| Search routes and authentication | Extract Spring routes |
| Enforce the use secure defaults | Securely set Flask cookies |
| Tainted data flowing into sinks | ExpressJS dataflow into sandbox.run |
| Enforce project best-practices | Use assertEqual for == checks, Always check subprocess calls |
| Codify project-specific knowledge | Verify transactions before making them |
| Audit security hotspots | Finding XSS in Apache Airflow, Hardcoded credentials |
| Audit configuration files | Find S3 ARN uses |
| Migrate from deprecated APIs | DES is deprecated, Deprecated Flask APIs, Deprecated Bokeh APIs |
| Apply automatic fixes | Use listenAndServeTLS |
Extensions
Visit Docs > Extensions to learn about using Semgrep in your editor or pre-commit. When integrated into CI and configured to scan pull requests, Semgrep will only report issues introduced by that pull request; this lets you start using Semgrep without fixing or ignoring pre-existing issues!
Documentation
Browse the full Semgrep documentation on the website. If you’re new to Semgrep, check out Docs > Getting started or the interactive tutorial.
Metrics
Using remote configuration from the Registry (like --config=p/ci) reports pseudonymous rule metrics to semgrep.dev.
When using configs from local files (like --config=xyz.yml), metrics are sent only when the user is logged in.
To disable Registry rule metrics, use --metrics=off.
The Semgrep privacy policy describes the principles that guide data-collection decisions and the breakdown of the data that are and are not collected when the metrics are enabled.
More
- Frequently asked questions (FAQs)
- Contributing
- Build instructions for developers
- Ask questions in the Semgrep community Slack
- CLI reference and exit codes
- Semgrep YouTube channel
- License (LGPL-2.1)
- Licensing Semgrep
Upgrading
To upgrade, run the command below associated with how you installed Semgrep:
# Using pipx
$ pipx upgrade semgrep

# Using uv tool command
$ uv tool upgrade semgrep

# Using Homebrew
$ brew upgrade semgrep

# Using Docker
$ docker pull semgrep/semgrep:latest


Release files for semgrep 1.184.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| semgrep-1.184.0.tar.gz | 543.0 kB | With provenance | Details for semgrep-1.184.0.tar.gz |
Built distributions (wheels)
Total release size: 418.2 MB
Release files / semgrep-1.184.0.tar.gz
| Download URL | semgrep-1.184.0.tar.gz |
|---|---|
| Size | 543.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
0fc8a58e9a62de59ce644dde792dfc36764245d0139ab85632f66a8e0846a8c5
|
|
BLAKE2b-256 checksum How to use checksums |
0c59791da93d093ef5e6fe671c43c751986ba24cfcb2a5e91958e11ef4153f84
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logRelease files / semgrep-1.184.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-win_amd64.whl
| Download URL | semgrep-1.184.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-win_amd64.whl |
|---|---|
| Size | 59.5 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
3c86b2961b4663d1338fb965de038c7869571661971b78e18e9346ab57e1e20a
|
|
BLAKE2b-256 checksum How to use checksums |
9b9b71a620f72bc6203286a4a6c031d53186863acf7d1af4f27c697ef176cbdf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logRelease files / semgrep-1.184.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_x86_64.whl
| Download URL | semgrep-1.184.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 79.0 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Linux musl 1.2+ x86-64 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 |
|
SHA-256 checksum How to use checksums |
cf82d77eb911f921902f3e9d098fb97604c5419c0a87cf7de7ab2944b05e2ceb
|
|
BLAKE2b-256 checksum How to use checksums |
b45663cd45a37ec2c292e4fc6b548a54df2f10d22948cf01672f13f652707e3e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logRelease files / semgrep-1.184.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_aarch64.whl
| Download URL | semgrep-1.184.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 81.4 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Linux musl 1.2+ ARM64 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 |
|
SHA-256 checksum How to use checksums |
42a59e95433fd05a0908f8083e25656c90994c65549e483e0de8a1a0004a7adf
|
|
BLAKE2b-256 checksum How to use checksums |
7b9d89e713d1faf9133274cc52b035986fa4dd46e36344c036a28c1fd33cf741
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logRelease files / semgrep-1.184.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_x86_64.whl
| Download URL | semgrep-1.184.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_x86_64.whl |
|---|---|
| Size | 72.3 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Linux glibc 2.34+ x86-64 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 |
|
SHA-256 checksum How to use checksums |
d847abb8fb6fdde77d9e30a6bc869dbfcb68eff4142dcd77897c52635a7600d9
|
|
BLAKE2b-256 checksum How to use checksums |
3f32d5f5f37bbfa8fee1527c749a7bfc5a1ab57f4316f98e91783721b340a35d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logRelease files / semgrep-1.184.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_aarch64.whl
| Download URL | semgrep-1.184.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_aarch64.whl |
|---|---|
| Size | 74.3 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Linux glibc 2.34+ ARM64 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 |
|
SHA-256 checksum How to use checksums |
f794d7c6d33126b6881f80d069583ef35b52bd796d882a5fa249ce1124aba3f3
|
|
BLAKE2b-256 checksum How to use checksums |
3239ac0756de46826d89e28fe06a7673a66b7f3203d2cb73740463aa113cfc98
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logRelease files / semgrep-1.184.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-macosx_11_0_arm64.whl
| Download URL | semgrep-1.184.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-macosx_11_0_arm64.whl |
|---|---|
| Size | 51.3 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
0ce3064175a44236dd9fd35603627e3f56139ac61e13ca967bae2b76b2cec9bf
|
|
BLAKE2b-256 checksum How to use checksums |
59f9fb7fd6b74cf7bdf087b4c3ef7cfcc1627df99e46c2a6805baacb8245812a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logSecurity for semgrep 1.184.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 7 files in this release have been uploaded with provenance metadata.
Attestation for semgrep-1.184.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














