
surgite
Standup summaries from Git history, in a browser or terminal.



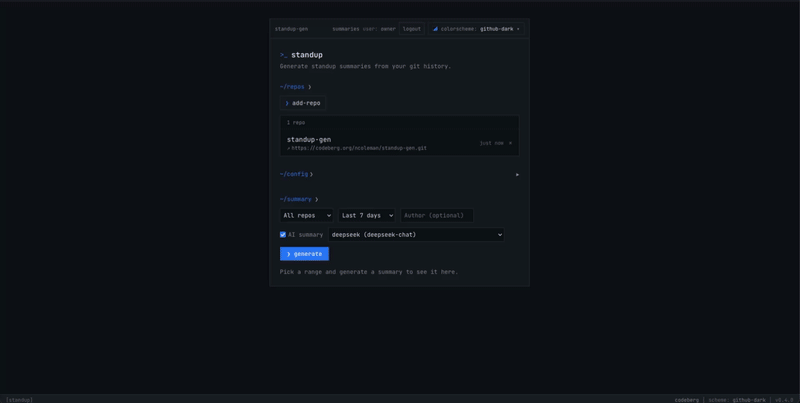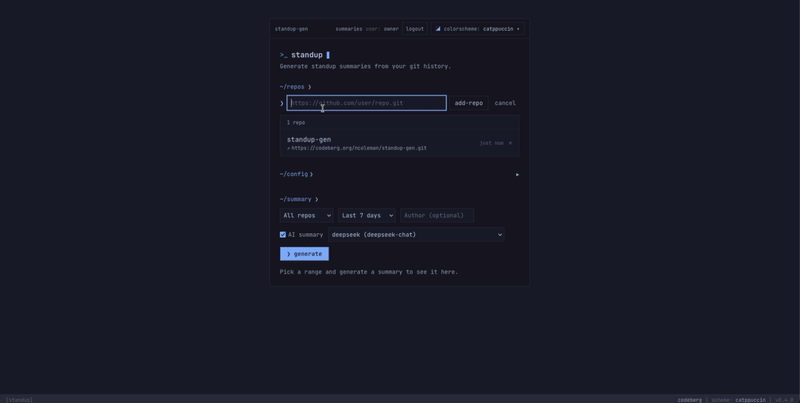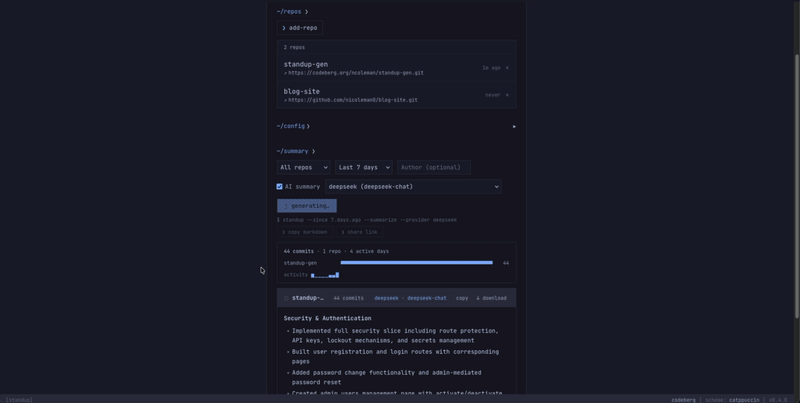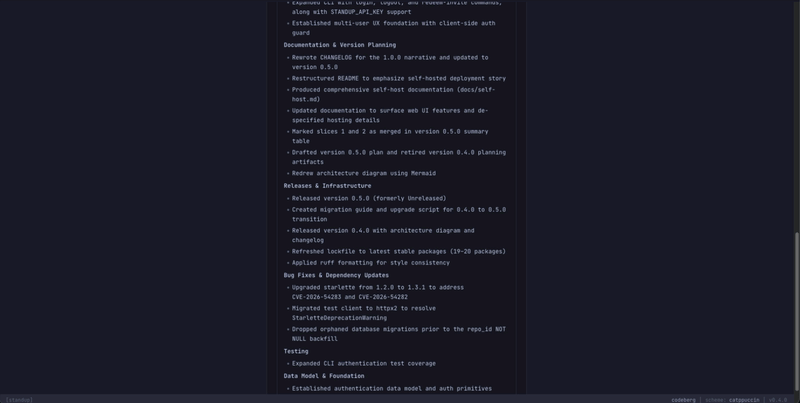
Quickstart
Workplace deployment requires Docker Compose 2.24.0 or newer and HTTPS:
git clone https://github.com/nicoleman0/surgite.git
cd surgite
cp .env.example .env
# In .env, set AUTH_MODE=multi_user and BOOTSTRAP_OWNER_EMAIL=you@work.example.
# Configure an HTTPS reverse proxy before exposing the app.
docker compose up -d
./scripts/bootstrap-admin.sh
Log in, open /admin, and create an email-pinned user invitation for each
colleague. Surgite does not email invitation links. Copy each link and share it
privately with its intended recipient.
Local CLI — no server or database:
pip install surgite
surgite /path/to/repo --since 7.days.ago
Add --summarize for an AI summary after configuring a provider key.
Personal web app — clone the repository and start Compose:
git clone https://github.com/nicoleman0/surgite.git
cd surgite
cp .env.example .env
docker compose up -d
Authentication remains off by default. The full deployment and conversion procedures are in docs/self-host.md.
Features
- Per-user repositories, prompt settings, summaries, and shared links
- Local CLI or a self-hosted FastAPI/Postgres/SvelteKit application
- Anthropic, Groq, DeepSeek, or OpenAI-compatible local models
- Email/password auth, API keys, encrypted per-user provider keys, Git connections, and audit logs
Private repositories
Add an HTTPS Git connection in Settings with a credential-free origin, username, and read-only access token. Surgite encrypts it at rest and only supplies it to Git through a non-interactive askpass helper. Never paste credentials into a repository URL.
Documentation
- Self-hosting
- Security model and security policy
- API stability policy and OpenAPI contract
- Contributing, release history, and upgrade guides
Development
uv sync --group dev
docker compose up -d db
uv run alembic upgrade head
uv run pytest
cd frontend && npm install && npm run check && npm run test
See CONTRIBUTING.md for the full workflow and AGENTS.md for architecture and project conventions.
License
MIT © 2026 Nick Coleman
1 maintainer

Metadata
1 maintainer
Release files for surgite 1.8.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| surgite-1.8.1.tar.gz | 47.0 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| surgite-1.8.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 100.9 kB
Release files / surgite-1.8.1.tar.gz
| Download URL | surgite-1.8.1.tar.gz |
|---|---|
| Size | 47.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
568ea678685a74ab2bb0bf394ee9d3e34ffbcb0b9466ada587543a003f09f64c
|
|
BLAKE2b-256 checksum How to use checksums |
7e26146ed0054e0bfb6f2b6fe2c56fe2b57b2e16899440a43799384845a0dc22
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 14, 2026.
Transparency logRelease files / surgite-1.8.1-py3-none-any.whl
| Download URL | surgite-1.8.1-py3-none-any.whl |
|---|---|
| Size | 54.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
97d529e55f08aa1cb81c55fcf826f5799317489ed318d0d95bf08aed9301e4e2
|
|
BLAKE2b-256 checksum How to use checksums |
3ac6cd9258278814768a7d47ec410da5944b47e9c9add6f3eb5e72e3a5bee540
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 14, 2026.
Transparency log













