
twitter_openapi_python
Twitter scraping with data validation by pydantic.
Setup
pip install twitter-openapi-python
Usage
import json
import datetime

from pathlib import Path
from tweepy_authlib import CookieSessionUserHandler
from twitter_openapi_python import TwitterOpenapiPython

# login by tweepy_authlib
if Path("cookie.json").exists():
    with open("cookie.json", "r") as f:
        cookies_dict = json.load(f)
        if isinstance(cookies_dict, list):
            cookies_dict = {k["name"]: k["value"] for k in cookies_dict}
else:
    auth_handler = CookieSessionUserHandler(
        screen_name=input("screen_name: "),
        password=input("password: "),
    )
    cookies_dict = auth_handler.get_cookies().get_dict()

# To extract cookies from Windows (Linux by default)
# If you use tweepy_authlib, you must be on Windows
client = TwitterOpenapiPython()
client.additional_api_headers = {
    "sec-ch-ua-platform": '"Windows"',
}
client.additional_browser_headers = {
    "sec-ch-ua-platform": '"Windows"',
}

# get client from cookies
𝕏 = client.get_client_from_cookies(cookies=cookies_dict)

# tweet "Hello World!!" with current time
time = datetime.datetime.now().strftime("%Y-%m-%dT%H:%M:%SZ")
𝕏.get_post_api().post_create_tweet(tweet_text=f"Hello World!!{time}")

# get user info
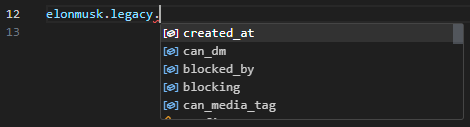
response = 𝕏.get_user_api().get_user_by_screen_name("elonmusk")
Login
from twitter_openapi_python import TwitterOpenapiPython

# guest client
𝕏 = TwitterOpenapiPython().get_guest_client()
tweet = 𝕏.get_default_api().get_tweet_result_by_rest_id("1349129669258448897")
assert tweet.data is not None
assert tweet.data.tweet.legacy is not None
print(tweet.data.tweet.legacy.full_text)
Multiple OS
The Token can only be used on the same OS that issued the Token In other words, if the sec-ch-ua-platform does not match, the Token cannot be used. This library uses the Linux Chrome header by default. To use Token issued by Windows, do the following.
client = TwitterOpenapiPython()
client.additional_api_headers = {
  "sec-ch-ua-platform": '"Windows"',
};
Development
cd twitter_openapi_python
uv sync
uv run pytest test/api
uv build
uv publish
License
This project is dual licensed. You can choose one of the following licenses:
1 maintainer

Metadata
1 maintainer
Release files for twitter-openapi-python 0.1.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| twitter_openapi_python-0.1.2.tar.gz | 31.3 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| twitter_openapi_python-0.1.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 72.0 kB
Release files / twitter_openapi_python-0.1.2.tar.gz
| Download URL | twitter_openapi_python-0.1.2.tar.gz |
|---|---|
| Size | 31.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
82d2c356b60ce3c04be5400f9f028e463406167cc8e6e9fd65610c0639102f23
|
|
BLAKE2b-256 checksum How to use checksums |
a340a72788ca058285f781ebee4b90702a6edf017472cd93eeeefa407c9e1557
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 16, 2026.
Transparency logRelease files / twitter_openapi_python-0.1.2-py3-none-any.whl
| Download URL | twitter_openapi_python-0.1.2-py3-none-any.whl |
|---|---|
| Size | 40.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
ecba0e87711fc9cc9ebfb4452f182d843ce3a90042b55712748b646bfab0b2b6
|
|
BLAKE2b-256 checksum How to use checksums |
cd8316f719e9eb28289f9823225d8e6491820d36dbd12c6b1204cad0a4084f9d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 16, 2026.
Transparency log













