
whoisport


Find out what is listening on a port, who started it, and stop it safely. Works on Linux, macOS and Windows. One small binary, no runtime dependencies.
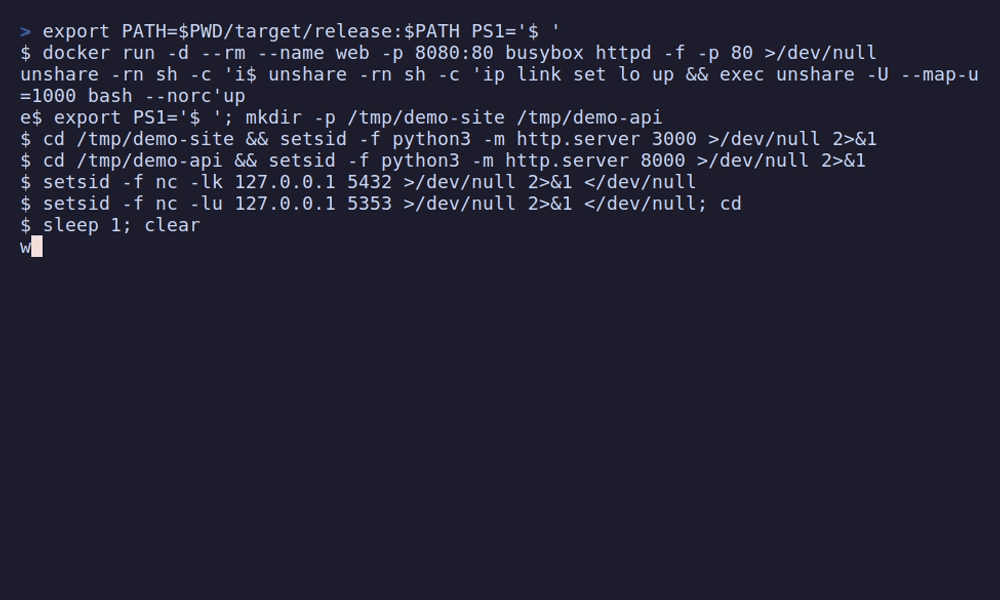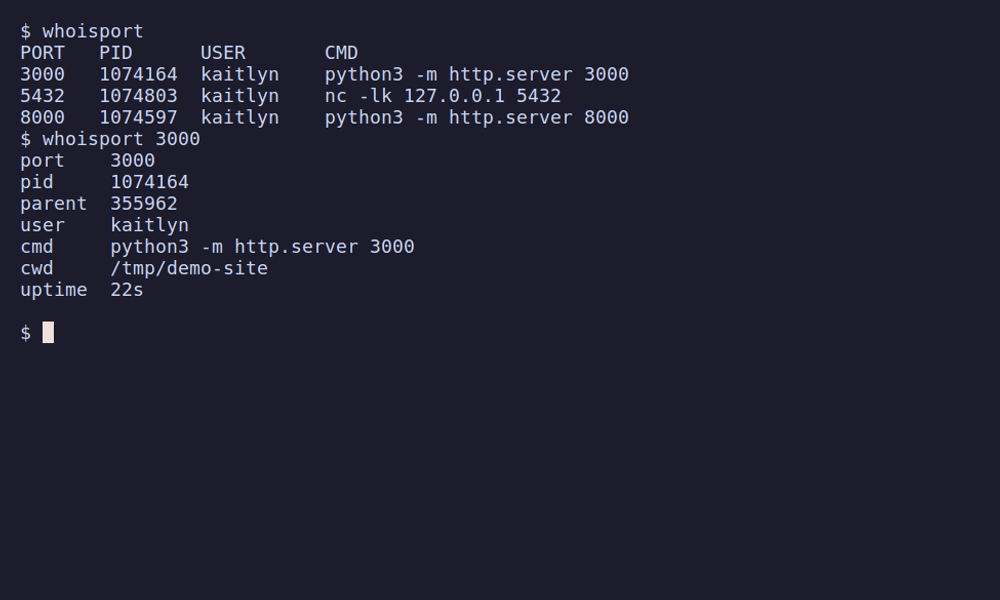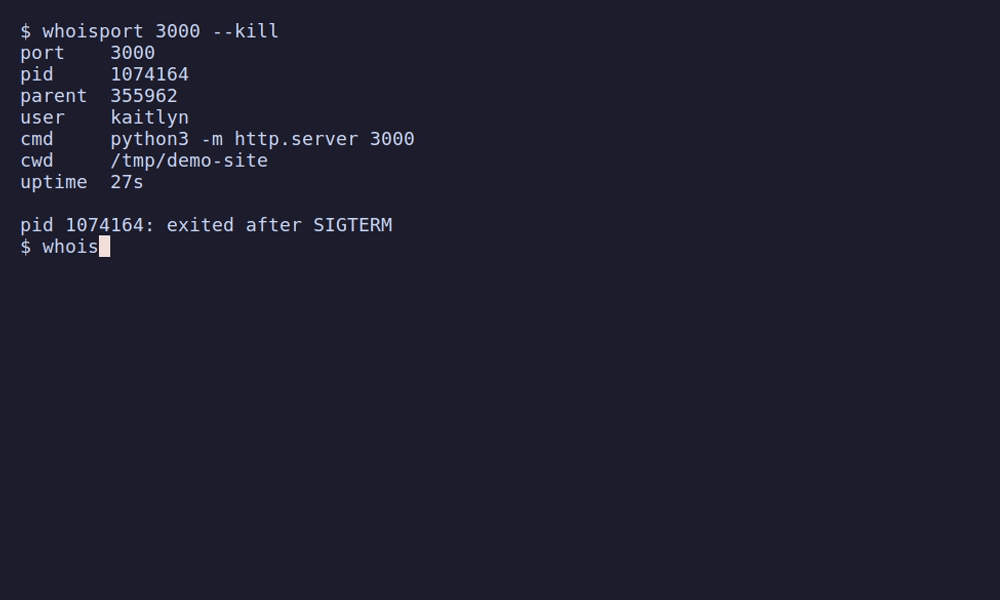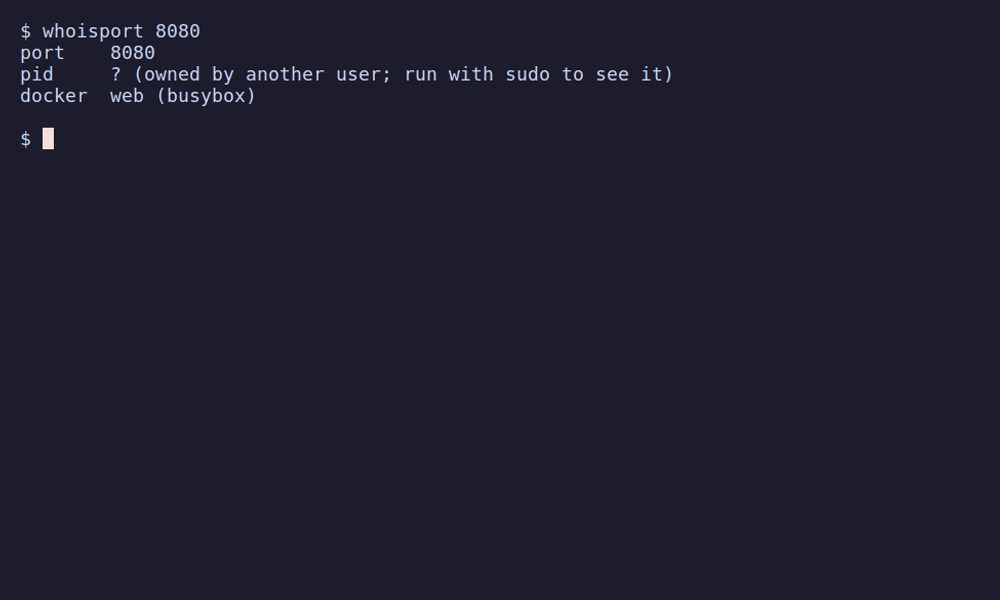
lsof -i :3000 gives you a PID and a wall of columns. whoisport gives you the command
line, the directory it was started from, who owns it and how long it has been running,
which is usually what you need to decide whether to kill it. And when you do kill it,
whoisport makes sure it only stops the process you were looking at.
Quickstart
whoisport              # what is listening on this machine?
whoisport 3000         # what is on port 3000, and who started it?
whoisport 3000 --kill  # ask it to exit (add --force if it refuses)
$ whoisport 3000
port    3000
pid     373232
parent  373230
user    kaitlyn
cmd     node node_modules/.bin/vite --port 3000
cwd     /home/kaitlyn/site
uptime  4m 12s

$ whoisport 3000 --kill
...
pid 373232: exited after SIGTERM

$ whoisport
PORT   PID      USER       CMD
3000   373232   kaitlyn    node node_modules/.bin/vite --port 3000
5432   ?        ?          ?
8080   41120    kaitlyn    python3 -m http.server 8080
ports marked ? are owned by another user; run with sudo to see it
Install
| Platform | Command |
|---|---|
| Any, with Rust | cargo binstall whoisport (prebuilt) or cargo install whoisport (builds from source) |
| Any, with Python | pipx install whoisport or uvx whoisport |
| macOS, Linux | brew install dpologdvinity/tap/whoisport |
| Windows | scoop bucket add whoisport https://github.com/dpologdvinity/scoop-whoisport then scoop install whoisport |
| Debian, Ubuntu | download the .deb from Releases, then sudo apt install ./whoisport_*.deb |
| Fedora, RHEL | download the .rpm from Releases, then sudo dnf install ./whoisport-*.rpm |
Or download a binary from the Releases page: Linux (static, x86_64 and aarch64), macOS (Apple silicon and Intel) and Windows (x86_64).
Supported systems: Linux (reads /proc, no other tools needed), macOS (uses the
built-in lsof), Windows 10 and 11.
Usage
whoisport [PORTS]... [--kill [--force]] [--json] [--udp]
| You type | You get |
|---|---|
whoisport |
A table of every listening port |
whoisport 3000 8080 |
Details of what is on each port (repeated ports are shown once) |
whoisport 3000 --kill |
The details, then the process is asked to exit and given 3 seconds |
whoisport 3000 --kill --force |
Same, but forcibly ended if it does not exit |
whoisport --json |
The same data as a JSON array, for scripts |
whoisport --udp |
UDP sockets instead of TCP |
--kill always needs explicit ports; it never means "kill everything". --json cannot
be combined with --kill.
JSON output
--json prints an array with one object per listener. Every object has the same keys;
what is unknown (for example the owner of a process you may not inspect) is null:
[
  {
    "port": 3000, "proto": "tcp", "pid": 373232, "ppid": 373230, "user": "kaitlyn",
    "cmd": "node node_modules/.bin/vite --port 3000", "cwd": "/home/kaitlyn/site",
    "uptime_secs": 252, "container": null, "image": null
  }
]
Exit codes
| Code | Meaning |
|---|---|
0 |
Success: everything asked for was found (and killed, if asked) |
1 |
A requested port has nothing listening, or nothing is listening at all |
2 |
Invalid arguments |
3 |
A kill failed, or a process holding the port was deliberately not killed (see below), so the port may still be in use |
Reading ?
On Linux, a process owned by another user cannot be inspected without sudo, so its row
shows ?. On macOS lsof only lists your own processes without sudo, so other
users' listeners are missing. On Windows, details of system services need an elevated
terminal.
Stopping processes safely
--kill is built so that it cannot take down more than you meant to:
- The process you saw is the process that is signalled. Each target is identified by its pid and its start time. If it exits and the system hands its pid to something else, that something else is left alone.
- Service managers and parents are never signalled. When several processes share a
socket (a supervisor and its workers, or
systemdsocket activation), stopping the supervisor takes down far more than one port.systemd,launchdandsvchost.exe, and any process that is a parent of another holder, are skipped. whoisport then says which one still holds the port and exits3. - It asks first. Each target is asked to exit; it is forced only with
--force.
| Platform | --kill asks by |
--force |
|---|---|---|
| Linux, macOS | SIGTERM |
SIGKILL |
| Windows | Ctrl+C in the process's console, and WM_CLOSE to its windows |
TerminateProcess |
On Windows, Ctrl+C reaches every program attached to a console, so whoisport only sends
it when the target's console holds nothing but the target, its child processes and a
shell. Otherwise it says so and leaves the choice of --force to you.
Text from other processes (command lines, paths) is printed with control characters, bidirectional-text overrides and zero-width characters escaped, so a hostile process cannot rewrite your terminal or disguise what it is.
Docker
When a port is published by a container, whoisport shows the container name and image
(docker web (nginx:alpine)), even though the docker-proxy process behind it is owned
by root. Docker is consulted only when a listener looks like Docker's forwarder or its
owner cannot be read, only for a local daemon (not an ssh:// or remote DOCKER_HOST),
and each Docker call is cut off after 2 seconds, so a stuck daemon never hangs
whoisport: the names are simply left out. --kill on such a port prints the matching
docker stop <name> command, because killing the forwarder only breaks the port mapping.
UDP
UDP has no listening state, so --udp lists bound sockets that have no remote peer.
Windows does not report UDP peers, so there every bound UDP socket is listed, including
short-lived client ones.
How it works
A short version (the long one is in ARCHITECTURE.md): whoisport asks
the operating system which sockets are listening and which process owns each one, looks
up details of those processes, and prints them. Each platform has its own small backend
for that (/proc on Linux, lsof on macOS, the IP Helper API on Windows); everything
else is shared.
cli ─► scan ─► output     (list, details, JSON)
         │
         └───► kill       (identity, safety rules, ask-then-force)
         ▲
   proc backend per OS · docker names
Development
cargo test                 # unit and end-to-end tests
cargo clippy --all-targets -- -D warnings
See CONTRIBUTING.md for the full workflow (formatting, coverage, checking the other platforms, commit style) and ARCHITECTURE.md for how the code is organised.
License
1 maintainer

Metadata
1 maintainer
Release files for whoisport 0.5.7
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| whoisport-0.5.7.tar.gz | 52.6 kB | With provenance | Details |
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| whoisport-0.5.7-py3-none-win_amd64.whl | Python 3 | none | Windows x86-64 | Details |
| whoisport-0.5.7-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.whl | Python 3 | none | Linux glibc 2.17+ x86-64 | Details |
| whoisport-0.5.7-py3-none-manylinux_2_17_aarch64.manylinux2014_aarch64.whl | Python 3 | none | Linux glibc 2.17+ ARM64 | Details |
| whoisport-0.5.7-py3-none-macosx_11_0_arm64.whl | Python 3 | none | macOS 11.0+ ARM64 | Details |
| whoisport-0.5.7-py3-none-macosx_10_12_x86_64.whl | Python 3 | none | macOS 10.12+ x86-64 | Details |
Total release size: 2.0 MB
Release files / whoisport-0.5.7.tar.gz
| Download URL | whoisport-0.5.7.tar.gz |
|---|---|
| Size | 52.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
31560f21fcc20c12ab4f07531e5818764d1a90c7c9f9d4afe490b295be540f37
|
|
BLAKE2b-256 checksum How to use checksums |
29f9664282e0f4b6b8c1d55fcceb0de1cb3df010c1faee5e5c1dca9291c359b2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / whoisport-0.5.7-py3-none-win_amd64.whl
| Download URL | whoisport-0.5.7-py3-none-win_amd64.whl |
|---|---|
| Size | 396.1 kB |
| Tags | Python 3 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
4924ccd50edcebbcaf37197bd793d4bd0f5ca6efbebb508004787707c234d832
|
|
BLAKE2b-256 checksum How to use checksums |
df870fe42cfa8d0740cb41f0ef97c53a17360910b0911e6d6f9385a8373a8e57
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / whoisport-0.5.7-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | whoisport-0.5.7-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 414.3 kB |
| Tags | Linux glibc 2.17+ x86-64 Python 3 |
|
SHA-256 checksum How to use checksums |
7d55912358107ea0ba98cab3fb6cfc0d0f035433ea846f9a5b0622894a2863f3
|
|
BLAKE2b-256 checksum How to use checksums |
322e6ef61084e8c98f2ad155ca979bd4eea7b6009ee1cdb4013ad2e56175b224
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / whoisport-0.5.7-py3-none-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | whoisport-0.5.7-py3-none-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 394.0 kB |
| Tags | Linux glibc 2.17+ ARM64 Python 3 |
|
SHA-256 checksum How to use checksums |
81b779c1990031c2065f9b9faaa103c8fcf84adf632a32c53f7e06a8c42f2dbb
|
|
BLAKE2b-256 checksum How to use checksums |
efdb63a70dc96b0ea8992ffb6ae3ca01f47c6685d1043d919d7e6a7c579c223c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / whoisport-0.5.7-py3-none-macosx_11_0_arm64.whl
| Download URL | whoisport-0.5.7-py3-none-macosx_11_0_arm64.whl |
|---|---|
| Size | 365.5 kB |
| Tags | Python 3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
1b11bfe082dc7a0cc94d7c60e5fff47b3af4f30703af0230786605c98eae5bdf
|
|
BLAKE2b-256 checksum How to use checksums |
6fb1da2475611a6fe506c8e460b9493047517fe43bc18f8c8c374b908f3a4746
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / whoisport-0.5.7-py3-none-macosx_10_12_x86_64.whl
| Download URL | whoisport-0.5.7-py3-none-macosx_10_12_x86_64.whl |
|---|---|
| Size | 393.5 kB |
| Tags | Python 3 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
3b680f0ba029b0a5d44692896c9d84de8af82d98243f5cf1b0c78c51d1ba4890
|
|
BLAKE2b-256 checksum How to use checksums |
d17a9a58140f15d669908d562e1b663ba53d2629b93d661212c5dac397b4fbad
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logSecurity for whoisport 0.5.7
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 6 files in this release have been uploaded with provenance metadata.
Attestation for whoisport-0.5.7.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














