
A11
Build AI applications like normal software.
A11 is the open-source runtime for connecting models, tools and interfaces while keeping your architecture. It gives ordinary asynchronous code named streams, concurrency, tools and local-to-remote execution, and exposes the running application to Studio.
The Python API runs on a native C++20 runtime. TypeScript, Kotlin, C++ and Flow use the same action boundary where an application needs another language or process.
- Named streams instead of mixed provider events. Read model text, reasoning, tool activity, progress, and durable interaction state from separate ports.
- The same action contract locally and remotely. Move a handler to a GPU host, browser, or service without changing its inputs and outputs.
- Deterministic runtime composition with Flow. Check and load compositions at runtime with defined concurrency, draining, deadlines, cancellation, and error propagation.
Run the first action · Try the live research agent · Read the documentation · Star A11
Try A11 live
The hosted parallel research agent plans a topic, searches the web for each brief, reviews the returned evidence concurrently, and streams a cited report to the browser. Its default model and search backends need no visitor account or API key.
Run your first streaming action
Install the core runtime on Python 3.11 or later:
python -m venv .venv
source .venv/bin/activate
pip install a11-kit
Save this as quickstart.py. The function signature becomes an action schema,
and its asynchronous iterator becomes a named streaming output:
import asyncio
from collections.abc import AsyncIterator

import a11


REGISTRY = a11.ActionRegistry()


@REGISTRY.action(name="split-words", output="words")
async def split_words(text: str) -> AsyncIterator[str]:
    """Emit the words in a line as they become available."""
    for word in text.split():
        yield word


async def main() -> None:
    action = REGISTRY.make_action("split-words")
    await action["text"].finalize("named streams arrive early")
    action.run()

    async for word in action["words"]:
        print(word)
    await action.wait()


asyncio.run(main())
Run it:
python quickstart.py
The output port streams four values and then closes successfully. The same
REGISTRY can be served over WebSocket, HTTP SSE, or WebRTC; callers still use
the text and words ports.
Add model providers when the application needs them. With Ollama already running locally:
pip install "a11-kit[llm]"
a11 chat --provider ollama --no-voice --no-shell-tools
a11 chat reuses a gateway at the default endpoint, or starts one for the
duration of the chat with the current directory as its coding workspace.
--cwd PATH selects another workspace for a new gateway. An explicit
--gateway URL must be reachable.
In a coding chat, /sandbox unrestricted grants host filesystem access and
disables kernel process confinement. /sandbox workspace-write or
/sandbox read-only restores confinement. Approval remains a separate setting
(/approval suggest|auto). Sandbox changes affect subsequent tool calls for
all clients of that gateway, not already-running processes.
Studio and IDE clients can call the UI-only configure_coding_agent action
with sandbox_mode (read-only, workspace-write, or unrestricted) and/or
approval_mode (suggest or auto). Omitted fields keep their current values;
the result contains approval_mode, sandbox_ceiling, and network. This
control is excluded from the coding agent's model-facing action list.
Input questions appear above the TUI composer. Use Up/Down to select and Enter
to answer, or type a response when free text is allowed. An output-area status
line shows Working during model calls and Waiting for input while a
question is pending.
Add capabilities incrementally
Streaming. An asynchronous iterator yields values before it finishes. Named outputs give model text, reasoning, progress and structured values their own interfaces. The caller reads those streams and checks the action's final status separately.
Concurrency. Use ordinary Python tasks or C++ runtime primitives for independent work. Use nested A11 actions when the runtime should understand a parent/child relationship and propagate cancellation.
Tools. Expose registered actions to model calls through the SDK, or serve the same registry through MCP. The application still owns validation, authorization and policy.
Remote execution. Serve a registry from another process or machine. The caller configures a connection and calls the action; the handler's input and output contract stays stable.
Flow is available when an application needs a composition expressed as data. It is optional: model APIs, MCP, LangGraph and existing application code can remain part of the stack.
Inspect the work with Studio
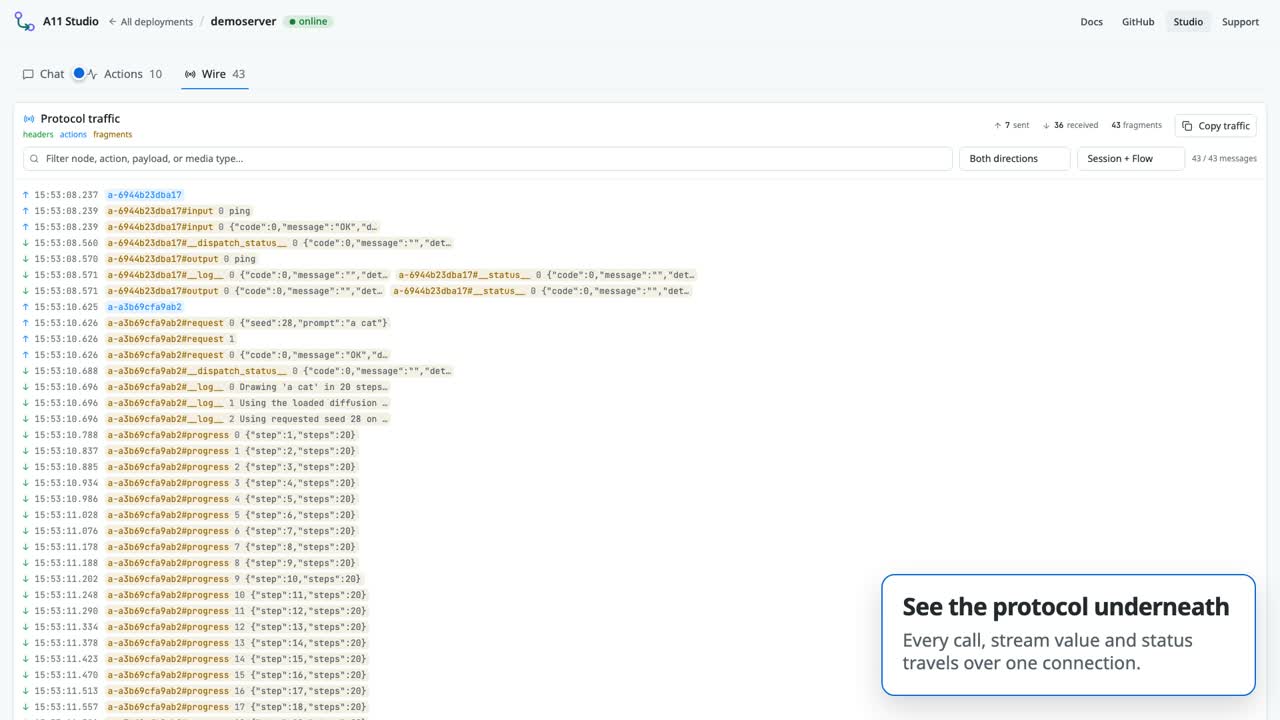
Open Studio to explore an endpoint's action schemas, run calls and inspect streamed outputs, logs, timings, failures and cancellation.
Explore complete applications
- Deep research plans a topic, searches the web in parallel and streams a cited synthesis.
- Model interactions present one streaming interface across Claude, Gemini, Ollama and OpenAI-compatible providers.
- The
a11 chat --voice-model ...path keeps audio capture, transcription and model interaction on separate streams. - Generative media streams progress independently from generated image bytes.
- Browser tools let a model call typed actions implemented inside an existing page.
Each guide names its provider, model and hardware prerequisites. Local actions and remote transports do not require a model.
Install only what the application needs
The Python distribution is a11-kit, imported as a11. Provider integrations
are optional extras such as a11-kit[ollama], a11-kit[claude] and
a11-kit[openai]. Browser and TypeScript applications use:
npm install @curiositystack/a11
The standalone C++20 runtime needs no Python installation. Build and link it through its exported CMake targets using the instructions below.
Go deeper
- Build a parallel research agent in Python.
- Stream one model interface across Claude, Gemini, and Ollama.
- Turn an application action into an LLM tool.
- Move a local action behind a remote service.
- Compose allowed actions safely at runtime.
Questions and rough edges are useful project signals: start a discussion, report friction, or tell us about an integration.
Building the C++ runtime
A11's runtime is a standalone C++20 library you can build and link without Python. The steps below are self-contained; for the editable Python build, wheel matrix, testing workflow, and architecture, see BUILDING.md.
1. Install the tools, then build the C++ libraries. A11 links a pinned set
of statically-built libraries (Boost, OpenSSL, libcurl, nghttp2, hiredis,
nlohmann-json, uvw) rather than system copies; scripts/bootstrap_wheel_deps.sh builds them
into a per-architecture prefix. From Homebrew you install only the tools (a C++20
compiler, CMake ≥ 3.28, Ninja; Linux tool package names vary):
brew install cmake googletest ninja pkg-config

export A11_DEPS_PREFIX="$HOME/.cache/a11-deps/$(uname -m)"
export CMAKE_PREFIX_PATH="$A11_DEPS_PREFIX"
export OPENSSL_ROOT_DIR="$A11_DEPS_PREFIX"
export PKG_CONFIG_PATH="$A11_DEPS_PREFIX/lib/pkgconfig"
export MACOSX_DEPLOYMENT_TARGET=14.4   # macOS only
scripts/bootstrap_wheel_deps.sh
CMake still fetches the pinned Abseil (and libdatachannel, for WebRTC) automatically. See BUILDING.md for the full rundown.
2. Configure, build, and install to a prefix (the exports above point CMake at the dependency prefix):
cmake -S . -B build -G Ninja \
  -DCMAKE_BUILD_TYPE=Release \
  -DA11_BUILD_PYTHON=OFF \
  -DCMAKE_OSX_DEPLOYMENT_TARGET=14.4 \
  -DCMAKE_INSTALL_PREFIX="$PWD/install"

cmake --build build -j
cmake --install build
On macOS, pass -DCMAKE_OSX_DEPLOYMENT_TARGET=14.4 as shown — it must match the
value the prefix was bootstrapped with. Setting it as a cache variable here (not
only via the MACOSX_DEPLOYMENT_TARGET environment export, which CMake may not
pick up) is what enables the Boost.Fiber futex spinlock; a lower target compiles
Boost.Fiber without futex support and fails with
"futex not supported on this platform". The flag is ignored on Linux.
3. Use it from your own CMake project. The install exports a CMake package
named a11 with per-component targets (a11::service links the whole runtime).
Point your consumer's CMAKE_PREFIX_PATH at both the install prefix and the
dependency prefix from step 1, so the transitive static Boost/OpenSSL/... resolve:
find_package(a11 CONFIG REQUIRED)

add_executable(my_agent main.cc)
target_link_libraries(my_agent PRIVATE a11::service)
target_compile_features(my_agent PRIVATE cxx_std_20)
#include <cstddef>
#include <iostream>
#include <memory>
#include <optional>
#include <string>
#include <vector>

#include <absl/log/log.h>
#include <absl/status/status.h>
#include <absl/status/status_macros.h>
#include <absl/strings/str_split.h>

#include "a11/actions/registry.h"
#include "a11/nodes/async_node.h"

namespace {

using a11::actions::Action;
using a11::actions::ActionPortSchema;
using a11::actions::ActionRegistry;
using a11::actions::ActionSchema;
using a11::nodes::AsyncNode;

ActionSchema SplitWordsSchema() {
  return ActionSchema{
      .name = "split-words",
      .inputs = {{"text", ActionPortSchema{
                             .name = "text", .type = "text/plain"}}},
      .outputs = {{"words", ActionPortSchema{
                               .name = "words", .type = "text/plain"}}},
  };
}

absl::Status SplitWords(std::shared_ptr<Action> action) {
  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> input,
                        action->GetInput("text"));
  ABSL_ASSIGN_OR_RETURN(
      std::optional<std::string> text,
      input->NextObject<std::string>().Await());
  if (!text.has_value()) {
    return absl::FailedPreconditionError("text input ended before a value");
  }

  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> output,
                        action->GetOutput("words"));
  std::vector<std::string> words =
      absl::StrSplit(*text, absl::ByAnyChar(" \t\n"), absl::SkipWhitespace());
  if (words.empty()) {
    return output->Finalize({.wait = true}).Await().status();
  }
  for (size_t index = 0; index + 1 < words.size(); ++index) {
    ABSL_RETURN_IF_ERROR(output->Put(words[index]).Await().status());
  }
  return output->Finalize(words.back(), {.wait = true}).Await().status();
}

absl::Status RunExample() {
  auto registry = std::make_shared<ActionRegistry>();
  ABSL_RETURN_IF_ERROR(registry->RegisterSync(
      "split-words", SplitWordsSchema(), SplitWords));
  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<Action> action,
                        registry->MakeAction("split-words"));

  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> input,
                        action->GetInput("text"));
  ABSL_RETURN_IF_ERROR(
      input->Finalize(std::string("named streams arrive early"),
                      {.wait = true})
          .Await()
          .status());
  ABSL_RETURN_IF_ERROR(action->Run().status());

  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> output,
                        action->GetOutput("words"));
  while (true) {
    ABSL_ASSIGN_OR_RETURN(std::optional<std::string> word,
                          output->NextObject<std::string>().Await());
    if (!word.has_value()) break;
    std::cout << *word << '\n';
  }
  return action->Wait().Await().status();
}

}  // namespace

int main() {
  const absl::Status status = RunExample();
  if (!status.ok()) {
    LOG(ERROR) << status;
    return 1;
  }
  return 0;
}
This is the same split-words action as the Python quickstart: the registry
owns its schema and handler, the input carries one complete value, and the
output emits words as a stream. Reading the output before Wait() drains it
while the handler is running and preserves backpressure.
Configure your project with -DCMAKE_PREFIX_PATH=/path/to/install so
find_package locates it. The generated C++ API reference is published
alongside the docs.
1 maintainer

Metadata
1 maintainer
Release files for a11-kit 0.7.25
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| a11_kit-0.7.25.tar.gz | 3.1 MB | With provenance | Details for a11_kit-0.7.25.tar.gz |
Built distributions (wheels)
Total release size: 158.7 MB
Release files / a11_kit-0.7.25.tar.gz
| Download URL | a11_kit-0.7.25.tar.gz |
|---|---|
| Size | 3.1 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
b5c1c895fa1694b100dd0ba7a03fff94a4e14609a6950c3c9ebac56fbe3ebfa6
|
|
BLAKE2b-256 checksum How to use checksums |
252576b0377940f135c251f5d7056b1d3bccfaada86ce63e92a1f01068be771a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / a11_kit-0.7.25-cp314-cp314-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.25-cp314-cp314-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 14.2 MB |
| Tags | CPython 3.14 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
e3e30f2f86c99191fd7bab05bf1b3ab3acaf8ece18d418d3d0dfd6d7968bd909
|
|
BLAKE2b-256 checksum How to use checksums |
9f0229d57a169268c1f8e96e86a5eb0679ac006a1915a4125bd9ba35dff6acd4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / a11_kit-0.7.25-cp314-cp314-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.25-cp314-cp314-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 13.4 MB |
| Tags | CPython 3.14 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
efc719ad9819cc4b0996d9e678e68d3056ef9d2121697afca4df4e45b5564d66
|
|
BLAKE2b-256 checksum How to use checksums |
450754fec37db4d7981c503606c6ab0201d87dae1b79aa46b67d2d3de1056e9d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / a11_kit-0.7.25-cp314-cp314-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.25-cp314-cp314-macosx_14_0_arm64.whl |
|---|---|
| Size | 11.2 MB |
| Tags | CPython 3.14 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
11e81f2a28565cebbedb11512db75f1bb2fe211e650d53bfbcd5cec00a219782
|
|
BLAKE2b-256 checksum How to use checksums |
696a6ec1a688ccaefd31a566e0812955d0723009fe3fc85429e71ffe138777b0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / a11_kit-0.7.25-cp313-cp313-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.25-cp313-cp313-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 14.2 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
6e95f063daef687ba998f6216a85c97df58a7678643ffc310fce0f8efc2539b5
|
|
BLAKE2b-256 checksum How to use checksums |
4f8c852c6550516ca3dbcfa0d198b65200d37953f425c62ac63f89e5cb16bdfb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / a11_kit-0.7.25-cp313-cp313-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.25-cp313-cp313-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 13.4 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
4544effccb1208f37dfc16b068af69d938005079b2eed9a7a654e301b683107a
|
|
BLAKE2b-256 checksum How to use checksums |
0d26a6c82e39fabf11d8f077d983335537450b501a4e34bcd2f88c5f609186af
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / a11_kit-0.7.25-cp313-cp313-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.25-cp313-cp313-macosx_14_0_arm64.whl |
|---|---|
| Size | 11.2 MB |
| Tags | CPython 3.13 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
e15bd9c6c5c7082ab7314bf005498f9d2ed45668379dc1c2f8f880f88205d811
|
|
BLAKE2b-256 checksum How to use checksums |
db4e8dda87c9564571f8190ad1efc37a2af33efe668cb129736911609a16803f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / a11_kit-0.7.25-cp312-cp312-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.25-cp312-cp312-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 14.2 MB |
| Tags | CPython 3.12 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
d6665755ffcf7b7be44fab3fa1dee4796c4c6be815b1681f4a130aac3eddcbaa
|
|
BLAKE2b-256 checksum How to use checksums |
8aa4508005726899671a8806539f49860f9e39795dd0a519d40770c9b89f62f5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / a11_kit-0.7.25-cp312-cp312-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.25-cp312-cp312-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 13.4 MB |
| Tags | CPython 3.12 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
1524fde55118f8f60f4630f806f3618a3d3d8ee5e1d5bdfb724099759c0ab92a
|
|
BLAKE2b-256 checksum How to use checksums |
6c11362e99ae0c80572c0b2c3887f75b63bc37436abfcef7ab134162fb1ab318
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / a11_kit-0.7.25-cp312-cp312-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.25-cp312-cp312-macosx_14_0_arm64.whl |
|---|---|
| Size | 11.2 MB |
| Tags | CPython 3.12 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
cada52bf00732d6bb5532c030c81fc822b4dd48e38385fa69d3fb7a108ef76d8
|
|
BLAKE2b-256 checksum How to use checksums |
291c4378fc0c82f4d649b59394ba01baec871fb0dff1cbc9880932480643dd6d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / a11_kit-0.7.25-cp311-cp311-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.25-cp311-cp311-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 14.2 MB |
| Tags | CPython 3.11 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
8070e17fefe79805beddf7661aef17d5952cd077ba8caf3ae124b240e097951b
|
|
BLAKE2b-256 checksum How to use checksums |
773990ec62e92265498ee8795be1cd4ab67dbdf5be21006273b5bd94f46594fd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / a11_kit-0.7.25-cp311-cp311-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.25-cp311-cp311-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 13.4 MB |
| Tags | CPython 3.11 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
962bfcf57722226efc0c2b1f2811a0a768b262805b26eee5fe36d08e16c85e27
|
|
BLAKE2b-256 checksum How to use checksums |
211b027ad24c26a283af22d57a21bd51ea11dac5a1bff1fe758a8a716d458147
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / a11_kit-0.7.25-cp311-cp311-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.25-cp311-cp311-macosx_14_0_arm64.whl |
|---|---|
| Size | 11.2 MB |
| Tags | CPython 3.11 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
ba01c00ad7d1528a5356866fbb36188fafab640bb4faae757999d654207131f5
|
|
BLAKE2b-256 checksum How to use checksums |
15f26a662b1f8401a29312c0e83dec77e957ef774674619fed145eb27cbc8f4c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logSecurity for a11-kit 0.7.25
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 13 files in this release have been uploaded with provenance metadata.
Attestation for a11_kit-0.7.25.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














