agent6
- Runs the model's commands in a Linux sandbox with the file and network access you set.
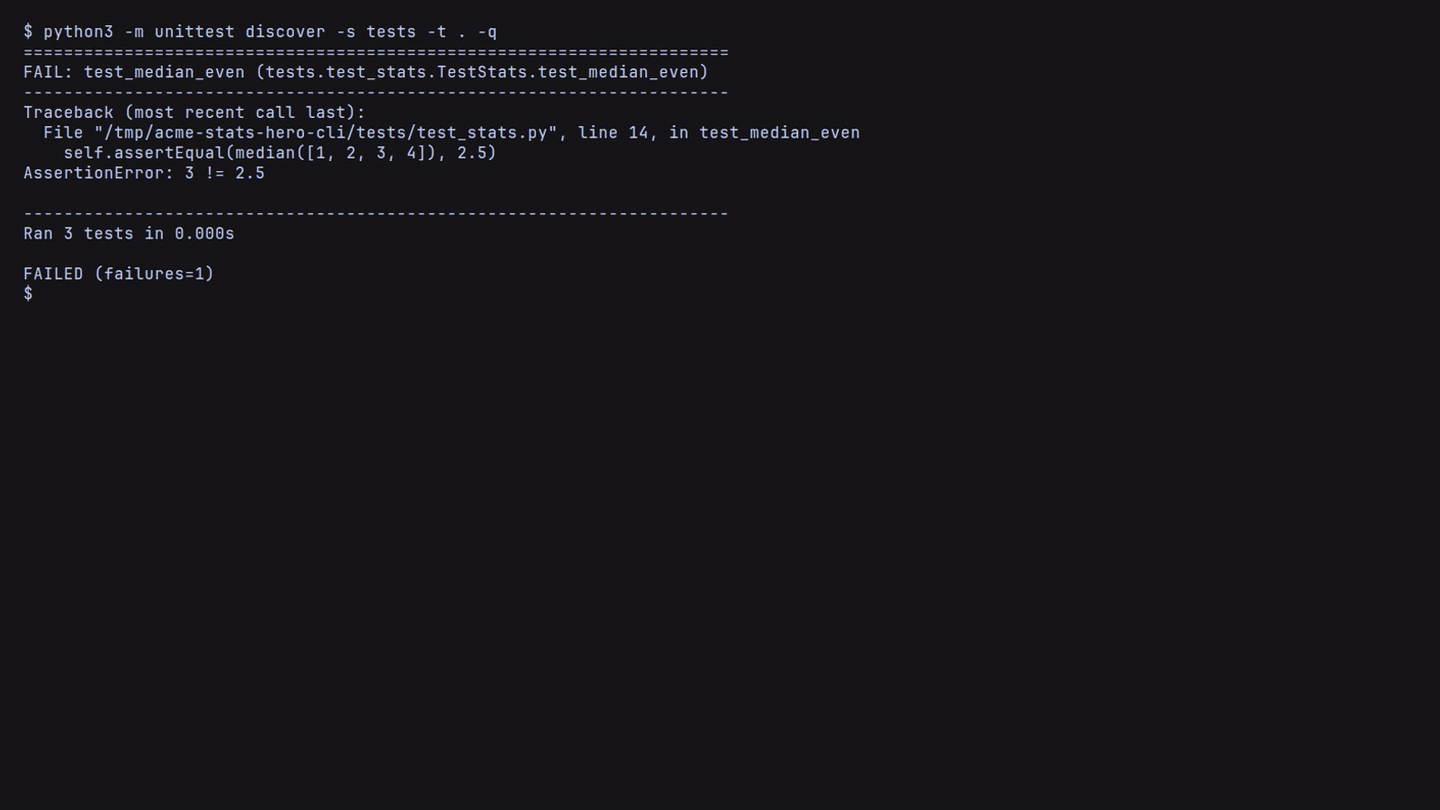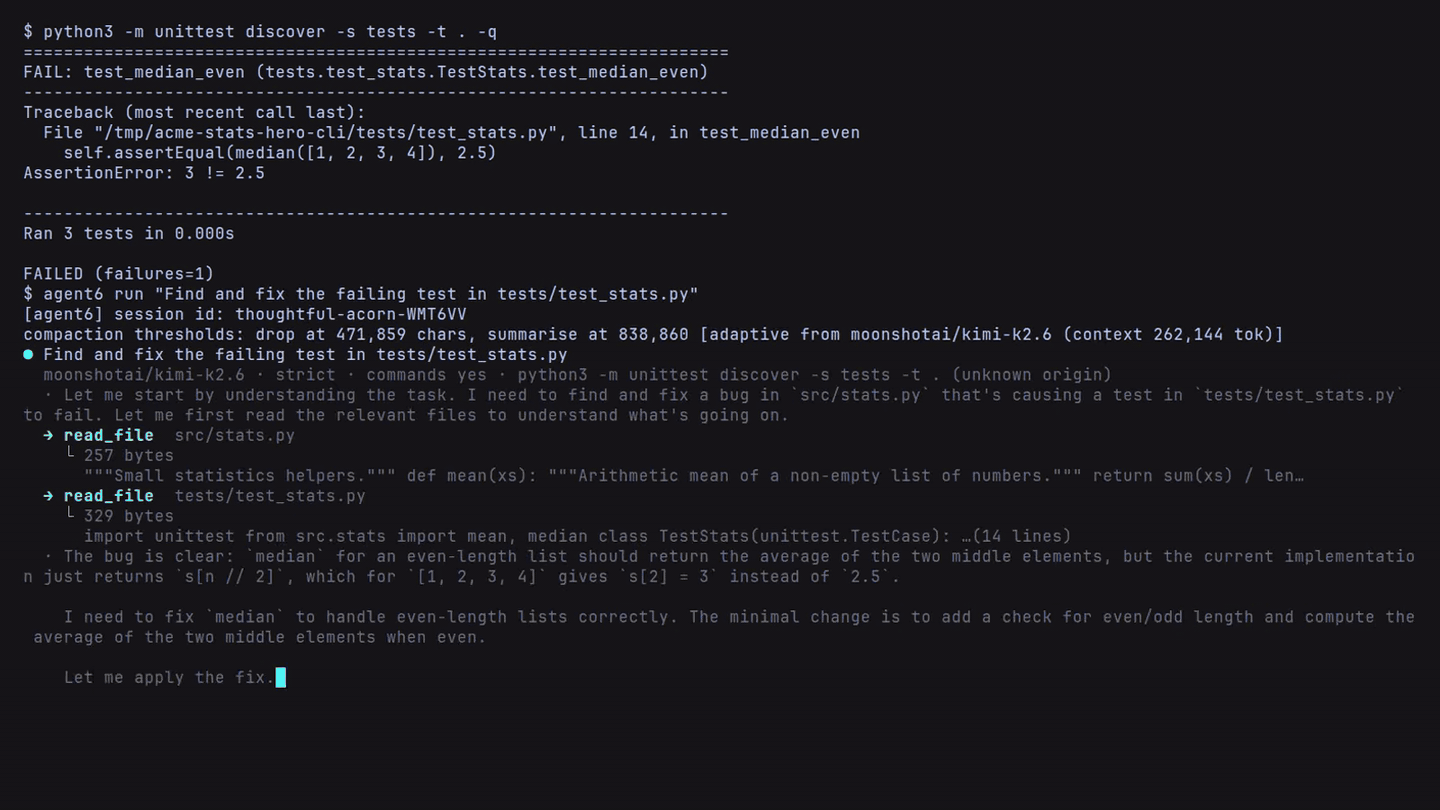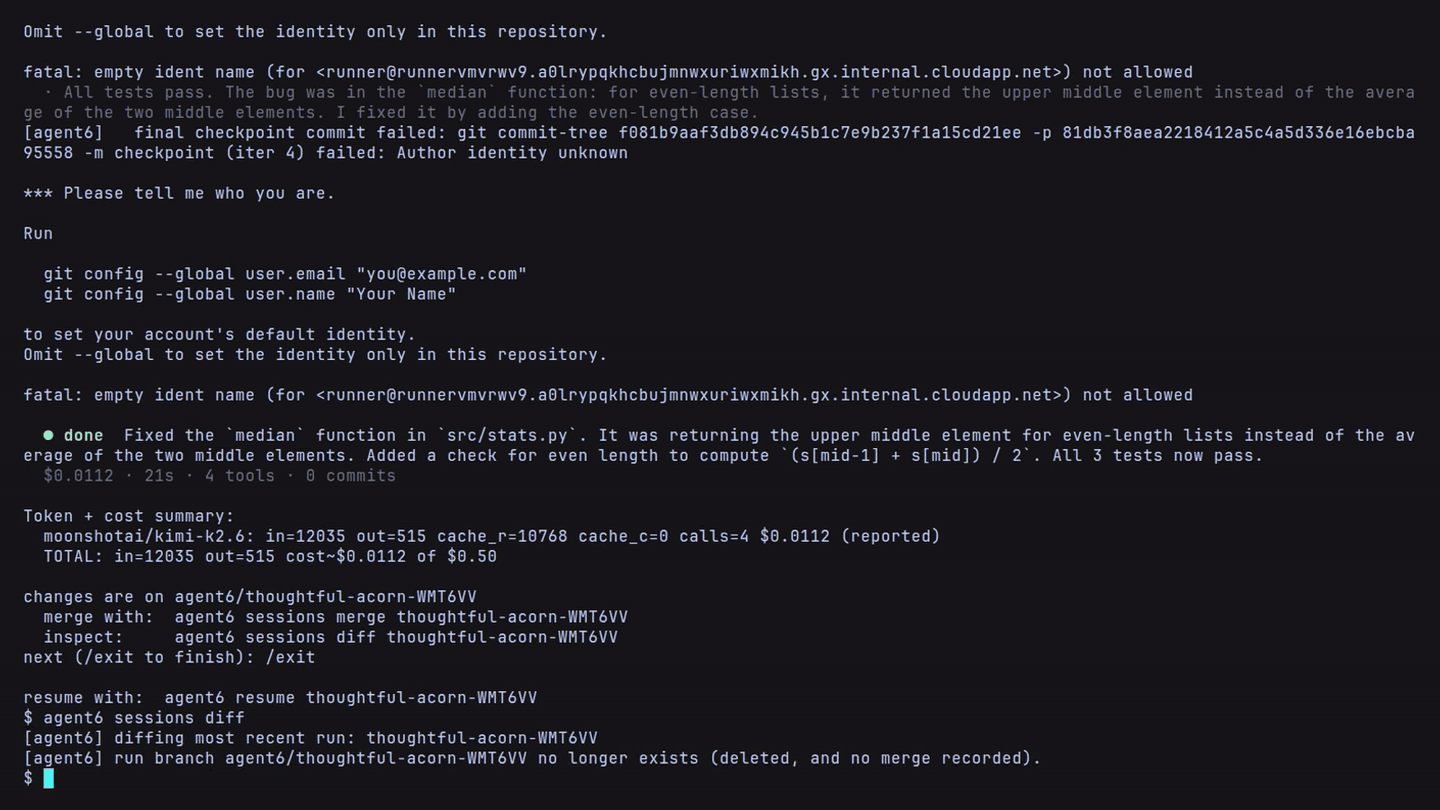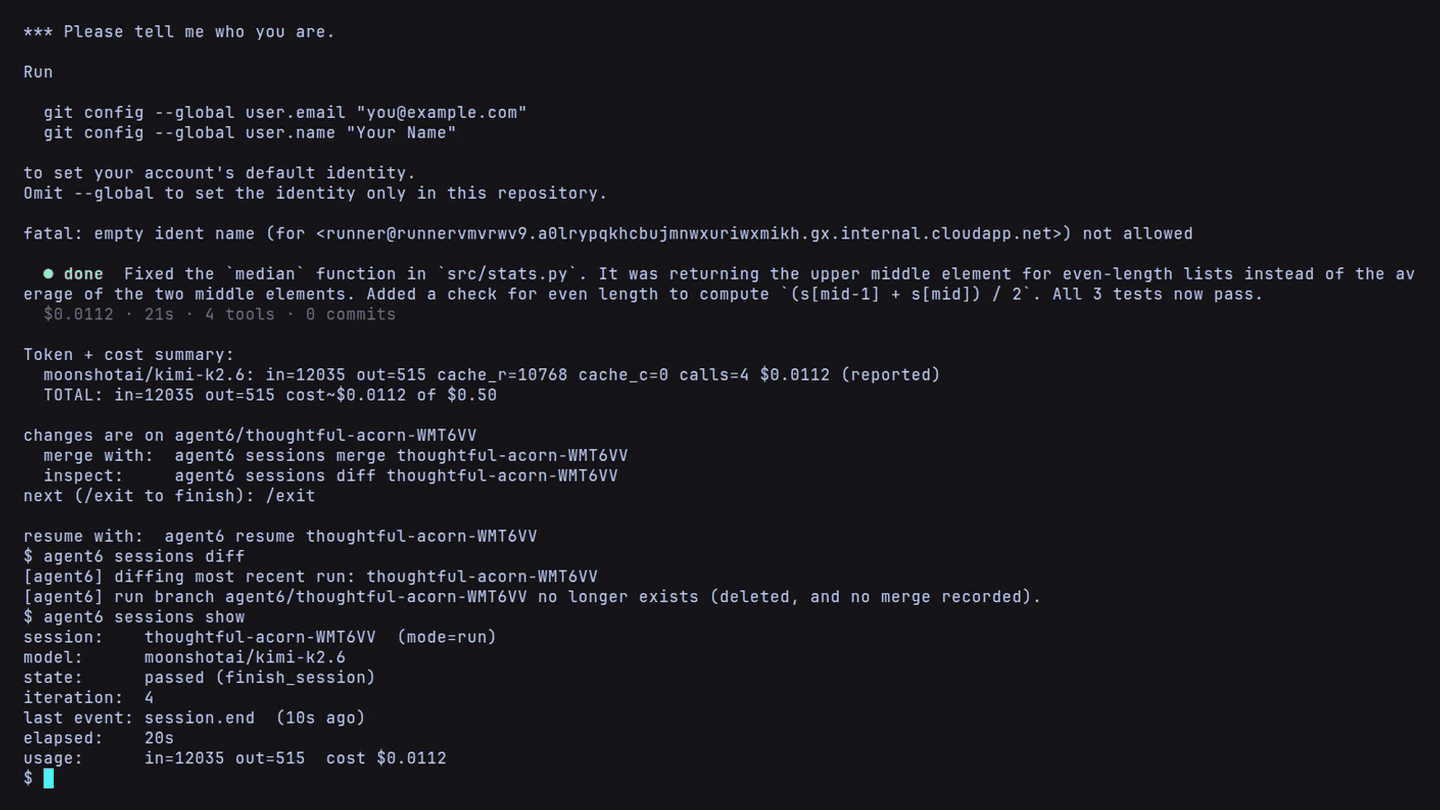
- Saves conversations, tool activity, and Git checkpoints so you can inspect, resume, or fork a session from an earlier turn.
- Shows the task graph, token usage and compaction as they happen.
- Pinned instructions survive compaction; repository memory carries facts across runs.
- Verifies work with a configured or inferred command, checking the starting tree by default, and reports whether the result passed, failed, or remains unverified.
- Reviews the diff with a panel of models you configure, keeps each finding open until you resolve it, and refuses to merge over an open blocking finding.
- Runs parallel attempts in isolated clones with
--parallel Nor a list of models, then ranks the results for you to choose which to merge. - Defines long-running workflows in editable TOML state machines, combining agent runs, tool calls, waits, and branches with offline tests, crash recovery, and replay from recorded results.
- Supports repository
AGENTS.mdinstructions, SKILL.md packs, MCP servers, and background commands for development servers and watchers. - Shows the repository in the browser: the commit graph, each commit's diff, a compare of two revisions, and the files at any revision with blame.
- Eight runtime dependencies, no telemetry unless you configure an export, and no automatic updates.
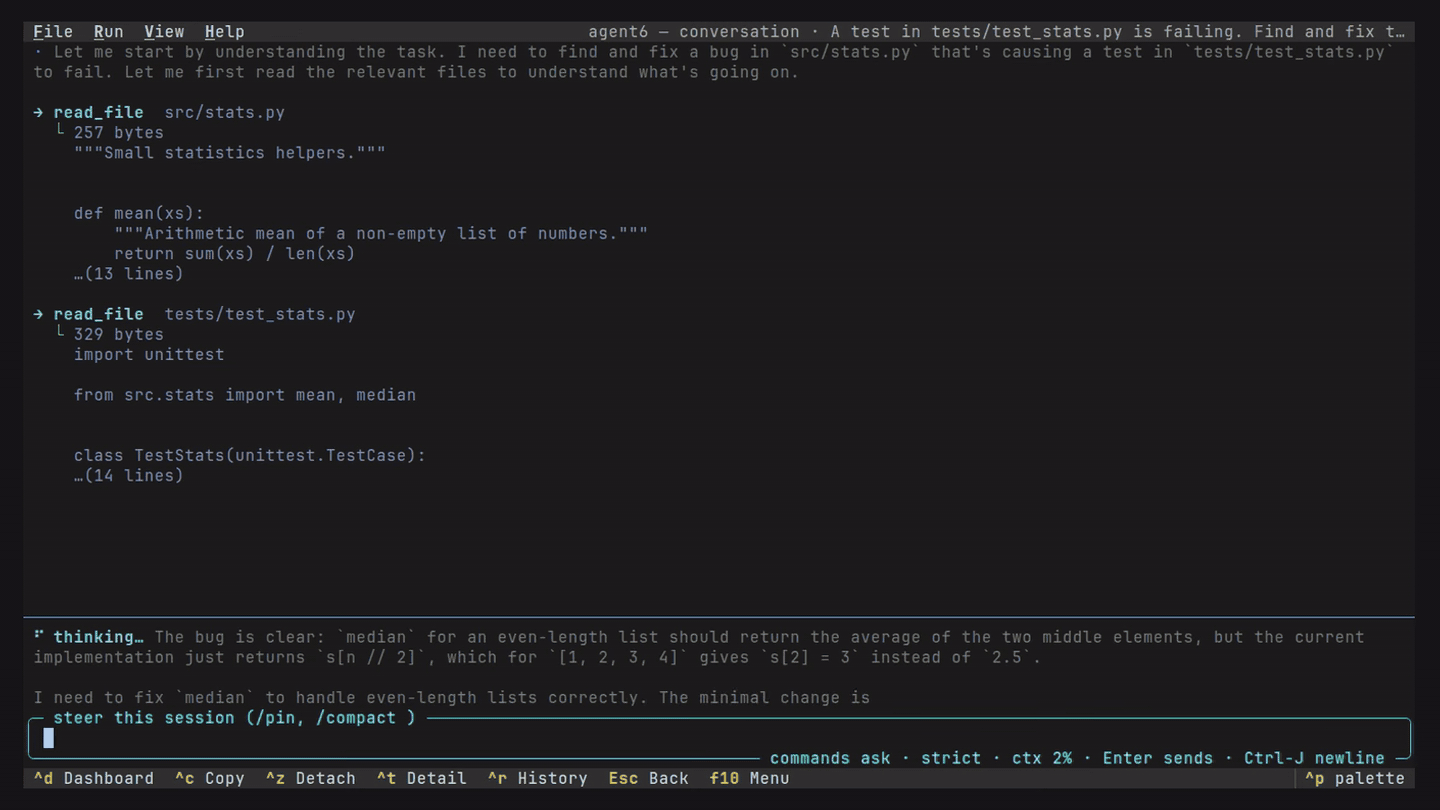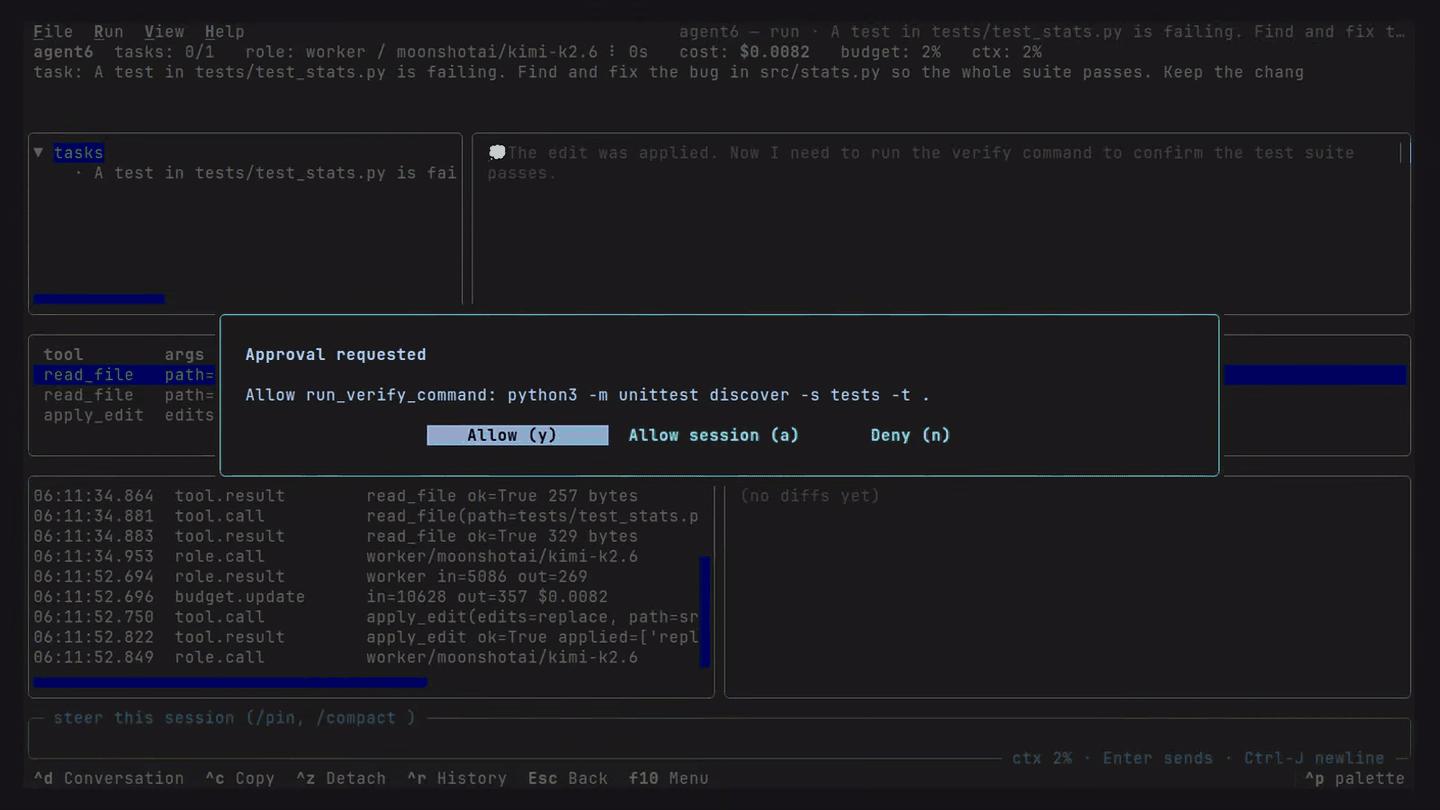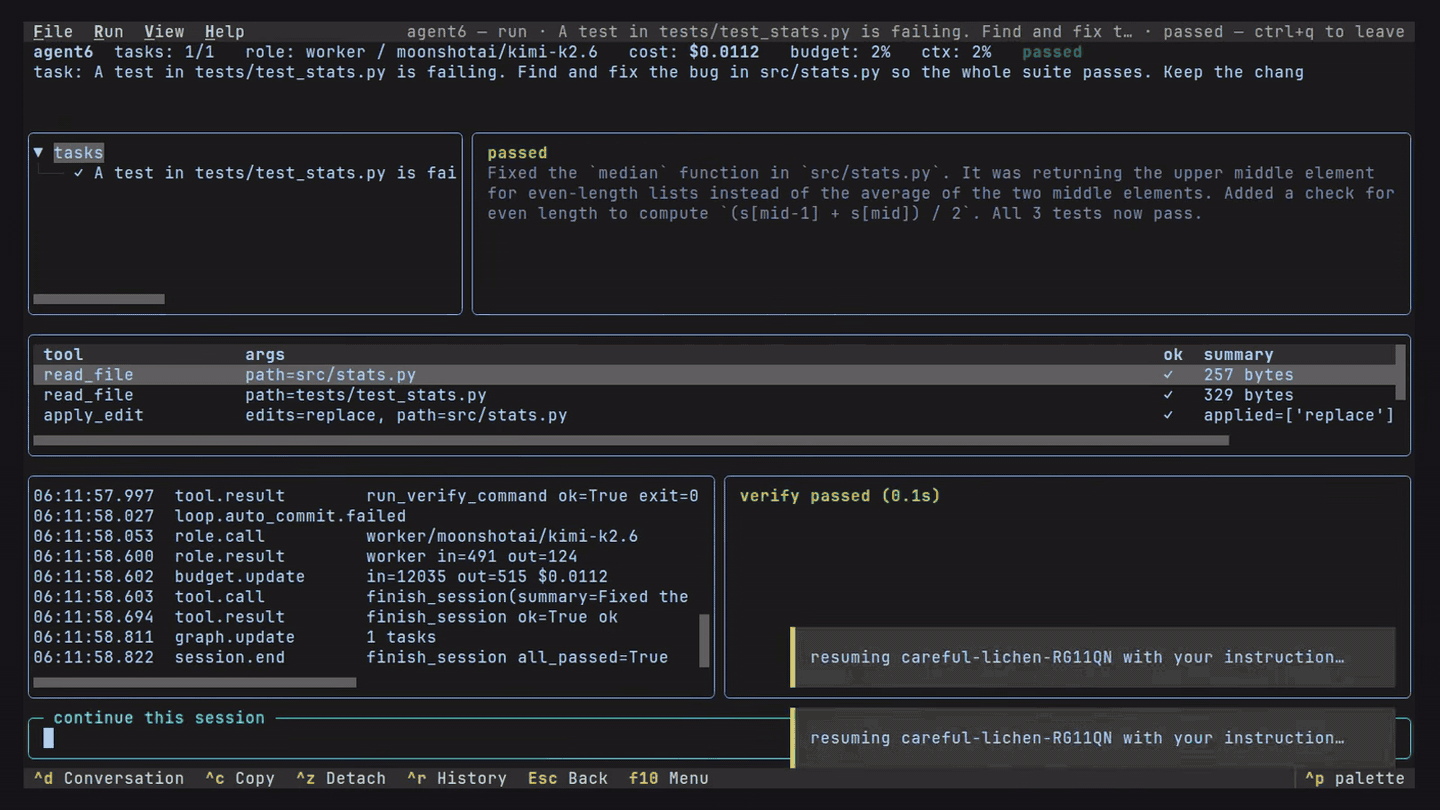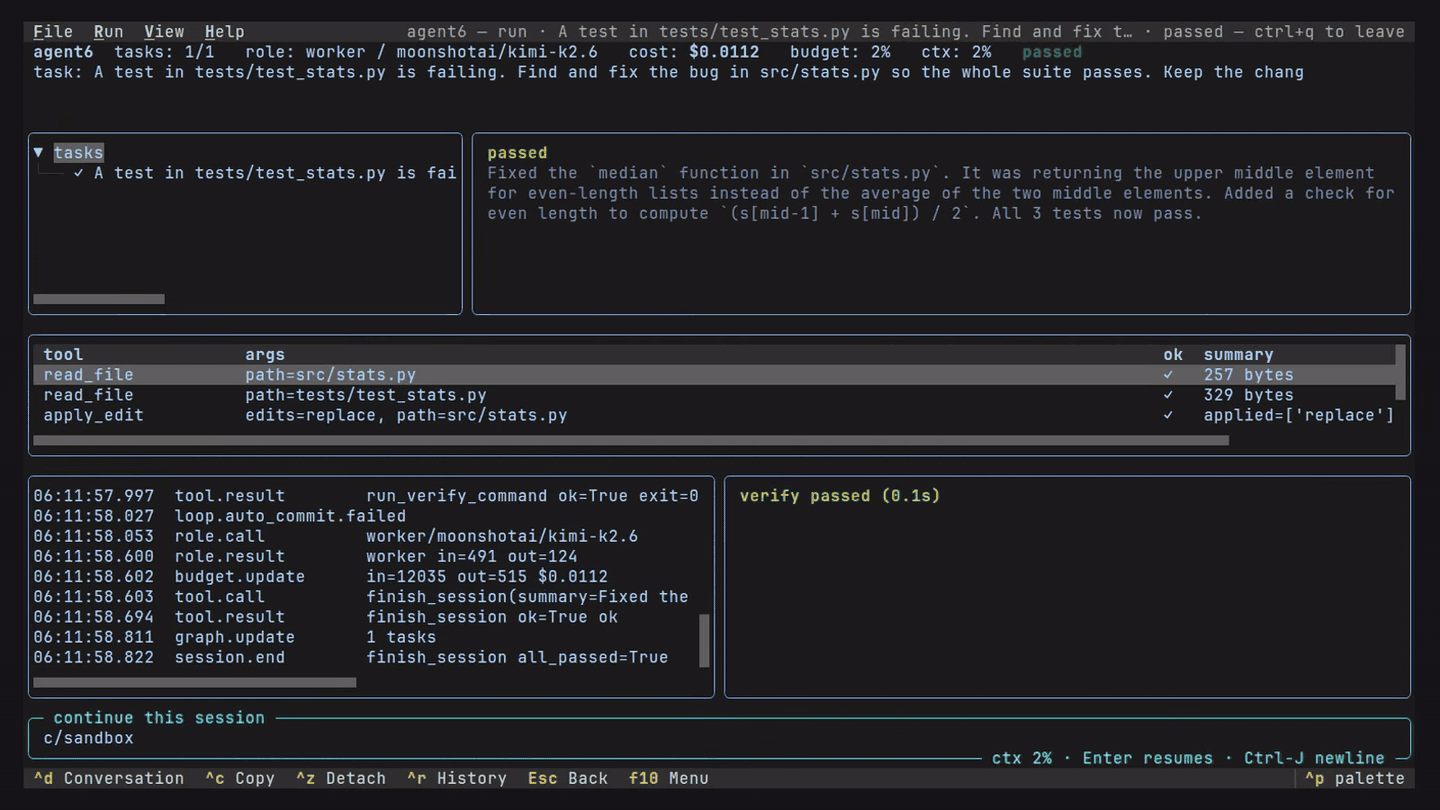
agent6 tui terminal interface |
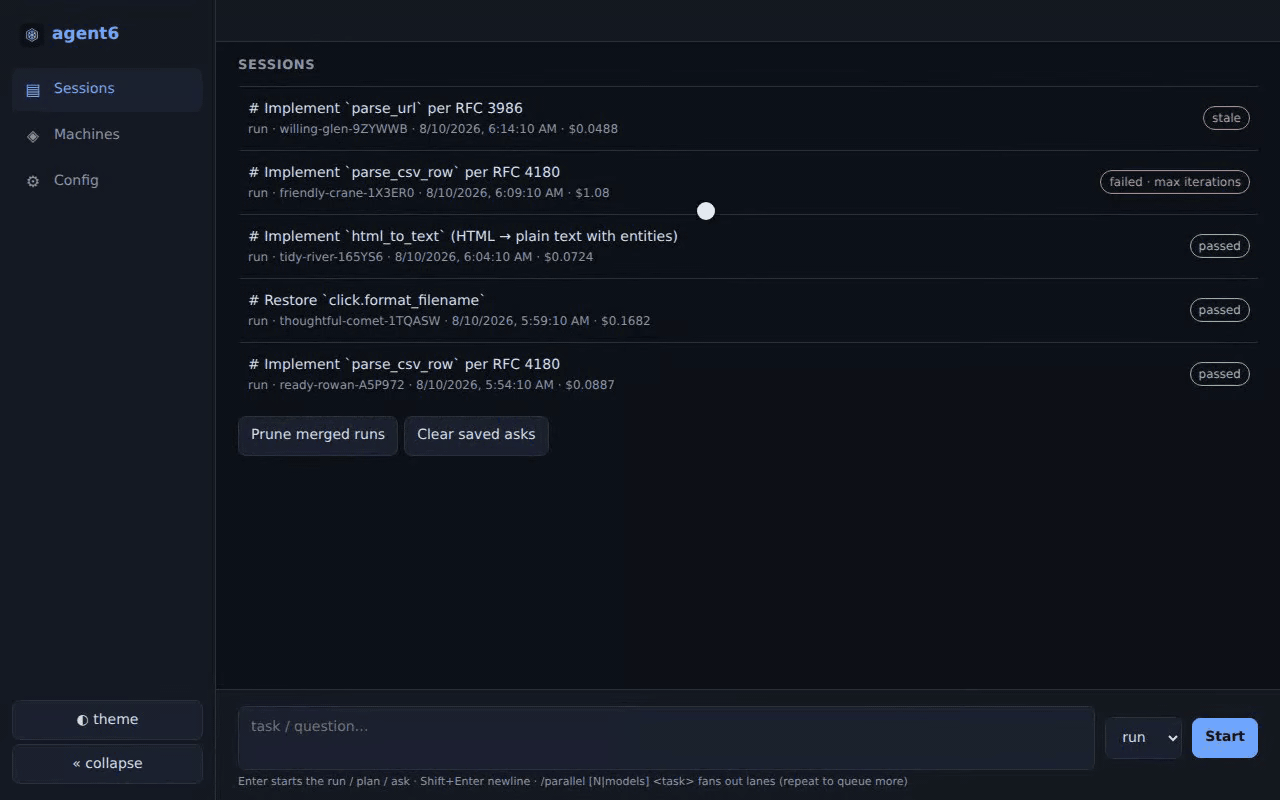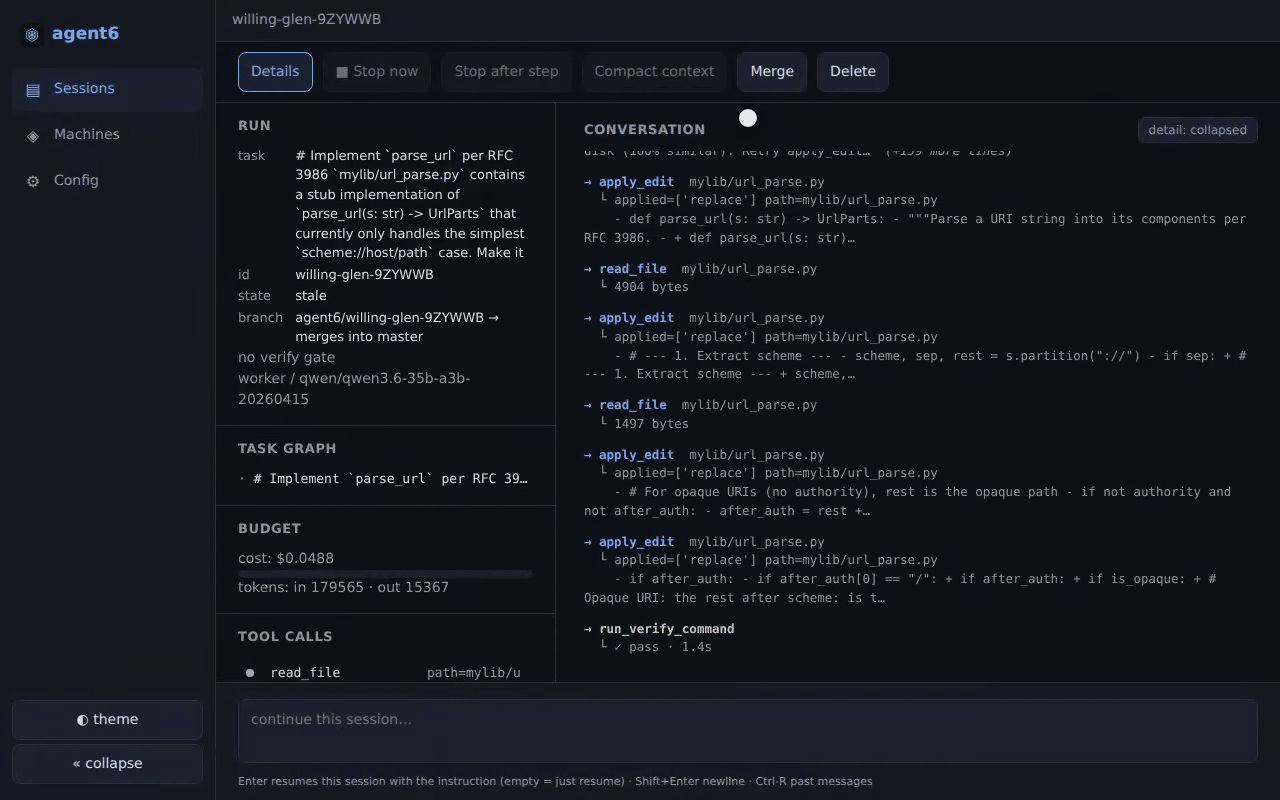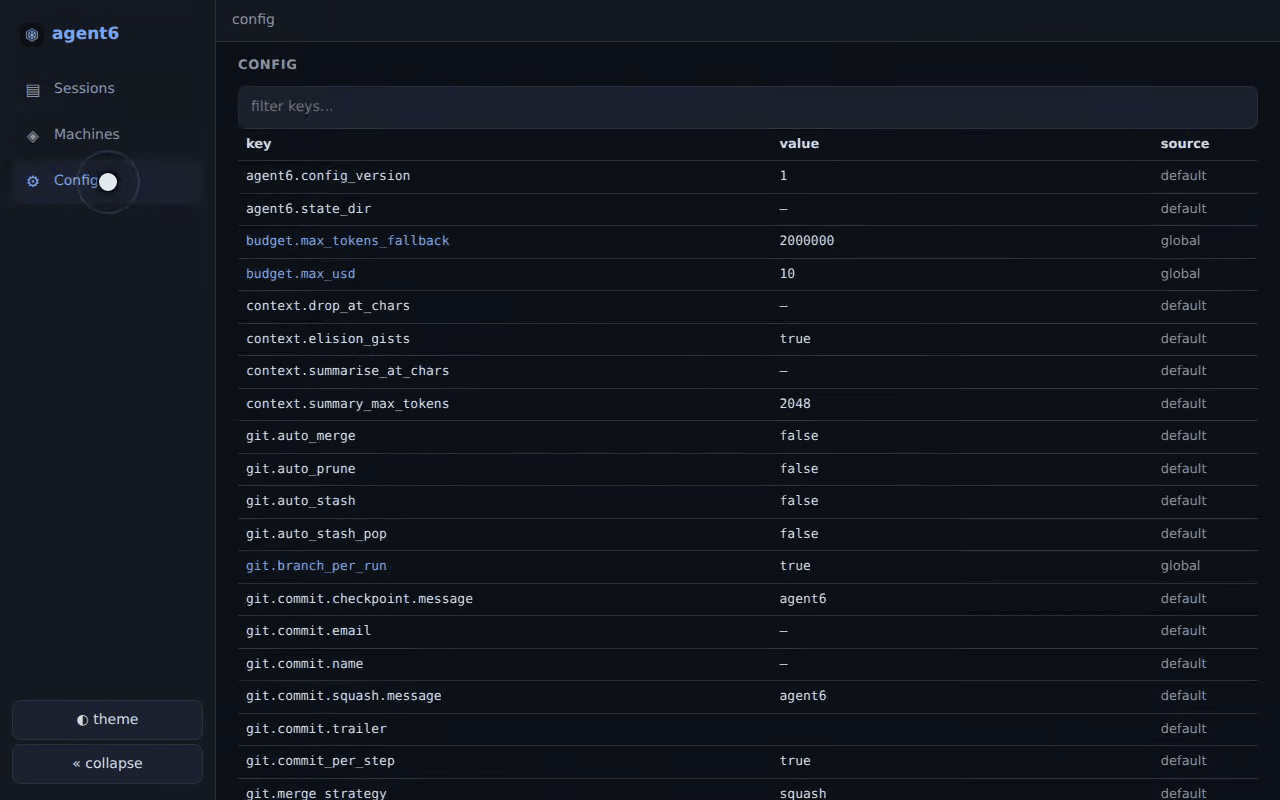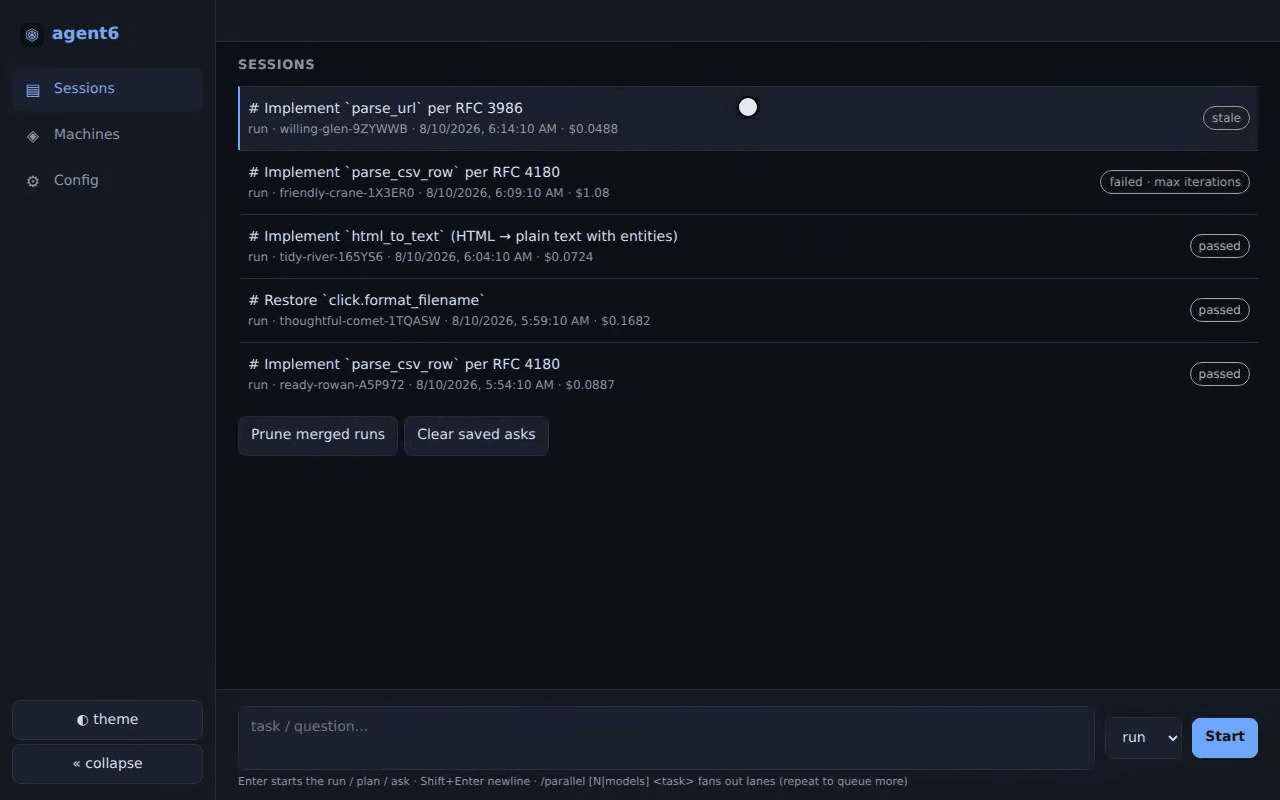
agent6 web browser interface for desktop or phone |
Also available as a streaming CLI and through ACP editor integration.
Installation
Sandboxing supports Linux on x86_64 and aarch64; macOS runs without it, and Windows users should use WSL.
Install with uv or pipx, then connect a provider and select a model:
uv tool install agent6      # or pipx install agent6
agent6 connect              # configure a provider
agent6 model worker         # choose a model
Use Anthropic or any OpenAI-compatible endpoint, including OpenAI, OpenRouter, Ollama, vLLM, llama.cpp, and LM Studio.
A provider entry can also use the Responses API (providers.<name>.api_format = "responses") or sign in at a configured OAuth issuer.
For subscriptions, replace agent6 connect with agent6 connect chatgpt or agent6 connect claude; the latter uses your installed, signed-in Claude Code binary.
agent6 completions installs tab completion for your shell.
Usage
A run edits your current checkout.
Checkpoint commits go on a separate agent6/<id> branch; checkpointing leaves your current branch's history and index in place.
For a separate checkout, use agent6 run --worktree "your task", which starts from committed HEAD without copying uncommitted changes or untracked dependencies.
cd your-repo
agent6 check                # check configuration and sandbox support
agent6 run "your task here"
Commands ask for approval by default.
After the task finishes, enter another instruction or type /exit.
Inspect the latest session, then merge its recorded changes when ready:
agent6 sessions show        # status and verification result
agent6 sessions diff        # recorded changes
agent6 sessions merge       # merge into the run's starting branch
Other commands:
| Command | Purpose |
|---|---|
agent6 plan "task" |
plan a change; agent6 run --from <plan-id> carries it out |
agent6 ask "question" |
ask about the repository |
agent6 review |
review a diff |
agent6 attach <id> |
follow a live session |
agent6 steer <id> "instruction" |
direct the next steps |
agent6 sessions findings <id> |
list a session's review findings |
agent6 sessions receipt <id> |
print the recorded tests, review outcome and how to revert |
agent6 stop <id> --after-step |
stop after the current step |
agent6 resume <id> |
continue an interrupted run |
agent6 fork <id> --at-turn 7 |
fork a coding run from an earlier turn into a separate worktree |
agent6 telemetry export |
export session journals as OpenTelemetry signals or a Prometheus textfile |
agent6 pack |
copy your config, secrets, sessions and memory into the workspace before a sync |
agent6 unpack |
move the packed files into the new home |
To give a finished run more work, use agent6 resume <id> --steer "next task".
Configuration
agent6 config show prints effective settings and where each value came from.
Changes are global unless you add --repo for a repository override, for example:
agent6 config set --repo harness.verify_command '["uv", "run", "pytest"]'
The worker, planner, and reviewer can use different models and reasoning effort; unset planner and reviewer roles use the worker. Budgets limit spending, tokens for unpriced calls, and supported subscription usage.
Security
The sandbox confines model commands; the agent6 process remains trusted, holds provider credentials, and connects to your configured providers.
agent6's own git never pushes, rewrites history or runs reset --hard, and no config key turns that on.
MCP is off by default, and locally spawned servers use the command sandbox unless explicitly configured otherwise.
sandbox.isolation = "auto" selects the strongest available level (full, partial, or none) and warns when it falls back, including to no confinement.
Under full, the default sandbox.network = "auto" gives a run's commands a private network; partial and none sandbox.isolation use the host network.
The defaults are sandbox.network = "auto", sandbox.run_commands = "ask" and sandbox.protect_git = "auto".
agent6 check sandbox shows the effective file and command boundaries, network and approval settings, and live probe results.
How it compares
A container or a VM confines the whole agent.
agent6 confines the model's commands in a jail on your host.
Its own work runs outside the jail.
Under sandbox.isolation = "full" or sandbox.isolation = "partial", the commands cannot read your provider keys or the secrets file.
Under sandbox.isolation = "full", the default sandbox.protect_git = "auto" keeps the project's .git read-only to the commands, so nothing can be planted for agent6's own git to run.
The repository stays at its real path.
The jail sees your installed toolchains read-only.
agent6 runs inside or outside a devcontainer.
Inside a container, sandbox.isolation = "auto" selects the strongest level the container allows, and agent6 check sandbox names it.
Docker's default seccomp and AppArmor profiles block user namespaces, so a plain devcontainer gets sandbox.isolation = "partial": the container's network, and .git writable to the commands, warned at startup.
A container started with --security-opt seccomp=unconfined --security-opt apparmor=unconfined allows sandbox.isolation = "full".
1 maintainer

Metadata
1 maintainer
Release files for agent6 0.0.40
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| agent6-0.0.40.tar.gz | 1.7 MB | With provenance | Details for agent6-0.0.40.tar.gz |
Built distributions (wheels)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| agent6-0.0.40-py3-none-manylinux_2_17_x86_64.musllinux_1_2_x86_64.whl | Python 3 | none | Linux musl 1.2+ x86-64, Linux glibc 2.17+ x86-64 | Details for agent6-0.0.40-py3-none-manylinux_2_17_x86_64.musllinux_1_2_x86_64.whl |
| agent6-0.0.40-py3-none-manylinux_2_17_aarch64.musllinux_1_2_aarch64.whl | Python 3 | none | Linux glibc 2.17+ ARM64, Linux musl 1.2+ ARM64 | Details for agent6-0.0.40-py3-none-manylinux_2_17_aarch64.musllinux_1_2_aarch64.whl |
Total release size: 6.1 MB
Release files / agent6-0.0.40.tar.gz
| Download URL | agent6-0.0.40.tar.gz |
|---|---|
| Size | 1.7 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
fbd010e52ee89f892f09eb055198471290c62c4bcb8cd55a5919f0456d593193
|
|
BLAKE2b-256 checksum How to use checksums |
45670e513173b9e719363510832efe741be804b483495fdafa785e59c7b53d87
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logRelease files / agent6-0.0.40-py3-none-manylinux_2_17_x86_64.musllinux_1_2_x86_64.whl
| Download URL | agent6-0.0.40-py3-none-manylinux_2_17_x86_64.musllinux_1_2_x86_64.whl |
|---|---|
| Size | 2.2 MB |
| Tags | Linux glibc 2.17+ x86-64 Linux musl 1.2+ x86-64 Python 3 |
|
SHA-256 checksum How to use checksums |
1140e07f33a638f7b5e23529c3526a8d9b82a2a2ed84a5206d8d3ca8bbf2c7a9
|
|
BLAKE2b-256 checksum How to use checksums |
b08b101d5d7c2f1fc299b40b06201aaee307ae20d5e3bc7fc2448c5eb3e83e4b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logRelease files / agent6-0.0.40-py3-none-manylinux_2_17_aarch64.musllinux_1_2_aarch64.whl
| Download URL | agent6-0.0.40-py3-none-manylinux_2_17_aarch64.musllinux_1_2_aarch64.whl |
|---|---|
| Size | 2.2 MB |
| Tags | Linux glibc 2.17+ ARM64 Linux musl 1.2+ ARM64 Python 3 |
|
SHA-256 checksum How to use checksums |
eb00d81aa743f1905ca0826d7d95121ee93b8cc03774e9d4dd086f01dab140a5
|
|
BLAKE2b-256 checksum How to use checksums |
2ab46ff98be922cf15b32ceb079b15a71a0dff98287bbac55d86e01b51cca526
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logSecurity for agent6 0.0.40
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 3 files in this release have been uploaded with provenance metadata.
Attestation for agent6-0.0.40.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.