
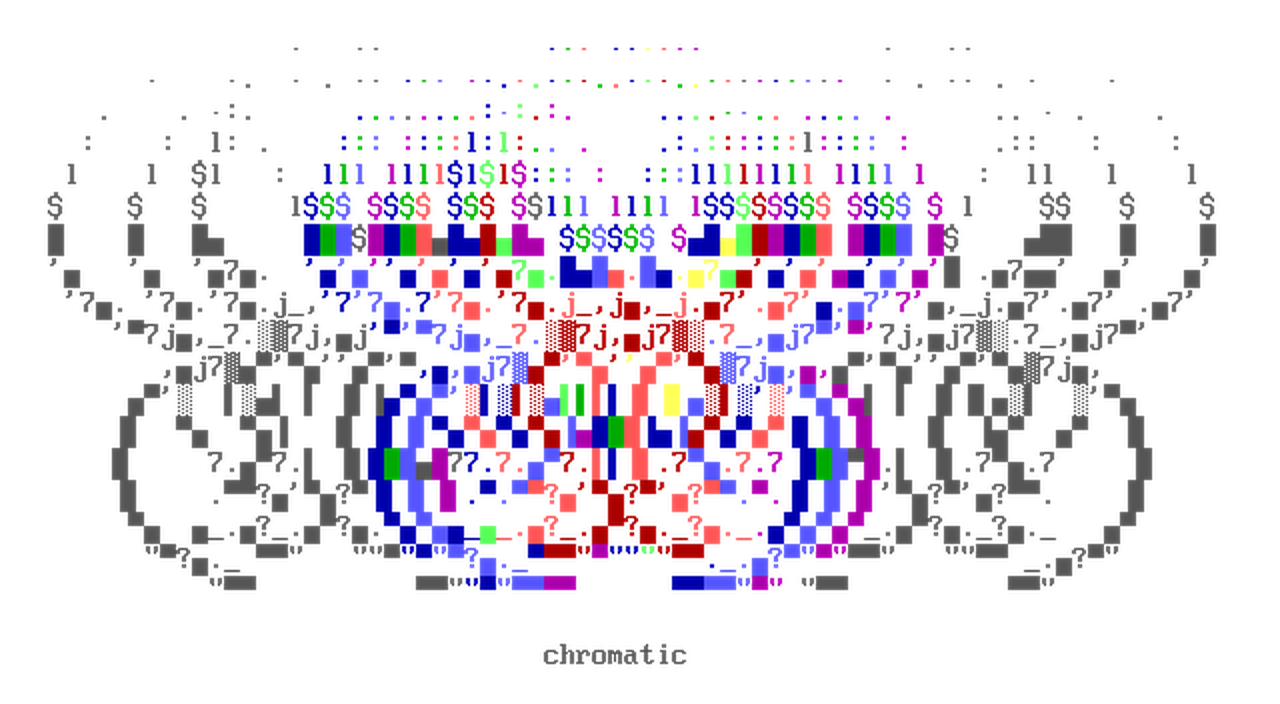



Chromatic is a library for processing and transforming ANSI escape sequences (colored terminal text).
It offers a collection of algorithms and types for a variety of use cases:
- Image-to-ASCII / Image-to-ANSI conversions.
- ANSI art rendering, with support for user-defined fonts.
- A
ColorStrtype for low-level control over ANSI SGR strings. - colorama-style wrappers (
Fore,Back,Style). - Conversion between 16-color, 256-color, and true-color (RGB) ANSI colorspace via the
colorbytestype. - Et Cetera 😲
Usage
Image-to-ANSI conversion
Convert an image into a 2d ANSI string array, and render the ANSI array as image:
from chromatic.color import ansicolor4Bit
from chromatic.image import ansi2img, img2ansi
from chromatic.data import userfonts, butterfly

input_img = butterfly()
font = userfonts['vga437']

# `char_set` is used to translate luminance to characters
#            | <- index 0 is the 'darkest'
char_set = r"'·,•-_→+<>ⁿ*%⌂7√Iï∞πbz£9yîU{}1αHSw♥æ?GX╕╒éà⌡MF╝╩ΘûǃQ½☻Ŷ┤▄╪║▒█"
#                                           index -1 is the 'brightest' -> |

# returns list[list[ColorStr]]
ansi_array = img2ansi(
	input_img,
	font,
	sort_glyphs=False,	# map `char_set` as-is
	char_set=char_set,
	ansi_type=ansicolor4Bit,
	factor=200,
)

# print your image to stdout
print(*map(''.join, ansi_array), sep="\x1b[0m\n")

# returns a PIL.Image.Image object
ansi_img = ansi2img(ansi_array, font, font_size=16)
ansi_img.show()
ColorStr
from chromatic import ColorStr

base_str = 'hello world'

red_fg = ColorStr(base_str, 0xFF0000, ansi_type='8b')

assert red_fg.base_str == base_str
assert red_fg.rgb_dict == {'fg': (0xFF, 0, 0)}
assert red_fg.ansi == b'\x1b[38;5;196m'
ColorStr will parse raw SGR sequences, and accepts different types for fg and bg:
from chromatic import ColorStr

red_fg = ColorStr('[*]', 0xFF0000, ansi_type='8b')

assert red_fg == ColorStr(b"\x1b[38;5;196m[*]")
assert red_fg == ColorStr('[*]', fg=(0xFF, 0, 0), ansi_type='8b')
ANSI color format can be specified with ColorStr(ansi_type=...), or as a new object via ColorStr.as_ansi_type():
from chromatic import ColorStr, ansicolor4Bit, ansicolor24Bit, ansicolor8Bit

# each colorbytes type has an alias that you can use
assert all(
	ansi_type.alias == alias
	for ansi_type, alias in [
		(ansicolor4Bit, '4b'),
		(ansicolor8Bit, '8b'),
		(ansicolor24Bit, '24b'),
	]
)

truecolor = ColorStr('*', 0xFF0000, ansi_type=ansicolor24Bit)
a_16color = truecolor.as_ansi_type(ansicolor4Bit)

assert a_16color == truecolor.as_ansi_type('4b')
assert truecolor.ansi_format is ansicolor24Bit and truecolor.ansi == b'\x1b[38;2;255;0;0m'
assert a_16color.ansi_format is ansicolor4Bit and a_16color.ansi == b'\x1b[31m'
Adding and removing SGR parameters from a ColorStr:
import chromatic as cm

regular_str = cm.ColorStr('hello world')

assert regular_str.ansi == b''

bold_str = regular_str.bold()

assert bold_str.ansi == b'\x1b[1m'

# use ColorStr.update_sgr() to remove and add SGR values
unbold_str = bold_str.update_sgr(cm.SgrParameter.BOLD)

assert unbold_str == regular_str
assert bold_str == unbold_str + cm.SgrParameter.BOLD	# __add__ can also be used
Installation
Install the package using pip:
pip install chromatic-python
Credits
Banner artwork: main rules by Crasher (2002)
1 maintainer

Metadata
1 maintainer
Release files for chromatic-python 0.8.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| chromatic_python-0.8.1.tar.gz | 929.7 kB | With provenance | Details for chromatic_python-0.8.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| chromatic_python-0.8.1-py3-none-any.whl | Python 3 | none | any | Details for chromatic_python-0.8.1-py3-none-any.whl |
Total release size: 1.6 MB
Release files / chromatic_python-0.8.1.tar.gz
| Download URL | chromatic_python-0.8.1.tar.gz |
|---|---|
| Size | 929.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
2baca512699e947b58837b4642e5b7c39a11610cad5cd30368b1e7c7116d4663
|
|
BLAKE2b-256 checksum How to use checksums |
1bc78d9f4f3985b62cdb65046677906ff74a76f4237ffab396d8f30279274133
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 12, 2026.
Transparency logRelease files / chromatic_python-0.8.1-py3-none-any.whl
| Download URL | chromatic_python-0.8.1-py3-none-any.whl |
|---|---|
| Size | 677.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
336d78e5ca7e9412b4bcba9e521d27a28fcd67fe2dcd28a64f7d667fe8594c2f
|
|
BLAKE2b-256 checksum How to use checksums |
ea4e493403519652191ff004da11e872d6d0010550ebe4182f59cf7b358c5566
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 12, 2026.
Transparency logSecurity for chromatic-python 0.8.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for chromatic_python-0.8.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 12, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














