
Get document loading right.
Compare loaders, trace every step and evaluate what reaches your model.


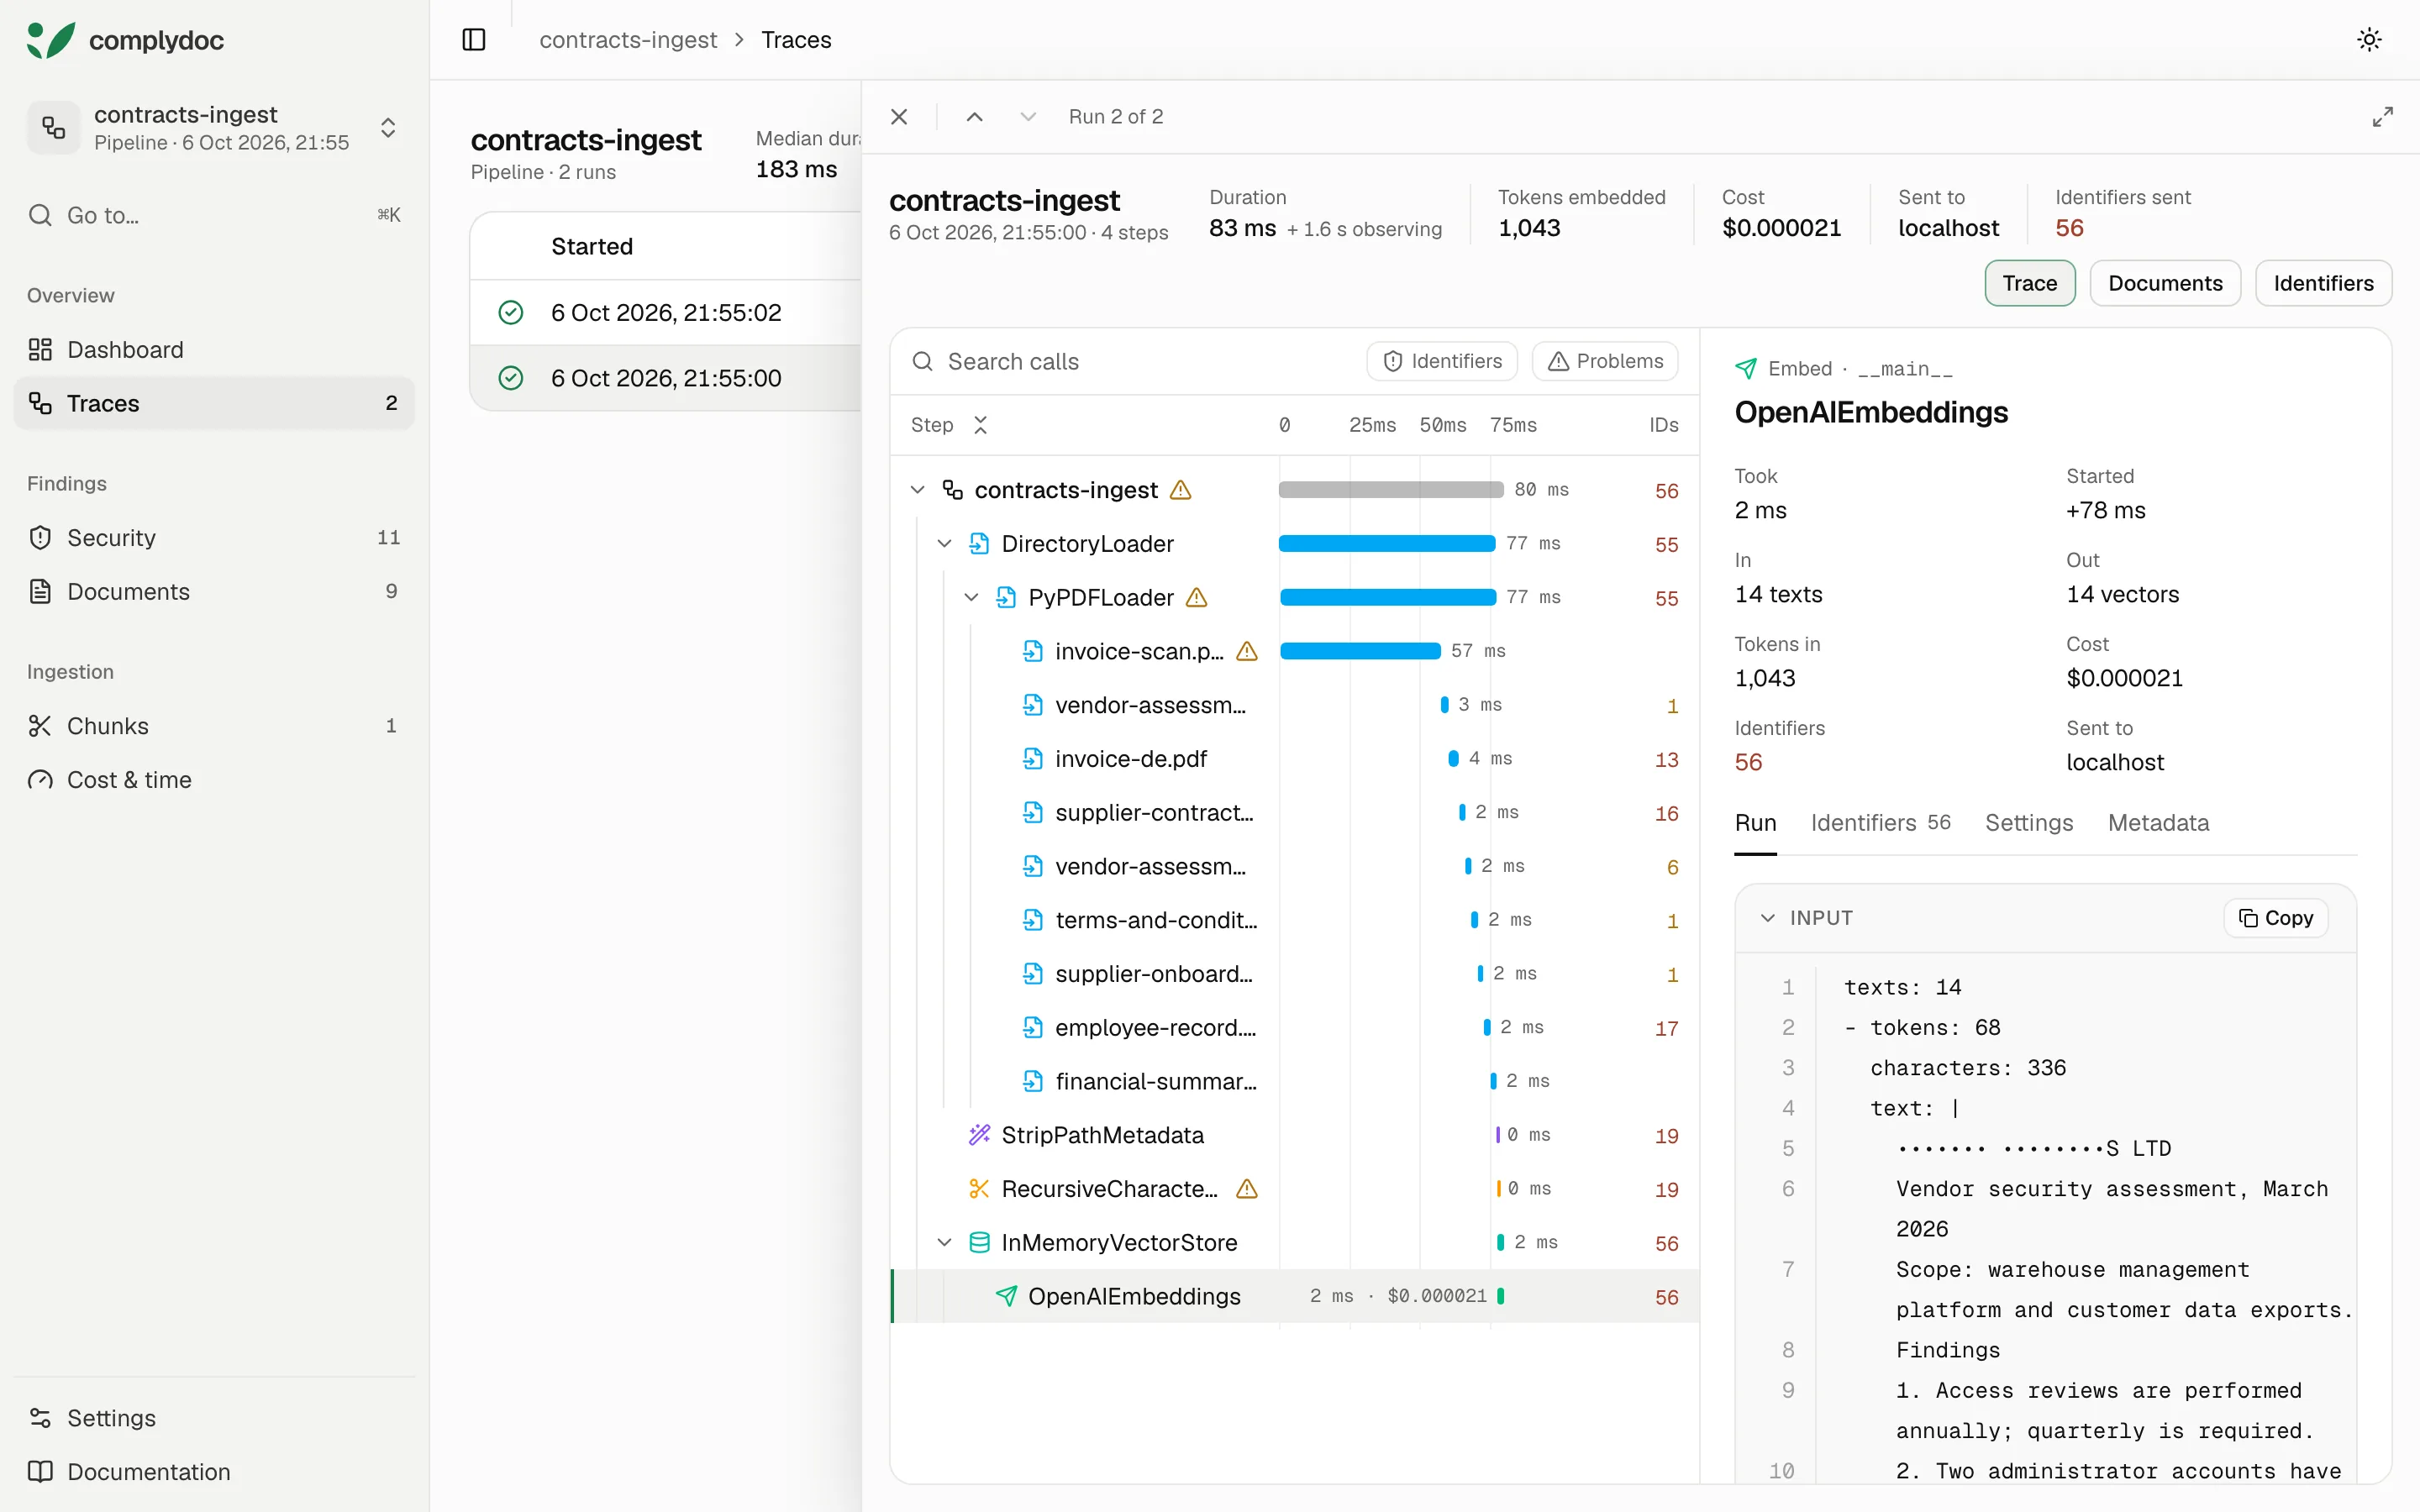
A PDF can say one thing to a person and another to your model. White text, tiny type, an IBAN behind a black bar: it's all still in the text layer, and most loaders pass it straight through. complydoc shows what your loaders actually extracted, flags hidden text and personal and financial identifiers before they're embedded, and traces every ingestion step with its time and cost. Nothing leaves your machine.
Works with LangChain, LlamaIndex, Unstructured, Haystack, Docling, LlamaParse, Azure Document Intelligence, Marker, Chonkie and the common vector stores and embedding APIs.
Try it
uv tool install complydoc
complydoc ui ./documents
complydoc ui audits the folder and opens the viewer on it, served from your machine. To
see a hidden clause caught, try the one-page contract in
examples/hidden_clause.pdf.
In your assistant
complydoc mcp lets Claude, Cursor or any MCP client open documents with personal and
financial details masked and hidden instructions taken out. In Claude Code:
/plugin install complydoc --marketplace complydoc/complydoc
Elsewhere, run it with uvx complydoc mcp; it is in the
MCP Registry as io.github.complydoc/complydoc.
Claude Desktop installs it from the extension on the
releases page. See
Documents into an assistant, cleaned.
Observe a pipeline
import complydoc as cd

with cd.observe("contracts-ingest"):
    documents = PyMuPDF4LLMLoader("contract.pdf").load()
    chunks = splitter.split_documents(documents)
    vector_store.add_documents(chunks)
Every loader, splitter, embedding call and vector store becomes a step, with its settings,
time, tokens, cost and the identifiers it passed on. Open it with complydoc ui.
What it shows
- Traces of each ingestion step, and how runs compare over time.
- Loader diffs: each loader's reading of a page side by side, with the page itself.
- Identifiers from Europe, the Americas, India and Australia, checksum-validated and masked until you choose to see them.
- Hidden content: text a reader does not see and a model does, and instructions written to a model.
- Evals: the facts a document must keep, checked on every reading.
- Chunks and cost: splitters side by side, and tokens priced across models.
In CI
- uses: complydoc/complydoc@v0.8.1
  with:
    path: documents
    policy: policy.yaml
complydoc check fails when a folder breaks your rules; finance, legal and hr ship as
ready policies. See GitHub Action.
More
- Documentation, and the playground with everything ready to run
- Run it for your team, in a container or from a bucket
- Network isolation: every run blocks outbound connections and records that it did
- Optional extras for scans and names:
complydoc doctorsays what is installed and how to add the rest - Changelog · Contributing · MIT
If complydoc is useful to you, a star helps other engineers find it.
1 maintainer

Metadata
1 maintainer
Release files for complydoc 0.8.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| complydoc-0.8.1.tar.gz | 6.7 MB | With provenance | Details for complydoc-0.8.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| complydoc-0.8.1-py3-none-any.whl | Python 3 | none | any | Details for complydoc-0.8.1-py3-none-any.whl |
Total release size: 10.9 MB
Release files / complydoc-0.8.1.tar.gz
| Download URL | complydoc-0.8.1.tar.gz |
|---|---|
| Size | 6.7 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
03257077ad8c4af14e72ecbe97b515b75a1aca4752363d2a1e24db6fb875584c
|
|
BLAKE2b-256 checksum How to use checksums |
4e8bdd3c56955d766dadcdb8d2f62701296260579f4fac10215180b9df654d3b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 18, 2026.
Transparency logRelease files / complydoc-0.8.1-py3-none-any.whl
| Download URL | complydoc-0.8.1-py3-none-any.whl |
|---|---|
| Size | 4.2 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
2afce4c7638349ba9d0ece9eafa068625565cd96dded44bd514b068ef7492832
|
|
BLAKE2b-256 checksum How to use checksums |
e74d56b2512ba815e5879c8b16a0662e7fa48377ab28b385beb22ea78340a064
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 18, 2026.
Transparency logSecurity for complydoc 0.8.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for complydoc-0.8.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 18, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














