
figure-gate


figure-gate reads a matplotlib figure you have already built and tells you which publication requirements it fails. It checks colorblind-safe color, composition, and whether your type is still legible at the size the figure actually prints.
audit(fig) returns (ok, rows), 21 rows, one per check. Each row is a
(name, status, detail) triple:
ok, rows = audit(fig) # (False, [("Clipping", False, "clipped: [...]"), ...])
figure-gate verifies figures. It does not draw them, restyle them, or judge whether a figure is good. Each check forbids one named defect, so a figure that passes every row has avoided 21 named defects and nothing more.
Every threshold is a module-level constant you can read and change.
Try it
git clone https://github.com/narenp12/figure-gate && cd figure-gate
python skill/scripts/check_palette.py "#E69F00,#56B4E9,#009E73" --pairs all
python skill/scripts/check_figure.py     # self-test on a deliberately broken figure
The second command prints a failing report and exits 0, because a checker that cannot fail is not a checker.
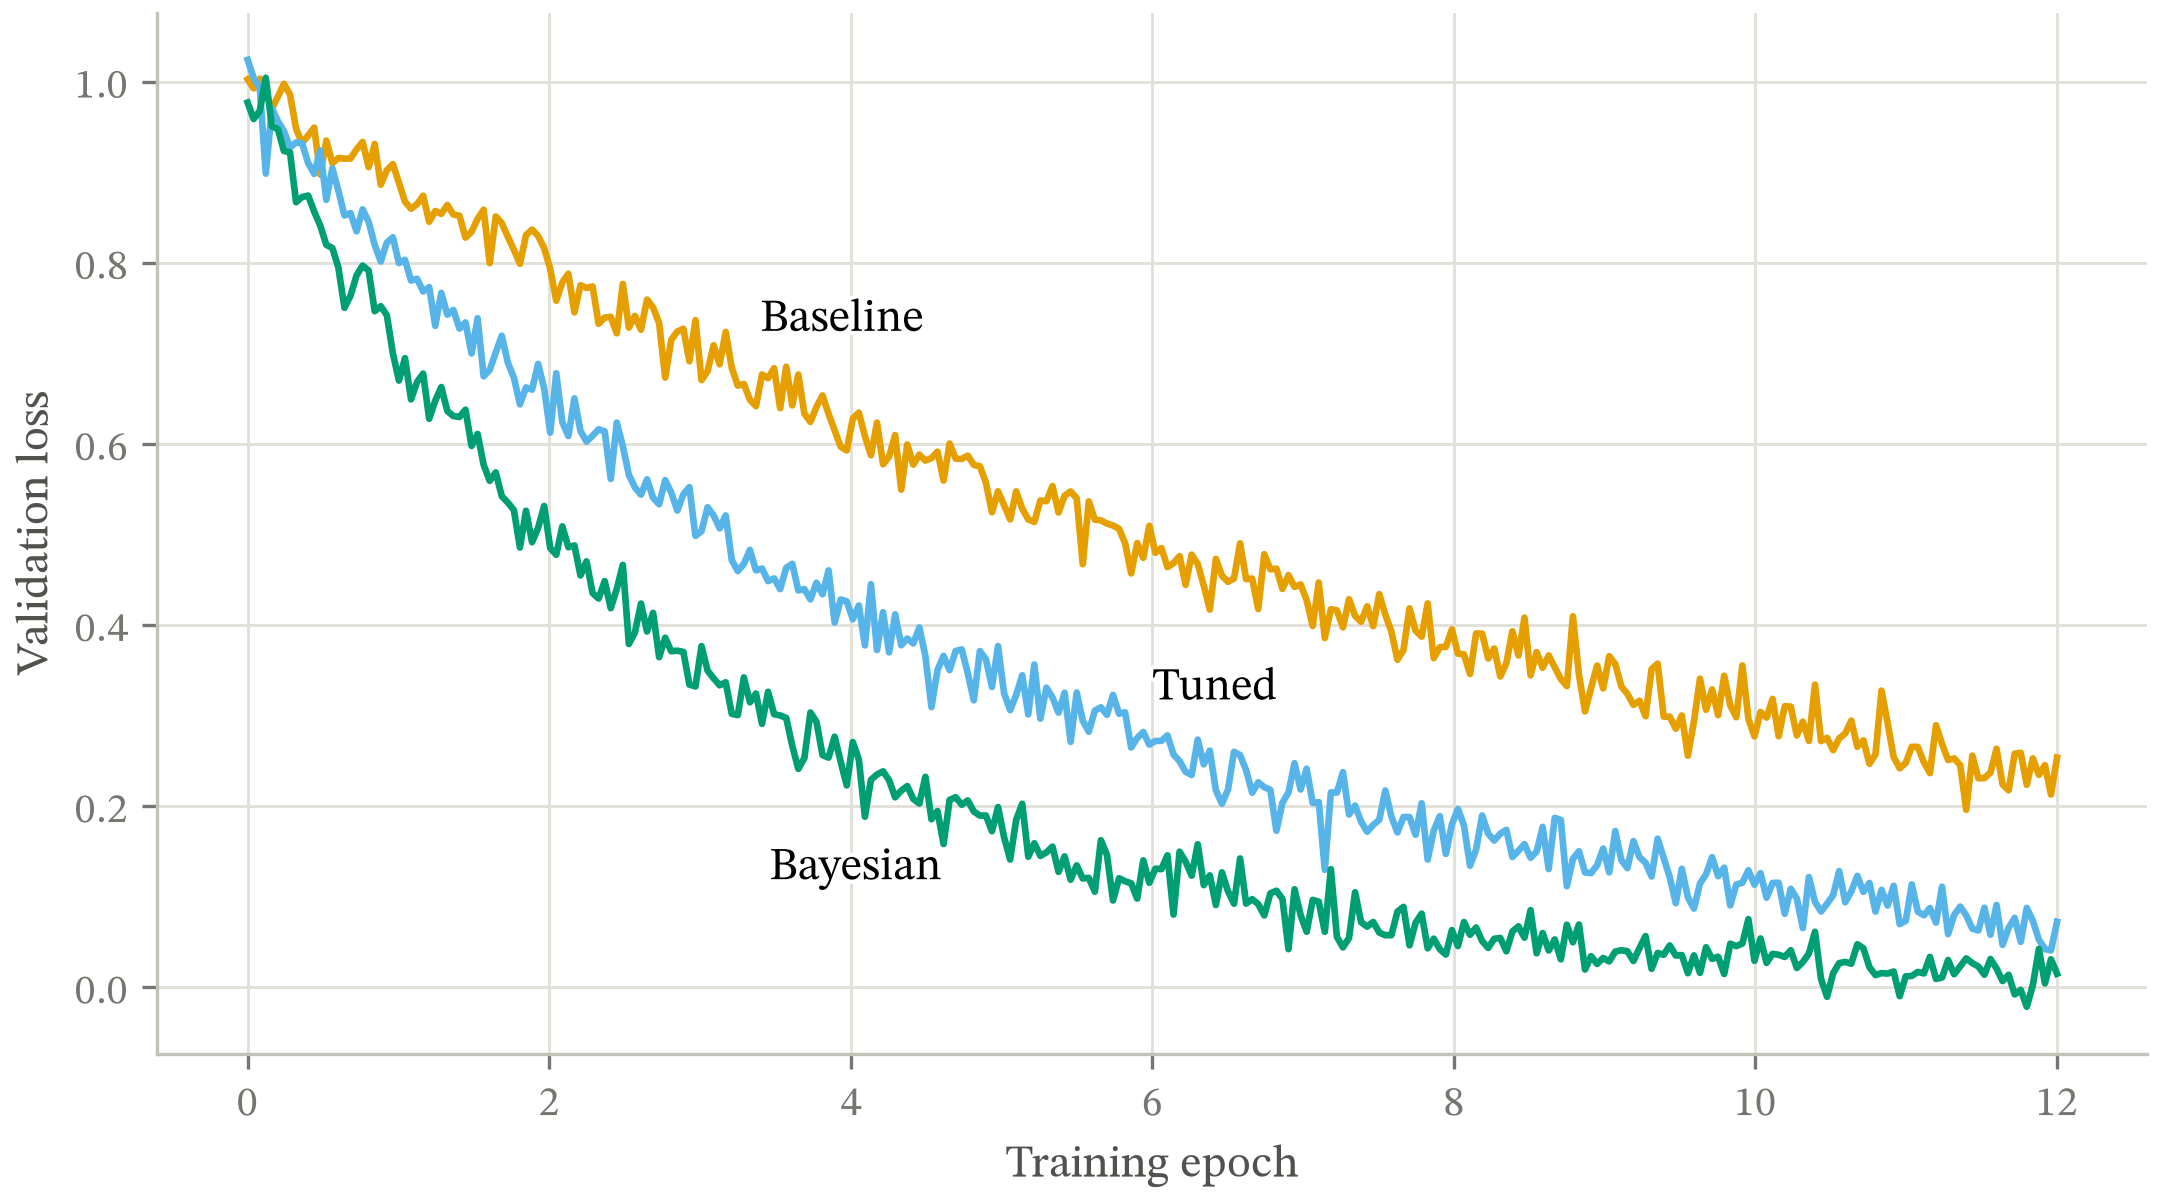
python examples/demo.py builds that figure and audits it, and
python examples/gallery.py covers the harder forms. Writing those twenty
found nine defects in the checks themselves.
Documentation
The documentation site is organised by what you came to do.
Learning. Start here if you have not run the checkers before:
- Gate your first figure — build a figure that fails, read the report, make it pass
Doing a task. Step-by-step directions for a goal you already have:
- Install figure-gate — copy the scripts, install the package, or install from conda-forge
- How-to guides — fix a failing row, gate a test suite, place at half width, attach alt text
Looking something up. What each check measures and what each function takes:
- The gates — every row, its threshold, and whether it can fail a build
- Commands — both command-line tools, their flags, and their exit codes
- Compatibility — Python and matplotlib floors, optional dependencies, import lines by version
- API reference — signatures and defaults, generated from the scripts when the site builds
Understanding why. Background, evidence, and the decisions behind the thresholds:
- How the checkers decide — the measurement model, the evidence, and what a passing run does not mean
- Figure style guide — the measurement behind each threshold, and the rules tried and reverted
- Choosing a form — the decision no styling rule rescues, built on Cleveland and McGill's ordering
- Gallery — twenty audited figures covering the forms that are hard to check
Use it with Claude Code
This repository is also a plugin marketplace, so Claude Code applies the same checks when it builds a figure for you:
/plugin marketplace add narenp12/figure-gate
Then run /plugin install figure-gate@figure-gate. The skill is invoked as
figure-gate:research-figures.
Where this sits
Prescriptive style sheets already exist and are good: SciencePlots and LovelyPlots for journal looks, tueplots and mpl_sizes for exact conference sizing. Accessibility tooling exists too: matplotalt generates alt text, Chart4Blind converts a chart image into an accessible one, and contrast reporters check colors in isolation.
Each of those acts before or beside the figure. None of them reads the built result and reports what it fails, which is the only thing figure-gate does. A style sheet and figure-gate are complementary: set your defaults with one, verify them with the other.
Stability
The public API is every name without a leading underscore in check_figure.py,
check_palette.py, and suggest_fixes.py. Below version 1.0, a minor release
may break it. Every break is named in
the changelog
under its release heading, and CI fails a pull request whose ## Unreleased
section does not name a symbol that moved.
The number of rows is not part of the contract. The shape is. For the full statement, see how the checkers decide.
Contributing
New gates are welcome at the bar the project holds itself to:
- A test proving the gate fails on a figure with that defect.
- A test proving it does not over-fire on the nearest legitimate case.
- A note naming the real failure that motivated it.
See CONTRIBUTING.md and SECURITY.md.
License
MIT. See LICENSE.
1 maintainer

Metadata
1 maintainer
Release files for figure-gate 0.9.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| figure_gate-0.9.0.tar.gz | 3.7 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| figure_gate-0.9.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 3.8 MB
Release files / figure_gate-0.9.0.tar.gz
| Download URL | figure_gate-0.9.0.tar.gz |
|---|---|
| Size | 3.7 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
595ff68ee63541d693c6fc6ceae47402df2bc68f2f5610985acc97aef7a8f4a7
|
|
BLAKE2b-256 checksum How to use checksums |
cacb46fcf19b33a4ff04b9af984a0a197a3f5a2166dee93a7af9d8489140b871
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / figure_gate-0.9.0-py3-none-any.whl
| Download URL | figure_gate-0.9.0-py3-none-any.whl |
|---|---|
| Size | 108.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f9d601a4b59b620d898fca1cd130ac2dfbc204cadb646d63b335dca114720f69
|
|
BLAKE2b-256 checksum How to use checksums |
d8acac6d99215f85e1d4442d764b3fbdbf9896826d48c85e5ae8be1d9c732d76
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency log













