

Code scanning at ludicrous speed.


Semgrep is a fast, open-source, static analysis tool that searches code, finds bugs, and enforces secure guardrails and coding standards. Semgrep supports 30+ languages and can run in an IDE, as a pre-commit check, and as part of CI/CD workflows.
Semgrep is semantic grep for code. While running grep "2" would only match the exact string 2, Semgrep would match x = 1; y = x + 1 when searching for 2. Semgrep rules look like the code you already write; no abstract syntax trees, regex wrestling, or painful DSLs.
Note that in security contexts, Semgrep Community Edition will miss many true positives as it can only analyze code within the boundaries of a single function or file. If you want to use Semgrep for security purposes (SAST, SCA, or secrets scanning), the Semgrep AppSec Platform is strongly recommended since it adds the following critical capabilities:
- Improved core analysis capabilities (cross-file, cross-function, data-flow reachability) that greatly reduce false positives by 25% and increase detected true positives by 250%
- Contextual post-processing of findings with Semgrep Assistant (AI) to further reduce noise by ~20%. In addition, Assistant enriches findings with tailored, step-by-step remediation guidance that humans find actionable >80% of the time.
- Customizable policies and seamless integration into developer workflows, giving security teams granular control over where, when, and how different findings are presented to developers (IDE, PR comment, etc.)
The Semgrep AppSec Platform works out-of-the-box with 20000+ proprietary rules across SAST, SCA, and secrets. Pro rules are written and maintained by the Semgrep security research team and are highly accurate, meaning AppSec teams can feel confident bringing findings directly to developers without slowing them down.
Semgrep analyzes code locally on your computer or in your build environment: by default, code is never uploaded. Get started →.
Language support
Semgrep Code supports 30+ languages, including:
Apex · Bash · C · C++ · C# · Clojure · Dart · Dockerfile · Elixir · HTML · Go · Java · JavaScript · JSX · JSON · Julia · Jsonnet · Kotlin · Lisp · Lua · OCaml · PHP · Python · R · Ruby · Rust · Scala · Scheme · Solidity · Swift · Terraform · TypeScript · TSX · YAML · XML · Generic (ERB, Jinja, etc.)
Semgrep Supply Chain supports 12 languages across 15 package managers, including:
C# (NuGet) · Dart (Pub) · Go (Go modules, go mod) · Java (Gradle, Maven) · Javascript/Typescript (npm, Yarn, Yarn 2, Yarn 3, pnpm) · Kotlin (Gradle, Maven) · PHP (Composer) · Python (pip, pip-tool, Pipenv, Poetry) · Ruby (RubyGems) · Rust (Cargo) · Scala (Maven) · Swift (SwiftPM)
For more information, see Supported languages.
Getting started 🚀
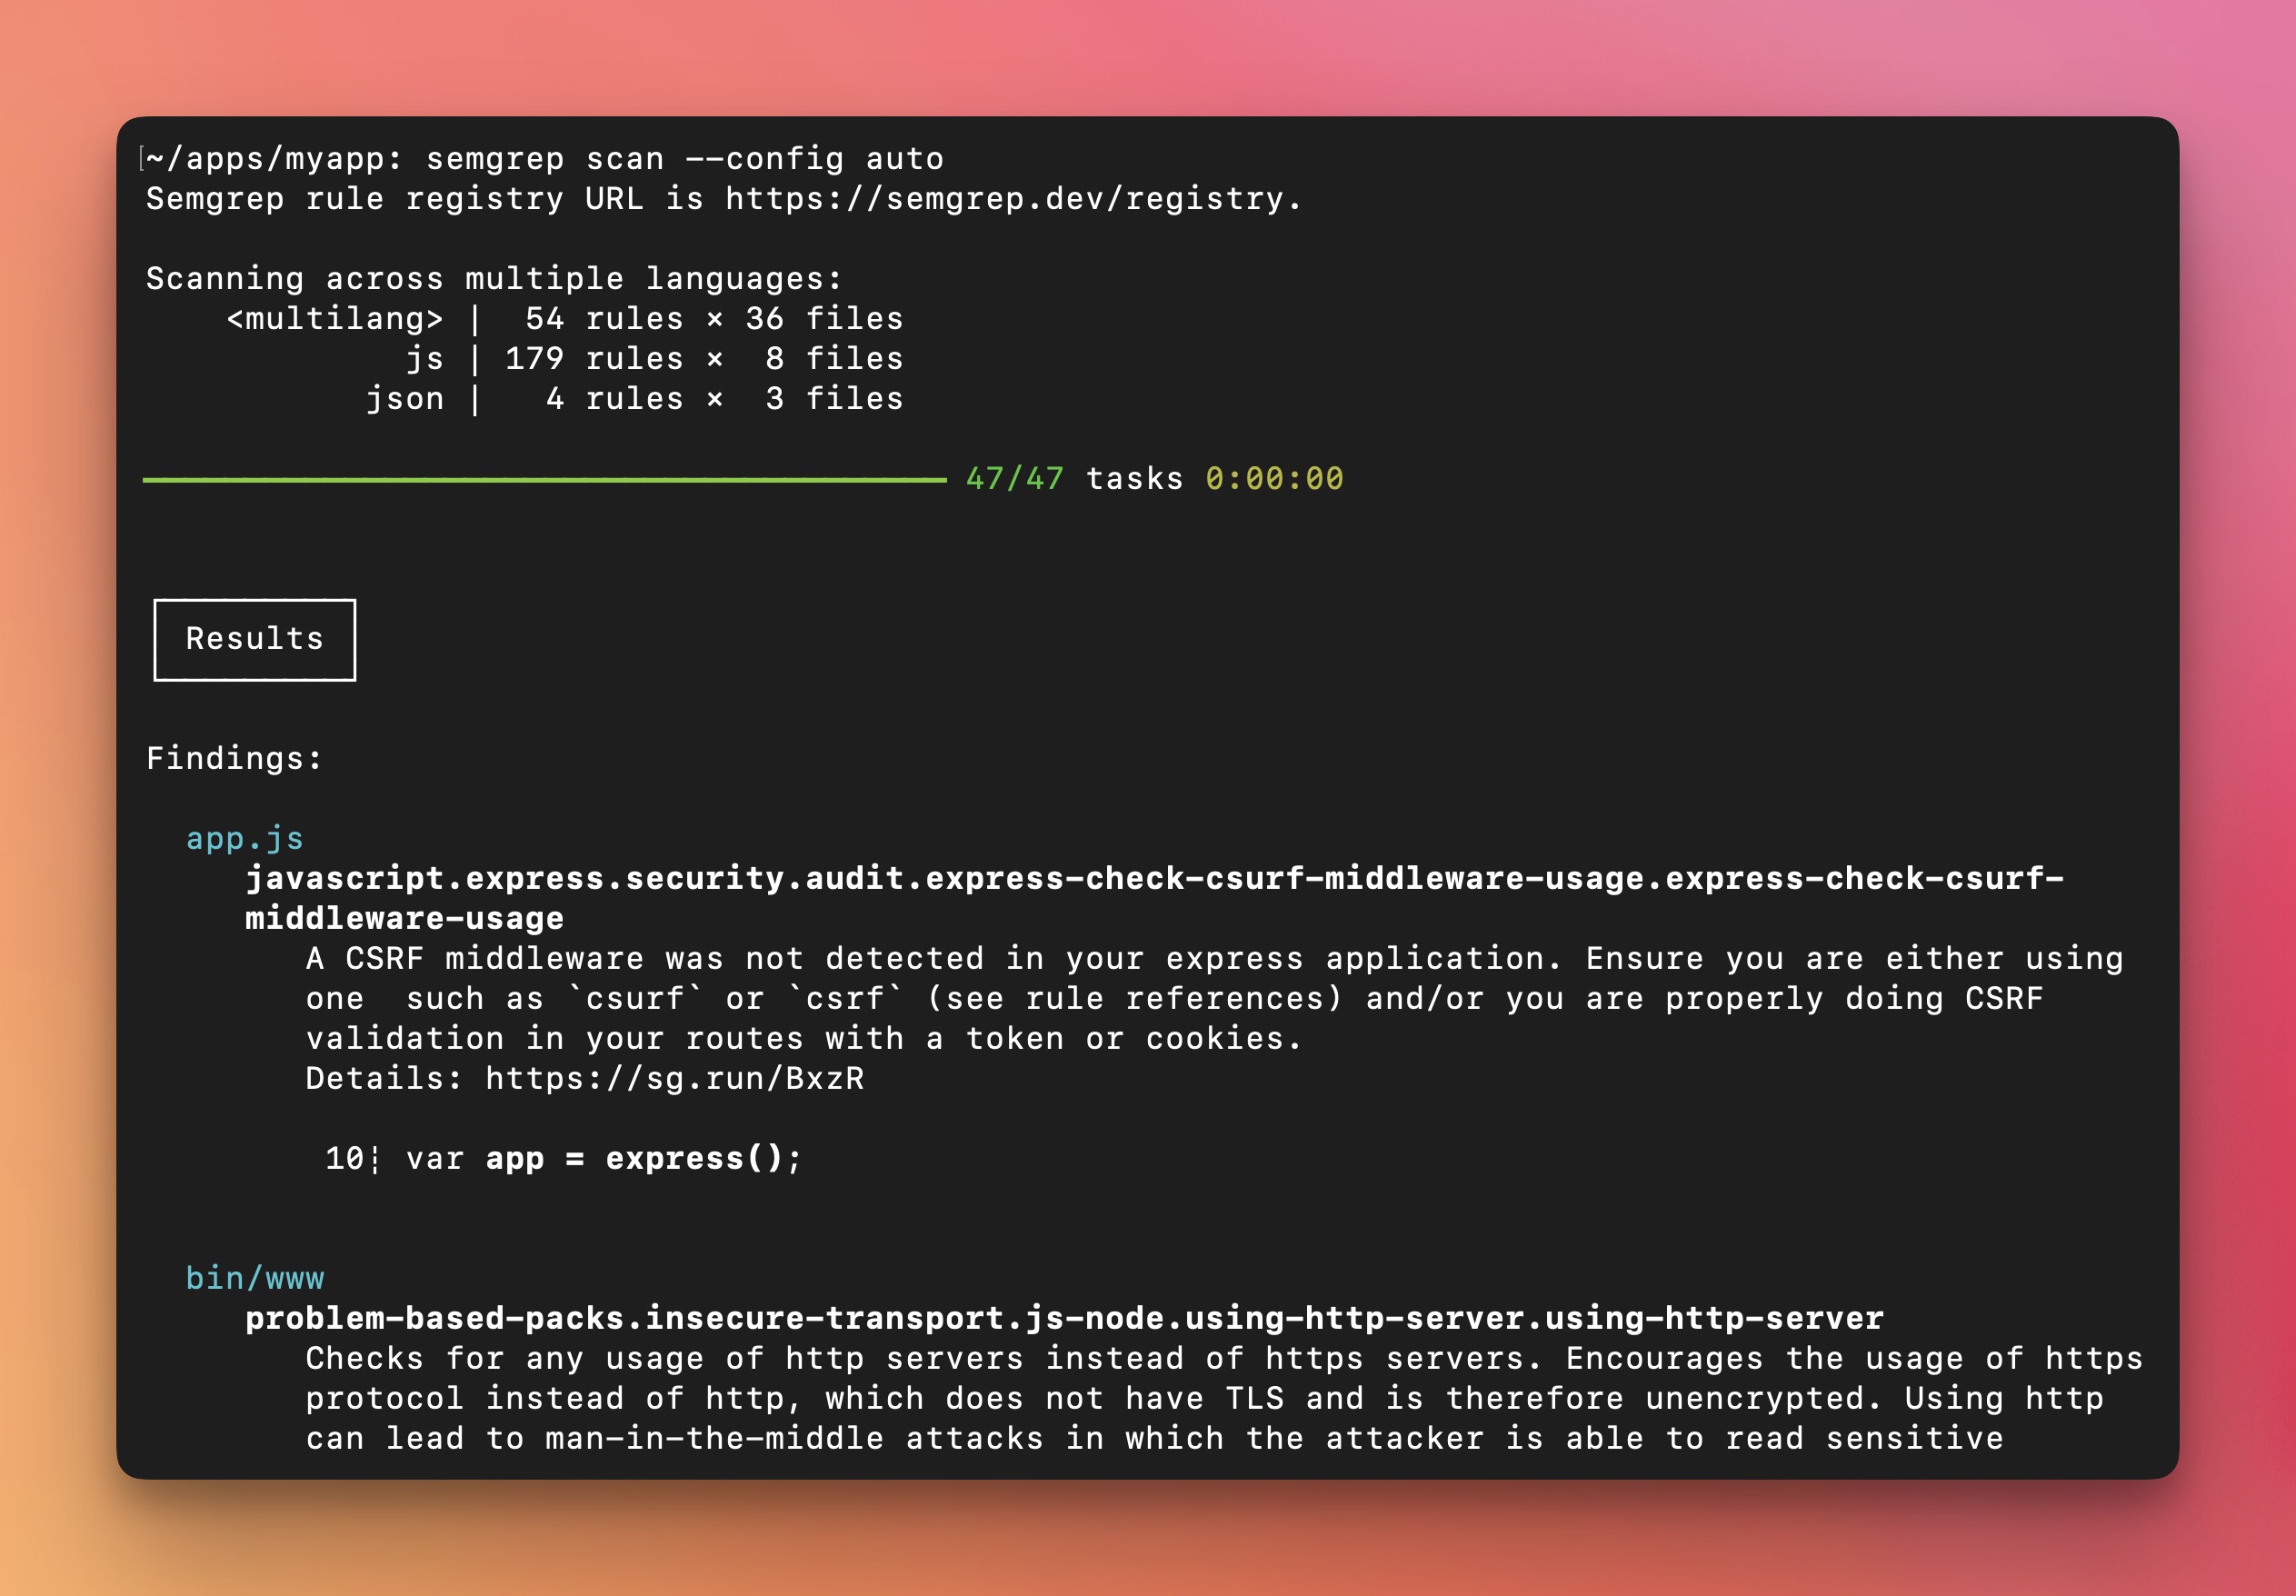
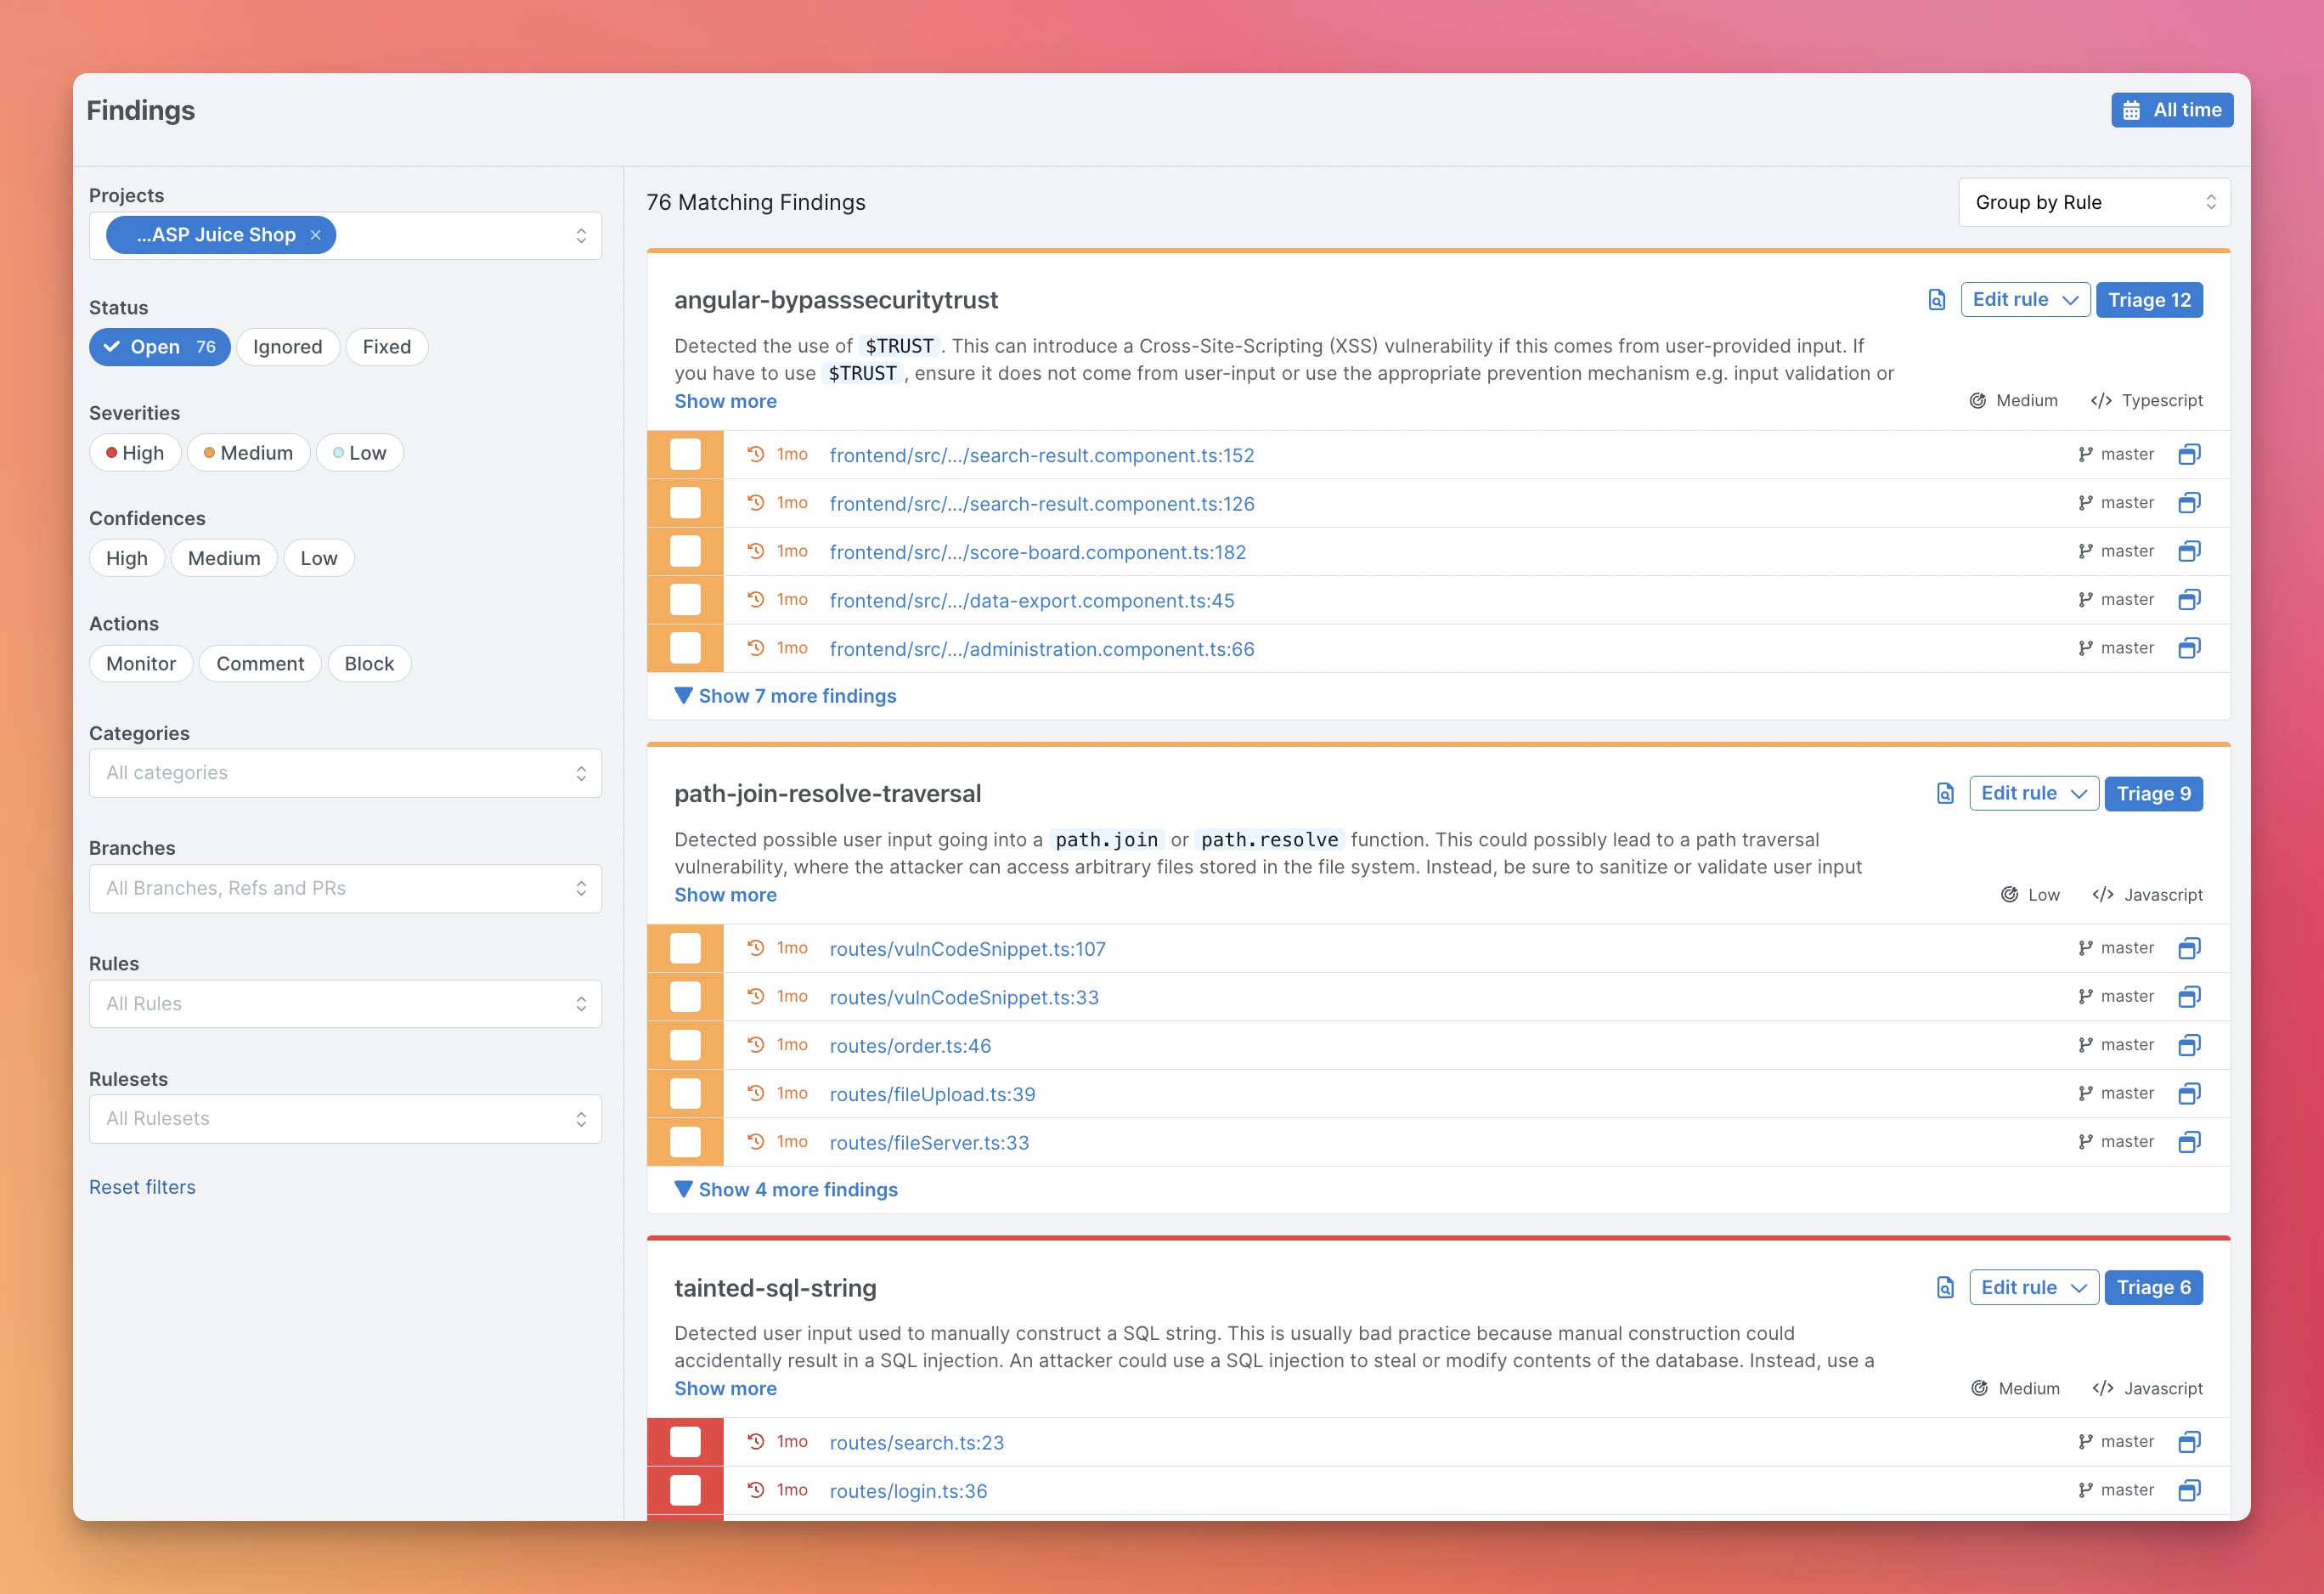
For new users, we recommend starting with the Semgrep AppSec Platform because it provides a visual interface, a demo project, result triaging and exploration workflows, and makes setup in CI/CD fast. Scans are still local and code isn't uploaded. Alternatively, you can also start with the CLI and navigate the terminal output to run one-off searches.
Option 1: Getting started from the Semgrep Appsec Platform (Recommended)
-
Register on semgrep.dev
-
Explore the demo findings to learn how Semgrep works
-
Scan your project by navigating to
Projects > Scan New Project > Run scan in CI -
Select your version control system and follow the onboarding steps to add your project. After this setup, Semgrep will scan your project after every pull request.
-
[Optional] If you want to run Semgrep locally, follow the steps in the CLI section.
Notes:
If there are any issues, please ask for help in the Semgrep Slack.
Option 2: Getting started from the CLI
-
Install Semgrep CLI
# For macOS # preferred: install through pipx (https://pipx.pypa.io/stable/how-to/install-pipx.html) pipx install semgrep # preferred: install through uv (https://docs.astral.sh/uv/getting-started/installation/) uv tool install semgrep # best-effort: install through homebrew (maintained on a best-effort basis; often lags behind the latest release) brew install semgrep # For Ubuntu/WSL/Linux/macOS $ python3 -m pip install semgrep # To try Semgrep without installation run via Docker $ docker run -it -v "${PWD}:/src" semgrep/semgrep semgrep login $ docker run -e SEMGREP_APP_TOKEN=<TOKEN> --rm -v "${PWD}:/src" semgrep/semgrep semgrep ci -
Run
semgrep loginto create your account and login to Semgrep. This step is optional, but logging into Semgrep gets you access to:- Semgrep Supply Chain: A dependency scanner that detects reachable vulnerabilities in third party libraries
- Semgrep Code's Pro rules: 600+ high confidence rules written by Semgrep's security research team
- Semgrep Code's Pro engine: An advanced code analysis engine, designed to detect complex vulnerabilities, and reduce false positives
-
Go to your app's root directory and run
semgrep ci. This will scan your project to check for vulnerabilities in your source code and its dependencies. -
Try writing your own query interactively with
-e. For example, a check for Python == where the left and right hand sides are the same (potentially a bug):$ semgrep -e '$X == $X' --lang=py path/to/src
Semgrep Ecosystem
The Semgrep ecosystem includes the following:
-
Semgrep Community Edition - The open-source program analysis engine at the heart of everything. Suitable for ad-hoc use cases with a high tolerance for false positives - think consultants, security auditors, or pentesters.
-
Semgrep AppSec Platform - Easily orchestrate and scale SAST, SCA, and Secrets scanning across an organization, with no risk of overwhelming developers. Customize which findings developers see, where they see them, and integrate with CI providers like GitHub, GitLab, CircleCI, and more. Includes both free and paid tiers.
-
Semgrep Code (SAST) - Make real progress on your vulnerability backlog with SAST that minimizes noise and empowers developers to quickly fix issues on their own, even if they have no security knowledge. Easy to deploy secure guardrails and tailored, step-by-step remediation guidance mean developers actually fix issues since they don't feel slowed down.
-
Semgrep Supply Chain (SSC) - A high-signal dependency scanner that detects reachable vulnerabilities in open source third-party libraries and functions.
-
Semgrep Secrets (Secrets scanning) - Secrets detection that uses semantic analysis, improved entropy analysis, and validation to accurately surface sensitive credentials in the developer workflow.
-
Semgrep Assistant (AI) - Assistant is an AI-powered AppSec engineer that helps both developers and AppSec teams prioritize, triage, and remediate Semgrep findings at scale. Humans agree with Assistant auto-triage decisions 97% of the time, and rate generated remediation guidance as helpful 80% of the time. For an overview of how Assistant works, read this overview.
-
-
Semgrep MCP Server - A Model Context Protocol (MCP) server that lets AI coding assistants run Semgrep scans directly. Integrates with Cursor, VS Code, Windsurf, Claude Desktop, and more. Run
semgrep mcpto start it locally.- Hooks - Automatically trigger Semgrep scans as you code.
- Skills / Prompts - Built-in MCP prompts like
write_custom_semgrep_rulehelp AI assistants write accurate Semgrep rules. - Claude Code plugin - Available on the official marketplace and via the semgrep/mcp-marketplace repo:
/plugin marketplace add semgrep/mcp-marketplace - Cursor plugin - Available on the official marketplace and via the semgrep/cursor-plugin repo.
Additional resources:
- Semgrep Playground - An online interactive tool for writing and sharing rules.
- Semgrep Registry - 2,000+ community-driven rules covering security, correctness, and dependency vulnerabilities.
Join hundreds of thousands of other developers and security engineers already using Semgrep at companies like GitLab, Dropbox, Slack, Figma, Shopify, HashiCorp, Snowflake, and Trail of Bits.
Semgrep is developed and commercially supported by Semgrep, Inc., a software security company.
Semgrep Rules
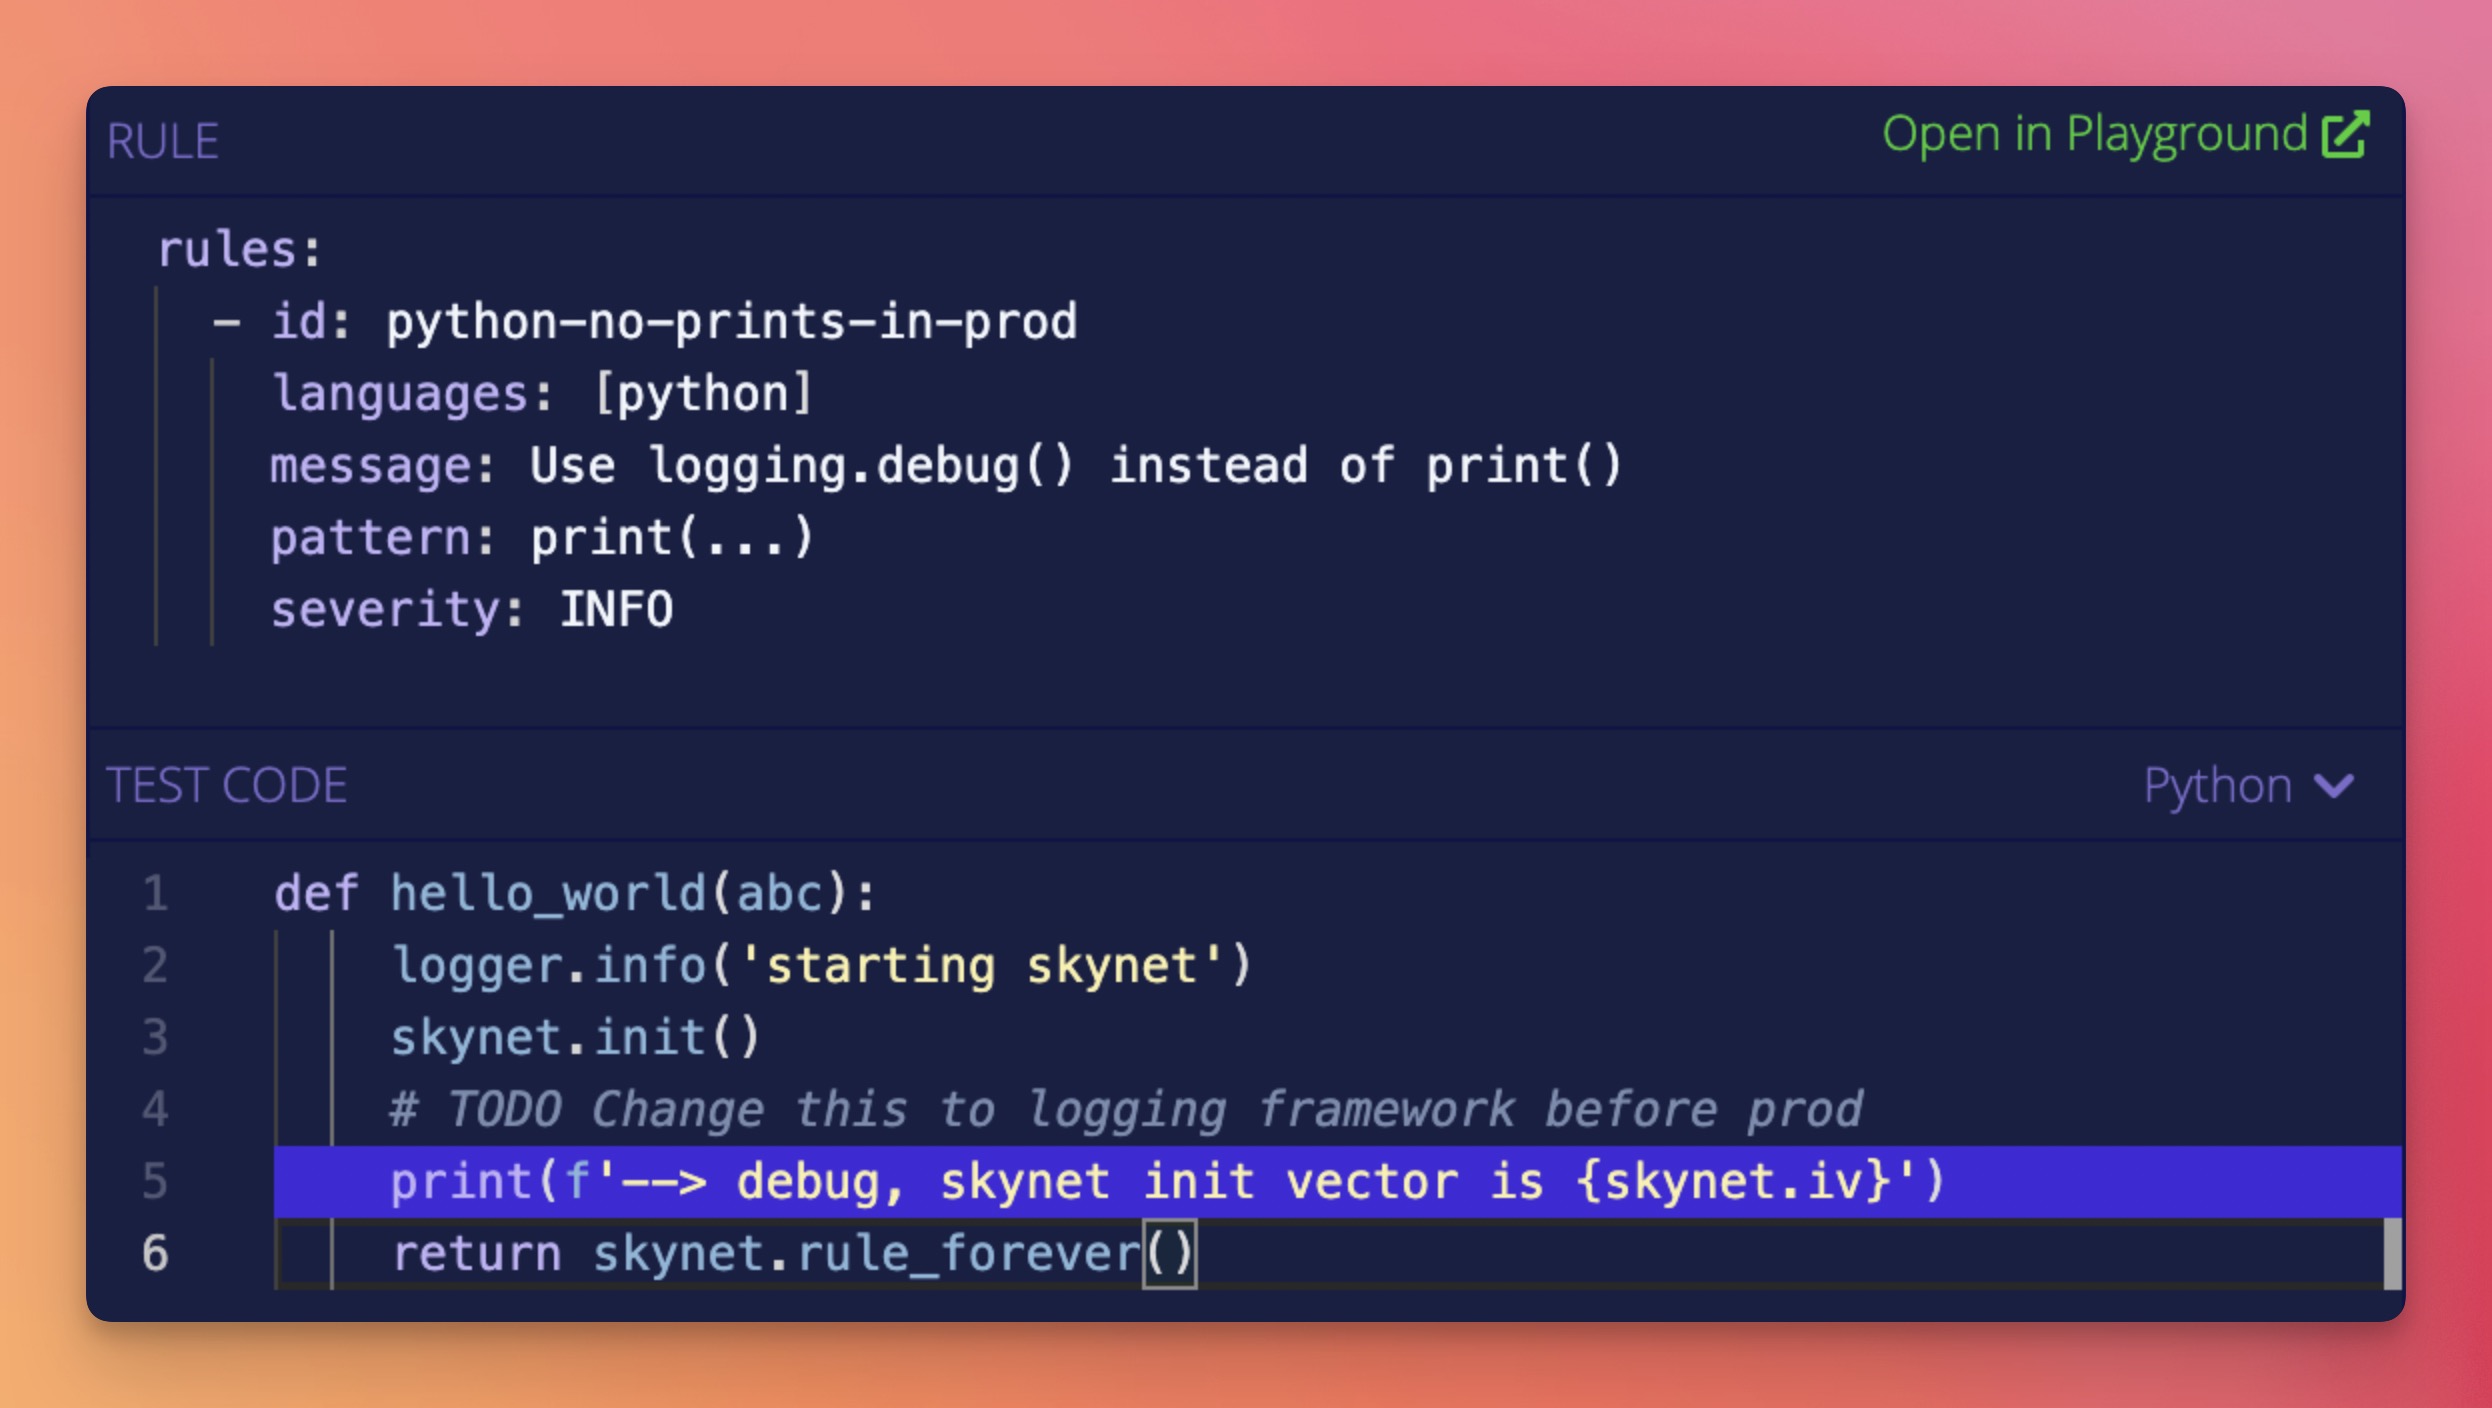
Semgrep rules look like the code you already write; no abstract syntax trees, regex wrestling, or painful DSLs. Here's a quick rule for finding Python print() statements.
Run it online in Semgrep’s Playground by clicking here.
Examples
Visit Docs > Rule examples for use cases and ideas.
| Use case | Semgrep rule |
|---|---|
| Ban dangerous APIs | Prevent use of exec |
| Search routes and authentication | Extract Spring routes |
| Enforce the use secure defaults | Securely set Flask cookies |
| Tainted data flowing into sinks | ExpressJS dataflow into sandbox.run |
| Enforce project best-practices | Use assertEqual for == checks, Always check subprocess calls |
| Codify project-specific knowledge | Verify transactions before making them |
| Audit security hotspots | Finding XSS in Apache Airflow, Hardcoded credentials |
| Audit configuration files | Find S3 ARN uses |
| Migrate from deprecated APIs | DES is deprecated, Deprecated Flask APIs, Deprecated Bokeh APIs |
| Apply automatic fixes | Use listenAndServeTLS |
Extensions
Visit Docs > Extensions to learn about using Semgrep in your editor or pre-commit. When integrated into CI and configured to scan pull requests, Semgrep will only report issues introduced by that pull request; this lets you start using Semgrep without fixing or ignoring pre-existing issues!
Documentation
Browse the full Semgrep documentation on the website. If you’re new to Semgrep, check out Docs > Getting started or the interactive tutorial.
Metrics
Using remote configuration from the Registry (like --config=p/ci) reports pseudonymous rule metrics to semgrep.dev.
When using configs from local files (like --config=xyz.yml), metrics are sent only when the user is logged in.
To disable Registry rule metrics, use --metrics=off.
The Semgrep privacy policy describes the principles that guide data-collection decisions and the breakdown of the data that are and are not collected when the metrics are enabled.
More
- Frequently asked questions (FAQs)
- Contributing
- Build instructions for developers
- Ask questions in the Semgrep community Slack
- CLI reference and exit codes
- Semgrep YouTube channel
- License (LGPL-2.1)
- Licensing Semgrep
Upgrading
To upgrade, run the command below associated with how you installed Semgrep:
# Using pipx
$ pipx upgrade semgrep

# Using uv tool command
$ uv tool upgrade semgrep

# Using Homebrew
$ brew upgrade semgrep

# Using Docker
$ docker pull semgrep/semgrep:latest


Release files for semgrep 1.185.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| semgrep-1.185.0.tar.gz | 545.0 kB | With provenance | Details for semgrep-1.185.0.tar.gz |
Built distributions (wheels)
Total release size: 418.5 MB
Release files / semgrep-1.185.0.tar.gz
| Download URL | semgrep-1.185.0.tar.gz |
|---|---|
| Size | 545.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
e6fa06ae6262b13b6ef14dd634e2b7d97ccc51ff41b94da59b63862d0c8578af
|
|
BLAKE2b-256 checksum How to use checksums |
7882530228c094e10e658ba323852b169ce807f8ce826384095f89c5e5a34482
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logRelease files / semgrep-1.185.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-win_amd64.whl
| Download URL | semgrep-1.185.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-win_amd64.whl |
|---|---|
| Size | 59.6 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
91812ac0856cfe5b6135a4dffde3052a04c36a46e4e82e78793e3a07e51d7894
|
|
BLAKE2b-256 checksum How to use checksums |
8e8ec8d5135ff77a60e825c08b68272a924572e59841d01beba29be7041d2c75
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logRelease files / semgrep-1.185.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_x86_64.whl
| Download URL | semgrep-1.185.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 79.0 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Linux musl 1.2+ x86-64 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 |
|
SHA-256 checksum How to use checksums |
f030c391af948b493ae2220a1b64372df5f18adf8e2dd909ab62035364c51890
|
|
BLAKE2b-256 checksum How to use checksums |
fb60e0557977f9b0ae3a5158e2a311c35f8ed59359cac2788bb3c6dc461de3dc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logRelease files / semgrep-1.185.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_aarch64.whl
| Download URL | semgrep-1.185.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 81.4 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Linux musl 1.2+ ARM64 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 |
|
SHA-256 checksum How to use checksums |
99fde53fda44c25d8ab27424f421947b0a0186d86ce888c593a6da62b811d783
|
|
BLAKE2b-256 checksum How to use checksums |
c64e77b2128d3a7f2e1f9abbeb4b0d7f9f59957663b6aa01a9b2e0f4d1c1b915
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logRelease files / semgrep-1.185.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_x86_64.whl
| Download URL | semgrep-1.185.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_x86_64.whl |
|---|---|
| Size | 72.3 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Linux glibc 2.34+ x86-64 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 |
|
SHA-256 checksum How to use checksums |
0eb6aaadad5b957af96d1300487e10af1dc8016e8ef53072effb48cd4906c02b
|
|
BLAKE2b-256 checksum How to use checksums |
f2130d4dc8d124794105f300082c46e3d8ad45eac7af63113b57a5966629b5a3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logRelease files / semgrep-1.185.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_aarch64.whl
| Download URL | semgrep-1.185.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-manylinux_2_34_aarch64.whl |
|---|---|
| Size | 74.3 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Linux glibc 2.34+ ARM64 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 |
|
SHA-256 checksum How to use checksums |
8cffbaf80abb8e39abc6d7a86588dcf94b7ddc1f40e8e16e555a1116347be3ef
|
|
BLAKE2b-256 checksum How to use checksums |
ba4ecae05468e1b8c33a18bafb25539f845d6f35e6e58973ebdd2aafa6b387ed
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logRelease files / semgrep-1.185.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-macosx_11_0_arm64.whl
| Download URL | semgrep-1.185.0-cp310.cp311.cp312.cp313.cp314.py310.py311.py312.py313.py314-none-macosx_11_0_arm64.whl |
|---|---|
| Size | 51.3 MB |
| Tags | CPython 3.10 CPython 3.11 CPython 3.12 CPython 3.13 CPython 3.14 Python 3.10 Python 3.11 Python 3.12 Python 3.13 Python 3.14 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
d54c7dc22f6f360e0f9f850b1ecdfe00ec755600f9cf2ec6be3928b42818f1b4
|
|
BLAKE2b-256 checksum How to use checksums |
638a746b73f404709f89cecbd80f7dcd4e347b21353bfdea163cb23158d4593f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logSecurity for semgrep 1.185.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 7 files in this release have been uploaded with provenance metadata.
Attestation for semgrep-1.185.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














