
 |
skillsawKeep your skills sharp. A linter for the files that steer AI coding agents. |
|
|
|

Agent instructions behave like code, but most teams still review them like prose. skillsaw gives them a linter. It validates structure across every major AI coding ecosystem, guards against many supply-chain attacks, and applies content and context rules backed by research and frontier lab guidance.
It understands Agent Skills,
Agent Plugins v1, Claude Code
plugins, OpenAI Codex plugins and marketplaces, CLAUDE.md, AGENTS.md,
GEMINI.md, QWEN.md, Cursor plugins and marketplaces, Copilot, Cline, Devin, Kiro, OpenCode, Goose recipes, Muse Code, Pi,
Grok Build, Google Antigravity, native OpenClaw plugins, hooks, agent configuration, MCP Registry
server.json publisher metadata,
Vercel skills CLI lockfiles, and eval formats. Safe structural fixes can be applied
automatically; everything else comes with precise, agent-friendly guidance.
Get started | Browse the rules | Read the documentation
See it work
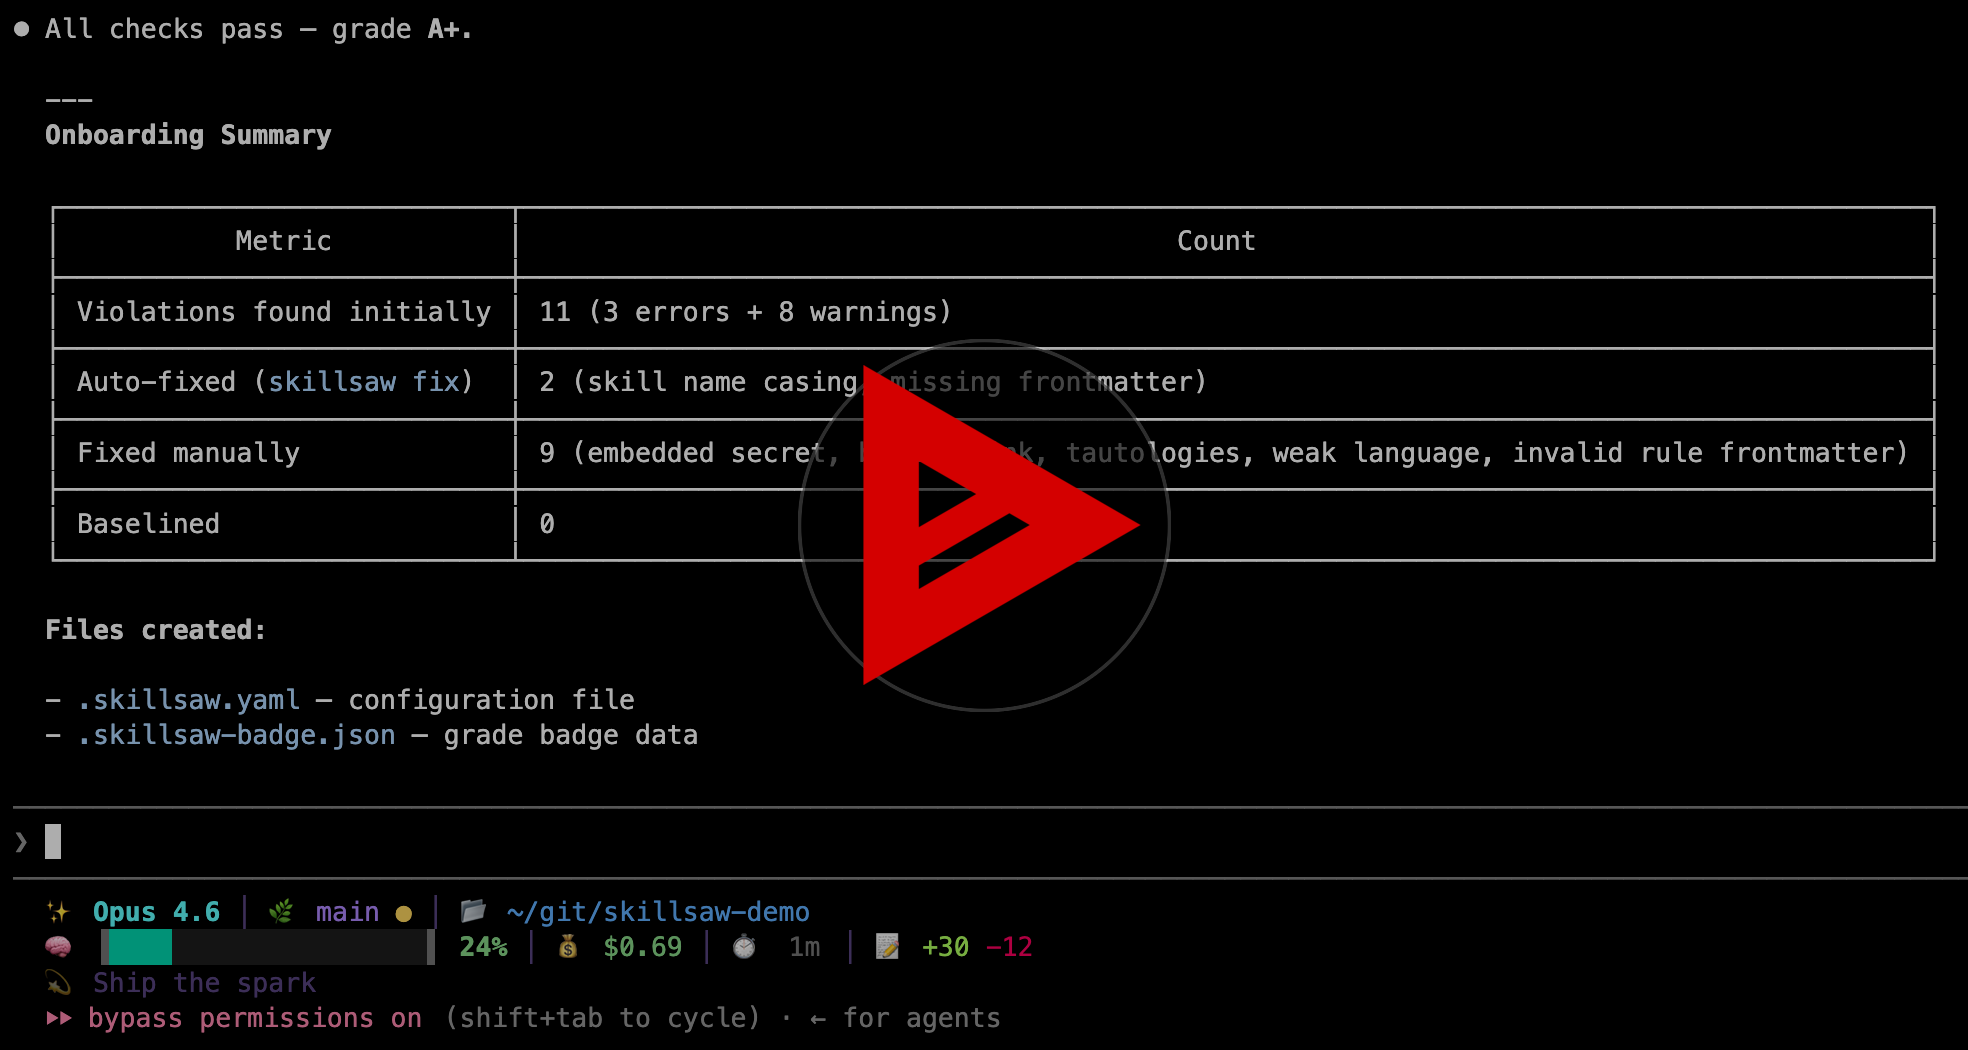
Watch an AI agent grade, fix, and configure a repository from scratch.
Try it
Paste this into your coding agent to onboard skillsaw now:
Read and follow the instructions at
https://raw.githubusercontent.com/stbenjam/skillsaw/refs/heads/main/skills/skillsaw-onboard/SKILL.md
to onboard this repo to skillsaw.
Or install the onboarding skill for regular use (recommended). Run this from the repository you want to lint:
npx skills add stbenjam/skillsaw
Select skillsaw-onboard and your coding agent, then ask the agent to use
that skill to onboard the repo. See Onboard with AI
for plugin installation alternatives.
Or run it yourself. No installation is required with
uvx:
uvx skillsaw tree      # See what skillsaw detects
uvx skillsaw           # Lint the current repository
uvx skillsaw fix       # Apply safe, deterministic fixes
uvx skillsaw baseline  # Accept existing findings and fail only on new ones
For lint --fail-on info, use baseline --include-info to accept existing
INFO findings too. A configured fail-on: info includes them automatically.
Goose recipes under .goose/recipes/ receive shared content and MCP security
checks. Enable the optional recipe checks for standalone recipe directories with:
uvx skillsaw lint my-recipes --type goose --rule goose-recipe-valid --rule goose-subrecipe-references
See Goose recipe support for discovery, path resolution and validation limits.
What it catches
- Multi-ecosystem structure & compatibility: schema, frontmatter, and manifest validation for Agent Skills (
SKILL.md), Claude Code, OpenAI Codex (project config, plugins & marketplaces), Cursor plugins & marketplaces, Grok Build (project config, plugins & marketplaces), Google Antigravity (configuration in any customization root —.agents/,.agent/,_agents/,_agent/— itsrules/andagents/prose, plugins, hooks, MCP servers and registries), Agent Plugins v1 (plugin.json,mcp.json), GitHub Copilot & VS Code custom agents (.github/agents/), OpenCode configuration, Pi packages and project resources, native OpenClaw plugins (including optional theme and artwork declarations), APM packages, MCP server maps, and MCP Registry metadata. - Content quality & token economy: research-backed rules detecting instruction drift across duplicate files, excessive instruction budgets, cognitive overload, section length violations, weak language, contradictions, and repetitive inline tool-call examples.
- Discovery & repository integrity: unreferenced bundled files, broken internal file references, inconsistent terminology, missing stop conditions, and stale baselines.
- Security & supply chain:
- Dangerous lifecycle hooks: blocks arbitrary remote code execution, download-and-execute (
curl | sh,wget | bash), and script obfuscation (eval) inhooks.jsonand settings. - Prohibited & unvetted MCP servers: enforces strict MCP allowlists across root, plugin, and custom agent configurations.
- Prompt injection & stealth payloads: detects invisible Unicode (ASCII smuggling, zero-width tags, bidi overrides), high-entropy encoded payloads (base64/hex), and hidden instructions in comments and code fences.
- Environment & context security: flags dangerous environment overrides (
LD_PRELOAD,NODE_OPTIONS,PYTHONPATH), unallowlisted dynamic context injection, and embedded credentials.
- Dangerous lifecycle hooks: blocks arbitrary remote code execution, download-and-execute (
- Deterministic autofixes: safe, instant automated fixes for invalid frontmatter, broken headings, missing manifests, unclosed code fences, and schema keys via
skillsaw fix.
skillsaw detects repository types automatically and lints multiple formats in the same project. See supported repository types and the complete rule reference for details.
Pi packages and .pi/ project resources are supported, including native skills,
prompt templates, manifest globs, local package references, and first-party
.pi/mcp.json servers. Shared MCP credential and policy checks cover these
servers; enable pi-mcp-valid for Pi 1.0 field validation, including
oauth.authServerMetadataUrl. See
Pi configuration checks and
Pi MCP checks.
Built for real workflows
skillsaw works locally, in CI, and inside coding-agent workflows. It provides
line-level findings, explanations for every rule, deterministic autofixes,
baselines for gradual adoption, GitHub and GitLab integration, and text, JSON,
SARIF, HTML, and Code Climate output. Rules are configurable, and projects can
add local rules or install rule plugins. Typo'd or wrong-typed rule options
in .skillsaw.yaml are reported with did-you-mean suggestions instead of
being silently ignored.
| Goal | Documentation |
|---|---|
| Install and run skillsaw | Getting Started |
| Tune rules and exclusions | Configuration |
| Adopt it without fixing everything at once | Baselines |
| Review the security model | Supply Chain Protection |
| Supported ecosystems and tools | Repository Types |
| Add checks to pull requests & CI | CI Integration |
| Understand and apply fixes | Autofixing |
| Convert plugins to Agent Plugins v1 | Porting to Agent Plugins |
| Create project-specific checks | Custom Rules |
| Publish reusable rule packages | Rule Plugins |
| Inspect the typed parse tree | Lint Tree |
| Look up commands and flags | CLI Reference |
| Feed the docs to an AI agent | llms.txt index, llms-full.txt full docs |
Updating from 0.20? See the 0.21 upgrade guide for removed commands and rules, new opt-in checks, and Pi skill validation.
Codex portable plugins can place OpenAI metadata and hooks in
plugin.json under extensions.com.openai. Skillsaw follows that overlay's
precedence over .codex-plugin/plugin.json, validates its declared resources,
and checks portable skills/ and mcp.json through the Agent Plugins rules.
Project .codex/config.toml files also get a targeted warning
when an HTTP MCP server uses the ignored headers field instead of
http_headers or env_http_headers.
Measure the result
Every run produces a letter grade based on weighted violation density. The same data can be rendered as a self-contained report card for a README or project dashboard.
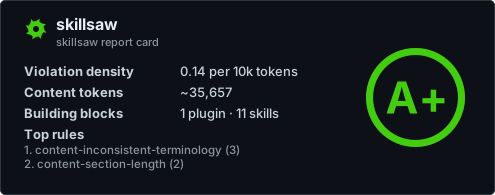
skillsaw's own report card, generated with skillsaw badge --large.
Learn how to generate a grade badge and report card for your project.
Contributing
Contributions are welcome. See CONTRIBUTING.md for the project guidelines and DEVELOPMENT.md for the local setup.
Questions and bug reports belong in GitHub
Issues. For a shareable diagnostic
bundle, run skillsaw feedback in the affected repository and review the ZIP
before attaching it to an issue. Files selected with --include or --config
are copied verbatim, including BOMs and line endings. Selections default to
4 MiB per file and 16 MiB total across distinct ZIP members; use positive byte
values with --max-file-bytes and --max-total-bytes to override these limits.
An oversized selection stops before diagnostic lint and creates no bundle.
These limits cover selected file bytes only, not diagnostic output or total
process memory. skillsaw is licensed under the Apache License 2.0.
Thank you to our contributors
skillsaw is better because people contribute code, bug reports, and ideas. Thank you!
| Contributors | |||
|---|---|---|---|
@alSergey |
@amy |
@btiernay |
@cblecker |
@cgwalters |
@ehelms |
@EmilienM |
@jeffreylo |
@jfchevrette |
@kannon92 |
@nyechiel |
@rajusem |
@skyth3r |
@stbenjam |
@tchughesiv |
@tyraziel |
@zerocodefast |
1 maintainer

Metadata
1 maintainer
Release files for skillsaw 0.22.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| skillsaw-0.22.0.tar.gz | 1.4 MB | With provenance | Details for skillsaw-0.22.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| skillsaw-0.22.0-py3-none-any.whl | Python 3 | none | any | Details for skillsaw-0.22.0-py3-none-any.whl |
Total release size: 2.4 MB
Release files / skillsaw-0.22.0.tar.gz
| Download URL | skillsaw-0.22.0.tar.gz |
|---|---|
| Size | 1.4 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
2d3621d8a5754bd60e8cca661b9dce904fa8e01fe4bab17a8358d6fca5516c1a
|
|
BLAKE2b-256 checksum How to use checksums |
b898a2853c5107dc257e13ac37661c31d009476d516babca88e35771ada2a82f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 16, 2026.
Transparency logRelease files / skillsaw-0.22.0-py3-none-any.whl
| Download URL | skillsaw-0.22.0-py3-none-any.whl |
|---|---|
| Size | 1.1 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
7c4b4f48961d9b1676831aeb65396ddc59a18efac39e505b0dfe500f4c055906
|
|
BLAKE2b-256 checksum How to use checksums |
88a4cc3c4c41717a3ce2d587b3cb386cc6e762ef6dfe1f97a8f7f5dec8c5c913
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 16, 2026.
Transparency logSecurity for skillsaw 0.22.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for skillsaw-0.22.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 16, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














