




Website: einarolafsson.github.io/projects/spacr
conda create -n spacr python=3.12 -y
conda activate spacr
python -m pip install spacr
spacr
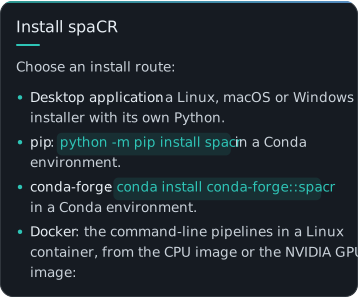
docker run --rm ghcr.io/einarolafsson/spacr:1.5.1.5 spacr-run --list
docker run --rm --gpus all ghcr.io/einarolafsson/spacr:1.5.1.5-cuda12.4 spacr-run --list
chmod +x SpaCR-*-Linux-x86_64-Online.run
./SpaCR-*-Linux-x86_64-Online.run
conda create -n spacr python=3.12 -y
conda activate spacr
python -m pip install --upgrade pip
python -m pip install spacr
spacr
python -m pip install spacr
spacr-run --list
conda create -n spacr python=3.12 -y
conda activate spacr
conda install conda-forge::spacr
spacr
git clone https://github.com/EinarOlafsson/spacr.git
cd spacr
conda create -n spacr python=3.12 -y
conda activate spacr
pip install -e .
spacr
git clone --branch v1.5.0.5 https://github.com/EinarOlafsson/spacr.git
git pull
pip install -e .
# One commit instead of every version: 2048 MB downloaded, 140 s.
# No history, so no git log, no git blame and no git bisect.
# git pull still works, but stays shallow until git fetch --unshallow.
git clone --depth 1 --branch nightly https://github.com/EinarOlafsson/spacr.git
cd spacr && pip install -e .

# Runtime files: 104 MB on disk, 6 s (Git: 38 MB; files: 66 MB).
# No history, docs, tests, tools, features or example data.
# --with-docs, --with-tests and --with-translations put those back;
# --dir, --branch, --no-install and --help do the obvious things.
# packaging/source_install_excludes.txt lists every skipped path.
curl -fsSL https://raw.githubusercontent.com/EinarOlafsson/spacr/nightly/packaging/install_from_source.sh -o install_spacr.sh
sh install_spacr.sh --branch nightly
spacr                                      # launch the Qt application
spacr-doctor                               # diagnose the installation
spacr-run --list                           # list headless modules
spacr-run --describe MODULE                # inspect a module contract
spacr-run MODULE --settings settings.csv   # execute a module
spacr-run validate --module MODULE \
    --settings settings.csv                # validate before running
spacr-repro RUN_DIR                        # replay a recorded run
spacr-download --list                      # what example data exists
spacr-download measure annotate            # fetch example sets by name
spacr-make-masks --folder DIR              # curate masks as a resumable queue
spacr-make-masks --folder DIR --order easy --limit 50

python tools/spacr_hardware_report.py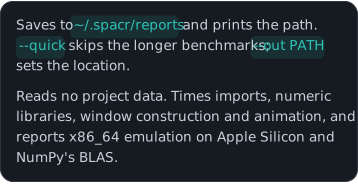
spacr              # the desktop application
spacr-tutorial     # the interactive tutorial library
spacr-server       # no first-run setup screen, for unattended launches
spacr-doctor       # diagnose the installation and say how to fix it
safespacr          # the least spaCR that can still change a setting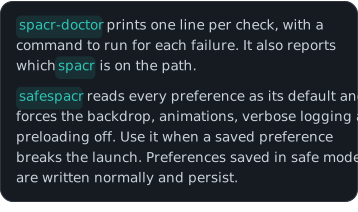
spacr-run --list                              # modules with a headless entry
spacr-run --describe MODULE                   # what a module consumes and produces
spacr-run validate --module MODULE \
    --settings settings.csv                   # check settings before spending the run
spacr-run MODULE --settings settings.csv      # execute
spacr-remote --help                           # submit and monitor SSH, Slurm or cloud jobs
spacr-repro RUN_DIR        # replay a recorded run from its journal
spacr-workspace RUN_DIR    # what that run had open: databases, montages, views
spacr-db-audit DB      # SQLite health, integrity, locking, reader/writer probe
spacr-leakage          # classifier train/test leakage audit
spacr-plugins          # installed plugin registry and failure diagnostics
SPACR_LOG_LEVEL=DEBUG spacr # verbose logging for one launch
1 maintainer

Metadata
1 maintainer
Release files for spacr 1.5.1.5
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| spacr-1.5.1.5.tar.gz | 55.8 MB | With provenance | Details for spacr-1.5.1.5.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| spacr-1.5.1.5-py3-none-any.whl | Python 3 | none | any | Details for spacr-1.5.1.5-py3-none-any.whl |
Total release size: 102.2 MB
Release files / spacr-1.5.1.5.tar.gz
| Download URL | spacr-1.5.1.5.tar.gz |
|---|---|
| Size | 55.8 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
4b3ec55b0140df6f34256e20927228b9deab4da0a17ea7e1abafcab36143e323
|
|
BLAKE2b-256 checksum How to use checksums |
793918ee9bd76a30f1818c68fac597e6b3e7430b85e39ac5402cdfcc18077d6f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 20, 2026.
Transparency logRelease files / spacr-1.5.1.5-py3-none-any.whl
| Download URL | spacr-1.5.1.5-py3-none-any.whl |
|---|---|
| Size | 46.4 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f1c1afcf9b4c7c46b0343ccd7e60508ce4455fba6516ef862389b7de496a283f
|
|
BLAKE2b-256 checksum How to use checksums |
1670a8ad412e0be2e8a2909ee49760c778762999303de178f90ec4a81cf831da
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 20, 2026.
Transparency logSecurity for spacr 1.5.1.5
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for spacr-1.5.1.5.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 20, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














