
twitter_openapi_python
Twitter scraping with data validation by pydantic.
Setup
pip install twitter-openapi-python
Usage
import json
import datetime

from pathlib import Path
from tweepy_authlib import CookieSessionUserHandler
from twitter_openapi_python import TwitterOpenapiPython

# login by tweepy_authlib
if Path("cookie.json").exists():
    with open("cookie.json", "r") as f:
        cookies_dict = json.load(f)
        if isinstance(cookies_dict, list):
            cookies_dict = {k["name"]: k["value"] for k in cookies_dict}
else:
    auth_handler = CookieSessionUserHandler(
        screen_name=input("screen_name: "),
        password=input("password: "),
    )
    cookies_dict = auth_handler.get_cookies().get_dict()

# To extract cookies from Windows (Linux by default)
# If you use tweepy_authlib, you must be on Windows
client = TwitterOpenapiPython()
client.additional_api_headers = {
    "sec-ch-ua-platform": '"Windows"',
}
client.additional_browser_headers = {
    "sec-ch-ua-platform": '"Windows"',
}

# get client from cookies
𝕏 = client.get_client_from_cookies(cookies=cookies_dict)

# tweet "Hello World!!" with current time
time = datetime.datetime.now().strftime("%Y-%m-%dT%H:%M:%SZ")
𝕏.get_post_api().post_create_tweet(tweet_text=f"Hello World!!{time}")

# get user info
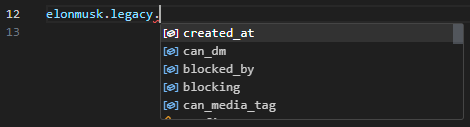
response = 𝕏.get_user_api().get_user_by_screen_name("elonmusk")
Login
from twitter_openapi_python import TwitterOpenapiPython

# guest client
𝕏 = TwitterOpenapiPython().get_guest_client()
tweet = 𝕏.get_default_api().get_tweet_result_by_rest_id("1349129669258448897")
assert tweet.data is not None
assert tweet.data.tweet.legacy is not None
print(tweet.data.tweet.legacy.full_text)
Multiple OS
The Token can only be used on the same OS that issued the Token In other words, if the sec-ch-ua-platform does not match, the Token cannot be used. This library uses the Linux Chrome header by default. To use Token issued by Windows, do the following.
client = TwitterOpenapiPython()
client.additional_api_headers = {
  "sec-ch-ua-platform": '"Windows"',
};
Endpoint
The generated client accepts any host that keeps X's path shape (/graphql/{queryId}/{operationName}, /1.1/..., /2/... under https://x.com/i/api). get_client_from_endpoint is for a host that already holds the session: it sends no cookie, no bearer, no browser headers and no transaction id, only the query and the headers you pass (the second argument is added to every request, for whatever the host defines). For example, twitter_api_safe_relay answers at http://localhost:3000/i/api with a logged-in browser session.
from twitter_openapi_python import TwitterOpenapiPython

client = TwitterOpenapiPython().get_client_from_endpoint("http://localhost:3000/i/api")
response = client.get_user_api().get_user_by_screen_name(screen_name="elonmusk")
Development
cd twitter_openapi_python
uv sync
uv run pytest test/api
uv build
uv publish
License
This project is dual licensed. You can choose one of the following licenses:
1 maintainer

Metadata
1 maintainer
Release files for twitter-openapi-python 0.1.5
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| twitter_openapi_python-0.1.5.tar.gz | 32.8 kB | With provenance | Details for twitter_openapi_python-0.1.5.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| twitter_openapi_python-0.1.5-py3-none-any.whl | Python 3 | none | any | Details for twitter_openapi_python-0.1.5-py3-none-any.whl |
Total release size: 74.6 kB
Release files / twitter_openapi_python-0.1.5.tar.gz
| Download URL | twitter_openapi_python-0.1.5.tar.gz |
|---|---|
| Size | 32.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
05132d0a1607ed7fe95a3e58ff76466ee49f1e96fc44349d7d937829460f0527
|
|
BLAKE2b-256 checksum How to use checksums |
937266b4f713110b578a605a809bcaa80ebba5814ca8249bdc7d7d2f144a4e1f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logRelease files / twitter_openapi_python-0.1.5-py3-none-any.whl
| Download URL | twitter_openapi_python-0.1.5-py3-none-any.whl |
|---|---|
| Size | 41.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
d1f1fd990ffdc8eb6c786bc2821d1911e416dba613b23fcace0d1a20966b6a21
|
|
BLAKE2b-256 checksum How to use checksums |
03ea5907cb9c5ed8c3bb10365dd76e07031d57ffc2053e2c5bf8907059c426c4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logSecurity for twitter-openapi-python 0.1.5
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for twitter_openapi_python-0.1.5.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 1, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














