agent6
A coding agent with sandboxed commands, resumable sessions, and editable workflows.
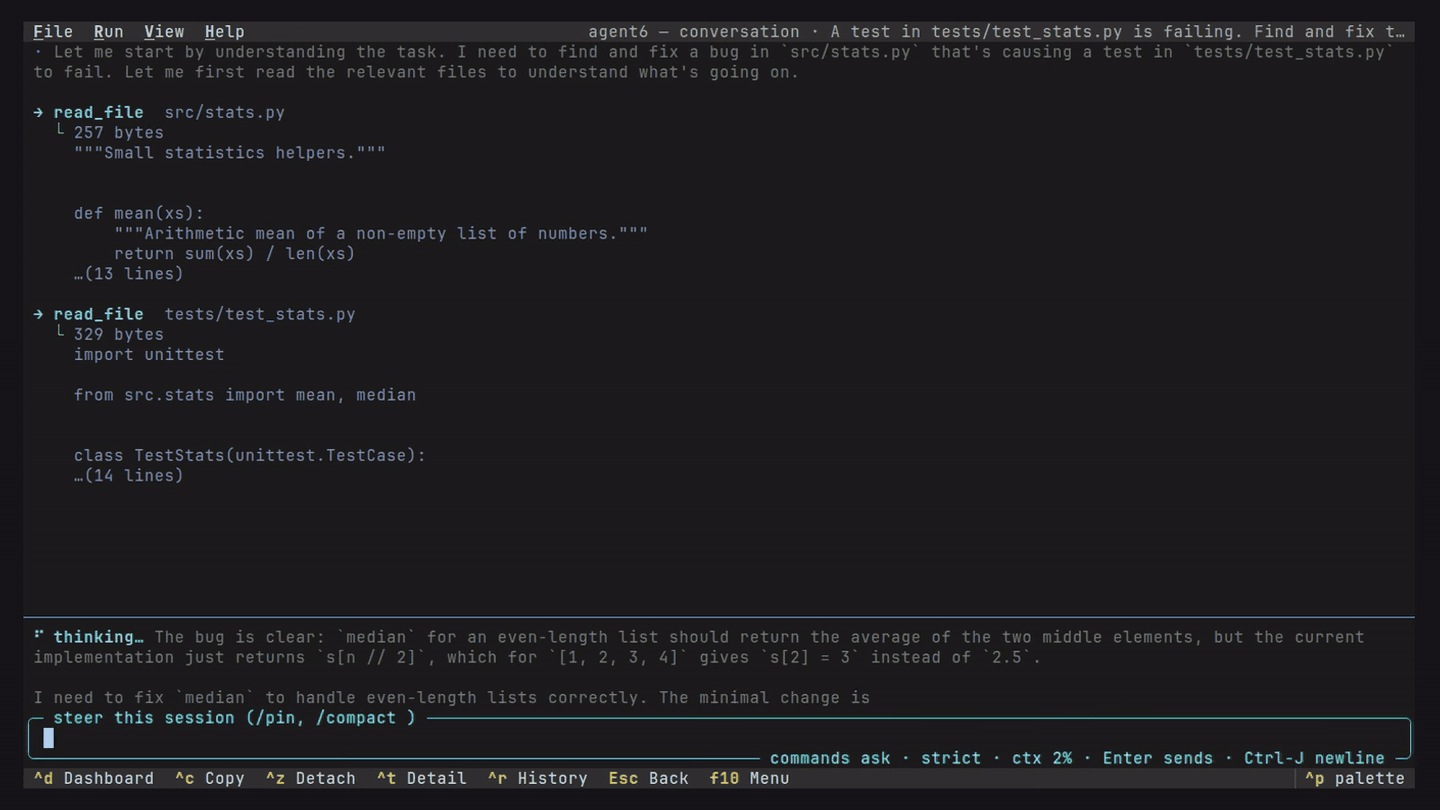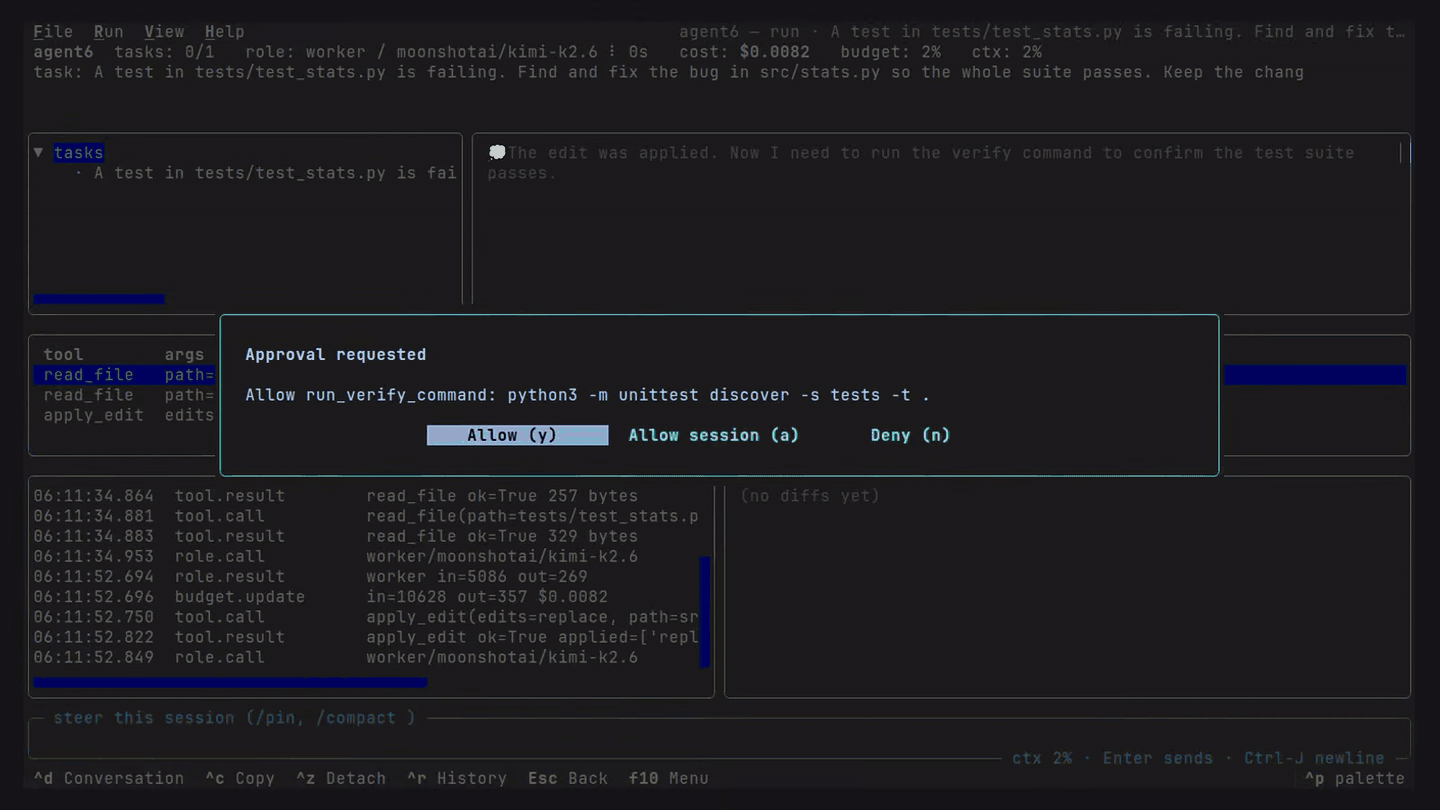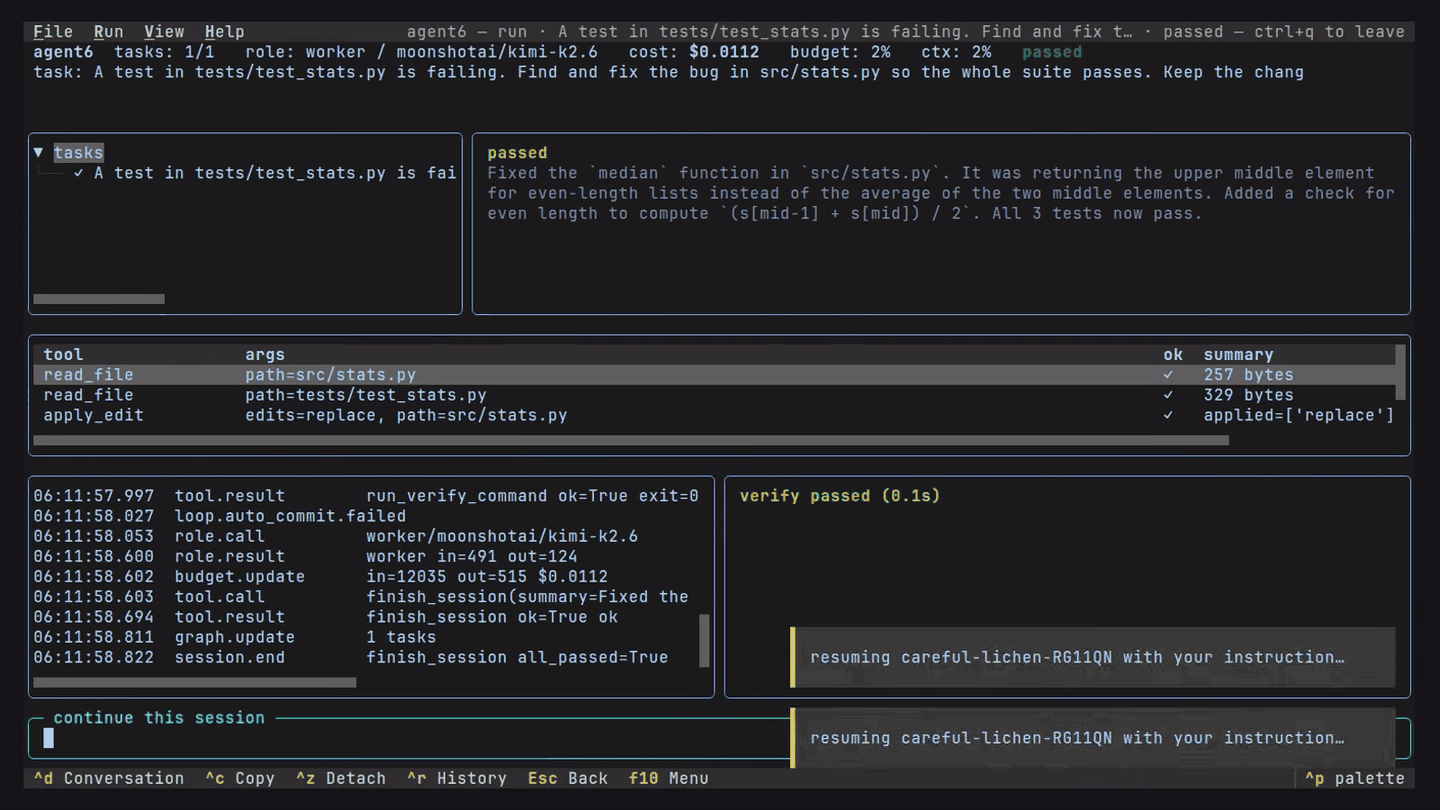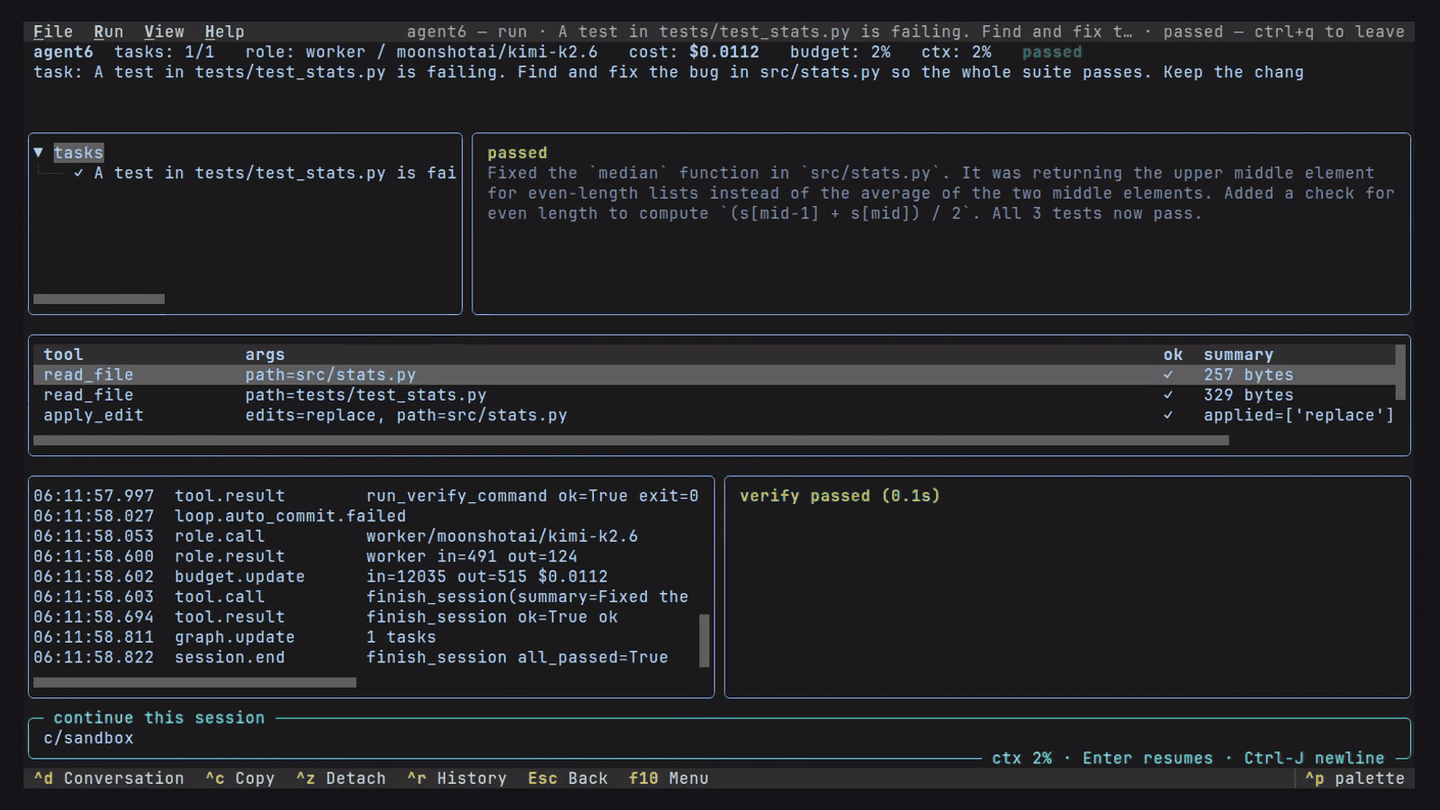
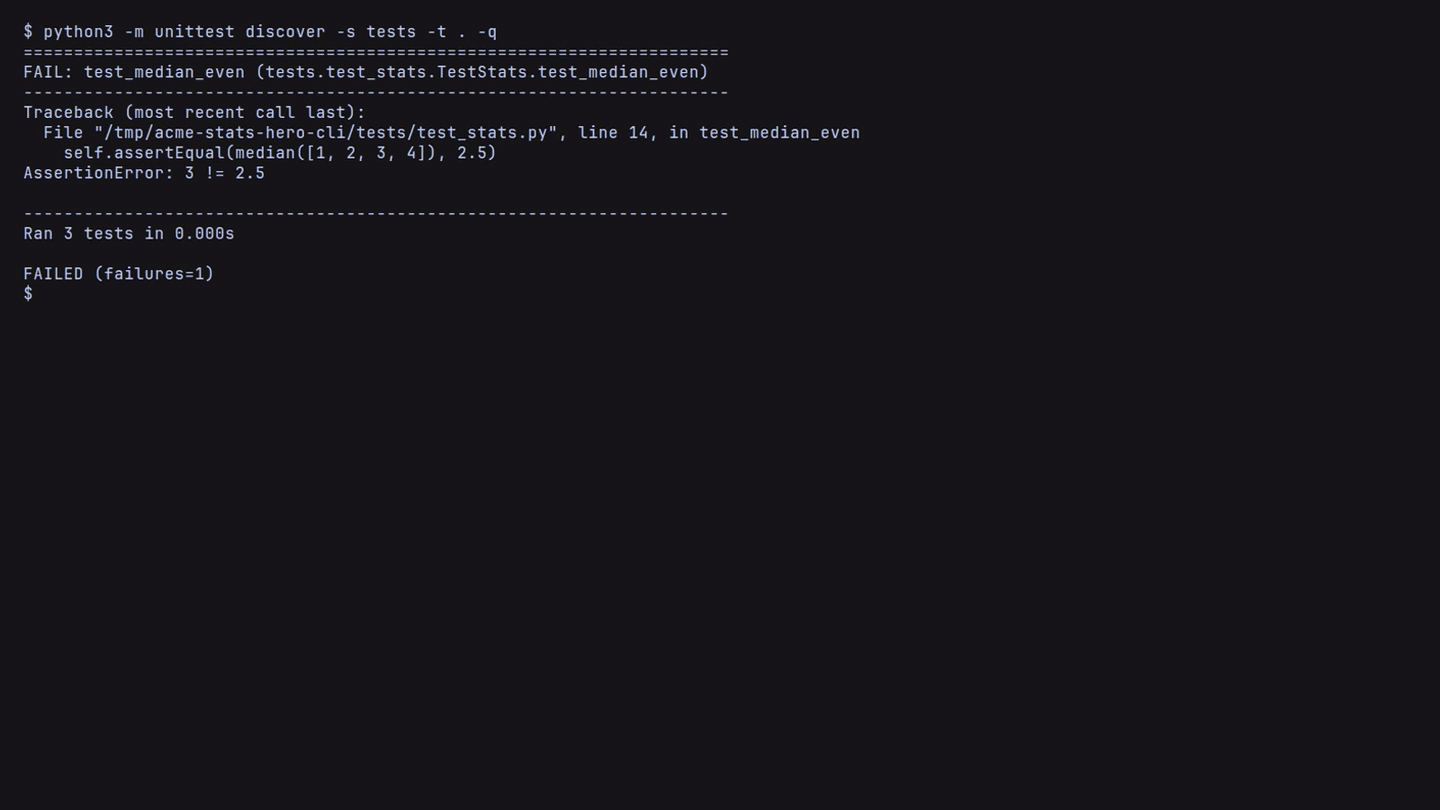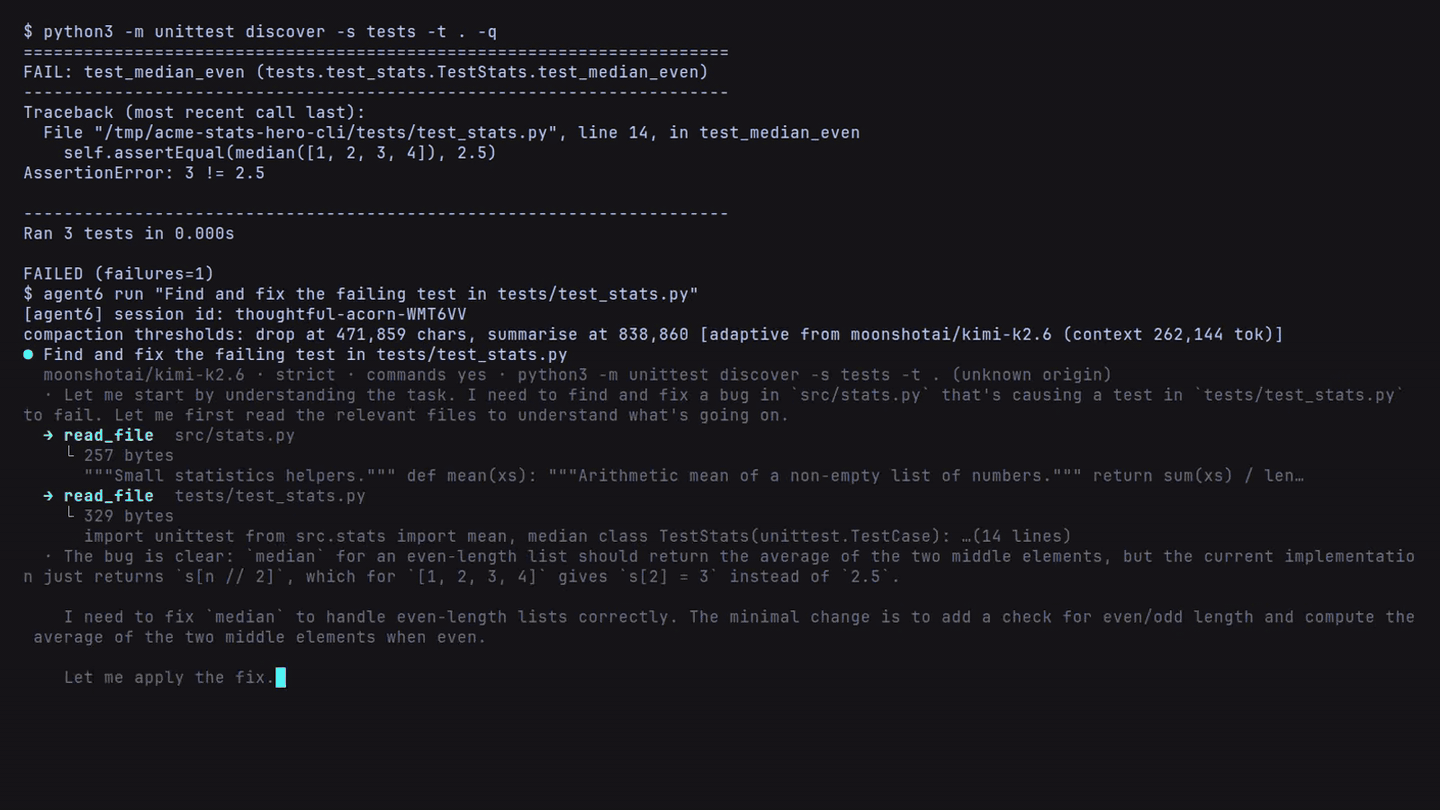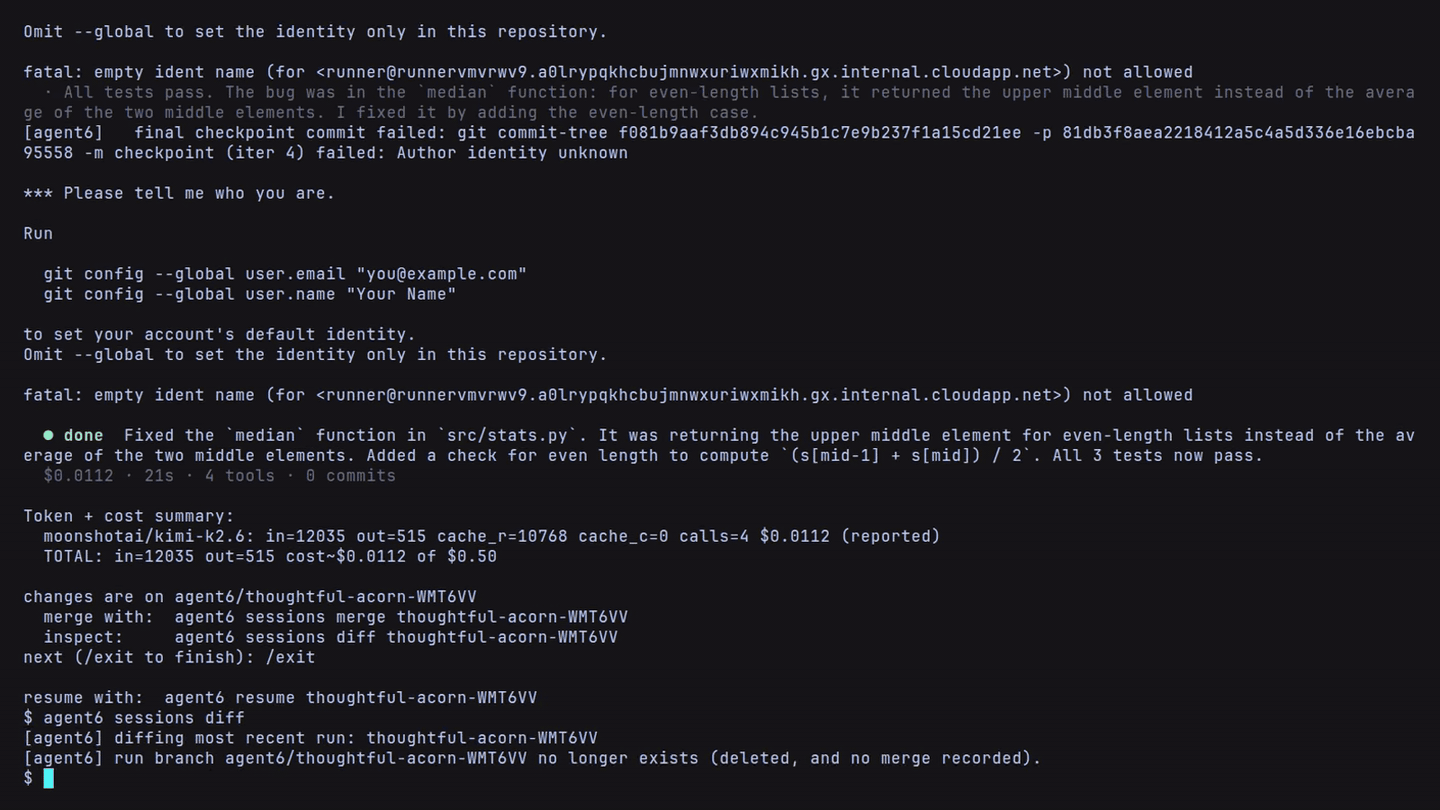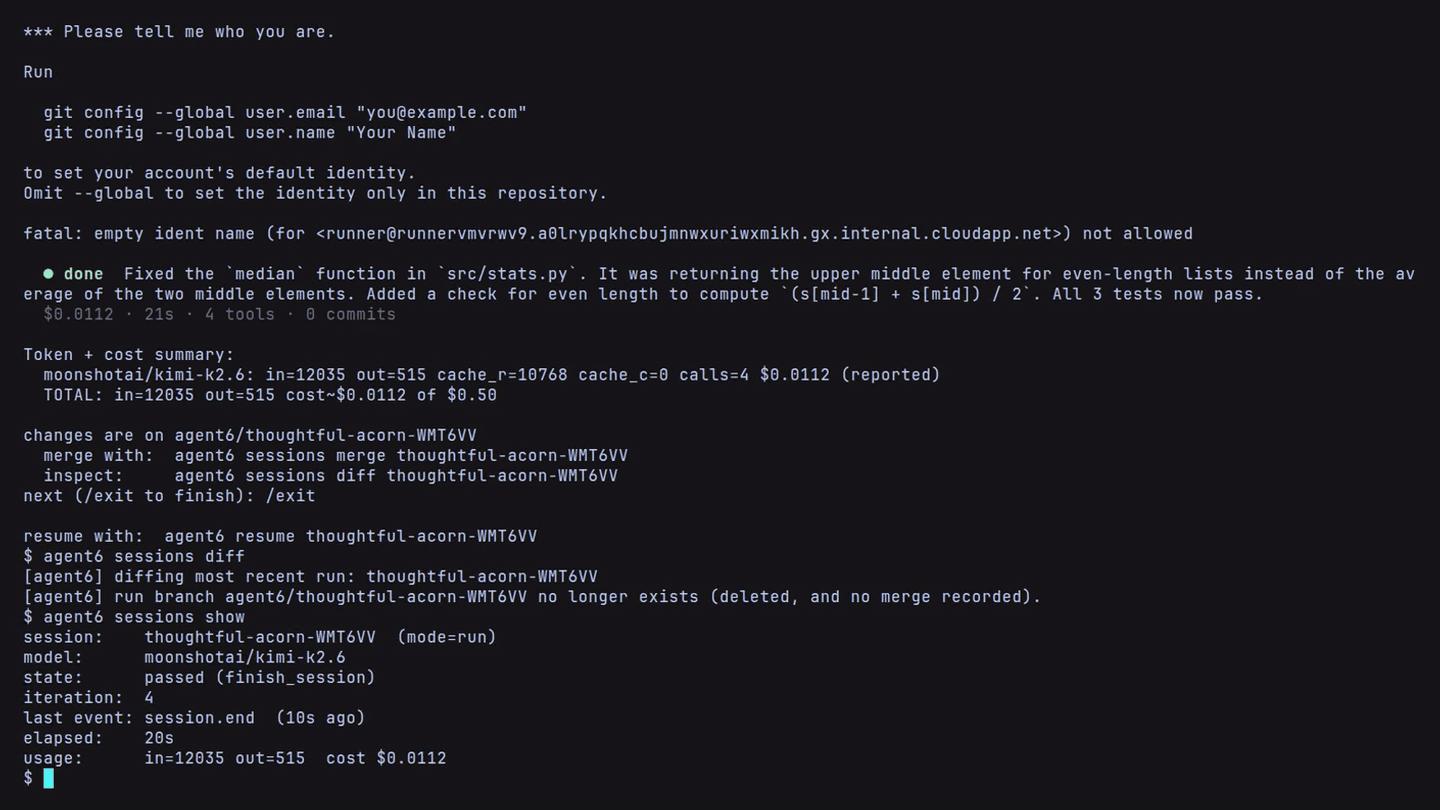
agent6 tui terminal interface |
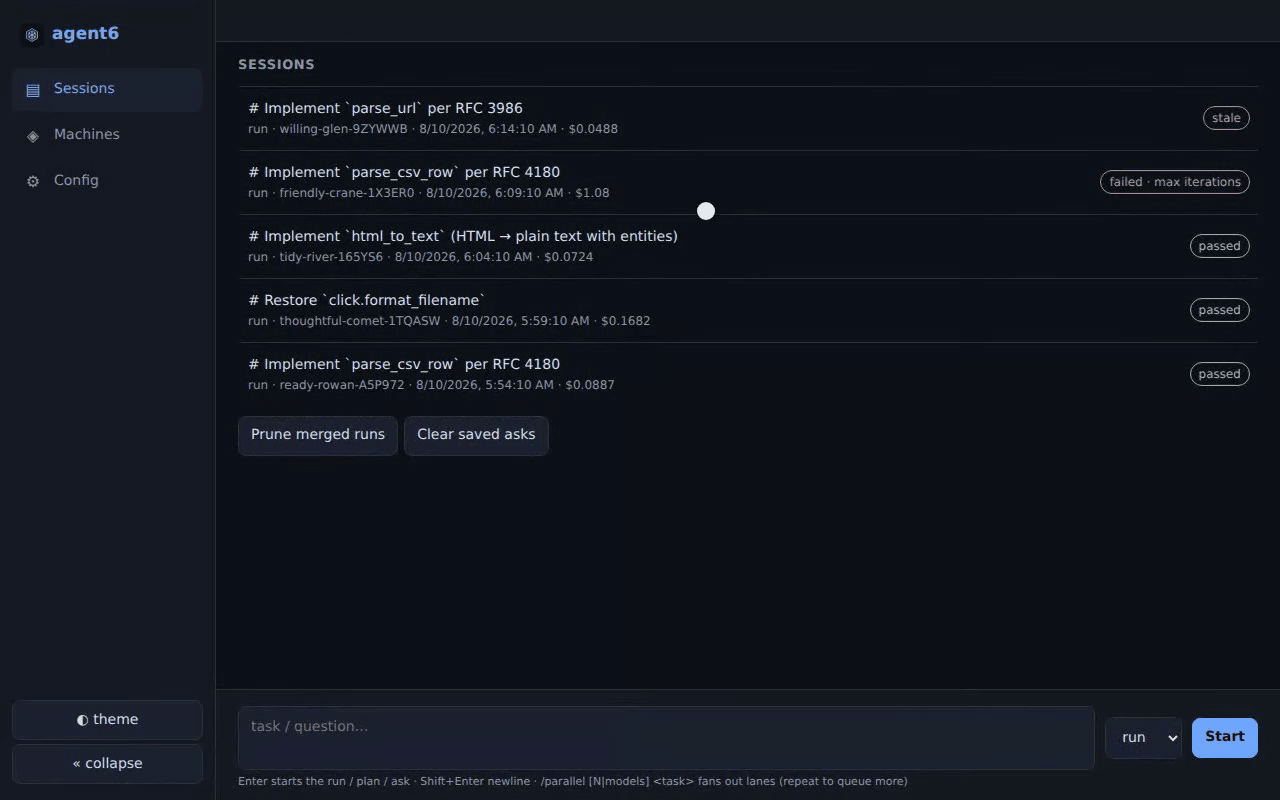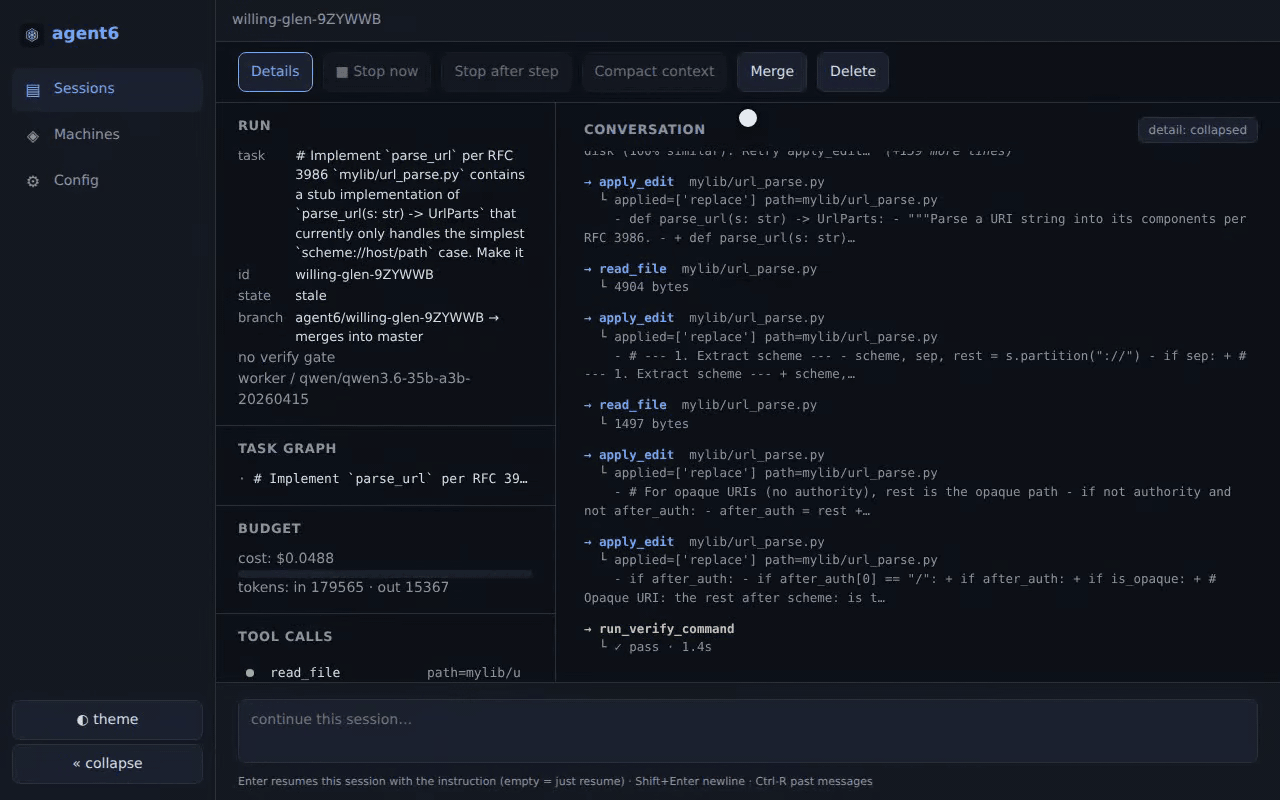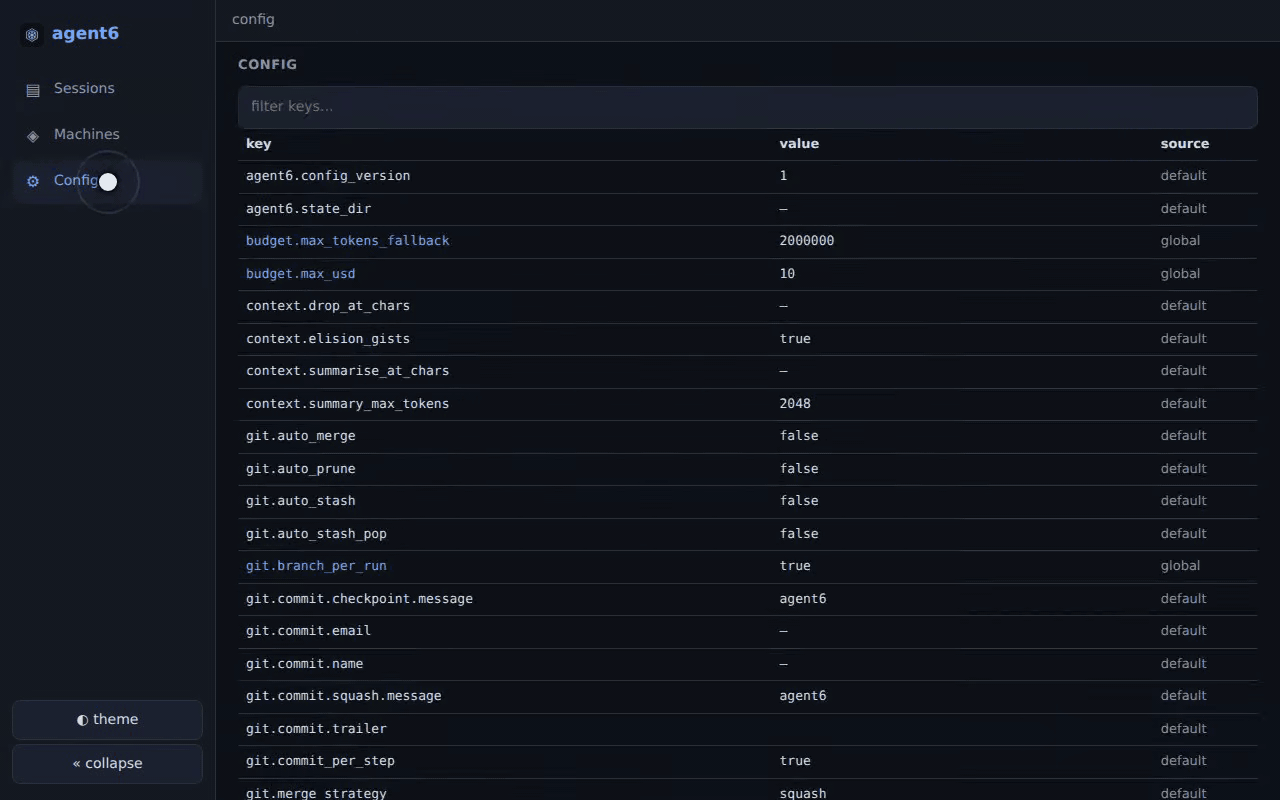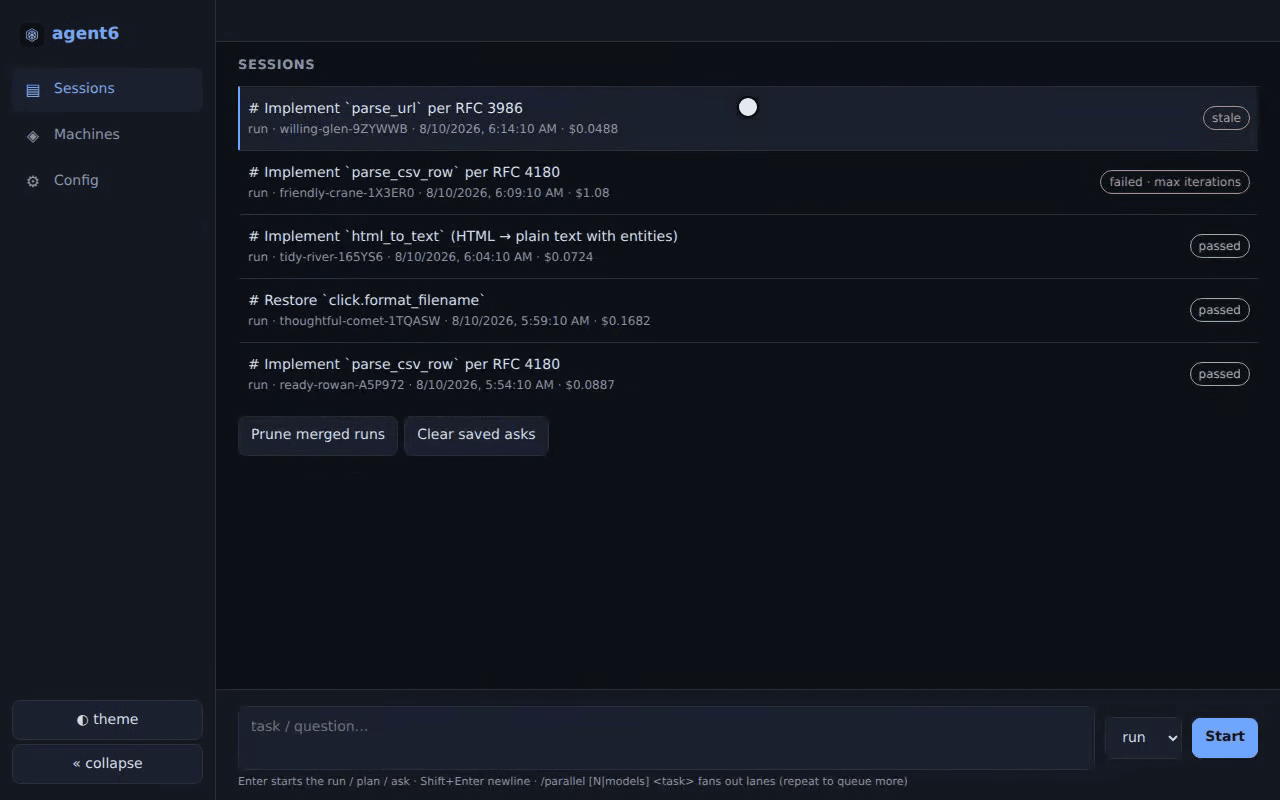
agent6 web browser interface for desktop or phone |
- Runs the model's commands in a Linux sandbox with the file and network access you set.
- Saves conversations, tool activity, and Git checkpoints so you can inspect, resume, or fork a session from an earlier turn.
- Shows the task graph, token usage and compaction as they happen.
- Pinned instructions survive compaction; repository memory carries facts across runs.
- The model can run a configured or inferred verification command; agent6 reports the result or marks the final tree unverified.
- Reviews the diff with a panel of models you configure, keeps each finding open until you resolve it, and refuses to merge over an open blocking finding.
- Runs parallel attempts in isolated clones with
--parallel Nor a list of models, then ranks the results for you to choose which to merge. - Defines long-running workflows in editable TOML state machines, combining agent runs, tool calls, waits, and branches with offline tests, crash recovery, and replay from recorded results.
- Supports repository
AGENTS.mdinstructions, SKILL.md packs, MCP servers, and background commands for development servers and watchers. - Shows the repository in the browser: the commit graph, each commit's diff, a compare of two revisions, and the files at any revision with blame.
- Nine runtime dependencies, no telemetry unless you configure an export, and no automatic updates.
Also available as a streaming CLI and through ACP editor integration.
Installation
Sandboxing supports Linux on x86_64 and aarch64; macOS runs without it, and Windows users should use WSL.
Install with uv or pipx, then connect a provider and select a model:
uv tool install agent6      # or pipx install agent6
agent6 connect              # configure a provider
agent6 model default        # choose the required default model
Use Anthropic or any OpenAI-compatible endpoint, including OpenAI, OpenRouter, Ollama, vLLM, llama.cpp, and LM Studio.
A provider entry can also use the Responses API (providers.<name>.backend = "responses") or sign in at a configured OAuth issuer.
For subscriptions, replace agent6 connect with agent6 connect chatgpt or agent6 connect claude; the latter uses your installed, signed-in Claude Code binary.
agent6 completions installs tab completion for your shell.
Usage
A run edits your current checkout.
Checkpoint commits go on a separate agent6/<id> branch; checkpointing leaves your current branch's history and index in place.
For a separate checkout, use agent6 run --worktree "your task", which starts from committed HEAD without copying uncommitted changes or untracked dependencies.
cd your-repo
agent6 check                # check configuration and sandbox support
agent6 run "your task here"
Commands ask for approval by default.
After the task finishes, enter another instruction or type /exit.
Inspect the latest session, then merge its recorded changes when ready:
agent6 sessions show        # status and verification result
agent6 sessions diff        # recorded changes
agent6 sessions merge       # merge into the run's starting branch
Other commands:
| Command | Purpose |
|---|---|
agent6 plan "task" |
plan a change; agent6 run --from <plan-id> carries it out |
agent6 ask "question" |
ask about the repository |
agent6 attach <id> |
follow a live session |
agent6 steer <id> "instruction" |
direct the next steps |
agent6 sessions findings <id> |
list a session's review findings |
agent6 sessions receipt <id> |
print the recorded tests, execution environments, review outcome and how to revert |
agent6 stop <id> --after-turn |
stop after the current turn |
agent6 resume <id> |
continue an interrupted run |
agent6 fork <id> --at-turn 7 |
fork a coding run from an earlier turn into a separate worktree |
agent6 telemetry export |
export session journals as OpenTelemetry signals or a Prometheus textfile |
agent6 pack |
copy your config, secrets, sessions and memory into the workspace before a sync |
agent6 unpack |
move the packed files into the new home |
To give a finished run more work, use agent6 resume <id> --steer "next task".
Configuration
agent6 config show prints effective settings and where each value came from.
Changes are global unless you add --repo for a repository override, for example:
agent6 config set --repo harness.verify_command '["uv", "run", "pytest"]'
The worker, planner, reviewer, and helper inherit each unset model, effort, and temperature from the required models.default.
Budgets limit spending, tokens for unpriced calls, and supported subscription usage.
Security
agent6 confines only the model's commands, in a jail on your host; the agent6 process stays trusted, holds your provider credentials, and connects to your configured providers.
The repository stays at its real path, and the jail sees your system toolchains and ~/.local/bin read-only.
sandbox.isolation = "auto" picks the strongest level the host allows and warns when it falls back:
full: commands cannot read your provider keys or the secrets file,.gitis read-only to them (sandbox.protect_git = "auto",git.control = "agent6"), and they get a private network (sandbox.network = "auto").partial: commands cannot read your keys or the secrets file, but they share agent6's network and can write.git.none: no confinement.container: commands run inside the dev container that mounts your workspace, found by its labels or named in[container]; the runtime is the boundary, and agent6 adds no confinement there.
Commands ask for approval by default (sandbox.run_commands = "ask").
agent6's own git never pushes, rewrites history or runs reset --hard, and no config key turns that on.
MCP is off by default, and locally spawned servers use the command sandbox unless explicitly configured otherwise.
agent6 check sandbox shows the effective file and command boundaries, network and approval settings, and live probe results.
In a container
- Docker gives
partialby default and allowsfullwith both--security-opt seccomp=unconfinedand--security-opt apparmor=unconfined. - Rootless Podman allows
fullwith no flags (rootful Podman).
On Ubuntu, full under Docker also needs the host to allow the jail launcher to use unprivileged user namespaces (Installation).
1 maintainer

Metadata
1 maintainer
Release files for agent6 0.0.42
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| agent6-0.0.42.tar.gz | 1.8 MB | With provenance | Details for agent6-0.0.42.tar.gz |
Built distributions (wheels)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| agent6-0.0.42-py3-none-manylinux_2_17_x86_64.musllinux_1_2_x86_64.whl | Python 3 | none | Linux musl 1.2+ x86-64, Linux glibc 2.17+ x86-64 | Details for agent6-0.0.42-py3-none-manylinux_2_17_x86_64.musllinux_1_2_x86_64.whl |
| agent6-0.0.42-py3-none-manylinux_2_17_aarch64.musllinux_1_2_aarch64.whl | Python 3 | none | Linux glibc 2.17+ ARM64, Linux musl 1.2+ ARM64 | Details for agent6-0.0.42-py3-none-manylinux_2_17_aarch64.musllinux_1_2_aarch64.whl |
Total release size: 6.6 MB
Release files / agent6-0.0.42.tar.gz
| Download URL | agent6-0.0.42.tar.gz |
|---|---|
| Size | 1.8 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a08d132f50b9348b1bee5776e73e855219110c2648914d5fbbb5ad975bcc83f7
|
|
BLAKE2b-256 checksum How to use checksums |
ada5926c11a44e883e4a11fa7fea1ce7fdb8cabd51c93c9fee70da544e942e8c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / agent6-0.0.42-py3-none-manylinux_2_17_x86_64.musllinux_1_2_x86_64.whl
| Download URL | agent6-0.0.42-py3-none-manylinux_2_17_x86_64.musllinux_1_2_x86_64.whl |
|---|---|
| Size | 2.4 MB |
| Tags | Linux glibc 2.17+ x86-64 Linux musl 1.2+ x86-64 Python 3 |
|
SHA-256 checksum How to use checksums |
705921de55f46211ea7b55815b5d9650ef2b9f5189b094314eb30ebc06529079
|
|
BLAKE2b-256 checksum How to use checksums |
6dce2b30ecd7839bd121dea7b57705e69da68585b6970dd3a7b7fc7a3bc2c842
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logRelease files / agent6-0.0.42-py3-none-manylinux_2_17_aarch64.musllinux_1_2_aarch64.whl
| Download URL | agent6-0.0.42-py3-none-manylinux_2_17_aarch64.musllinux_1_2_aarch64.whl |
|---|---|
| Size | 2.4 MB |
| Tags | Linux glibc 2.17+ ARM64 Linux musl 1.2+ ARM64 Python 3 |
|
SHA-256 checksum How to use checksums |
b40ed1f128f0b83cc5f0335f056dc06e177d338491e0c6deaf26d17477f60ccc
|
|
BLAKE2b-256 checksum How to use checksums |
ae8c33317c8bb19b79cdb942b05221daab03c8fce85e8248f5545a97316e318f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logSecurity for agent6 0.0.42
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 3 files in this release have been uploaded with provenance metadata.
Attestation for agent6-0.0.42.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 9, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.