

nff — let coding agents iterate on hardware
docs · quick start · mcp tools · cli · platform · discord



nff is an MCP server that gives coding agents direct control over physical hardware — on the bench during development, and in the field for maintenance and diagnosis.
Connect your board over USB and Claude writes, compiles, flashes, and reads serial output autonomously. Deploy devices with the nff-sdk-c library and Claude can reach them remotely: capture crash state, diagnose failures, and push fixes — without physical access.
nff is the open-source bench CLI of the nff platform — an end-to-end, agent-driven system for developing, shipping, and operating ESP32-class firmware (bench → OTA → fleet diagnosis). This repo holds the bench CLI (
nff/,nff-rs/), the device library (sdk-c/), the fleet services (observability/) and the fleet dashboard (dashboard/, deployed by Vercel as app.nanoforgeflow.com), all MIT-licensed.

you: "Run the sensor init sequence and assert the calibration values over serial"
LLM: [writes firmware] → [compiles] → [flashes ESP32] → [reads serial] → returns structured output

you: "Why did the unit in the field just hard-fault?"
LLM: [captures panic over OTA] → [reads registers + backtrace] → "Stack overflow in your sensor ISR at line 47"
features
- the bench loop, in one conversation — no switching between editor, terminal, and serial monitor. The agent iterates on firmware in response to serial output, catches exceptions, and reflashes.
- field maintenance when the firmware is dead — a crashed bare-metal MCU has no shell, no SSH, no process table. nff captures registers, stack, memory, and backtrace and routes them to a cloud agent that explains the failure and drives recovery. This is the gap Mender, balena, and similar OTA tools cannot fill: they need a living network client inside the firmware.
- ship it over the air —
nff ota deployturns the binary you just built into a staged, ECDSA-signed rollout with per-device tracking and automatic rollback;nff fleet --watchshows it land. ota → - board-universal — any of PlatformIO's ~1000+ boards across ~40 platforms (every ESP32 variant, RP2040/Pico, all STM32 families, AVR, SAMD, Teensy, nRF52, Uno R4, RISC-V…), toolchain auto-installed on first build. arduino-cli remains available as a second backend. boards →
- live on-chip debugging — real breakpoints, call stacks, and variable inspection over JTAG/SWD (OpenOCD + GDB, driven by nff). debug →
- local-first — compile, flash, monitor, debug, and the MCP tools need no account and never open a browser. Only OTA,
repair, andagentrequire a sign-in. - one Rust binary — self-contained, no Python runtime, and it self-updates in the background like Claude Code does.
get started
macOS / Linux:
curl -fsSL https://nanoforgeflow.com/install.sh | sh
Windows (PowerShell):
irm https://nanoforgeflow.com/install.ps1 | iex
Then plug in your board and run:
nff init      # detects the board, writes config, registers + starts the MCP server
nff doctor    # verify
Restart Claude Code so it picks up the MCP server, then just describe what you want:
you: "Flash sketches/blink_esp32 and confirm the LED is toggling over serial"
LLM: [compiles] → [flashes ESP32] → [reads serial] → "LED toggling at 1 Hz, confirmed"
Full install options, --cloud sign-in, and first-run detail: quick start →
mcp tools
34 tools over streamable HTTP on 127.0.0.1:3010/mcp, started in the background by nff init.
| Group | Tools | Covers |
|---|---|---|
| Bench | 7 | list_devices, compile, flash, serial_read/write, reset_device, get_device_info |
| Debug | 14 | breakpoints, call stack, variables, registers, memory, stepping, raw GDB |
| Field | 8 | diagnose (local, no login), repair (cloud, ELF-symbolized) + auth lifecycle |
| Fleet & OTA | 5 | ota_deploy, ota_status, ota_deployments, ota_devices, fleet_status |
Full signatures and return shapes: mcp tools →
demo
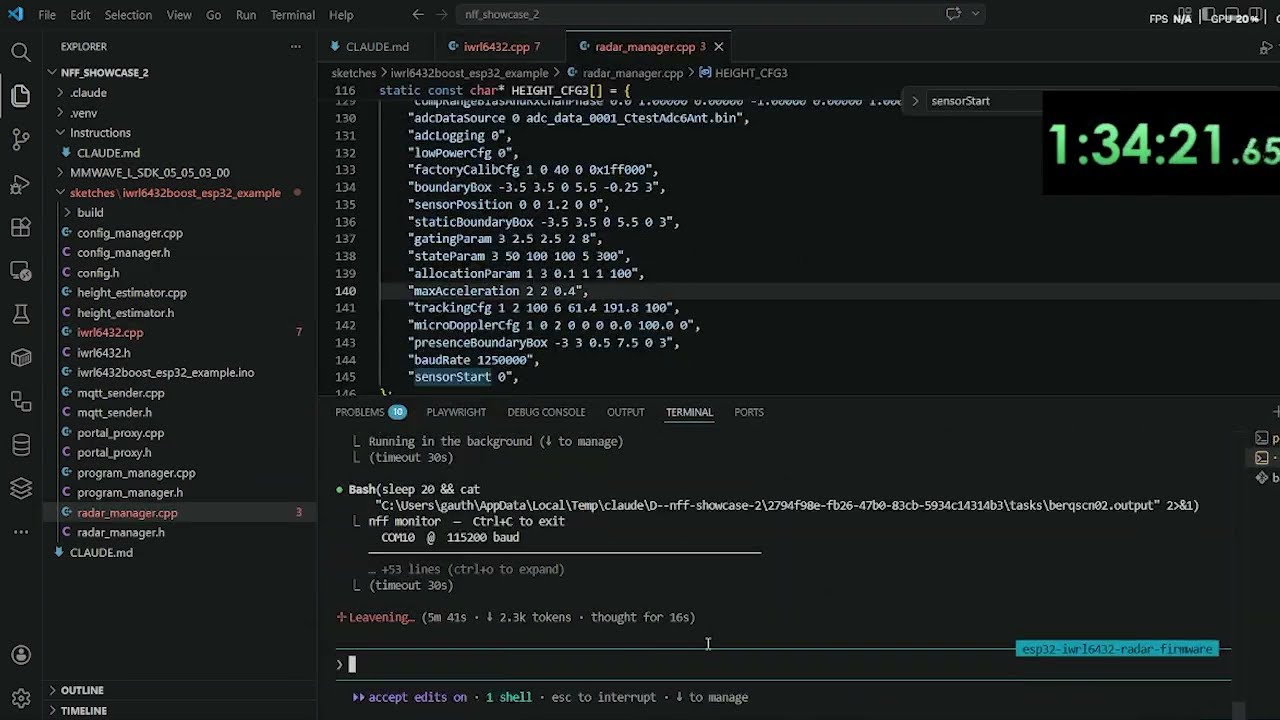
docs

everything lives at nanoforgeflow.com/docs: quick start · cli reference · configuration · mcp tools · using claude code · device sdk · provisioning · ota deploys · git-push deploys · fleet status · crash diagnosis · on-chip debug · power · security
In-repo reference (docs/): boards & USB ids · self-update & config · roadmap · architecture
contributing
Bugs and feature requests go to GitHub Issues; read CONTRIBUTING.md before opening a PR — adding a board is usually a two-line change. Please follow the Code of Conduct, and report vulnerabilities via SECURITY.md. Questions and ideas are welcome on Discord.
license
MIT — see LICENSE.
Copyright (c) 2026 Gauthier Lechevalier
1 maintainer

Metadata
1 maintainer
Release files for nff 0.2.41
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distributions (wheels)
| File | Actions Reset | |||
|---|---|---|---|---|
| nff-0.2.41-py3-none-win_amd64.whl | Python 3 | none | Windows x86-64 | Details for nff-0.2.41-py3-none-win_amd64.whl |
| nff-0.2.41-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.whl | Python 3 | none | Linux glibc 2.17+ x86-64 | Details for nff-0.2.41-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
| nff-0.2.41-py3-none-macosx_11_0_arm64.whl | Python 3 | none | macOS 11.0+ ARM64 | Details for nff-0.2.41-py3-none-macosx_11_0_arm64.whl |
| nff-0.2.41-py3-none-macosx_10_12_x86_64.whl | Python 3 | none | macOS 10.12+ x86-64 | Details for nff-0.2.41-py3-none-macosx_10_12_x86_64.whl |
Total release size: 20.1 MB
Release files / nff-0.2.41-py3-none-win_amd64.whl
| Download URL | nff-0.2.41-py3-none-win_amd64.whl |
|---|---|
| Size | 4.9 MB |
| Tags | Python 3 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
9b24c01f5058f116765241c36d2f4960a17463c5b4ab7783ab7c2f6853ccac14
|
|
BLAKE2b-256 checksum How to use checksums |
5d8723060c03a1a21de3dcf38f71034e80031c43f1f75649d664a3a140e79eb4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.15
|
Release files / nff-0.2.41-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | nff-0.2.41-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 5.6 MB |
| Tags | Linux glibc 2.17+ x86-64 Python 3 |
|
SHA-256 checksum How to use checksums |
a0a1d122bab397551f8be9418f768a06268b405fa047d69f5c1be0fb372c515e
|
|
BLAKE2b-256 checksum How to use checksums |
c3623b58303c374daf9352167a90f831ad5359e3c56f1eeb798991fa9d946650
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.15
|
Release files / nff-0.2.41-py3-none-macosx_11_0_arm64.whl
| Download URL | nff-0.2.41-py3-none-macosx_11_0_arm64.whl |
|---|---|
| Size | 4.8 MB |
| Tags | Python 3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
bd93fbe522851bb6855b38abfc4c68ebbb1862d6003fe1f18cf97c3257a5dff8
|
|
BLAKE2b-256 checksum How to use checksums |
acddb56085b7d41a91ed873bf4ab28a50ca467b6afbba115cbf0e06be232d3be
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.15
|
Release files / nff-0.2.41-py3-none-macosx_10_12_x86_64.whl
| Download URL | nff-0.2.41-py3-none-macosx_10_12_x86_64.whl |
|---|---|
| Size | 4.9 MB |
| Tags | Python 3 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
37b876efd4dcce5968a4d2e42c5380d806e40fee7440d518d412e68933ee52f1
|
|
BLAKE2b-256 checksum How to use checksums |
31a33b6cf97ef3d8030fde7d82d079a6c187f4da283baf1b1d55784c793bdb4f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.15
|
Security for nff 0.2.41
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














